Answers to common questions about selling, implementing, and operating DMARC monitoring for MSP clients.
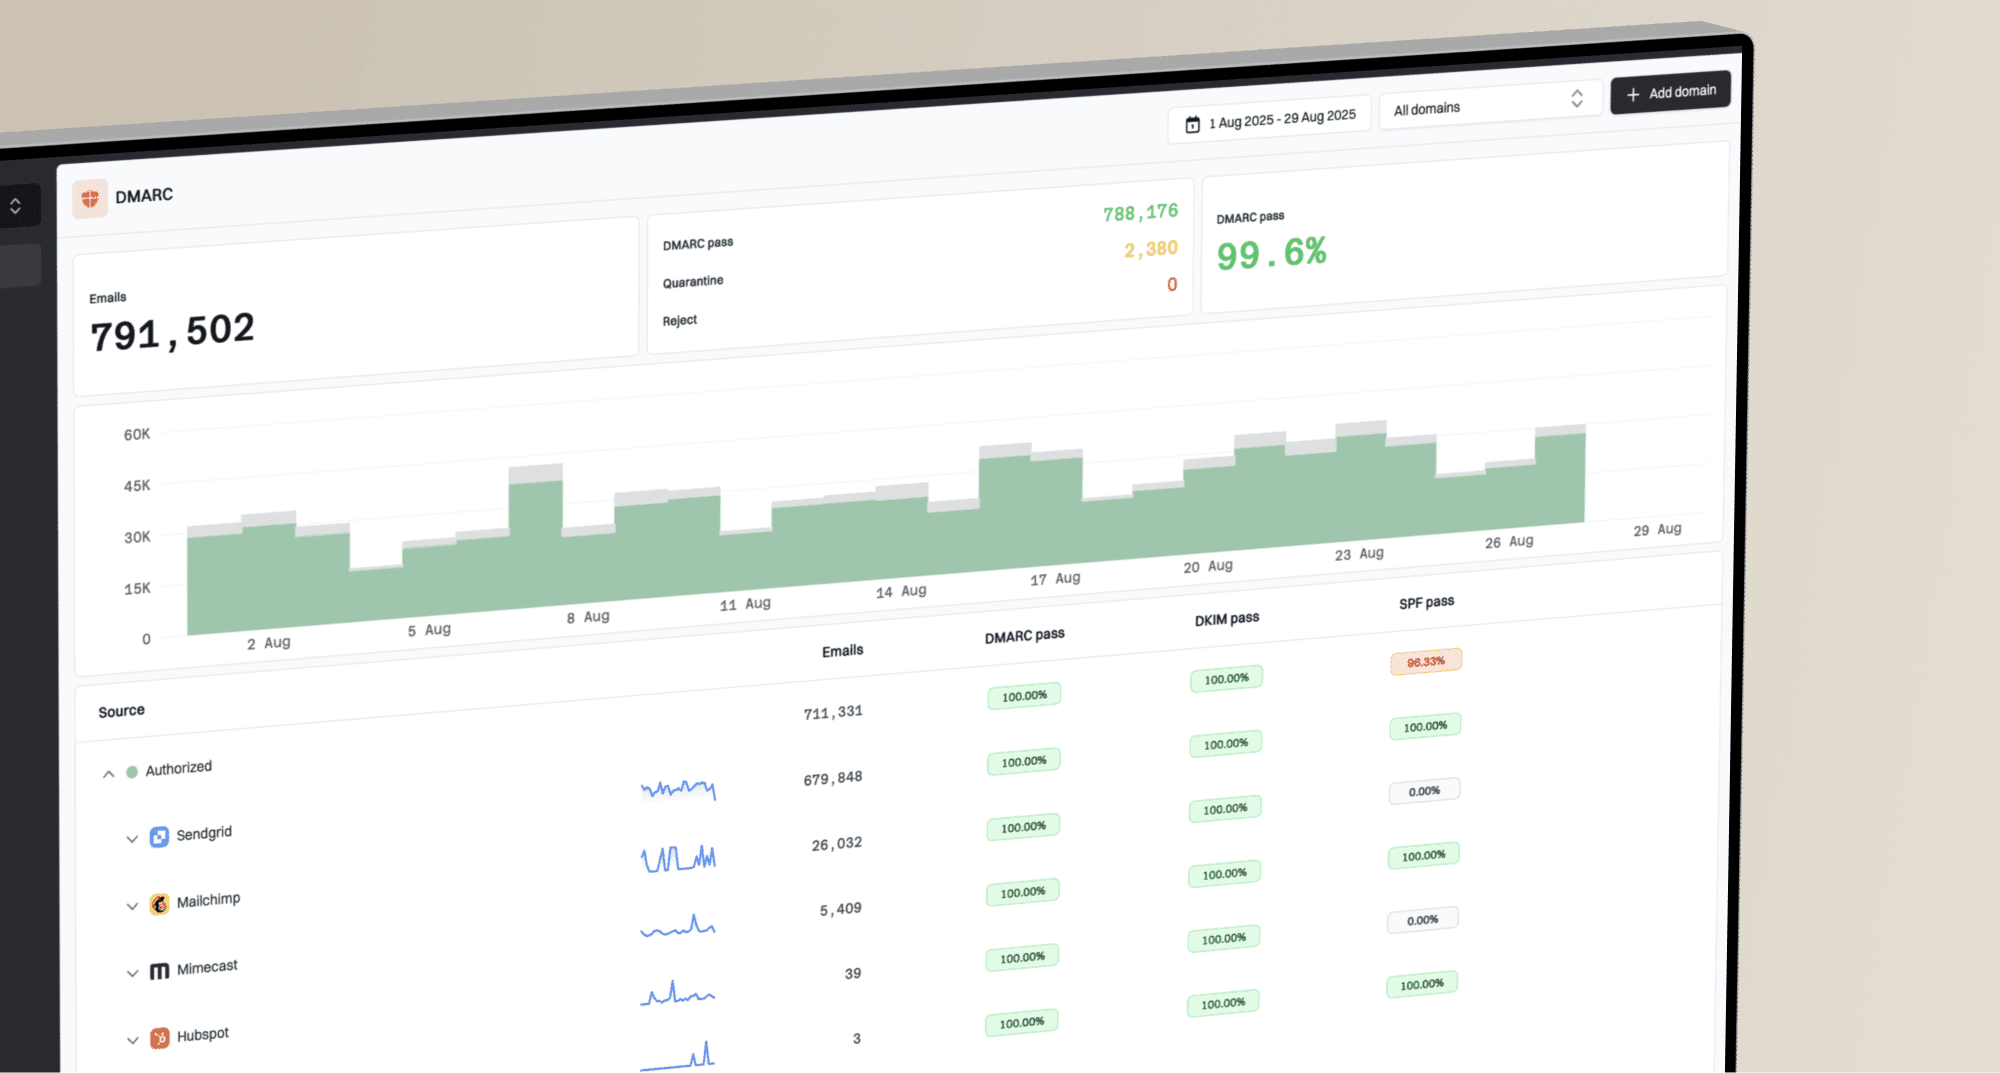
DMARC monitoring for MSPs is the process of collecting client DMARC reports, identifying authorized and unauthorized senders, fixing SPF and DKIM alignment, and reporting progress across many client domains.
Most MSPs package DMARC monitoring as a managed email security service that includes onboarding, sender discovery, DNS guidance, policy staging, issue triage, and recurring client reports.
Yes. A DMARC audit can show visible gaps in spoofing protection, sender governance, and DNS hygiene. It gives sales teams a concrete security finding instead of a generic pitch.
MSPs should start with monitoring, identify legitimate senders, fix SPF or DKIM alignment, use staged policy changes, and move to p=reject only after client mail streams are understood.
Useful client reports should cover policy status, sender cleanup, authentication failures, new sources, spoofing attempts, open risks, and the next practical action.
Start monitoring your DMARC reports today
What you'll get with Suped
Real-time DMARC report monitoring and analysis
Automated alerts for authentication failures
Clear recommendations to improve email deliverability