
How does SURBL impact email deliverability and what are best practices for avoiding listings?

Published 10 Aug 2025
Updated 27 Oct 2026
13 min read
Summarize with

Updated on 27 Oct 2026: We clarified SURBL lookup results, confirmed opt-in requirements, and checks to verify recovery after delisting.
SURBL can affect email deliverability by giving mailbox providers and filtering gateways a reputation signal about the URLs inside an email. It does not list your sending IP, your From domain, or your mail server merely because those identities sent the message. Its public Multi dataset lists hosts associated with malicious or abused URLs, including compromised websites and click trackers used in unsolicited mail.
That distinction matters. A SURBL blocklist or blacklist listing can hurt placement when the message body contains a listed domain, tracking host, redirect, or landing page URL and the receiver uses that signal. The same sender can pass SPF, DKIM, and DMARC while still landing in spam because the content points to a domain with poor URL reputation. A listing alone does not prove it caused a placement change, so compare it with message content and recipient results before taking broad action.
For ongoing monitoring, Suped's product keeps DMARC, SPF, DKIM, blocklist monitoring, and deliverability signals in one workflow. Use that context to compare a domain listing with sending-source and authentication changes, then inspect the affected campaign's links separately.
What SURBL checks
SURBL is a URI and domain reputation data source. Its public description says it is used to filter or tag unsolicited messages based on links in the message body, regardless of sender IP address. The SURBL site also makes a key point: SURBLs are lists of websites, not lists of mail servers, sender addresses, open proxies, or message sending IPs. Its implementation guidelines also cover numeric IP addresses used literally as URL hosts. Do not resolve a linked domain to its hosting IP and treat that IP as a sender-IP listing.
When a receiver scans a message, its filtering stack can extract URLs, normalize hostnames, evaluate redirects, and check domains against URL reputation data. A listed tracking domain has a different operational cause than a listed landing page, but both create the same core problem: the email body contains a URL associated with abuse.
A SURBL listing is also different from a registrar or registry suspension. The listing does not itself stop the domain from resolving or prevent its mail from being transmitted. It supplies reputation data that a receiving filter can use when deciding how to handle a message.
SURBL signal
- Object: The domain or numeric IP host in a message-body URL.
- Trigger: Spam traps, abuse reports, phishing pages, malware, or abused redirects.
- Impact: Messages with the listed URL can receive a negative content reputation signal.
Sending reputation
- Object: The IP, DKIM domain, Return-Path domain, or visible From domain.
- Trigger: Complaints, bounces, bad engagement, failed authentication, or volume spikes.
- Impact: The sending identity receives a negative sender reputation signal.
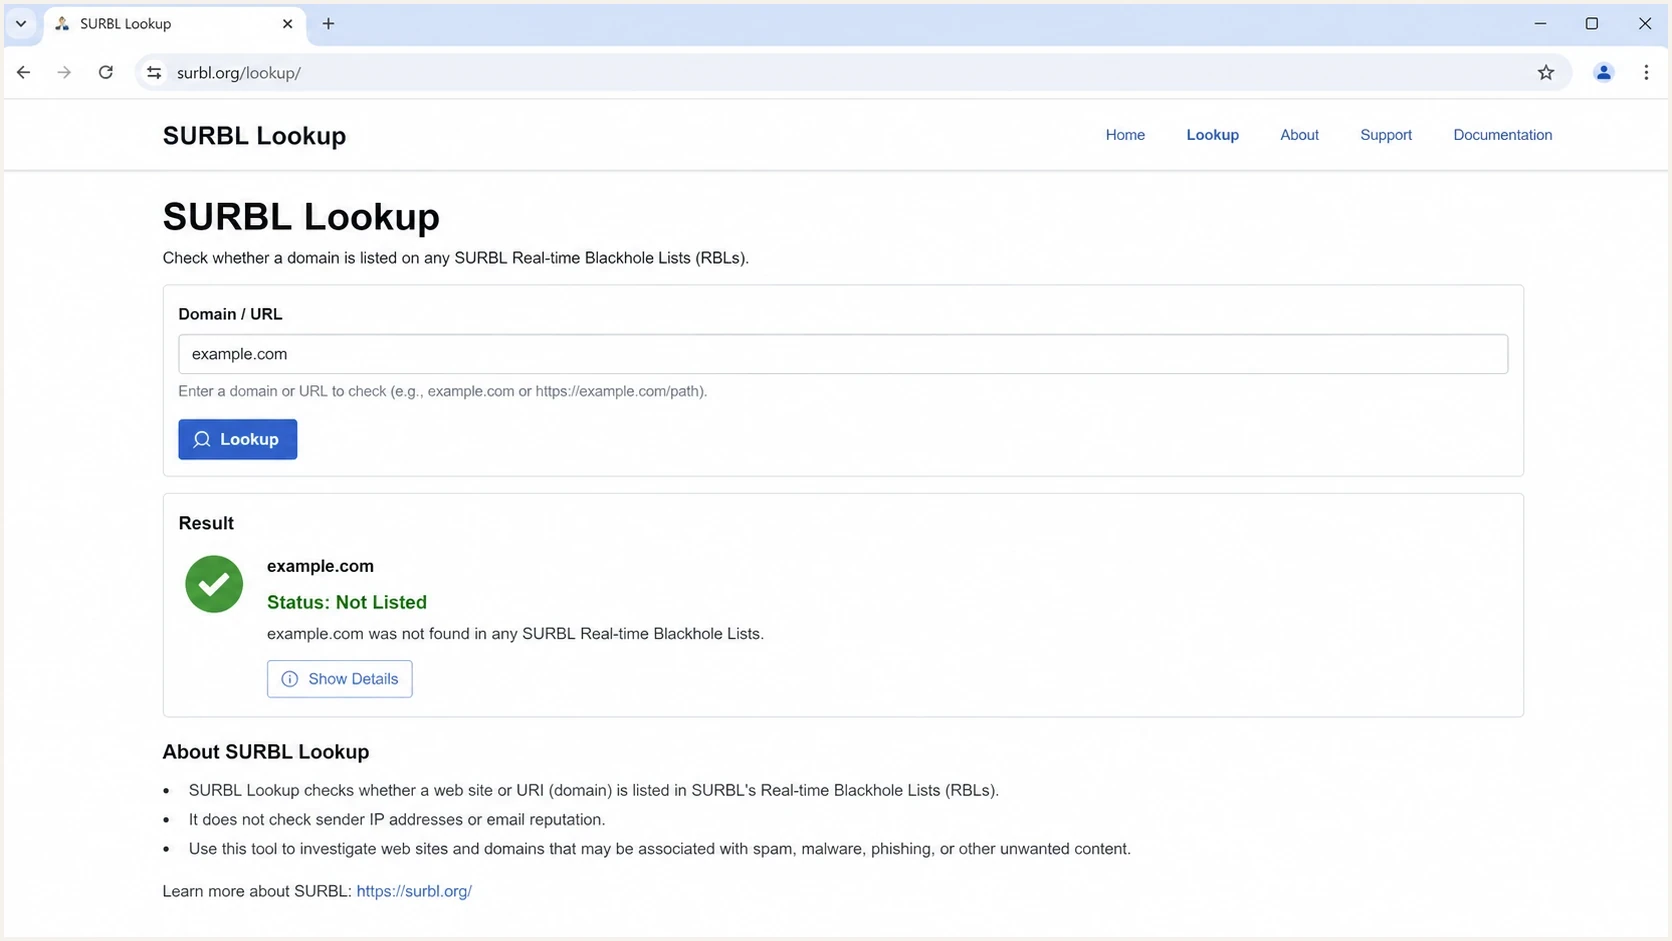
SURBL Lookup page for checking URL and domain reputation.
SURBL list types to know
SURBL's public Multi data set combines several list types into one bitmasked response. The category matters because a phishing listing, cracked site listing, click tracker listing, and disposable mail domain listing point to different fixes. Treat the lookup result as a clue about the cause, not only as a pass or fail result.
|
|
|
|---|---|---|
ABUSE | Spam or abused sites | Identify bad traffic |
PH | Phishing sites | Remove fake pages |
MW | Malware sites | Clean hosted files |
CR | Cracked sites | Patch site access |
CT | Click tracker domains | Confirm opt-in and retain evidence |
DM | Disposable mail domains | Verify disposable-mail classification |
Common SURBL categories and the first remediation focus.
Public Multi checks domains or subdomains and can return more than one category through its bitmask. SURBL also describes private data sets for newly delegated domains, hashed abuse data, shortener domains, abused shortener URIs, and full-URI checks. Full path analysis belongs to those URI-specific data sets, so do not assume a public Multi result evaluated every path or query string in the original link. A DM result identifies a disposable email domain, not a phishing or malware finding.
How to read SURBL lookup results
SURBL's list documentation explains Multi response codes. The last octet identifies categories, including combined results.
|
|
|---|---|
127.0.0.64 | ABUSE |
127.0.0.32 | CT |
127.0.0.80 | MW and ABUSE combined: 16 + 64 |
127.0.0.1 | Query access is blocked; this is not a domain listing |
Examples of Multi A-record responses, not live lookup results.
Distinguish unlisted hosts from failed queries
NXDOMAIN from a working, permitted query means the queried host is not listed at that moment. A timeout or SERVFAIL is inconclusive. The implementation guidelines explain that public DNS queries use wildcards, so a listed parent can match its subdomains. A fresh subdomain does not reliably escape a parent listing.
How SURBL affects deliverability
A SURBL listing can affect message filtering when a receiver uses it. A listed URL can contribute to spam placement, quarantine, temporary rejection, or a gateway block. Separate delivery from inbox placement: server acceptance does not establish that a message reached the inbox. The behavior behind a URL listing can also damage sender reputation.
A SURBL listing does not produce a universal one-to-one failure. Receivers set their own filtering rules, combine URL reputation with other signals, and can change those rules without publishing the weighting. Treat the listing as evidence to investigate, then measure recipient-domain results before deciding how widely to pause mail.
When the impact is most visible in Gmail, do not assume either that SURBL caused the drop or that Gmail ignores the listing. Gmail does not publicly document SURBL as a named filtering input. Compare the listing time with Gmail domain reputation, complaint spikes, stale cohorts, template changes, and results at other recipient domains. A correlation narrows the investigation, but a controlled message test provides stronger evidence.
|
|
|
|
|---|---|---|---|
Tracking host | Abuse on a shared host | Spam folder | Identify the owner and stop abuse |
Landing page | Abuse signal | Gateway block | Clean page |
Short link | Abused redirect | Content penalty | Remove shortener |
Root domain | Abusive mail or compromised content | Broad filtering | Fix the confirmed cause |
Common SURBL-related deliverability patterns
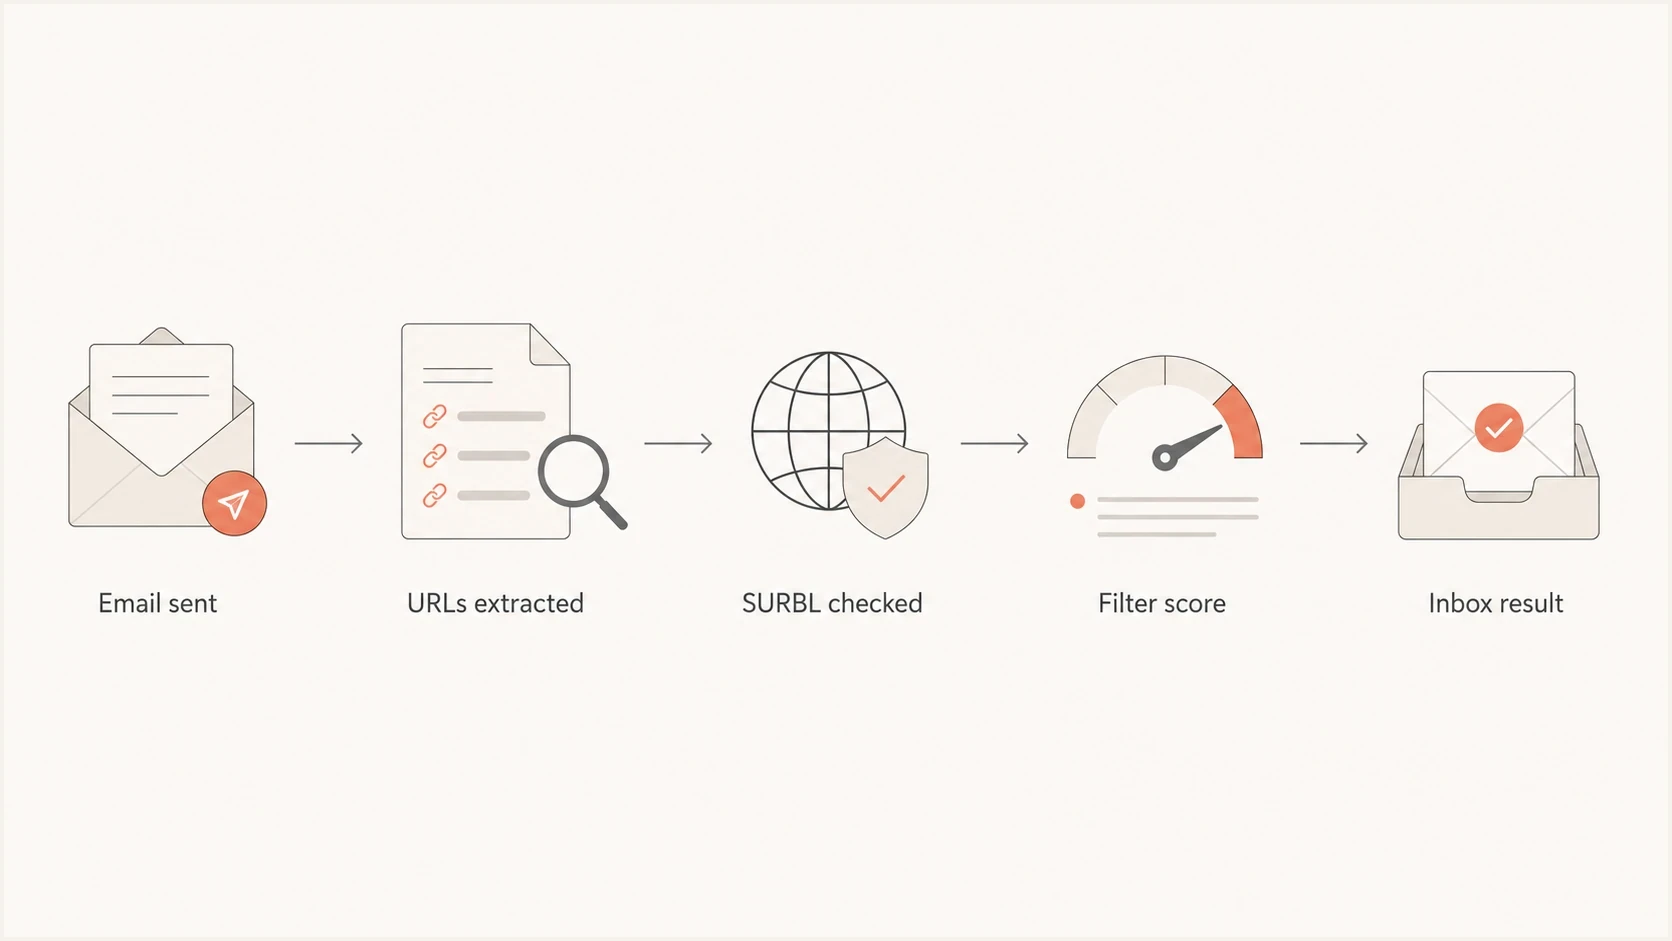
SURBL email filtering flow: URL extraction, reputation check, filter score, and inbox result.
If the issue shows up mainly at one mailbox provider, compare those results against your broader blocklist basics checks and recent campaign changes. That keeps the investigation focused on what changed: an acquisition source, a click domain, a landing page, or a campaign sent to old records.
How to verify whether SURBL is affecting delivery
A listing is evidence of URL reputation risk, not proof that it caused a placement change. Public claims that every major mailbox provider either relies on or ignores SURBL are not supported by provider documentation. Test the affected message before pausing a healthy program or dismissing the listing.
- Confirm the live result: Check the exact domain or subdomain, record the category and time, and recheck before acting because Multi data changes quickly.
- Map it to the message: Verify that the listed item appears in a visible link, tracking URL, image host, unsubscribe URL, or redirect chain in the delivered MIME content.
- Preserve a baseline: Record inbox, spam, rejection, bounce, and complaint results by recipient domain before changing the message.
- Run a controlled comparison: For listings without a security issue, send two versions to a small internal seed set with the same authenticated sender and content, changing only the listed URL. Compare placement by recipient domain. Never test links to known harmful content.
- Inspect receiver evidence: Review SMTP status text, message headers, and gateway logs for a named URL reputation rule. The absence of a named rule does not prove the URL had no effect.
- Match action to risk: Pause links to compromised, phishing, or malware content immediately. For an unexplained ABUSE or CT listing, isolate the URL, clean the cause, and measure results instead of replacing unrelated mailboxes or IPs.
What a clean test proves
If the version without the listed URL performs better across repeated tests, the URL is a credible contributor. If results remain unchanged, keep investigating sender reputation, audience quality, authentication, and the rest of the message. One test narrows the cause but does not establish a permanent provider rule.
Why SURBL listings happen
Listings can follow unsolicited mail or compromised websites even when DNS authentication is correct. Weak acquisition and list hygiene can expose linked domains to complaints or spam traps. Forms without ownership confirmation accept mistyped addresses and bot submissions. Purchased, appended, scraped, or poorly sourced contacts make the problem worse because they send campaign URLs into places that measure abuse.
- Single opt-in: A weak form lets typo addresses and fake records enter the list without proof of inbox ownership.
- Old lists: Reactivating stale records risks bounces or complaints, and some abandoned addresses become spam traps.
- Shared tracking: A shared click domain carries risk from other senders using the same infrastructure.
- Public shorteners: Abused redirect services make it harder for filters to trust the final destination.
- Compromised pages: A clean sender can link to a hacked page, expired domain, injected redirect, or compromised CMS.
- DNS abuse: A compromised DNS control panel can add malicious subdomains under a legitimate domain.
- Weak governance: Teams reuse old campaign URLs without checking current redirects, page status, or ownership.
Confirmed opt-in and CT listings
SURBL's CT policy covers tracking domains used in mail sent without confirmed opt-in, including mail reaching spam traps. Double opt-in confirms mailbox ownership; retain the confirmation evidence.
- Confirmation: Record the signup source and the confirmation event before adding an address to ongoing marketing sends.
- Validation limits: Validation checks address quality; it does not prove consent or guarantee that an address is not a spam trap.
For opt-in programs, the risk is still real when signup forms accept unconfirmed addresses or bot submissions. The distinction between recorded consent and mailbox confirmation is covered in the guide to 100% opt-in lists. Address validation does not establish mailbox ownership, and a role address is not inherently abusive.
Best practices for avoiding listings
The best way to avoid a SURBL listing is to reduce the chance that your URLs appear in abusive, trap-heavy, or poorly sourced mail. URL reputation is a shared responsibility across the teams that control targeting, consent, landing pages, redirects, tracking domains, and monitoring.
- Use confirmed opt-in: Confirm mailbox ownership before click-tracked marketing sends and retain confirmation records for CT review.
- Validate forms: Reject malformed addresses, flag likely typos, and rate-limit submissions with bot controls. Validation does not establish consent.
- Clean often: Suppress hard bounces, complaints, and unsubscribes promptly. Review inactivity using confirmed subscriber actions rather than non-opens alone.
- Separate links: Use branded tracking domains by brand, customer, or mail stream instead of one shared click host for everything.
- Avoid shorteners: Do not use public URL shorteners in commercial email when a branded tracking domain is available.
- Audit redirects: Check every redirect hop, expired domain, parked domain, affiliate link, and legacy campaign URL before sending.
- Segment sends: Review consent before reactivating older records and start with engaged subscribers. Segmentation does not repair a listed URL.
- Monitor changes: Check domain and IP reputation before major launches, after source changes, and after unexplained spam placement.
Campaign URL review checklisttext
Campaign name:
Tracking domain:
Landing domain:
Redirect hops:
Final URL owner:
Opt-in source:
Last list cleanse:
Known risky cohorts:
Send date:
Reviewer:
Testing a message before launch also helps because URL reputation problems often appear in the body scan, not the DNS scan. A practical preflight is to send the real campaign to an email tester and review the authentication, content, and link signals before the audience receives it.
Blocklist checker
Check your domain or IP against 144 blocklists.





Use the widget for quick blocklist checks alongside a campaign URL inventory. A clean sending-domain result does not establish that every tracking host or linked destination in tomorrow's campaign is unlisted.
How to request SURBL delisting
When a SURBL listing appears, first confirm which URL is listed, where it appears, and whether recipient results changed. Pause any compromised, phishing, or malware destination immediately. For an ABUSE or CT result without a confirmed security issue, isolate the affected link and investigate the source before filing a removal request or changing unrelated sending infrastructure.
Evidence to gather first
- Confirm scope: Check whether the listed item is the root domain, a subdomain, a tracking host, or a final landing page.
- Trace sends: Find the campaigns, segments, forms, and data sources that included the listed URL.
- Remove risk: Suppress weak records, pause risky campaigns, clean redirects, secure DNS, and fix compromised pages.
- Document action: Prepare a short delisting note with facts, dates, and remediation steps already completed.
Delisting request notestext
Listed domain:
Listed subdomain:
SURBL category:
Affected campaigns:
Audience source:
Opt-in method:
Problem found:
Remediation done:
Date paused:
Date cleaned:
Contact email:
For shared email infrastructure, prove whether the listed URL belongs to your branded tracking domain, the platform's shared click host, your landing page, or another linked service. A shared relay domain that appears only in SPF is not a SURBL message-body hit. Remediation depends on who controls the URL that the receiver actually extracted.
Check the actual MIME content before changing infrastructure. A campaign can look clean at a DNS level and still contain a redirect chain, link shortener, stale destination, or cracked page that damages reputation. If the issue sits in the links themselves, changing the sending IP or rotating the From domain does not remove the listed URL.
After remediation, use SURBL's official removal form, reached through the Lookup option on its site. The SURBL list documentation requires cleanup before requesting removal for compromised sites, phishing, or malware. Include evidence of the completed fixes and keep follow-ups with the original case.
After removal, recheck the affected host and representative subdomains, then compare recipient-domain results. Allow for DNS cache expiry and continue investigating receiver-specific reputation if delivery remains poor. Delisting does not guarantee inbox placement.
Use Suped for SURBL monitoring
Suped's product is useful when SURBL is one signal inside a wider deliverability investigation. The blocklist monitoring workflow tracks domain and IP listings, pairs them with DMARC and authentication data, and turns issues into practical remediation steps. This helps teams avoid one-off blacklist checks when multiple brands, senders, or client domains need regular review.

Blocklist monitoring page showing domain and IP checks across blocklists with importance and status
Use Suped's blocklist alerts to identify the affected domain and list source, then review DMARC, SPF, and DKIM results for separate authentication issues. Inspect the campaign MIME content to confirm which listed host is present; authentication results do not establish that its links are safe.
For MSPs and agencies, the multi-tenant dashboard keeps each client's evidence separate. A SURBL listing for one client and an authentication failure for another can be reviewed without mixing affected domains or incident notes. That keeps the response focused on the cause.
A broader domain health checker is still worth using for quick validation because authentication, DNS, and reputation issues often arrive together after a migration or new sending source.
Practical SURBL prevention tips
Best practices
Use confirmed opt-in for click-tracked marketing and retain evidence of mailbox confirmation.
Keep branded tracking domains separate by customer, business unit, or major mail stream.
Review every linked landing page before each campaign, including redirects and old pages.
Common pitfalls
Assuming a URL blocklist or blacklist problem is only about the sending IP address alone.
Using public shorteners or shared click domains that inherit other senders' bad behavior.
Treating address validation as proof of consent or a guarantee that no spam traps remain.
Expert tips
Keep a campaign URL inventory so delisting work starts with evidence, not guesswork.
Separate transactional and marketing links, then check for listings on their parent domain.
Monitor DMARC and blocklist signals together, since receivers score many signals at once.
Frequently asked questions
SURBL does not assess an IP as a mail sender. Numeric IP addresses can be listed when they appear literally as hosts in message-body URLs. A separate sender-IP blocklist or blacklist checks sending infrastructure.
A listed URL can coincide with worse Gmail placement, but Gmail does not publicly document SURBL as a named filtering input. Compare recipient-domain results and run a controlled version without the listed URL. Do not treat the listing alone as proof that Gmail used it.
Do not pause every campaign based on one lookup. Pause immediately if the URL leads to compromised, phishing, or malware content. Otherwise isolate the listed tracking link, test its effect, fix the cause, and keep unrelated mail streams separate.
For CT, SURBL's stated criterion covers tracking domains used in mail sent without confirmed opt-in. Address validation does not replace confirmation. Confirmed opt-in does not prevent separate website-security listings.
Confirm which URL is listed, identify the campaigns that used it, check the SURBL category, remove weak data sources, clean redirects or compromised pages, and document what changed. Start the removal request through the SURBL lookup process after remediation.
No. A registrar or registry suspension can stop a domain from resolving. A SURBL listing supplies reputation data to filters and does not itself disable DNS, mailboxes, or the domain registration.




