Why doesn't Brevo offer full SPF alignment and how much does it impact deliverability?
Published 1 Jul 2025
Updated 24 Oct 2026
12 min read
Summarize with

Updated on 24 Oct 2026: We updated the Brevo setup guidance and clarified SPF alignment, full DMARC participation, and bulk sender requirements.
Brevo's legacy or default shared-IP setup keeps the envelope sender, also called the Return-Path or SMTP MAIL FROM domain, under Brevo's infrastructure instead of your visible From domain. SPF then passes for Brevo's bounce domain, not your brand domain. Brevo is gradually rolling out a branded-subdomain setup that can put SPF and the Return-Path on your domain, so the current answer depends on which domain setup flow your account has.
Missing SPF alignment does not prevent DMARC from passing when DKIM passes with your domain. An SPF alignment warning is not the same as a delivery failure or a spam-folder diagnosis. Delivery means the receiving server accepted the message, while deliverability is where the message lands after filtering. Treat the warning as a diagnostic signal, then check whether a branded subdomain is available before considering a dedicated IP.
- Direct answer: Older shared-IP setups use a Brevo bounce domain, while the new branded-subdomain flow can provide SPF alignment.
- Deliverability impact: Missing SPF alignment alone does not establish the cause of spam placement when domain-matched DKIM and DMARC pass.
- When it matters: Investigate when DKIM fails, DMARC fails, or your authentication requirements call for both mechanisms to match your domain.
- Best next step: Check headers, DKIM, DMARC reports, the Return-Path, and Brevo's domain settings before changing infrastructure.
How SPF alignment affects DMARC
SPF alignment is a DMARC concept. It asks whether the domain that passed SPF matches the visible From domain. SPF itself can pass while SPF alignment fails. Under relaxed alignment, the domains can be different subdomains of the same organizational domain. Under strict alignment, they must match exactly. A provider-owned Brevo bounce domain does not match your From domain in either mode. That domain is visible in Authentication-Results as smtp.mailfrom and often appears in Return-Path after delivery.
A message-level DMARC pass does not require both SPF and DKIM to match the From domain. It requires at least one of them to pass and match. If Brevo signs with DKIM using your authenticated sending domain, DMARC can pass through DKIM even when SPF alignment is absent. That distinction separates a noisy warning from a real authentication failure. The separate concepts are easier to debug when you keep SPF authentication and alignment apart.
Typical legacy shared-IP resulttext
Authentication-Results:
  spf=pass smtp.mailfrom=mail123.sender-sib.com
  dkim=pass header.d=example.com
  dmarc=pass header.from=example.com

Result:
  SPF passes, but SPF alignment is not present.
  DKIM passes and matches the From domain.
  DMARC passes.
Check whether DMARC passes for the domain in the visible From address. If it does, the SPF alignment warning still identifies a configuration gap, but it does not automatically explain spam placement.
Why Brevo handles SPF this way
A provider-owned Return-Path centralizes bounce handling on Brevo's legacy shared-IP setup. A custom SMTP MAIL FROM domain, also called a custom MAIL FROM or custom Return-Path, requires customer-domain configuration and working bounce routing. Those are operational considerations, not evidence of a confirmed internal reason for Brevo's earlier limitation.
A Brevo dedicated IP uses customer-domain DNS and gives the sender direct responsibility for IP reputation. That path can provide SPF alignment, but it is no longer the only documented path. Brevo's newer branded-subdomain setup can also move SPF and the Return-Path onto a customer subdomain while mail still uses shared IPs.
A Brevo community thread records customer confusion about SPF alignment and merging SPF records. It does not establish that a dedicated IP is the only solution. Use current domain setup instructions for your account rather than treating older discussions as configuration guidance.
Shared IP
Shared IP sending reduces the sender's infrastructure work. The legacy setup uses a provider-owned Return-Path, while eligible accounts can use a branded subdomain.
- Upside: Suitable for low or uneven volume, with no separate IP warm-up.
- Tradeoff: SPF remains provider-domain based unless the branded-subdomain setup is enabled.
Dedicated IP
Dedicated IP sending can use customer-domain infrastructure and puts reputation work on the sender, including warm-up and volume consistency.
- Upside: Direct IP reputation control and customer-domain SPF are available with the right configuration.
- Tradeoff: Low or inconsistent volume can make IP reputation unstable.

Brevo domain authentication settings for SPF, DKIM, DMARC, and dedicated IP setup.
A provider-owned Return-Path can look like a defect in your DNS even when your DNS is correct. Adding another include to your root SPF record does not force Brevo's legacy setup to use your domain in the Return-Path. The envelope sender must change, which is what the branded-subdomain or dedicated-IP configuration does.
How Brevo's branded subdomain changes the answer
Brevo documents a branded subdomain in its new domain setup flow. The rollout is gradual, so it is not available to every account. When enabled, Brevo uses a subdomain of your sending domain for SPF and the Return-Path, as well as branded tracking and image links. This removes the older assumption that shared-IP sending must always use a Brevo-owned envelope domain.
For a visible From address at example.com and a Return-Path under mail.example.com, a passing SPF result meets DMARC's default relaxed alignment because both share the organizational domain. It does not satisfy strict SPF alignment when aspf=s requires the domains to match exactly. An enforcement policy such as p=quarantine or p=reject does not require strict SPF matching. The policy controls handling of DMARC failures; aspf controls SPF domain matching. Domain-matched, passing DKIM still gives a message a DMARC pass under either enforcement policy.
- Open Brevo's domain settings and check whether the new guided setup or branded-subdomain option appears.
- Use an unused sending subdomain when practical, because it supports managed delegation without handing over DNS control of your root domain. Subdomains help organize mail streams, but do not guarantee complete reputation isolation.
- Publish only the DNS records Brevo generates for that domain, then verify smtp.mailfrom and Authentication-Results in a received message. Preserve an existing DMARC policy and reporting destinations when applying DNS changes.
- If the option is absent, keep domain-matched DKIM and ask Brevo about account availability before buying a dedicated IP.
Brevo's current domain setup guidance says the branded-subdomain flow is still being rolled out. Account availability is therefore part of the diagnosis.
How much deliverability risk this creates
For normal marketing or transactional mail on Brevo shared IPs, missing SPF alignment alone does not diagnose a deliverability problem when domain-matched DKIM and DMARC pass. There is no fixed inbox-placement percentage gain that follows from adding SPF alignment. Mailbox providers also judge domain and IP reputation, complaints, list quality, and sending behavior.
SPF alignment becomes more important when DKIM is unreliable. It also supplies a second independent DMARC path and clearer evidence during audits, migrations, and incident response. For a third-party sender, stable domain-matched DKIM still comes first. A branded Return-Path is the next improvement when your account supports it. Forwarding often breaks SPF or replaces the envelope sender, while DKIM can survive if the signed content remains intact. A branded Return-Path therefore does not replace DKIM.
Authentication risk by result
Qualitative triage for Brevo authentication, not a prediction of inbox placement.
Lower authentication risk
DKIM pass
DKIM passes with your domain and DMARC passes. Inbox placement still depends on filtering.
Needs investigation
Mixed DKIM
DKIM passes inconsistently or only some mail streams are signed.
Authentication failure
DMARC fail
DKIM fails and SPF is not matched to the From domain.
Do not treat a dedicated IP as a universal fix. Brevo's dedicated IP guidance recommends one for senders running at least three campaigns a week to 3,000 or more contacts, or sending more than 100,000 emails a month with no gaps longer than a week between sends. It needs warm-up, steady volume, and active reputation management. Low or inconsistent volume can produce thin reputation history and worse delivery consistency than a healthy shared pool.
- DMARC passes: SPF is not matched, DKIM is matched, and DMARC passes across real inbox tests. Investigate other evidence before blaming SPF alignment.
- Needs attention: Different campaign types show different DKIM domains or unsigned mail.
- Fix first: DMARC aggregate reports show Brevo volume failing DMARC.
- Watch closely: Inbox placement drops at the same time authentication failures rise.
Does a DMARC pass meet every sender requirement?
A passing message and a complete sender configuration are different checks. RFC 9989 still allows a message to pass DMARC through either SPF or DKIM when the passing domain matches the From domain under the configured mode. Its section 8 requirements for full DMARC participation also call for domain owners to send with both SPF and DKIM alignment. Passing through DKIM alone does not establish full participation. A branded Return-Path helps close that configuration gap.
Gmail's bulk sender FAQ requires both SPF and DKIM authentication, but only one must match the From domain to meet its current alignment requirement. Gmail recommends matching both. A Brevo message with spf=pass for a provider-owned bounce domain, domain-matched dkim=pass, and dmarc=pass can therefore meet that authentication requirement without SPF alignment. That is different from SPF failing altogether, and it does not establish compliance with every sender requirement.
Publishing p=none does not turn a DMARC failure into a pass. It requests no DMARC enforcement action for failures. Keep checking the actual authentication results and meet the separate requirements for marketing mail, including one-click unsubscribe. Choose a branded Return-Path to improve authentication coverage, without assuming a guaranteed inbox-placement gain.
What to check before changing anything
Start with the received message headers, not the dashboard warning. Send a real email to a mailbox you control, open the original message, and check SPF, DKIM, and DMARC results. Record which domain passed DKIM, which domain passed SPF, which domain appears in smtp.mailfrom, and which mechanism gave DMARC its pass. Use the Authentication-Results added by the receiving mailbox provider.
Then check Brevo's Domains page. Look for the new guided domain setup and a branded subdomain before editing your root SPF record. Brevo's legacy authentication instructions do not require SPF or MX records. The new guided setup supplies a branded CNAME for SPF and Return-Path when using individual records, or NS records for eligible managed delegation. Use the records for your actual configuration.
If your domain already has an SPF record, check it for broken syntax, duplicate SPF records, and the limit of 10 DNS-querying terms, including nested includes and redirects. Multiple SPF records at one hostname return permerror. A broken record can affect other senders that use that domain in the envelope sender. A focused SPF checker separates record problems from Brevo's Return-Path behavior.
Add include:spf.brevo.com or mx only when the DNS instructions for your Brevo account explicitly require them, at the exact hostname shown. Merge required mechanisms into an existing SPF record at that hostname rather than publishing a second SPF record. If Brevo supplies a CNAME at a hostname, do not add an SPF TXT record at that same name. Keep one final all mechanism at the end of an SPF record.
An SPF include authorizes a sender for the domain where the record is evaluated, but it does not change a provider-owned SMTP MAIL FROM. Changing ~all to -all only changes the result for unauthorized IPs. It does not change the domain DMARC compares. Treat every SPF include as active sending permission, not as proof of DMARC alignment.
SPF checker
Find SPF syntax issues, lookup limits, and weak records.
?/16tests passed
For a broader view, run a domain health check and compare it with your DMARC aggregate reports. Check the DMARC-evaluated SPF and DKIM results as well as the raw authentication results: a raw SPF pass can appear alongside an SPF alignment failure. Confirm whether Brevo passes through DKIM and whether a branded Return-Path appears after setup. Aggregate reports describe authentication and receiver disposition, not inbox placement.
Illustrative DMARC monitoring recordtext
_dmarc.example.com. TXT "v=DMARC1; p=none; rua=mailto:dmarc@example.com"
Replace the example domain and reporting mailbox with values you control. If a DMARC record already exists, preserve its policy and reporting destinations rather than replacing it with this monitoring example.
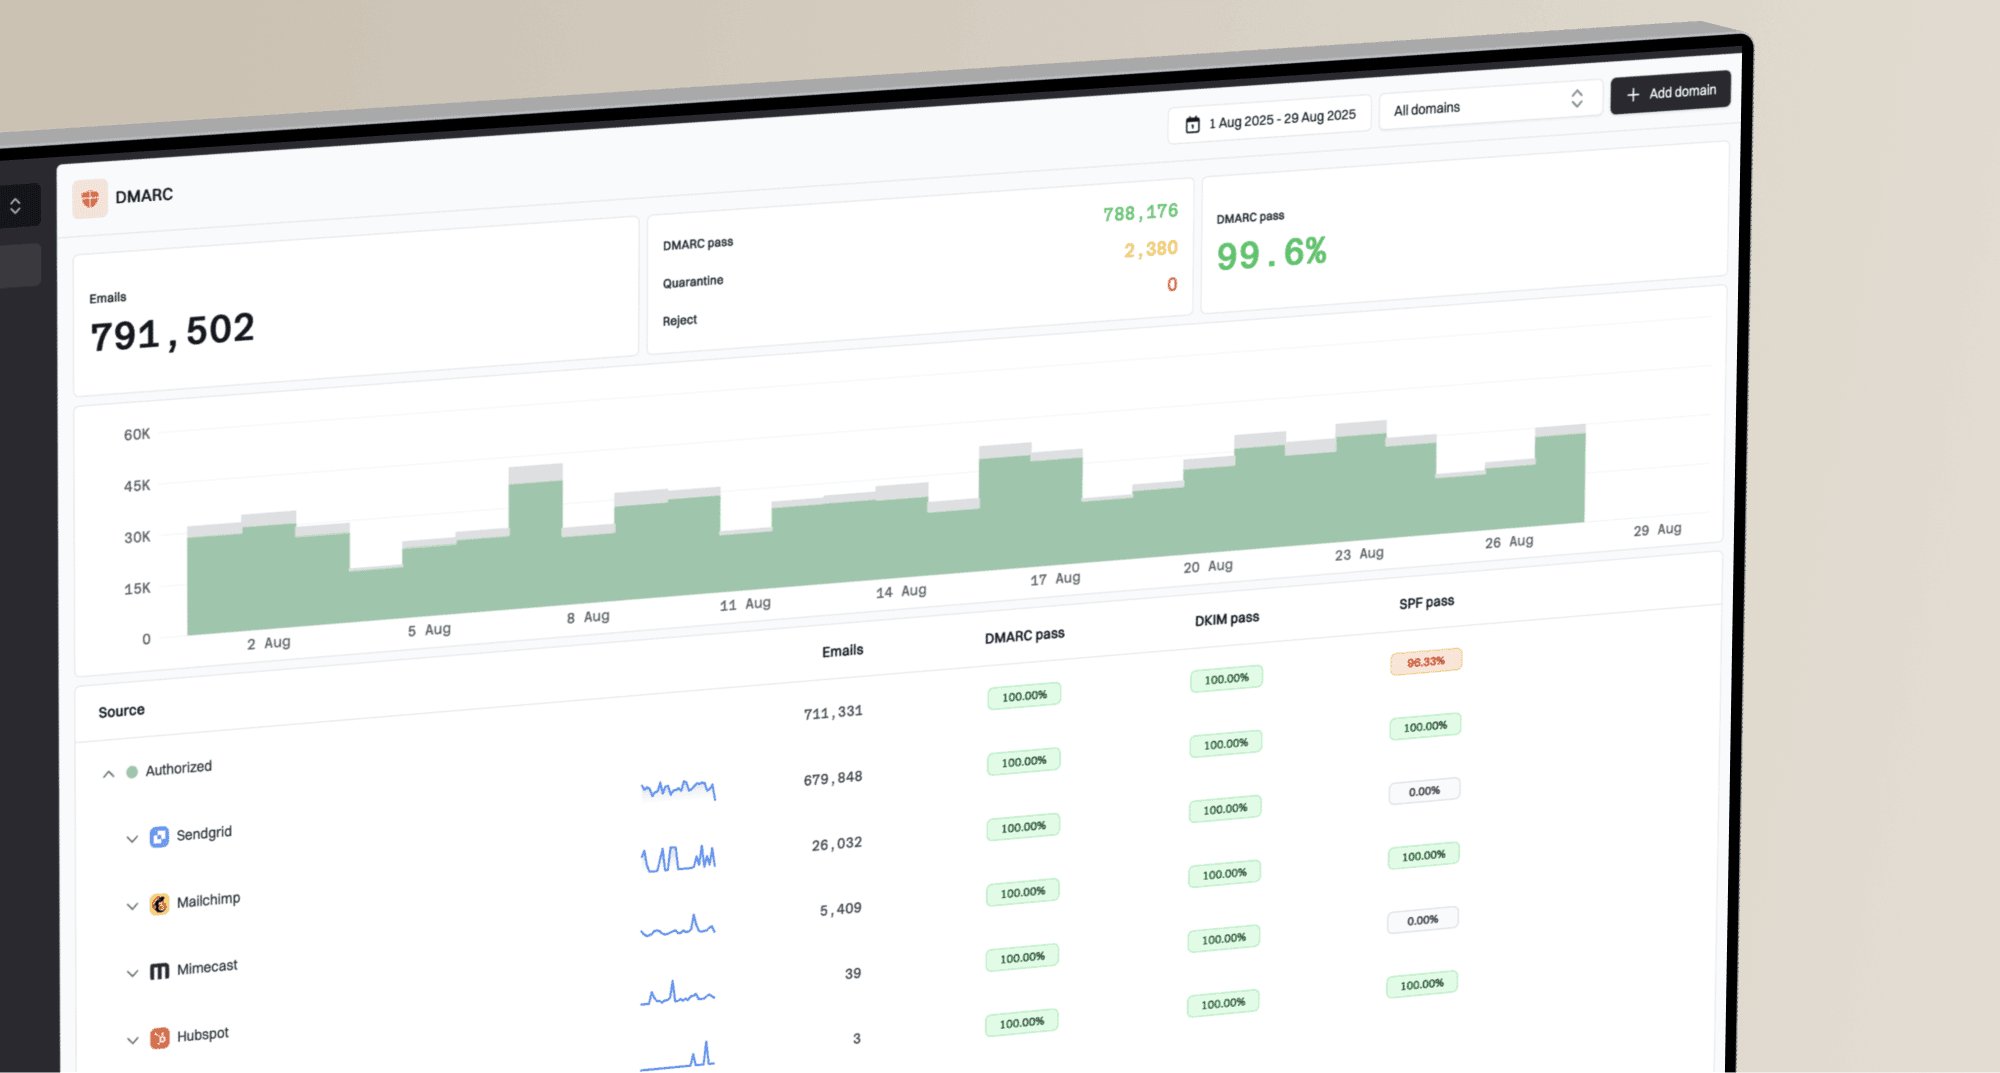
Suped is our DMARC reporting and email authentication platform. Use its source-level reports to check whether Brevo mail passes through DKIM, distinguish raw SPF results from SPF alignment, and investigate the mail streams that fail DMARC.
DMARC record detail view showing SPF, DKIM, DMARC, rDNS diagnostics, and DNS records
Your practical options
There are five realistic paths. The right one depends on whether DMARC passes today, whether the branded-subdomain option is available, whether your volume supports a dedicated IP, and whether strict SPF alignment is a policy requirement. A dedicated IP is about reputation ownership and sending control, not simply removing a warning.
|
|
|
|---|---|---|
Stay shared | DKIM and DMARC pass | Legacy SPF warning remains |
Branded subdomain | Eligible shared-IP accounts | Gradual rollout |
Fix DKIM | DMARC gaps | Needs DNS access |
Dedicated IP | Steady high volume | Warm-up required |
Move provider | Verified support for required domain matching | Migration work |
Common choices for Brevo SPF alignment issues.
For most teams, first make DKIM and DMARC routine. Authenticate the sending domain, keep DKIM stable, collect DMARC reports, and stage policy changes. Suped's product supports that work by turning raw reports into source-level issues and fix steps. When SPF complexity grows across multiple senders, Hosted SPF in Suped's product helps manage sender authorization. It does not change Brevo's Return-Path or create SPF alignment for a provider-owned envelope domain.
If Brevo is your only sender and DKIM passes cleanly, check for a branded subdomain before paying for a dedicated IP. A dedicated IP becomes reasonable when volume is large and steady, IP reputation control matters, and you have a warm-up plan. If DMARC reports show Brevo failing because DKIM is missing or broken, fix that first. If exact SPF domain matching is mandatory, verify the actual smtp.mailfrom value before choosing a dedicated IP or migrating.
When to keep Brevo on shared IPs
Do not treat missing SPF alignment as an automatic deliverability problem. Prove the authentication path first. If DKIM passes with the From domain and DMARC passes in real mailbox headers and aggregate reports, investigate reputation and recipient-specific responses before attributing poor placement to SPF alignment.
Validate DKIM, collect DMARC reports, and check for Brevo's branded-subdomain option. Test both marketing and transactional mail at mailbox providers your audience uses, and compare SMTP rejection codes, deferrals, and spam placement. Gmail's Promotions tab is part of the inbox, not the spam folder. Small test samples do not predict every recipient's result; use them alongside campaign outcomes.
For a sender with low or inconsistent volume, stay on shared IPs when DKIM and DMARC pass. Enable a branded subdomain if available and monitor the result. Consider dedicated-IP infrastructure when steady volume and reputation control justify the warm-up work.
Frequently asked questions
No. A message passes DMARC when either SPF or DKIM passes and matches the visible From domain under the configured mode. On a legacy shared-IP setup, domain-matched DKIM usually supplies that pass. Full DMARC participation under RFC 9989 also calls for SPF and DKIM alignment.
Publish only the DNS records Brevo shows for your account and sending setup. Legacy authentication does not require SPF or MX records. The new branded-subdomain setup uses Brevo-supplied CNAME or delegated DNS records. If an SPF TXT record is required, use the exact hostname shown, keep one SPF record there, and stay within the 10 DNS-querying-term limit.
Use the qualifier Brevo supplies for its managed or dedicated-IP configuration. For a record you manage, ~all gives a softfail for unlisted IPs; -all gives a fail. Inventory all legitimate senders before tightening the policy. Neither qualifier changes the Return-Path domain or fixes SPF alignment.
Yes, when the new Brevo domain setup is available. A passing SPF result for a branded Return-Path under the same organizational domain as the From address satisfies relaxed SPF alignment. Check the received headers after setup because strict aspf=s still requires an exact domain match.
Usually no. Low or inconsistent volume often struggles to build stable dedicated-IP reputation. Use shared IPs, stable DKIM, DMARC reporting, and a branded subdomain if available. Choose a dedicated IP when steady volume and direct IP reputation control justify the warm-up work.
Monitor DKIM pass rates, DMARC pass rates, source identification, complaint trends, bounce patterns, and blocklist or blacklist status for domains and IPs. Recheck smtp.mailfrom after any branded-subdomain change.