
How to set up DMARC/DKIM/SPF for Web Hosting Romania

To set up DMARC/DKIM/SPF for Web Hosting Romania, open cPanel, publish the SPF value recommended for your hosting account, enable DKIM signing for your domain, and add a DMARC TXT record at _dmarc. Start a new DMARC deployment with p=none, then verify real messages before enforcing p=reject.
I use the cPanel workflow for Web Hosting Romania's Claus Web hosting infrastructure. A VPS without cPanel needs equivalent mail server configuration. If your domain already has p=quarantine or p=reject, keep that policy while fixing authentication.
Add your domain
I start with the cPanel login supplied in the hosting welcome email. If your sending domain is already listed under Domains, use that entry and skip domain creation.
- Add the domain: Open Domains > Create a New Domain. Enter your actual domain, such as example.com. For a separate website, clear Share document root, check the document root, and click Submit.
- Confirm provisioning: Check that the domain appears under Domains and in the domain selector under Email Accounts. Ask hosting support to provision it if your plan has no domain creation option.
- Locate authoritative DNS: Check the domain's current nameservers. Edit authentication records there. Use cPanel's Zone Editor only when that DNS zone is authoritative; keep existing nameservers unless a hosting migration requires a change.
- Create the sender: Open Email Accounts > Create, select the domain, set the mailbox name and password, and click Create. Open Connect Devices to obtain the authenticated SMTP hostname and TLS settings.
Claus Web's public instructions use Domains > Create a New Domain for additional domains. Domain provisioning and access to its authoritative DNS are the prerequisites here; do not invent a separate email verification TXT record.
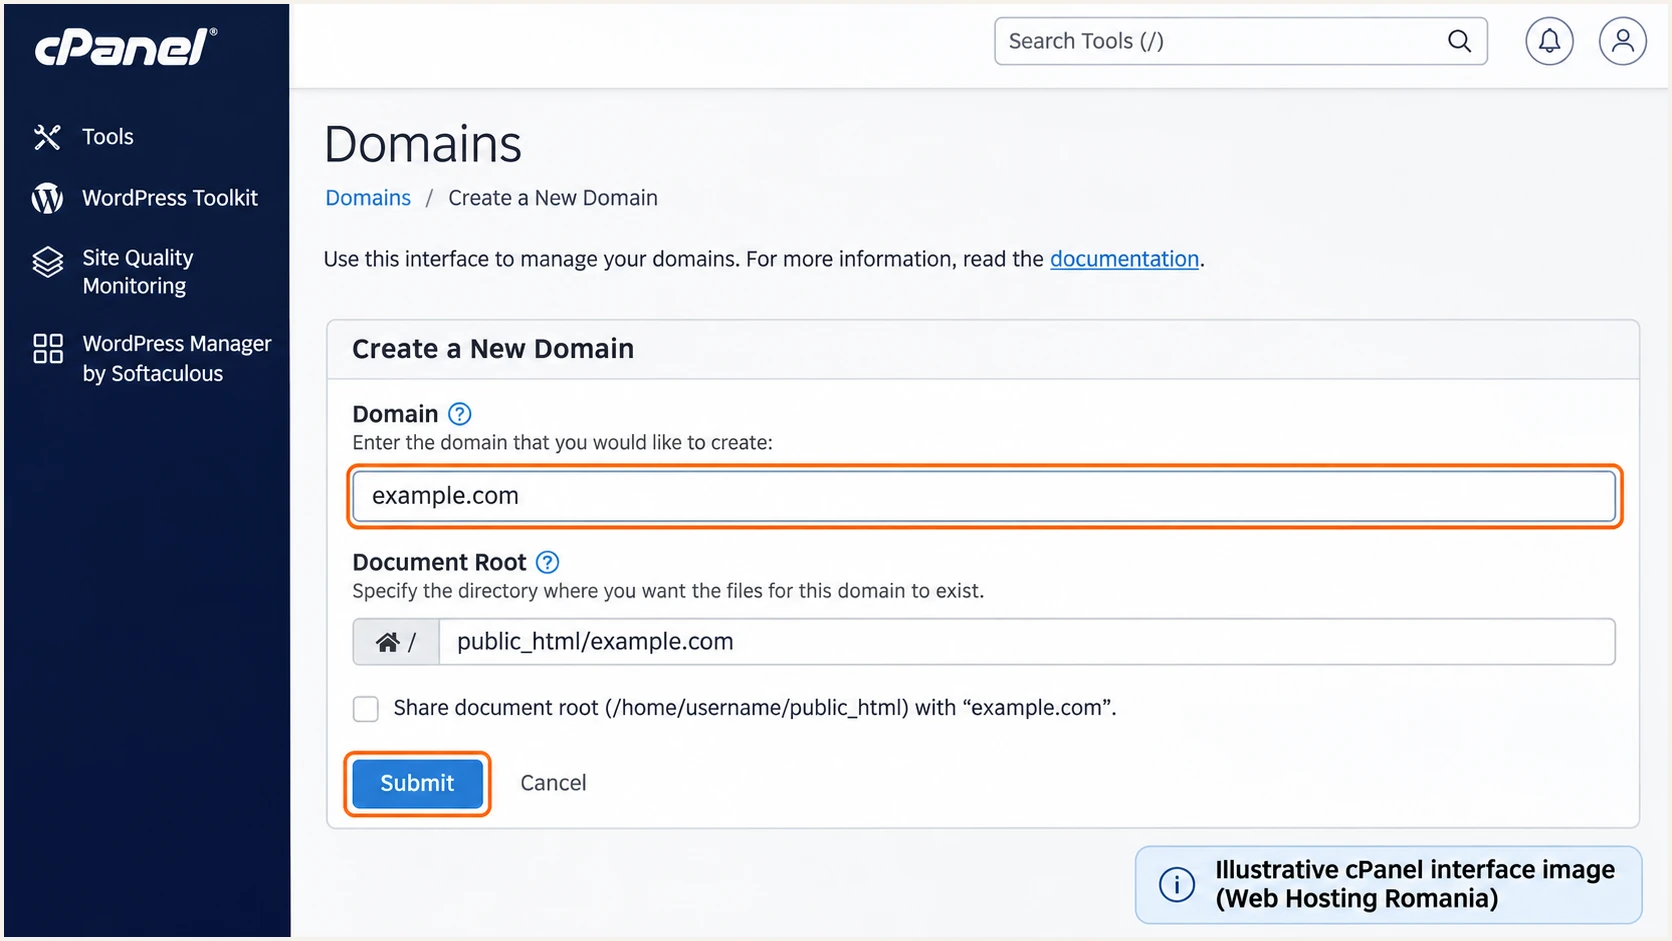
Illustrated cPanel screen for adding a domain to Web Hosting Romania.
For website mail, I use a mailbox on the same domain as the visible From address. Copy the SMTP settings shown in Connect Devices, including the full email address as the username.
Set up SPF
Web Hosting Romania supports Return-Path alignment. I configure SPF for the domain actually used in SMTP MAIL FROM, which appears in the delivered Return-Path header. The account's recommended SPF value is the starting point, rather than a guessed provider-wide record.
- Read the recommendation: Open Email > Email Deliverability, find your domain, and click Manage. Copy the Name and Value under Suggested SPF (TXT) Record. If no recommendation is available, request the account's outbound SPF requirements from hosting support.
- Merge existing senders: Inspect the existing TXT record beginning v=spf1. Add the required hosting mechanisms to that record, retaining other authorized senders and one final all mechanism. Publish only one SPF record at each name.
- Publish the TXT value: For authoritative cPanel DNS, open Domains > Zone Editor > Manage. Edit the existing SPF TXT entry, or choose Add Record > TXT when none exists. Save the combined value. For external DNS, make the same change there.
- Check the envelope sender: Configure the application to submit through the mailbox's authenticated SMTP service and use your domain in MAIL FROM. A visible From address alone does not set the envelope sender. Ask support to check any server-side rewriting.
Keep SPF within the limit of 10 DNS-querying terms during evaluation, including nested includes. Extra authorized IP addresses do not automatically fix an incorrect MAIL FROM domain.
Enter the actual MAIL FROM domain in the SPF checker. If it differs from your visible From domain, check both the SPF result and domain alignment before treating the configuration as complete.
SPF checker
Find SPF syntax issues, lookup limits, and weak records.
?/16tests passed
SPF alignment requires the authenticated MAIL FROM domain to match the visible From domain, or share its organizational domain under relaxed alignment. A passing SPF check for a provider-owned domain does not authenticate your From domain for DMARC.
If a particular sending route still uses a provider-owned Return-Path, adding more SPF entries to your domain will not change that identity. Fix the route with hosting support; passing DKIM with domain alignment can still give that message a DMARC pass.
Set up DKIM
I return to Email > Email Deliverability > Manage for the sending domain. DKIM needs a server-held private key and its matching public DNS record.
- Generate the key: Inspect the DKIM section. If no local key exists and Generate Local DKIM Key is available, use it. If DKIM controls are unavailable, ask Web Hosting Romania support to enable domain signing.
- Copy the public record: Copy the Name and Value shown under Suggested DKIM (TXT) Record. Use the selector supplied by the server. Do not replace its public key with an independently generated key.
- Publish authoritative DNS: Install or repair the suggested record when cPanel controls authoritative DNS. Otherwise, copy the TXT name and complete public value to your DNS provider. Multiple quoted DNS strings must concatenate into the original key.
- Confirm actual signing: Send a fresh message through the hosted mailbox and through the website. Inspect DKIM-Signature for d= and s=, then confirm the receiver reports dkim=pass with the signing domain matching your From domain.
The selector is often default in cPanel, but I use the value in the actual signature and server recommendation. The lookup name is the selector followed by ._domainkey. and the signing domain. Never publish the private key.
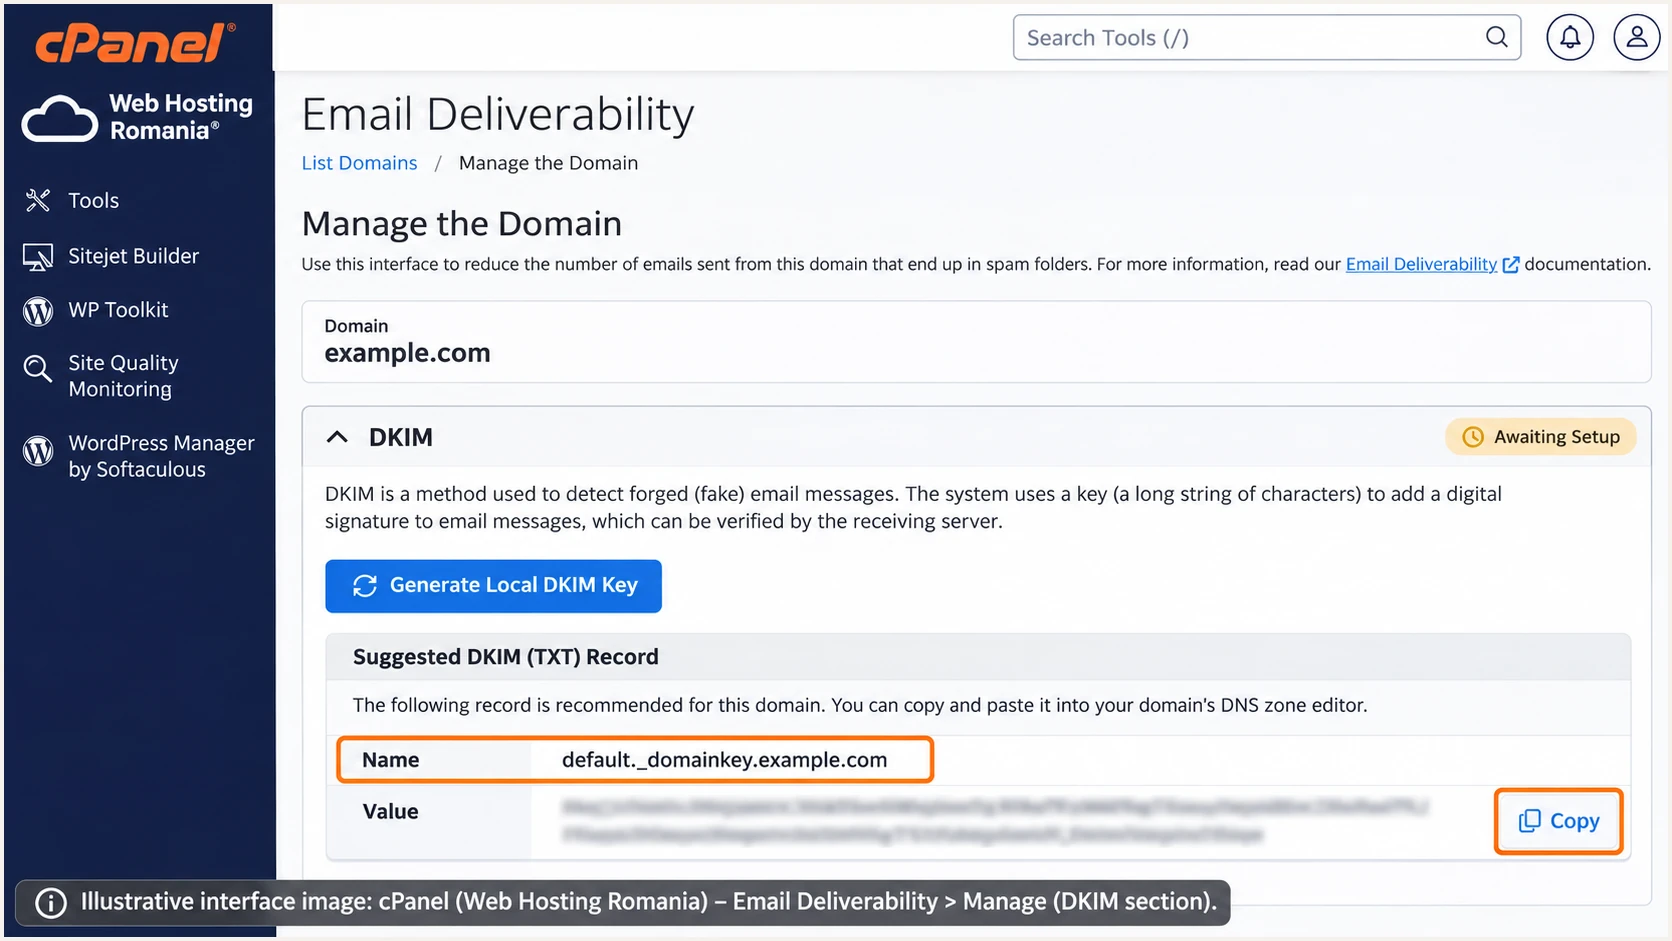
Illustrated cPanel DKIM record and selector controls.
A public DKIM key in DNS does not prove that an application signs its messages. I test the website's actual form or transactional email, because a PHP mail route can behave differently from authenticated SMTP.
For a consistent path, configure the application with the mailbox's Connect Devices settings and retest. Keep the visitor's address in Reply-To when sending contact form notifications, with your own domain in From.
Your domain in Return-Path
Configure SPF for that domain and enable domain DKIM signing. This is the target setup for Web Hosting Romania.
- SPF: Confirm the actual outbound IP is authorized and SPF alignment passes.
- DKIM: Confirm a valid signature with domain alignment on each sending route.
Provider domain in Return-Path
SPF can pass for the provider while SPF alignment fails for your From domain.
- DMARC: A valid DKIM signature with domain alignment is sufficient for a message to pass.
- Repair: Request the supported Return-Path configuration rather than repeatedly editing unrelated SPF records.
Set up DMARC
I publish DMARC on the domain used in the visible From address. For a new deployment, p=none collects evidence while sending routes are checked. Preserve an existing quarantine or reject policy.
- Prepare reporting: Create a working report mailbox on your domain, or use an authorized aggregate reporting destination. Replace the example address below with that destination.
- Build the record: Use the DMARC record generator and retain relaxed alignment initially. Keep any existing reporting destinations that your team still needs.
- Save one TXT record: Open authoritative DNS. In cPanel, use Zone Editor > Manage > Add Record > TXT. Set Name to _dmarc.example.com., retain a suitable TTL, enter the value below, and save. Edit an existing DMARC entry instead of adding a duplicate.
For a new policy, use this starting record. The example domain and report mailbox must be replaced with values you control before publishing.
DMARC TXT value at _dmarc.example.comtext
v=DMARC1; p=none; rua=mailto:dmarc@example.com
The p=none policy requests no DMARC-based quarantine or rejection. It does not stop domain impersonation by itself. Messages still need a passing SPF or DKIM result with domain alignment to pass DMARC.
The rua address receives aggregate reports, usually as XML attachments. A reporting destination on another domain needs external reporting authorization; use the destination's supplied configuration.
DMARC checker
Look up a domain's DMARC record and catch policy issues.
?/7tests passed
Check the public record for the visible From domain. Confirm that the lookup returns a single DMARC policy with the intended reporting address, and check any explicit subdomain policy separately.
In the cPanel editor, confirm the saved Name is _dmarc.example.com. Some DNS interfaces append the domain automatically, so inspect the final name to avoid a duplicated domain suffix.
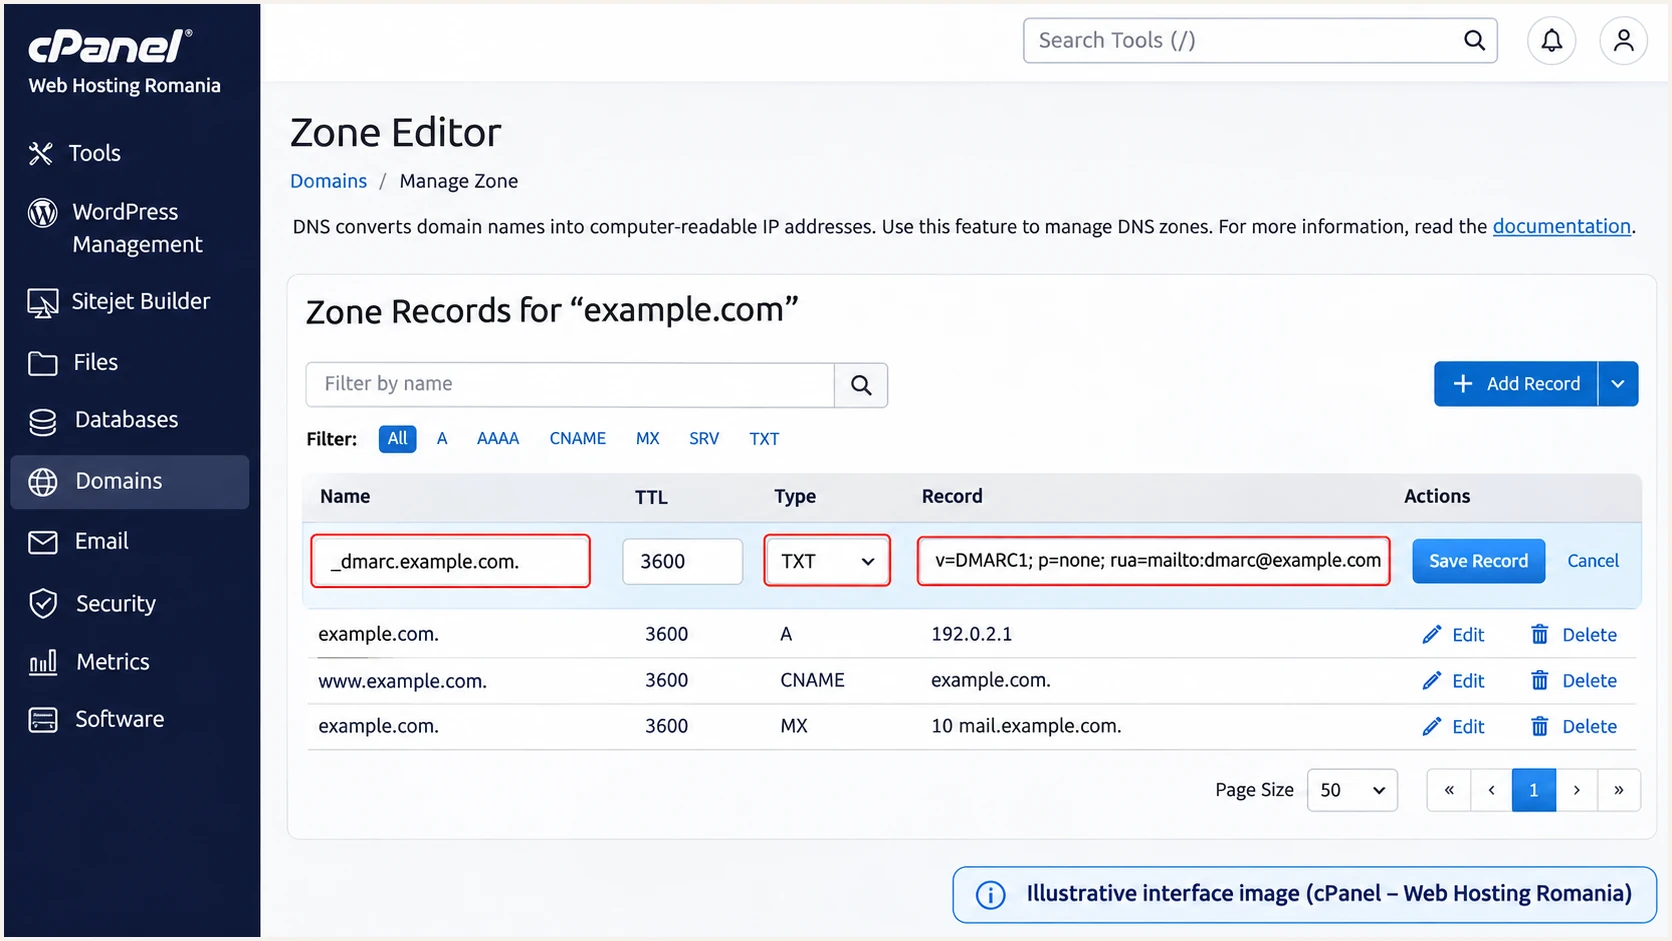
Illustrated cPanel Zone Editor with a monitoring DMARC TXT record.
Verify and troubleshoot
I verify public DNS first, then send fresh messages through every production route. A green DNS status in cPanel cannot prove that the website is using the intended server or signing domain.
- Test both routes: Send one message from the hosted mailbox and another from the actual website workflow. Include a contact form notification and an order confirmation if those routes use different application settings.
- Inspect receiver results: Read the receiving server's Authentication-Results. Confirm spf=pass for the expected MAIL FROM domain, dkim=pass for your signing domain, and dmarc=pass for the visible From domain.
- Check alignment: Compare From with Return-Path and the DKIM d= value. If SPF alignment fails but DKIM passes with domain alignment, the message can still pass DMARC.
- Escalate server faults: For missing signatures, unexpected outbound IPs, or PTR problems, give hosting support the raw message headers and sending time. The IP owner manages reverse DNS; a PTR entry in your normal domain zone will not fix it.
The email tester is the quickest configuration check: send a message to the address shown by the widget using your real Web Hosting Romania mailbox or application. It returns a diagnosis of the received message.
Email tester
Send a real email to this address. Suped shows a results button when the test is ready.
?/43tests passed
Retest after the previous DNS TTL has expired and confirm that authoritative DNS and public lookups agree. Authentication-Results on an older message will not update when DNS changes.
Use the symptom below to choose the next check. For application-only failures, compare a passing mailbox message with the failing website message before changing DNS again.
|
|
|
|---|---|---|
SPF permerror | Duplicate records; lookup limit | Merge SPF; count lookups |
DKIM none | Unsigned application mail | Check authenticated SMTP |
DKIM fail | Wrong key; message changed | Check selector and message |
DMARC fail | No authenticated domain match | Compare From and identities |
PTR error | Outbound IP reverse DNS | Contact hosting support |
Common authentication failures and the next check.
A DMARC pass confirms domain authentication, not inbox placement. If authentication passes but delivery fails, inspect the SMTP rejection and ask the host about the sending IP's blocklist status (blacklist status).
Get alerted when it breaks
I use Suped's DMARC monitoring to track Web Hosting Romania alongside the domain's other senders. Our platform groups report data by source and gives authentication issues specific steps to fix.
- Route aggregate reports: Set the existing DMARC record's rua value to the reporting address supplied by Suped. Preserve the current enforcement policy and any other required recipients.
- Verify sending sources: Review the source table and match Web Hosting Romania traffic to known sending IPs and test headers before marking a source as verified. Review unexpected sources separately.
- Enable notifications: Enable Issues detected and Sending sources need verification notifications. Turn on DMARC summary emails for ongoing review.
- Investigate the failure: Open the affected records and inspect the SPF, DKIM, and rDNS diagnostics. Apply the DNS or application fix, send another test, and check subsequent reports for recovery.
Suped's DNS history helps connect failures with a record edit. Its blocklist monitoring adds blacklist context when a shared sending IP has delivery problems despite passing authentication.
Report timing
DMARC aggregate reports are delayed, commonly arriving a day or two after sending. Suped's notifications depend on the data received; they are not an instant alert for every message or an SMTP outage monitor.
I keep notifications enabled after migrations and mailbox changes. A new application or a hosting IP change is enough to invalidate an otherwise working setup.
Secure your domain with p=reject
I move to p=reject after every legitimate sending route has reliable DKIM authentication with domain alignment, and SPF is correct wherever supported. The decision depends on observed traffic and tested workflows.
- Cover a full sending cycle: Review normal mail and less frequent jobs, including scheduled invoices. Test low-volume senders that have not appeared in aggregate reports.
- Fix known senders: Use Suped's source table and record detail view to resolve failures on verified sources. Judge legitimate sender health separately from unauthorized traffic; an overall pass rate can hide a broken website form.
- Test indirect delivery: Check forwarding paths where relevant. SPF commonly fails after forwarding, so keep working DKIM signing and investigate changes that break signatures.
- Stage enforcement: For a new deployment, move to p=quarantine, review reports and delivery failures, then move to p=reject. Keep relaxed alignment unless a documented requirement calls for strict matching.
- Keep policy control: Use Suped's Hosted DMARC policy controls when hosted DNS delegation is configured, or edit the existing authoritative TXT record. Retain reporting and review subdomain policies before enforcement.
Suped's monitoring and issue diagnostics provide the evidence for each policy change. Hosted DMARC manages the published policy; the hosting server still needs correct signing and sender configuration.
Final DMARC TXT value after legitimate senders are verifiedtext
v=DMARC1; p=reject; rua=mailto:dmarc@example.com
Replace the example reporting address with your working destination. A reject policy requests rejection of messages that fail DMARC, subject to the receiver's handling decisions.
I keep reports and source notifications active under p=reject so new website workflows are checked before they become delivery incidents.
Frequency asked questions
The romania-webhosting.com hostname suffix is associated with Web Hosting Romania and Claus Web hosting infrastructure. Shared hosting and resellers use this infrastructure, so rDNS alone does not identify an individual customer or prove that a message is authorized. Compare the actual sending IP with your hosting account and inspect authentication results.
A message passes DMARC when either SPF or DKIM passes with domain alignment. Configure both for Web Hosting Romania because it supports Return-Path alignment, and keep DKIM working before enforcing p=reject. A provider-owned Return-Path does not give your From domain SPF alignment.
The website can use a different envelope sender, an unsigned PHP mail path, or another SMTP server. Configure authenticated SMTP using the hosted mailbox's Connect Devices settings, keep your domain in From, and test the actual website workflow. Ask support to inspect server signing if DKIM remains absent.
Publish SPF, DKIM, and DMARC in the authoritative DNS zone at your current DNS provider. Copy the server-specific SPF and DKIM recommendations out of cPanel. Editing a non-authoritative cPanel zone alone will not change public DNS.
Read s= in DKIM-Signature on a fresh message and d= for the signing domain. Query that selector under _domainkey at the signing domain, then compare it with cPanel's recommended Name and public key. Do not assume default if the actual signature uses another selector.
Allow for DNS caching and the receiving provider's reporting schedule. Aggregate reports commonly arrive within a day or two after messages are received, and some receivers do not report. Use the email tester for immediate checks on a newly sent message while waiting for aggregate data.




