
How to set up DMARC/DKIM/SPF for Telenet

To set up authentication for a custom domain sending through Telenet, publish the SPF authorization for your sending service, enable DKIM signing if that service supports your domain, and add a DMARC TXT record at _dmarc. Start with p=none unless you already enforce quarantine or reject. I verify the result with a received message, because valid DNS records alone do not prove that outgoing mail passes DMARC.
For an @telenet.be mailbox, Telenet controls the authentication records. You cannot edit them yourself. Use authenticated SMTP at smtp.telenet.be on port 587 with TLS and your Telenet credentials. The DNS steps below apply to a domain you own, with separate checks for Telenet's standard SMTP service and Hosting & Cloud.
Add your domain
I first establish who controls the domain's authoritative DNS. Owning a Telenet internet connection does not automatically give you DNS access or custom-domain mail hosting.
- Confirm ownership: Use your own domain, such as example.com. If it is not provisioned in your business account, arrange registration, transfer or hosting activation with Telenet Business. There is no customer verification step for the shared telenet.be domain.
- Open MyCloud: For a domain managed through Hosting & Cloud, sign in with your Hosting & Cloud credentials. Select Domeinnamen, choose the domain, then open Resource records.
- Use the correct route: For domains ordered directly through MyTelenet, Telenet documents an online DNS change request. Choose the subject Technisch - DNS records and provide the required record names, types and values.
- Verify control: Check the public NS records and confirm that changes are being made at the authoritative DNS service. Domain registration, DNS hosting and outbound email are separate services.
Telenet's support articles 'DNS-instellingen aanpassen via MyCloud' and 'DNS-instellingen aanpassen voor Business' document these two management routes. I keep a copy of the existing records before requesting changes.
The MyCloud navigation illustration below shows where to locate the domain's records. It does not imply that every Telenet account has this control panel.
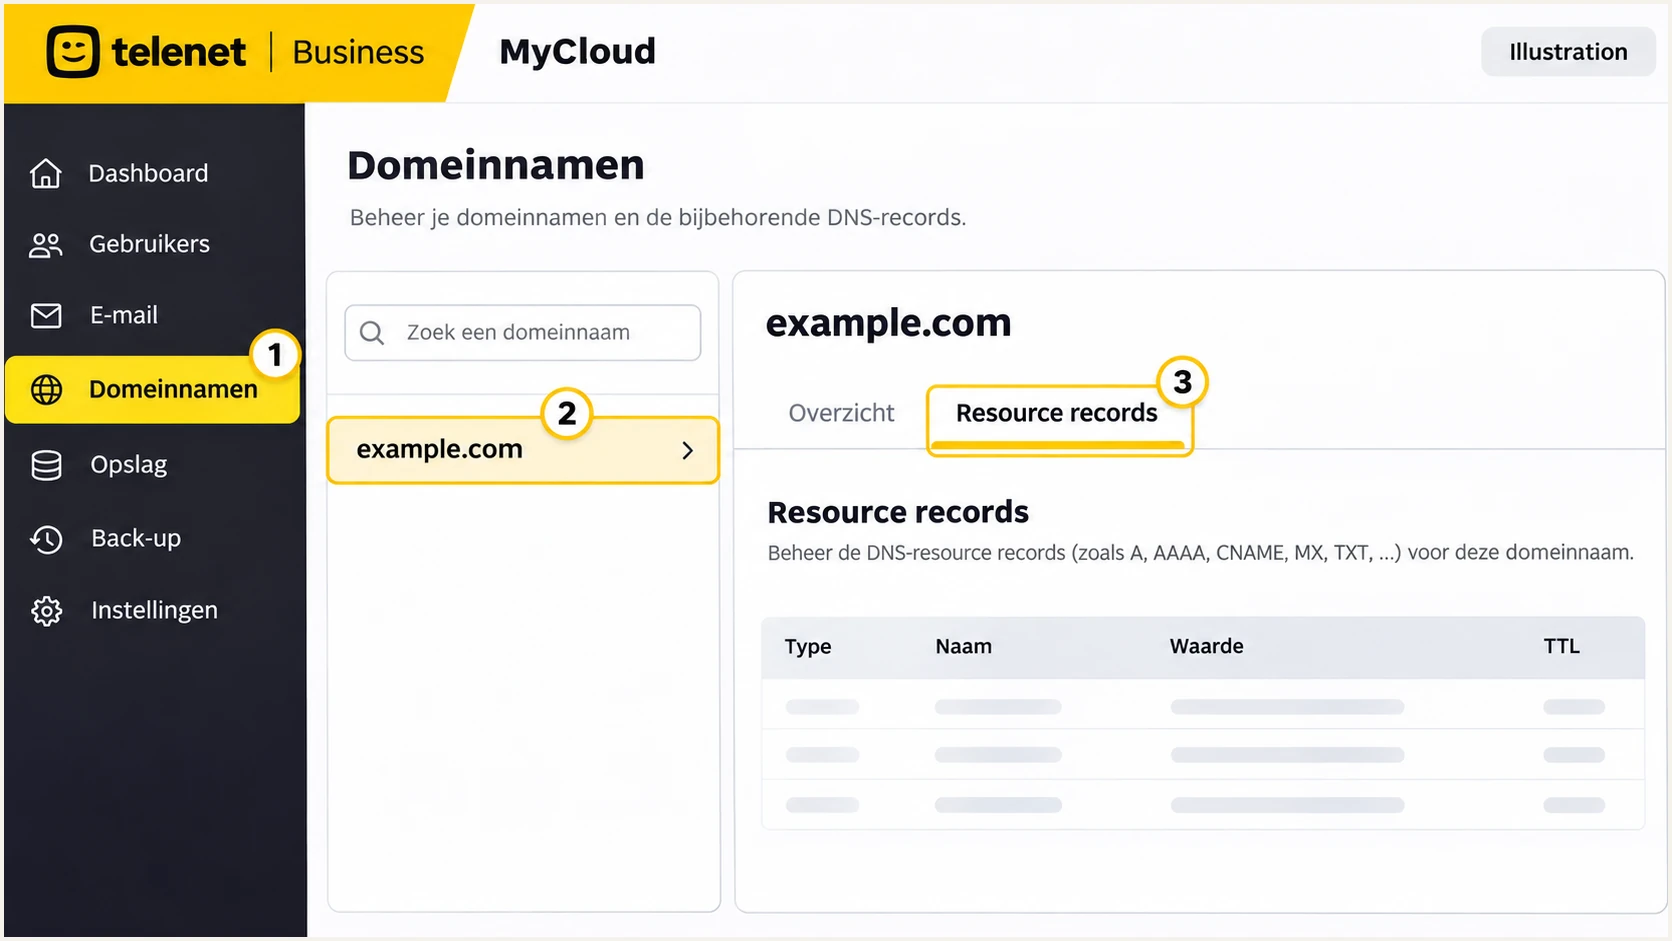
Illustrated MyCloud path: Domeinnamen, select your domain, then Resource records.
Check that the selected zone is active. If its nameservers point elsewhere, publish authentication records there instead of editing an unused Telenet zone.
Keep existing MX records unless you are also changing the inbound mail service. SPF, DKIM and DMARC setup does not itself require an MX migration.
Set up SPF
SPF authorizes the servers sending with your envelope sender domain, which normally appears in Return-Path after delivery. I check that domain before changing the SPF record for the visible From address.
- Identify the service: Confirm whether the message leaves through standard Telenet SMTP or a Hosting & Cloud mail service. Ask Telenet for the SPF authorization for that exact service; these are not interchangeable pools.
- Confirm the envelope: For custom-domain SPF alignment, the envelope sender must use your From domain or a subdomain under the same organizational domain with relaxed alignment. An SMTP login address does not establish this.
- Merge authorization: Edit the single TXT record beginning v=spf1 at the envelope sender domain. Keep authorization for other legitimate senders, insert the confirmed Telenet mechanism before the final all mechanism, and avoid a second SPF record.
- Check the limit: Keep evaluation within SPF's limit of 10 DNS-querying terms, including nested includes and redirects. Do not authorize inbound MX servers or your home IP unless they actually send this mail.
If Telenet confirms that your service uses the standard telenet.be SPF policy, the following is a Telenet-only example. The include is conditional on that confirmation; it is not a universal Hosting & Cloud record. Keep existing sender authorizations when adapting it.
SPF example for a confirmed standard Telenet SMTP pooltext
Name: example.com
Type: TXT
Value: v=spf1 include:telenet.be ~all
Publish the value at the domain used in the envelope sender. Use the DNS editor's root-domain convention when applicable, and preserve your existing final all policy unless you deliberately change it.
Run the SPF check below against that envelope sender domain. It checks DNS syntax and lookup limits; the later email test checks whether your actual outgoing server is authorized.
SPF checker
Find SPF syntax issues, lookup limits, and weak records.
?/16tests passed
After saving, wait for the previous DNS TTL to expire and test a new message. A successful SPF lookup is not evidence that the From domain matches the authenticated domain.
If your particular sending path uses a provider-owned Return-Path and cannot change it, editing SPF at your From domain will not fix that mismatch. Expect SPF alignment errors in that case, and require passing DKIM with a signing domain that matches your From domain. If neither method matches, DMARC fails.
Set up DKIM
DKIM must be enabled on the server that signs outgoing email. Telenet's public setup instructions do not document a universal custom-domain DKIM activation screen or selector. I request the signing configuration for the exact mail service instead of inventing DNS values.
- Request signing: For your own domain, ask Telenet Hosting & Cloud whether your service supports DKIM signing with your domain in d=. Request the selector, record type and complete TXT value or CNAME target.
- Publish exactly: In the authoritative DNS zone, add the supplied record under the supplied selector's _domainkey name. Enter a hostname target for a CNAME, or the complete public key value for a TXT record.
- Enable and retest: Have the sending service activate signing after publication. Send a fresh message and confirm a DKIM-Signature header exists; publishing a key alone does not start signing.
- Check the identity: Read d= and s= in that signature. Require dkim=pass and a d= domain that matches your visible From domain under your DMARC alignment setting.
Use the selector from the actual signature to query DNS. Replace SELECTOR and example.com below; there is no fixed selector to copy for every Telenet customer.
Look up the selector used by your received messagebash
dig +short TXT SELECTOR._domainkey.example.com
dig +short CNAME SELECTOR._domainkey.example.com
For an @telenet.be mailbox, Telenet manages the signing keys. For a custom From domain, a valid signature with d=telenet.be does not satisfy DMARC's DKIM identity requirement.
I distinguish these two outcomes before enforcing DMARC. Passing SPF with a matching envelope domain can pass DMARC without DKIM, but that leaves less resilience when mail is forwarded.
Your domain is signed
The signature passes and its d= domain matches your From domain. Keep the supplied public records published and test after key rotation.
Only Telenet is signed
A passing d=telenet.be signature covers Telenet's identity. For a custom From domain, obtain custom-domain signing or verify that SPF passes with a matching envelope domain.
If the service cannot sign your domain, ask Telenet for a supported sending configuration before relying on DKIM. A locally generated key cannot configure a server you do not control.
Set up DMARC
DMARC passes when SPF or DKIM passes and the authenticated domain matches the visible From domain under the applicable alignment rules. I add reporting before tightening a new policy.
- Keep enforcement: If your domain already uses p=quarantine or p=reject, keep that policy while adding Telenet. Do not downgrade an established policy to p=none for onboarding.
- Create the record: For a domain without DMARC, publish one TXT record at _dmarc.example.com. In a zone editor that appends the domain, enter only _dmarc as the name.
- Set reporting: Use the monitoring record below, replacing dmarc@example.com with a real reporting destination you control. The example address does not collect your reports.
- Preserve settings: Edit an existing DMARC record rather than adding a second one. Keep its reporting destinations and other intentional settings when making changes.
Initial monitoring policy for a domain without enforcementtext
Name: _dmarc.example.com
Type: TXT
Value: v=DMARC1; p=none; rua=mailto:dmarc@example.com
Use our DMARC record generator to build the record with your real reporting address. The example uses the default relaxed SPF and DKIM alignment settings.
If reports go to a different domain, ensure the reporting service has published the required external-report authorization. Then check the public record for the domain in your visible From address.
DMARC checker
Look up a domain's DMARC record and catch policy issues.
?/7tests passed
A valid lookup confirms policy publication. It does not confirm that the Telenet mail stream passes DMARC or that aggregate reports have already arrived.
I inspect the first reports and compare their authentication results with a fresh test email. Aggregate reports normally arrive on a daily schedule; not every recipient service sends them.
Monitoring does not request blocking
p=none requests monitoring rather than quarantine or rejection for DMARC failures. Receivers still apply their own filtering. Keep quarantine or reject if either is already protecting your domain.
Verify and troubleshoot
I test the production sending path, including the actual application or device. A webmail test does not verify a printer or website using different SMTP settings.
- Send a fresh test: Use the normal From address and the same SMTP connection used in production. For a standard Telenet mailbox, verify smtp.telenet.be, port 587, TLS and authentication as documented in Telenet's E-mail instellen support article.
- Inspect receiver results: Read the receiving system's Authentication-Results. Check spf=pass, dkim=pass where supported, and dmarc=pass. Compare smtp.mailfrom and header.d with header.from.
- Separate failures: A 550 Access denied response before delivery is an SMTP submission or sender-permission problem. A DNS change does not itself grant permission to submit mail through Telenet.
- Retest each path: Repeat after DNS cache expiry and after changes to the sending service. Include mobile clients and automated senders instead of checking only one successful mailbox.
The email tester below is the quickest verification path. Send a message to the address it provides using your normal Telenet configuration, then review the full diagnosis.
The test examines the delivered message, so it catches identity mismatches that a DNS-only lookup misses. Save its authentication results with the sending time when asking Telenet to investigate.
Email tester
Send a real email to this address. Suped shows a results button when the test is ready.
?/43tests passed
Fix actual authentication failures before changing DMARC policy. If SPF passes but its domain is unrelated to your From domain, it still fails DMARC's SPF identity requirement.
Use the following checks to distinguish identity problems from DNS publication problems. A passing DKIM signature with a matching signing domain is sufficient for DMARC even when SPF fails.
|
|
|
|---|---|---|
SPF failure | Envelope domain | Fix authorization |
SPF mismatch | From vs envelope | Fix sender domain |
DKIM failure | Selector and key | Fix signing or DNS |
DMARC failure | Passing identity | Match SPF or DKIM |
Telenet's support article 'Waar staat de header of koptekst van een e-mail?' documents the Webmail inspection path: right-click a received message in the inbox and choose Oorspronkelijke tekst.
Use a received copy when checking recipient authentication. A Sent-folder copy often lacks the receiving system's verdict. The illustration below shows the documented Webmail action.
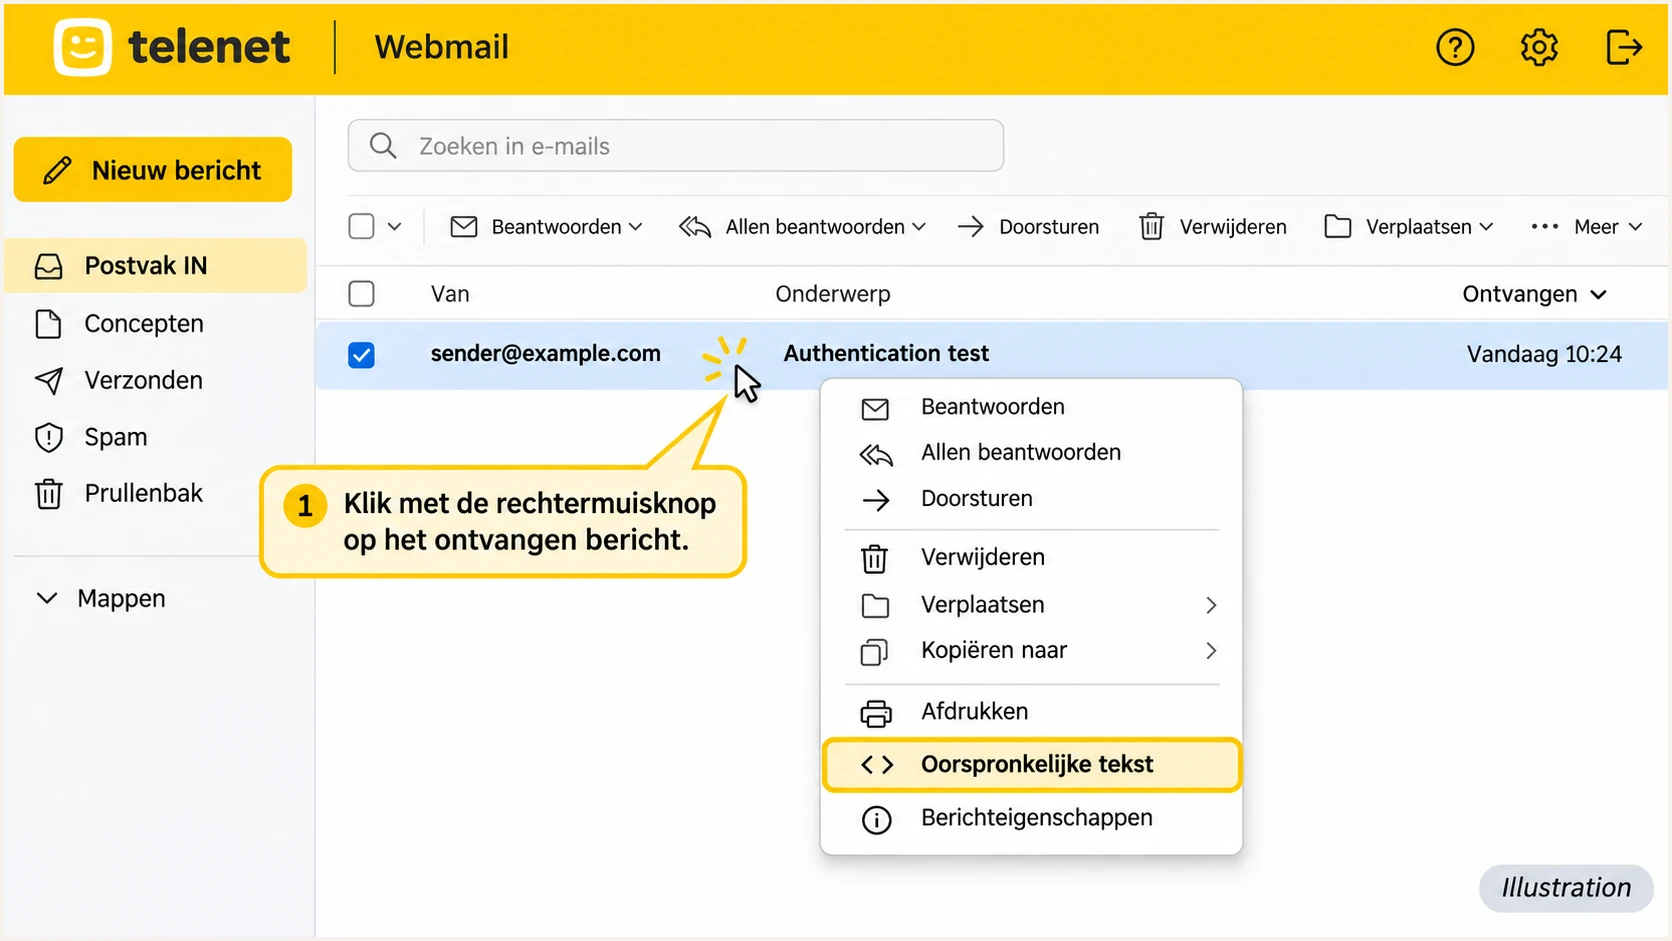
Illustrated Telenet Webmail action for opening a received message's original text.
If authentication passes but messages still go to spam, inspect the bounce response and recipient filtering. DMARC success does not guarantee inbox placement.
For failures on Telenet-managed domains or signing infrastructure, provide Telenet with the complete received headers and timestamps. Do not publish copied Telenet keys under your own domain as a workaround.
Get alerted when it breaks
Suped is our DMARC reporting and email authentication platform. I configure ongoing monitoring for Telenet traffic because a successful setup test does not detect later DNS changes or new sending paths.
- Verify the source: In Suped's source table, confirm Telenet is an authorized sender before marking it verified. Inspect its sending IPs and authentication results rather than relying on the source name alone.
- Enable notifications: Open notification settings and enable Issues detected and Sending sources need verification. Keep DMARC summary emails enabled for routine review.
- Investigate failures: Open the affected source and detail view to inspect SPF, DKIM and DMARC results. Use the issue's steps to fix, then verify a new test message after the correction.
- Check DNS history: Compare previous and current DNS values when a previously passing source starts failing. Look for removed SPF authorization or changed DKIM records.
Our DMARC monitoring connects source-level failures with specific remediation steps. This keeps the Telenet investigation tied to the envelope domain and signing identity actually reported by receivers.
I treat an alert as a reason to inspect evidence, not as proof that every message is failing. Check the affected source's volume and distinguish legitimate traffic from unauthorized use of your domain.
Alerts depend on arriving data
Suped evaluates the reports and checks it receives. DMARC aggregate reporting is usually daily, so an alert is not an instant verdict on every individual SMTP transaction. Use a new email test when you need immediate confirmation.
Secure your domain with p=reject
I move a custom domain to p=reject after every legitimate sending path has a proven DMARC pass mechanism. Telenet traffic must pass through a matching SPF envelope domain or a matching DKIM signing domain.
- Review a full cycle: Use Suped's reports across a complete business sending cycle. Include infrequent billing messages and automated devices; a quiet day is not enough evidence.
- Resolve legitimate failures: Verify authorized sources and follow Suped's issue-specific fixes. Do not add unknown IPs to SPF just to improve the overall pass rate.
- Stage enforcement: For a new deployment, move to quarantine, inspect the next reports and test critical workflows, then move to reject. Keep reject if it is already established and fix new sender failures directly.
- Check subdomains: Review explicit subdomain policies and the parent policy's inherited effect before enforcement. Keep reporting enabled and retest forwarded mail, where SPF often fails.
Suped's Hosted DMARC supports policy management in the dashboard once configured. For a Telenet-hosted DNS zone managed by support requests, that reduces repeated DNS requests during later policy changes.
For a directly published TXT policy, update the existing record to the following only after those checks pass. Replace the example reporting address and preserve other reporting destinations or settings you intentionally use.
Enforcement policy after verified sender readinesstext
Name: _dmarc.example.com
Type: TXT
Value: v=DMARC1; p=reject; rua=mailto:dmarc@example.com
After the change, verify the published policy and send fresh tests through each critical path. In Suped, continue investigating failures by verified source; unauthorized traffic is expected to fail authentication.
If a legitimate sender breaks, correct its authorization or signing setup and verify the fix. Any emergency policy relaxation should be deliberate and temporary, with a recorded owner and a retest before restoring reject.
Frequency asked questions
No. Telenet controls DNS and signing for telenet.be. Configure authenticated SMTP using Telenet's documented settings and escalate authentication failures to its support team. To control your own policy and records, use a domain you own.
Confirm the outbound service first. include:telenet.be is the example for a service confirmed to use that policy. Hosting & Cloud requires its own service-specific instructions. I do not copy an authorization solely because Telenet registered the domain or provides the internet connection.
There is no universal customer selector documented in Telenet's public setup instructions. Read s= and d= in a fresh message's DKIM-Signature. For custom-domain signing, obtain the exact selector and public DNS records from the team operating your sending service.
Yes. DKIM must pass with a signing domain that matches the visible From domain under the applicable DMARC rules. This is the required route when a sender cannot use a matching Return-Path. A passing signature for an unrelated provider domain is insufficient.
The telenet-ops.be suffix is associated with Telenet infrastructure. Publicly archived received headers include mail hosts such as albert.telenet-ops.be and andre.telenet-ops.be. I confirm the connecting IP and authentication results before treating the traffic as authorized; the hostname alone does not establish that.
Check authoritative DNS after publication, then account for the previous record's TTL and Telenet's processing time. Test with a newly sent email after the updated values are visible. Allow roughly 24-48 hours for initial aggregate reports, and verify reporting authorization if they remain absent.




