
How to set up DMARC/DKIM/SPF for Name.com

For Name.com Hosting Email, get the SPF and DKIM values in cPanel > Email Deliverability > Manage, publish them as TXT records in authoritative DNS, and add a DMARC TXT record at _dmarc. Start a new DMARC setup with p=none, then verify a real message before enforcing p=reject. Keep an existing quarantine or reject policy.
I first check that Name.com hosting actually sends the email. Registering a domain at Name.com does not make it the sender. These steps cover its cPanel hosting mail, including website applications using that mail server. A separate mailbox service supplies its own SPF and DKIM values, even when Name.com hosts the DNS.
Add your domain
I check the existing hosting domain before creating anything. If the domain already appears in cPanel, keep it and continue with authentication.
For an additional domain, use a hosting plan that supports additional domains. Adding the domain to cPanel connects it to the hosting account; public DNS and a delivered test message verify the working setup.
- Open hosting. In Name.com, select My Products, open the hosting package, and click cPanel Login on the Web Hosting Dashboard. Record the listed hosting server name for later SMTP checks.
- Add if missing. In cPanel, open Domains > Create A New Domain. Enter your domain, review its document root, and submit. Confirm it appears in the Domains list.
- Prepare the sender. For Hosting Email, create the sending mailbox under Email Accounts. Configure the website or application to use that account rather than assuming its default mail function uses the correct identity.
- Check DNS authority. Run the NS lookup below. Use Name.com DNS Management only when Name.com hosts the authoritative DNS. Otherwise, publish the records at the DNS host identified by the nameservers.
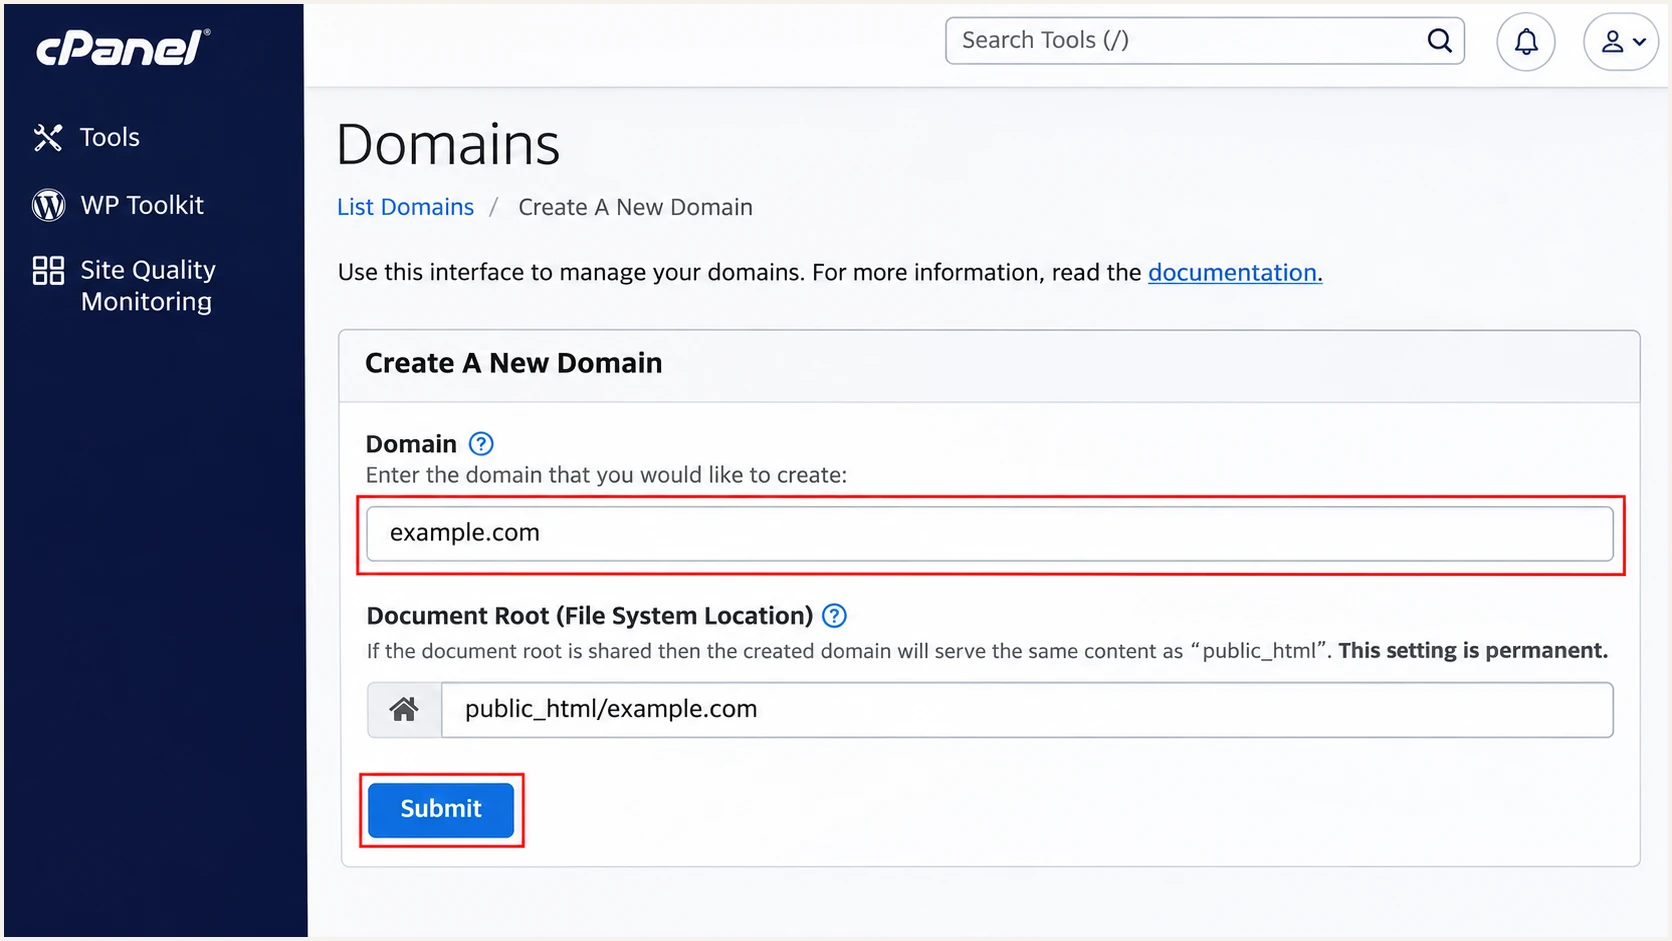
Illustrative Name.com hosting cPanel screen for adding a domain.
For a new domain receiving mail through Hosting Email, select it in the Web Hosting Dashboard DNS Management dropdown, then use DNS Templates > Hosting Email > Confirm. Review existing records first. Keep the current MX records when another service receives the mail.
I check the public nameservers and MX destination separately. MX records control incoming delivery; they do not enable DKIM signing or authorize an outgoing IP through SPF.
Check DNS authority and incoming mail routingbash
dig +short NS example.com
dig +short MX example.com
Set up SPF
I use the SPF policy suggested for the actual hosting account. Name.com documents copying this value out of cPanel; do not invent an include based on the registrar name.
SPF checks the SMTP envelope sender, which becomes the delivered Return-Path. Name.com hosting supports using your domain for this address, but a website script still needs the correct envelope-sender configuration.
- Copy SPF. Open cPanel > Email Deliverability > Manage beside the sending domain. Copy the Name and Value under Suggested "SPF" (TXT) Record.
- Open DNS. In Name.com, open My Domains, select the domain, and choose Manage DNS Records. The hosting dashboard also has DNS Management for its domains. Use Type TXT, a blank Host for the root domain, and the suggested value in Answer.
- Merge existing senders. If a TXT record already starts with v=spf1 at that name, edit it. Keep every authorized sender in one SPF policy, with one v=spf1 prefix and one final all mechanism. Preserve unrelated TXT records.
- Match the envelope. Set the application MAIL FROM to an address on your sending domain where supported. Check the received Return-Path. If it uses a subdomain, publish SPF at that subdomain and authorize the actual outbound server there.
Use the SPF checker on the envelope domain, not automatically on the visible From domain. Check syntax and the recursive lookup count. SPF permits at most 10 DNS-querying mechanisms and modifiers during evaluation.
For a root-domain policy in Name.com, leave Host blank, set TTL to 300 unless your DNS policy requires another value, and save the record. For a subdomain policy, use only that subdomain label in Host.
SPF checker
Find SPF syntax issues, lookup limits, and weak records.
?/16tests passed
I expect SPF to pass for the actual outbound IP and the envelope domain to match the visible From domain under the DMARC matching mode. With the default relaxed mode, a bounce subdomain under the same organizational domain is sufficient.
The syntax example below combines two authorized IPs into one policy. Both IPs are reserved documentation addresses. Replace them with values confirmed for your sending systems; do not publish this example unchanged.
Replace the example IPs
SPF merge example using documentation IPs onlytext
v=spf1 ip4:192.0.2.10 ip4:198.51.100.20 ~all
Set up DKIM
I use the public DKIM key generated by the hosting server. A separately generated key will not work unless the server signs with its matching private key.
For Name.com Hosting Email, the documented selector is default. Check the Name displayed in your account and the selector on a live message before publishing it.
- Get the key. Open cPanel > Email Deliverability > Manage for the domain. In the DKIM section, copy the suggested public TXT Name and Value. If no local key exists and Generate Local DKIM Key is available, generate it there.
- Publish the key. In authoritative DNS, add the supplied TXT record. For the documented default selector in Name.com, Host is default._domainkey. Paste the complete public value beginning v=DKIM1 into Answer. Do not append the domain twice.
- Protect signing. Publish the public key only. Keep other active selectors. If the same selector already has a record, confirm which server signs with it before replacing its key.
- Test each route. Send a new mailbox message and a separate website-generated message. Check DKIM-Signature for the signing domain and selector, then confirm the receiving server reports dkim=pass for your domain.
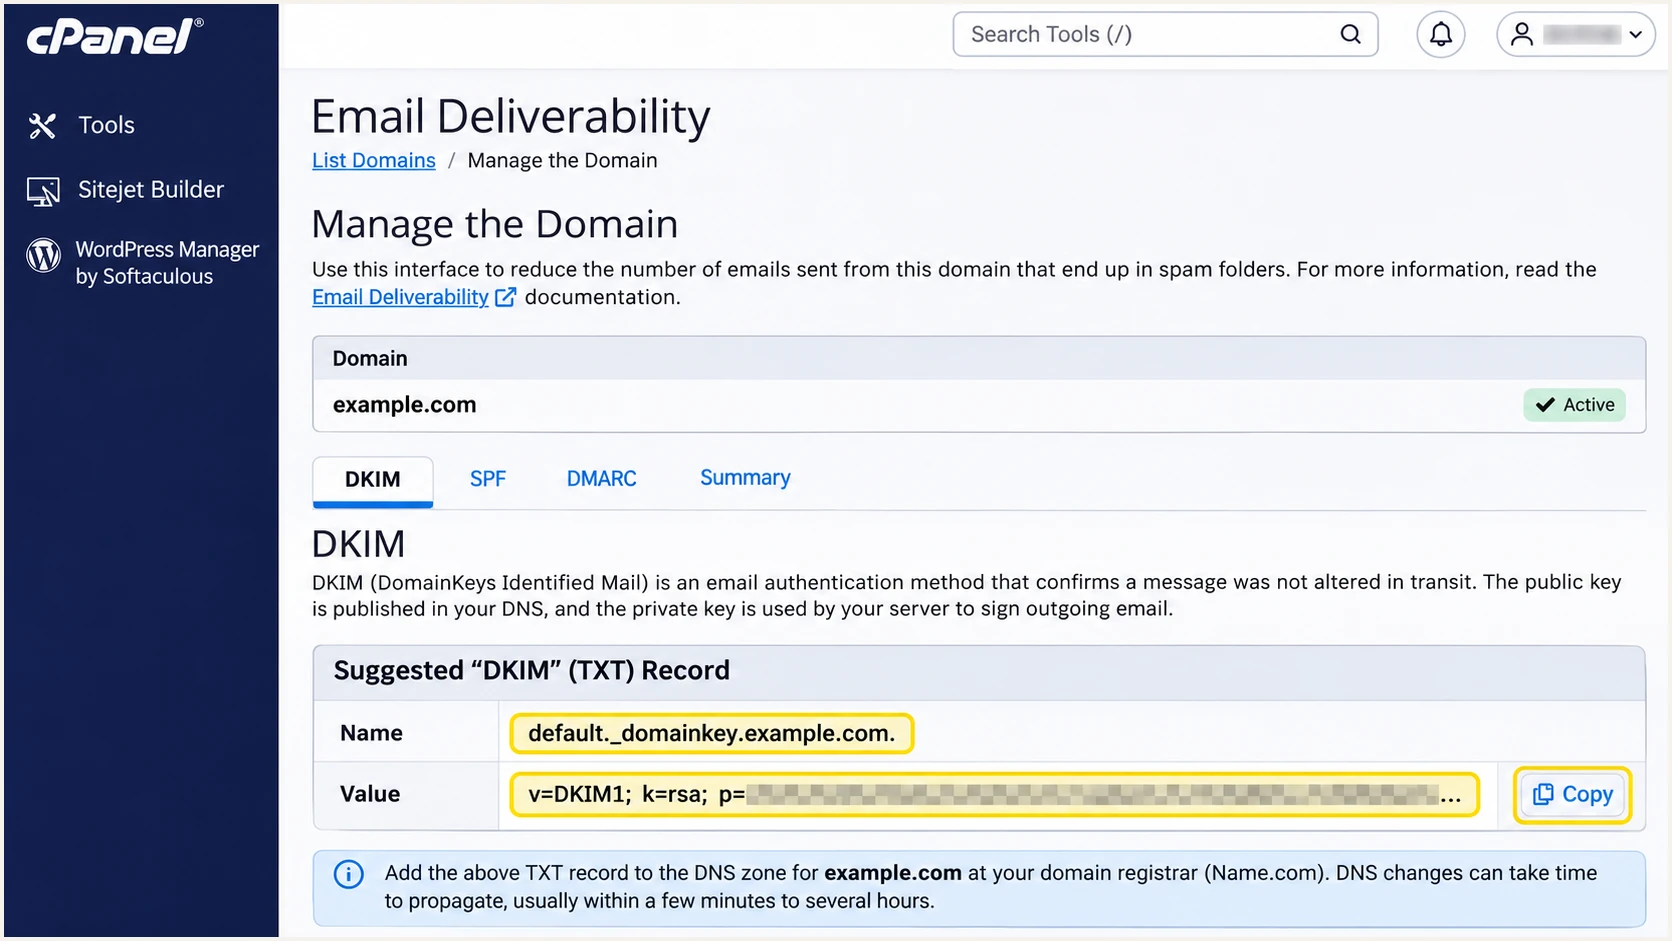
Illustrative cPanel DKIM view showing the public record name and Copy control.
Name.com explicitly warns that "Install the suggested record" is not functional in its documented hosting workflow. Copying the values into authoritative DNS is the required publishing step; clicking that button is not confirmation.
A valid DNS key does not prove that a website signs mail. If webmail passes but an application has dkim=none, route the application through authenticated hosting SMTP or ask Name.com to investigate signing for that application path.
SPF checks the envelope
A passing SPF result authenticates the envelope domain against the sending IP. DMARC also requires that domain to match the visible From domain under its matching mode.
DKIM checks the signature
A passing DKIM result authenticates a signing domain and message signature. DMARC passes when at least one valid signature has a signing domain that matches the visible From domain under its matching mode.
Set up DMARC
For a new setup, I publish the monitoring policy below. If the domain already has p=quarantine or p=reject, keep that policy and repair authentication without weakening enforcement.
The example uses dmarc@example.com. Replace it with a real aggregate-report destination you control or the address assigned by your reporting service. An ordinary mailbox receives XML reports; it does not automatically turn them into a monitoring dashboard.
- Prepare the policy. Use the DMARC record generator if you need help building the record. For an initial monitoring policy, use the exact syntax shown below with your reporting address.
- Publish one record. In Name.com > My Domains > your domain > Manage DNS Records, choose TXT. Enter _dmarc in Host and the policy in Answer. Use TTL 300 and click Add Record. Edit an existing DMARC record instead of creating a second one.
- Authorize reports. Confirm the reporting destination accepts aggregate reports. When reports go to another domain, follow that recipient's external-report authorization instructions. The receiving domain publishes that authorization.
- Check the name. Verify the public record is at _dmarc.example.com, not at the root or at a name with example.com repeated. For mail using a From subdomain, check its applicable DMARC policy too.
Initial DMARC TXT valuetext
v=DMARC1; p=none; rua=mailto:dmarc@example.com
The p=none policy requests reporting without asking receivers to quarantine or reject messages because they fail DMARC. It does not itself prevent domain spoofing.
In Name.com, the domain suffix is added to the Host label. Enter only _dmarc for this root-domain policy and paste the value without surrounding quotation marks.
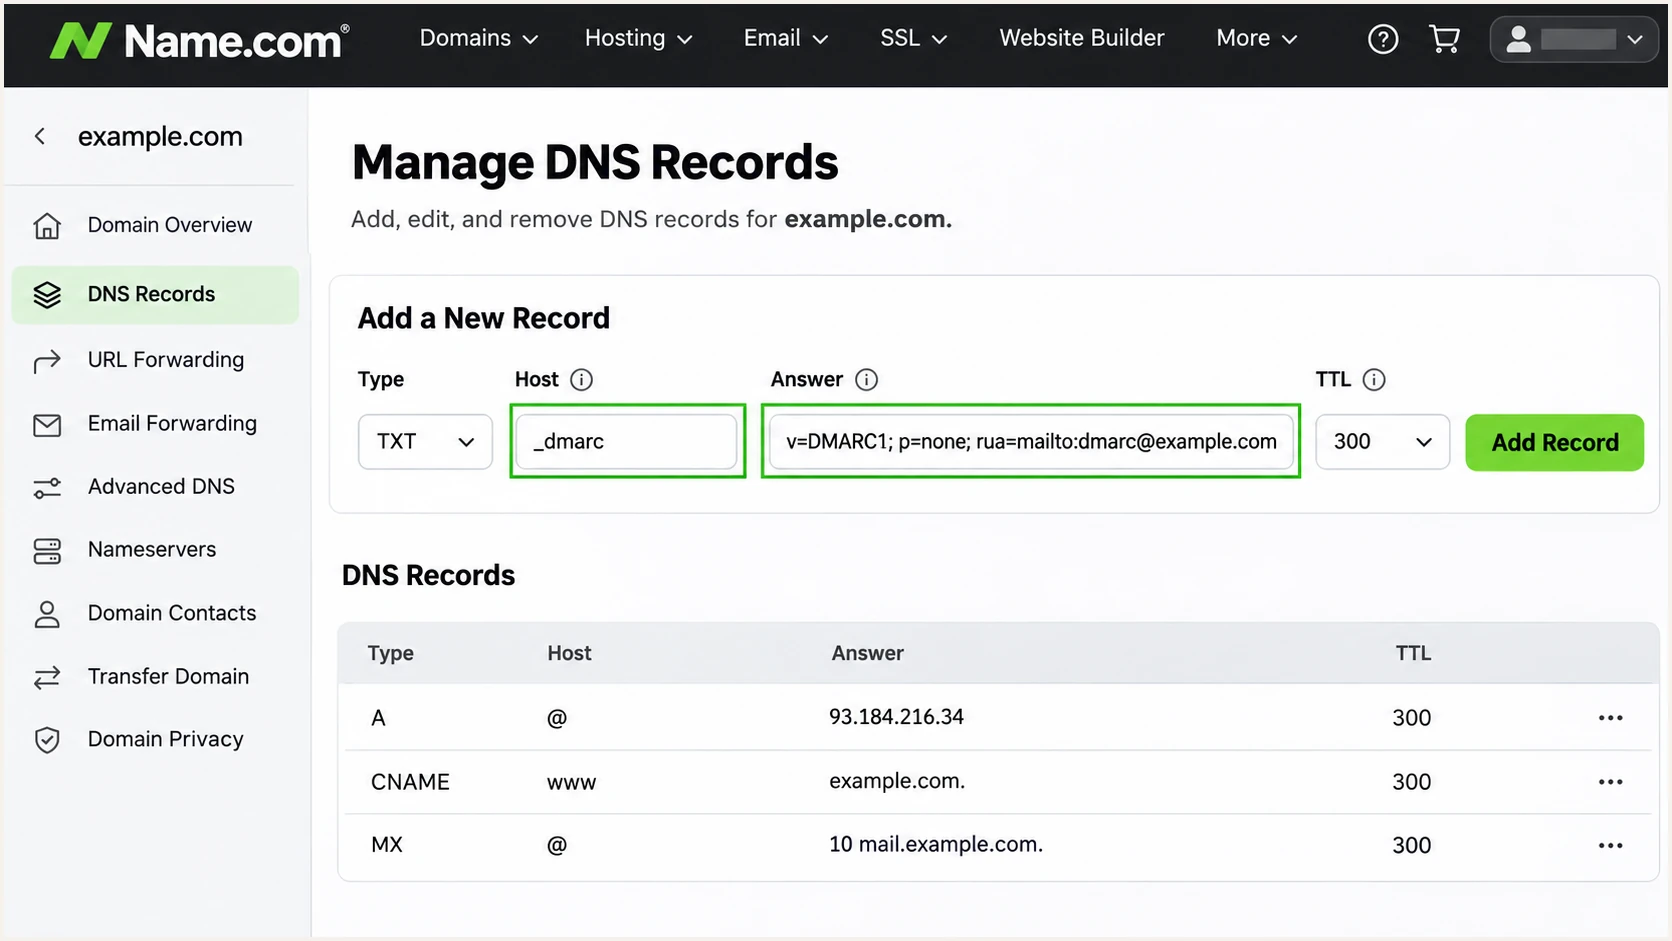
Illustrative Name.com DNS form with the initial DMARC TXT record.
I check public DNS after saving, rather than relying on the record being visible in the account. A record in an inactive DNS zone has no effect on mail received elsewhere.
Enter the domain in the DMARC checker below. Confirm it finds one valid policy and the intended report destination. Existing cached responses continue until their previous TTL expires.
DMARC checker
Look up a domain's DMARC record and catch policy issues.
?/7tests passed
A successful lookup confirms policy publication. It does not confirm that the hosting server signs correctly or that the application uses your domain in its envelope sender.
Keep the reporting address present as you change policy later. Aggregate reports normally arrive on a daily reporting cycle, and reporting coverage depends on which receivers send them.
Verify and troubleshoot
I test the same route that sends production mail. A successful webmail test does not establish that a website contact form or scheduled application job uses the same server settings.
Query the published records, then send fresh messages after DNS caches refresh. Use the selector from the message if it differs from default.
- Inspect public DNS. Run the TXT lookups below using your domain. Confirm one SPF policy at the envelope domain, the complete DKIM public key at the active selector, and one DMARC policy.
- Inspect received headers. Read Authentication-Results added by the destination server. Check spf=pass with smtp.mailfrom, dkim=pass with header.d, and dmarc=pass with header.from. A standalone SPF or DKIM pass on an unrelated domain is insufficient.
- Fix application SMTP. Use the hosting server name displayed in the Name.com dashboard, your full mailbox address as the SMTP username, and its password. Name.com documents port 465 for SMTP over implicit TLS. Set the application envelope sender as well as its visible From address.
- Check server identity. Compare the sending IP with the account's outbound configuration. If PTR or SMTP server identity is wrong, ask Name.com to repair it. Reverse DNS for a shared hosting IP is controlled by the IP operator, not your ordinary domain DNS zone.
Check the records, using the active DKIM selectorbash
dig +short TXT example.com
dig +short TXT default._domainkey.example.com
dig +short TXT _dmarc.example.com
The email tester is the quickest check of a real message. Open it, copy its destination address, and send a message through the Name.com mailbox or application being tested. Its report checks authentication and provides a diagnosis.
For a contact form, use your domain in From and put the visitor's address in Reply-To. Using the visitor's domain as From asks your hosting server to authenticate a domain you do not control.
Email tester
Send a real email to this address. Suped shows a results button when the test is ready.
?/43tests passed
I repeat the test separately for webmail and every application sending route. When SPF alignment fails but DKIM passes with a matching signing domain, DMARC still passes. Fix the envelope configuration where supported rather than adding unrelated provider domains to SPF.
Use the result to choose the next check. If authoritative DNS has the correct record but cached lookups do not, wait for cache expiry. Name.com warns that hosting authentication changes take up to 48 hours to become effective.
|
|
|
|---|---|---|
SPF fail | Outbound IP | Check SPF policy |
SPF mismatch | Envelope domain | Fix MAIL FROM |
DKIM none | Signing route | Enable signing |
DKIM fail | Key or message | Inspect signature |
DMARC fail | Domain matching | Check both identities |
Authentication results and the next check
Get alerted when it breaks
Suped is our DMARC reporting and email authentication platform. I recommend its DMARC monitoring for ongoing Name.com checks because it connects reported authentication failures with source details and specific steps to fix them.
Keep the initial hosting and DNS configuration in Name.com. For domains already monitored in Suped, use its notifications to catch authentication regressions and unexpected senders after that setup is working.
- Enable issue emails. In Suped notification settings, enable Issues detected and Sending sources need verification. Enable DMARC summary emails for regular review.
- Verify expected sources. Review the source table and verify expected Name.com traffic after checking its IPs and authentication domains against your account. Do not approve a source solely because its reverse DNS looks familiar.
- Trace the change. Open the affected records in Detail view. Compare SPF and DKIM results with DNS history to identify a changed SPF policy, missing selector, or unexpected sending IP.
- Confirm recovery. Apply the correction in Name.com or the authoritative DNS host. Send another test message and confirm recovery in newly received DMARC reports.
This connects an alert to a concrete repair: find the affected sending source, inspect the failure, change the relevant setting, and verify a new message. It also exposes a new website application that started sending without the expected authentication.
I treat report-based monitoring as ongoing evidence, not an immediate test after a DNS edit. Use the email tester for that immediate check and aggregate reports for broader sending coverage.
Alerts follow available data
Suped detects issues and sends notifications as data becomes available. DMARC aggregate reports are delayed by receiver reporting schedules; they are not a live feed of every message.
Secure your domain with p=reject
I move to p=reject after every authorized sending route has a demonstrated DMARC pass. Review failures by source; a high overall pass rate still hides a low-volume password-reset system that fails every message.
Suped provides source verification and record-level diagnostics for that review. Our hosted DMARC product also lets a team manage policy changes in the dashboard after its DNS configuration is complete. With a manual TXT record, make the policy change in Name.com DNS Management.
- Inventory real traffic. Verify Name.com hosting mail and every other authorized sender in Suped. Include contact forms, account notifications, scheduled jobs, and rarely used sending systems.
- Fix legitimate failures. Require a passing, matching SPF identity or DKIM signature on each route. Keep the default relaxed domain-matching mode unless strict matching is a deliberate requirement.
- Observe a full cycle. Collect enough reports to cover normal business activity and infrequent sends. Investigate unexplained sources before treating them as either authorized traffic or spoofing.
- Stage enforcement. Change p=none to p=quarantine, inspect new reports, and resolve legitimate failures before changing to p=reject. Keep an existing reject policy if it is already working.
- Check subdomains. Review explicit subdomain policies and the root policy's subdomain settings before enforcement. A root reject policy applies to subdomains without a more specific applicable policy unless subdomain settings change that behavior.
The examples below are successive policy stages. Publish only one DMARC record at _dmarc, and retain your real report destination at each stage.
Use Suped to inspect the new reports after each change. Fix an affected source directly; keep a saved copy of the last working policy for a controlled rollback if legitimate mail is disrupted.
Policy stages, publish one value at a timetext
v=DMARC1; p=quarantine; rua=mailto:dmarc@example.com
v=DMARC1; p=reject; rua=mailto:dmarc@example.com
A reject policy asks receivers to reject messages that fail DMARC. It does not guarantee inbox placement or stop messages sent through a compromised authorized account.
Keep monitoring after enforcement. Retest after a Name.com hosting migration, outbound SMTP change, or DKIM key rotation, and review any newly detected sending source before verifying it.
Frequency asked questions
No. Domain registration, DNS hosting, and outgoing email are separate functions. For Name.com cPanel Hosting Email, retrieve SPF and DKIM from the hosting account and publish them in authoritative DNS. If another service sends the mail, use that service's authentication records.
Copy the suggested SPF value from cPanel > Email Deliverability > Manage for your domain. There is no account-independent include established by these instructions. Preserve other authorized senders in the same SPF policy, and do not substitute an example IP or the registrar's domain.
Yes. DMARC passes when DKIM passes with a signing domain that matches the visible From domain under the applicable matching mode, even if SPF alignment fails. Name.com hosting supports your own envelope domain, so check the application MAIL FROM setting. Adding SPF at the visible From domain does not change a provider-owned Return-Path.
Name.com's hosting authentication instructions explicitly warn that this button is not functional in the documented workflow. Copy the suggested SPF and DKIM public values into authoritative DNS, then verify public lookups and a newly delivered message.
Name.com documents Hosting Email server names such as hs1.name.tools and older hs1.name.com names. If a sending IP's rDNS has a similar suffix, treat it as a lead when investigating Name.com hosting traffic. These examples are server naming patterns, not a verified list of all outbound PTR records. Confirm the sending IP and authentication domains against your hosting account before authorizing it.
New records work once authoritative DNS publishes them and prior cached answers expire. A TTL of 300 does not shorten an older cached TTL. Name.com warns that hosting SPF and DKIM changes take up to 48 hours. Test a fresh message after DNS updates, and allow the receiver's reporting cycle for DMARC aggregate reports.




