How to set up DMARC/DKIM/SPF for HostGo
To set up DMARC, DKIM and SPF for HostGo, publish the SPF and DKIM values shown in cPanel's Email Deliverability screen, then add a DMARC TXT record at your domain's _dmarc hostname. I start new DMARC deployments with p=none and verify a message sent by the actual website or application.
These steps apply to HostGo shared hosting with cPanel. Publish records at your authoritative DNS host, which is not necessarily HostGo. If your existing DMARC policy is p=quarantine or p=reject, keep that policy while fixing authentication.
Add your domain
I first confirm the sending domain belongs to the correct HostGo hosting account. If it is already listed in cPanel's Domains screen, skip domain creation.
- Open cPanel. Sign in to your HostGo hosting account and open its cPanel. Select Domains and look for the domain used in your email's From address.
- Add a missing domain. Select Create A New Domain, choose Registered Domain if shown, and enter your domain. Set the appropriate document root and click Submit.
- Handle older screens. HostGo's older instructions use Domains > Addon Domains. Enter New Domain Name, check Document Root, then click Add Domain. Ask HostGo about ownership validation if an externally hosted DNS zone prevents domain creation.
- Confirm the domain. Check that it appears in Domains and Email Deliverability. Verify your DNS changes publicly and send a test message after completing the authentication steps.
Check the domain's nameservers before editing DNS. Use HostGo's Zone Editor when its DNS is authoritative; otherwise publish the supplied records at your current DNS host. Adding a domain to cPanel does not transfer DNS authority.
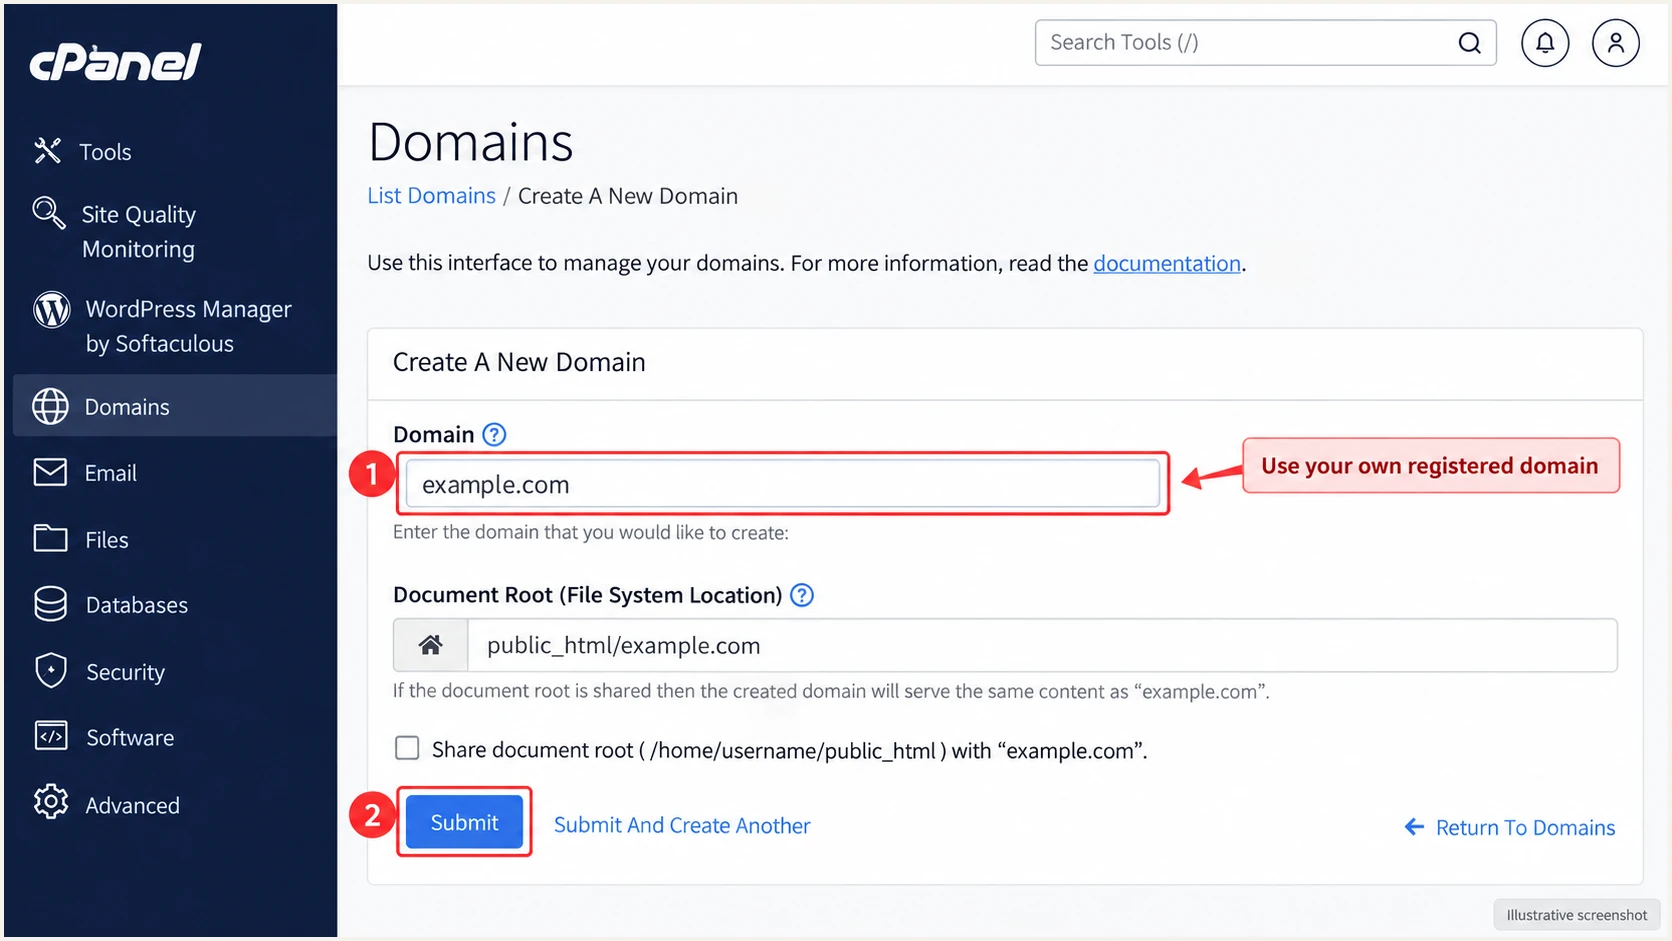
Illustrative HostGo cPanel domain creation screen.
Set up SPF
HostGo supports a return-path on your own domain. I configure SPF for the envelope sender domain used in SMTP MAIL FROM. That address normally appears in the delivered message's Return-Path header.
- Get the account value. Open Email > Email Deliverability, click Manage beside your domain, and find the suggested SPF TXT record. Copy its Name and Value.
- Preserve other senders. Find the existing SPF TXT record at that hostname. Merge HostGo's required mechanisms before its final all mechanism, if present. Keep one v=spf1 prefix and preserve other required senders.
- Publish the record. When HostGo hosts authoritative DNS, open Domains > Zone Editor > Manage, edit the TXT record, and click Save Record. Otherwise make the equivalent edit at your DNS host.
- Set the envelope sender. Configure your application's mailer to use a working sender or bounce mailbox on your domain. For From: notices@example.com, bounces@example.com uses the same domain. Changing Reply-To does not change MAIL FROM.
- Check DNS lookups. Allow at most 10 evaluated SPF terms of the types include, a, mx, ptr, exists and redirect, including nested includes. Authorize the actual outbound route.
I take sending IPs and include values from the account's suggestion, with HostGo support confirming any outbound relay. Your website's IP and inbound MX records do not reliably identify the server that delivers outgoing mail.
SPF checker
Find SPF syntax issues, lookup limits, and weak records.
?/16tests passed
Run the check against the envelope sender's domain. Resolve duplicate SPF records and lookup-limit errors before sending another test message.
If your actual route keeps a provider-owned return-path, adding HostGo to the visible From domain's SPF will not fix SPF alignment. Passing DKIM with a matching signing domain is sufficient for DMARC in that situation.
Keep one SPF policy
Publishing a second SPF record at the same hostname causes an SPF error. Preserve other approved senders when editing. Copy account-specific values instead of guessing an include for hostgo.com.
Set up DKIM
I enable signing on the HostGo server and publish its matching public key. A public key added to DNS only works when the sending server signs messages with the corresponding private key.
- Open DKIM settings. Go to Email > Email Deliverability > Manage for your sending domain and find the DKIM section.
- Create a missing key. If Generate Local DKIM Key is offered, use it to create the domain's key. If signing controls are unavailable, ask HostGo to enable domain signing.
- Publish the public key. Copy the exact suggested TXT Name and Value. The name commonly uses default._domainkey.example.com; use the selector shown in your account. Install the suggested record locally when HostGo is authoritative, or publish it at your external DNS host.
- Check the signature. Recheck the domain's DKIM status and send a fresh message. Inspect DKIM-Signature: its d= domain must match your From domain under DMARC's matching rules, and s= identifies the selector to look up.
Copy the entire public key. cPanel's Full and Split views change how the TXT value is displayed. If your DNS host requires multiple quoted strings, keep them within one TXT record. Keep the private key on the hosting server.
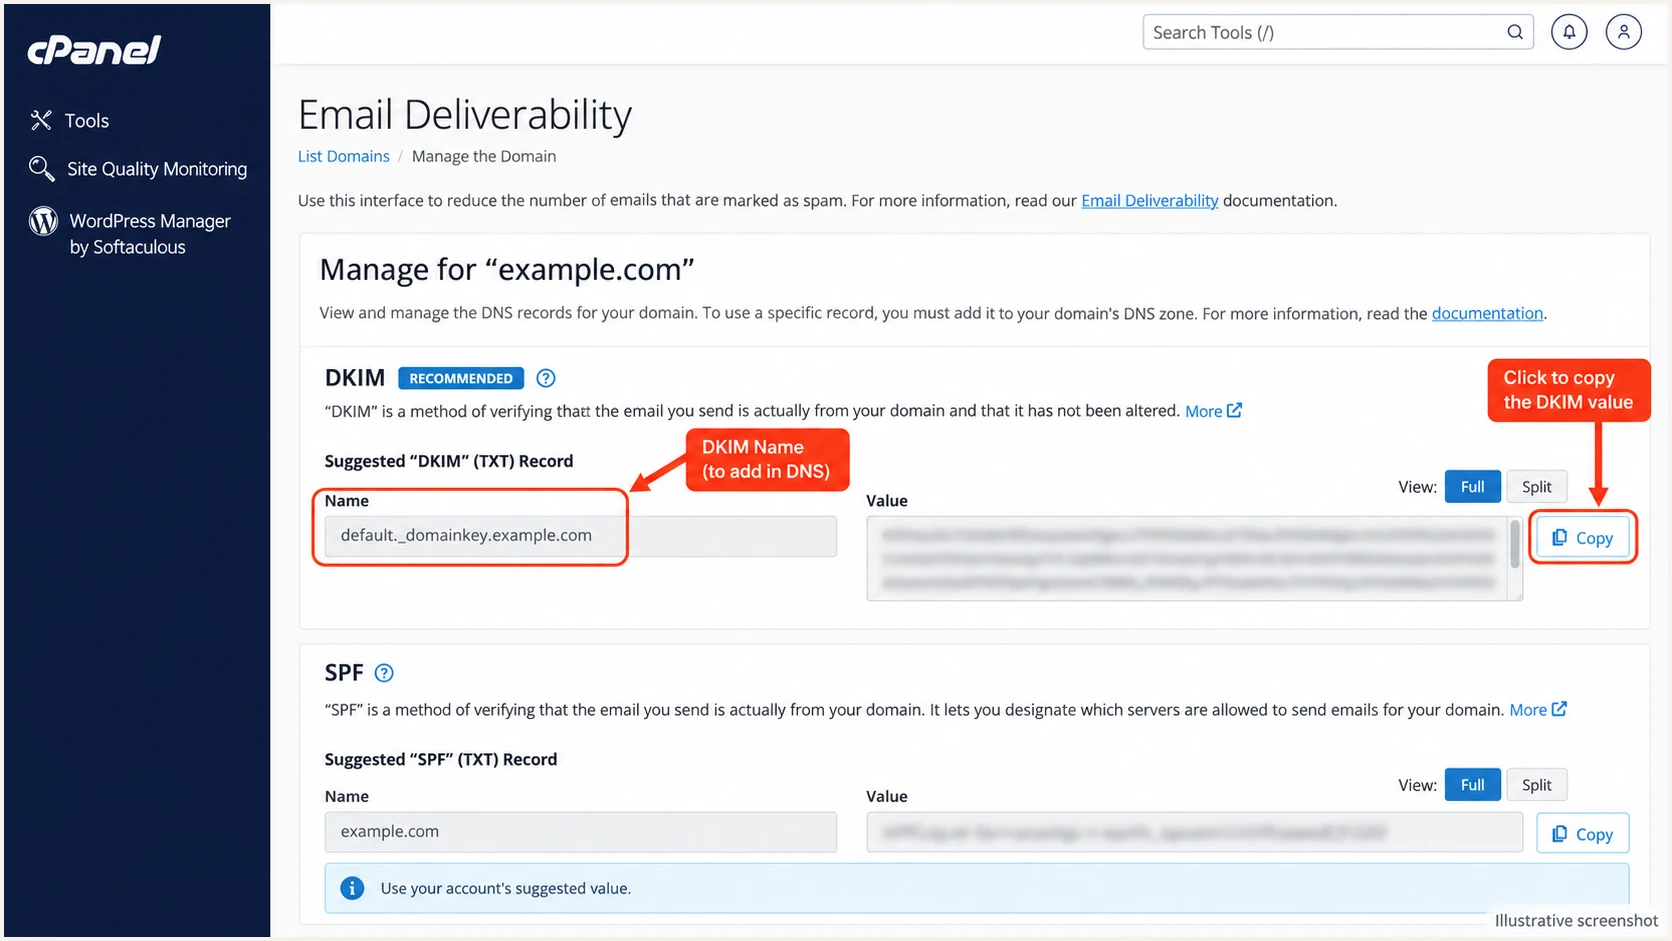
Illustrative HostGo cPanel SPF and DKIM record controls.
For website mail, I use authenticated SMTP with the settings in Email Accounts > Connect Devices. Use the displayed outgoing hostname and secure port, authenticate with the full mailbox address, and send using your configured domain. Test the application itself because PHP mail submission does not always use the same signing route.
Set up DMARC
DMARC checks the visible From domain. It passes when SPF or DKIM passes with the required domain matching. I configure both for HostGo, while checking each result separately.
- Check existing policy. Look up _dmarc.example.com using your own domain. Check inherited parent-domain policy for subdomains. Keep existing p=quarantine or p=reject enforcement and preserve reporting destinations.
- Generate a starter record. For a domain without DMARC, use the DMARC record generator and choose p=none. Set a reporting mailbox you control.
- Save one TXT record. At your authoritative DNS host, create or edit _dmarc.example.com as TXT with TTL 3600. Use _dmarc in a relative-name field. Keep only one DMARC policy record at that hostname.
- Keep matching defaults. Leave adkim and aspf unset for relaxed domain matching unless you need strict matching. For relaxed matching, the authenticated domain and From domain share the same organizational domain.
For a new policy, use this initial record. Replace example.com with your domain and dmarc@example.com with an actual reporting mailbox before publishing.
Initial DMARC TXT recordtext
Name: _dmarc.example.com
Type: TXT
TTL: 3600
Value: v=DMARC1; p=none; rua=mailto:dmarc@example.com
Confirm the reporting address receives mail before using it in DNS. Aggregate reports arrive as XML files; a report processor makes those files usable for monitoring.
A p=none policy requests monitoring without requesting rejection or quarantine for DMARC failures. It does not change SPF or DKIM results. Keep existing enforcement when a domain is already protected.
DMARC checker
Look up a domain's DMARC record and catch policy issues.
?/7tests passed
Check your visible From domain after saving. Resolve missing-record and duplicate-policy results at the authoritative DNS host, then check again after cached responses expire.
When HostGo is authoritative, use Domains > Zone Editor > Manage > Add Record > TXT. Reopen the saved entry and confirm its name is _dmarc.example.com, with your domain appearing only once.
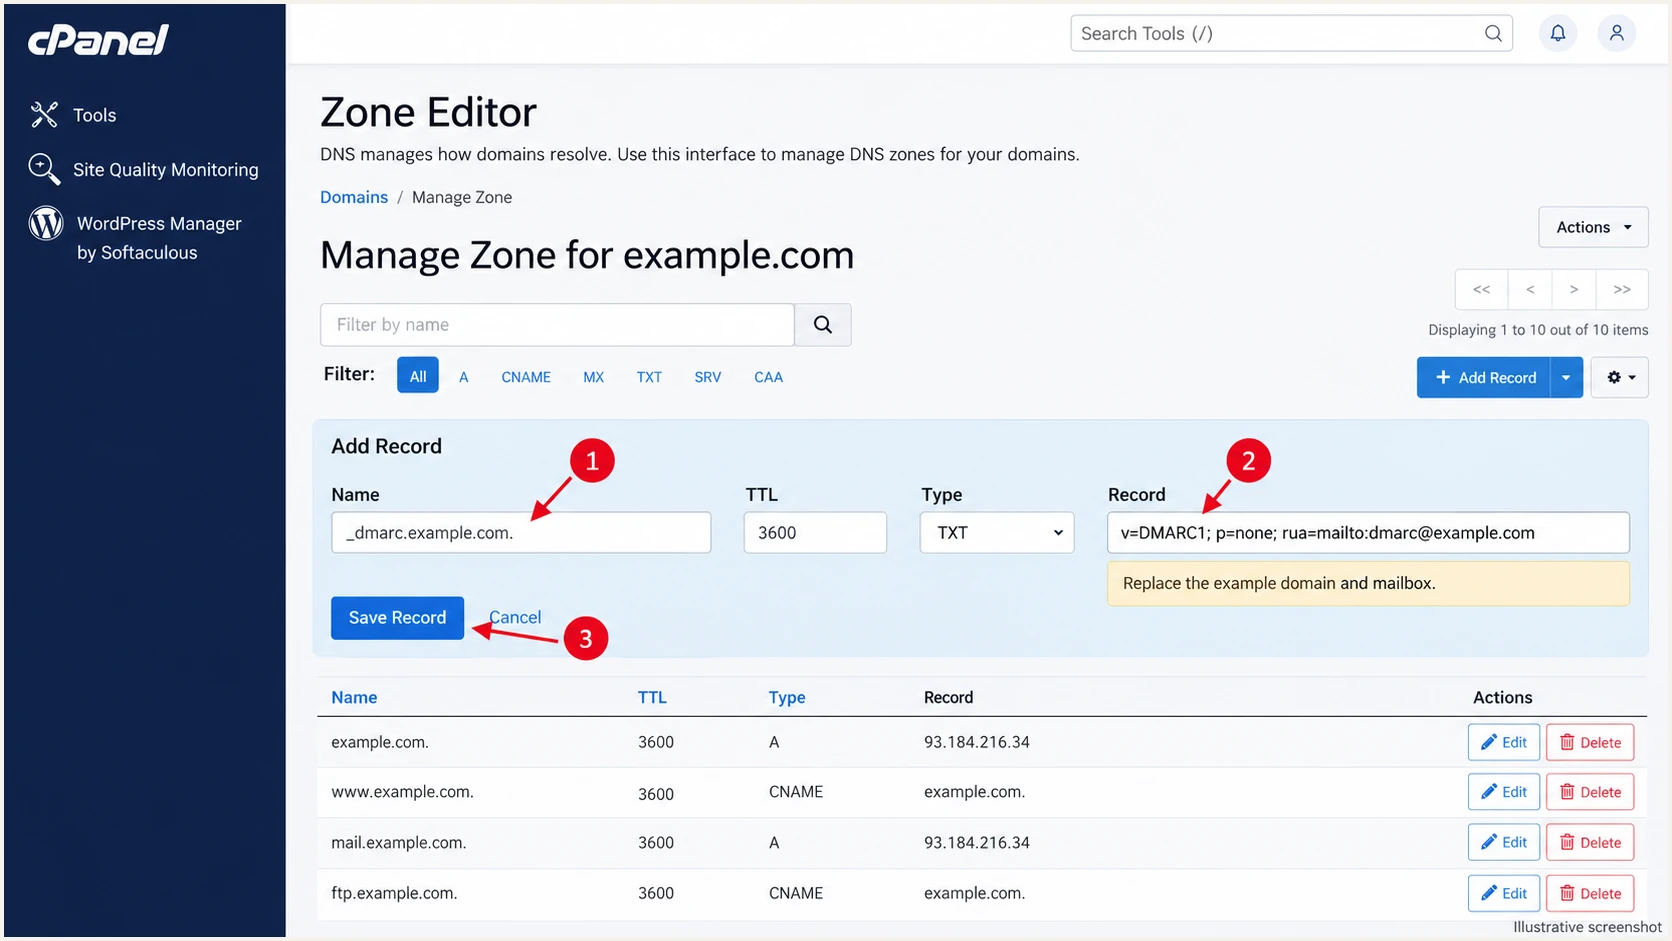
Illustrative HostGo cPanel DMARC TXT record entry.
Verify and troubleshoot
I test every production sending route separately. A successful webmail message does not verify your website's contact form or its scheduled jobs.
- Send through HostGo. Get the test address from the email tester and send a message from your actual application. Repeat for each route that sends using your domain.
- Read receiver results. Inspect the diagnosis and the receiving server's Authentication-Results header. Look for spf=pass, dkim=pass and dmarc=pass, and inspect the domains associated with those results.
- Check domain matching. Compare smtp.mailfrom with the visible From domain for SPF, and DKIM's d= domain with From for DKIM. An SPF pass for an unrelated bounce domain does not provide SPF alignment.
- Retest after repairs. Correct the relevant DNS record or HostGo signing configuration. Wait for the previous DNS TTL to expire, send a fresh test, and confirm recovery in subsequent aggregate reports.
The email tester supplies a destination address and a full diagnosis after you send a message. This checks the actual HostGo message, including authentication and related delivery checks.
Email tester
Send a real email to this address. Suped shows a results button when the test is ready.
?/43tests passed
A DNS check confirms the published record. A live message reveals the sending IP and signing domain actually used. I use receiver-added results when comparing these two checks.
For a missing signature, check server signing and application submission. For a failed signature, compare the published selector key with cPanel and investigate message changes after signing. Ask HostGo to investigate PTR problems on its shared sending IPs.
|
|
|
|---|---|---|
SPF permerror | Duplicates or limits | Repair SPF |
SPF domain mismatch | Provider bounce domain | Check MAIL FROM |
DKIM missing | Unsigned app route | Enable signing |
DKIM fail | Key or message mismatch | Check selector |
DMARC fail | No matching pass | Fix domain matching |
PTR warning | Server reverse DNS | Contact HostGo |
Match the failure to the setting that needs repair.
Get alerted when it breaks
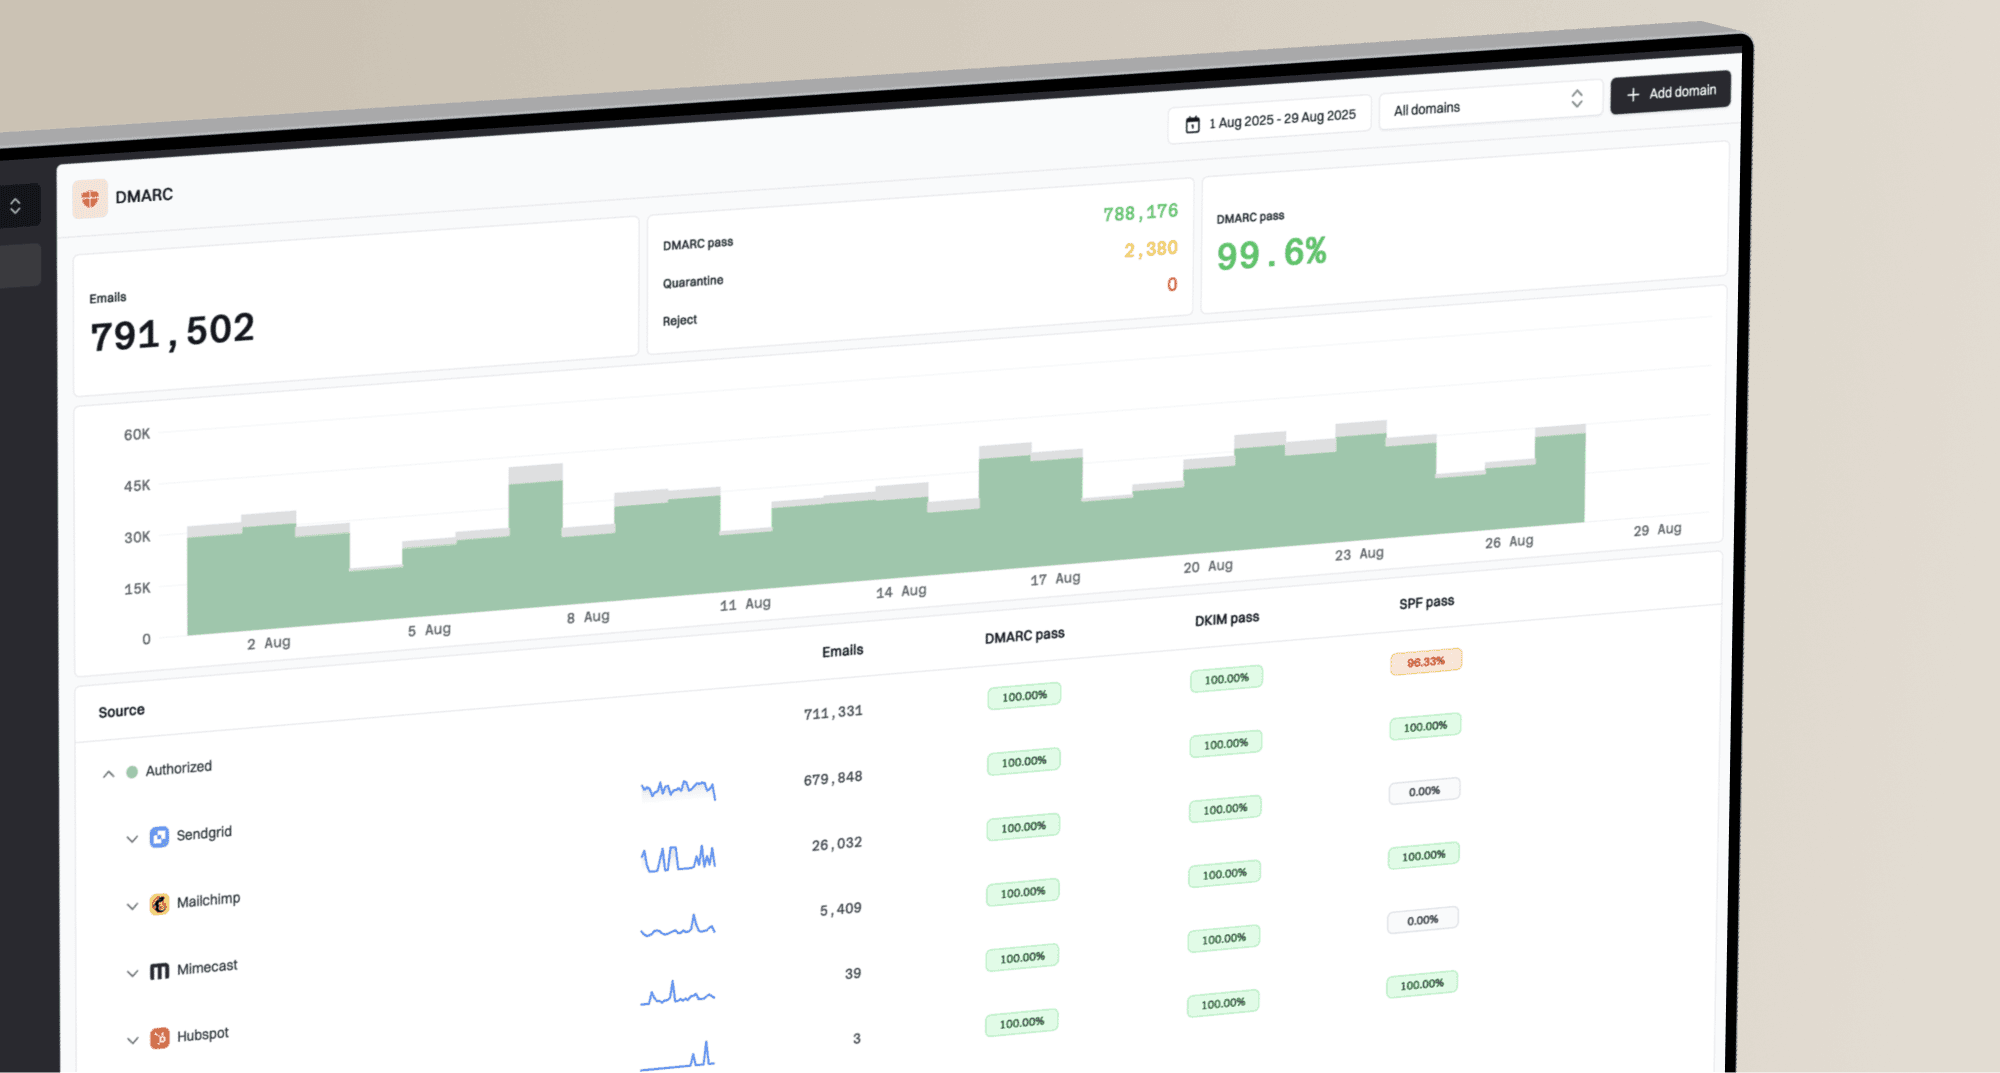
cPanel's record status is a DNS snapshot. Suped, our DMARC platform, processes receiver reports so your team can monitor HostGo authentication alongside other authorized senders. Our DMARC monitoring connects source-level failures with issue details and steps to fix them.
- Route aggregate reports. Use the reporting address supplied by Suped for your monitored domain in the existing DMARC rua tag. Keep the current p= value. A normal mailbox alone does not create failure alerts.
- Enable notifications. In Suped, open Settings > Notifications and enable DMARC alerts. Enable summary emails for regular reviews of authentication changes.
- Investigate HostGo failures. Inspect the source's SPF and DKIM results. Filter records by source IP or reporter to distinguish a new outbound server from a persistent signing issue.
- Confirm recovery. Apply the fix in HostGo or authoritative DNS, send another application test, and review new reports for the affected source.
Suped's alerts depend on incoming aggregate reports. Those reports generally arrive daily, so they are not an immediate per-message failure feed. I use a live test for urgent validation and reporting for ongoing coverage.
cPanel checks
Inspect and repair the HostGo account's DNS records. Send application tests after changes to confirm the server is signing mail correctly.
Suped monitoring
Review authentication results reported by receivers across your domain's senders. Suped detects issues and provides fix steps, with alerts when configured failure conditions are met.
Secure your domain with p=reject
I move to p=reject after legitimate sources have a reliable DMARC pass. Suped's source table and record diagnostics provide the evidence for that decision, including HostGo traffic that a single test message misses.
- Inventory legitimate mail. Review aggregate reports across a complete sending cycle, including infrequent jobs and transactional messages. Confirm authorized sources before changing policy.
- Repair known sources. Fix HostGo signing and envelope-sender problems. Confirm every legitimate route has at least one passing authentication method with the required domain matching. Test forwarding paths you depend on.
- Stage enforcement. Use p=quarantine as an intermediate stage when operationally useful. Review legitimate-mail failures after the change. Keep existing enforcement while repairing individual sources.
- Enforce rejection. Edit the existing DMARC policy to p=reject and retain working reporting destinations. Recheck public DNS and send fresh HostGo application tests.
- Review subdomains. Check inherited policy and any separate subdomain DMARC records. An explicit sp=none or a subdomain's own policy changes the protection those subdomains get.
Suped's hosted DMARC lets your team manage policy changes in the dashboard after DNS delegation. Use the monitoring data to validate each stage, and continue fixing SPF or DKIM in HostGo where the underlying issue exists.
Publish reject after validation
Use p=reject once legitimate sending routes pass DMARC. Replace the example domain and reporting mailbox, and preserve any other required tags in your existing policy.
Final DMARC TXT recordtext
Name: _dmarc.example.com
Type: TXT
TTL: 3600
Value: v=DMARC1; p=reject; rua=mailto:dmarc@example.com
A p=reject policy requests rejection of messages that fail DMARC. Receiving servers apply their own handling rules; an authentication pass also does not guarantee inbox placement.
I keep reporting and alerts enabled after enforcement. Recheck the actual application after a HostGo server migration or a change to website mail settings.
Frequently asked questions
Use the account-specific SPF value in cPanel > Email Deliverability > Manage. Confirm any outbound relay with HostGo support. I merge the required mechanisms with existing authorized senders instead of publishing a second SPF record.
HostGo supports using your domain for the envelope sender. Configure the application's MAIL FROM and inspect a delivered message's Return-Path to verify the actual route. A Reply-To address or a manually added Return-Path header does not configure the SMTP envelope sender.
SPF authenticates the envelope sender domain. If that domain differs from the visible From domain under DMARC's matching rules, the SPF pass does not count toward DMARC. DMARC still passes with a valid DKIM signature using a matching domain. I check both authentication results and domain matching.
The suffix suggests HostGo hosting infrastructure. I confirm the sending IP with HostGo because a PTR hostname alone does not prove who operates the server or whether a customer application is authorized. Check SPF and DKIM before approving the source.
No. DMARC uses a TXT record at _dmarc, SPF uses a TXT record at the envelope sender domain, and HostGo's cPanel DKIM setup publishes a selector TXT record. Keep working MX records unless you are also changing where incoming mail is delivered.
The website's submission route still needs server-side signing. I configure authenticated SMTP using Email Accounts > Connect Devices and test the application again. If the message remains unsigned, ask HostGo to check the domain's signer and any outbound relay configuration.