What are the best practices for sunsetting inactive email subscribers according to ISPs and GDPR?
Updated on 10 Oct 2026: We clarified lawful re-engagement, tracking permissions, and suppression safeguards for inactive subscribers.
The best practice is to use a documented sunset policy: define inactivity, reduce cadence or attempt reconfirmation while marketing permission remains valid, suppress inactive subscribers after a clear window, keep the minimum suppression record needed, and delete or anonymise old engagement data when it no longer has a purpose. Gmail, Yahoo, and Apple direct senders to manage inactive recipients and maintain clean subscriber lists. GDPR does not ban this by default. It requires a lawful basis, transparent notices, purpose limitation, data minimisation, and storage limitation.
The important legal nuance is that measuring inactivity can involve personal-data processing. Open and click data are personal data when tied to an email address. That does not mean every sunset rule is prohibited profiling. The better framing is operational retention and suppression: the sender is deciding whether continuing to send marketing is still necessary, wanted, and safe for mailbox reputation.
- Direct answer: Sunsetting inactive subscribers is a normal deliverability practice and can support GDPR storage limitation.
- Starting window: Six months is an example for regular marketing programs, not an ISP rule or a GDPR consent-expiry deadline. Frequency and buying cycle matter.
- Key caveat: Do not rely on opens alone. Tracking permission and accuracy are separate issues, and Apple Mail Privacy Protection distorts open data.
- Legal framing: Treat it as retention, suppression, and deliverability risk management, with legal review for your market.
Why sunsetting supports deliverability and privacy
Subscriber sunsetting is both a deliverability control and a privacy control. Continuing to mail persistently inactive subscribers increases exposure to complaints and unnecessary sending costs, and keeps identifiable engagement history longer than needed. Complaints and other negative recipient signals can damage sender reputation; inactivity alone does not prove that an address is invalid.
A sunset rule needs reliable, lawfully collected data. Verified human clicks, recent replies, subscription confirmation, and lawfully collected customer activity give more context than remote image loads alone. Opens are useful as a weak signal, but they are not reliable enough to be the only trigger. Purchases and logins do not override an unsubscribe or create marketing permission.
Legal and deliverability requirements
- ISP position: Major mailbox providers want senders to mail people who want the mail and manage inactive recipients.
- GDPR position: Keep personal data only while necessary for the stated purpose, and document the processing basis.
- Policy position: Use a written rule that applies consistently and gives subscribers a fair chance to remain subscribed.
- Risk position: Continuing to mail inactive users increases exposure to complaints, wasted sending, and unnecessary data retention.
If the internal debate is whether a six-month inactive segment is allowed, document why that window fits the sender's cadence. A daily retailer and a yearly renewal business should not use the same rule.
What mailbox providers actually ask for
Mailbox providers rarely use the exact phrase "sunset policy" in the way email teams use it. They do tell bulk senders to manage inactive recipients, reconfirm subscribers, honor unsubscribe requests, process bounces, and avoid sending mail that recipients do not want. That supports a sunset policy without overstating the provider language.
|
|
|
|---|---|---|
Confirm addresses and interest, consider unsubscribing people who do not read messages, and support one-click unsubscribe for bulk marketing mail. | Run reconfirmation while permission remains valid, then suppress nonresponders under the written policy. | |
Monitor hard and soft bounces, complaints, and inactive recipients; consider periodic reconfirmation emails. | Watch inactivity, process complaints promptly, and remove invalid recipients. | |
Periodically remove inactive subscribers, suppress disengaged users, and do not reactivate addresses on unsubscribe or suppression lists. | Suppress inactive contacts and remove repeat bounces; do not automatically restore suppressed addresses. | |
Reputation, complaints, authentication, and recipient signals affect filtering. | Reduce risk with clean lists and lower complaint pressure. |
How mailbox-provider guidance translates into a sunset policy.
Google, Yahoo, and Apple give the clearest support for inactivity management. Microsoft guidance focuses more on reputation, authentication, complaints, and filtering outcomes. No provider in this comparison mandates a universal six-month cutoff. The defensible claim is that mailbox providers reward wanted mail and penalise mail that draws negative recipient signals.
Keep unsubscribe handling separate from the inactivity window. Gmail's bulk-sender guidance calls for RFC 8058 one-click unsubscribe for marketing mail and recommends processing requests within 48 hours. A preference-center link alone does not meet that requirement. Yahoo's sender requirements require bulk senders to honor unsubscribes within two days. Stop affected marketing promptly; do not wait for the sunset deadline.
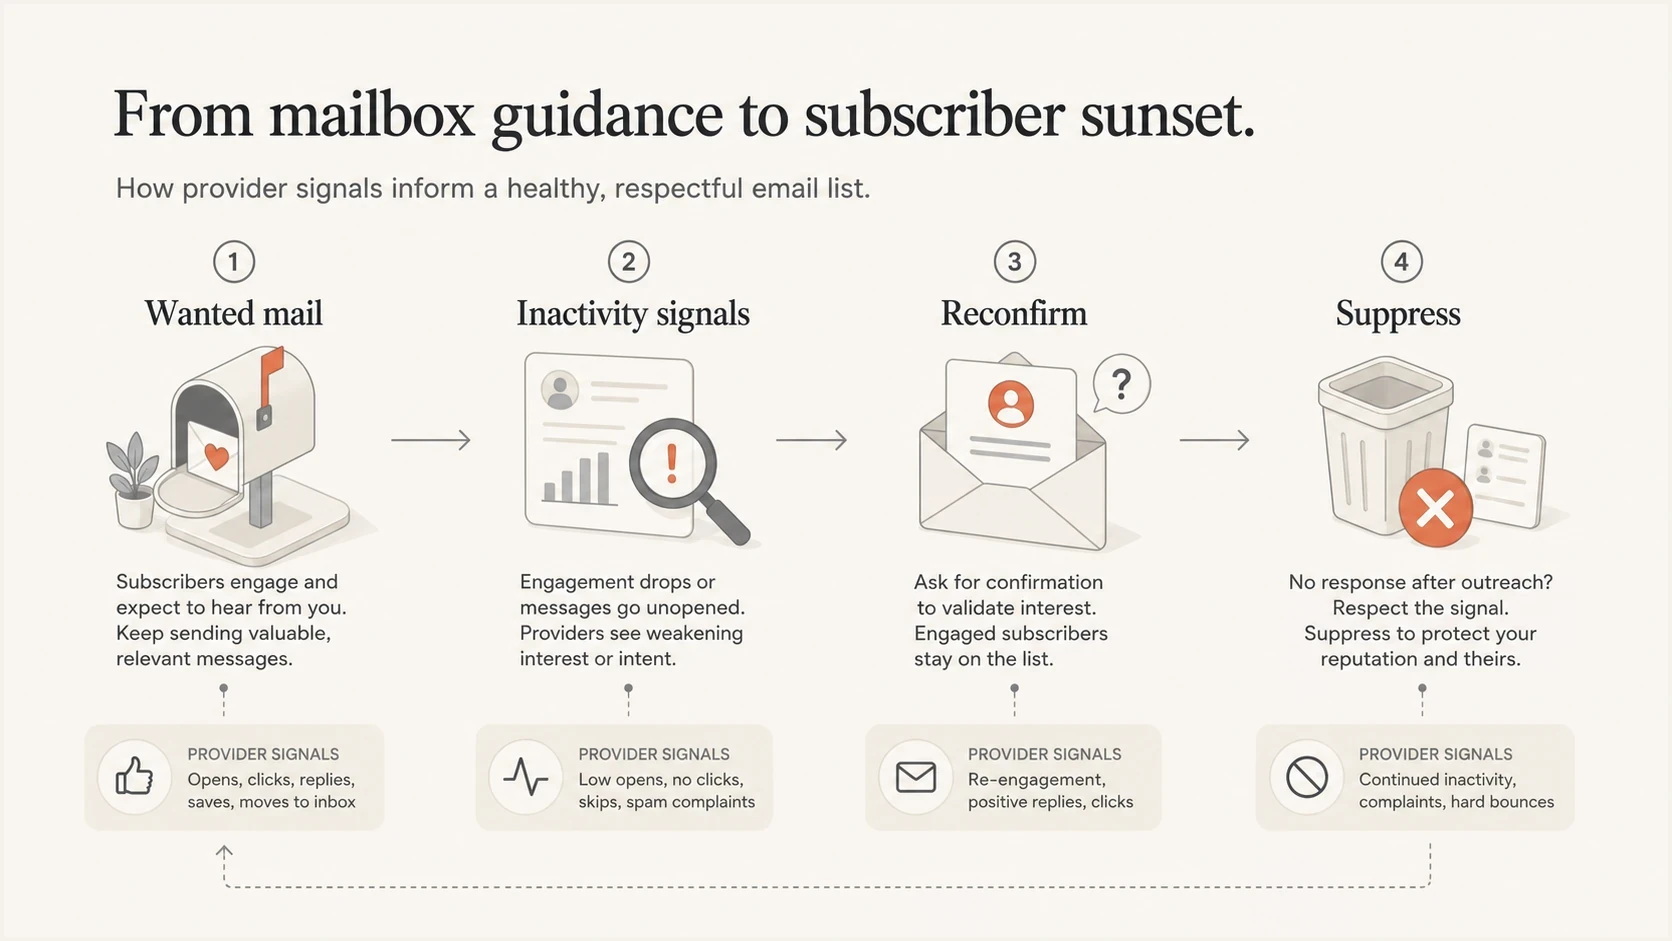
How ISP guidance leads to wanted email, inactivity checks, reconfirmation, and subscriber suppression.
How to define inactivity
The best inactivity definition combines engagement, commercial context, and risk. Start with positive signals, not just missing opens. A subscriber who clicked, bought, logged in, replied, renewed, used the product, or updated preferences is not the same as a subscriber whose only activity is a pixel load from an automated privacy proxy. Use customer activity only for compatible, disclosed purposes, and keep the marketing-permission check separate. Measure inactivity across enough delivered campaigns to reflect the normal buying cycle.
Illustrative inactivity windows
These are starting examples, not ISP requirements or legal deadlines. Adjust them to mailing cadence, delivered campaigns, and the normal purchase or renewal cycle.
High-frequency senders
60-90 days
Daily or near-daily promotional programs usually need a shorter window.
Weekly senders
120-180 days
Regular campaigns usually support a longer observation period than daily sends.
Seasonal senders
9-12 months
Longer cycles need a longer observation window and, where permission remains valid, a reminder before suppression.
Transactional mail
separate
Do not sunset operational notices using marketing inactivity rules.
For most marketing programs, use a staged approach: reduce frequency first, send a preference or reconfirmation message while permission remains valid, then suppress. If the brand has a long buying cycle, the reconfirmation step matters more than the exact day count. If the brand sends daily promotions, waiting a full year keeps too much uninterested mail flowing.
- Clicks: Use verified human clicks as a stronger signal than opens, and filter automated link scans before resetting the inactivity clock.
- Purchases: Respect buying cycles and avoid suppressing seasonal customers too early. A purchase does not renew withdrawn marketing consent.
- Replies: Treat real replies and preference updates as strong signs of ongoing interest.
- Opens: Use opens only as supporting evidence because privacy proxies and blocked images distort them.
- Complaints: Suppress complainers immediately and keep enough proof to avoid mailing them again.
How GDPR applies to subscriber sunsetting
The GDPR argument should be more specific than "inactive suppression is profiling". EU GDPR Articles 4 and 22 distinguish profiling from solely automated decisions that produce legal or similarly significant effects. A rule that evaluates engagement can be profiling without automatically falling under Article 22. For a rule that only stops optional marketing, assess whether either effect actually occurs. The processing still needs a lawful basis, transparency, and a necessary, proportionate purpose.
Article 5 is the stronger operational hook. Personal data should be adequate, relevant, limited to what is necessary, and kept in identifiable form only as long as needed. If the purpose is commercial email communication, a retention rule that stops mailing persistently inactive contacts can support that principle. GDPR does not set a universal date when marketing consent expires. Consent must still remain valid for its purpose and the subscriber's reasonable expectations; inactivity does not automatically renew it.
Weak framing
- Profiling label: Calling the rule profiling without explaining the actual legal effect creates confusion.
- Open-only rule: Using only pixel opens creates accuracy and consent problems in EU programs.
- No retention date: Keeping inactive contacts forever conflicts with minimisation and storage limitation.
- No audit trail: Unrecorded suppressions are harder to defend and easier to reverse by mistake.
Stronger framing
- Retention purpose: State that the rule limits data use after the marketing purpose weakens.
- Composite signal: Use clicks, purchases, logins, replies, bounces, and complaints instead of opens alone.
- Documented policy: Approve and record the policy; assess Article 22 separately if its conditions apply.
- Suppression proof: Keep the minimum record needed to prevent accidental future marketing.
For EU senders, separate permission to receive marketing from permission to use tracking pixels or tracked links. National ePrivacy rules apply alongside GDPR, and a GDPR lawful basis does not replace consent where those rules require it. A privacy notice alone does not supply consent. If the required permission is missing, stop that tracking and use lawfully collected signals for sunsetting.
Country-specific guidance also matters. CNIL's 2026 tracking-pixel guidance allows a narrowly defined consent exemption for deliverability tracking only when all stated conditions are met, including a service explicitly requested by the subscriber and data limited to what is necessary to adjust frequency or stop inactive-recipient sends. Calling a pixel "list hygiene" does not establish that exemption. Campaign analytics and profiling require their own assessment. Apply the rules for the relevant jurisdiction rather than assuming one EU-wide tracking exemption.
When a re-engagement email is lawful
A re-engagement campaign is still marketing when its purpose is to keep someone subscribed. The ICO classifies consent requests as direct marketing even without an offer. For UK individual subscribers, check valid consent or a fully applicable PECR soft opt-in before sending; the ICO explains those conditions. For EU recipients, apply the relevant national electronic-marketing rules. Calling the message "re-permission" does not repair missing or withdrawn permission.
- Check eligibility: Screen the segment against current permission records, unsubscribes, complaints, objections, and invalid addresses.
- Make the choice clear: Explain the subscription and the planned stop date. Offer an intentional confirmation or frequency preference plus an easy unsubscribe.
- Limit the sequence: Start with one message to a small eligible batch. Set a defined response window, pause routine promotions, and stop if complaints or bounces rise.
- Record the result: Save the confirmation or preference submission and the relevant notice version. Nonresponse is not renewed consent; suppress it under the policy.
If permission is absent or withdrawn, skip the email and suppress marketing. Offer a fresh opt-in when the person next visits the site or account, without making access to an existing service conditional on resubscribing.
How suppression differs from deletion
Inactivity is not the same event as an unsubscribe, a complaint, a hard bounce, or an erasure request. A nonresponse to reconfirmation supports stopping regular marketing, but it does not by itself prove that the person made an explicit legal objection. Record the actual reason for each status so future imports and reactivation work do not erase the distinction.
|
|
|
|---|---|---|
Inactive after reconfirmation | Suppress routine marketing; restore it only after intentional confirmation or a valid preference update, with permission still valid. | Keep the minimum status record; delete or anonymise expired event detail. |
Unsubscribe, complaint, or objection | Stop direct marketing promptly and do not reactivate without a new valid opt-in. | Keep a minimal do-not-contact record so later imports cannot remail the person. |
Hard bounce or invalid address | Stop sending immediately. | Retain only the bounce or suppression marker required to prevent retries. |
Valid erasure request | Stop the affected marketing processing. | Erase covered data; assess and explain any justified exception for a minimal compliance record. |
Use a status-specific action instead of treating every inactive address as deleted.
Do not let imports undo suppression
Hash or otherwise minimise the identifier when the policy allows, but keep it usable for screening. A matchable email hash remains personal data, so hashing does not remove GDPR obligations. Deleting every trace of an opt-out can cause a later customer-data import to add the person back to marketing. The ICO's suppression guidance supports keeping only the information needed to respect the objection. Restrict access, screen imports against the record, and document its separate retention purpose.
How to automate a subscriber sunset policy
The safest operational pattern uses defined subscriber states instead of deleting everyone after one silent period. That gives marketing a chance to keep real customers, gives legal a defined retention path, and gives deliverability teams a way to reduce risk before reputation damage shows up. Automate the rules in the email platform or customer database, and run suppression checks before every marketing send. Double opt-in at signup helps record subscriber intent and prevent invalid addresses entering the list.
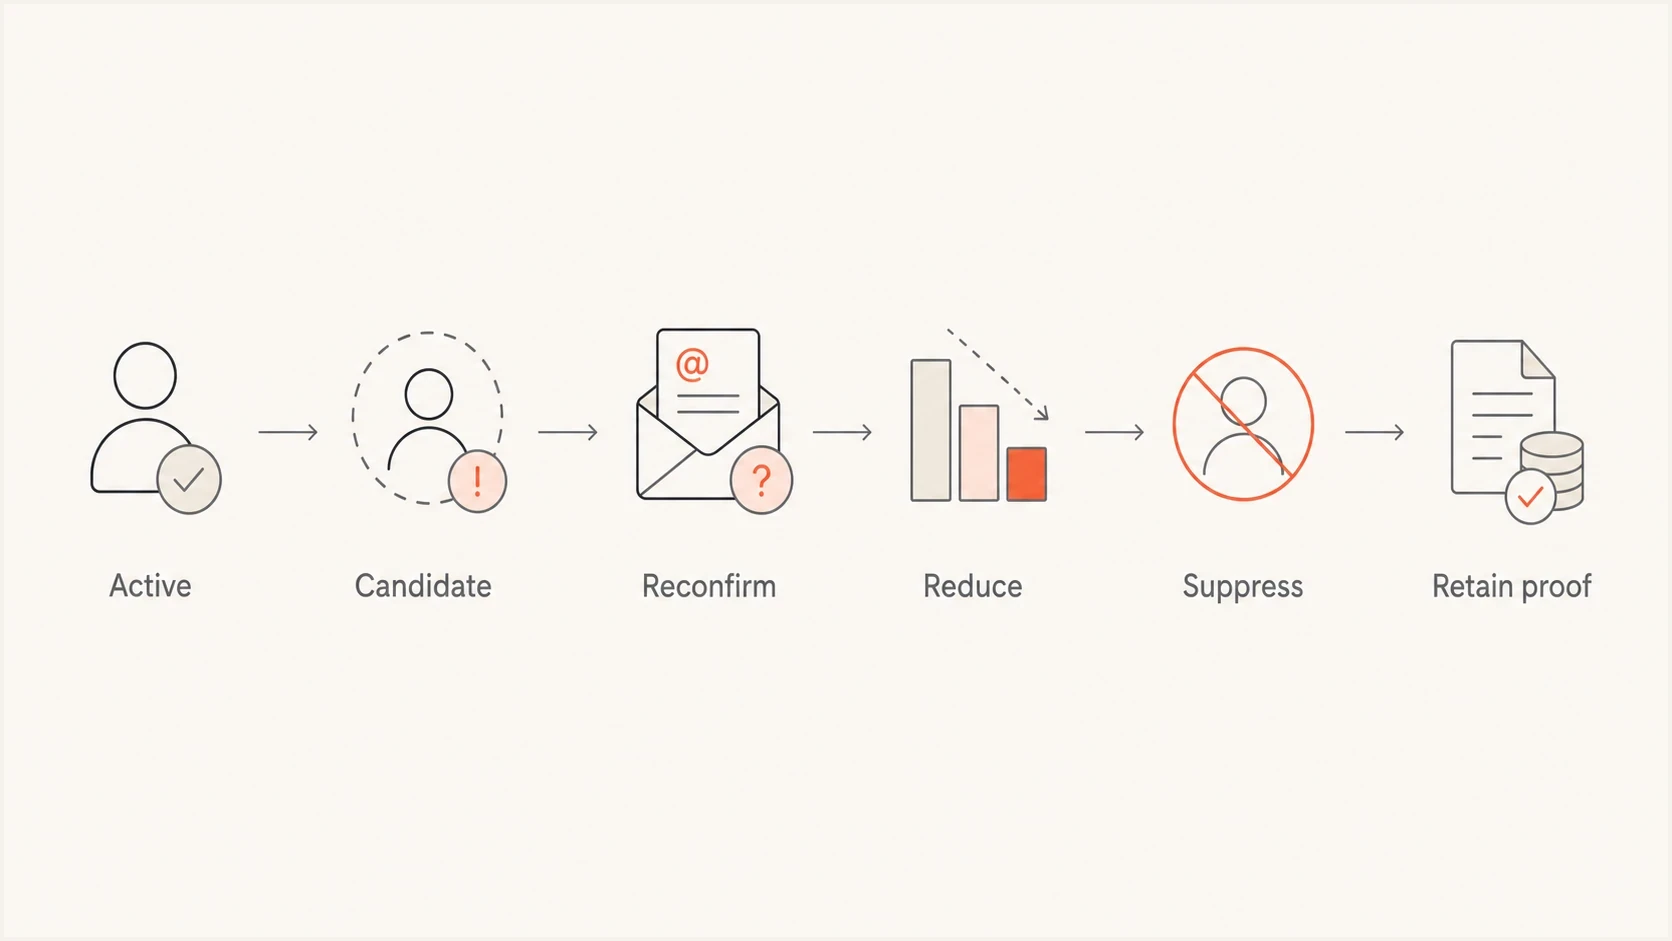
Inactive-subscriber sunset workflow: active, candidate, reconfirm, reduce, suppress, and retain proof.
- Define activity: List the lawful events that reset the inactivity clock. Filter automated clicks and use the signup date when no verified engagement exists.
- Separate mail types: Apply the rule to marketing mail, not account security notices, receipts, or required service messages.
- Create candidates: Move quiet subscribers into a pre-sunset segment at the chosen threshold, excluding unsubscribes, objections, complaints, and invalid addresses.
- Ask clearly: Send a reconfirmation or preference message only where marketing permission remains valid, with a clear way to stay, change cadence, or leave.
- Reduce cadence: Pause normal campaigns while the reconfirmation sequence runs.
- Suppress safely: Stop marketing to nonresponders and store only the minimum suppression evidence. Apply opt-outs and complaints immediately, outside this waiting period.
- Review retention: Delete or anonymise old engagement events once they no longer support the stated purpose.
Illustrative sunset policy pseudocode
IF unsubscribe OR objection OR complaint OR invalid_address
THEN suppress_from_marketing = true
AND exit_sunset_workflow

IF marketing_permission_valid = false
THEN do_not_send_reconfirmation = true
AND suppress_from_marketing = true
AND exit_sunset_workflow

# Use signup date if no verified email action exists.
# Email actions include human clicks, replies, and preference updates.
IF subscription_age_days >= 180
AND days_since_last_verified_email_action_or_signup >= 180
AND (last_purchase IS NULL OR days_since_last_purchase >= 365)
AND (last_login IS NULL OR days_since_last_login >= 180)
THEN move_to = sunset_candidate

IF reconfirmation_sent = true
AND days_since_reconfirmation >= 30
AND no_intentional_confirmation_or_preference_update = true
THEN suppress_from_marketing = true

KEEP minimal_matching_identifier
KEEP suppression_reason
KEEP suppression_date
KEEP necessary_permission_evidence under its retention policy
DELETE old_event_detail when retention period ends
For reactivation programs, define who still has valid marketing permission, cap volume, and stop quickly when complaints or bounces rise. Require intentional confirmation before restoring routine campaigns. A separate plan for re-engaging inactive subscribers becomes useful.
Checks before and after sunsetting
A sunset policy should improve deliverability, but it is not a replacement for authentication, complaint handling, bounce processing, and reputation monitoring. Before the policy goes live, check that SPF, DKIM, DMARC, unsubscribe handling, bounce categories, and suppression imports are working. Otherwise the change looks clean in a spreadsheet while the sending system still leaks risk.
Send sample messages through Suped's email tester before and after a sunset change. The result will not prove inbox placement for every recipient, but it helps identify authentication and message-configuration problems before contacting the inactive segment.
Email tester
Send a real email to this address. Suped shows a results button when the test is ready.
?/43tests passed
After rollout, compare spam complaint rate, bounce rate, delivered volume, and engagement among remaining recipients. Track absolute clicks and conversions as well as rates: removing inactive addresses changes the denominator, so a higher click-through rate alone does not prove better inbox placement. Compare similar campaigns and seasonal periods before attributing a revenue change to the sunset window. If complaint rate stays high, inspect acquisition quality, expectations at signup, content, send frequency, and authentication.
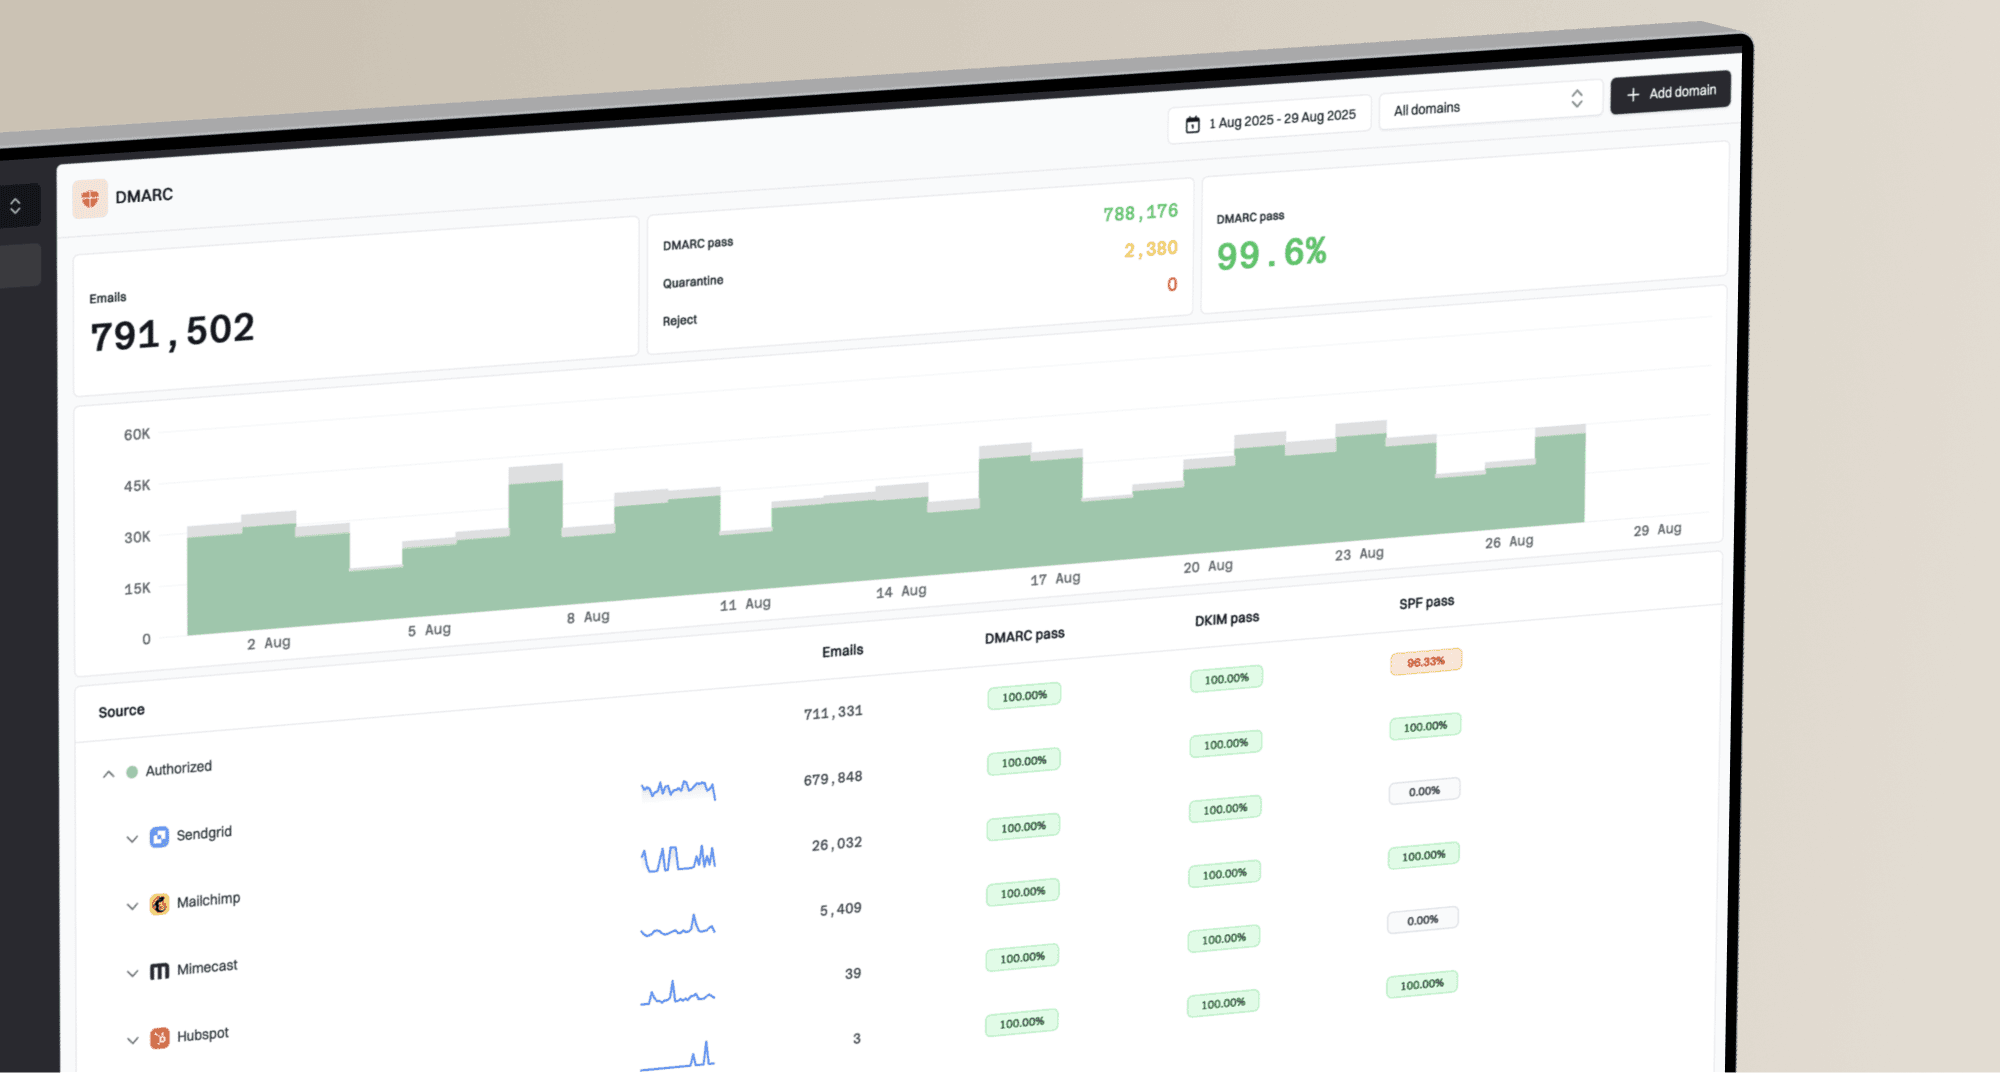
Suped's DMARC and email authentication product supports the controls around this workflow. Use DMARC monitoring to review sending sources and SPF, DKIM, and DMARC results during the rollout. Suped's blocklist monitoring helps identify domain or IP listings. Investigate authentication failures, unexpected source changes, and blocklist (blacklist) events alongside campaign results.
Issues page showing top issues, verified sources, unverified sources, and authentication pass rates
The sunset decision still belongs in the email platform or customer database. Suped supports the surrounding controls: whether legitimate sources pass authentication, whether unknown sources appear, whether policy changes create failures, and whether a domain or IP lands on a blacklist or blocklist during a risky campaign.
Use provider-specific complaint rates. Gmail recommends keeping the user-reported spam rate below 0.1% and preventing it from reaching 0.3% or higher. Yahoo requires a spam rate below 0.3%. Provider calculations use their own definitions, so an email platform's aggregate complaint rate is not interchangeable with those rates. Pause re-engagement batches when complaints or bounces rise rather than treating 0.3% as a safe operating target.
What to document for legal review
The document for legal should be short and concrete. Ask legal to approve a retention and suppression policy with clear purpose, data fields, timing, notices, and safeguards instead of asking them to bless "profiling" in the abstract.
- Purpose: Protect deliverability, respect recipient intent, and avoid retaining marketing data longer than needed.
- Data fields: Record subscription source and date, the permission evidence, lawful engagement fields, bounce and complaint status, and reconfirmation outcome.
- Excluded fields: Exclude sensitive categories, inferred traits, and tracking data collected without required consent or a documented exemption.
- Subscriber control: Provide a clear preference or unsubscribe route; send reconfirmation only while permission remains valid.
- Retention: Set separate purposes and retention criteria for suppression records, permission evidence, and detailed engagement history.
- Controls: Log the rule, approval date, data owner, suppression date, and reactivation exception path.
Do not rely on opens alone
Open tracking has privacy and accuracy problems. Some mail clients block images. Some privacy systems preload images. Some subscribers read in previews. A legal team has a fair reason to challenge an open-only rule.
- Better signal: Verified human clicks, replies, preference updates, and lawfully used customer activity give more context than opens alone.
- Cleaner proof: An intentional confirmation or preference submission gives stronger evidence than an automatic link fetch.
- Safer default: When the signal is weak, reduce frequency before suppression instead of deleting immediately.
- Required split: Keep transactional notices separate so account or legal messages still reach the recipient.
Document the Article 6 lawful basis for each purpose. If relying on legitimate interests, record the necessity and balancing assessment; that basis does not bypass electronic-marketing or tracking-consent rules. Under GDPR Article 21, an objection to direct marketing requires stopping that marketing, including related profiling. Keep that obligation separate from the discretionary inactivity threshold.
Sunset-policy checks and common mistakes
Best practices
Document the sunset purpose, data fields, review owner, and retention period before rollout.
Use lawful human activity and bounce data so open tracking is never the only inactivity signal.
Send a reconfirmation message only while marketing permission remains valid for that subscriber.
Keep suppression evidence minimal, durable, and separate from detailed engagement history.
Common pitfalls
Treating inactive suppression as a secret segmentation tactic creates avoidable legal friction.
Using a fixed six-month rule for every brand ignores cadence, seasonality, and buying cycles.
Deleting suppression records can cause accidental remailing after imports or platform changes.
Emailing to seek consent after an opt-out or without valid permission creates compliance risk.
Expert tips
Document the actual processing purpose; a retention label does not establish a lawful basis.
Keep transactional and required account messages outside the marketing inactivity workflow.
Use mailbox-provider language carefully; some guidance supports the outcome, not the exact term.
Review the policy after each major acquisition source change or deliverability incident.
An example six-month sunset policy
For a regular commercial program with enough delivered campaigns to assess engagement, a six-month inactivity candidate segment is a starting point. Where permission remains valid, send a reconfirmation message and suppress nonresponders after an illustrative 30-day response window. Extend the inactivity window for seasonal products and shorten it for high-frequency senders with clear complaint pressure.
Set a recurring policy review and repeat it after an acquisition-source change or deliverability incident. Monitor authentication, complaints, bounces, and blacklist or blocklist status during rollout. Require intentional confirmation or a preference update, together with valid marketing permission, before restoring an inactive contact. After an explicit opt-out, accept a new valid opt-in initiated by the subscriber; a purchase or login does not remove the suppression.