What DMARC policy settings are required for BIMI and how do I determine the best setting for sp=?
Published 25 Jul 2025
Updated 11 Oct 2026
12 min read
Summarize with
Updated on 11 Oct 2026: We clarified BIMI policy requirements and the checks needed to choose sp without disrupting legitimate mail.
For BIMI, both the organizational domain and the domain in the visible From address need an enforced DMARC policy. In practical terms, p= must be quarantine or reject, and any explicit sp= must also be quarantine or reject. A record with p=reject and sp=none does not meet BIMI's policy requirement.
The short recommendation is to keep p=reject for the root domain if it is already working, then move sp= to reject once legitimate subdomain senders pass DMARC and indirect delivery has been tested. Use sp=quarantine while reviewing remaining traffic after known senders are authenticated. It still requests spam placement for failing mail. Keep full enforcement and do not use t=y for a BIMI-ready policy.
MX records and sender reputation do not decide DMARC compliance. MX tells other servers where to deliver inbound mail. Sender reputation can affect whether a mailbox provider displays a BIMI logo, but the DMARC test depends on SPF or DKIM authentication plus a domain match with the visible From header. DMARC monitoring provides the evidence needed before changing enforcement.
DMARC policy requirements for BIMI
The BIMI implementation guide says DMARC must be at enforcement on the organizational domain and subdomains used for mail. It lists quarantine and reject as accepted policies and rejects none policies or legacy pct values below 100 percent. RFC 9989 now makes pct historic, so new records can omit it. If it remains for compatibility, keep it at 100.
- Set the root policy to p=quarantine or p=reject. If the domain is already stable at reject, keep it there.
- If publishing an explicit subdomain policy, use sp=quarantine or sp=reject. Do not use sp=none when the goal is BIMI. If sp is omitted, subdomains without their own DMARC record inherit p.
- Use full enforcement. Under RFC 9989, omit the historic pct tag and leave t absent or set it to n. If a legacy pct tag remains, use 100.
- Make sure every real sender passes DMARC through SPF or DKIM domain matching for the visible From domain.
BIMI minimum
The minimum root-domain policy is p=quarantine with full enforcement. An explicit sp=quarantine is sufficient; if sp is omitted, subdomains without their own record inherit p. For a new RFC 9989 record, omit pct and do not publish t=y. For controlled sending domains ready for reject, use p=reject and sp=reject, with reporting enabled so new senders do not drift outside policy.
BIMI policy threshold
How fully applied DMARC policies meet BIMI's policy requirement. Logo display also depends on the message and provider.
None
Fails
Monitoring only. BIMI policy requirements are not met.
Quarantine
Passes
Meets the DMARC policy requirement when fully applied. It can be a staging or ongoing policy.
Reject
Passes
Meets the DMARC policy requirement when fully applied. Review sender and indirect delivery results first.
Meeting the policy requirement and passing DMARC makes a message eligible for BIMI processing. It does not guarantee that the logo will appear because each mailbox provider applies its own display criteria. BIMI does not require adkim=s or aspf=s; the message needs to pass DMARC under the domain's configured matching mode. Relaxed matching accepts the same organizational domain, such as DKIM d=example.com for a visible From domain of news.example.com. Strict matching requires identical domains.
How to choose sp for subdomains
The sp tag controls the DMARC policy for existing subdomains that do not publish their own DMARC record. It applies to mail where the visible From domain is a subdomain, such as mail.example.com or news.example.com. It does not apply just because the return path or bounce domain is on a subdomain.
If a subdomain publishes its own DMARC record, that record's p= value takes priority for mail using the subdomain in the visible From address. Under RFC 9989, an sp= tag inside a subdomain-level DMARC record is ignored. A strict parent sp= setting still protects new and forgotten existing subdomains by default.
The decision should come from report data, not a DNS guess. List every observed visible From domain in aggregate reports, then group each source under the exact domain it uses. Each observed subdomain needs a clear owner and a decision on whether it should keep sending, supported by the sending platform and DMARC result. Compare reports with DNS records and the sending-system inventory because not every receiver sends reports.
That inventory matters because sp=reject requests rejection of failing mail. It works well for controlled sending streams. It can disrupt an old product notification or billing process if DKIM is broken and there is no matching SPF pass. sp=quarantine still risks spam placement for legitimate failures. Authenticate known senders before applying either enforced policy.
Use sp=quarantine
- Use it after known senders pass DMARC, while you review remaining traffic and indirect delivery.
- Receivers are asked to quarantine failing mail, which often means spam placement rather than rejection.
- Keep it when quarantine fits the subdomain's delivery needs; BIMI does not require a move to reject.
Use sp=reject
- Use it when legitimate senders pass DMARC reliably and indirect delivery has been tested.
- It requests rejection of failing mail. Receivers still apply their own filtering rules.
- Use it for controlled sending streams after checking forwarding and mailing lists.
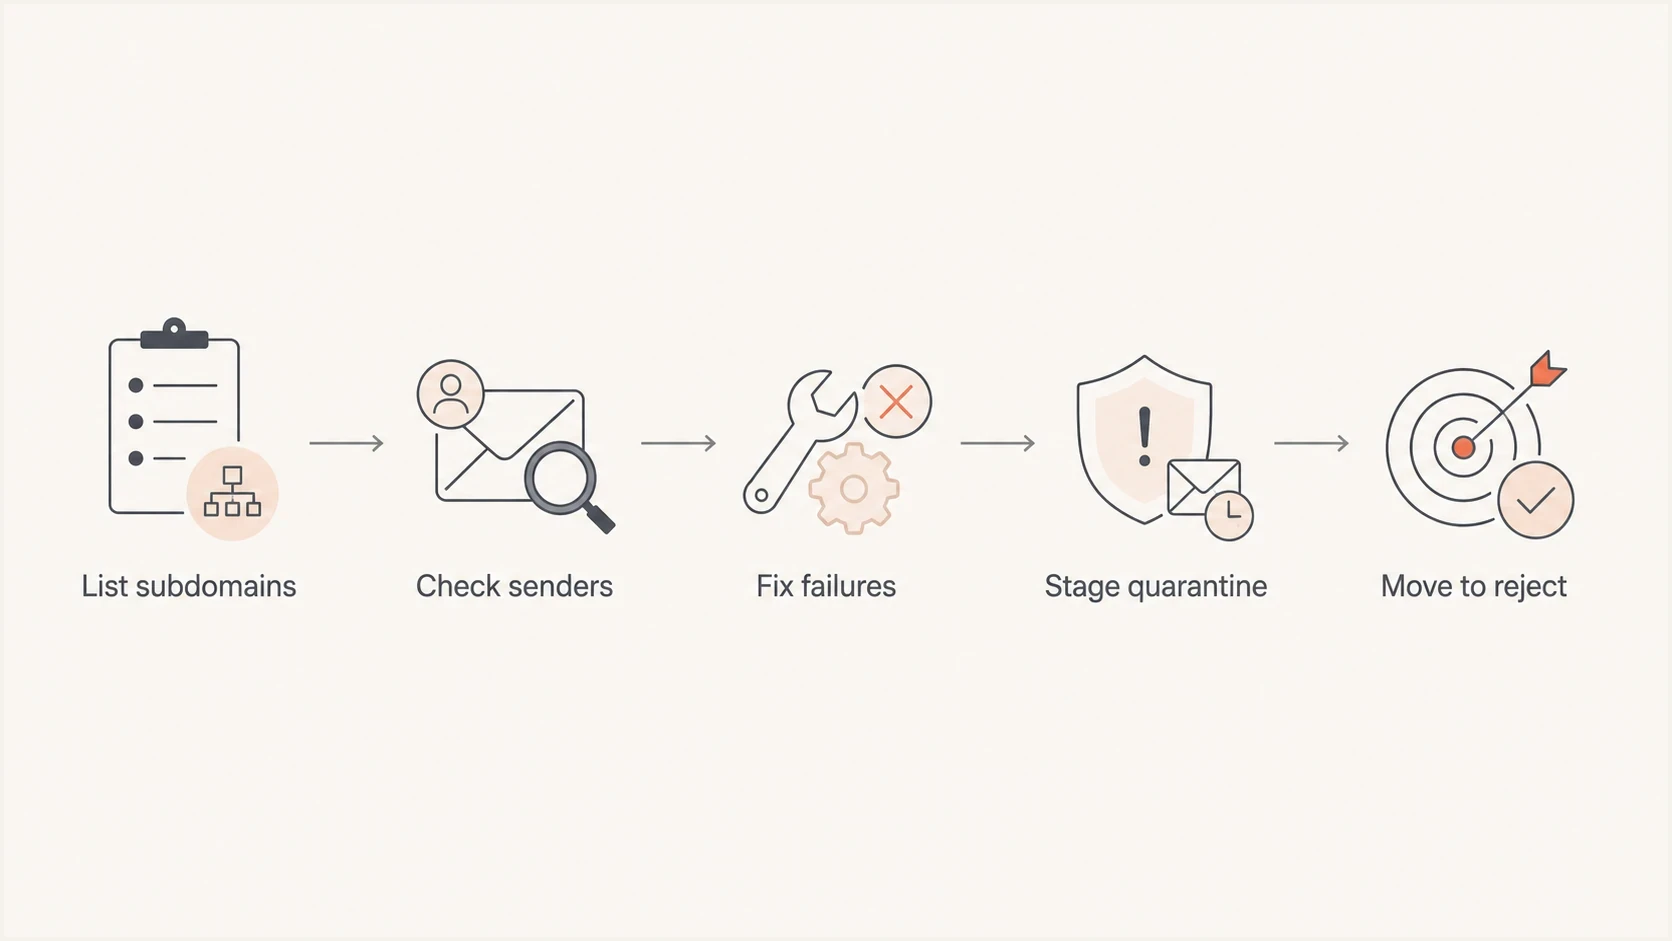
DMARC subdomain policy flowchart for BIMI: check senders and fix failures before moving to reject.
If no existing subdomains send mail, set sp=reject. Use the same setting for controlled sending subdomains after authentication and indirect delivery testing. Otherwise, use sp=quarantine once known senders authenticate, and review remaining failures before deciding whether reject fits.
What to verify before changing sp
Before changing sp=, collect proof that legitimate subdomain mail will not break. Review aggregate DMARC reports, group sources by visible From domain, and separate known senders from unexpected traffic. DMARC needs at least one passing SPF or DKIM identity with the required domain match. Sign legitimate mail with matching DKIM before reject because forwarding often breaks SPF.
Use a DMARC checker to confirm the DNS syntax, but do not stop there. Syntax only tells you the record can be read. Reports show whether real mail will pass after enforcement.
|
|
|
|---|---|---|
Visible From domains | Shows which subdomains need policy review. | All senders known |
DKIM domain | A passing DKIM signature must use a d= domain with the required match to the visible From domain. | Matching DKIM pass |
SPF domain | A passing SPF identity, normally the SMTP MAIL FROM domain, must have the required match to the visible From domain. | Matching SPF pass |
SPF lookups | SPF returns permerror when evaluation exceeds 10 mechanisms or modifiers that cause DNS queries, including nested includes. | 10 or fewer counted terms |
Subdomain DMARC records | A subdomain's own p policy overrides the inherited parent policy for that From domain. | Quarantine or reject for BIMI |
Effective policy | BIMI requires full enforcement rather than a testing policy. | No t=y; no pct below 100 |
Report analysis | Sources must be mapped before policy changes are safe. | Sources mapped |
Pre-change checks for BIMI and subdomain enforcement.
For a first pass, run a broad domain check. It catches obvious DMARC, SPF, and DKIM mistakes before report analysis. The check is not a replacement for report data, but it can find broken DNS quickly.
?
What's your domain score?
Deep-scan SPF, DKIM & DMARC records for email deliverability and security issues.
After the DNS check, inspect live report data for at least one normal sending cycle. A week can be enough for a small sender, but the review period must also cover less frequent billing, account, campaign, and batch mail. Before moving to reject, account for every expected sending cycle using reports and direct delivery tests, including forwarding or mailing lists where used.
DMARC record examples for BIMI
This record suits a controlled sending domain after sender review and indirect delivery testing. It keeps enforcement clear at the root and for existing subdomains, and it uses current RFC 9989 syntax.
Reject policy for root and subdomainsdns
_dmarc.example.com. 3600 IN TXT (
  "v=DMARC1; p=reject; sp=reject; "
  "rua=mailto:dmarc@example.com"
)
This staging record keeps the root domain at reject while existing subdomains remain at quarantine. It maintains BIMI-compatible enforcement without rejecting every subdomain failure immediately.
Reject root policy with quarantined subdomainsdns
_dmarc.example.com. 3600 IN TXT (
  "v=DMARC1; p=reject; sp=quarantine; "
  "rua=mailto:dmarc@example.com"
)
Common BIMI policy mistake
An enforced parent record does not override a subdomain's own p=none. Check _dmarc.news.example.com for mail from news.example.com, as well as _dmarc.example.com. The subdomain needs its own quarantine or reject policy to qualify.
If you are building the record from scratch, use the DMARC record generator to create the TXT value, then validate it in DNS after publishing.
When sp= is absent, an existing subdomain without its own DMARC record inherits the parent p= policy. Publishing sp= explicitly still makes the intended subdomain policy clear during reviews and future DNS changes.
What RFC 9989 changes for BIMI
RFC 9989 replaced the earlier DMARC specification. It makes pct historic and introduces t as a testing control. This changes how a new BIMI-ready record should express full enforcement, even though some BIMI and mailbox-provider documentation still describes the older pct=100 rule.
- Omit pct in a new RFC 9989 record. If an older record keeps the tag for compatibility, use only pct=100.
- Do not use t=y for BIMI. It asks receivers to apply a policy one level below the published policy. Omit t or use t=n.
- Use sp for existing subdomains covered by the organizational-domain record. A subdomain with its own record uses its own p policy.
- Use np=reject when you want an explicit reject policy for non-existent subdomains. np does not replace sp for subdomains that exist in DNS.
RFC 9989 Section 7.4 advises against reject for domains whose users post to Internet mailing lists. Quarantine remains valid for BIMI. Review forwarding and mailing-list delivery before choosing reject for an active subdomain.
What else BIMI requires after DMARC
DMARC enforcement is one prerequisite for Brand Indicators for Message Identification (BIMI). The BIMI implementation guide also requires logo preparation and a separate DNS record.
- Publish a BIMI TXT record at default._bimi.example.com for the default selector. Include v=BIMI1, with l= for the logo URL and a= for the certificate URL where required.
- Use a square SVG Tiny Portable/Secure (SVG Tiny PS) logo. Host BIMI files publicly over HTTPS so mailbox providers can retrieve them.
- Check the receiving provider's certificate rules. Gmail requires a Verified Mark Certificate (VMC) or Common Mark Certificate (CMC). A VMC also enables Gmail's verification checkmark; a CMC does not.
- For sending subdomains, verify each visible From domain's effective DMARC policy and BIMI record lookup. A subdomain BIMI record can override the organizational-domain logo.
BIMI does not improve inbox placement by itself. Providers still evaluate sender reputation and apply their own logo display criteria.
How Suped handles this workflow
Suped is our DMARC reporting and email authentication platform. For a BIMI rollout, it connects DMARC record checks, aggregate report analysis, policy changes, and alerts so the team can see which source needs a fix before moving sp= to reject.
Hosted DMARC configuration dialog showing policy controls, CNAME setup, and expanded advanced options
For this BIMI workflow, Suped's Hosted DMARC lets teams stage policy changes without repeated DNS edits. The domain can move through monitoring, quarantine, and reject while reports and issue detection stay in the same workflow.
- Group report data by visible From domain and sending source to build the subdomain inventory.
- Trace failed domain matching to SPF or DKIM so each legitimate sender has a specific fix.
- Stage and review policy changes before moving existing subdomains to reject.
- Alert on new DMARC failures after enforcement so newly added senders are caught.
The practical workflow is to find every subdomain sender, fix SPF or DKIM domain matching, confirm full enforcement, then monitor for new failures after BIMI mail becomes eligible for logo display.
Views from the trenches
Best practices
Inventory visible From subdomains before changing sp so no live sender is missed.
Authenticate known subdomain senders before staging quarantine to limit spam placement.
Keep rua reporting active after reject so new senders are caught before damage spreads.
Common pitfalls
Checking only the root domain hides subdomain senders that will break under sp reject.
Confusing return-path domains with visible From domains leads to the wrong DMARC fix.
Sending aggregate reports to a mailbox leaves too much work for enforcement decisions.
Expert tips
Treat BIMI as the last step after DMARC, DKIM, SPF, sender inventory, and logo work.
Make p and sp explicit in DNS so policy intent stays clear during future security audits.
Move slowly enough to cover periodic mail streams before rejecting subdomain failures.
Marketer view
Marketer from Email Geeks says BIMI requires DMARC enforcement on both the organizational domain and subdomains, with quarantine or reject as the acceptable policies.
2025-02-06 - Email Geeks
Marketer view
Marketer from Email Geeks says MX records and sender reputation do not decide DMARC compliance; SPF or DKIM must pass for the visible From domain.
2025-02-06 - Email Geeks
Recommended sp setting
If the root domain is already stable at p=reject, keep it there. Use sp=reject for controlled sending subdomains after sender review and indirect delivery testing. Quarantine also satisfies BIMI when it better fits an active subdomain.
If legitimate subdomain senders pass DMARC but indirect delivery still needs review, use sp=quarantine and review the reports under full enforcement. Move to sp=reject only when delivery tests support that choice. That follows a staged transition policy while keeping a BIMI-compatible policy.
Keep reporting active after the change because a broken source often appears only when a scheduled campaign or product process runs.
Frequently asked questions
No. BIMI requires an effective DMARC policy of p=quarantine or p=reject. Do not use t=y, and do not retain a legacy pct value below 100.
Yes. It keeps both policies at enforcement while subdomain delivery is reviewed. Authenticate known senders first because quarantine still affects failing legitimate mail. It can also remain the ongoing policy when it fits the subdomains.
Not by itself. The sp policy applies when an existing subdomain is used in the visible From header, not merely in the return path.
No. Existing subdomains without their own DMARC record inherit the parent p policy when sp is absent. Publishing sp explicitly makes the BIMI enforcement intent clear.
Yes, for non-sending subdomains that exist in DNS and do not have an overriding DMARC record. Under RFC 9989, np=reject explicitly covers non-existent subdomains. Without np, non-existent subdomains inherit sp, or p when sp is absent.
RFC 9989 makes pct historic, so new records should omit it. If an older record retains pct for compatibility, keep it at 100. Do not use t=y.