How does relaxed domain alignment work in DMARC and SPF?
Published 16 Apr 2025
Updated 2 Oct 2026
10 min read
Summarize with
Updated on 2 Oct 2026: We added guidance on delegated subdomains and clarified how relaxed SPF alignment interacts with DKIM and null return paths.
A message can pass DMARC through SPF when SPF passes for its return-path domain and DMARC discovers the same Organizational Domain for that domain and the visible From domain. For example, subdomain1.domain.com and subdomain3.domain.com are aligned for SPF when both resolve to domain.com. The return-path domain can be a sibling of the visible From subdomain.
The part that trips people up is that SPF itself does not know about DMARC alignment. SPF checks the IP against the SPF policy for the SMTP MAIL FROM identity, commonly exposed as the Return-Path. DMARC then checks whether that SPF-authenticated domain lines up with the Author Domain in the visible 5322.From field. For ongoing DMARC monitoring, check both pieces separately: did SPF pass, and did the SPF-authenticated domain line up with the From domain under DMARC rules?
When sibling subdomains align
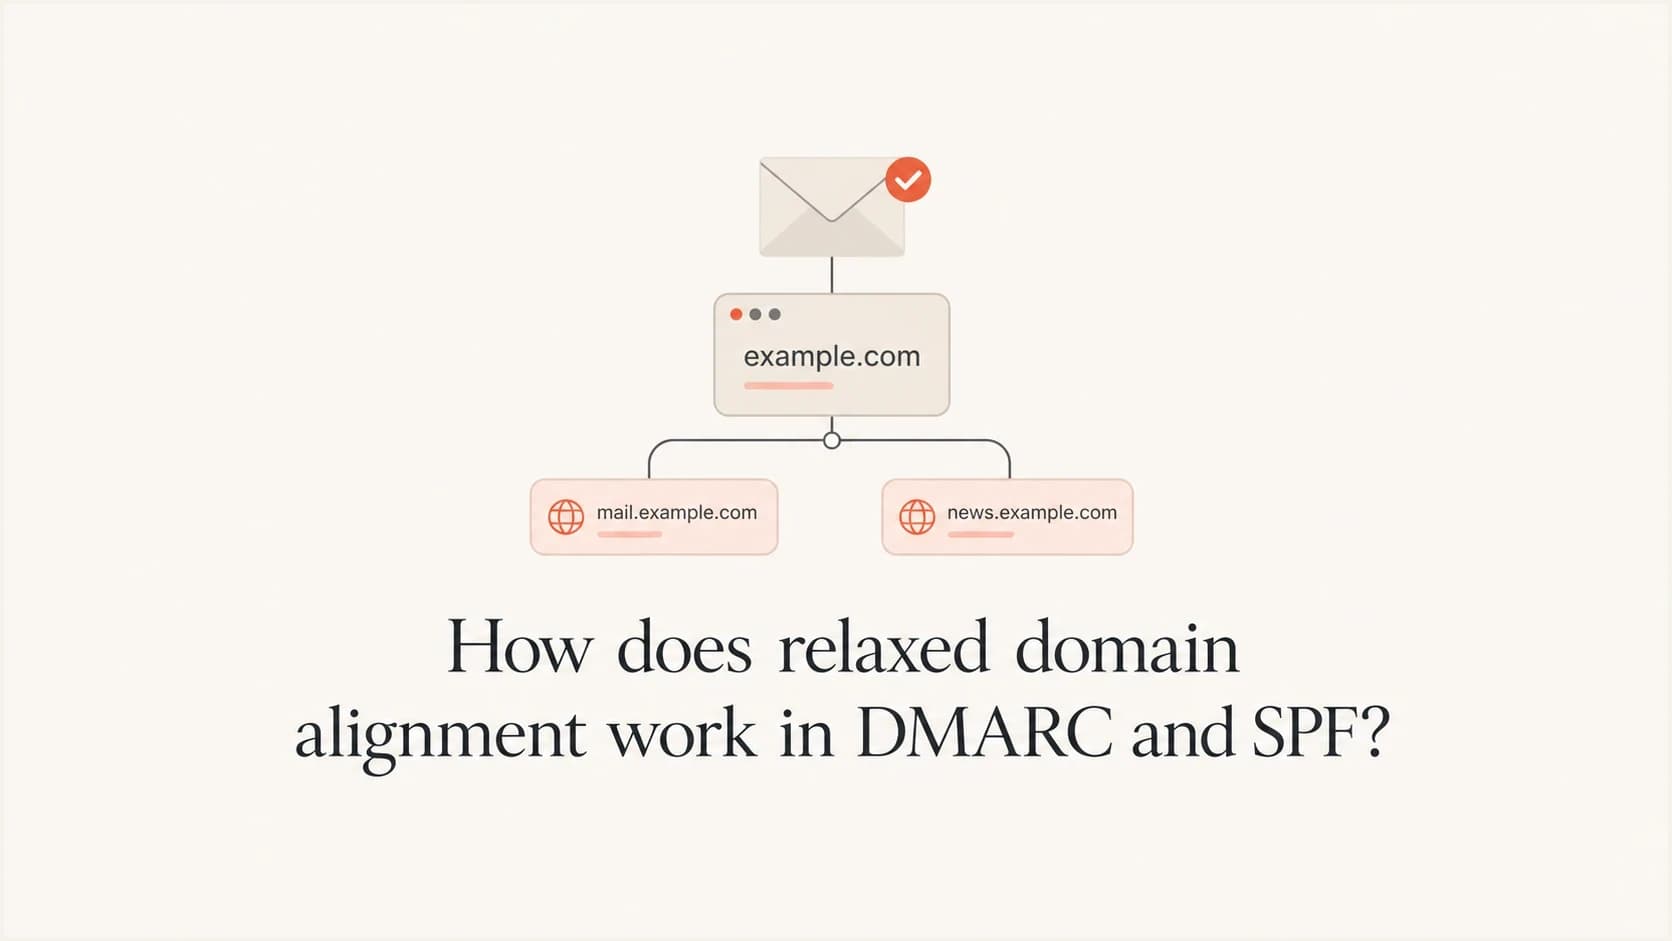
Relaxed SPF alignment in DMARC compares Organizational Domains, not the full hostname tree. If DMARC discovers the same Organizational Domain for two domains, it treats them as aligned for relaxed SPF alignment. That means a visible From domain at subdomain1.domain.com can pass DMARC through SPF when the return-path domain is subdomain3.domain.com, provided SPF passes for subdomain3.domain.com and DMARC discovers domain.com as the Organizational Domain for both.
- Same organization: Sibling subdomains pass relaxed DMARC SPF alignment when DMARC discovers the same Organizational Domain for both.
- SPF first: The sending IP still needs to pass SPF for the SMTP MAIL FROM identity used by DMARC.
- No inheritance: SPF does not walk up to the parent domain or across to another subdomain to find a record.
- DMARC decides: The relaxed comparison belongs to DMARC, after SPF has already authenticated a domain.
Practical rule
If the visible From domain and the SPF-authenticated domain have the same Organizational Domain under DMARC's discovery rules, relaxed SPF alignment passes. If their Organizational Domains differ, it fails unless DKIM gives DMARC another passing, aligned result.
How relaxed SPF alignment is calculated
DMARC works with two domain identities for this check. The first is the Author Domain, taken from the visible 5322.From field. The second is the SPF-Authenticated Identifier, which is the domain whose SMTP MAIL FROM identity passed SPF. Relaxed mode discovers the Organizational Domain for each identity and compares those results.
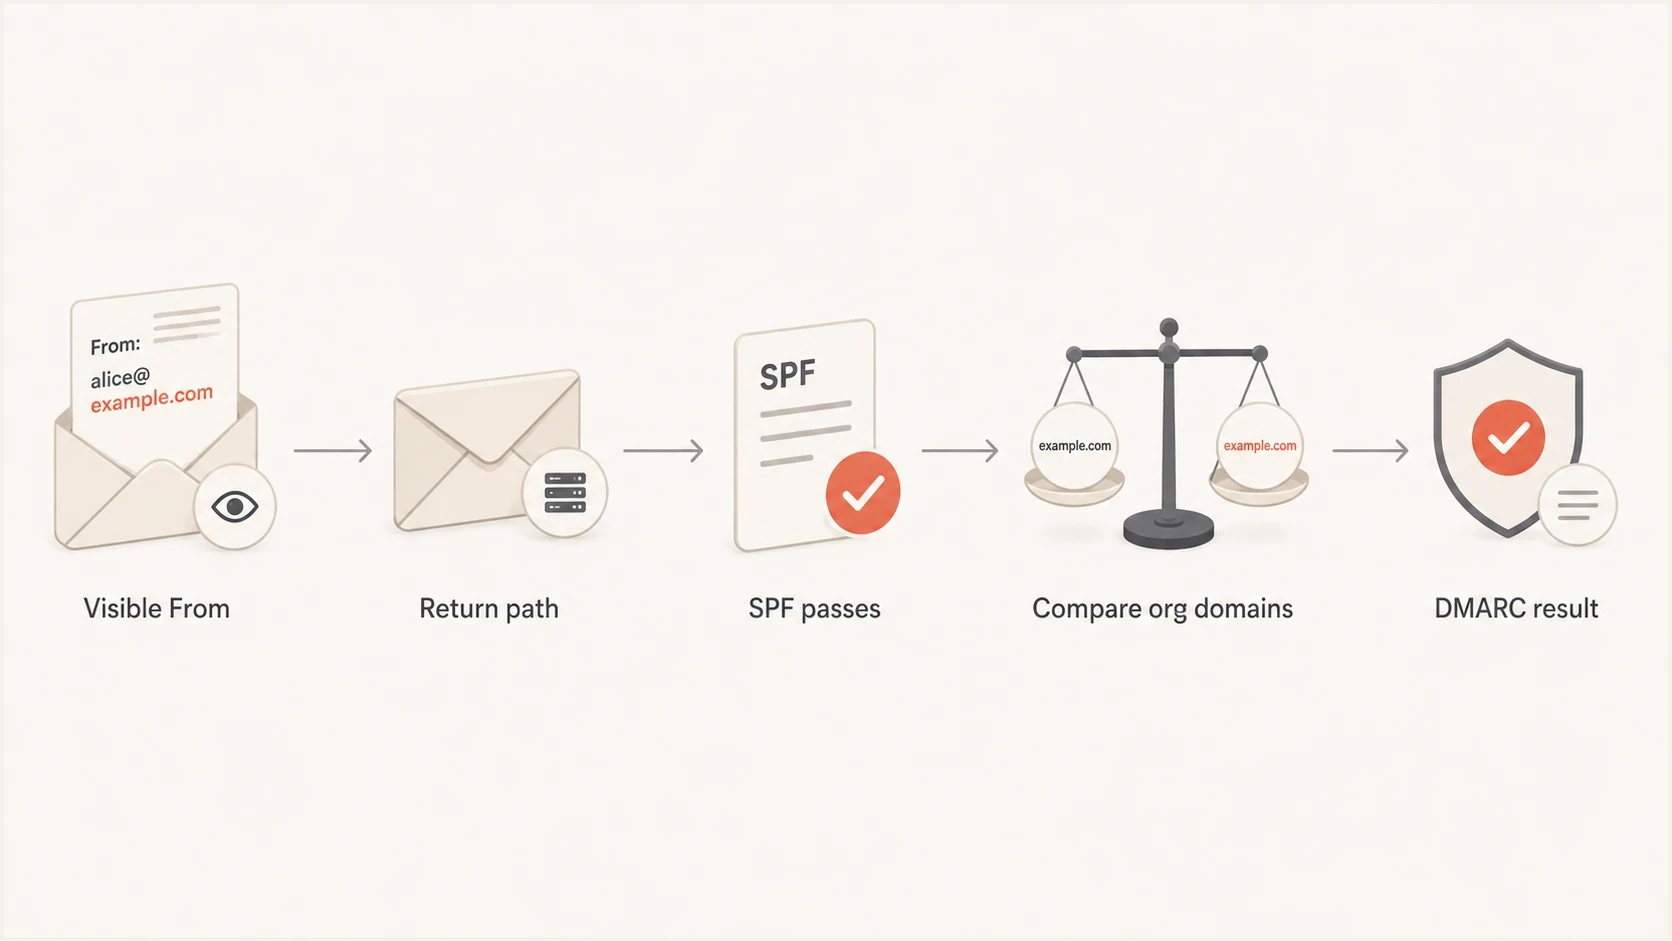
Flowchart showing SPF pass first, then DMARC relaxed organizational domain comparison.
For subdomain1.domain.com and subdomain3.domain.com, a typical DNS Tree Walk discovers domain.com as the Organizational Domain for both. That is enough for relaxed alignment. The same logic covers deeper names, such as a.b.domain.com, when DMARC discovers domain.com as their shared Organizational Domain.
|
|
|
|
|---|---|---|---|
subdomain1.domain.com | subdomain3.domain.com | Passes | Both have Organizational Domain domain.com |
subdomain1.domain.com | subdomain2.subdomain1.domain.com | Passes | Both have Organizational Domain domain.com |
subdomain1.domain.com | mail.other.com | Fails | The Organizational Domains differ |
news.example.co.uk | bounce.example.co.uk | Passes | Both have Organizational Domain example.co.uk |
Relaxed SPF alignment examples for one visible From domain, assuming the stated Organizational Domains are discovered.
The organizational boundary still matters in names such as example.co.uk, but current DMARC no longer determines that boundary by relying on a Public Suffix List. RFC 9989 uses a DNS Tree Walk over DMARC policy records. This is why current DMARC processing must inspect the relevant policy records instead of stripping labels based only on a suffix list.
What RFC 9989 changed
RFC 9989 now defines DMARC and obsoletes RFC 7489 and RFC 9091. The relaxed alignment rule remains the same: the Author Domain and an authenticated identifier have relaxed alignment when they share an Organizational Domain. The method for discovering that Organizational Domain has changed.
- DNS Tree Walk: Receivers query DMARC policy-record locations up the DNS tree for the Author Domain and each authenticated identifier that passed.
- Organizational boundary: The discovered DMARC policy records help determine which domain has the relevant administrative authority.
- Public suffix signals: A psd=y record marks a Public Suffix Domain, while psd=n can identify the current domain as the Organizational Domain.
- Migration differences: A receiver still using RFC 7489 and a Public Suffix List can reach a different answer in edge cases.
Operational impact
Common sibling-subdomain setups still have relaxed alignment when the Tree Walk discovers the same parent Organizational Domain. For delegated subdomains or public-suffix arrangements, publish explicit DMARC policy records and verify the discovered Organizational Domain instead of assuming that the registrable-looking label is decisive.
Relaxed alignment and delegated subdomains
Relaxed alignment also sets a trust boundary for delegated subdomains. If another party controls DNS for vendor.domain.com, it can publish SPF there and send mail with From: finance@domain.com and a MAIL FROM address at vendor.domain.com. When SPF passes and DMARC discovers domain.com as the Organizational Domain for both identities, that message can pass DMARC through SPF. The parent domain does not need to list the sender in its own SPF record.
Before delegating a subdomain, check who can change its SPF record and DKIM signing records. Where exact-domain separation is required, consider strict alignment after testing legitimate mail: aspf=s requires the MAIL FROM domain to equal the visible From domain, and adkim=s applies the same exact-domain rule to DKIM. Review aggregate reports after any change because either mechanism can still produce a DMARC pass when it authenticates and aligns.
Why an SPF pass differs from alignment
Separate SPF authentication from DMARC SPF alignment because they answer different questions. SPF asks whether the sending IP is authorized by the SPF record for the SMTP MAIL FROM identity. DMARC asks whether the domain authenticated by SPF matches the visible From domain closely enough for the chosen DMARC alignment mode.
SPF authentication
- Question: Is this IP allowed to send for the SMTP MAIL FROM identity?
- Domain used: The MAIL FROM domain. For a null reverse path, SPF constructs the MAIL FROM identity as postmaster at the HELO domain; DMARC still uses the MAIL FROM SPF result.
- Record lookup: The receiver starts with the SPF record published at the domain being evaluated.
DMARC SPF alignment
- Question: Does the SPF-authenticated domain match the visible From domain?
- Domain used: The SPF-Authenticated Identifier and the Author Domain are compared.
- Mode choice: Relaxed mode compares Organizational Domains, while strict mode compares exact domains.
This difference explains the common surprise: subdomain3.domain.com can be aligned with subdomain1.domain.com under DMARC, but SPF will not pass if subdomain3.domain.com has no SPF record or its record does not authorize the sending IP. SPF does not check domain.com as a fallback, and it does not inspect subdomain1.domain.com just because that is the visible From domain.
Do not rely on SPF inheritance
Publish SPF at the actual return-path domain used by the sender, or configure the sender to use a return-path domain that already has the right SPF record. Parent-domain SPF does not automatically cover child subdomains.
Relaxed and strict SPF alignment examples
The DMARC record controls SPF alignment mode through the aspf tag. If the tag is missing, DMARC uses relaxed SPF alignment by default. The adkim tag controls DKIM alignment independently and also defaults to relaxed. Set either tag deliberately when the policy needs to be obvious to future administrators.
Relaxed SPF alignment in a DMARC recorddns
_dmarc.domain.com. TXT
"v=DMARC1; p=quarantine; aspf=r; adkim=r;"
"rua=mailto:dmarc-reports@domain.com"
With that record, a message using From: user@subdomain1.domain.com and Return-Path: bounce@subdomain3.domain.com can pass DMARC through SPF if the sending IP passes SPF for subdomain3.domain.com and the Tree Walk discovers domain.com as the Organizational Domain for both identities. The shared Organizational Domain determines relaxed alignment.
Strict SPF alignment in a DMARC recorddns
_dmarc.domain.com. TXT
"v=DMARC1; p=quarantine; aspf=s; adkim=r;"
"rua=mailto:dmarc-reports@domain.com"
With strict SPF alignment, the same message fails DMARC through SPF because the return-path domain and visible From domain are not identical. Strict mode requires subdomain1.domain.com to match subdomain1.domain.com exactly for SPF alignment. A different sibling subdomain fails strict SPF alignment even when SPF authentication itself passes.
SPF alignment modes
How much domain matching DMARC requires after SPF passes.
Relaxed
aspf=r
Organizational Domains match
Strict
aspf=s
Full domains match exactly
If you want a deeper split between SPF authentication and alignment, the related explanation on SPF authentication and alignment is useful when a report says SPF passed but DMARC still failed.
How to test relaxed SPF alignment
Start troubleshooting with the actual message headers, not assumptions about the sending platform. The visible From domain, the SMTP MAIL FROM domain, the SPF result, and the DMARC result explain most relaxed alignment outcomes.
- Find From: Read the visible header From domain, not the display name shown in the inbox.
- Find MAIL FROM: Read the envelope sender domain that SPF evaluated, commonly shown in Return-Path or Authentication-Results.
- Check SPF: Confirm the sending IP passed SPF for that MAIL FROM domain.
- Compare domains: Use DMARC's RFC 9989 DNS Tree Walk to discover both Organizational Domains when alignment is relaxed.
- Check DKIM: Compare the d= domain of a passing DKIM signature with the visible From domain. Aligned DKIM can pass DMARC when SPF does not.
Forwarding often changes the sending IP and can rewrite the MAIL FROM identity, so SPF authentication or alignment can fail at the final receiver. An aligned DKIM signature can still produce a DMARC pass if the signature survives the forwarding path.
If a sending service uses an unrelated Return-Path domain, configure a custom MAIL FROM domain under your Organizational Domain where the service supports it. Otherwise, configure the service to sign with an aligned DKIM domain so DMARC can pass through DKIM.
A focused DMARC checker helps validate the published record, but header inspection still matters because SPF alignment depends on the domain used in a real message.
DMARC checker
Look up a domain's DMARC record and catch policy issues.
?/7tests passed
For production domains, check whether each mail stream uses a predictable return-path domain. Random or sender-controlled bounce domains create reports that look inconsistent until each source is mapped to its actual envelope sender.
DMARC record detail view showing SPF, DKIM, DMARC, rDNS diagnostics, and DNS records
Monitor alignment across sending sources
Suped's product helps when the question moves from one example message to a domain-wide operating problem. A single header explains one delivery. Aggregate DMARC reports show which sources use each return-path domain, which ones pass SPF, which ones pass DKIM, and which ones fail alignment.
The source breakdown and issue views in Suped separate legitimate sender configuration problems from mail that should be rejected. The workflow is to identify the source, confirm its return-path domain, fix SPF or DKIM on that source, then advance the DMARC policy after legitimate traffic has aligned results.
What Suped helps you see
- Source mapping: Which platforms send mail for each domain and subdomain.
- Issue detection: Whether SPF, DKIM, DMARC, DNS, or policy staging needs attention.
- Hosted controls: Hosted SPF, SPF flattening, hosted DMARC, and hosted MTA-STS without constant DNS edits.
- Reputation checks: Blocklist (blacklist) monitoring alongside authentication and deliverability signals.
For teams managing several sending sources, Suped combines DMARC reporting with hosted policy controls, alerts, and multi-tenant reporting. If DNS ownership is fragmented across teams, hosted DMARC makes policy staging a managed workflow instead of a chain of manual TXT record changes.
Views from the trenches
Best practices
Compare organizational domains after SPF passes, not before checking the SPF result.
Document each sender's return-path domain so reports map cleanly to real systems.
Use relaxed SPF alignment unless strict matching has a clear operational purpose.
Common pitfalls
Assuming SPF records inherit from parent domains creates false confidence in subdomains.
Treating sibling subdomains as misaligned hides valid relaxed DMARC pass results.
Ignoring DKIM alignment makes SPF issues look worse than the actual DMARC outcome.
Expert tips
Test real headers because dashboards often hide the envelope sender domain detail.
Set aspf deliberately so future DNS reviewers understand the intended matching rule.
Use aggregate reports to spot senders that rotate return-path domains unexpectedly.
Marketer view
Marketer from Email Geeks says sibling subdomains under the same organizational domain count as aligned in relaxed DMARC SPF alignment.
2023-07-26 - Email Geeks
Marketer view
Marketer from Email Geeks says any hostnames below the same organizational domain can satisfy relaxed alignment when SPF has passed.
2023-07-26 - Email Geeks