Netcraft Fraud Detection vs.
DMARCLytics in 2026
Netcraft Fraud Detection

DMARCLytics
vs.
We tested Netcraft Fraud Detection and DMARCLytics for 90 days across a corporate domain, a marketing subdomain, and a parked domain, with Microsoft 365, Google Workspace, SendGrid, Mailchimp, and a support desk sender connected. Netcraft handled the unauthorized spoof as a broader fraud case, but its DMARC workflow felt secondary to enterprise threat operations. DMARCLytics was the more direct choice for routine DMARC reporting and policy work, although its plan labels and MSP path need confirmation before purchase.
Published 6 Nov 2025
Updated 20 Aug 2026
8 min read
Summarize with
Netcraft Fraud Detection
Enterprise fraud detection with DMARC processing
Starts at
Not publicly listed
Best fit
Enterprises already running a fraud response program
In one line
We found capable fraud triage with DMARC evidence, but buyers requiring published starter pricing should keep Suped in the shortlist.
DMARCLytics
DMARC reporting for SMBs and growing teams
Starts at
From £9.99 / month
Best fit
Teams that want a direct path to enforcement
In one line
We moved our three-domain test toward enforcement faster because hosted records and the policy wizard kept the work in one place.
Suped
The better option. Hosted SPF, DMARC, and MTA-STS on every plan. Published pricing. Monthly plans. No long contract required.
Learn about Suped
Choose Netcraft for fraud operations, DMARCLytics for daily DMARC work
Pick Netcraft Fraud Detection if
Choose Netcraft when DMARC evidence feeds an enterprise fraud response team
Our spoof sample became a tracked fraud case with evidence and escalation context.
Microsoft 365 and Google Workspace traffic could be reviewed beside wider impersonation signals.
The support handoff matched a formal enterprise onboarding and response process.
Not publicly listed
Pick DMARCLytics if
Choose DMARCLytics when a small team owns DMARC policy movement
We added all three domains with clear DNS steps and immediate aggregate parsing.
SendGrid and Mailchimp were easier to classify in the sender views.
The policy wizard made the move toward quarantine easier to explain internally.
From £9.99 / month
Consider Suped if
Choose Suped for guided fixes, hosted records, and simpler ownership
Require fixes that name the sender, record change, and responsible owner.
Check automatic issue detection and alert quality with real authentication edge cases.
Compare MSP account separation against published starter pricing of $19 per month.
Free plan available
The differences that actually change your week
Netcraft Fraud Detection
DMARCLytics
Suped
DMARC report analysis
Turns authentication reports into traffic and failure views.
DMARC processing and visualisation are available within the enterprise service.
Aggregate RUA parsing is included on every listed plan.
Aggregate and forensic report analysis
Source detection
Names the services behind raw IP addresses and authentication results.
Strong threat-source evidence, with manual ownership work for ordinary senders.
Sender and host views are strongest on paid tiers.
Named sending sources with owner context
Forward detection
Separates forwarding behavior from an unauthorized sender.
Forwarding remained visible in evidence, but needed analyst interpretation.
Report drilldowns exposed the SPF failure path and surviving DKIM result.
Forwarding detection and explanation
Spoof detection
Flags unauthorized use of the visible From domain.
A core strength tied to fraud verification and countermeasure workflows.
Spoof and brand impersonation alerts are listed across plans.
Spoof detection with DMARC context
Notifications and alerts
Routes material authentication changes without excessive noise.
Enterprise threat notifications support formal escalation.
Email alerts are basic on Starter and configurable on paid tiers.
Actionable alerts with noise controls
Reporting
Provides dashboards, exports, and recurring stakeholder views.
Real-time dashboards, CSV export, and regular reports are available.
Volume, sender, host, geography, and deliverability reporting vary by tier.
Dashboards, exports, and scheduled reports
API
Makes report or event data available to other systems.
A secure JSON API is part of the enterprise service.
No public API entitlement was confirmed in the listed plans.
API access for operational workflows
Multi-tenancy
Separates domains, teams, or client accounts for delegated work.
Enterprise account separation is available, but it is not an MSP-first workflow.
Multi-team and Agency options are custom tier capabilities.
MSP workspaces with client separation
SPF flattening
Keeps SPF within lookup limits through managed flattening.
No hosted SPF flattening was available in our DMARC workflow.
Hosted SPF is listed, but flattening was not confirmed.
Managed SPF flattening
Hosted DMARC
Hosts and updates the DMARC policy record.
Reporting and processing only in the tested workflow.
Hosted DMARC begins on the Professional or Business tier.
Hosted DMARC records
Hosted SPF
Hosts and manages the SPF policy record.
No hosted SPF capability was tested or publicly listed.
Hosted SPF is checked every minute on the middle paid tier.
Hosted SPF records
Hosted MTA-STS
Hosts the policy needed to enforce inbound transport security.
Not included in the reviewed DMARC service scope.
No hosted MTA-STS entitlement was confirmed.
Hosted MTA-STS and TLS reporting
Blocklists and reputation
Checks sending IPs against blocklist and blacklist signals.
Broader threat intelligence is available, but no DMARC-focused blacklist monitor was confirmed.
An IP blocklist reputation checker begins on the middle paid tier.
Blocklist and blacklist monitoring
Automatic issue detection
Surfaces record and authentication problems without manual report hunting.
Fraud detection is automated, but DMARC configuration fixes remained manual.
Smart alerts and policy guidance identify common DMARC issues.
Automated issue detection with next steps
AI copilot
Explains report data and helps operators choose a next action.
No DMARC copilot was present in the tested workflow.
Guardian AI is basic on Starter and gains history on paid tiers.
AI guidance for diagnosis and fixes
DNS monitoring
Watches authentication records for changes or failures.
DNS authentication monitoring was not part of the tested fraud workflow.
Hosted DMARC and SPF records receive frequent checks on paid tiers.
Continuous authentication record monitoring
Self hostable
Can run on infrastructure controlled by the customer.
Cloud service only.
Cloud service only.
Cloud service only
Free trial/free tier
Allows evaluation before a paid commitment.
A 14-day trial is publicly listed for the wider service.
A 14-day trial is clear; the claimed free tier conflicts with the pricing card.
Free plan plus 14-day unrestricted trial
Ten dimensions, scored from 0 to 10
We scored each product against a fixed editorial rubric based on our 90-day setup, sender tests, policy work, alerts, account separation, exports, pricing review, and support handoff. Higher is better in every row.
DMARCLytics leads the DMARC workflow; Netcraft leads the fraud response handoff
DMARCLytics scored higher on enforcement speed because we could add three domains, identify SendGrid and Mailchimp, and use its policy wizard without moving between systems. Netcraft scored higher for support and escalation because the unauthorized spoof entered a formal fraud workflow with stronger evidence handling. Neither product earned points for unsupported capabilities: Netcraft had no hosted SPF or MTA-STS and no DMARC blacklist monitor, while DMARCLytics had no hosted MTA-STS and only a partially clear MSP package.
Netcraft Fraud Detection score
45/100
DMARCLytics score
70/100
Netcraft Fraud Detection
45/100
DMARC enforcement
5.5
Customer support
8.5
Source resolution
7.5
Setup and onboarding
6.0
MSP workflows
4.0
Alerting and integrations
7.0
Hosted SPF and MTA-STS
0.0
Blocklist monitoring
0.0
Pricing transparency
2.0
Time to enforcement
4.5
DMARCLytics
70/100
DMARC enforcement
8.0
Customer support
7.0
Source resolution
8.0
Setup and onboarding
8.0
MSP workflows
6.5
Alerting and integrations
5.5
Hosted SPF and MTA-STS
6.5
Blocklist monitoring
6.5
Pricing transparency
6.0
Time to enforcement
8.0
Feature set
Fraud depth vs DMARC breadth
DMARCLytics wins the DMARC workflow; Netcraft wins fraud scope
We would choose DMARCLytics for day-to-day source classification and policy movement, while Netcraft makes more sense when DMARC evidence must enter a wider fraud detection and countermeasure operation. Buyers who require guided fixes and automatic issue detection should score Suped alongside both products because neither reviewed workflow closed every test case without manual judgement.
Netcraft Fraud Detection
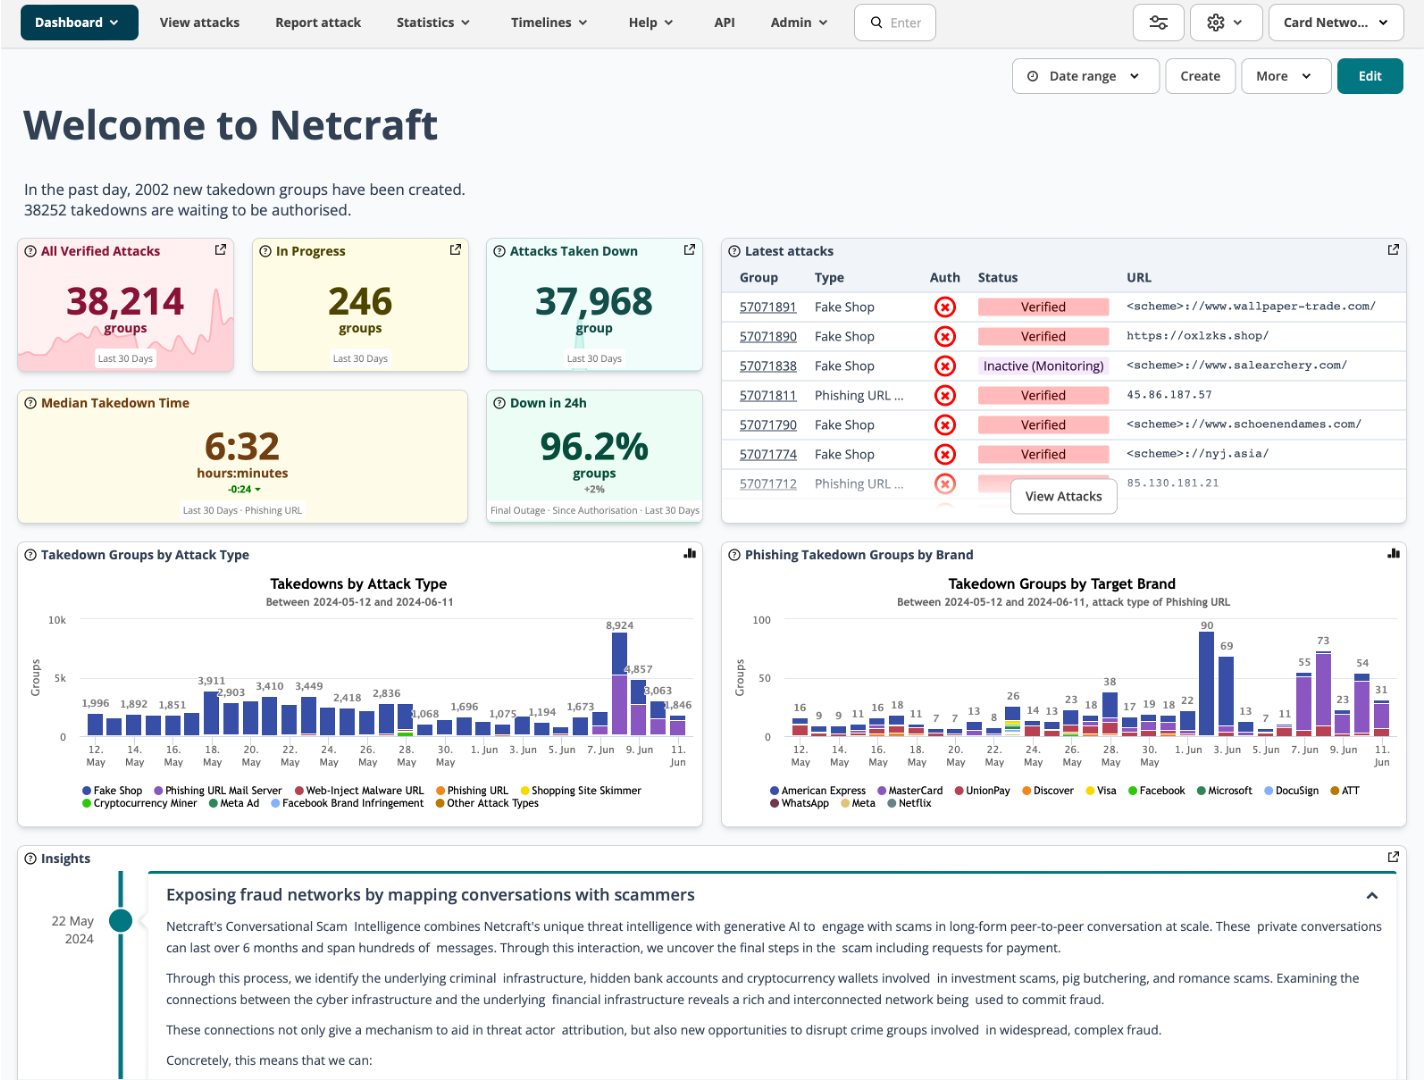
Microsoft 365 spoof evidence grouped
Google Workspace forwarding stayed visible
Fraud cases extend beyond DMARC
DMARCLytics
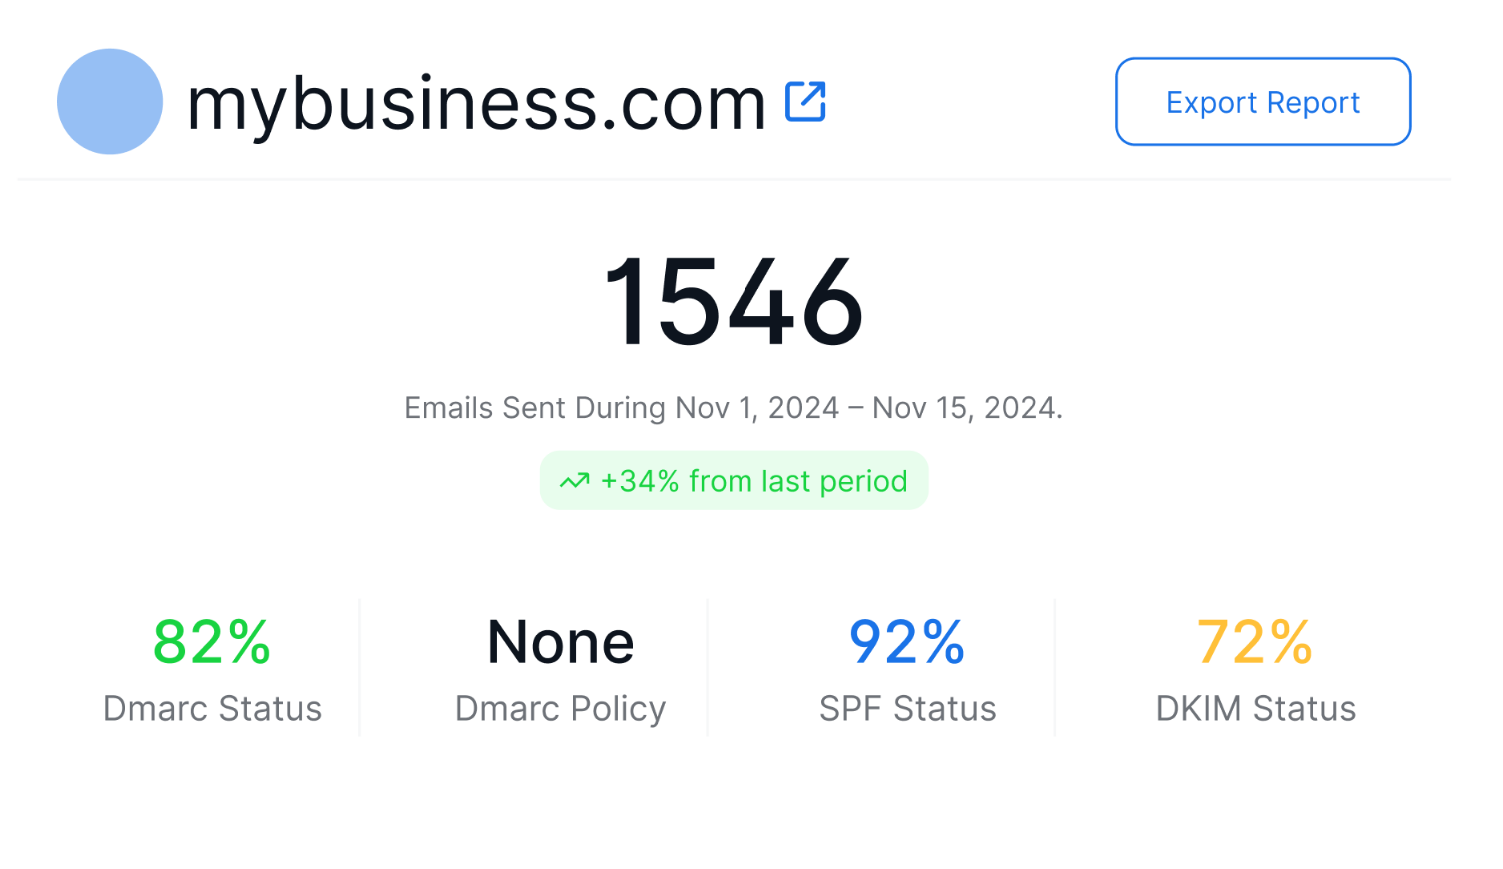
SendGrid and Mailchimp resolved quickly
Unknown support sender classified
Subdomain DKIM retained context
Netcraft grouped the unauthorized spoof with evidence useful to a fraud analyst, and it preserved enough detail to compare Microsoft 365 with Google Workspace traffic. The forwarded message showed an SPF failure and surviving aligned DKIM result, but we had to interpret that authentication edge case ourselves before clearing it. Its scope beyond DMARC was useful, although routine policy movement never felt like the center of the product.
DMARCLytics identified SendGrid and Mailchimp in sender views with less manual work, and its host drilldowns helped us classify the unknown support desk sender. The DKIM pass on our marketing subdomain retained the parent-domain policy context, which made the result easier to explain. Hosted DMARC, hosted SPF, smart alerts, and the policy wizard gave it broader coverage for an operator who owns authentication rather than fraud takedowns.
User experience
Control vs guidance
DMARCLytics gets operators to answers faster
DMARCLytics gave us the shorter path between a failed authentication result and a policy action. Netcraft gave us more control around evidence and escalation, but the interface assumed a fraud operations process rather than a small team checking DMARC each morning.
Netcraft Fraud Detection

Three assets received formal onboarding
Unknown sender required case detail
Forwarding needed analyst explanation
DMARCLytics

Three domains connected quickly
Unknown sender surfaced by volume
Drilldown explained SPF forwarding
Netcraft onboarding treated our corporate domain, marketing subdomain, and parked domain as assets within a broader protection scope. That produced a deliberate setup and a clear enterprise handoff, but finding the unknown support desk sender required opening the case detail and tracing the host evidence. The forwarded mail SPF failure was visible, although the interface did not plainly explain why aligned DKIM still allowed DMARC to pass.
DMARCLytics let us add the same three domains with shorter DNS instructions and began organizing aggregate traffic quickly. We found the unknown sender through a volume change, opened its host view, and marked it trusted after checking the support desk configuration. Its drilldown connected the forwarded SPF failure to the surviving DKIM alignment, so the explanation was easier to hand to a non-specialist owner.
Support
Enterprise handoff vs self-service
Netcraft has the stronger escalation model; DMARCLytics is easier to start
Netcraft fit the buyer who expects scoped onboarding, a defined support handoff, and help escalating a confirmed fraud event. DMARCLytics suited the team that wants to configure DNS itself and bring support into a specific record or plan question.
Netcraft Fraud Detection
Formal enterprise onboarding path
DNS handoff included scope review
Fraud escalation had clear ownership
DMARCLytics

Self-service DNS steps worked
Priority help requires paid tiers
Enterprise engineer needs custom plan
Netcraft's setup expectations were closer to an enterprise engagement than a self-serve DMARC trial. The DNS handoff for our three domains was deliberate, and the unauthorized spoof had a clear route into verification and escalation. That approach gave us confidence for a formal response program, but it increased the effort required before routine DMARC reporting felt operational.
DMARCLytics made the initial DNS handoff easier through direct record instructions, and we could complete most onboarding without scheduling an enterprise session. Email support was the expected route for our Starter questions, while priority help and a dedicated DMARC engineer depended on higher tiers. We would confirm escalation timing and the Enterprise SLA before relying on it for a time-sensitive spoof incident.
Suitability
Enterprise fit vs operator fit
Netcraft fits centralized fraud teams; DMARCLytics fits hands-on DMARC owners
We would route a large enterprise with an established fraud response function to Netcraft and an SMB with a named DMARC owner to DMARCLytics. MSPs should also score Suped's client separation and alert quality against both options, because Netcraft's account model felt enterprise-led and DMARCLytics left its Agency packaging unclear.
Netcraft Fraud Detection

Enterprise domains stay centrally governed
Client handoff needs external process
Recurring reports favor security teams
DMARCLytics
SMB domain grouping felt natural
Multi-team controls require Enterprise
Agency packaging needs confirmation
Netcraft kept the corporate domain, marketing subdomain, and parked domain inside a controlled enterprise scope, and its reports could support a central security review. Account separation was workable for internal business units, but recurring client reports and handoff notes required more process outside the tested interface. We see the best fit in an enterprise where a fraud team already owns escalation and procurement.
DMARCLytics made domain grouping and recurring DMARC review more natural for an SMB operator. Team roles and multi-team controls exist on higher tiers, but the Agency reference did not match the main plan table, so we would verify client separation, recurring report delivery, and offboarding before an MSP rollout. The faster sender classification and policy workflow still made it the more practical daily tool in our test.
What each tool feels like after 90 days of real use
What Netcraft Fraud Detection felt like after 90 days of real use
Netcraft Fraud Detection
By day 30, Netcraft felt less like a standalone DMARC console and more like one input to an enterprise fraud operation. We could trace the unauthorized spoof, retain evidence, and understand its escalation path, but sender ownership for ordinary Microsoft 365, Google Workspace, and support desk traffic took extra analyst work.
By day 90, the approach made sense when we treated DMARC as one detection channel among wider impersonation threats. Routine policy work remained slower because hosted authentication records, a DMARC policy wizard, and plain-language forwarding guidance were not part of the tested workflow.
Where it wins
Unauthorized spoof became a structured case
Fraud evidence supported formal escalation
API and CSV supported downstream analysis
Enterprise onboarding established clear ownership
Where it lags
Commercial pricing required a sales process
Routine source ownership stayed manual
No hosted authentication records
No DMARC-focused blocklist monitoring
Pricing
Not publicly listed
Free tier
No confirmed free tier
Onboarding
Scoped enterprise handoff
G2 rating
0 / 5
What DMARCLytics felt like after 90 days of real use
DMARCLytics
By day 30, DMARCLytics had become the easier morning check. We could compare Microsoft 365 with Google Workspace, find SendGrid and Mailchimp in sender views, and investigate the unknown support desk sender without turning every anomaly into a security case.
By day 90, hosted DMARC, hosted SPF, and the policy wizard had made the path toward quarantine clearer. We still wanted firmer answers on the Starter price conflict, API availability, MTA-STS hosting, and the exact Agency account model before treating it as the default for an MSP.
Where it wins
Three-domain onboarding stayed quick
Known senders resolved with less work
Policy wizard supported enforcement planning
Forwarded mail retained authentication context
Where it lags
Starter pricing statements conflict
Agency packaging remains unclear
No confirmed hosted MTA-STS
API entitlement was not confirmed
Pricing
From £9.99 / month
Free tier
Unclear; 14-day trial confirmed
Onboarding
Self-service DNS setup
G2 rating
0.0 / 5
Pricing
Netcraft Fraud Detection
DMARCLytics
Suped
Small
1 domain, up to 1k emails / month.
Not publicly listed as of May 15, 2026
Commercial DMARC scope requires a tailored quote, with no small-domain list plan.
£9.99 / month
Starter covers 3 root domains and 150,000 emails, but its free-plan wording conflicts.
$0 / month
Free plan covers 1 domain and 1,000 monthly emails.
Medium
2 domains, up to 100k emails / month.
Not publicly listed as of May 15, 2026
No commercial volume band maps this usage to a fixed price.
£9.99 / month
Starter remains within its stated domain and monthly email limits.
Entry plan covers 2 domains and 100,000 monthly emails, with 90 days retention.
Large
10 domains, up to 1 million emails / month.
Not publicly listed as of May 15, 2026
Public-sector reference tiers do not publish matching domain or message limits.
£30 / month
Professional or Business covers 10 root domains and 3 million monthly emails.
10 domains and 1,000,000 monthly emails, with 365 days retention.
Enterprise
Over 20 domains and 1 million emails / month.
Not publicly listed as of May 15, 2026
The quote depends on covered brands, threat types, service level, and countermeasure scope.
Custom
Enterprise lists unlimited domains and volume, with final retention and MSP terms to confirm.
20 domains and 2,500,000 monthly emails, with 365 days retention. Unlimited domains/emails negotiable.
No prices in this table are estimated. DMARCLytics figures are public list prices in GBP per month excluding VAT, checked May 15, 2026; annual billing is advertised at a discount, but the eligible plans need confirmation. Netcraft's commercial prices were not public on that date; its £36,000 yearly DMARC public-sector reference was excluded because it is not a guaranteed commercial list price.
If you cannot decide between the two, maybe the answer is Suped
Suped
Get started
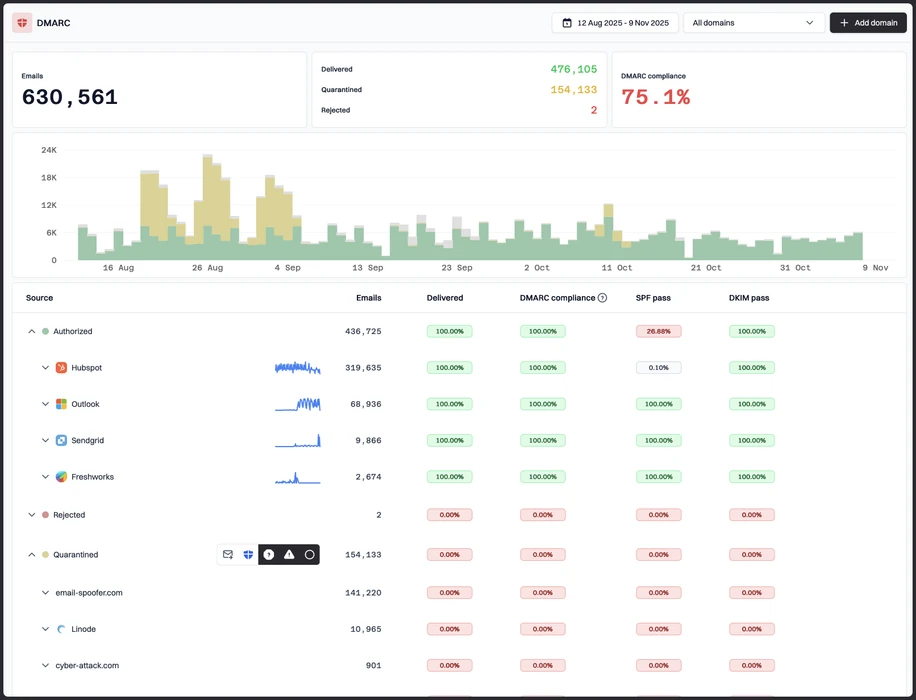
Turn unknown senders into owned fixes
Suped links sending-source identification to guided next steps, reducing the manual ownership work we encountered in Netcraft when classifying the support desk sender.
Keep hosted authentication together
Suped combines hosted DMARC, SPF, and MTA-STS, covering the MTA-STS gap we found in DMARCLytics and the hosted-record gap in Netcraft.
Price MSP operations before rollout
Suped publishes a $7 per-domain MSP rate with client separation, avoiding Netcraft's quote-only entry and DMARCLytics' unclear Agency packaging.
The difference was significant. We moved from limited visibility to a much clearer dashboard. Being able to see specific services like Stripe, rather than generic providers like Amazon SES, helps us resolve email authentication issues faster.
Markus Hugenschmidt, Managing Director, Jam Cyber
Migrating from Netcraft Fraud Detection or DMARCLytics?
We have done the migration enough times to know the shape.
Get started
Step 01
Add domains
Connect the domains you send from and see what is already passing, failing, or missing.
Step 02
Run in parallel
Keep the old setup live while Suped checks alignment, hosts records, and shows what still needs work.
Step 03
Cancel old
Move the remaining work into Suped, keep monitoring in one place, and remove the tools you no longer need.
Frequently asked questions
How MONEYME proactively strengthens domain security and unlocks higher email engagement with Suped
See how MONEYME uses Suped
How cybersecurity specialist Jam Cyber delivers scalable DMARC protection with Suped
See how Jam Cyber uses Suped
How Vision Australia maintains full DMARC enforcement across a large domain portfolio with Suped
See how Vision Australia uses Suped
How The POP Team turns domain checks and DMARC visibility into client ready delivery work
See how The POP Team uses Suped
How DigiBean simplified DMARC monitoring and improved email security for their MSP clients
See how DigiBean uses Suped
How Alliance Group moved from reactive guesswork to proactive email management with Suped
See how Alliance Group uses Suped