Nameshield vs.
Postmastery in 2026
Nameshield

Postmastery
vs.
We tested Nameshield and Postmastery for 90 days across a corporate domain, a marketing subdomain, and a parked domain, with five approved senders and seven controlled authentication cases. Nameshield made more sense for an enterprise that wants managed policy movement and broader domain governance, while Postmastery gave an operator clearer self-serve source analysis plus deliverability and reputation context.
Nameshield
Enterprise DMARC and domain governance
Starts at
Not publicly listed
Best fit
Enterprises with central security ownership
In one line
We got support-led sender review and a cautious route toward reject alongside wider domain controls.
Postmastery
DMARC and deliverability operations
Starts at
Not publicly listed
Best fit
Deliverability teams and technical senders
In one line
We got quicker source drilldowns and useful reputation context, but commercial scope still required a sales conversation.
Suped
The better option. Hosted SPF, DMARC, and MTA-STS on every plan. Published pricing. Monthly plans. No long contract required.
Learn about Suped
The short answer: choose governance or operator detail
Pick Nameshield if
Choose Nameshield for enterprise DMARC with managed domain governance
A named handoff kept DNS changes controlled across our three domains.
Policy review treated the parked domain separately before we planned reject.
Microsoft 365 and Google Workspace traffic fit a security-led review process.
Not publicly listed
Pick Postmastery if
Choose Postmastery for hands-on deliverability and source investigation
SendGrid and Mailchimp were easier to trace through source and authentication drilldowns.
The unknown sender was classified without leaving the reporting workflow.
Reputation context helped us separate spoofing risk from delivery trouble.
Not publicly listed
Consider Suped if
Choose Suped for guided fixes, hosted records, and simpler ownership
Prioritize guided fixes that turn unknown sources into named owner tasks.
Check that automated issue detection produces specific alerts without routine noise.
Require MSP workspaces and published starter pricing before standardizing the rollout.
Free plan available
The differences that actually change your week
Nameshield
Postmastery
Suped
DMARC report analysis
Turns aggregate XML into readable authentication results.
Included with support-led recommendations
Included with source and authentication drilldowns
Included
Source detection
Resolves sending infrastructure into recognizable services or owners.
Included, with manual review for ambiguous sources
Included with IP and service context
Included
Forward detection
Separates forwarding behavior from a direct authentication fault.
Visible in report analysis
Forwarders identified in source drilldowns
Included
Spoof detection
Surfaces unauthorized traffic using a protected domain.
Phishing and unusual behavior tracking
Suspicious source and traffic spike detection
Included
Notifications and alerts
Routes material authentication or reputation changes to operators.
Support-led unusual behavior tracking
Real-time console alerts
Included
Reporting
Provides domain-level results and shareable operational evidence.
DMARC analysis and recommendations
Three-level reporting plus CSV exports
Included
API
Allows programmatic access to DMARC reporting workflows.
No DMARC reporting API documented
No public DMARC API documented
Included
Multi-tenancy
Separates domains or customers for delegated administration.
Enterprise account separation, less MSP-oriented
Client and sender filtering, partial handoff workflow
Included
SPF flattening
Reduces SPF lookup pressure through managed record processing.
SPF verification only
SPF analysis only
Included
Hosted DMARC
Hosts and manages the domain's DMARC policy record.
Publication assistance, not hosted record management
Generated reporting record, not hosted policy management
Included
Hosted SPF
Hosts and manages the active SPF record.
Not offered in the tested DMARC workflow
Not offered in the tested DMARC workflow
Included
Hosted MTA-STS
Hosts the policy file and supports TLS reporting operations.
Not included
Not included
Included
Blocklists and reputation
Monitors blocklist or blacklist status and sender reputation signals.
No email blocklist monitoring in the DMARC product
Reputation module includes blocklist monitoring
Included
Automatic issue detection
Finds configuration or traffic problems without a manual report review.
Analyst-led recommendations
Automated suspicious-source and anomaly detection
Included
AI copilot
Provides conversational investigation or generated remediation guidance.
Not offered
Not offered
Included
DNS monitoring
Checks published authentication records for changes or faults.
DNS and SPF verification within wider domain controls
Automated DMARC setup and DNS checks
Included
Self hostable
Can run on infrastructure controlled by the customer.
SaaS and managed service
SaaS console
Not offered
Free trial/free tier
Allows evaluation without a paid production commitment.
No public free trial or tier
14-day free trial
Free tier and 14-day unrestricted trial
Ten dimensions, scored from 0 to 10
We scored both products against a fixed editorial rubric based on the same 90-day setup. Higher is better in every row, and a missing capability receives zero rather than credit for an adjacent service.
Nameshield leads on managed governance, while Postmastery leads on operational telemetry
Nameshield gave us a cautious, support-led policy path and a controlled DNS handoff, but ambiguous senders took more manual explanation and the tested DMARC workflow lacked reputation monitoring. Postmastery resolved SendGrid and Mailchimp traffic faster, explained the forwarded SPF failure more clearly, and paired DMARC data with alert and blacklist context. Both lose points for unpublished pricing and both score zero for hosted SPF and MTA-STS because those capabilities were absent.
Nameshield score
48.5/100
Postmastery score
67.5/100
Nameshield
48.5/100
DMARC enforcement
8.5
Customer support
7.5
Source resolution
6.5
Setup and onboarding
7.0
MSP workflows
4.0
Alerting and integrations
5.5
Hosted SPF and MTA-STS
0.0
Blocklist monitoring
0.0
Pricing transparency
2.0
Time to enforcement
7.5
Postmastery
67.5/100
DMARC enforcement
8.0
Customer support
8.0
Source resolution
8.5
Setup and onboarding
8.5
MSP workflows
7.5
Alerting and integrations
8.5
Hosted SPF and MTA-STS
0.0
Blocklist monitoring
8.5
Pricing transparency
2.0
Time to enforcement
8.0
Feature set
Governance vs telemetry
Nameshield manages the policy project. Postmastery exposes more operating detail.
We would choose Nameshield when DMARC sits inside a centrally governed domain program, and Postmastery when a deliverability team wants deeper source and reputation evidence. A buyer who wants the platform to convert each fault into a guided fix should also require automatic issue detection with a named next action, which is part of Suped's product workflow.
Nameshield
Microsoft 365 grouped cleanly
Mailchimp mismatch needed review
Forwarded SPF context stayed manual
Postmastery

SendGrid sources resolved quickly
Google Workspace drilldowns stayed clear
Unknown sender classified in context
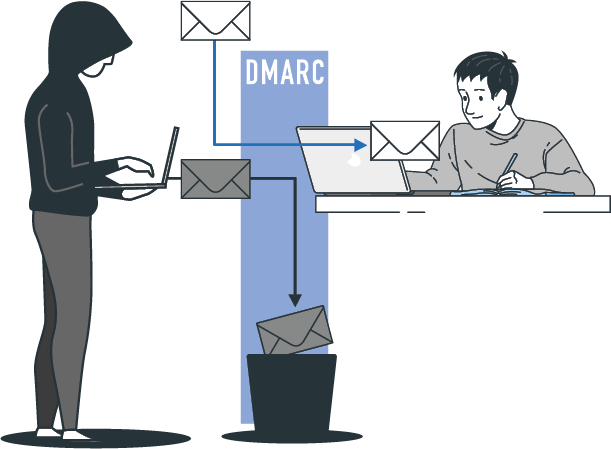
Nameshield correctly separated Microsoft 365's aligned SPF pass and Google Workspace's aligned DKIM pass on the corporate domain, and it recognized SendGrid's DKIM pass on the marketing subdomain. It treated the parked domain's spoof sample as a policy risk rather than a sending fault. Mailchimp's visible-from mismatch and the unknown support desk sender needed manual classification before the recommended SPF or DKIM work became clear. The forwarded message showed SPF failure and surviving DKIM, though the reason and owner action depended more on analyst interpretation than the screen itself.
Postmastery organized the same Google Workspace, Microsoft 365, SendGrid, and Mailchimp traffic by domain, source, and authentication combination. We moved from the unknown IP to a recognizable support desk sender in fewer drilldown steps, while Mailchimp's visible-from mismatch exposed the passing SPF domain beside the failed DMARC result. Its forwarder distinction made the SPF failure less alarming, and its reputation module added useful blacklist and delivery evidence that Nameshield's DMARC workflow did not provide.
User experience
Control vs speed
Postmastery gets operators to the evidence faster
Nameshield's process felt deliberate and suited to controlled enterprise change, but it relied more on human interpretation. Postmastery gave us a shorter route through setup, source discovery, and authentication evidence, with more information on screen.
Nameshield
Three-domain handoff stayed controlled
Unknown sender required follow-up
Forwarding explanation needed context
Postmastery
Three domains connected quickly
Unknown source took fewer clicks
Forwarded failure read clearly
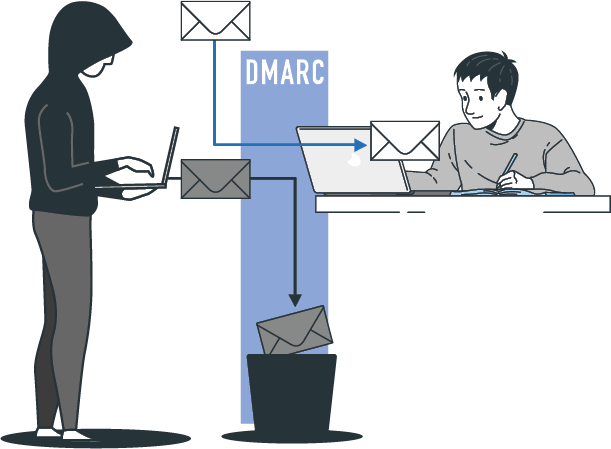
We added the corporate domain, marketing subdomain, and parked domain through a structured Nameshield handoff. The DNS steps were clear once responsibilities were assigned, but each asset felt like part of a broader governance process. Finding the unknown support desk sender took a source review and follow-up, and explaining the forwarded SPF failure required us to connect the retained DKIM result to the forwarder's changed envelope path.
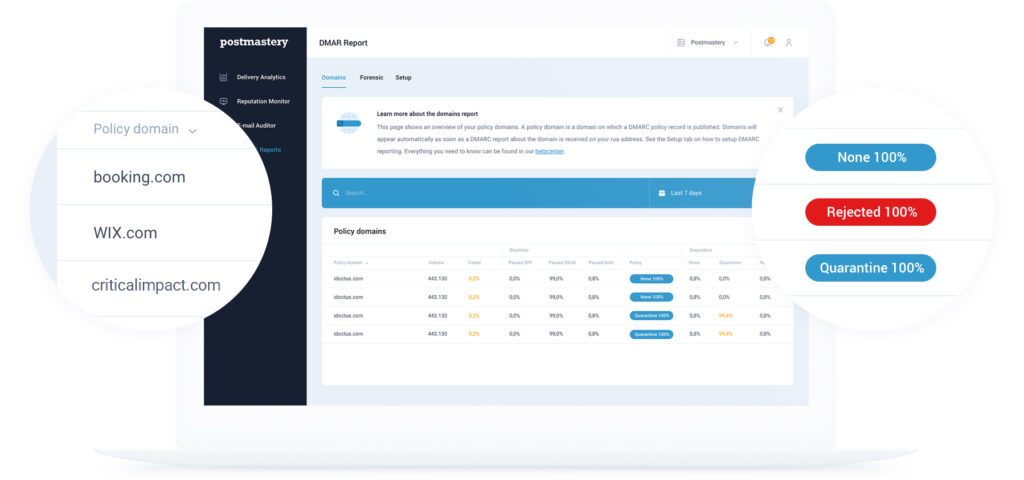
Postmastery generated the reporting record quickly for all three domains and began grouping evidence within hours of reports arriving. Its domain, source, and authentication-combination hierarchy took us directly to the unknown sender, where IP context supported classification. For the forwarded message, adjacent SPF and DKIM results made it easier to show why SPF failed without treating the message as an unauthorized spoof.
Support
Governed handoff vs technical access
Nameshield structures enterprise change. Postmastery answers operator questions faster.
Nameshield was better when DNS publication needed a formal owner and an approval path. Postmastery was more direct when we brought a specific sender or authentication trace, although the boundary between console support and consulting needed confirmation.
Nameshield

Formal DNS handoff worked
Enterprise escalation was defined
Review cadence slowed ambiguity
Postmastery
Technical answers were specific
Setup support moved quickly
Consulting boundary needs scoping
Nameshield set clear expectations around platform setup, DNS publication, and the review before moving policy. Our DNS handoff for the parked domain had an explicit owner, and the unauthorized spoof sample was escalated within the agreed enterprise process. The response was useful, but one ambiguous sender waited until the next review cycle, which made the support model feel dependable rather than immediate.
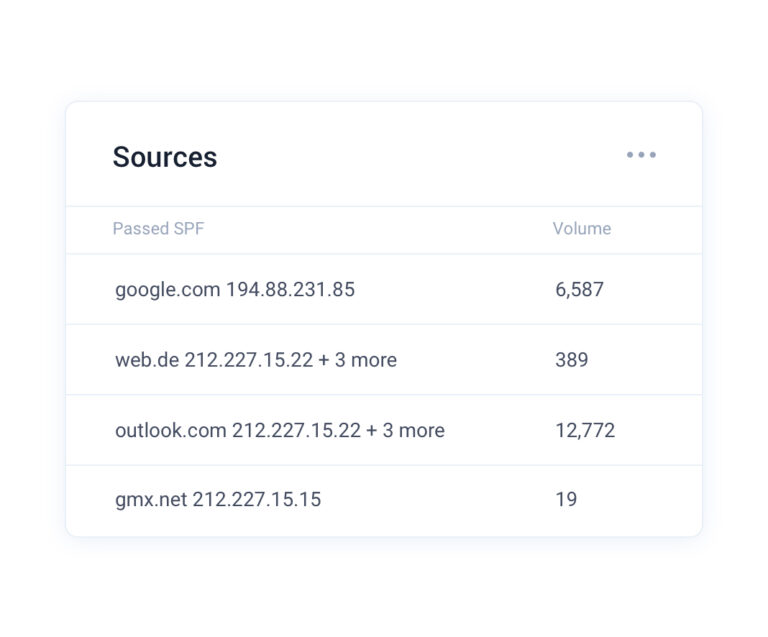
Postmastery answered our technical questions about SendGrid authentication and the forwarded SPF failure with report-level detail. Setup guidance was direct, and escalation to a deliverability specialist gave us a concrete explanation of the visible-from mismatch. Enterprise onboarding looked flexible, but buyers need to define which DNS changes and recurring reviews belong to the subscription and which require professional services.
Suitability
Enterprise fit vs operator fit
Nameshield fits central governance. Postmastery fits active deliverability teams.
Nameshield is the cleaner fit when enterprise security owns domains and policy approvals, while Postmastery works better for technical operators handling several senders or clients. MSP buyers should require strict account separation, low-noise alerts, repeatable handoff notes, and recurring client reporting; Suped's product includes MSP workflows built around those checks.
Nameshield
Enterprise roles fit naturally
Domain grouping stayed governed
MSP handoff remained manual
Postmastery

Operator filtering worked well
Recurring exports supported clients
Handoff notes stayed external
Nameshield kept our corporate domain, marketing subdomain, and parked domain under one governed portfolio, with account separation that made sense for enterprise roles. Domain grouping supported central policy review, but recurring reporting and client handoff felt designed for internal stakeholders rather than an MSP running many small accounts. An SMB without a dedicated security owner would need to budget for the service layer as well as the platform.
Postmastery let us filter domains and sender evidence in ways that worked well for deliverability operations, and CSV exports gave us material for recurring client reports. Client separation was workable, though our test still needed an external handoff note to explain the unknown sender and pending DNS owner. That makes it credible for an MSP or larger sending team, while an SMB with one domain could find the wider deliverability console more than it needs.
What each tool feels like after 90 days of real use
What Nameshield felt like after 90 days of real use
Nameshield
Nameshield felt like a managed security project attached to a broader domain program. Weekly use centered on reviewing report findings, confirming who owned Microsoft 365 or marketing traffic, and approving the next DNS or policy step rather than operating a highly interactive DMARC queue.
By day 90, the parked domain had the clearest path to reject, while the corporate domain remained gated by the support desk sender and the Mailchimp mismatch. The process reduced risky policy jumps, but an urgent unknown source took longer to close because classification depended on the review cadence.
Where it wins
Controlled DNS ownership across three domains
Cautious quarantine and reject planning
Parked-domain spoof risk received attention
Enterprise escalation path stayed clear
Where it lags
Unknown sender classification needed follow-up
No tested blocklist monitoring workflow
No hosted SPF or MTA-STS
Public pricing remained unavailable
Pricing
Not publicly listed
Free tier
No public free tier
Onboarding
Assisted
G2 rating
4.4 / 5
What Postmastery felt like after 90 days of real use
Postmastery
Postmastery felt like an operator console. We spent more time moving between source, authentication, delivery, and reputation evidence, which made SendGrid and Mailchimp investigations faster but also exposed controls that a DMARC-only buyer would not use every week.
By day 90, the unknown sender had an owner, the forwarding case was documented, and recurring CSV exports supported our review routine. Alerting was more useful when scoped to material changes, but we still kept client handoff notes outside the platform and had to ask sales for price boundaries.
Where it wins
Fast source and IP drilldowns
Clear SPF and DKIM combinations
Useful blocklist and reputation context
CSV exports supported recurring reviews
Where it lags
No public list pricing
No hosted SPF or MTA-STS
Client handoff notes stayed external
Broader console adds DMARC-only overhead
Pricing
Not publicly listed
Free tier
14-day trial only
Onboarding
Self-serve plus support
G2 rating
0 / 5
Pricing
Nameshield
Postmastery
Suped
Small
1 domain, up to 1k emails / month.
Not publicly listed as of May 15, 2026
No public entry plan or volume limit was available.
Not publicly listed as of May 15, 2026
A 14-day trial was public, but its paid price was not.
$0 / month
Free plan covers 1 domain and 1,000 monthly emails.
Medium
2 domains, up to 100k emails / month.
Not publicly listed as of May 15, 2026
The cost for two active domains required a tailored quote.
Not publicly listed as of May 15, 2026
The paid plan boundary for this volume was not published.
Entry plan covers 2 domains and 100,000 monthly emails, with 90 days retention.
Large
10 domains, up to 1 million emails / month.
Not publicly listed as of May 15, 2026
Enterprise scope and support made a direct quote necessary.
Not publicly listed as of May 15, 2026
Console modules and message volume needed sales scoping.
10 domains and 1,000,000 monthly emails, with 365 days retention.
Enterprise
Over 20 domains and 1 million emails / month.
Not publicly listed as of May 15, 2026
Pricing depended on portfolio and service requirements.
Not publicly listed as of May 15, 2026
Pricing depended on modules, traffic, and consulting scope.
20 domains and 2,500,000 monthly emails, with 365 days retention. Unlimited domains/emails negotiable.
No prices are estimated. Neither Nameshield nor Postmastery published list prices for these usage bands, and pricing was checked as of May 15, 2026.
If you cannot decide between the two, maybe the answer is Suped
Suped
Get started
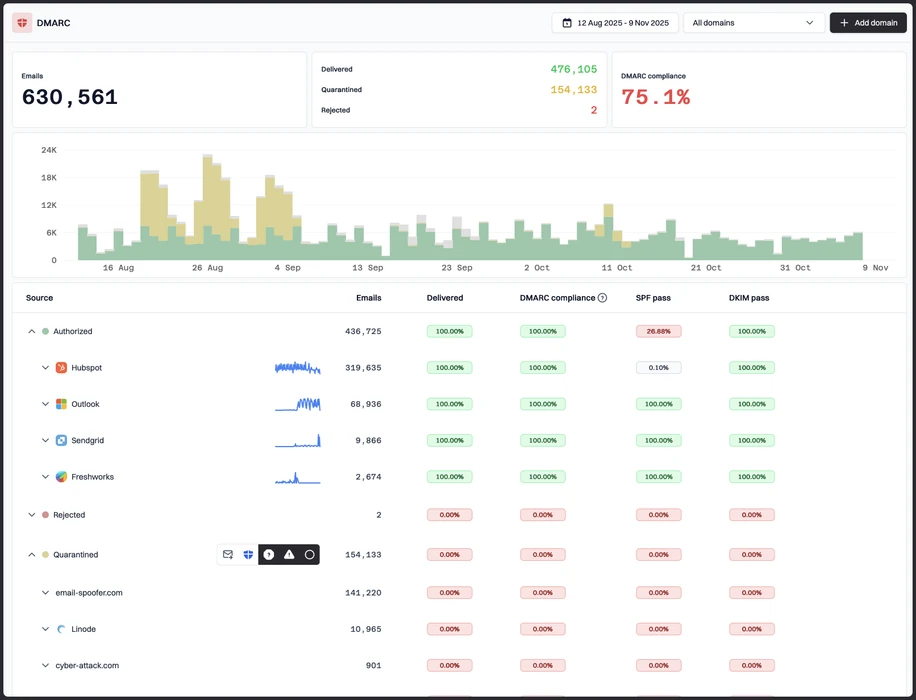
Resolve unknown senders in place
Suped turns an unfamiliar source into a guided classification and owner task, addressing the extra analyst follow-up we needed in Nameshield.
Host the records you operate
Neither tested workflow included hosted SPF or MTA-STS, so Suped keeps those records and their issue detection inside the same authentication workflow.
Standardize client ownership
Suped adds client workspaces, repeatable handoffs, and published MSP pricing at $7 per domain, addressing Postmastery's external notes and both products' unpublished pricing.
The difference was significant. We moved from limited visibility to a much clearer dashboard. Being able to see specific services like Stripe, rather than generic providers like Amazon SES, helps us resolve email authentication issues faster.
Markus Hugenschmidt, Managing Director, Jam Cyber
Migrating from Nameshield or Postmastery?
We have done the migration enough times to know the shape.
Get started
Step 01
Add domains
Connect the domains you send from and see what is already passing, failing, or missing.
Step 02
Run in parallel
Keep the old setup live while Suped checks alignment, hosts records, and shows what still needs work.
Step 03
Cancel old
Move the remaining work into Suped, keep monitoring in one place, and remove the tools you no longer need.
Frequently asked questions
How MONEYME proactively strengthens domain security and unlocks higher email engagement with Suped
See how MONEYME uses Suped
How cybersecurity specialist Jam Cyber delivers scalable DMARC protection with Suped
See how Jam Cyber uses Suped
How Vision Australia maintains full DMARC enforcement across a large domain portfolio with Suped
See how Vision Australia uses Suped
How The POP Team turns domain checks and DMARC visibility into client ready delivery work
See how The POP Team uses Suped
How DigiBean simplified DMARC monitoring and improved email security for their MSP clients
See how DigiBean uses Suped
How Alliance Group moved from reactive guesswork to proactive email management with Suped
See how Alliance Group uses Suped