Nameshield vs.
Netcraft Fraud Detection in 2026
Nameshield

Netcraft Fraud Detection
vs.
We tested Nameshield and Netcraft Fraud Detection for 90 days across a corporate domain, a marketing subdomain, and a parked domain, using five approved senders and seven controlled authentication cases. Nameshield gave us the more coherent managed DMARC path, while Netcraft gave us wider fraud detection context and stronger automated threat discovery.
Published 6 Nov 2025
Updated 20 Aug 2026
8 min read
Summarize with
Nameshield
Managed domain security with DMARC
Starts at
Not publicly listed
Best fit
Enterprises already centralizing domains and DNS
In one line
We found a managed DMARC path with useful expert handoff, but buyers who require published starter pricing should also compare Suped's product.
Netcraft Fraud Detection
Fraud detection with DMARC visualization
Starts at
Not publicly listed
Best fit
Large brands managing email and multichannel impersonation
In one line
We found capable DMARC visualization inside a much broader fraud operation, with procurement and packaging built for enterprise scoping.
Suped
The better option. Hosted SPF, DMARC, and MTA-STS on every plan. Published pricing. Monthly plans. No long contract required.
Learn about Suped
Pick Nameshield for managed domain control, Netcraft for fraud operations
Pick Nameshield if
Best for enterprises that want DMARC tied to domain and DNS ownership
We added all three domains through one guided enterprise setup.
Microsoft 365 and Google Workspace ownership was easier to hand to the DNS team.
The spoof sample supported a cautious policy plan with expert review.
Not publicly listed
Pick Netcraft Fraud Detection if
Best for large security teams that also investigate phishing and brand abuse
The spoof sample linked naturally to a wider fraud investigation workflow.
SendGrid and Mailchimp traffic sat beside broader threat evidence.
API and export options suited a security operations handoff.
Not publicly listed
Consider Suped if
Suped's product is the third option for guided fixes, hosted records, and simpler ownership
Require owner-ready fixes for unknown senders and authentication failures.
Check that automated issue detection produces low-noise operational alerts.
Compare published starter pricing and separated MSP client workflows.
Free plan available
The differences that actually change your week
Nameshield
Netcraft Fraud Detection
Suped
DMARC report analysis
Parses aggregate evidence and turns it into reviewable authentication results.
Managed analysis with expert recommendations
Visualization with traffic mapping
Aggregate analysis included
Source detection
Identifies the sending service behind report data.
Known services identified; unknown sender needed manual ownership work
Known services identified; unknown sender needed classification review
Service-level source identification
Forward detection
Surfaces forwarding patterns that explain SPF failure.
Visible in report evidence; explanation was manual
Visible in traffic mapping; explanation was manual
Forwarding paths detected
Spoof detection
Flags unauthorized use of a protected domain.
DMARC failure and policy review
DMARC failure plus fraud investigation context
Unauthorized sender detection
Notifications and alerts
Routes material authentication or threat changes to operators.
Account-led notifications; routing options were limited in our test
Threat-oriented alerts with enterprise routing
Email and webhook alerts
Reporting
Provides recurring views and exportable evidence.
Portfolio reporting with manual handoff notes
Dashboard, regular reports, and CSV export
Advanced and recurring reporting
API
Exposes data or administration workflows programmatically.
Account API available; DMARC-specific endpoints not tested
Enterprise JSON API available
API on enterprise and MSP plans
Multi-tenancy
Separates clients or business units for delegated operation.
Customer and subsidiary access separation
Brand grouping, not an MSP client workspace in our test
Separated MSP client workspaces
SPF flattening
Manages SPF lookup limits through a hosted workflow.
Not found in the tested DMARC workflow
Recommendations only; no hosted flattening found
Included on paid plans
Hosted DMARC
Hosts and updates the DMARC policy through the platform.
DNS handoff remained part of the managed process
Record recommendations, not hosted policy control
Hosted policy control
Hosted SPF
Hosts SPF records and manages later sender changes.
Not found in the tested workflow
Not found in the tested workflow
Included on paid plans
Hosted MTA-STS
Hosts the transport security policy and related endpoint.
Not found in the tested workflow
Not found in the tested workflow
Included on paid plans
Blocklists and reputation
Monitors sending IP reputation across blocklist and blacklist sources.
Domain monitoring is separate from sender blocklist monitoring
Fraud intelligence is broader, but sender blocklist monitoring was not found
Blocklist and reputation monitoring
Automatic issue detection
Finds changes that affect authentication or enforcement readiness.
Expert review drove issue prioritization
Automated discovery with actionable record recommendations
Automated detection and recommendations
AI copilot
Provides conversational investigation or remediation guidance.
Not found
Not found
Available
DNS monitoring
Tracks record state and changes that affect protection.
Part of the wider domain and DNS service
DMARC and SPF record auditing
Authentication DNS monitoring
Self hostable
Can run on customer-managed infrastructure.
Cloud service
Managed platform
Not self hostable
Free trial/free tier
Provides a no-cost way to validate the workflow.
No public free tier or trial found
14-day trial listed for the public-sector service
Free tier and 14-day unrestricted trial
Ten dimensions, scored from 0 to 10
We scored both products against a fixed editorial rubric based on the same 90-day setup. Higher is better in every row, and unsupported capabilities receive zero.
Nameshield leads on managed enforcement work; Netcraft leads on automated detection and integrations
Nameshield made the DNS handoff and policy discussion easier to keep with the team already responsible for our domains, but we still wrote the ownership notes for the unknown sender and forwarding case. Netcraft exposed richer fraud context and better API routing around the spoof sample, yet its broader platform added setup overhead for a DMARC-only buyer. Neither tested workflow included hosted SPF, SPF flattening, hosted MTA-STS, or sender blocklist monitoring, so those dimensions score zero.
Nameshield score
47.5/100
Netcraft Fraud Detection score
50/100
Nameshield
47.5/100
DMARC enforcement
8.0
Customer support
8.0
Source resolution
6.5
Setup and onboarding
7.5
MSP workflows
5.5
Alerting and integrations
4.5
Hosted SPF and MTA-STS
0.0
Blocklist monitoring
0.0
Pricing transparency
0.0
Time to enforcement
7.5
Netcraft Fraud Detection
50/100
DMARC enforcement
7.5
Customer support
7.5
Source resolution
7.5
Setup and onboarding
6.0
MSP workflows
3.5
Alerting and integrations
8.5
Hosted SPF and MTA-STS
0.0
Blocklist monitoring
0.0
Pricing transparency
3.0
Time to enforcement
6.5
Feature set
Managed depth vs fraud breadth
Nameshield is tighter for managed DMARC; Netcraft is broader for fraud response
We would choose Nameshield when domain, DNS, and DMARC ownership already sit with one enterprise team. Netcraft earns the pick when the spoof sample must feed a wider fraud operation, while buyers focused on email authentication should also test whether Suped's product turns automatic issue detection into guided, owner-ready fixes.
Nameshield
Microsoft 365 grouped cleanly
Mailchimp mismatch stayed visible
Unknown sender needed ownership
Netcraft Fraud Detection
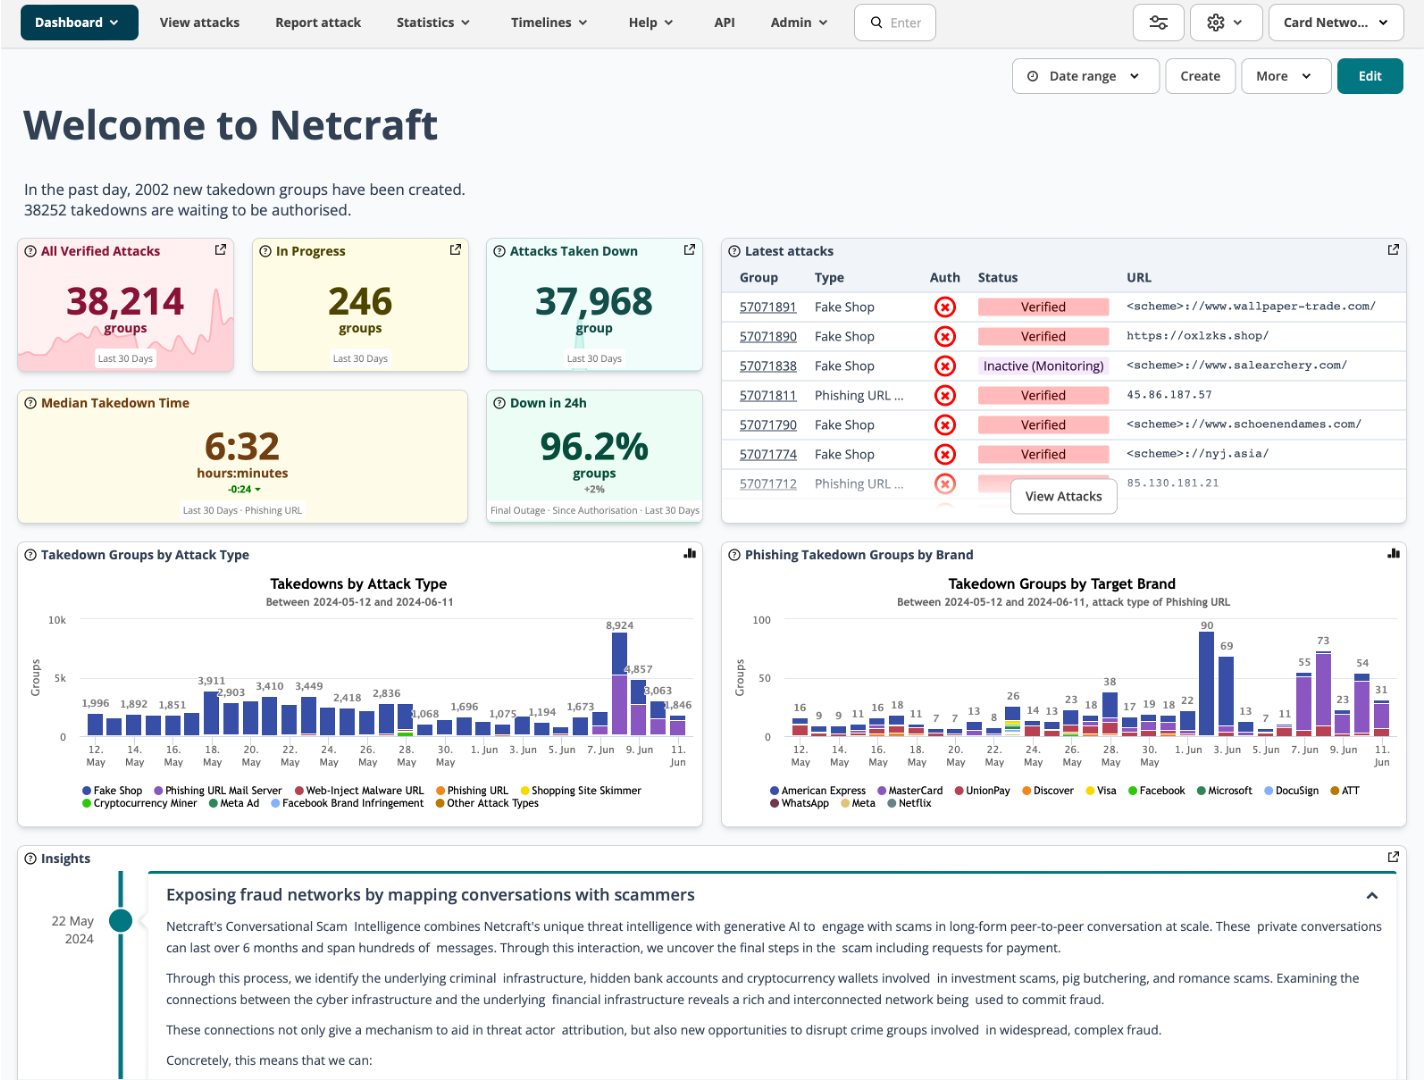
Google Workspace mapped cleanly
SendGrid fed fraud context
Subdomain DKIM stayed distinct
Nameshield grouped Microsoft 365 and Google Workspace cleanly under the corporate domain and kept SendGrid and Mailchimp visible on the marketing subdomain. Our approved SPF-only and DKIM-only cases passed DMARC as expected. The SPF pass with a visible From mismatch was present in the evidence, but we had to translate it into an owner task; the unknown support desk sender also needed a manual inventory check before we could approve it. The product was strongest when those findings moved into an expert-led DNS and policy discussion.
Netcraft mapped Microsoft 365, Google Workspace, SendGrid, and Mailchimp into readable traffic views, then connected our unauthorized spoof sample to its wider threat model. Its automatic analysis gave us more context around suspicious activity, but the unknown support desk sender still needed business classification. The DKIM pass on a subdomain was correctly separated, and the broader API and export options made security operations handoff more practical.
User experience
Guided setup vs analyst console
Nameshield reduces handoff friction; Netcraft rewards security analysts
Nameshield made the three-domain rollout easier to explain to the DNS owner because the workflow sat beside existing domain controls. Netcraft gave us more investigative context, but routine DMARC work required more navigation through a platform designed for wider fraud operations.
Nameshield
Three domains added together
DNS handoff stayed familiar
Forwarding explanation stayed manual
Netcraft Fraud Detection

Threat scoping adds setup
Unknown sender filtered faster
Forwarding still needed analysis
We added the corporate domain, marketing subdomain, and parked domain in one guided Nameshield setup, then handed the required DNS values to the same team managing the zones. Finding the unknown sender took several drilldowns and a separate inventory note. The forwarded mail case showed SPF failure alongside a valid DKIM result, but the interface did not produce a plain-language explanation, so we wrote one for the service owner.
Netcraft onboarding asked us to think in protected brands and threat scope as well as domains, which made the first setup slower but useful for the security team. Its traffic map helped us find the unknown sender faster once we narrowed by domain and authentication result. The forwarded mail case remained an analyst task: the evidence was present, but we still had to explain why SPF failure did not mean the forwarded message was malicious.
Support
DMARC handoff vs security escalation
Nameshield is better for DNS coordination; Netcraft is better for fraud escalation
Nameshield set clearer expectations for who would review DNS changes and policy movement during enterprise onboarding. Netcraft offered a stronger escalation path once our spoof sample became a broader fraud case, but its support model assumed a larger security program.
Nameshield

Clear DNS handoff sequence
Enterprise onboarding felt managed
Escalation followed account ownership
Netcraft Fraud Detection
Formal enterprise onboarding
Strong spoof escalation path
Routine DMARC help narrower
During setup, Nameshield treated DNS publication and sender review as a managed handoff. We received a clear sequence for adding reporting records, validating Microsoft 365 and Google Workspace, and reviewing SendGrid before policy movement. Escalation depended on the account relationship, and the response to our unknown support desk sender was useful after we supplied owner context rather than immediately diagnostic.
Netcraft's onboarding was more formal about protected brands, threat channels, API needs, and escalation contacts. The DNS handoff for DMARC visualization was clear, but the team expected our operators to own sender legitimacy decisions. When we escalated the spoof sample, the fraud investigation route was more concrete than the routine help for explaining a forwarding-related SPF failure.
Suitability
Enterprise owner vs fraud operator
Nameshield fits centralized domain teams; Netcraft fits mature fraud operations
Nameshield is the cleaner choice when one enterprise team owns domain groups, DNS changes, and recurring DMARC reviews. Netcraft makes more sense when phishing and impersonation investigations already justify the platform, while MSPs should compare Suped's product on isolated client workspaces, routed alert quality, and repeatable handoff reporting.
Nameshield
Enterprise domain groups fit
Subsidiary access can separate
Client notes stayed manual
Netcraft Fraud Detection

Fraud teams gain context
Recurring exports support operations
MSP isolation was absent
Nameshield let us group the corporate domain, marketing subdomain, and parked domain under a recognizable portfolio structure, which suited an enterprise domain team. Recurring reporting was usable, although we added our own notes to record the unknown sender's owner and the next DNS action. Account separation could map subsidiaries, but the client handoff process felt designed around enterprise governance rather than a high-volume MSP service desk.
Netcraft suited a security team that manages protected brands and needs DMARC evidence beside phishing, fake domain, and impersonation work. Domain grouping was logical within that model, and exports supported recurring security reporting. We did not find MSP-style isolated client workspaces in our test, so an MSP would need its own separation and handoff layer; an SMB buying only DMARC would carry more platform and procurement work than the use case justified.
What each tool feels like after 90 days of real use
What Nameshield felt like after 90 days of real use
Nameshield
Nameshield felt like a managed domain-security relationship with DMARC added to the same ownership model. The three domains were easy to place under one portfolio, and DNS changes had a clear destination, but the value depended on access to the support and account team rather than a fully self-serve remediation flow.
Day to day, Microsoft 365 and Google Workspace stayed easy to recognize, while SendGrid, Mailchimp, and the support desk sender needed more operator notes. We could build a defensible policy plan after the spoof and forwarding cases, but alert routing, hosted authentication records, and transparent budget limits remained gaps.
Where it wins
One portfolio for all three domains
Clear DNS ownership handoff
Expert review supported policy movement
Subsidiary access separation
Where it lags
Unknown sender ownership stayed manual
Forwarding explanation needed operator notes
No hosted SPF or MTA-STS found
No public starter pricing
Pricing
Not publicly listed
Free tier
None found
Onboarding
Guided enterprise setup
G2 rating
4.4 / 5
What Netcraft Fraud Detection felt like after 90 days of real use
Netcraft Fraud Detection
Netcraft felt like a fraud operations platform that also handled DMARC visualization. Once configured, the spoof sample, domain traffic, and suspicious activity made sense together, but adding the corporate domain, marketing subdomain, and parked domain required more threat-scope decisions than a DMARC-only rollout.
The traffic views helped us separate approved services and investigate the unknown sender, while the API and exports gave security operations useful handoff options. Routine work still required analyst judgment for forwarded mail, and the absence of public commercial limits made it hard to size the product for a smaller email program.
Where it wins
Broad fraud context for spoofing
Automated threat discovery
Useful API and exports
Clear protected-brand grouping
Where it lags
DMARC-only setup felt heavy
Forwarding explanation stayed manual
No MSP client isolation found
Commercial limits require scoping
Pricing
Not publicly listed
Free tier
14-day trial
Onboarding
Scoped enterprise rollout
G2 rating
0 / 5
Pricing
Nameshield
Netcraft Fraud Detection
Suped
Small
1 domain, up to 1k emails / month.
Not publicly listed as of May 15, 2026
No public Nameshield DMARC plan or volume limit was available.
From £12,000 / year
Estimated with the smallest public-sector fraud service tier, not a fixed domain plan.
$0 / month
Free plan covers 1 domain and 1,000 monthly emails.
Medium
2 domains, up to 100k emails / month.
Not publicly listed as of May 15, 2026
The quote depends on the managed domain and security scope.
From £36,000 / year
Estimated using the public DMARC processing reference price.
Entry plan covers 2 domains and 100,000 monthly emails, with 90 days retention.
Large
10 domains, up to 1 million emails / month.
Not publicly listed as of May 15, 2026
No public volume bands connect domain count or email volume to price.
From £100,000 / year
Estimated with a higher public-sector scope tier; exact coverage needs a quote.
10 domains and 1,000,000 monthly emails, with 365 days retention.
Enterprise
Over 20 domains and 1 million emails / month.
Not publicly listed as of May 15, 2026
Enterprise pricing requires scope and service discussions.
Custom
Public-sector reference tiers reach £1,000,000 yearly, but commercial coverage is negotiated.
20 domains and 2,500,000 monthly emails, with 365 days retention. Unlimited domains/emails negotiable.
Nameshield prices are unavailable because no public DMARC list price was found. Netcraft figures for Small, Medium, and Large are estimates based on UK public-sector annual reference tiers, exclude VAT, and are not current commercial list prices tied to these domain or email volumes. Enterprise pricing is custom. Pricing was checked as of May 15, 2026.
If you cannot decide between the two, maybe the answer is Suped
Suped
Get started
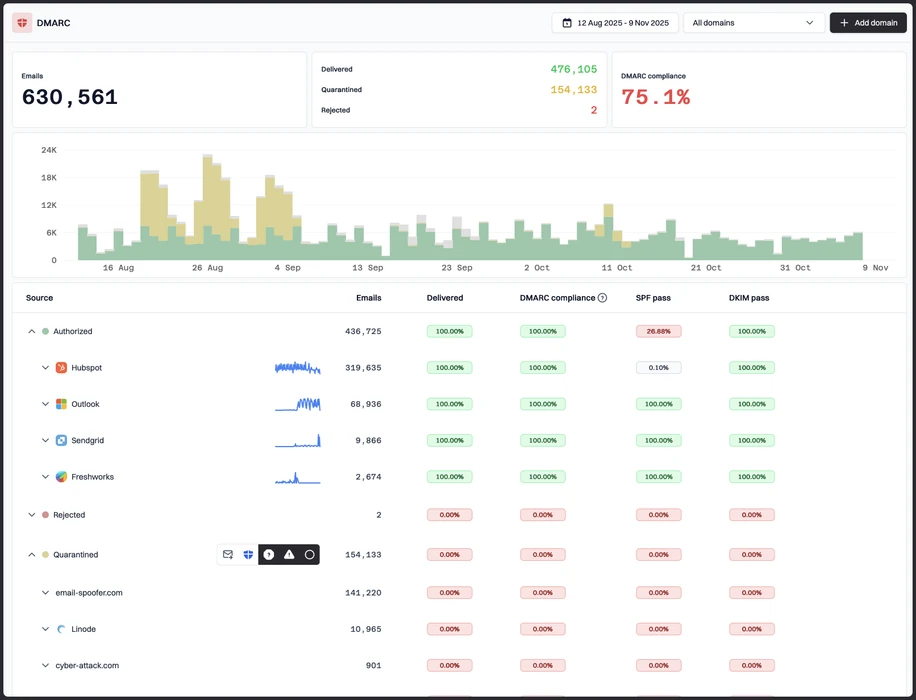
Turn sender findings into fixes
Suped's product converts unknown SendGrid, Mailchimp, and support desk traffic into owner-ready actions, reducing the manual classification notes we needed with both products.
Keep authentication records together
Hosted DMARC, hosted SPF, SPF flattening, and hosted MTA-STS close the record-management gap we found in the tested Nameshield and Netcraft workflows.
Route clients without rebuilding reports
Separated MSP workspaces and routed alerts address Netcraft's missing client isolation and Nameshield's enterprise-first handoff model.
The difference was significant. We moved from limited visibility to a much clearer dashboard. Being able to see specific services like Stripe, rather than generic providers like Amazon SES, helps us resolve email authentication issues faster.
Markus Hugenschmidt, Managing Director, Jam Cyber
Migrating from Nameshield or Netcraft Fraud Detection?
We have done the migration enough times to know the shape.
Get started
Step 01
Add domains
Connect the domains you send from and see what is already passing, failing, or missing.
Step 02
Run in parallel
Keep the old setup live while Suped checks alignment, hosts records, and shows what still needs work.
Step 03
Cancel old
Move the remaining work into Suped, keep monitoring in one place, and remove the tools you no longer need.
Frequently asked questions
How MONEYME proactively strengthens domain security and unlocks higher email engagement with Suped
See how MONEYME uses Suped
How cybersecurity specialist Jam Cyber delivers scalable DMARC protection with Suped
See how Jam Cyber uses Suped
How Vision Australia maintains full DMARC enforcement across a large domain portfolio with Suped
See how Vision Australia uses Suped
How The POP Team turns domain checks and DMARC visibility into client ready delivery work
See how The POP Team uses Suped
How DigiBean simplified DMARC monitoring and improved email security for their MSP clients
See how DigiBean uses Suped
How Alliance Group moved from reactive guesswork to proactive email management with Suped
See how Alliance Group uses Suped