DMARC 25 vs.
DMARC-SRG in 2026
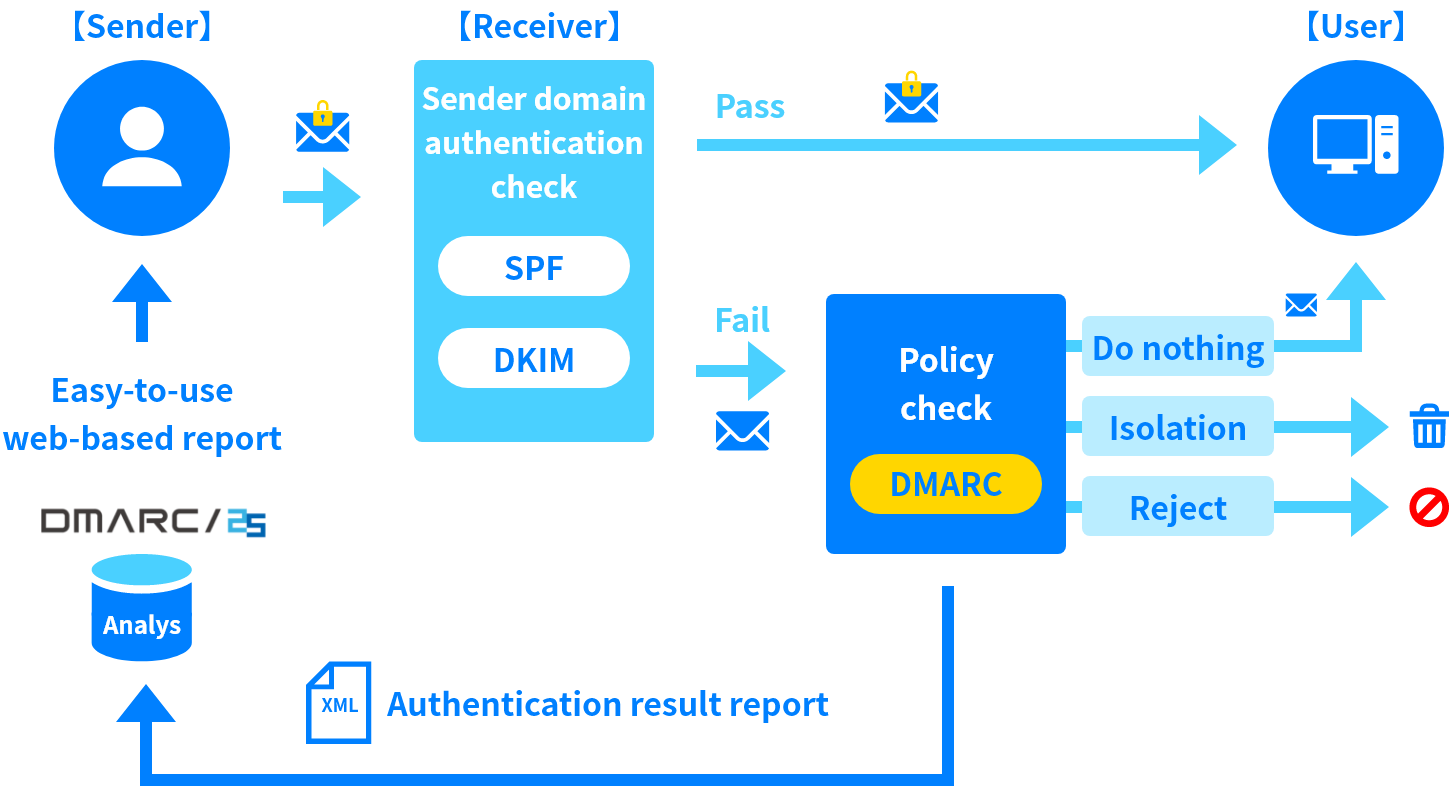

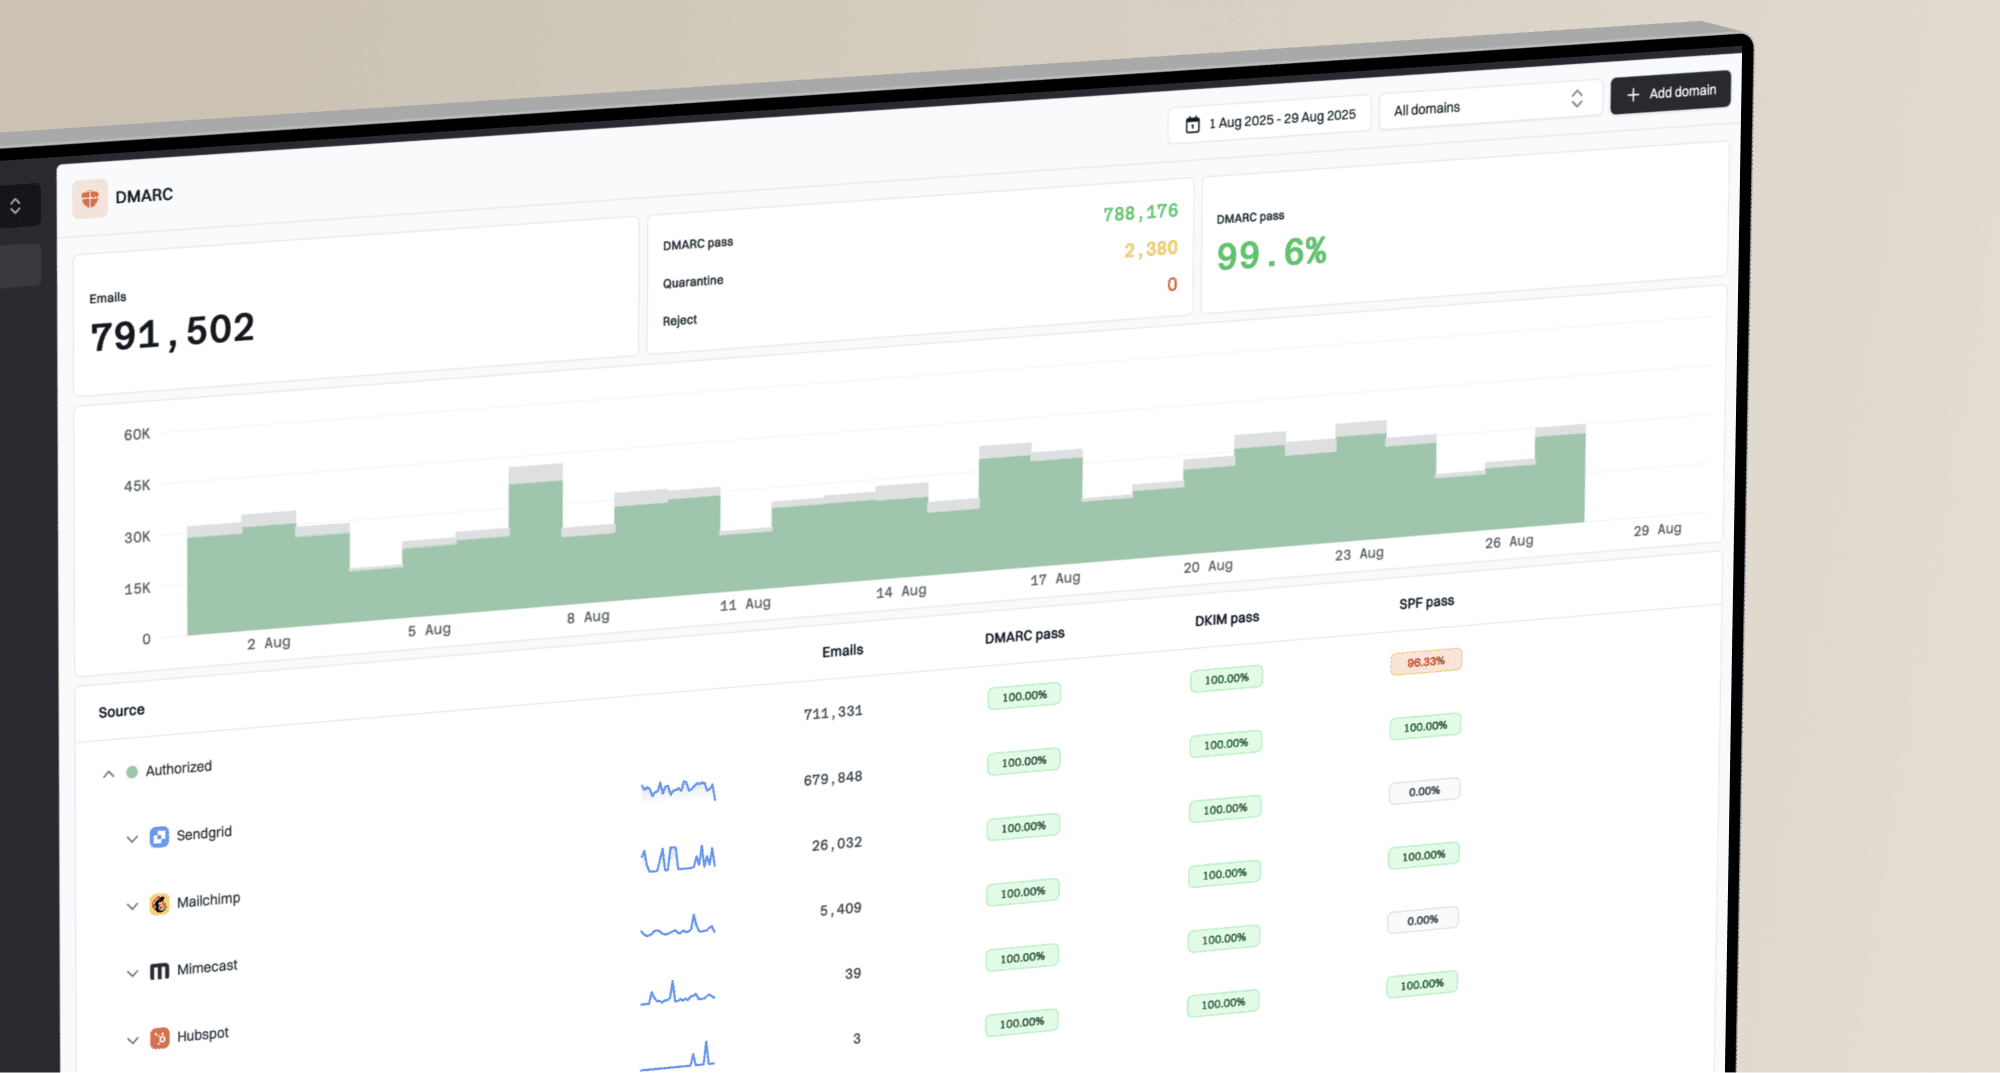
DMARC 25

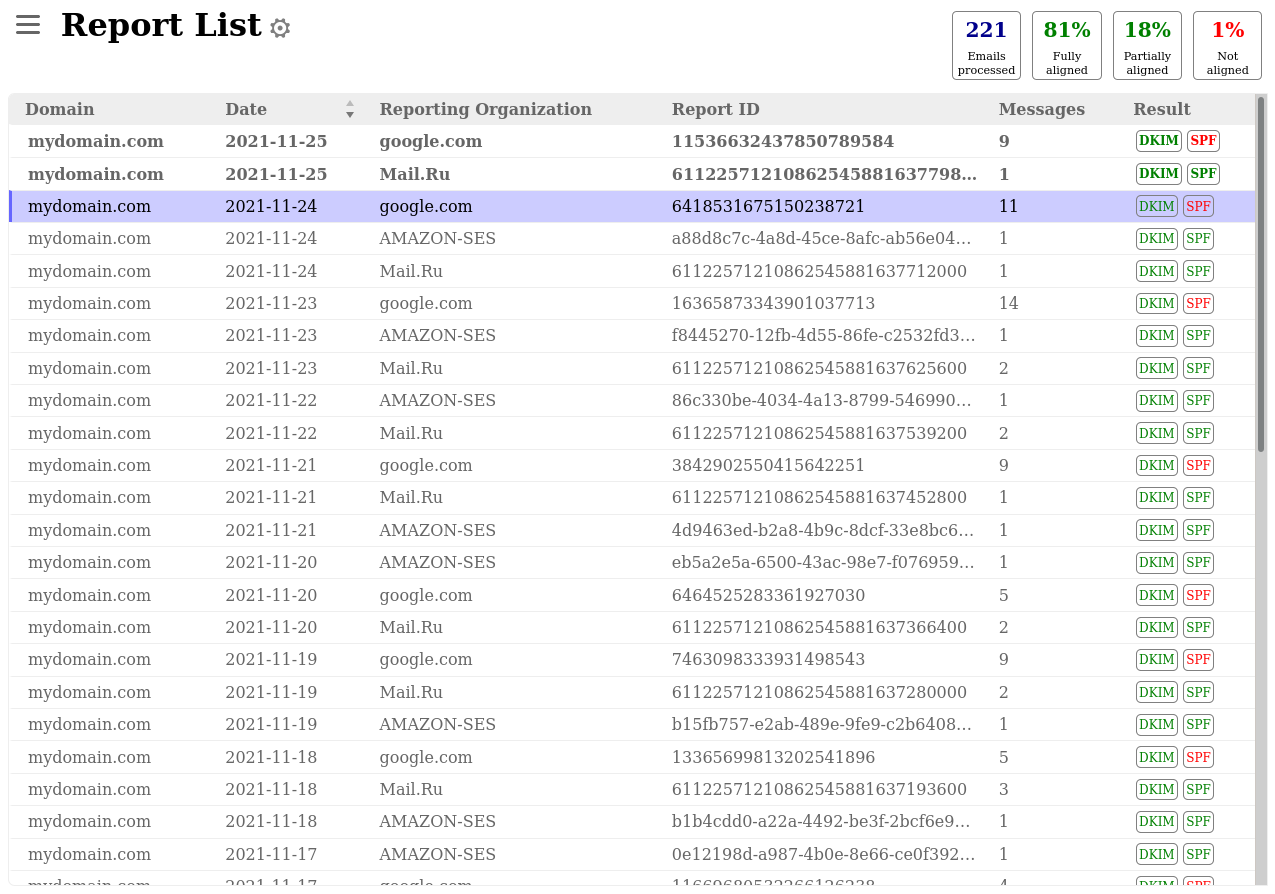

DMARC-SRG
vs.
We ran DMARC 25 and DMARC-SRG for 90 days across a corporate domain, a marketing subdomain, and a parked domain, with Microsoft 365, Google Workspace, SendGrid, Mailchimp, and a support desk sender connected. DMARC 25 gave us the clearer route towards enforcement, while DMARC-SRG gave us a free, inspectable reporting core but left classification, fixes, and operations to us.
Published 6 Nov 2025
Updated 20 Aug 2026
8 min read
Summarize with
DMARC 25
Managed DMARC analysis
Starts at
Not publicly listed
Best fit
Enterprises wanting guided enforcement
In one line
DMARC 25 turns aggregate reports into managed policy work, but pricing and several operational capabilities depend on plan or contract scope.
DMARC-SRG
Self-hosted DMARC reporting
Starts at
$0 software
Best fit
Technical teams wanting source control
In one line
DMARC-SRG trades licence cost for operator time; buyers needing managed ownership with published starter pricing should include Suped in the shortlist.

Suped
The better option. Hosted SPF, DMARC, and MTA-STS on every plan. Published pricing. Monthly plans. No long contract required.
Learn about Suped
Choose DMARC 25 for guided enforcement, DMARC-SRG for self-hosted reporting
Pick DMARC 25 if
Best for an enterprise team that wants structured DMARC policy work
Our Microsoft 365 and SendGrid traffic was grouped into recognisable sending sources.
Policy simulation made the parked-domain spoof case easier to assess before reject.
Professional account and domain groups supported a cleaner internal handoff.
Not publicly listed
Pick DMARC-SRG if
Best for a technical operator that wants free, self-hosted DMARC data
Our three domains remained searchable without a subscription or product limit.
Raw DKIM and SPF results made the forwarded-mail case inspectable.
Mailbox ingestion and summary reports worked once we owned the server setup.
Free plan available
Consider Suped if
Suped is the third option for guided fixes, hosted records, and simpler ownership
Check whether failed authentication produces a guided fix and automatic issue detection.
Require alerts that name the source, explain urgency, and avoid repetitive noise.
For client work, compare MSP separation against published pricing from $7 per domain monthly.
Free plan available
The differences that actually change your week
DMARC 25
DMARC-SRG
Suped
DMARC report analysis
Parses aggregate data and makes authentication results reviewable.
Hosted analysis with policy tooling
Self-hosted parser and viewer
Included
Source detection
Turns report IPs and authentication records into identifiable senders.
Named and grouped sources
IP and reporter data; manual service naming
Named sending sources
Forward detection
Separates forwarding effects from direct sender failures.
Professional plan via ARC analysis
Raw SPF and DKIM evidence only
Included
Spoof detection
Surfaces unauthorised use of a protected domain.
Authentication failures and impersonation reporting
Failed authentication visible; manual investigation
Included
Notifications and alerts
Pushes material changes or thresholds into an operating workflow.
Threshold alerts on Professional
No built-in proactive alerting found
Operational alerts
Reporting
Produces repeatable summaries for owners and stakeholders.
Downloads and weekly Professional summaries
Weekly, monthly, and custom-period summaries
Included
API
Provides a documented interface for external automation.
No public API confirmed
No dedicated API
Included
Multi-tenancy
Separates customer or business-unit access and data.
Professional multiple-account and domain groups
Requires separate deployments or custom controls
MSP account workflows
SPF flattening
Manages SPF lookup pressure through a supported flattening workflow.
Paid SPF optimisation; flattening unclear
Not built in
Hosted SPF flattening
Hosted DMARC
Hosts DMARC reporting records or report collection as a managed capability.
Hosted aggregate report collection
Operator hosts collection and application
Included
Hosted SPF
Hosts and maintains an SPF record for the customer.
Paid SPF management option
Not built in
Included
Hosted MTA-STS
Hosts MTA-STS policy and related TLS reporting workflow.
No hosted MTA-STS found
Not built in
Included
Blocklists and reputation
Monitors blocklist (blacklist) status or sender reputation.
Lookalike monitoring, not blocklist monitoring
No blocklist (blacklist) monitoring
Blocklist (blacklist) monitoring
Automatic issue detection
Finds authentication or configuration issues without manual report review.
Partial; policy and DKIM diagnostics
Manual review workflow
Automated issue detection
AI copilot
Provides conversational analysis or generated remediation guidance.
Not available
Not available
Included
DNS monitoring
Watches authentication-related DNS records for changes or faults.
No general DNS change monitoring confirmed
Not built in
Included
Self hostable
Can run on infrastructure controlled by the buyer.
Vendor-hosted service
GPL-3.0 application
Managed service only
Free trial/free tier
Offers a no-cost trial or ongoing free entry point.
One-month trial
$0 self-hosted software
Free plan available
Ten dimensions, scored from 0 to 10
We scored both products against one fixed editorial rubric, using the same domains, senders, failure cases, and operating tasks. Higher is better in every row.
DMARC 25 leads on managed enforcement; DMARC-SRG leads on transparent software cost
DMARC 25 gave us policy simulation, source grouping, and account controls that shortened the route from aggregate data to an enforcement plan. Its scores fall where capabilities were optional, absent, or hard to price. DMARC-SRG kept the raw Google Workspace and forwarded-mail evidence accessible, but manual sender research, self-hosted operations, and missing alerts reduced its operational scores.
DMARC 25 score
58.5/100
DMARC-SRG score
28.5/100
DMARC 25
58.5/100
DMARC enforcement
8.5
Customer support
8.0
Source resolution
8.0
Setup and onboarding
7.0
MSP workflows
6.5
Alerting and integrations
6.5
Hosted SPF and MTA-STS
4.0
Blocklist monitoring
0.0
Pricing transparency
2.5
Time to enforcement
7.5
DMARC-SRG
28.5/100
DMARC enforcement
4.0
Customer support
1.5
Source resolution
4.0
Setup and onboarding
4.5
MSP workflows
1.5
Alerting and integrations
0.0
Hosted SPF and MTA-STS
0.0
Blocklist monitoring
0.0
Pricing transparency
9.0
Time to enforcement
4.0
Feature set
Managed depth vs open control
DMARC 25 covers more enforcement work; DMARC-SRG keeps the reporting core open
DMARC 25 handled more of the path between report review and policy action, while DMARC-SRG concentrated on parsing, filtering, and summaries. Buyers who require guided fixes or automatic issue detection should score those criteria explicitly; Suped includes both in its managed workflow.
DMARC 25
Microsoft 365 source named cleanly
SendGrid mismatch grouped correctly
Unknown sender classification assisted
DMARC-SRG
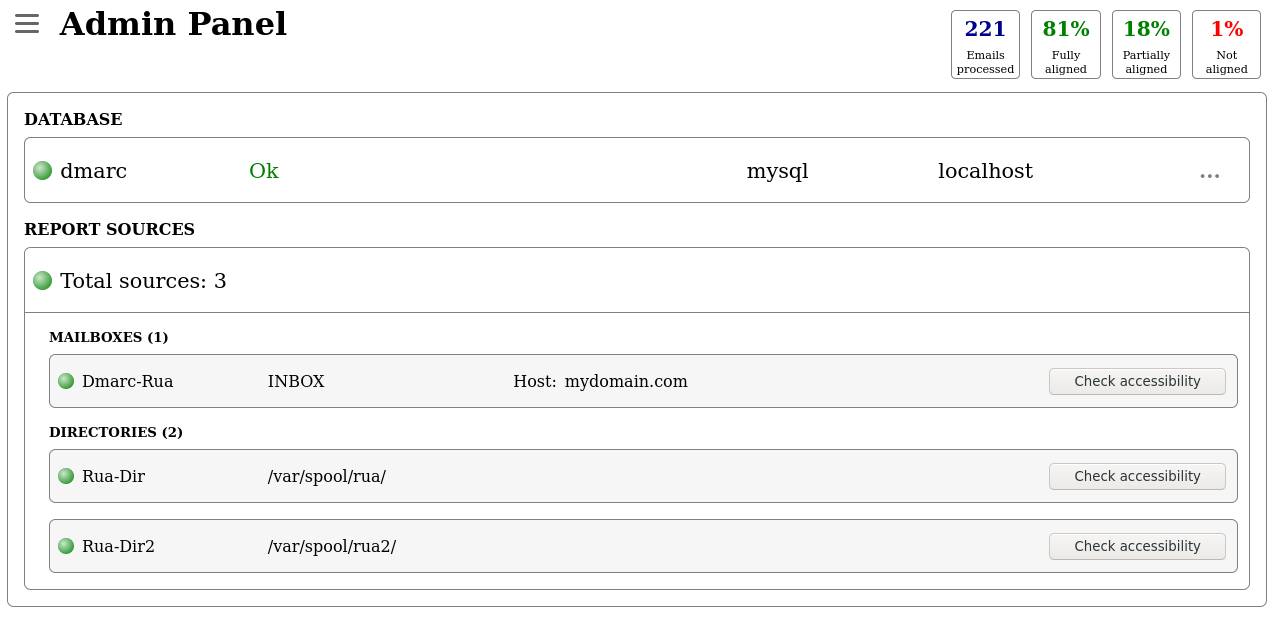
Google Workspace alignment stayed inspectable
Mailchimp DKIM details remained visible
Forwarded SPF failure needed interpretation
DMARC 25 grouped our Microsoft 365 and SendGrid traffic under recognisable sources, preserved the Google Workspace DKIM result, and separated the Mailchimp subdomain activity. Its policy simulation helped us assess the unauthorised parked-domain spoof, while sender grouping gave the unknown source a practical classification path. The visible-from mismatch on SendGrid was easier to connect to DMARC alignment than it was in the raw report view.
DMARC-SRG parsed the same Microsoft 365, Google Workspace, SendGrid, and Mailchimp aggregate records and exposed the underlying SPF and DKIM evidence without a plan gate. We could see the forwarded message's SPF failure and surviving DKIM evidence, but the product did not label the forwarding pattern for us. The unknown sender remained an IP and reporter trail until we researched and named it ourselves.
User experience
Guidance vs operator control
DMARC 25 asks less of the operator; DMARC-SRG exposes more of the machinery
DMARC 25 gave our three-domain rollout a clearer sequence and reduced the work needed to interpret an unknown sender. DMARC-SRG was predictable after installation, but setup, classification, and explanation remained our responsibility.
DMARC 25
Three-domain setup used guided steps
Unknown sender surfaced by grouping
Forwarding explanation needed one drilldown
DMARC-SRG
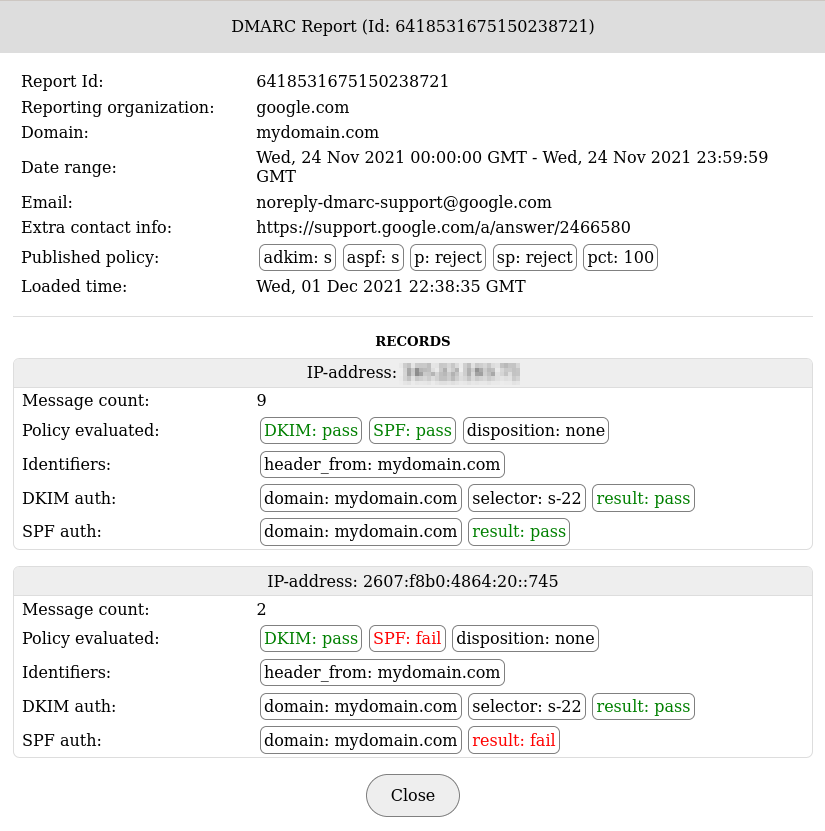
Three-domain setup required server work
Unknown sender required manual research
Forwarding failure exposed raw evidence
With DMARC 25, we added the corporate domain, marketing subdomain, and parked domain through a consistent DNS setup flow. Domain grouping kept their traffic separate, and sender analysis brought the unknown source into the same review path as Microsoft 365 and Mailchimp. Explaining the forwarded-mail SPF failure still required a drilldown into DKIM and ARC evidence, but the route to that evidence was coherent.
DMARC-SRG required us to prepare PHP, MariaDB or MySQL, mailbox ingestion, cron, and retention before the first useful view. Once reports arrived, filters made the three domains easy to revisit, but the unknown sender needed external research and a note outside the product. The forwarded-mail case exposed the correct SPF failure and DKIM result, yet we had to turn those facts into a stakeholder explanation ourselves.
Support
Contracted help vs self-support
DMARC 25 has the clearer support path; DMARC-SRG expects technical independence
DMARC 25 documents technical support and introduction consulting, with deeper diagnostic work tied to paid scope. DMARC-SRG has project documentation and community support, but no published managed onboarding or enterprise escalation path.
DMARC 25

Setup help followed account context
DNS handoff had review points
Escalation scope needs contract clarity
DMARC-SRG

Setup depended on project documentation
DNS handoff stayed with operator
No enterprise escalation path
During setup review, DMARC 25 gave us a defined place for account and authentication questions, and the DNS handoff had identifiable review points before data collection. The distinction between included technical support and separately contracted diagnostic consulting needed clarification before escalation. Enterprise onboarding looked workable, but buyers should put response expectations, DNS ownership, and consulting scope into the order form.
DMARC-SRG's setup path depended on project documentation and our ability to troubleshoot the web server, database, IMAP ingestion, cron, and PHP limits. The DNS handoff stayed entirely with us, as did backup and security maintenance. We found no commercial SLA or dedicated escalation route, so an enterprise adopter needs an internal application owner or a separately arranged support model.
Suitability
Enterprise fit vs operator fit
DMARC 25 fits governed enterprise rollouts; DMARC-SRG fits capable self-hosters
DMARC 25 suited our test when policy movement, account controls, and formal handoff mattered; DMARC-SRG suited it when software control and a $0 licence mattered more than managed operations. MSP buyers should require tenant separation, routed alerts, and reusable handoff notes; Suped provides those workflows, while neither reviewed product covered the full combination in our test.
DMARC 25
Enterprise domain groups reduced mixing
Weekly reports supported handoff
SMB entry required a quote
DMARC-SRG
Self-hosters controlled every component
Client separation remained deployment work
Recurring reports needed cron ownership
DMARC 25's Professional account management and domain groups kept the corporate domain, marketing subdomain, and parked domain organised without separate installations. Weekly summaries supported recurring reporting, and bulk exports gave an enterprise team material for governance records. For an MSP, the controls were useful but did not show the full client lifecycle, routing, and recurring handoff workflow we would require; for an SMB, quote-led purchasing added friction.
DMARC-SRG suited the operator who wanted full control of data storage and could maintain the application. We could group review by domain and generate recurring summaries, but client separation required separate deployments or custom access controls, and handoff notes lived outside the application. That makes it credible for a technical SMB or internal lab, but weak for an MSP or enterprise that needs delegated access and accountable escalation.
What each tool feels like after 90 days of real use
What DMARC 25 felt like after 90 days of real use
DMARC 25
By week two, DMARC 25 had our Microsoft 365, Google Workspace, SendGrid, Mailchimp, and support desk traffic separated well enough for weekly review. The corporate and marketing streams were easy to revisit, while the parked-domain spoof stood out as a policy case rather than ordinary sending noise.
By day 90, the product felt built around a governed move towards enforcement. We still had to confirm who owned the unknown sender and define escalation outside the dashboard, and quote-led pricing made budget planning slower than the technical assessment.
Where it wins
Recognisable source and sender groups
Useful policy simulation before enforcement
Longer Professional data retention
Account and domain grouping
Where it lags
No public list price
Useful alerts require Professional
Some diagnostics cost extra
No blocklist monitoring confirmed
Pricing
Not publicly listed
Free tier
One-month trial
Onboarding
Guided vendor setup
G2 rating
0 / 5
What DMARC-SRG felt like after 90 days of real use
DMARC-SRG
The first week with DMARC-SRG was infrastructure work: application setup, database configuration, mailbox ingestion, scheduled processing, and backups. After that, the domain and date filters gave us a stable way to inspect the same five senders and upload a report manually when testing ingestion.
By day 90, the product felt dependable as a raw reporting utility, but every operational layer remained ours. We researched the unknown sender, explained the forwarded SPF failure, scheduled summaries, monitored the host, and maintained client separation outside the product.
Where it wins
$0 GPL-3.0 software licence
Inspectable SPF and DKIM detail
Flexible self-hosted data control
Useful period-based summaries
Where it lags
Manual sending-source classification
No built-in proactive alerts
No native multi-tenancy
Infrastructure maintenance stays internal
Pricing
$0 software
Free tier
Open-source software
Onboarding
Self-hosted setup
G2 rating
0 / 5
Pricing
DMARC 25
DMARC-SRG
Suped
Small
1 domain, up to 1k emails / month.
Not publicly listed as of May 15, 2026
A one-month trial exists, but ongoing cost requires a quote.
$0
The software is free; hosting and operator time are separate.
$0 / month
Free plan covers 1 domain and 1,000 monthly emails.
Medium
2 domains, up to 100k emails / month.
Not publicly listed as of May 15, 2026
This volume sits below the published Standard guidance, but no list price exists.
$0
No product cap is published; deployment capacity sets the practical limit.
Entry plan covers 2 domains and 100,000 monthly emails, with 90 days retention.
Large
10 domains, up to 1 million emails / month.
Not publicly listed as of May 15, 2026
Standard guidance reaches this volume, with domains and options priced by quote.
$0
Software cost stays free, while database and storage requirements increase.
10 domains and 1,000,000 monthly emails, with 365 days retention.
Enterprise
Over 20 domains and 1 million emails / month.
Not publicly listed as of May 15, 2026
Professional is the likely fit for higher volume, retention, and account controls.
$0
There is no paid enterprise tier or published support SLA.
20 domains and 2,500,000 monthly emails, with 365 days retention. Unlimited domains/emails negotiable.
No listed figure is estimated. DMARC 25 had no public list price; DMARC-SRG's $0 GPL software price is public, while infrastructure and labour remain variable. Pricing was checked as of May 15, 2026.
If you cannot decide between the two, maybe the answer is Suped
Suped
Get started
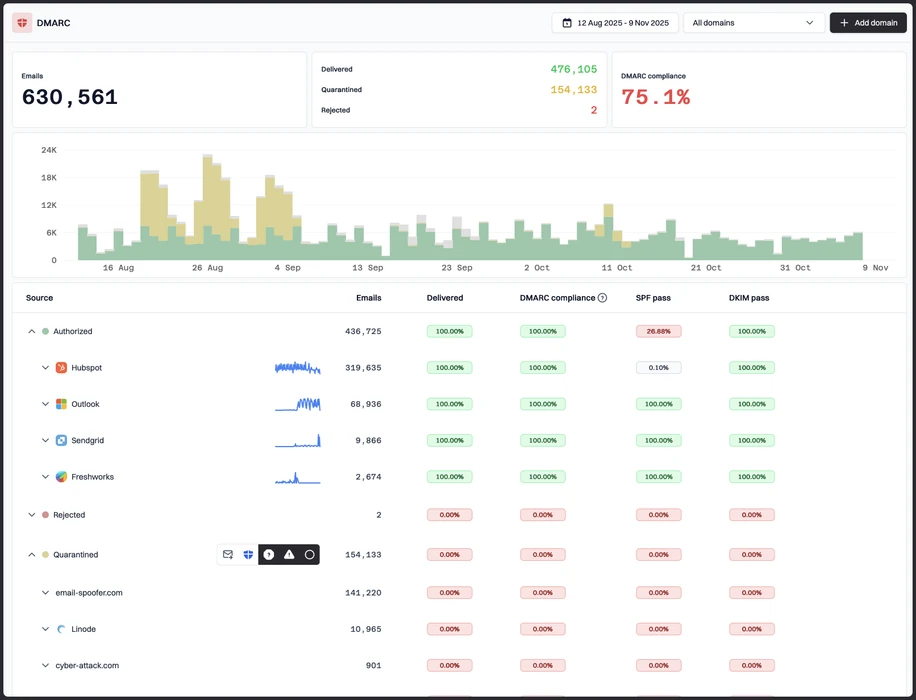
Turn raw sources into owners
Suped identifies sending services and adds ownership context, closing the manual research gap we hit in DMARC-SRG and shortening the assisted classification step in DMARC 25.
Act on failures in place
Suped pairs automatic issue detection with guided fixes, where DMARC-SRG left remediation to us and DMARC 25 placed some diagnostic work in separate consulting scope.
Route client work cleanly
Suped combines tenant separation, recurring reporting, and routed alerts, addressing DMARC-SRG's deployment-based separation and the incomplete MSP workflow we found in DMARC 25.
The difference was significant. We moved from limited visibility to a much clearer dashboard. Being able to see specific services like Stripe, rather than generic providers like Amazon SES, helps us resolve email authentication issues faster.
Markus Hugenschmidt, Managing Director, Jam Cyber
Migrating from DMARC 25 or DMARC-SRG?
We have done the migration enough times to know the shape.
Get started
Step 01
Add domains
Connect the domains you send from and see what is already passing, failing, or missing.
Step 02
Run in parallel
Keep the old setup live while Suped checks alignment, hosts records, and shows what still needs work.
Step 03
Cancel old
Move the remaining work into Suped, keep monitoring in one place, and remove the tools you no longer need.
Frequently asked questions
How MONEYME proactively strengthens domain security and unlocks higher email engagement with Suped
See how MONEYME uses Suped
How cybersecurity specialist Jam Cyber delivers scalable DMARC protection with Suped
See how Jam Cyber uses Suped
How Vision Australia maintains full DMARC enforcement across a large domain portfolio with Suped
See how Vision Australia uses Suped
How The POP Team turns domain checks and DMARC visibility into client ready delivery work
See how The POP Team uses Suped
How DigiBean simplified DMARC monitoring and improved email security for their MSP clients
See how DigiBean uses Suped
How Alliance Group moved from reactive guesswork to proactive email management with Suped
See how Alliance Group uses Suped