
How can I resolve Barracuda blocklist issues and improve email deliverability?
Published 11 Jun 2025
Updated 11 Oct 2026
11 min read
Summarize with
Updated on 11 Oct 2026: We clarified Barracuda delisting, bounce handling and the checks needed to stop repeat listings.
To resolve Barracuda blocklist (blacklist) issues, stop the traffic that caused the reputation problem first, then prove what is still failing. Confirm the exact sending IP, envelope sender, DKIM signing domain, visible From domain, recipient system, SMTP rejection, and message type before requesting a review.
The Barracuda Reputation Block List (BRBL) is an IP-based DNS blocklist (DNSBL), but Barracuda can also act on URL reputation, content scoring, sender or domain policy, and recipient settings. Failures can be intermittent when messages leave through a shared pool, because a lookup on one IP does not describe every IP used by the platform.
Steps to resolve Barracuda blocklist issues
Treat a Barracuda rejection as a deliverability incident. Use the complete SMTP reply and the recipient's Message Log reason to identify the signal behind the rejection before requesting delisting.
- Stop the source: Pause cold outreach, scraped-list sends, and any campaign with recent complaints or hard bounces.
- Classify failures: Stop automatic retries after a 5xx rejection. Permanently suppress confirmed invalid addresses; put valid recipients affected by policy blocks on hold until the cause is fixed.
- Identify routes: Pull headers and logs so you know the sending IP, envelope sender, DKIM domain, visible From domain, and remote Barracuda host.
- Check authentication: Run a domain health check and confirm DMARC passes through aligned SPF or DKIM, with valid underlying records.
- Document reputation signals: Check every outbound IP in the pool, then record the domains and URLs in the rejected message. Read the blocklist basics if you need the distinction between a blocklist and a local policy block.
- Escalate correctly: Submit one BRBL removal request for a listed IP after fixing the cause. For a clean lookup and wanted mail, ask the recipient administrator to report the message as incorrectly blocked.
A 550 rejection does not prove an invalid address
A 550 or 554 response ends that delivery attempt, but a policy rejection does not mean the recipient address is invalid. Fix the cause before sending a new test. RFC 5321 distinguishes permanent 5xx rejections from temporary 4xx replies, which the sending server normally queues and retries.
Why Barracuda blocks email when BRBL is clean
A public reputation lookup checks a narrow slice of the problem. BRBL reports IP reputation, while Barracuda customer systems can also quarantine or block mail using URL reputation, local policy, content scoring, recipient history, sender identity, and the reputation of another IP in the outbound pool. A recipient's gateway also checks configured external real-time blocklists (RBLs); use the log reason to identify the actual list rather than requesting BRBL removal for every rejection.
Visible listing
- Clear signal: The exact outbound IP appears as poor in the Barracuda Reputation System.
- Direct action: Fix the cause, collect proof, then submit one removal request for that IP.
- Main risk: Delisting without fixing the source usually leads to another listing.
Clean lookup
- Hidden signal: Investigate URL reputation, content filters, local sender rules, external RBLs, and every shared-pool IP.
- Best action: Use headers, timestamps, a controlled content test, and the recipient's Message Log reason.
- Main risk: A BRBL removal request has nothing to adjust when the checked IP is not listed.
This is why a sender can be not listed and still see a Barracuda rejection. The rejection text is evidence, but the Message Log reason or a controlled test is needed to identify the blocking layer.
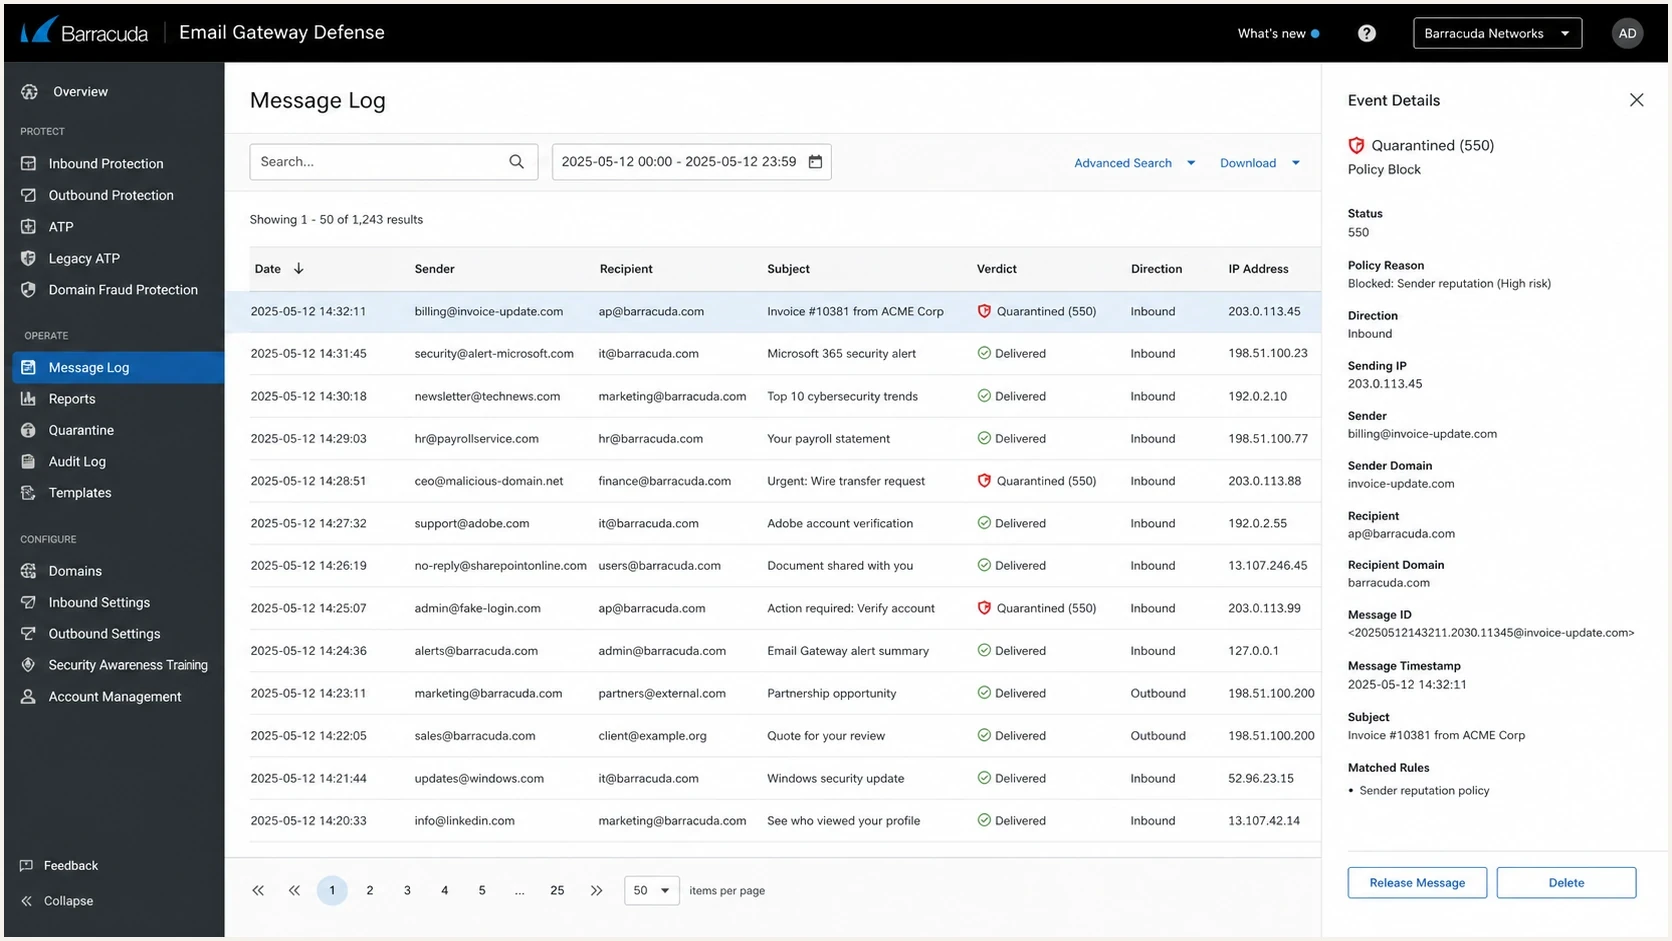
Barracuda Email Gateway Defense Message Log for investigating blocked and quarantined email.
Test message links and content
A clean BRBL lookup with content-specific failures points to the message itself. Barracuda maintains URL reputation separately from IP reputation, so a poorly rated company URL, tracking hostname, redirected destination, or third-party link can cause a block.
- Create a baseline: After pausing the affected campaign, send a short plain-text message without a signature, link, or attachment through the same route to a consenting test recipient.
- Add elements one at a time: Restore the normal signature, links, and attachment separately until the verdict changes.
- Trace every redirect: Record each tracking hostname and final destination instead of checking only the visible link text.
- Inspect owned websites: Check for compromise, injected pages, unexpected redirects, stale DNS, and certificate errors.
- Compare Barracuda reasons: Ask the recipient administrator to compare Message Log reasons for the accepted and blocked samples, then report a legitimate message as incorrectly blocked.
Use isolation as diagnosis
Do not remove required business information merely to bypass filtering. If removing a company URL restores delivery, repair the website or request review of the URL reputation, then repeat the controlled test.
Collect bounce codes and Message Log evidence
Good evidence turns a vague blocklist problem into a supportable case. Collect one rejected sample and one accepted sample if possible. The differences often show whether the issue follows a route, message element, sender identity, or recipient policy.
Bounce evidence templatetext
Timestamp: YYYY-MM-DD HH:MM:SS UTC
Sending IP: 192.0.2.10
Visible From domain: example.com
Envelope sender: sender@example.com
DKIM signing domain: example.com
Recipient: user@recipient.example
Remote host: d136162a.ess.barracudanetworks.com
SMTP reply: [paste the full response, including any enhanced status code]
Barracuda Message Log action: [Blocked, Deferred, Quarantined or Allowed]
Barracuda Message Log reason: [copy the exact reason, if available]
Message ID or mail-server queue ID: [copy from headers or logs]
Message type: 1:1 business reply
Then send a controlled test message and compare the headers. An email tester result shows authentication on that test route; verify the affected recipient's results separately. Barracuda's SMTP error codes distinguish policy rejections from invalid-recipient errors and include a 554 Barracuda Reputation rejection.
|
|
|
|---|---|---|
550 or 554 | Permanent rejection of this attempt | Read the full reason; hold policy-blocked delivery until fixed |
4xx | Temporary deferral | Allow normal queued retries; investigate persistent delays |
Quarantine | Message held by the recipient's gateway | Ask the recipient administrator to review and release wanted mail |
IP shift | A different outbound route | Trace the actual IP and check its reputation |
URL shift | A content or URL-related filter signal | Isolate links and compare Message Log reasons |
DMARC fail | Neither SPF nor DKIM passed with a domain aligned to the visible From domain | Check authentication results and domain matching |
Compact evidence map for Barracuda investigations.
Check email authentication and reverse DNS
Authentication does not guarantee inbox placement, but broken authentication makes reputation recovery harder. Require DMARC to pass through aligned SPF or DKIM using the domain visible in the From address. An SPF failure alone is not a DMARC failure when aligned DKIM passes, although the recipient's separate SPF policy still applies. For a mail server you control, verify that reverse DNS (the PTR record) names the sending host, that hostname resolves back to the sending IP, and the SMTP EHLO/HELO name is valid. Ask the IP owner or mail provider to correct these records when you do not control them.
Illustrative DNS recordstext
Host: _dmarc.example.com
Type: TXT
Value:
v=DMARC1; p=none; rua=mailto:dmarc@example.com

Host: example.com
Type: TXT
Value:
v=spf1 include:mail.example.net -all

Host: selector1._domainkey.example.com
Type: TXT
Value:
v=DKIM1; k=rsa; p=MIIB...
Replace the example domains, SPF include hostname and abbreviated DKIM key with your actual configuration, and use a mailbox that can receive aggregate reports. RFC 9989 marks pct as historic, so omit it from new DMARC records. RFC 9990 defines aggregate reporting. A record with p=none and rua requests reports without requesting quarantine or rejection.
DMARC aggregate reports show reported sending sources and authentication results, but they do not show every SMTP rejection or replace mail-server logs. Old marketing systems, abandoned senders, or shadow tools can keep sending after the visible campaign stops, so remove or authorize each source deliberately.
Suped, our DMARC and email authentication product, connects blocklist monitoring with DMARC reports and SPF and DKIM checks. Compare listing alerts with authentication changes, then use mail-server logs and the recipient's Message Log to establish the rejected message's route and reason.
Blocklist checker
Check your domain or IP against 144 blocklists.





Check for compromised senders and open relays
Barracuda's IP listing guidance names infected mail servers or devices and server misconfiguration as causes of poor reputation. Investigate unexpected outbound mail even when your marketing campaigns are paused.
- Inspect outbound queues and login logs for sudden volume changes, unfamiliar access and senders that continue after a campaign is paused.
- Disable compromised sending accounts, revoke active sessions and exposed credentials, and remove malware from affected devices before restoring access.
- Close open relays. Require authentication or an explicitly authorized source for relaying mail to external recipients, and confirm that an unauthenticated external client cannot relay through the server.
- Restrict direct outbound TCP port 25 to approved mail servers so infected endpoints cannot send spam using the organization's public IP.
For shared infrastructure, ask the mail provider to investigate the listed outbound IP and coordinate delisting. Keep a record of the unauthorized traffic stopped and the controls changed for the removal request.
Improve sending practices and shared-IP reputation
If unwanted outreach or complaints coincide with the incident, pause the affected campaigns. Even a small volume of unwanted mail damages normal business mail when both streams share the same sending identity. Use documented opt-in, honor unsubscribes and suppress confirmed invalid addresses; purchased or scraped lists also expose the sender to spam traps.
Barracuda incident states
Use these operational triggers to choose the next action. They are not Barracuda scoring thresholds.
Trace
One sample
One isolated rejection with clean authentication still needs a route and content comparison.
Investigate
Repeated pattern
Repeated failures tied to one route, link, sender, or recipient need evidence and isolation tests.
Pause
Ongoing failures
An active campaign producing permanent failures must stop while the source is fixed.
If the sender uses a shared IP, record every outbound IP used by the mail platform. Intermittent Barracuda failures often happen when one route in the pool has weaker reputation than the others. Ask the provider that controls the pool to investigate and coordinate removal; changing IPs without stopping the cause invites repeat listings.
What not to do
- Do not resend: Do not automatically retry an unchanged message after a 550 or 554 reply. Investigate the reason before a new controlled test.
- Do not mix: Keep risky prospecting mail away from the domain used for normal business replies. Separating mail streams does not fix unwanted sending.
- Do not guess: Collect logs and controlled test results before changing DNS, content, or routing.
Request Barracuda delisting or a false-positive review
Use the result to choose the escalation path. A confirmed poor IP belongs in the BRBL removal process. A clean IP with a blocked or quarantined message belongs in the recipient's Message Log review and the policy or filter identified by its Reason.
- Confirmed IP listing: Fix the cause first, then submit one Barracuda removal request for the exact outbound IP. Ask the mail provider to coordinate the request if it owns that IP.
- Removal evidence: Provide the email server IP, a valid contact email, a phone number, and a concise explanation of the cause and remediation.
- False positive: Ask the recipient administrator to open the message in Email Gateway Defense, record the Reason, and use Report as Incorrectly Blocked.
- Immediate recipient action: The recipient administrator can release a quarantined message and, where appropriate, create a narrowly scoped sender-policy exemption for wanted mail. This does not remove a global BRBL listing, and virus or other security checks still apply.
- Processing time: Barracuda says requests with a valid explanation are typically investigated and processed within 12 hours. It states that invalid or multiple requests are ignored; processing does not guarantee removal.
This is especially important for Barracuda bounces that identify a policy block rather than a public listing. Quarantined mail is held in the recipient's gateway, which is different from an SMTP rejection. The receiving organization can see the Message Log event and policy reason that the sender cannot see.
Where Suped fits
Suped centralizes DMARC reports, authentication checks, blocklist monitoring, and deliverability alerts. Use these signals to identify a reported sending source or authentication change around the Barracuda incident, then match it to SMTP evidence.

Blocklist monitoring page showing domain and IP checks across blocklists with importance and status
Teams need to identify the sender involved, verify authentication, confirm whether a blacklist listing is active, and watch for the same issue after recovery. Suped's monitoring supports these checks; it does not request Barracuda delisting or reveal the recipient's private filtering rules.
Mail-server and recipient evidence
- SMTP details: Collect the actual outbound IP and complete rejection from the sending server.
- Message Log: Ask the recipient administrator for the action and reason on the affected message.
- Incident owner: Assign the next step to the team that controls the sending account, DNS or shared IP.
Suped monitoring workflow
- Authentication context: Review DMARC reports and SPF and DKIM results for the reported sending sources.
- Listing alerts: Track blocklist status changes for monitored IPs during remediation.
- Recovery checks: Compare monitoring results after the fix, then confirm delivery with the recipient.
Verify recovery and prevent recurrence
Resume with a small volume of wanted mail after the cause is fixed. Confirm the exact affected IP is no longer listed, test delivery through every relevant outbound route, and ask the recipient administrator to verify the Message Log action.
Monitor new rejections, complaints and authentication results during the restart. A clean BRBL result does not prove that a recipient's separate content or policy filter has cleared.
Keep Suped's DMARC and blocklist monitoring active after recovery, with an assigned owner for new alerts. Maintain opt-in records and suppression lists, and review unexpected sending sources before they cause another incident.
Frequently asked questions
A clean BRBL lookup shows that the checked IP is not reported as poor at that moment. Barracuda can still block a message because of URL reputation, another shared-pool IP, content scoring, sender policy, or recipient rules.
Barracuda says removal requests with valid information are typically investigated and processed within 12 hours. That timing is not a guarantee of removal. Fix the cause before submitting and do not send multiple requests.
No. Stop automatic retries after a 550 or 554 rejection, then read the complete reason. Permanently suppress confirmed invalid addresses; hold valid recipients affected by policy blocks until the cause is fixed. Temporary 4xx deferrals normally stay queued for retry.
DMARC does not remove a Barracuda blocklist (blacklist) entry. It checks whether a passing SPF or DKIM domain matches the visible From domain under its DMARC alignment policy and provides reports that help identify unauthorized or forgotten senders. Authentication passing does not guarantee inbox placement.
The receiving organization's administrator can see the Message Log reason and use Report as Incorrectly Blocked. The sender should provide the timestamp, sending IP, recipient, SMTP response, headers, and a concise explanation. If the message is quarantined, the administrator can also release wanted mail after reviewing the reason.
Yes. Barracuda uses URL reputation as well as IP reputation. Test a plain-text baseline, then add the signature, links, redirects, and attachments separately to identify the element associated with the block.




