Why is my DMARC success rate suddenly dropping, and how does this affect spam rates and blocklists?
Published 12 Jul 2025
Updated 19 Oct 2026
13 min read
Summarize with
Updated on 25 Oct 2026: We clarified DMARC pass-rate targets and added checks for SPF errors, sender ownership, and recovery after DNS changes.
A sudden drop in your DMARC success rate means a larger share of reported mail using your domain is failing DMARC. That includes legitimate mail with authentication problems and forged mail using your visible From domain. A change in report coverage can also change the percentage. Start with the source data in your aggregate reports.
A drop from 100% to 63% warrants investigation. Check for source changes, then rule out reporting differences. A sales team can add a cold outreach platform, a marketing team can move a campaign, a billing system can start sending receipts, or an attacker can start spoofing the domain. Each one looks different in DMARC monitoring data because the source IP, SPF domain, DKIM domain, and final DMARC result are visible.
This does not automatically explain a spike in user-reported spam, and it does not automatically explain a blocklist or blacklist listing. Those symptoms can share a root cause, but different systems measure them. Separate the evidence before opening a delisting request or changing DNS and policy.
What the DMARC drop actually means
DMARC passes when at least one authentication path passes and its domain matches the visible From domain. Either SPF passes for an aligned MAIL FROM domain, or a valid DKIM signature uses an aligned signing domain. A raw SPF or DKIM pass for an unrelated domain does not make DMARC pass. Relaxed alignment, the default, requires the same organizational domain; strict alignment requires an exact domain match. Check aspf and adkim if a policy edit preceded the drop. See Microsoft's alignment guidance.
Example success-rate change
Illustrative reported traffic: 63% passes DMARC and 37% fails. The failed share can include forged mail.
Pass
Fail
The percentage is also sensitive to volume and report coverage. At low volume, a small burst of failed mail can move the rate sharply. At high volume, a drop that large usually means a meaningful stream changed. Compare the same reporting window and reporting organizations, then confirm that late or duplicate reports did not distort either period.
Do not weaken your DMARC policy as the first move. A weaker policy changes requested receiver handling, but it does not repair SPF or DKIM. First identify whether the failing mail is yours, a vendor's, a forwarded stream, or a forgery.
- Known sender: Fix SPF, DKIM, or the visible From domain used by that sender.
- Unknown sender: Check sender ownership and forwarding before classifying the source; do not authorize an unfamiliar IP just to raise the pass rate.
- Shared IP: Separate IP reputation from your domain's authentication results.
- Low volume: Check message counts before treating the percentage as a crisis.
What DMARC pass rate should you target?
Calculate the DMARC pass rate using message counts: passing messages divided by all DMARC-evaluated messages in the selected report set, multiplied by 100. Count a message as passing when either aligned SPF or aligned DKIM passes. Add the message counts across report rows before dividing; averaging row percentages gives small sources too much weight.
For example, 630 legitimate messages passing DMARC plus 370 forged messages failing DMARC produce a 63% overall pass rate. The legitimate sender still has a 100% pass rate. Rejected spoofing attempts can remain in aggregate reports after p=reject is enabled, so enforcement does not guarantee a higher overall percentage. See the aggregate reporting specification.
Aim for every authorized sending stream to pass DMARC consistently, and investigate failures by source. There is no universal 95% or 98% overall DMARC pass-rate threshold that guarantees inbox placement. Track known-sender authentication separately from spoofing volume. Invalid recipient addresses cause delivery failures; they do not, by themselves, make SPF or DKIM fail.
Common causes of a sudden DMARC pass-rate drop
When a domain's DMARC pass rate falls overnight, check for source changes as well as record changes. New senders, changed return paths, and broken DKIM selectors can each explain the drop.
|
|
|
|---|---|---|
New sender | Known service, new IP | Enable aligned DKIM or SPF |
Return-path change | SPF passes, DMARC fails | Use an aligned domain |
Forwarding or mailing lists | SPF fails; changed signed content also breaks DKIM | Preserve aligned DKIM and review receiver overrides |
Spoofing | Unexplained source after sender and forwarding checks | Enforce policy after review |
DNS or key change | DKIM fail or temperror | Restore the selector or DNS |
SPF lookup limit | SPF permerror after nested include changes | Reduce DNS-lookup-causing terms to 10 or fewer |
Strict alignment change | Subdomain used with aspf=s or adkim=s | Use the exact domain or review the alignment mode |
Use this as a first-pass triage map.
A large failed volume from an unfamiliar IP range warrants investigation. Check your sender inventory and sending logs, including forwarding routes, before calling it spoofing. An IP belonging to a platform your company uses is not enough to prove ownership because other customers share that infrastructure.
An SPF permerror can also indicate multiple SPF records at the same DNS name. Nested includes count toward the 10-term DNS lookup limit even when your own record did not change. After DKIM key rotation, confirm that the active selector still resolves to the correct public key. These SPF limits are defined in RFC 7208.
Legitimate mail failing
Prioritize these failures because legitimate messages risk rejection or spam-folder placement.
- Sender match: Match the source IP and authenticated domains to an approved sending account and your logs.
- Fix path: Configure aligned DKIM or SPF for that sender.
- Business risk: Delivery and reputation can both be affected.
Forged mail failing
This is still important, but it is not the same as your own mail being broken.
- Sender match: The source remains unexplained after checking approved senders and forwarding routes.
- Fix path: Move policy toward quarantine or reject after review.
- Business risk: Brand misuse is the main issue, not your normal sending setup.
How spam rates and blocklists fit in
User-reported spam rates are not caused by DMARC failures in a direct mechanical way. Recipients do not see a DMARC pass or fail label in the inbox. They report spam because of message content, weak consent, excessive frequency, irrelevant targeting, unwanted sales outreach, or mail sent to the wrong people.
DMARC failures can still affect spam-folder placement or SMTP rejection. A quarantine policy requests suspicious-message handling, commonly the junk folder, while reject requests refusal; receivers apply their own filtering rules. With p=none, those filters still operate. Microsoft's DMARC handling documentation separates the authentication result from the handling action.
A DMARC pass proves aligned domain authentication, not inbox placement. Domain and IP reputation, sudden volume changes, sending consistency, list quality, content, and recipient response still affect filtering. The same new stream can therefore cause DMARC failures and complaints for different reasons. A poorly configured outreach platform is a good example: authentication explains the DMARC drop, while consent and targeting explain the complaint spike. DMARC aggregate reports do not contain user complaint counts or prove inbox placement. Compare complaint counts as well as rates: the same count produces a higher percentage when fewer messages enter the provider's calculation.
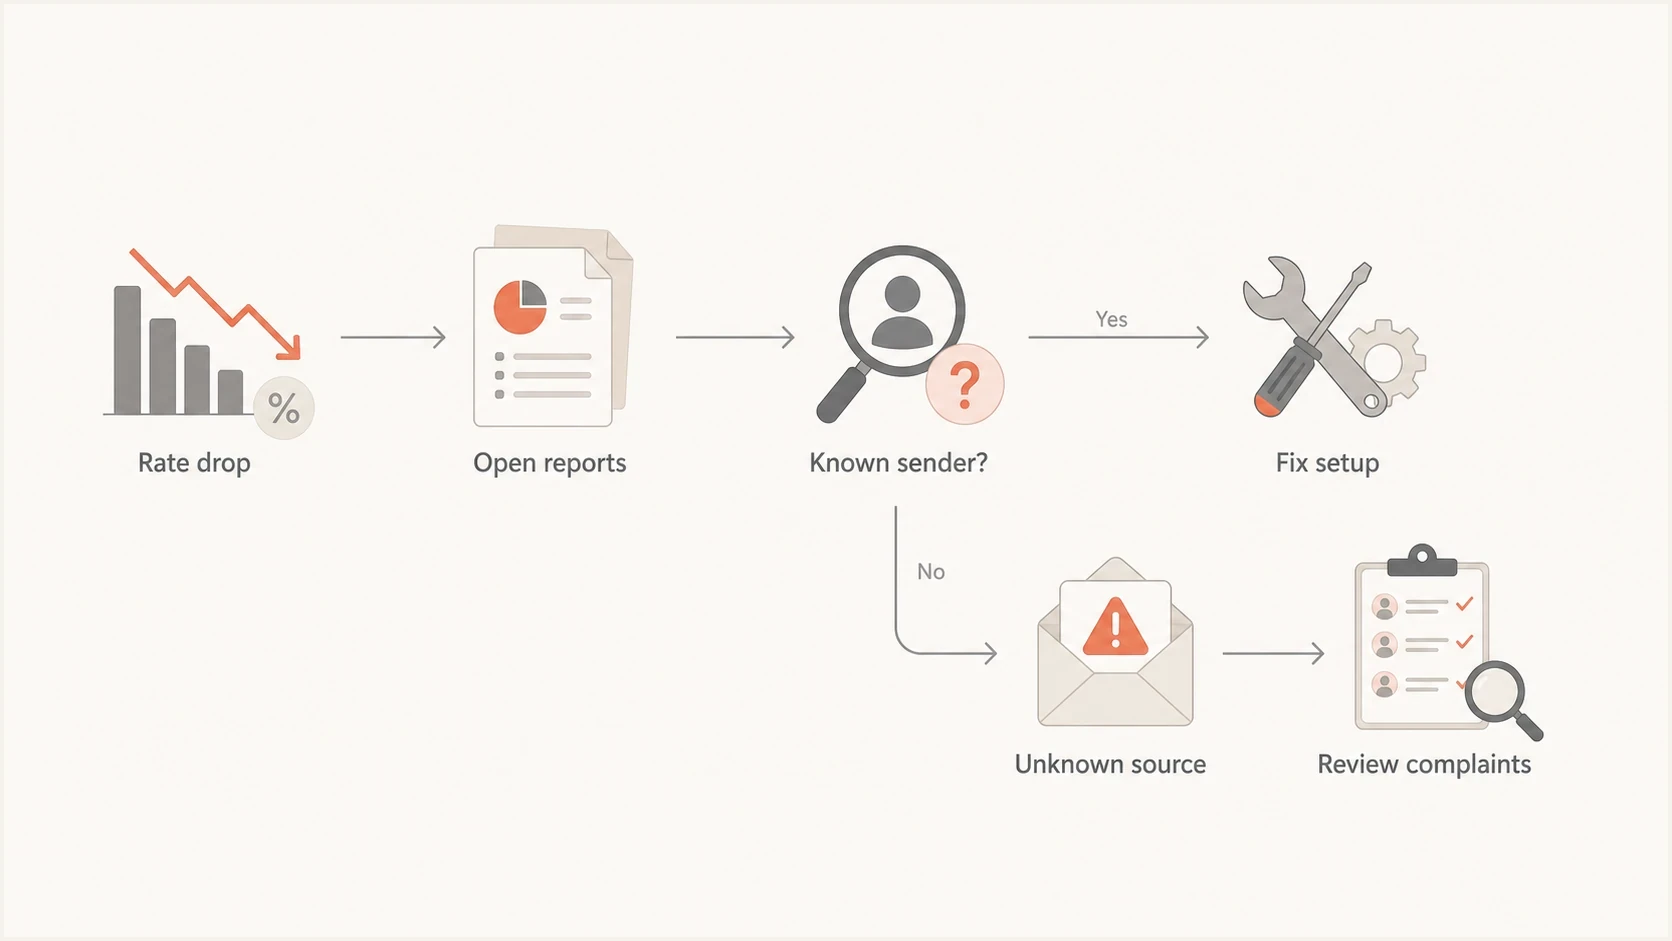
DMARC troubleshooting flowchart for checking reports, identifying senders, and reviewing spam complaints.
Blocklist (blacklist) issues need the same separation. A public listing does not happen just because DMARC failed. Listing criteria vary by operator and include abusive sending behavior or spam-trap hits. If your listing is on a shared IP, another sender on that IP pool can be responsible.
A blocklist result matters most when you can tie it to delivery evidence. Look for bounce messages or rejection logs that name the blacklist. A listing you found only after searching is a data point, not proof that it caused delivery trouble. Fix the sending cause before requesting removal.
- IP listing: Check whether the IP is shared and whether rejects cite the listing.
- Domain listing: Identify which domain or message URL is listed, read the reason, and match it to rejection logs.
- No rejects: Prioritize DMARC reports and complaint evidence first.
Check DNS and DMARC aggregate reports
Start with the DMARC policy record in DNS at _dmarc for the visible From domain, such as _dmarc.example.com. Confirm that exactly one DMARC TXT record is published there, or check the inherited policy if that name has no record. Confirm that the aggregate-report destination receives data. If you do not control DNS, ask the team that does to confirm the record and destination.
Example DMARC monitoring recorddns
_dmarc.example.com TXT
v=DMARC1; p=none; rua=mailto:dmarc-reports@example.com;
This p=none example is for an initial monitoring setup. Keep an existing enforcement policy while investigating; changing policy does not repair authentication. If rua sends reports to another domain, confirm that the report destination has authorized external reporting.
If you only need to confirm the published record, use a DMARC checker. If the question is broader, including SPF, DKIM, DMARC, and domain reputation, run a domain health check and then compare that with the aggregate report data.
?
What's your domain score?
Deep-scan SPF, DKIM & DMARC records for email deliverability and security issues.
Then open the aggregate reports and group failures by source. Prioritize the source and failed message count before the overall percentage. A single unverified source with 50 messages has a different response than a company-owned platform sending 500,000 failing messages.
- Source IP: Identify whether the IP is a known sender, shared platform, or unknown host.
- SPF result: Check whether SPF passed and which MAIL FROM domain was evaluated.
- DKIM result: Check whether DKIM passed, its signing domain (d=), and the selector (s=) used to find the public key.
- Header From: Confirm the visible domain that DMARC used for the final decision.
- Message count: Sort by volume so low-risk noise does not distract from the main cause.
- Disposition and override: Check what the receiver did and whether local policy, forwarding, or a mailing list changed the requested handling.
In the XML, auth_results contains raw SPF and DKIM outcomes, while policy_evaluated contains their DMARC alignment outcomes. A raw pass with an alignment failure points to a domain mismatch. Use Microsoft's report-field examples to distinguish them. After a fix, send a fresh message through the affected sender and inspect the receiving server's Authentication-Results header. Confirm dmarc=pass and the expected authenticated domain.
Allow for DNS caching and the next reporting cycle when validating recovery. RFC 9990 describes daily or more frequent aggregate feedback, but arrival can lag. Compare the report's covered time range with the fix time; an old failure appearing in a newly received file is not a new failure.
For a deeper walkthrough, keep a separate failure troubleshooting process for recurring failures. The one-day triage should still begin with report grouping and source ownership.
What RFC 9989 changed
- Review pct: RFC 9989 marks pct historic. Its presence does not invalidate an otherwise valid record, but it is no longer a reliable percentage-rollout control.
- Use test mode carefully: Under RFC 9989, t=y requests quarantine instead of reject, or none instead of quarantine. It has no effect on p=none; older receivers that ignore t=y can apply the full p policy.
- Check inherited policy: DNS Tree Walk replaced the older public-suffix-list method for policy discovery.
- Handle unused names: The np tag can set a policy for non-existent subdomains of an organizational domain.
These changes do not alter the first diagnostic step. Use RFC 9990 aggregate data to find the source, authenticated domains, result, disposition, override reason, and volume behind the rate drop. Failure reports can contain message-level detail, but receivers choose whether to send them and apply their own privacy rules.
Investigate failed senders with Suped
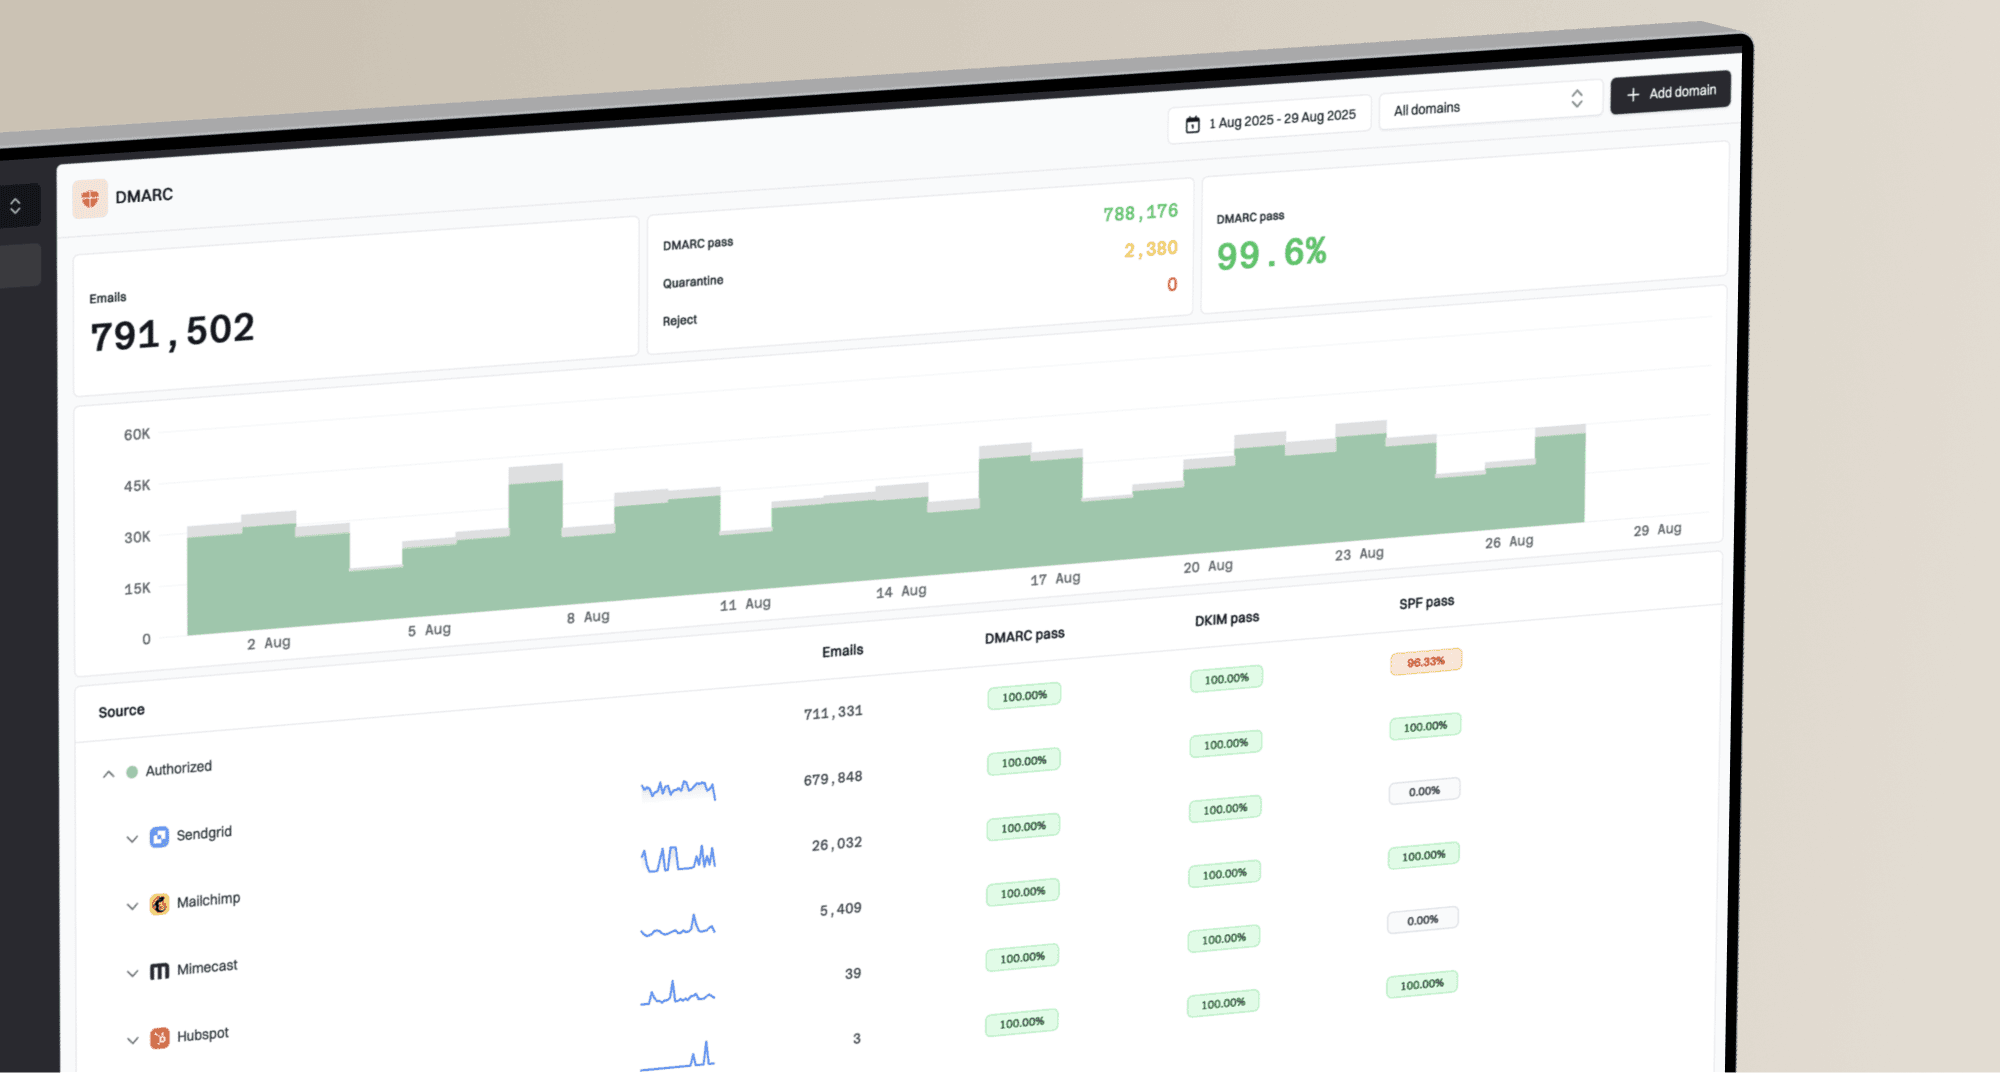
Suped's product turns aggregate reports into source groups, pass rates, issue detection, and remediation steps. This replaces manual XML review with a workflow that connects each failed source to its SPF result, DKIM result, message volume, and ownership status.
Issues page showing top issues, verified sources, unverified sources, and authentication pass rates
Identify the failing source, confirm whether it belongs to the business, fix an authorized sender's setup, and monitor that source's pass rate. Suped can alert the team when new report data shows a failing source. Hosted DMARC supports policy staging after the DNS handoff. Compare Suped's blocklist monitoring results with your sending provider's rejection logs to establish delivery impact.
If you lack DNS access, Suped's Hosted DMARC is useful because engineering can set the required DNS once, then the mail or security team can manage policy staging in Suped. That avoids a ticket every time the policy needs to move.
- Detection: Surface new failing senders when aggregate data arrives.
- Remediation: Show concrete steps for SPF, DKIM, and DMARC fixes.
- Scale: Use multi-tenant views for agencies and managed service providers.
- Reputation: Track blacklist data alongside authentication results and compare it with delivery evidence.
A practical triage order
If the DMARC rate dropped, spam complaints rose, and a blacklist appeared at the same time, handle the evidence in this order. Compare the affected sending streams and reporting windows before assuming a common cause.
- Confirm volume: Check failed message counts, matching report windows, and receiver coverage before judging the percentage.
- Map sources: Group failures by source IP and authenticated domain before editing DNS.
- Own the source: Check approved sending accounts and forwarding routes before classifying the source as legitimate or forged.
- Review complaints: Compare complaint rates and denominators with recent campaigns, list acquisition, consent, and targeting changes.
- Check rejects: Treat a blocklist as urgent when rejection logs name it, then review bounce and spam-trap patterns.
- Fix and watch: Apply the sender fix, then monitor source volume, DMARC pass rate, complaints, and provider-specific rejects.
The correct first fix depends on the source. If the failing mail is yours, configure the sender. If the failing mail is forged, keep legitimate senders passing and move the DMARC policy toward enforcement. If the blacklist is only on a shared IP and there are no rejects, treat it as supporting context rather than the root cause. If the apparent drop came from a different report mix, correct the comparison before changing the sender setup. Stop or slow campaigns generating unwanted-mail complaints while investigating them.
Views from the trenches
Best practices
Separate your known senders from unknown sources before changing policy or DNS records.
Keep a current sender inventory so sales, marketing, billing, and support mail are visible.
Compare report volume by source IP before treating a percentage drop as a delivery crisis.
Common pitfalls
Assuming a blacklist listing caused DMARC failure wastes time when the listing is IP based.
Weakening policy first changes handling but leaves the authentication fault unresolved.
Reading only one mailbox provider's dashboard can miss where the failing source started.
Expert tips
Ask for bounce evidence before treating a blocklist or blacklist result as delivery impact.
Check whether sales outreach uses the same visible domain and has a proper DKIM signature.
Use aggregate reports to prove whether a failing IP belongs to your mail stack today.
Expert view
Expert from Email Geeks says a sudden DMARC drop means mail using the domain failed authentication, and aggregate reports show the source IP, SPF domain, DKIM domain, and result.
2020-12-01 - Email Geeks
Marketer view
Marketer from Email Geeks says user complaint data needs to be tied to the actual message stream before it can be connected to a DMARC drop.
2020-12-01 - Email Geeks
Frequently asked questions
Not directly. Users report spam because of the message they receive. DMARC failure is invisible to most recipients. The same bad sending stream can cause both a DMARC drop and complaints.
A DMARC mismatch does not automatically create a blacklist listing. Listings depend on the operator's criteria, including abusive sending or spam-trap hits. Check the listing reason and whether rejection logs cite it.
No. First find the failing source. If the mail is legitimate, fix authentication. If the mail is forged, move policy toward enforcement after confirming legitimate senders pass.
Ask the DNS owner to confirm the DMARC TXT record and report destination. With Suped's Hosted DMARC, engineering can set DNS once while the mail team manages policy staging later.
Start with source IP, SPF domain, DKIM domain, Header From domain, final DMARC result, disposition, policy override reason, and message count. Compare those fields with your sender inventory and sending logs to establish ownership and how the receiver handled the mail.
Yes. A partial reporting window, late files, duplicate data, or a changed mix of reporting organizations can distort a comparison. Match the time range and report coverage before treating the percentage as a sending change. After a DNS fix, compare each report's covered time range with the fix time and confirm current authentication using a fresh message.