Why are legitimate emails blocked when DMARC policy is higher than p=none?
Published 9 Jun 2025
Updated 9 Oct 2026
14 min read
Summarize with
Updated on 9 Oct 2026: We clarified alignment failures and safer DMARC enforcement, including test-mode limits and checks for blocked legitimate mail.
Legitimate emails are blocked when DMARC moves beyond p=none because enforcement requests stricter handling of messages that fail DMARC. At p=quarantine, a receiving mailbox provider can place failing mail in spam. At p=reject, a receiver can reject failing mail during SMTP after considering the published policy with its own evidence and local rules. The usual cause is simple: the message did not pass SPF or DKIM in alignment with the visible From domain.
DMARC enforcement exposes sending paths that lack authenticated domain alignment. Those failures are operational signals: fix the sender, authenticate the mail, move it to a dedicated sending domain, or stop that sender from using the domain.
- Main cause: The email fails DMARC because neither SPF nor DKIM passes with domain alignment.
- Common trigger: A CRM, ESP, helpdesk, calendar app, billing system, or marketing tool sends without proper authentication.
- Important caveat: A message can pass DMARC and still be blocked for reputation, content, complaint rate, spam-trap history, or recipient-side policy.
How DMARC enforcement blocks legitimate email
DMARC checks authenticated domain identity rather than the sender's business intent. A failed DMARC result lets the receiving system apply the published policy as one input to its local handling decision. A legitimate business email can still fail DMARC when the technical identity in the message does not match the domain the recipient sees in the From header.
The key phrase is "aligned authentication." SPF checks whether the sending IP is allowed for the SMTP MAIL FROM domain, also called the envelope sender or return-path domain. DKIM verifies a message signature against the signing domain's published key. DMARC then asks whether either passing result aligns with the visible From domain. If neither mechanism supplies an aligned pass, DMARC fails. One valid, aligned DKIM signature is enough even if another DKIM signature fails.
A stricter policy changes the requested consequence, not the authentication math. The same broken sender that quietly appeared in reports under p=none starts causing user-visible damage when you publish p=quarantine or p=reject.
This is why DMARC should be treated as a monitored rollout, not a one-line DNS change. Suped's DMARC monitoring supports that workflow by identifying sending sources, separating business mail from spoofing, and showing the authentication fixes needed before enforcement causes avoidable blocking.
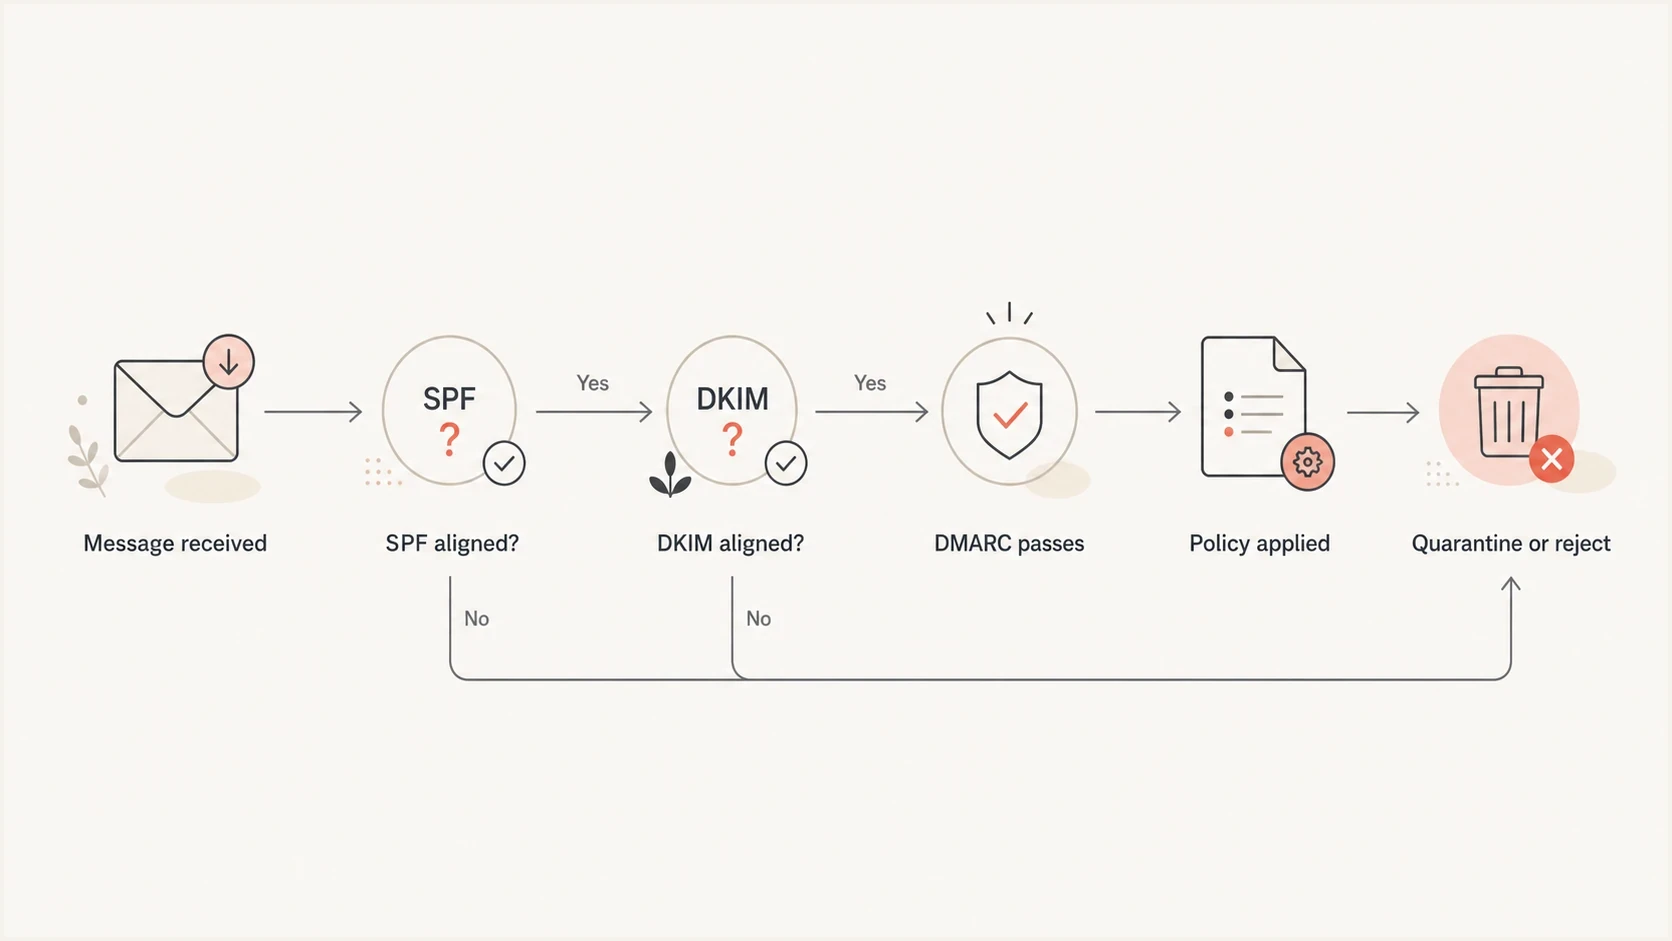
DMARC decision path showing how SPF or DKIM alignment determines a pass or policy evaluation.
Why delivery changes after p=none
A p=none policy requests no DMARC-specific quarantine or rejection. Aggregate reports require a valid rua destination and a receiver that sends reports. It is the right starting point for collecting evidence, but a receiver can still filter or reject mail for reasons unrelated to DMARC. Broken mail can therefore keep flowing while you map sending sources.
When you move to enforcement, the same underlying failures become visible to users. The sales team notices a CRM email in spam. Finance sees an invoice notification bounce. A calendar cancellation fails where the original invitation delivered. These are not new failures created by DMARC. They are existing authentication gaps becoming consequential.
Before enforcement
- Policy effect: Receivers that send aggregate reports expose DMARC failures without a requested quarantine or reject policy.
- Business impact: Misconfigured senders continue sending, so teams often do not notice the risk.
After enforcement
- Policy effect: Receivers can quarantine or reject mail that fails aligned authentication after applying local rules.
- Business impact: Unknown senders, broken DKIM, forwarding paths, and shared tools can fail visibly.
Before raising a policy, collect enough report history to identify every important sending source, including infrequent workflows such as month-end invoices. Aggregate reports are typically daily summaries, not a complete message log; use delivery logs and test messages to cover gaps.
The main causes of legitimate blocking
The most common failure pattern is not mysterious. A tool sends mail with your visible From domain, but SPF authorizes a different envelope domain or DKIM signs with the tool's domain instead of your domain. The message might be legitimate to the business, but it is not authenticated as legitimate for your domain under DMARC.
|
|
|
|---|---|---|
ESP setup | DKIM alignment | Enable custom DKIM signing with your domain |
CRM mail | SPF alignment | Configure a custom MAIL FROM domain under your domain |
Forwarding | SPF; DKIM if signed content changes | Rely on aligned DKIM |
Rogue sender | SPF, DKIM | Authorize or remove |
Calendar invites | SPF or DKIM after message changes | Test invite flows |
Subdomain sender | Inherited policy or alignment | Check the effective policy and configure subdomain authentication |
SPF record errors | SPF permerror | Keep one SPF record and stay within the DNS-lookup limit |
DKIM key or selector errors | DKIM verification | Publish the active selector's key and confirm signing is enabled |
Common causes of legitimate mail failing under DMARC enforcement.
Publishing DKIM DNS records alone does not enable signing. SPF returns permerror for multiple SPF records or when evaluation exceeds its limit of 10 DNS-lookup mechanisms and modifiers, including nested includes. These errors cause a DMARC failure only when no other aligned authentication passes.
Forwarding is a special case because SPF is tied to the sending IP. Once another server forwards the message, SPF often fails because the forwarder is not listed in the original sender's SPF record. DKIM should survive simple forwarding, but it breaks when a system modifies signed headers, rewrites the body, alters MIME boundaries, appends footers, or changes calendar parts. ARC can preserve the original authentication results across an intermediary, but it does not make the message pass DMARC. The final receiver decides whether to trust the ARC chain as local evidence.
Rogue sending is the other recurring cause. Someone in the business opens a marketing, survey, billing, scheduling, or support account and sends as the company domain without telling IT. Under p=none, that might work by luck. Under enforcement, it breaks because no aligned authentication was configured.
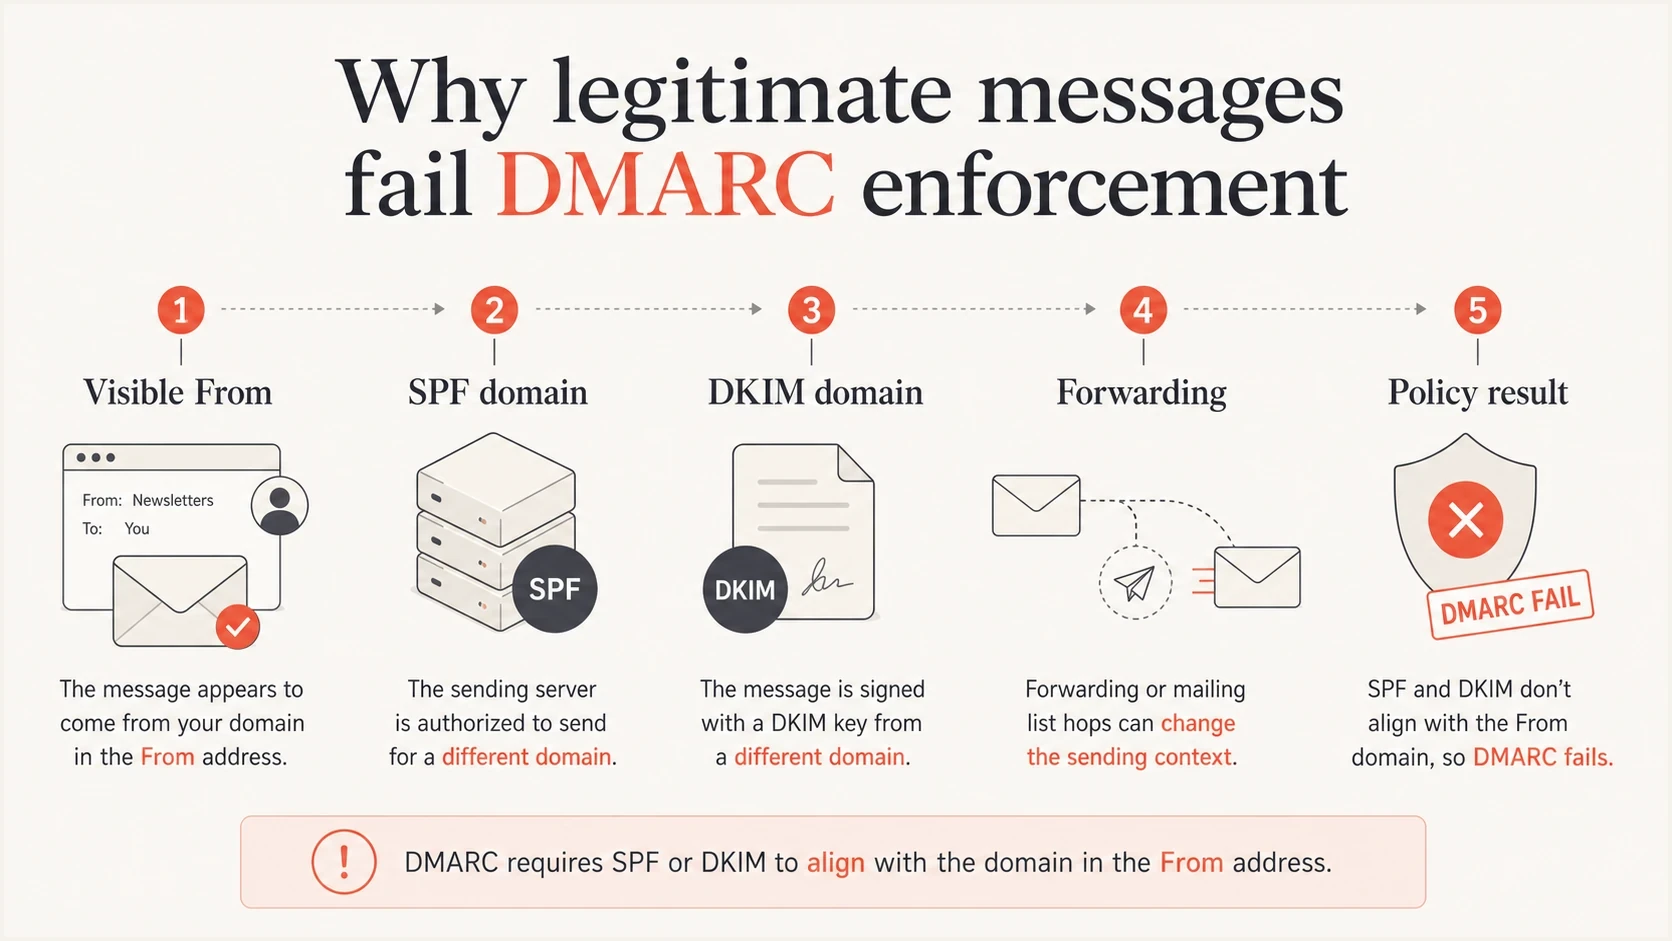
DMARC failure causes showing mismatched From, SPF, and DKIM domains alongside email forwarding.
Why SPF and DKIM can pass while DMARC fails
A valid DMARC reject record can expose sender configuration problems. For example:
DMARC reject policy exampledns
_dmarc.example.com. 3600 IN TXT (
  "v=DMARC1; p=reject; rua=mailto:dmarc@example.com"
)
If that domain has a helpdesk sending as support@example.com, the helpdesk needs aligned DKIM or aligned SPF. A vendor DKIM signature such as d=vendor.example does not protect example.com for DMARC. An envelope sender such as bounces.vendor.example is not aligned with example.com because it belongs to a different organizational domain.
Simplified authentication resulttext
From: support@example.com
SPF: pass for bounces.vendor.example
DKIM: pass with d=vendor.example
DMARC: fail because neither result aligns with example.com
Configure the sender with custom DKIM using the vendor's CNAME or TXT records, or an authenticated custom bounce domain under your domain. Adding a vendor to SPF at example.com does not fix alignment while MAIL FROM remains bounces.vendor.example. Moving mail to mail.example.com still requires aligned authentication and an effective subdomain policy; without its own applicable DMARC record, it can inherit the parent policy.
DMARC checker
Look up a domain's DMARC record and catch policy issues.
?/7tests passed
If you are unsure whether the published record says what you think it says, validate it with the DMARC checker before changing policy. Then compare the DNS record to real aggregate reports, because the record alone does not tell you which senders are ready.
How strict and relaxed alignment affect legitimate mail
DMARC enforcement and strict alignment are separate settings. The adkim tag controls DKIM alignment and aspf controls SPF alignment. Both default to relaxed mode (r), which requires the same organizational domain. Strict mode (s) requires an exact domain match.
|
|
|
|---|---|---|
example.com | Pass | Pass |
bounces.example.com | Pass | Fail |
vendor.example | Fail | Fail |
Assumes From: support@example.com and example.com is the organizational domain for these examples. Each result also requires an SPF or DKIM authentication pass.
A custom return-path at bounces.example.com therefore works with aspf=r but fails with aspf=s. Check the configured DKIM signing domain before changing adkim, and avoid tightening policy and alignment settings in the same rollout.
Passing DMARC does not guarantee inbox placement
One point gets missed in DMARC rollouts: authentication helps mailbox providers identify the sender, but it does not force delivery. A sender can pass SPF, DKIM, and DMARC and still be blocked because the authenticated identity has poor reputation or the message trips other filters.
- Complaints: High spam complaints can override technically correct authentication.
- Engagement: Recipient behavior, including spam reports and deletions, can influence mailbox-specific filtering.
- Content: Suspicious URLs, attachments, wording, or inconsistent branding can still trigger filtering.
- Reputation: The domain, subdomain, IP, and DKIM identity each contribute signals receivers can use.
If the blocking receiver records dmarc=pass, investigate its other filtering rules. A pass recorded before forwarding does not establish the result at the final receiver. Check reputation, content, recipient policy, and blocklist (blacklist) status.
This distinction matters because lowering DMARC to p=none will not fix a reputation problem. It reduces protection against unauthenticated use of your exact From domain. DMARC does not stop someone using a separate lookalike domain. Treat authentication and deliverability signals as separate issues.
What RFC 9989 changes about enforcement
RFC 9989 replaced RFC 7489 as the core DMARC specification. It keeps the familiar policy values, marks the pct percentage tag as historic, adds policy test mode, and gives clearer guidance for indirect mail flows such as forwarding, role aliases, and mailing lists.
- Test mode: Use t=y to request handling one policy level below the published policy at receivers that support it; reporting is unaffected.
- General-purpose mail: Domains used by people who post to mailing lists should generally avoid p=reject because indirect mail can break alignment.
- Receiver decisions: RFC 9989 recommends that receivers consider other evidence rather than reject solely because a domain publishes p=reject.
- Subdomain policy: The sp tag covers existing subdomains without their own applicable policy record. The np tag states policy for non-existent subdomains.
RFC 9989 test mode exampledns
_dmarc.example.com. 3600 IN TXT (
  "v=DMARC1; p=reject; t=y; rua=mailto:dmarc@example.com"
)
With p=reject; t=y, RFC 9989 asks receivers to apply quarantine to DMARC failures. With p=quarantine; t=y, it asks them to apply no DMARC policy handling. Older receivers ignore t=y and can still reject mail under p=reject. Test mode is not a universal rollback mechanism.
How to move beyond p=none safely
Do not jump to p=reject until reports show that important business mail consistently passes aligned SPF or DKIM and indirect mail has been assessed. Do not stay at p=none indefinitely either. For a general-purpose domain, p=quarantine can be the right enforcement policy. Reserve p=reject for controlled mail streams where its interoperability cost is understood.
Policy rollout readiness
Use DMARC pass rate and source confidence together. A high pass rate is not enough if unknown senders still send important mail.
Monitor
p=none
Inventory senders and fix visible authentication failures.
Test
t=y
Supported receivers use one policy level lower; older receivers still apply p.
Enforce
p=quarantine or p=reject
Choose quarantine or reject based on the domain's actual mail flows.
Use a checklist that makes ownership clear. Each sending source should have a named business owner, an authentication method, and a decision: approve, fix, isolate on a subdomain, or shut down.
- Inventory: List every IP, platform, and vendor seen in aggregate reports.
- Classify: Separate approved business mail, unknown mail, spoofing, and retired systems.
- Fix: Configure aligned DKIM first, then use SPF alignment where the platform supports it cleanly.
- Stage: Start with quarantine before reject; use t=y only where receiver support is known, and test human mail and calendar workflows.
- Watch: Review failures after each policy change and keep a rollback plan for critical flows.
Suped's domain health checker helps with the first pass by checking DMARC, SPF, and DKIM DNS health in one place. That does not replace report analysis, but it catches obvious record problems before a policy change.
?
What's your domain score?
Deep-scan SPF, DKIM & DMARC records for email deliverability and security issues.
Once DNS checks are clean, compare DMARC reports with fresh test messages through each important workflow. A healthy record does not prove that a platform is signing mail or that forwarded messages retain an aligned pass.
What to do when legitimate mail is already blocked
When a user reports a blocked message after enforcement, start with the headers or bounce. Capture the receiver's DMARC result, SPF result, DKIM result, envelope sender, visible From domain, DKIM signing domain, sending IP, and SMTP status text. Read Authentication-Results added by the receiving system; a sender-supplied header is not proof of authentication at that receiver.
A 550 5.7.26 response can report a DMARC rejection, but read the full text because that code also covers other authentication failures. A 554 5.7.5 label alone does not identify a DMARC syntax error; 5.7.5 is a broader cryptographic-failure status.
For a business-critical outage, a temporary p=none rollback can reduce DMARC-related rejection while the sender is repaired. Record the reason, assign an owner, set a deadline to restore enforcement, and account for DNS caching.
The faster fix depends on the failure. If DKIM is absent, enable custom DKIM at the platform and publish the CNAME or TXT records. If DKIM passes but does not match the From domain, switch the sender to sign with your domain. If SPF passes for a vendor domain only, configure a custom return-path or bounce domain if the vendor supports it. If forwarding is the issue, preserve signed content and inspect intermediary changes. DKIM must still sign the From header.
After DNS or signing changes, account for cached records until their TTL expires, then send fresh messages through the failing workflow. Mail already rejected with a permanent 5xx response is not automatically recovered; resend it after verifying the fix. Temporary 4xx failures normally remain in the sender's retry queue.
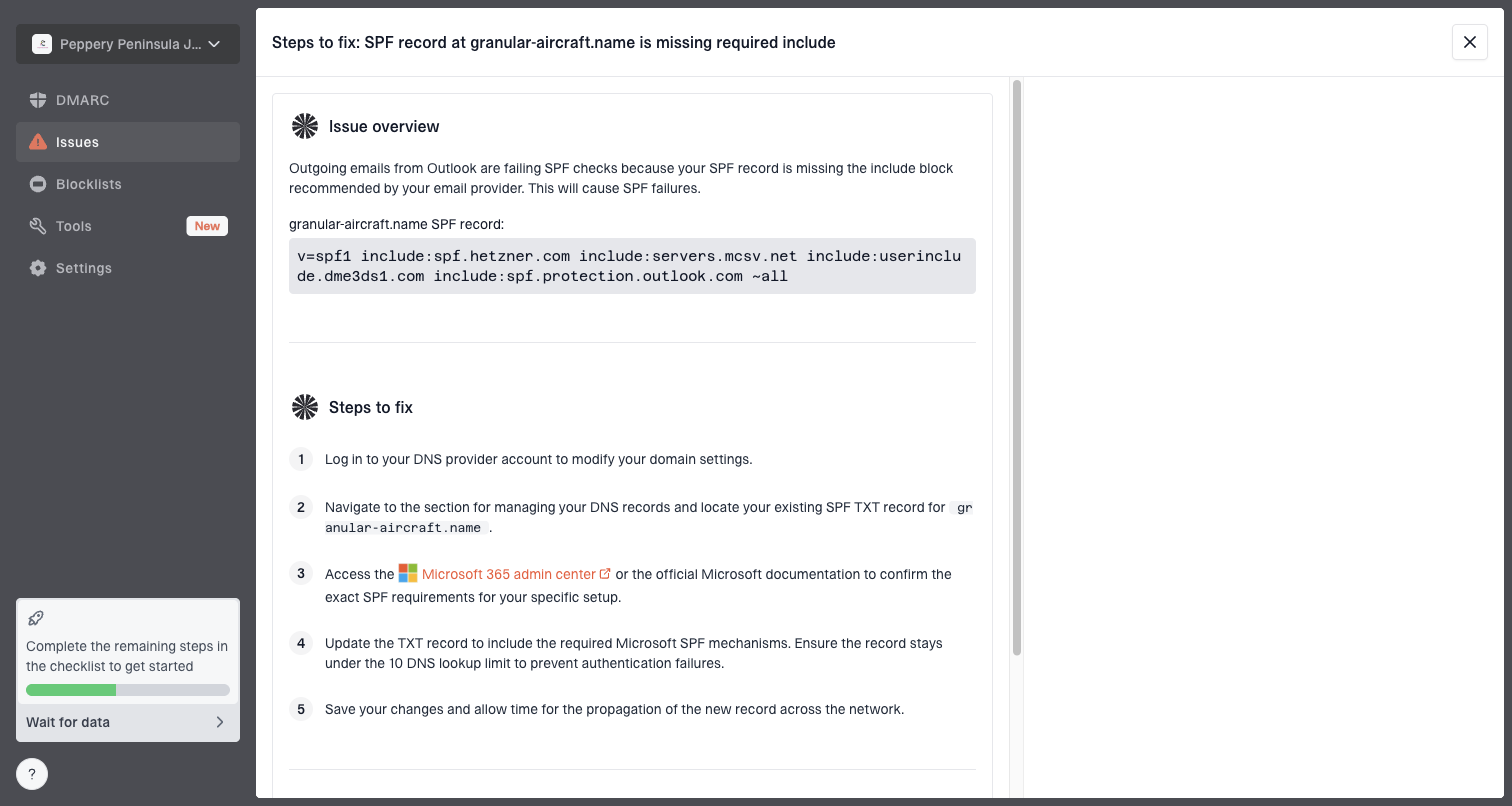
Issue steps to fix dialog showing the issue overview, tailored fix steps, and verification action
Suped's issues workflow groups failing sources, shows the authentication pattern, and provides fix steps for each source. Suped's Hosted DMARC supports staged policy changes without repeated DNS tickets.
How local receiver behavior affects outcomes
The published policy is a domain owner's requested assessment policy, not a guarantee of final disposition. RFC 9989 recommends that receivers consider other evidence alongside DMARC. A receiver can accept, quarantine, or reject a failing message under local policy, and aggregate reports can record an override reason when the receiver departs from the published request.
That explains why two receivers can treat the same message differently. It also explains why a bounce with a DMARC-related 5xx status is stronger evidence of policy rejection than a message merely landing in spam. Preserve the exact SMTP response when troubleshooting.
Calendar workflows can involve indirect mail flows. An invitation, update, or cancellation can move through systems that preserve the original From domain while changing transport details or message structure. Some recipients accept the first invite and reject a later cancellation. Inspect the failed message, identify which aligned mechanism broke, and test that exact workflow after changing DNS or vendor settings.
How to decide whether to raise policy
Raise policy when remaining failures are confirmed spoofing or abandoned tools, and any indirect-flow failures have an explicitly accepted business impact. Pause when reports show unknown sources or important senders still awaiting an authentication fix, regardless of their volume.
Ready to enforce
- Known sources: Every important sender has an owner and a passing, aligned authentication result.
- Aligned DKIM: Core mail streams pass with DKIM aligned to the visible domain.
- Resolved unknowns: Each unidentified source has been investigated; no remaining failure is tied to important business mail.
Wait and fix
- Unknown volume: Large failing sources still appear in reports without a business owner.
- Vendor gaps: Important platforms still sign with only their own domain.
- Weak monitoring: No one will see new failures quickly after policy changes.
Keep Suped's DMARC alerts active after enforcement so teams can investigate new failing sources and policy changes.
Operational checks for DMARC enforcement
Best practices
Review report data before enforcement and assign an owner to each business sender.
Prioritize aligned DKIM for critical flows because SPF often breaks after forwarding.
Use quarantine as a visible staging step when several teams send through external SaaS tools.
Common pitfalls
Treating p=none reports as noise leaves broken senders hidden until policy changes.
Adding every vendor to SPF without alignment still leaves DMARC failures unresolved.
Assuming every receiver follows the requested policy can hide local handling differences.
Expert tips
If DMARC passes and mail is blocked, investigate reputation and content signals next.
Calendar updates and cancellations need testing because handling differs by receiver.
Unconfigured business senders need an owner; authorize the workflow or stop using the domain.