What are the recommended VMC providers for BIMI setup after Entrust's acquisition by Sectigo?
Published 26 Jun 2025
Updated 13 Oct 2026
13 min read
Summarize with
Updated on 13 Oct 2026: We updated our VMC recommendations with current DMARC requirements and clearer certificate purchasing checks.
For a new BIMI setup, shortlist DigiCert, GlobalSign, and SSL.com, the three issuers in the current BIMI Group Mark Certificate Issuer directory. DigiCert is a practical starting point, but compare all three against your target mailbox providers and validation needs. Sectigo now sells VMCs and CMCs and handles former Entrust accounts, but confirm the exact certificate chain and acceptance by target mailbox providers before purchase.
BIMI success depends on more than appearing on an issuer list. Gmail, Apple Mail, Yahoo, Fastmail, and other mailbox providers decide whether they honor a given Mark Verifying Authority. A certificate can be valid PKI and still fail to produce the inbox logo you expected.
- Initial shortlist: Evaluate DigiCert alongside GlobalSign and SSL.com for the mailbox providers you target.
- Existing Entrust users: Use Sectigo support for the migrated account, then check the issuer chain before renewal.
- Listed alternatives: Compare GlobalSign and SSL.com, then test the target inboxes before rollout.
- DMARC prerequisite: Do not buy a VMC until DMARC enforcement and alignment are clean.
Recommended VMC providers after Entrust's sale
Evaluate DigiCert for a new VMC or CMC, then compare procurement terms and trademark validation coverage with the other listed issuers. GlobalSign and SSL.com also appear in the current issuer directory and deserve a direct commercial comparison. Sectigo is relevant for migrated Entrust customers and now offers its own VMCs and CMCs, but its current issuer-directory status requires an extra acceptance check.
|
|
|
|---|---|---|
New VMC or CMC deployments | Verify mailbox acceptance and renewal cost | |
Alternative VMC quote | Confirm trademark coverage and mailbox support | |
Alternative VMC quote | Confirm validation process and mailbox support | |
Former Entrust accounts or new certificates | Confirm exact chain and receiver acceptance | |
Entrust | Historical certificates | Issuance ended; check expiry and trust |
Practical VMC provider shortlist after Entrust's public certificate business moved to Sectigo.
Entrust's published dates say VMC and S/MIME issuance from Entrust Certificate Services ended on May 12, 2025, and the public certificate migration finished on September 18, 2025. Entrust stated that existing certificates would remain valid through expiration, but receiver trust rules still apply. The Sectigo FAQ explains how Entrust customer data and certificate inventory moved to Sectigo Certificate Manager.
Account migration leaves the certificate chain unchanged
Migration of a customer account is not the same thing as changing the issuing CA inside an already issued certificate. A VMC issued under an Entrust chain stays under that chain until it is replaced or renewed.
- Account migration: Moved access, inventory, records, contacts, and management workflow.
- Certificate chain: Controls which root and intermediate CA mailbox providers evaluate.
- Renewal decision: Confirms the new issuer, validity, and supported certificate type.
What changed after Entrust's sale
The Entrust sale created two separate questions that are easy to mix together. The first is operational: where do former Entrust public certificate customers manage their accounts after the completed migration? The answer is Sectigo. The second is delivery-facing: which VMC issuer chain will Gmail, Apple Mail, and other receivers honor for BIMI logo display? That answer depends on the actual certificate chain and each mailbox provider's policy.
Sectigo acquired Entrust's public certificate business, rather than the entire Entrust company. For BIMI, the VMC or CMC must satisfy mailbox-provider requirements for Mark Certificates, and providers can accept different issuers.
Certificate validity and mailbox trust are separate. Apple's certificate changes identify Entrust Verified Mark Root Certification Authority - VMCR1 with an effective date of November 15, 2024. Certificates issued after that date under the affected root do not successfully validate on up-to-date Apple systems; certificates issued on or before it are expected to work until their natural expiration. Check issuance date and chain before relying on an older Entrust VMC for Apple Mail.
What the migration handled
- Portal access: Customer accounts moved out of Entrust ECS into Sectigo management.
- Inventory: Certificate metadata and domain records moved with the account.
- Support path: Sectigo is now the contact for migration, renewal, and replacement questions.
What still needs checking
- Issuer chain: The certificate path is what receivers evaluate for trust.
- Mailbox support: An MVA listing does not force every receiver to show the logo.
- BIMI record: The DNS record still needs the correct logo or certificate URL.
The safest procurement question is: "Which issuing CA and certificate type will we receive, and which mailbox providers have accepted that chain for BIMI display?"
Check the current issuer directory
The current Mark Certificate Issuer directory lists DigiCert, GlobalSign, and SSL.com. It publishes issuer evidence such as Certification Practice Statements, Certificate Transparency logs, revocation information, roots, and audit reports where available. It does not currently list Sectigo. Inclusion is informational, not BIMI Group accreditation or a guarantee of acceptance by every mailbox provider.
Sectigo sells VMCs and CMCs, including through Sectigo Certificate Manager. Its migration FAQ confirms that former Entrust customers can obtain new VMCs and explains how existing inventory credits are handled. Request the exact chain and receiver acceptance evidence from any issuer before purchase; Sectigo's absence from the directory warrants an explicit check.
Evidence to request before purchase
- Certificate details: Get the exact VMC or CMC product name, root, and intermediate chain.
- Issuer evidence: Review the CPS, CT logging, CRL or revocation data, and current audit.
- Mailbox acceptance: Ask which target providers have vetted the chain, then confirm with test mail.
- Renewal behavior: Confirm whether a renewal changes the issuer or requires fresh validation.
Compare DigiCert, GlobalSign, SSL.com, and Sectigo
DigiCert is a practical starting point for new VMC work. It appears in the current BIMI Group issuer directory and publishes VMC and CMC validation workflows. Compare those certificate types against logo eligibility and the mailbox providers the audience uses.
GlobalSign and SSL.com are active alternatives in the issuer directory. Compare validation coverage, procurement terms, certificate format, and support for the organization's trademark jurisdiction. For a brand where Gmail and Apple logo display is the business case, run a pilot message and verify inbox rendering before production rollout.
Sectigo is the operational choice for former Entrust customers and a new direct VMC or CMC option. Because Sectigo is absent from the current BIMI Group issuer directory, obtain written confirmation of the exact chain and its acceptance by the mailbox providers that matter. Do not infer acceptance only because the certificate is available for sale.
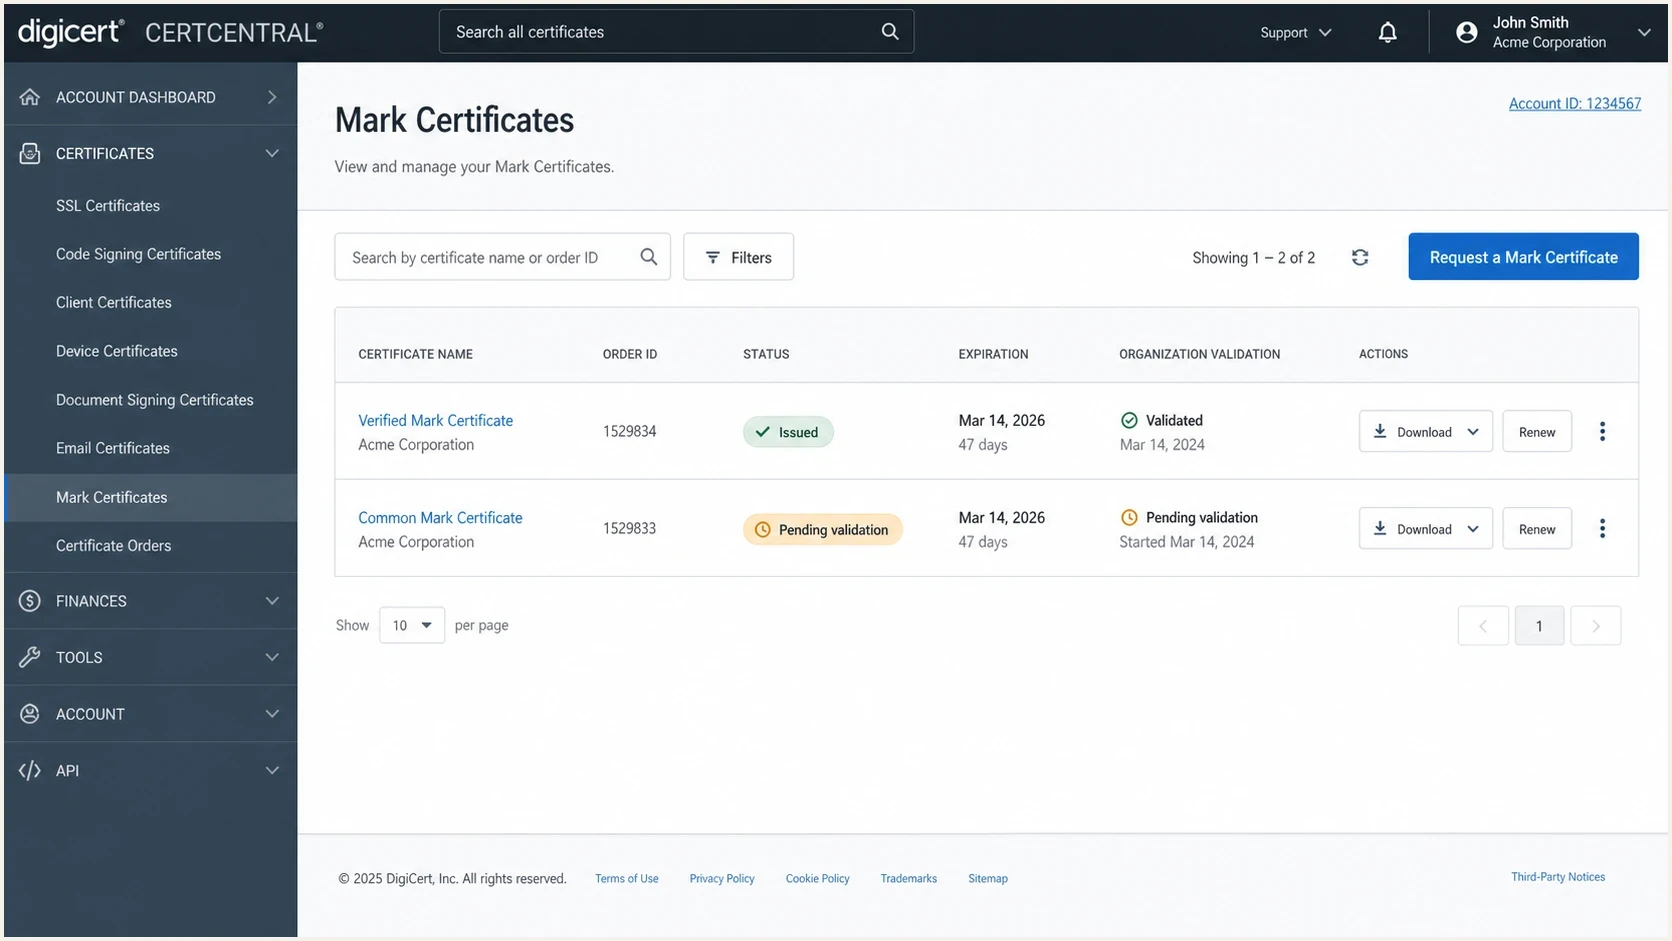
Illustrative DigiCert CertCentral screen with VMC and CMC orders, validation status, and expiration dates.
Compare providers on the same checks
- DigiCert: Evaluate VMC and CMC products against mailbox requirements and renewal cost.
- GlobalSign and SSL.com: Compare listed alternatives on validation coverage and commercial terms.
- Sectigo: Use for former Entrust support or direct issuance after verifying acceptance.
- Entrust ECS: New VMC issuance ended; choose an active issuer for the next certificate.
Compare certificate eligibility and total cost
A Verified Mark Certificate (VMC) normally requires a registered logo trademark at an intellectual property office accepted by the issuer; approved government marks are another eligibility path. A pending trademark application is not a registered mark. A Common Mark Certificate (CMC) supports qualifying unregistered logos. DigiCert's CMC requirements specify at least 12 months of use on a domain you control for its prior-use route. Confirm the chosen issuer's validation route before ordering.
Google's BIMI requirements accept a VMC or CMC for Gmail logo display, but only a VMC enables the verified checkmark. Check CMC acceptance separately for other mailbox providers. BIMI certificate guidance also identifies Yahoo and Fastmail as supporting self-asserted logos without a purchased Mark Certificate, subject to their display rules.
- Request the annual renewal price, any hosting charges, and revalidation fees. Compare total recurring cost rather than a starting price alone.
- Confirm accepted trademark jurisdictions, required documents, and the validation schedule for your application. Allow extra time if trademark registration is still pending.
- Inventory active header From domains using the same logo and ask about multi-domain certificate coverage through Subject Alternative Names (SANs). Confirm per-domain charges, logo limits, and domain control validation requirements.
- Ask about nonprofit pricing where applicable, cancellation terms, and support response times. Former Entrust customers should also confirm inventory credits and any fresh validation needed.
DMARC enforcement requirements for BIMI
A VMC will not rescue a weak authentication setup. BIMI requires a suitable logo asset, a correct BIMI DNS record, and DMARC enforcement. The header From domain and organizational domain, if different, need DMARC at p=quarantine or p=reject, applied to all mail, with an aligned SPF or DKIM pass for each message that needs the logo. Check subdomain policies as well; sp=none weakens the enforcement needed for BIMI.
Suped is our DMARC and email authentication platform for preparing sending domains for BIMI. Suped's DMARC monitoring turns aggregate reports into source-level remediation, shows SPF and DKIM alignment problems, and tracks authentication health before certificate procurement.
BIMI readiness by DMARC policy
BIMI requires a suitable enforced DMARC policy; eligibility does not guarantee logo display.
Not ready
p=none
Reporting only, useful for discovery but not enough for BIMI.
Eligible enforcement
p=quarantine
Eligible when enforcement covers all mail and sending subdomains.
Reject policy
p=reject
Requests rejection of messages that fail DMARC; receivers decide final handling.
Example enforced DMARC record with subdomain coveragedns
_dmarc 3600 IN TXT (
  "v=DMARC1; p=reject; sp=reject; "
  "rua=mailto:dmarc@example.com"
)
Current DMARC rules and legacy BIMI guidance
RFC 9989 marks pct as historic. BIMI still needs enforcement for all mail. Google's published instructions continue to specify pct=100; retain it when following that guidance as a legacy compatibility setting, rather than treating it as a current DMARC control. Avoid testing mode with t=y for a production BIMI deployment.
Strict DMARC alignment for SPF and DKIM is optional for BIMI. The example omits adkim=s and aspf=s so the default relaxed alignment applies. Choose strict modes only after reports confirm that legitimate senders support them.
Before buying the certificate, run the domain through the domain health checker and fix authentication gaps. If the domain uses many sending services, Suped's hosted SPF and SPF flattening can keep DNS lookup limits under control while DMARC enforcement moves forward.
?
What's your domain score?
Deep-scan SPF, DKIM & DMARC records for email deliverability and security issues.
BIMI record setup
Publish the BIMI record for the domain visible in the header From address, rather than choosing the Return-Path domain by default. Once the certificate is issued, the BIMI TXT record uses l= for the logo location when required and a= for the Mark Certificate PEM. When the certified logo is embedded in the PEM, a common certificate-backed record leaves l= empty. The PEM should contain the entity certificate followed by any supplied intermediate and root certificates in issuing order. Host the file at a publicly reachable HTTPS URL, and make sure the embedded SVG matches the validated logo and SVG Tiny Portable/Secure (SVG Tiny PS) requirements.
Example certificate-backed BIMI DNS recorddns
default._bimi 3600 IN TXT (
  "v=BIMI1; l=; "
  "a=https://example.com/bimi/vmc.pem"
)
If DMARC is still being staged, use Hosted DMARC to manage policy changes without repeated DNS edits. Validate the authentication record with the DMARC checker before moving the domain to enforcement.
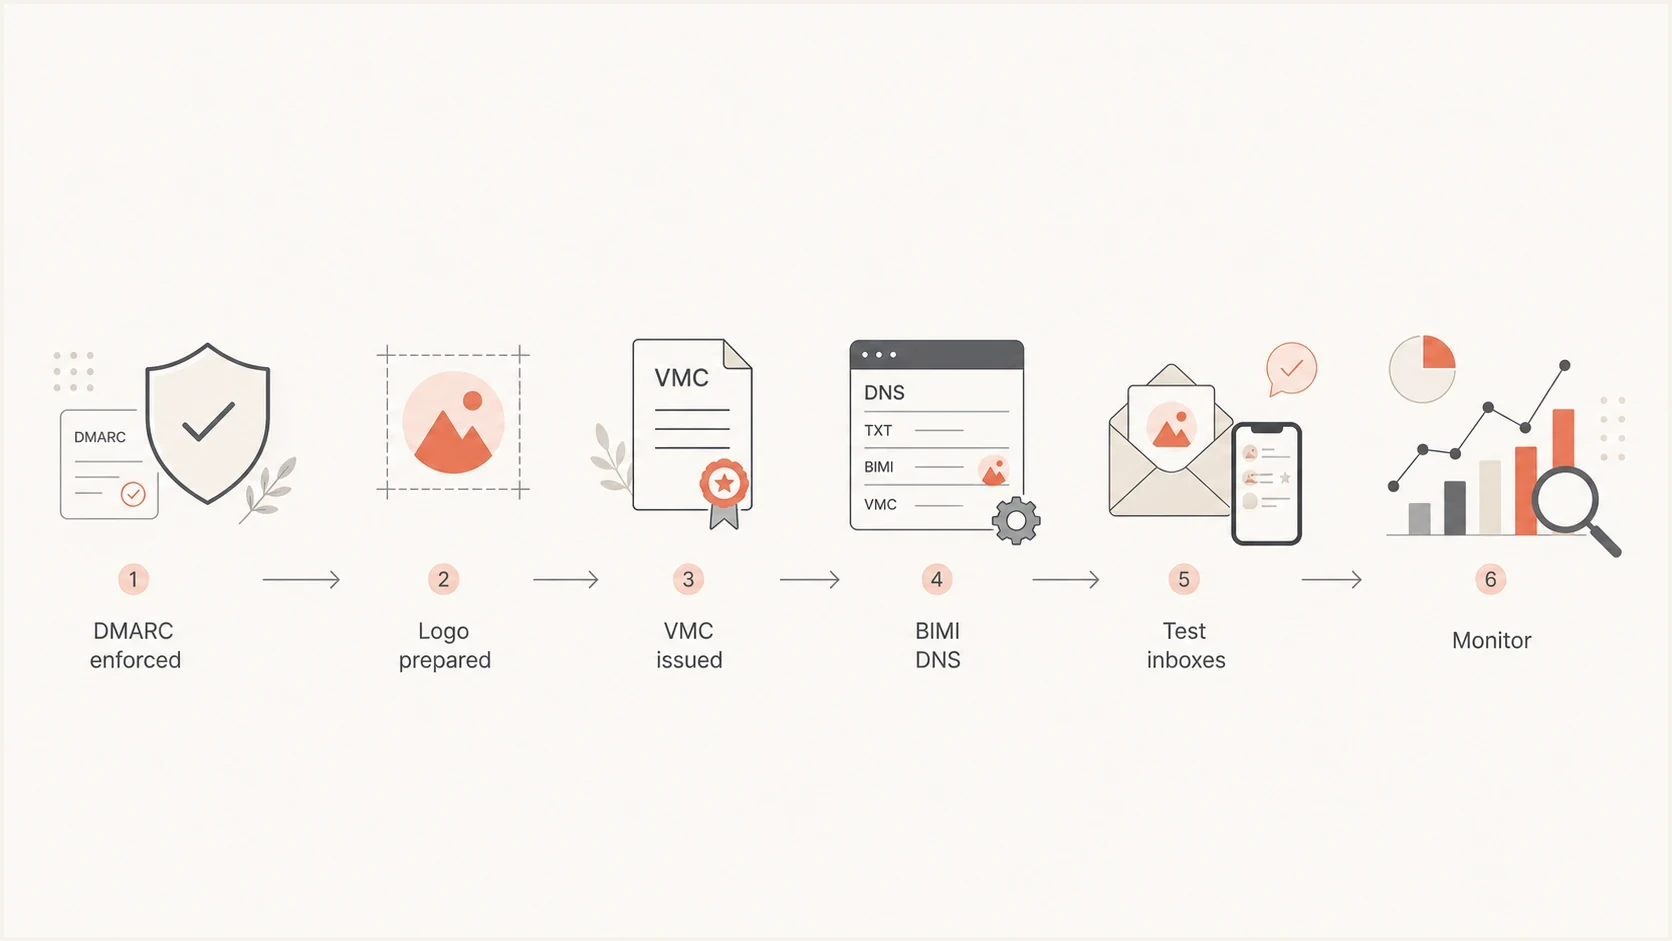
BIMI setup flowchart showing DMARC enforcement, logo preparation, VMC issuance, DNS publication, inbox testing, and monitoring.
A common failure pattern is buying the certificate first, then finding unauthenticated mail streams, an SPF lookup problem, or an SVG that fails validation. Clean DMARC first, prepare the logo second, buy the certificate third, and test the actual inboxes last.
How to choose safely
Use a short checklist before signing off on a VMC provider. A sales statement that the certificate is valid is not enough. The certificate must work for the receiver mix that matters to the business.
- Ask for issuer details: Get the root and intermediate CA names before purchase or renewal.
- Confirm the type: Use a VMC for a qualifying registered trademark, or a CMC when the use case fits.
- Check mailbox targets: Test Gmail, Apple Mail, Yahoo, and Fastmail if they matter.
- Validate expiration: Check the actual expiry date and allow time for replacement and fresh validation.
- Budget for validation: Trademark, organization, domain control, and logo checks take longer than DNS setup.
A practical rollout order
- Authentication: Inventory senders and fix SPF or DKIM alignment failures.
- Enforcement: Apply quarantine or reject to all mail and sending subdomains after reports are clean; follow target receivers' legacy compatibility guidance.
- Validation: Prepare the SVG and complete VMC or CMC checks.
- Launch: Publish BIMI DNS and test real messages in target inboxes.
If an Entrust VMC is still in use, check its actual expiration date, revocation status, issuer chain, and issuance date. The end of new issuance did not itself revoke existing certificates, but expiration and Apple trust restrictions are separate reasons to replace one. Arrange a new certificate through an active issuer rather than assuming account migration renewed the old VMC.
For teams comparing VMCs with CMCs, decide whether the brand needs Gmail's verified checkmark, trademark-backed identity, or a supported BIMI logo without that checkmark. The certificate types are not interchangeable. The VMC and CMC comparison explains the cost and eligibility tradeoffs.
Where Suped fits
Suped is our DMARC and email authentication product for the work before and after VMC issuance. It helps teams find sending sources, fix authentication failures, stage policy enforcement, and track SPF, DKIM, blocklist (blacklist), and deliverability signals in one workflow.
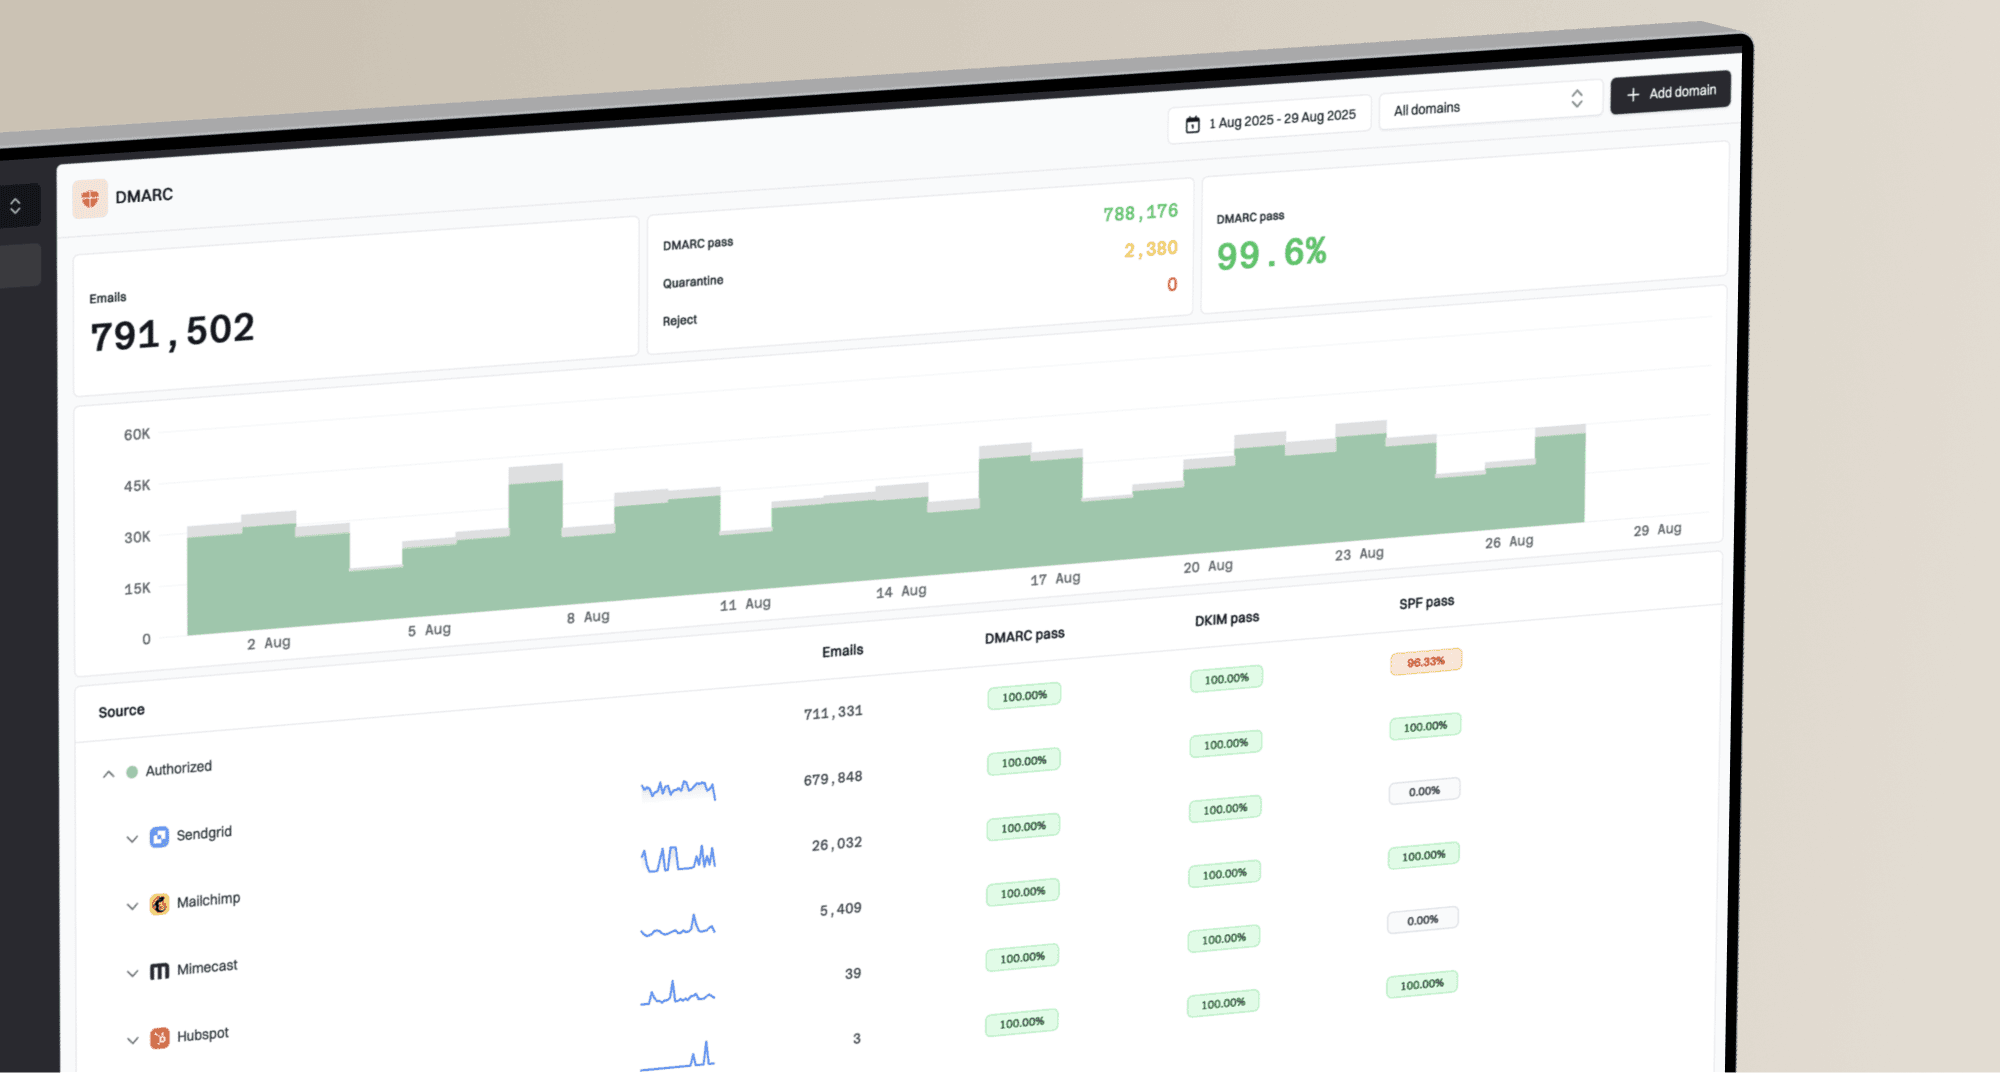
Suped DMARC dashboard showing email volume, authentication health, and source breakdown
This matters for BIMI because authentication changes can interrupt logo display. If a marketing platform stops signing with aligned DKIM and SPF does not provide an aligned pass, the affected messages fail DMARC and lose BIMI eligibility. Suped's alerts and issue detection flag those changes for remediation.
For a fuller provider checklist, use the VMC issuer guide. For the separate issue of Apple and Entrust trust behavior, read the Apple distrust explanation before renewing an older certificate.
Choose a VMC issuer for the next renewal
For new BIMI deployments, start by comparing DigiCert with the other listed issuers. GlobalSign and SSL.com are also in the current Mark Certificate Issuer directory and should be compared on validation coverage, support, and commercial terms. Use Sectigo for former Entrust account support or consider its direct VMC and CMC products only after confirming the exact chain and target mailbox acceptance.
For former Entrust customers, check the current certificate issuer, actual expiration date, and inbox behavior. Arrange replacement before expiry, allowing time for validation and publication of the replacement PEM. Update the BIMI record if the certificate URL changes. Choose the next issuer based on target mailbox acceptance and renewal terms.
Frequently asked questions
No. DigiCert is a practical starting point for new BIMI work, while GlobalSign and SSL.com also appear in the current Mark Certificate Issuer directory. Compare validation coverage, renewal terms, and acceptance by the target mailbox providers before rollout.
Yes. Sectigo now sells VMCs and CMCs. It does not currently appear in the BIMI Group Mark Certificate Issuer directory, so request the exact chain and evidence of acceptance by the mailbox providers that matter before buying.
The issuance cutoff did not itself revoke existing Entrust VMCs. Check actual expiry, revocation status, issuance date, and chain. Apple's certificate policy restricts certificates issued after November 15, 2024 under the affected Entrust VMCR1 root, so an unexpired certificate is not a guarantee of Apple Mail logo display.
No. Account and inventory migration does not rewrite an already issued certificate. The issuer chain remains part of the certificate until the certificate is replaced or renewed.
Compare total renewal cost alongside mailbox acceptance, validation time, domain coverage, and support. Confirm that a lower quote covers the same certificate type and sending domains; a CMC does not provide the Gmail verified checkmark offered by a VMC.
Yes. Prepare the domain for BIMI with p=quarantine or p=reject applied to all mail and aligned authentication. RFC 9989 makes pct historic, although Google's BIMI instructions still specify pct=100 as legacy guidance. Stabilize authentication and subdomain policy before buying the certificate and publishing the BIMI record.