
Why is Google Postmaster Tools (GPT) showing incorrect SPF and DKIM authentication rates?

Updated on 20 Oct 2026: We clarified reporting delays, domain matching, and the checks that distinguish a dashboard discrepancy from a real authentication failure.
Google Postmaster Tools can show apparently incorrect SPF and DKIM authentication rates when the selected domain view differs from the message being tested or when different sending streams have different results. Its dashboards cover personal Gmail accounts, not Google Workspace recipients, and reporting is delayed. A sudden one-day drop to 0% SPF or 0% DKIM does not prove your DNS broke. Treat it as a signal to verify before making changes.
If fresh Gmail headers show SPF pass, DKIM pass, and DMARC pass, compare their authenticated domains with the selected Postmaster Tools view and check the same sending streams in DMARC aggregate reports. One passing test does not validate every message in the chart. If failures are not confirmed, allow time for reporting to update before changing DNS.
Fast triage
- Do not change DNS first: Changing SPF or DKIM records before checking headers can turn a reporting discrepancy into a real outage.
- Check reported dates: A completed calendar day can still be awaiting processing. Check the latest available date before comparing authentication rates.
- Use independent evidence: Compare headers, DMARC aggregate reports, and controlled test sends before making changes.
Why the rates disagree
Postmaster Tools does not inspect your DNS record in isolation and declare your SPF or DKIM setup good or bad. It reports what Gmail saw for messages associated with the selected domain and dashboard view. That Gmail-specific view can differ from a DNS lookup, a sending platform's dashboard, or a test message because each examines a different part of the authentication path.
Recent-day data can be incomplete. Google's dashboard documentation says updates typically arrive within 24 hours but can take longer. Low-volume privacy filtering can leave gaps. A displayed 0% is a reported rate; a gap or N/A means data is unavailable. Compare a zero with headers and historical data rather than assuming it is a reporting delay.
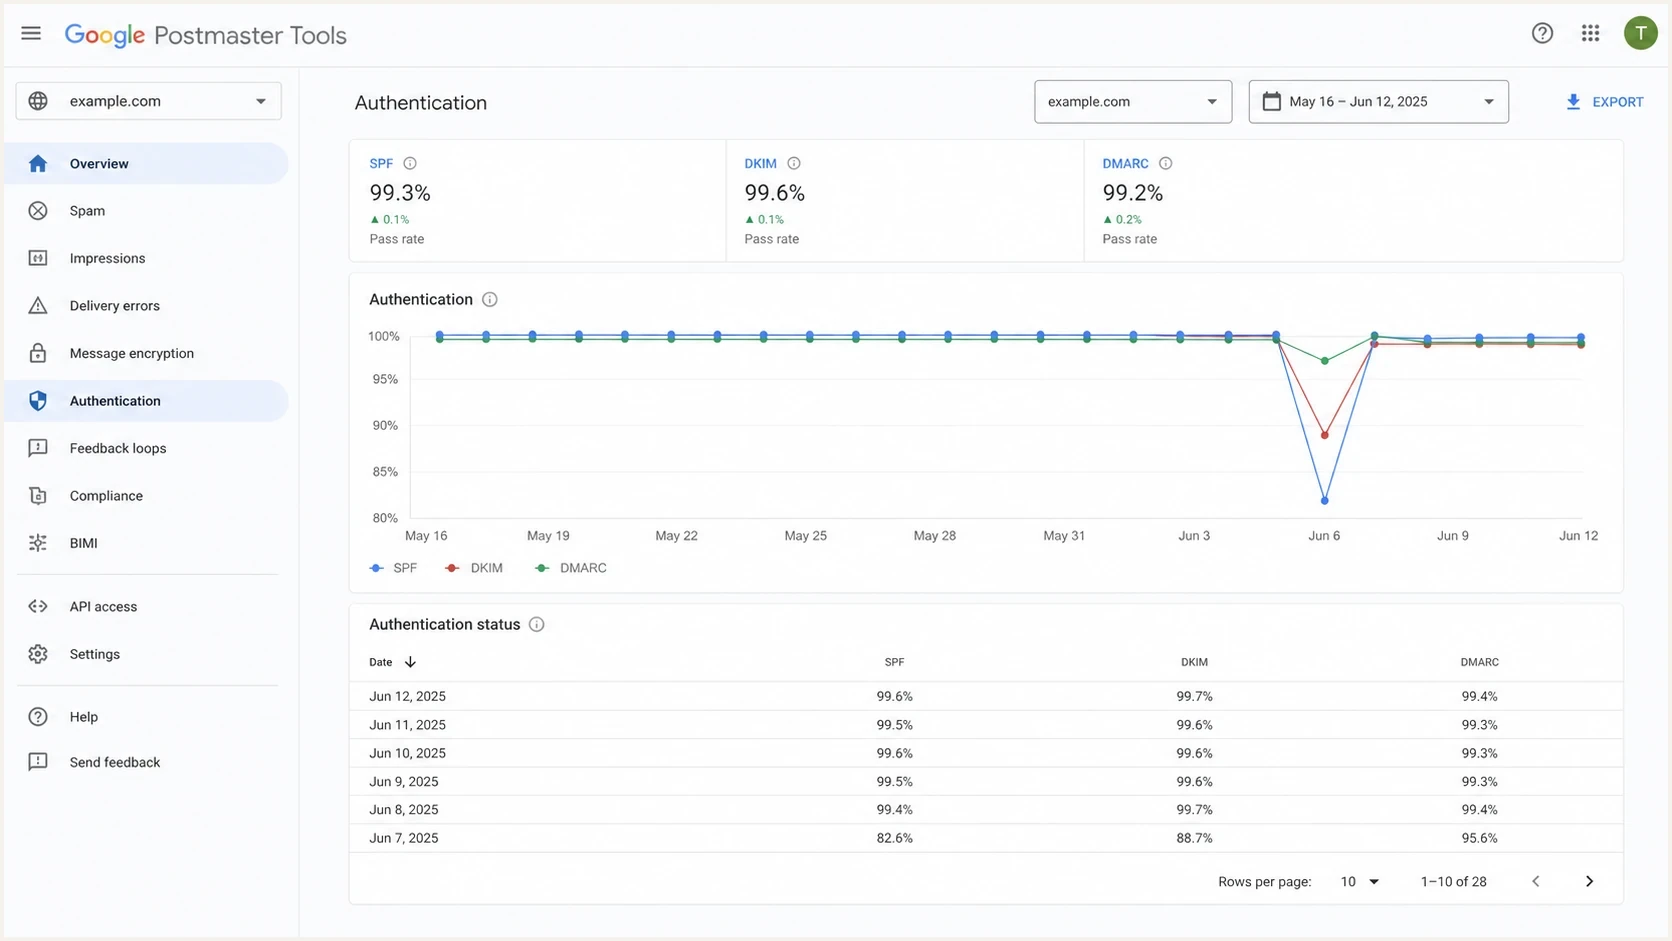
Google Postmaster Tools Authentication dashboard showing a sudden SPF and DKIM rate drop.
What Postmaster Tools shows
- Gmail view: It reflects mail sent to personal Gmail accounts, not delivery to every provider.
- Delayed aggregation: Recent data can change because the dashboards are not real time.
- Selected scope: The From-header view and the DKIM/SPF-domain view count different sets of messages.
What verifies authentication
- Message headers: A delivered Gmail message shows authentication results for that exact message.
- DMARC reports: Aggregate reports show outcomes by source and authenticated identifier.
- Controlled tests: A fresh production-path test shows whether the current sender signs and authorizes mail.
Check the selected authentication view
The Authentication dashboard has two views. View by From header domain covers messages where the selected domain appears in the visible From header and focuses on authentication connected to that domain. View by DKIM and SPF domains instead covers messages where the selected domain matches the DKIM signing domain or SPF domain.
|
|
|
|---|---|---|
From header domain | Mail using the selected visible From domain | Compare results with the same From domain |
DKIM and SPF domains | Mail matching the selected DKIM or SPF domain | DMARC success rate is not shown |
Confirm the selected view before comparing a chart with headers or aggregate reports.
A rate can look wrong when a message header is checked against one domain while the dashboard groups another. Confirm the visible From domain, smtp.mailfrom domain, and DKIM header.d domain, then select the matching view. Google's dashboard documentation describes both views and notes that forwarded messages are excluded where possible, although some can remain in dashboard data.
Common causes of wrong-looking SPF and DKIM rates
Separate reporting effects from real authentication failures before editing DNS. Domain scope and mixed sending streams can explain a sharp chart drop, while reporting delays and low-volume privacy filtering can leave data incomplete.
|
|
|
|---|---|---|
Data lag | The newest reporting day is missing or still changing | Check the latest reported date and compare headers |
Wrong view selected | Header and chart use different domains | Compare From, smtp.mailfrom, and header.d |
SPF domain mismatch | SPF passes for an unrelated bounce domain | Compare From and Return-Path |
Third-party DKIM | DKIM passes for another domain | Check the DKIM d value |
Mixed streams | Some sends fail while others pass | Segment results by source |
Low Gmail volume | Days or metrics are missing | Compare Gmail-bound daily volume |
Forwarding | SPF fails or authenticates the forwarding domain | Check whether DKIM survives |
Use the table to sort the likely cause before editing SPF or DKIM.
SPF authenticates the envelope sender, commonly the bounce or Return-Path domain. For DMARC, its authenticated domain must share the visible From domain's organizational domain under relaxed matching, or match it exactly under strict matching. For example, bounces.example.com and example.com match in relaxed mode, but bounce.example.net and example.com do not.
DKIM uses the signing domain in the d= value, with the same relaxed or strict matching rules for DMARC. A provider's signature can pass without satisfying DMARC for your From domain. DMARC passes when at least one passing SPF result or DKIM signature meets the matching rule. This means SPF can fail while DKIM still provides a DMARC pass.
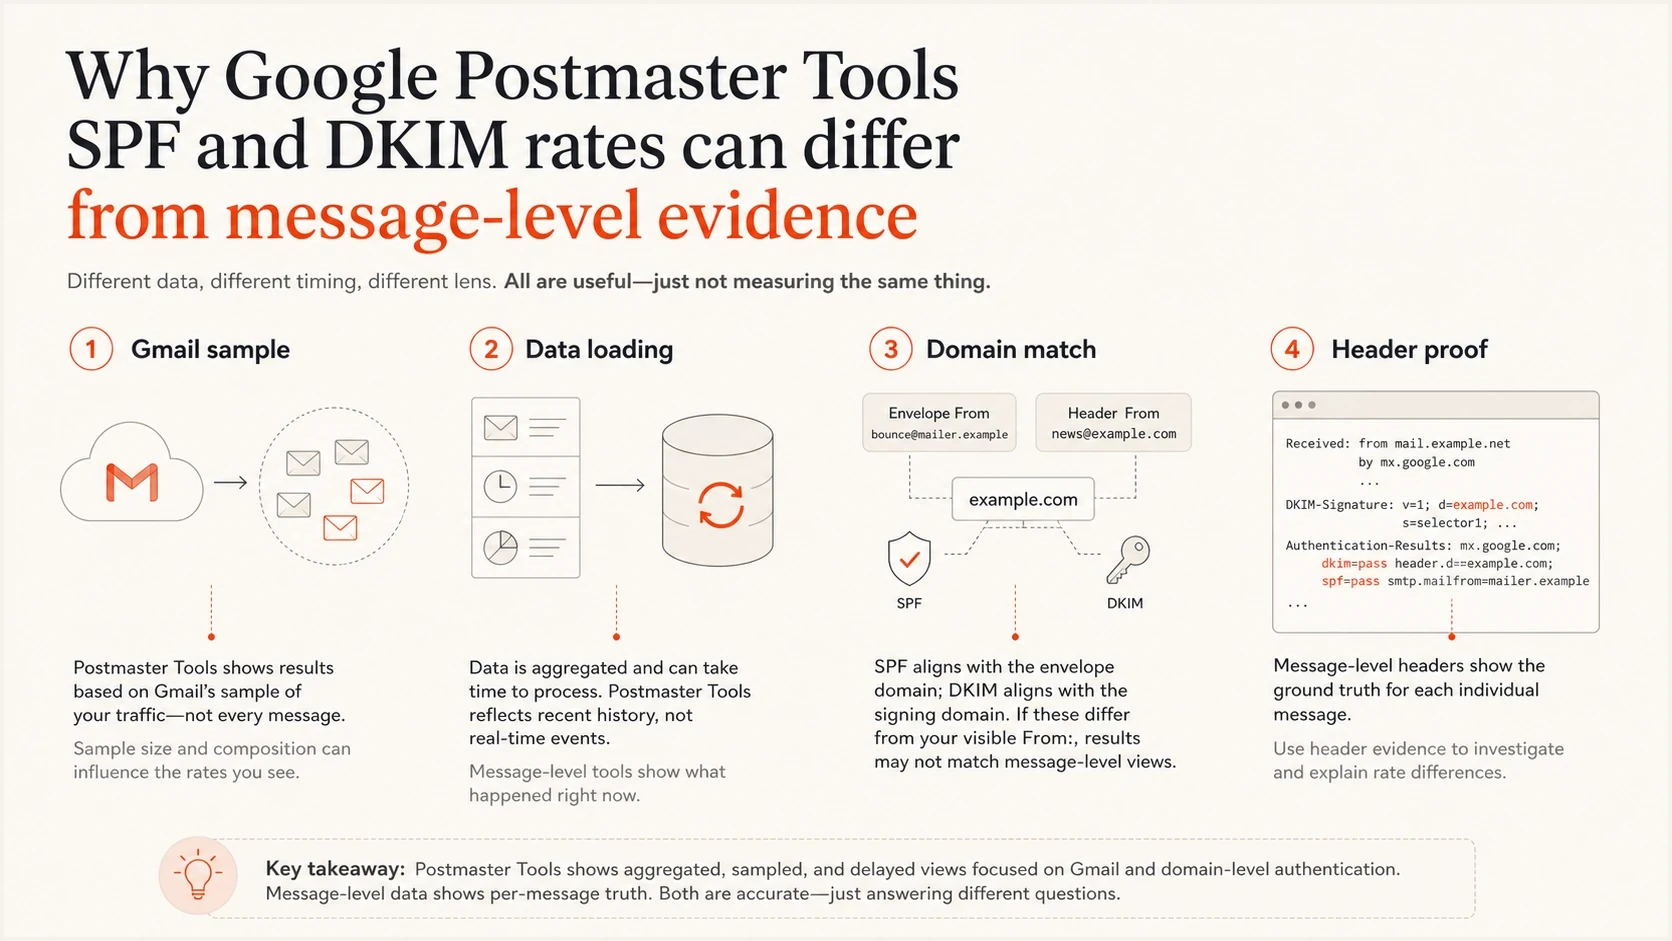
Gmail traffic, reporting delays, domain matching, and headers explain authentication rate differences.
Compare reporting windows and sending streams
Postmaster Tools uses Coordinated Universal Time (UTC), as Google's dashboard documentation explains. Match the chart date to the DMARC report's reporting period, not its arrival date or your campaign's local date.
- Start with aggregate reports issued by Google rather than an all-provider average. Their traffic coverage still differs from Postmaster Tools' personal Gmail data.
- Match the visible From domain and authenticated domains, then split the results by sending source or IP address. Include transactional mail as well as marketing sends.
- Weight results by message count. A high-volume failing stream can dominate a domain's rate even when a small test stream passes.
- Compare messages sent during the affected period. A successful test after a configuration fix cannot disprove failures before that fix.
Use the reports to locate a failure pattern rather than expecting identical percentages. Privacy filtering and Google's attempts to exclude forwarded mail limit direct comparisons. Missing reports are incomplete evidence, not proof that every message passed.
How to verify before changing DNS
Start with a real message delivered to Gmail. Open More, then Show original, and read the Authentication-Results header added by mx.google.com. It shows how Gmail evaluated that exact message. If the header passes while the chart drops, check the dashboard view and compare the affected streams in DMARC aggregate data before touching DNS.
Good Gmail header patterntext
Authentication-Results: mx.google.com;
  spf=pass smtp.mailfrom=bounces.example.com;
  dkim=pass header.d=example.com header.s=s1;
  dmarc=pass (p=none) header.from=example.com
Check smtp.mailfrom for SPF, header.d for DKIM, and header.from for DMARC. Also confirm the DKIM selector in header.s. The example's SPF domains match in relaxed mode, while its DKIM domain matches exactly. For a deeper walkthrough, the message headers walkthrough explains the message-level evidence needed for comparison.
- Confirm SPF syntax: Check the SPF record at the envelope-sender domain. Look for multiple v=spf1 records at that name, missing sending IPs, or more than 10 DNS-lookup-causing terms across the evaluated SPF chain.
- Confirm DKIM DNS: Check the DKIM selector used by the message and confirm that outgoing mail carries its signature. Publishing a key or a Postmaster Tools verification TXT record does not enable DKIM signing.
- Review DMARC reports: Find the same source, domain, and failure type for the affected reporting period.
- Send a controlled test: Send through the exact production path and inspect the output with an email tester.
Email tester
Send a real email to this address. Suped shows a results button when the test is ready.
?/43tests passed
A controlled test checks the actual path. Teams sometimes validate SPF against one domain while the mail stream uses another return-path domain, an unexpected DKIM selector, or a relay that rewrites signed content. The test message also provides a timestamp for comparison with the Postmaster Tools chart.
DMARC record that collects aggregate reportsdns
v=DMARC1; p=none; rua=mailto:dmarc-reports@example.com
Publish this monitoring record at _dmarc.example.com only if the domain has no DMARC record. Replace the example reporting address with a mailbox that accepts aggregate reports. If a DMARC record already exists, update its reporting destination without adding a second record or weakening an existing quarantine or reject policy.
When the chart points to a real issue
A single chart point needs investigation, while a confirmed production-stream authentication failure warrants action immediately. Do not wait for aggregate reports or later chart points to confirm a failure already visible in fresh Gmail headers. Repeated drops and matching DMARC reports help establish its scope. The fix depends on whether SPF, DKIM, or domain matching failed.
How much confidence to place in the signal
Use the evidence level to decide whether to investigate further or fix the sending path.
Low confidence
Verify
One recent point is abnormal, sampled headers pass, and the affected streams still need checking.
Medium confidence
Segment
The same sender shows mixed pass and fail results in DMARC reports.
High confidence
Fix
Fresh Gmail headers confirm a production-stream failure, even if aggregate reporting still lags.
Resolved
Monitor
New test sends pass and later aggregate reports confirm recovery.
Do not ignore these patterns
- Repeated header failure: Fresh Gmail messages show SPF fail or DKIM fail for the affected stream.
- Third-party DKIM mismatch: A provider's signing domain passes DKIM but does not match the visible From domain.
- Unconfigured sending stream: A website, application, or service sends mail without the expected SPF authorization or DKIM signature.
- Lookup limit failure: SPF returns permerror because the record exceeds the DNS lookup limit.
If SPF fails, inspect the sending IP authorization and return-path domain. If DKIM fails, inspect selector DNS, key length, signing domain, and post-signing message changes. If both pass but DMARC fails, inspect domain matching. Google's setup guide is useful when access, verification, or domain setup in Postmaster Tools is the problem.
Possible reporting discrepancy
The newest chart point drops, but sampled Gmail headers pass or the selected dashboard view differs from the tested domain. Check other active streams before calling it a false alarm.
- Best move: Confirm the view, check affected streams, and preserve the evidence while reporting catches up.
- Risk: Unneeded DNS edits create avoidable authentication problems.
Real issue pattern
Fresh Gmail headers confirm an authentication failure in a production stream. A matching pattern in DMARC reports or completed-day charts strengthens the diagnosis.
- Best move: Fix the sending path, then verify it with a new test send.
- Risk: Waiting prolongs authentication failures for legitimate mail.
Use Suped to investigate sending sources
Postmaster Tools provides Gmail-specific dashboard signals. Suped's product provides DMARC monitoring that groups aggregate authentication results by sending source and routes alerts when failures cross a chosen threshold.
For this workflow, Suped turns aggregate reports into source-level findings and remediation steps. A team can check whether the sender behind a Postmaster Tools drop also failed DMARC, identify the affected sending source, and track the result after a fix.
Issues page showing top issues, verified sources, unverified sources, and authentication pass rates
- Source evidence: See which sending services pass or fail authentication instead of reacting to one chart.
- Automated detection: Surface SPF, DKIM, DMARC, and DNS issues with remediation steps.
- Alerts: Notify the team when authentication failures exceed a chosen threshold.
- Multi-domain work: Compare domains and sending sources in one dashboard.
Triage a Postmaster Tools authentication drop
When a Postmaster Tools authentication rate drops, save the evidence and inspect the affected sending path before changing DNS. If authentication passes but delivery is poor, check spam complaints and Gmail delivery errors separately; a 100% authentication rate does not guarantee inbox placement.
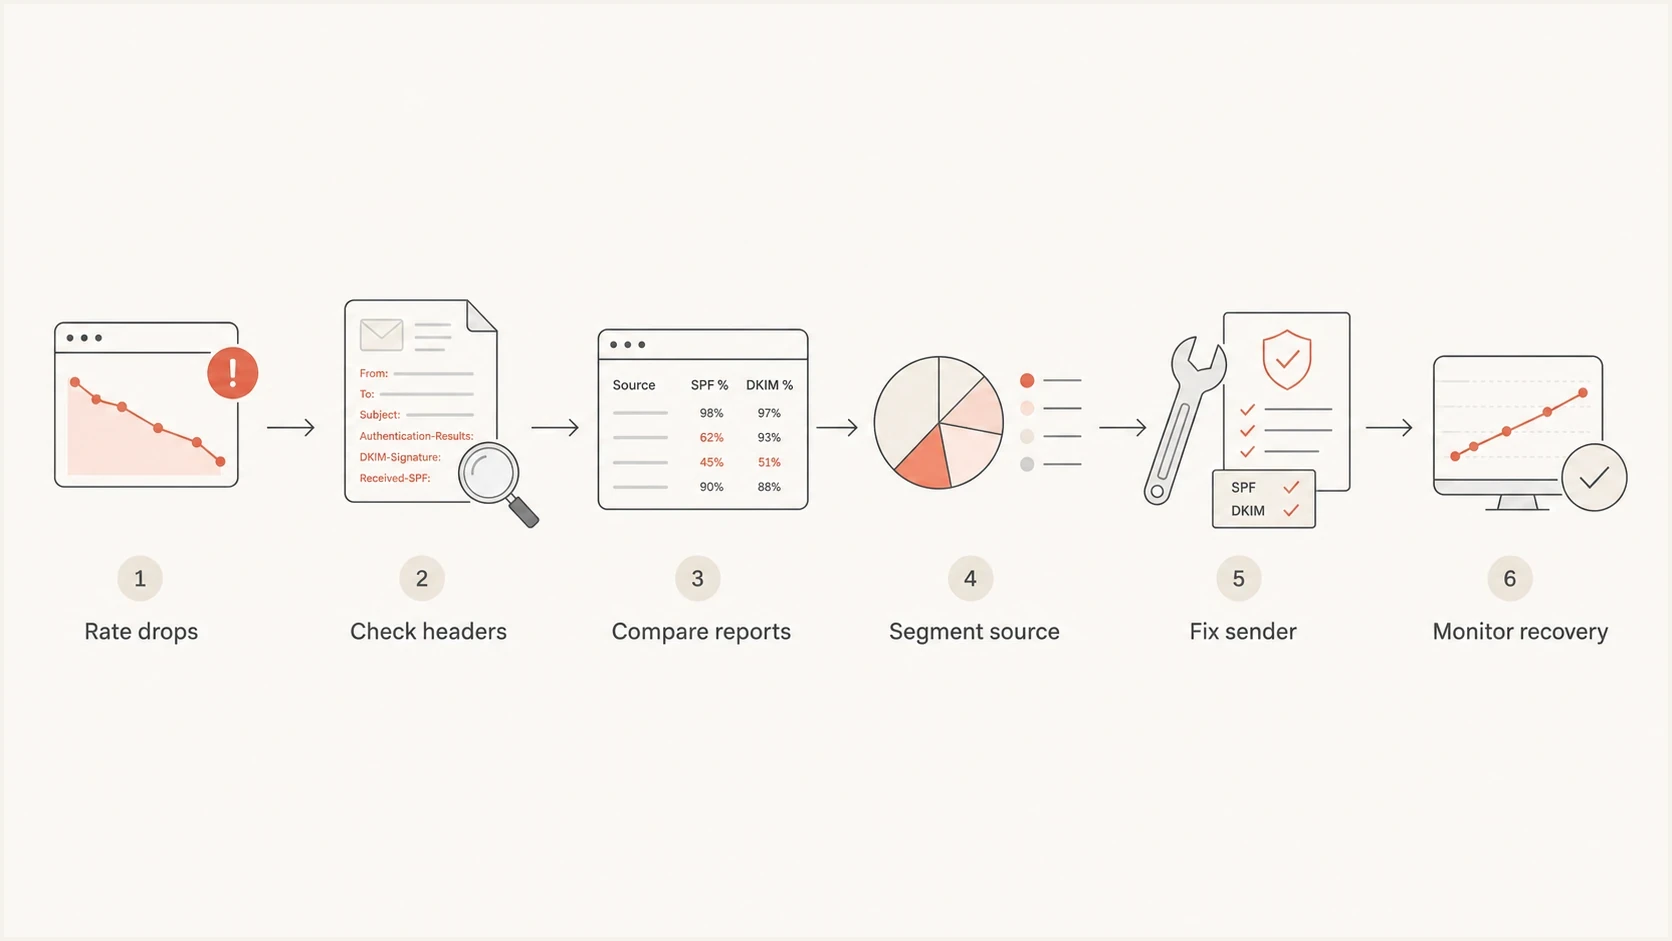
Steps to verify a Google Postmaster Tools SPF or DKIM rate drop before changing DNS.
If Postmaster Tools has no data at all, the problem differs from a wrong-looking authentication rate. The domain might not be verified, the selected domain might not send mail, traffic might be too low for Google's privacy thresholds, or Gmail might not have populated data yet. The no data scenario needs a separate check.
Default order of operations
- Save the chart: Record the domain, selected view, UTC date, and metric before the data changes.
- Inspect Gmail headers: Use a delivered message from the same stream and reporting period.
- Compare DMARC data: Check whether aggregate reports show the same source failing.
- Change one thing: If a failure is confirmed, fix its cause and retest that stream. Check later reporting to confirm recovery.
Views from the trenches
Best practices
Check Gmail headers before editing DNS, then compare the same stream in aggregate reports.
Treat newest-day Postmaster Tools data as provisional until related dashboards populate.
Keep custom return-path and custom DKIM active so domain matching can be verified fast.
Common pitfalls
Changing SPF after one bad chart point can create a real failure where none existed.
Assuming SPF pass means DMARC pass ignores the visible From domain matching requirement.
Comparing all-domain reports with one Gmail chart hides source-specific authentication breaks.
Expert tips
Segment by sender, domain, and date before deciding whether the issue is data lag or DNS.
Use completed-day evidence when briefing stakeholders so transient chart points do not distract.
Watch for low Gmail volume, since privacy filtering can leave gaps in dashboard data.
Marketer view
Marketer from Email Geeks says a sudden 0% SPF reading across known-good sending platforms should be verified against headers before any DNS change.
2024-02-27 - Email Geeks
Marketer view
Marketer from Email Geeks says a chart that loads yesterday's authentication data before other dashboards finish can create a false alarm.
2024-02-27 - Email Geeks




