What are the purposes of bots signing up for emails and accounts on websites?
Published 7 Aug 2025
Updated 23 Oct 2026
14 min read
Summarize with
Updated on 23 Oct 2026: We added guidance on abusive confirmation emails and clarified what signup verification and DMARC can prove.
Signup bots automate email subscriptions and account registrations because the signup itself has value. Sometimes the goal is to bury a real security alert inside thousands of subscription messages. Sometimes it is comment spam automation that treats every form field as a target. Sometimes it is account farming, promotion abuse, list poisoning, harassment, account enumeration, or reconnaissance against weak plugins and badly handled form inputs.
The same logic applies to newsletter, account, sales, quote, and lead forms. If a form accepts an email address, triggers an email, creates a record, or passes data into a CRM, it gives bots and fake-data operators something to exploit.
The address can be one the attacker controls, a victim address, a purchased address, or a disposable mailbox. If the attacker controls the inbox, they can confirm accounts and collect delivery signals. If they use a victim's address, the goal is usually disruption, concealment, or abuse of your signup infrastructure.
- Spam automation: Generic spam bots submit forms at scale because forms are easy to find and cheap to test.
- Fraud concealment: List bombing can hide password reset, login, purchase, transfer, or loyalty-point theft alerts.
- Security probing: A signup form can tell an attacker which sites run weak plugins, unsafe templates, or poor validation.
- Response: Treat fake signups as an abuse signal as well as a list hygiene problem.
Why bots submit signup forms
Bot signups happen for several reasons, and more than one can apply in the same incident. Random-looking newsletter abuse can be a fraud-covering mail bomb, a deliverability test, a list-poisoning attempt, or a probe for unsafe form handling.
Some fake submissions are not classic bot signups. They are fake leads, outsourced form fills, typo domains, disposable mailboxes, or real users who want access to a quote, result, trial, or download without future follow-up.
|
|
|
|
|---|---|---|---|
Mail bomb | Victim | Many brands | Fraud hidden |
Spam testing | Attacker | Fast confirms | Abuse |
Form probing | Any | Odd names | Security |
List poisoning | Bad data | Low engagement | Reputation |
Account farming | Controlled | Reusable accounts | Platform abuse |
Common bot signup motives and the signals they leave
An unwanted-signup complaint does not establish the attacker's motive. Check for a wider flood of unrelated confirmation emails before classifying the incident as list bombing.
Why attackers use real addresses
A form can trigger a confirmation email for any submitted address. Attackers use deliverable addresses because the messages reach a real inbox, either one they control or one they want to disrupt. A working mailbox does not establish permission to send marketing.
The address does not have to belong to the attacker. In list bombing, it often belongs to the person being targeted. The attacker submits that victim address to hundreds or thousands of forms, filling the inbox with welcome emails, opt-in requests, coupons, and newsletter confirmations. A real transaction alert or account-change notice is easier to miss inside that flood.
Address the attacker controls
- Confirmation: They can click verification links and create usable accounts.
- Testing: They can see what emails your site sends and how fast they arrive.
- Automation: They can reuse accounts for scraping, spam, trials, or promo abuse.
Address the attacker does not control
- Noise: They can flood a victim's mailbox with unrelated signup messages.
- Harassment: They can make the victim spend time unsubscribing and reporting abuse.
- Damage: They can make your sender reputation absorb complaints caused by their attack.
That distinction matters. Confirmed opt-in reduces downstream list pollution, but the first confirmation email can still contribute to a victim's mailbox flood.
Account pre-hijacking risk
Some signup abuse prepares an account before the real user arrives. In an account pre-hijacking pattern, an attacker creates or primes an account with a victim's email address, then tries to keep access after the victim verifies, resets, or connects that account later.
- Unverified account state: The site gives an unverified account sensitive capabilities or preserves attacker-set access when the real owner claims it.
- SSO merge behavior: Password login and single sign-on are not merged or reset cleanly.
- Recovery settings: Old recovery paths, secondary addresses, or pending changes remain active.
- Session cleanup: Existing sessions survive after email verification, password reset, or account claim.
Keep unverified accounts inactive until mailbox verification is complete. During an account claim, revoke pre-verification sessions and remove attacker-set recovery methods. Do not automatically merge password and single sign-on accounts solely because their email addresses match.
The main purposes behind bot signups
Separate the motives into practical groups because the same controls are not equally effective against every type of abuse.
- Hiding fraud: The attacker floods the victim with signup emails so a bank, card, loyalty, or account-security alert gets buried.
- Harassment: The attacker uses forms as a cheap way to make a victim's inbox unusable for hours or days.
- Comment spam: The bot sees a form, fills every field, and hopes the site publishes a link, profile, or comment.
- Account farming: The attacker creates accounts for content spam, fake reviews, free trials, inventory holds, referral rewards, discount codes, or scraping.
- Reconnaissance: The bot checks whether your form leaks plugin details, reflects unsafe input, or sends predictable emails.
- Account enumeration: The bot compares registration responses to learn which email addresses already have accounts.
- Deliverability testing: The attacker watches whether your email reaches an inbox, spam folder, or security gateway.
- List poisoning: The bot injects low-quality addresses that later bounce, complain, or distort campaign metrics.
- Lead-quality abuse: A dishonest affiliate or paid lead supplier can use bots or click farms to claim pay-per-lead commissions or meet a signup quota. The resulting contacts waste sales time and add invalid or non-consenting addresses to email programs.
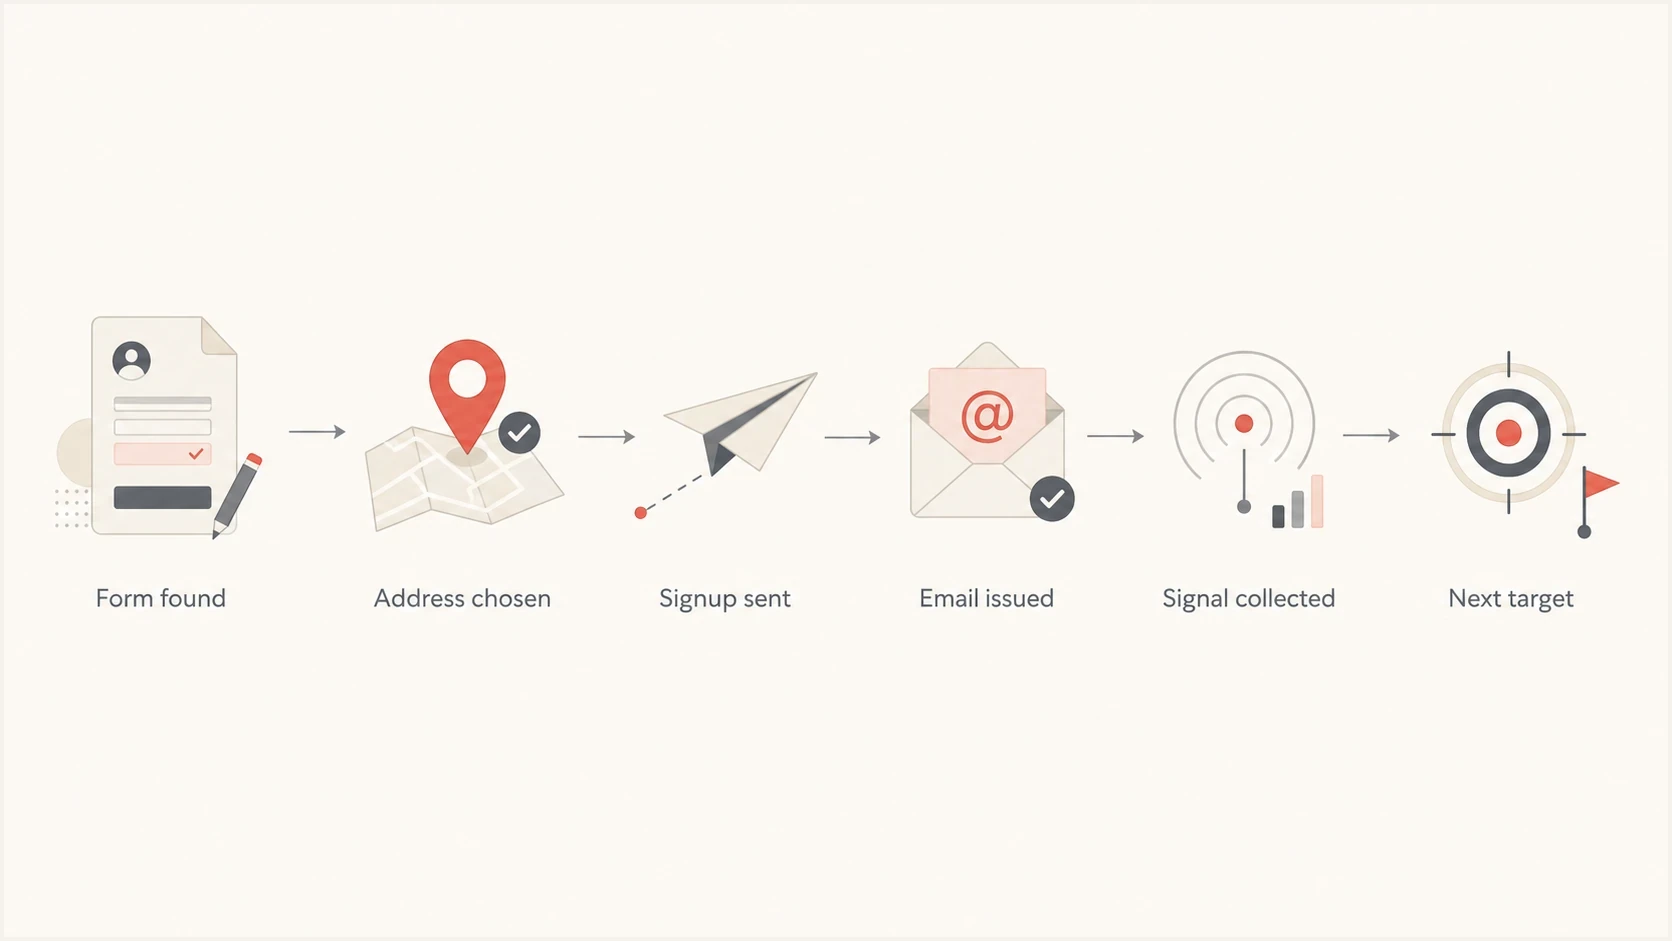
Bot signup process showing form discovery, address submission, email delivery, and response collection.
Cost inflation and resource exhaustion
Some campaigns intentionally consume the resources behind a signup form. Each submission can write database rows, trigger email or SMS, call verification services and webhooks, start onboarding automations, or notify sales staff. At scale, normal application behavior becomes an operating-cost and capacity problem.
- Outbound costs: Email, SMS, verification, and webhook calls consume paid capacity.
- Queue pressure: Automated jobs can delay legitimate confirmations and account events.
- Promotion loss: Fake accounts claim trial access, signup credits, referral rewards, or discount codes.
- Metric distortion: Fake records skew conversion rates, experiments, forecasting, and fraud models.
Set per-action budgets and limits, not only a global request limit. Cap submissions by recipient, IP, network, device, and session. Hold expensive downstream actions until risk checks pass, then alert on unexpected changes in spend or queue depth.
How subscription bombing hides fraud alerts
List bombing, also called subscription bombing or registration bombing, uses many website forms to flood a target inbox with signup messages. Your confirmation or welcome email becomes one message in that flood.
The hidden message is often a security alert: a password reset, account login, payout change, purchase receipt, transfer confirmation, or loyalty-point redemption. The victim sees a wall of ordinary email and misses the one message that matters. A reported email-bomb incident describes a recipient flooded with confirmation messages from unrelated websites.
Illustrative list-bombing inbox
Hypothetical percentages, not measured attack data. The example shows how signup messages can bury a security alert; real inboxes have different proportions.
Signup mail
Confirmation mail
Security alert
Other mail
A useful clue is breadth. A recipient reporting messages from many unrelated brands suggests a mailbox-targeted flood. Many addresses submitted to your own form suggest broader signup abuse, but volume alone does not establish the motive.
A victim receiving a signup flood should search for bank, payment, password, login, purchase, gift card, and loyalty terms before deleting the noise. Website owners should make unwanted signups easy to report.
How bots probe signup forms
Not every bot cares about the inbox. Some bots use signup pages to learn about the website. A form tells an attacker whether the site accepts automation, which framework it uses, whether it sends email, whether it reflects input, and whether old plugins are present. Registration responses can also disclose whether an email address already has an account.
One strong signal is payload content. A harmless-looking name field can carry a script tag, SQL-like text, a long string, or a URL. If the page or email template reflects that value without proper escaping, the attacker learns that the application has weak output handling. Validate fields, use parameterized database queries, and encode output for its destination; blocking a few suspicious strings does not replace these controls.
Response differences are another signal. A bot can compare messages, status codes, redirects, and response time to enumerate registered addresses. Return the same public response with similar timing whether an address exists, then send account-specific instructions only through the mailbox.
Suspicious signup payload examplestext
first_name=<script>alert(1)</script>
first_name=' OR '1'='1
website=https://spam.example/path
comment=Nice post cheap pills
email=victim@example.com
Plugin-specific fields and exploit-shaped payloads warrant investigation. An unusual name or URL alone is not proof of an attack; compare the payload with request patterns and application behavior.
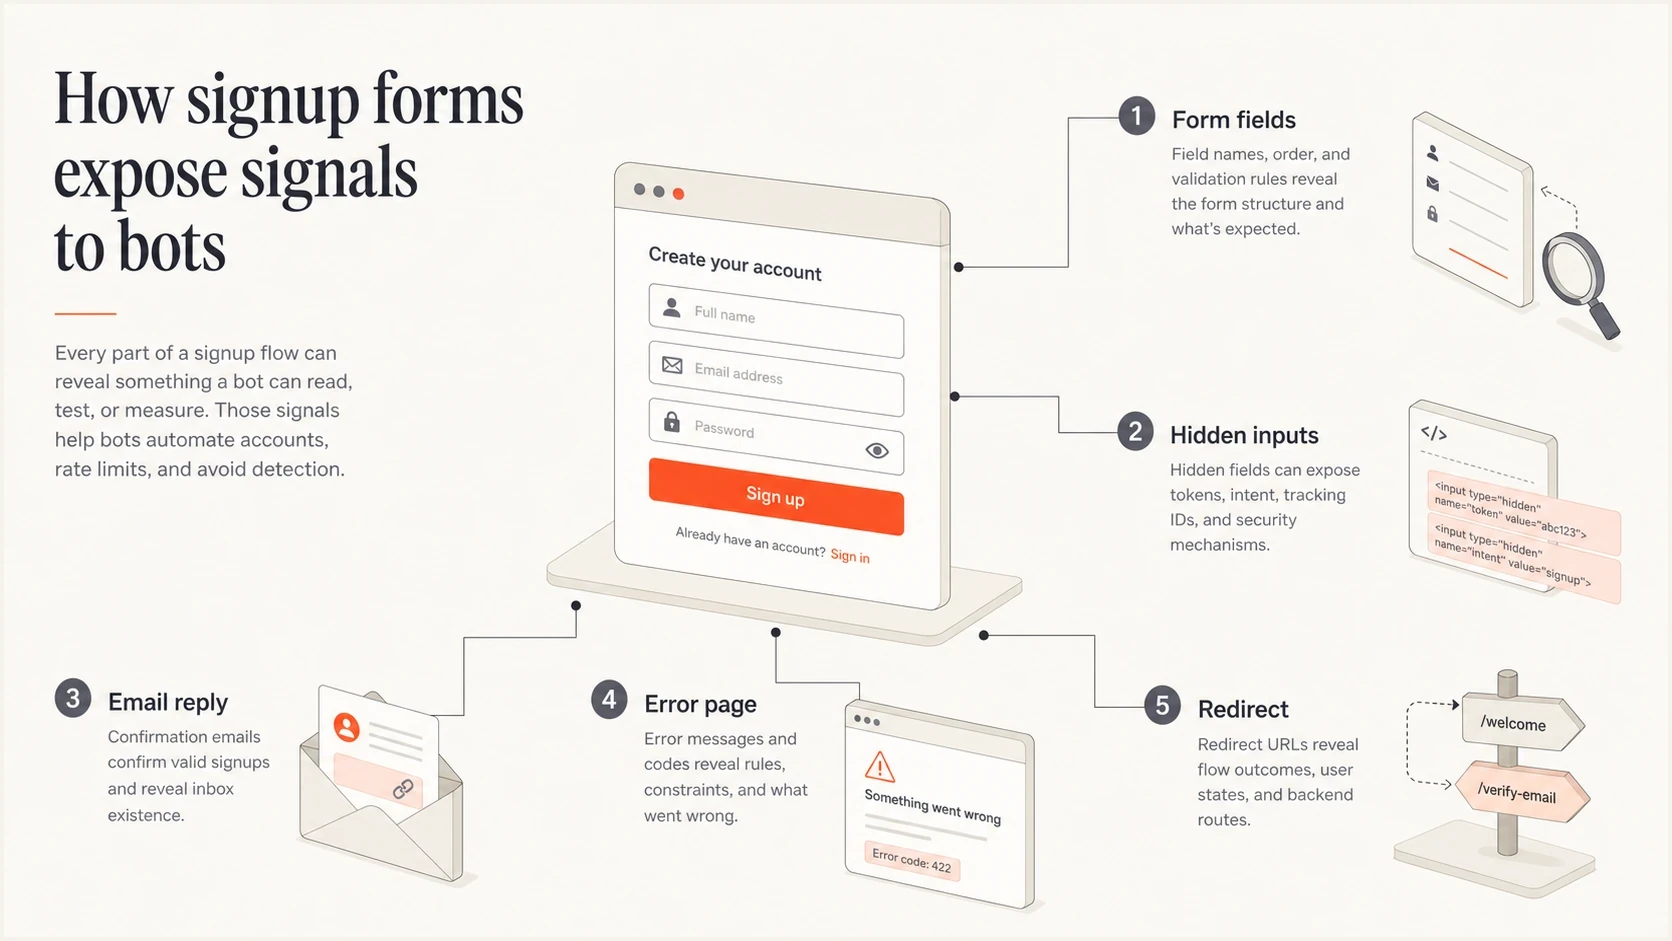
Website signup form fields and responses used by bots for account enumeration and security probing.
Abusing trusted signup emails
Another motive is to make your website send the attacker's content. If a confirmation template copies a name, company, or message field into an email, a bot can put an unwanted advertisement or deceptive URL in that field. This applies the content-spoofing mechanism described by OWASP to email templates: submitted text appears inside a message sent by a trusted brand.
The resulting email can pass SPF, DKIM, and DMARC because your own system sends it. Authentication does not validate the submitted content or prove that the recipient requested the message.
- Keep confirmation emails focused on verification; omit unnecessary free-text fields.
- Apply field length and format rules, and reject URLs in fields that have no reason to contain them.
- Encode inserted values for the email's HTML or text context. Encoding alone does not prevent deceptive plain-text content.
- Review both HTML and plain-text templates, including welcome emails and confirmation resends.
How bot signups affect email deliverability
For email teams, bot signups create two problems. They pollute audience data, and they can turn your domain into a tool inside someone else's abuse campaign.
When bots add addresses that never wanted mail, bounce, complaint, unsubscribe, and engagement signals suffer. A list-bombing victim can also report your confirmation email as spam, even if you never added them to a marketing list.
Email tester
Send a real email to this address. Suped shows a results button when the test is ready.
?/43tests passed
After tightening signup controls, send a real test email and inspect the authentication and content signals with Suped's email tester. A clean test checks that message only; it does not demonstrate bot prevention or guarantee inbox placement.
Bot-generated messages sent by your own form can pass SPF, DKIM, and DMARC. Suped's DMARC monitoring shows sending sources and authentication results in receiver reports; it does not identify individual signup requests or prove consent. Suped's blocklist (blacklist) monitoring tracks domain and IP listings, which are one reputation signal rather than a complete reputation assessment.
Issues page showing top issues, verified sources, unverified sources, and authentication pass rates
How to tell what type of bot problem you have
The fastest way to classify the incident is to compare signup volume, address variety, timing, confirmation behavior, and payload content. Start with evidence.
- Count bursts: Look for sudden spikes by minute, IP, ASN, country, form path, and user agent. Compare campaign, referrer, and affiliate IDs to identify traffic sources that bring unusually poor-quality signups.
- Group recipients: Separate many signups to one victim address from many signups across many addresses.
- Inspect fields: Search names, comments, URLs, and hidden fields for scripts, SQL-like strings, or plugin-specific values.
- Compare responses: Check whether messages, status codes, redirects, or timing reveal if an account exists.
- Check consent: Compare unconfirmed, confirmed, bounced, complained, unsubscribed, disposable, and typo-domain addresses.
- Trace downstream cost: Measure email, SMS, webhook, verification, queue, and sales-automation activity caused by each signup.
- Review sending: Confirm that only approved systems are sending signup, confirmation, and welcome messages.
- Watch reputation: Monitor blocklist and blacklist status when complaints or volume spike suddenly.
?
What's your domain score?
Deep-scan SPF, DKIM & DMARC records for email deliverability and security issues.
A broad domain health check is useful after a bot-signup incident because it checks the public email foundation around the domain. If your website form was abused, you still need to know whether DMARC, SPF, DKIM, and DNS signals are healthy before the next campaign goes out.
Matching submissions across scattered IPs suggest distributed automation, but shared networks and normal-looking addresses are not decisive evidence. Compare the traffic source, request sequence, consent records, and downstream behavior before classifying the incident.
How to reduce signup abuse
The right controls slow bots without punishing legitimate subscribers. Good defenses combine friction, validation, rate limits, consent handling, and monitoring.
|
|
|
|---|---|---|
Rate limits | Bursts | Shared IPs |
Honeypot field | Simple bots | Autofill errors |
CAPTCHA | Simple automated submissions | Accessibility |
Confirmed opt-in (double opt-in) | List pollution | Initial email still sends |
Field validation | Bad payloads | Maintenance |
Address checks | Malformed addresses and typos | False positives |
Suppression | Repeat abuse | False matches |
Monitoring | Blind spots | Needs response |
Practical controls for bot signups
For newsletter forms, confirmed opt-in (double opt-in) keeps unverified addresses out of marketing sends. It does not fully stop mail bombing, because the confirmation email itself can be part of the flood. Apply recipient-based cooldowns before the first send and to resend requests. Confirmation proves access to the verification link, not that the visitor is human; bots can operate mailboxes and follow links.
Use CAPTCHA or another step-up challenge when risk rises, with an accessible alternative. Enforce challenges and rate limits on the server at every signup endpoint, including direct API requests, before sending mail. Follow OWASP's input validation guidance for field rules and separate output protections. A passed challenge or valid address does not prove consent.
Illustrative signup abuse scoring pseudocodetext
# Illustrative only. Tune thresholds and time windows to observed traffic.
score = 0
score += recent_submissions_by_ip > 5 ? 25 : 0
score += recent_submissions_by_email > 2 ? 40 : 0
score += hidden_field_filled ? 50 : 0
score += payload_contains_script ? 80 : 0
score += disposable_domain ? 20 : 0
if score >= 60: hold email and review
For account creation, use progressive friction. Let low-risk users proceed normally. Step up verification when the submission looks automated, repeats too often, uses suspicious payloads, or comes from poor-history infrastructure.
For accounts with sensitive capabilities, require 2FA or step-up verification before profile changes, purchases, referral actions, or payout changes. Keep CMS, plugins, templates, and form libraries current so old signup endpoints do not become the easiest path in.
A good signup defense does not depend on one gate. It limits repeated submissions, validates field content, delays suspicious email sends, stores consent state clearly, and keeps traceable logs.
How Suped supports incident checks
Suped is our DMARC reporting and email authentication platform. Use it to investigate sending sources and authentication results while your web team handles rate limits, input validation, confirmed opt-in, and account rules.
In practice, Suped's DMARC monitoring helps identify unfamiliar sources and authentication problems in receiver reports. A message passes DMARC when SPF or DKIM passes and the corresponding authenticated domain matches the visible From domain under DMARC's domain-matching rules. Passing DMARC does not establish signup consent.
Form-layer controls
- Purpose: Limit abusive submissions and keep unconfirmed addresses out of marketing sends.
- Examples: Rate limits, honeypots, validation, risk scoring, confirmed opt-in.
- Owner: Usually web, product, security, or growth engineering.
Suped monitoring
- Purpose: Show reported authentication results and tracked blocklist listings.
- Examples: DMARC monitoring, SPF visibility, DKIM visibility, blocklist monitoring.
- Owner: Usually email, deliverability, security, or MSP teams.
If complaint rates rise after a signup attack, check DMARC monitoring and blocklist monitoring together. Use authentication results to investigate unfamiliar sources and configuration failures. Compare blocklist status with complaint and bounce rates; delivery problems can occur without a monitored blacklist listing.
How to respond to bot signups
If you run the website, stop the current abuse, preserve evidence, protect recipients, and prevent your mail from becoming part of another flood. Handle it in this order.
- Pause risky sends: Temporarily hold confirmation or welcome emails for submissions that match the abusive pattern.
- Preserve logs: Keep timestamps, request identifiers, form paths, email event IDs, and redacted payload samples with restricted access. Exclude passwords and verification tokens.
- Suppress victims: Hold unwanted signup and marketing emails to reporting recipients. Keep legitimate account-security alerts available.
- Block patterns: Apply rate limits, IP reputation checks, field validation, and bot challenges where the abuse enters.
- Clean data: Quarantine affected signups before campaigns, automations, or lead scoring use them, then review evidence before deleting records.
- Review auth: Check DMARC, SPF, and DKIM so legitimate mail remains identifiable during cleanup.
If you are the mailbox owner receiving the flood, search for important account activity first. Review recent transactions and account changes by opening official sites directly instead of clicking links in unexpected email. Use temporary rules that move suspected signup mail to a review folder instead of deleting it, and keep checking for security alerts. If you find unauthorized activity, contact the affected provider, reset the affected account's password, revoke unfamiliar sessions, and enable multi-factor authentication.
For a deeper prevention workflow, the practical next step is preventing list bombing, because that is where form controls, consent handling, and incident response come together.