Why is my BIMI logo not showing up in Gmail despite having a VMC certificate?
Updated on 25 Oct 2026: We clarified Gmail's BIMI requirements and added reputation checks for logos that still do not appear.
Your BIMI logo can stay hidden in Gmail despite a valid VMC because Gmail checks the complete BIMI path. Common causes include DMARC that is not enforced with p=quarantine or p=reject, a wrong PEM URL, an expired certificate, a malformed or incomplete PEM chain, an invalid SVG embedded in the certificate, a stale subdomain override, unreachable or redirected assets, a DKIM signature that uses the body-length tag, or sender reputation that does not meet Gmail's display criteria.
A VMC verifies a registered mark for an organization and domain. It does not force Gmail to display the logo. Google's BIMI setup guide says Gmail supports VMCs and CMCs through PEM files. Gmail can show a checkmark next to VMC-verified senders, while CMC-backed senders do not get that VMC checkmark.
The fastest first check is the live a= URL. Retrieve the PEM for the BIMI record Gmail should use, verify the complete certificate chain, and inspect the SVG embedded in that PEM. If you also publish an external logo with l=, validate that file separately.
The fastest diagnosis
Start with the message Gmail actually received, not the domain you expected to use. BIMI lookup depends on the visible From domain and selected BIMI selector. If news.example.com has no applicable BIMI record, it can use the same selector at the organizational domain. With no accepted selector header, that selector is default. A BIMI record published on the child domain overrides that fallback.
- Confirm the From domain: In Gmail, open the message menu and select "Show original". Check the visible From address and Gmail's Authentication-Results for dmarc=pass; SPF or DKIM passing for an unrelated domain is insufficient.
- Resolve the selector and fallback: Check the selected record on the From domain, then the same selector at the organizational domain when no child record exists.
- Fetch the certificate file: Confirm the a= URL returns the current PEM and full certificate chain.
- Inspect the embedded SVG: The logo inside the PEM must use Gmail-compatible SVG Tiny PS formatting.
- Check hosting behavior: Use public HTTPS URLs, TLS 1.2 or later, the expected domain, and direct responses without redirect chains.
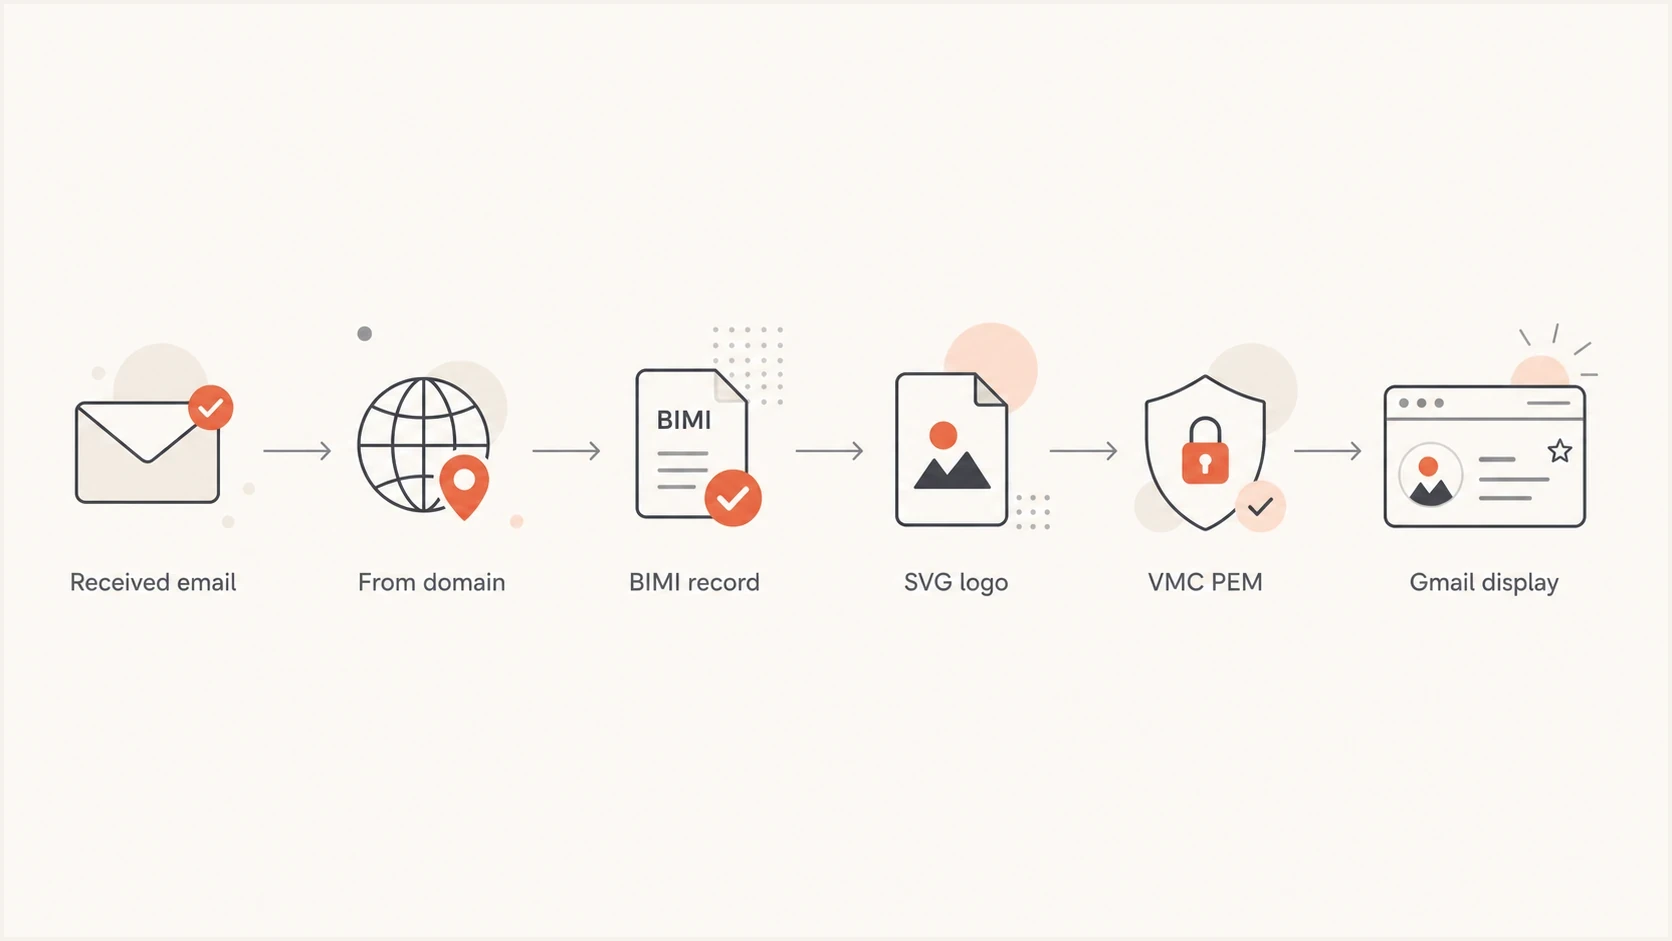
Flowchart for troubleshooting a BIMI logo not showing in Gmail with VMC, DNS, SVG, and display checks.
Separate internal Google Workspace images from BIMI. If the logo appears for employees but not personal Gmail recipients, the internal view can come from directory data, contact images, or an account profile photo rather than the BIMI record. Test with a fresh external Gmail message before treating the internal logo as proof that BIMI works.
If the VMC was recently renewed, treat the renewed certificate as a new asset. Verify its status, embedded SVG, certificate chain, public URL, and live DNS reference even when the file name and brand mark appear unchanged.
Gmail BIMI authentication and logo requirements
Gmail checks BIMI after authentication and policy checks. The message needs to pass DMARC for the visible From domain through SPF or DKIM identity matching. Use p=quarantine or p=reject at the organizational domain and in any separate sending-domain policy, and avoid sp=none. A DMARC pass under a monitoring policy does not meet BIMI enforcement requirements.
RFC 9989 retires pct and uses t= for policy testing. Google's BIMI setup guide still lists pct=100, so the example below retains it for compatibility with that guidance and older checks. Leave t= absent or set t=n for enforcement; t=y signals testing.
|
|
|
|---|---|---|
DMARC | Use p=quarantine or p=reject | Move out of monitoring mode |
Coverage | Google's published BIMI guidance still lists pct=100 | Retain for legacy compatibility; keep policy testing disabled |
Subdomains | Check sp= or child policies | Enforce organizational and sending-domain policies; avoid sp=none |
Authentication | A DMARC pass requires SPF or DKIM identity matching | Fix failing senders; Gmail bulk senders must configure both SPF and DKIM |
BIMI | Check the live a= PEM URL | Publish the current full PEM |
Hosting | Public HTTPS with no redirects | Use stable public URLs that return the actual files |
Reputation | Stable authenticated sending | Review spam complaints and sending history |
Compact checklist for Gmail BIMI readiness
Gmail's current setup guide says Gmail supports BIMI through a PEM file, not a standalone SVG. For a VMC deployment, the PEM contains the certificate and embedded SVG. Google's example permits l= to be empty when a= points to that PEM, so an external SVG URL is not required for this Gmail path.
The embedded SVG still has to satisfy Gmail's image rules. Use SVG Tiny PS with baseProfile="tiny-ps" and version="1.2". Gmail requires absolute pixel dimensions of at least 96 by 96 pixels and prohibits relative sizing. Google recommends a centered square logo, a solid background, a file size of 32 KB or smaller, and a <desc> element for accessibility. Do not include scripts, animation, external references, or root-level x= and y= attributes.
The PEM file matters too. Upload the entity certificate with all intermediate and root certificates appended in the order supplied by the certificate authority, then make sure the a= URL returns that full file directly over HTTPS.
Use Suped's DMARC checker to confirm the published policy quickly. For production domains, DMARC monitoring is more useful than a one-time lookup because it identifies sending sources that fail DMARC and block BIMI eligibility for their messages.
DMARC enforcement example retaining Google's documented pct valueDNS
_dmarc.example.com TXT "v=DMARC1; p=quarantine; sp=quarantine; pct=100; rua=mailto:dmarc@example.com"
BIMI logo location and DKIM body length
BIMI and DKIM both use a tag written as l=, but the tags have different meanings. In a BIMI TXT record, l= identifies an external logo location. In a DKIM-Signature header, l= limits how much of the message body the signature covers.
Google's current BIMI troubleshooting guidance tells organizations using an email system other than Google Workspace not to use the DKIM body-length tag because it leaves unsigned body content open to abuse. Inspect the raw DKIM-Signature header. Removing this tag requires a change in the sending system's DKIM signer, not an edit to the BIMI TXT record.
Check the VMC PEM and embedded logo
A renewed VMC can break a previously working BIMI setup when DNS still points to the old PEM, the replacement file lacks part of its certificate chain, or the embedded SVG no longer meets Gmail's format requirements. If l= also points to a logo, use the exact SVG supplied for certificate issuance. Receivers can compare that file with the embedded logo and reject a mismatch; a visually similar export is insufficient.
What Gmail reads
- BIMI record: The selected record supplies the live a= certificate URL.
- Certificate chain: The PEM includes the entity certificate and issued CA certificates.
- Embedded mark: The VMC contains the SVG logo that Gmail validates for display.
What breaks display
- Old PEM: DNS still points to a previous certificate after renewal.
- Incomplete chain: The public file omits an intermediate or root certificate.
- Invalid embedded SVG: The logo inside the renewed certificate fails Gmail's image rules.
When the certificate authority offers a hosted PEM URL, using that URL can reduce asset drift. The important checks are that DNS points to the current file, Gmail can retrieve it, the chain is complete, and the embedded SVG is valid. If you publish a separate l= image for another receiver, keep that asset current too.
The issuer name alone rarely explains a missing Gmail logo. Check that a certificate from a currently trusted Mark Verifying Authority is within its validity period and has not been revoked, then verify its SVG and full chain. Check the Subject Alternative Name (SAN) entries against the domain where the selected BIMI assertion record was found. An organizational-domain fallback and a separate subdomain record can require different domain coverage. Renewing the web server's TLS certificate does not renew the VMC.
Gmail BIMI record with a VMC PEMDNS
default._bimi.example.com TXT "v=BIMI1; l=; a=https://assets.example.com/bimi/vmc.pem"
Subdomains and selectors
The subdomain issue is easy to miss. If your brand sends mail as offers.example.com, check the selected BIMI record for that visible From domain. When the child domain has no applicable record, the record for the same selector at the organizational domain can be used. With the default selector, if default._bimi.offers.example.com exists, it overrides the parent record and can keep an old PEM URL active.
Check the sending and organizational domainsBASH
dig TXT default._bimi.offers.example.com

dig TXT default._bimi.example.com
If you use a BIMI-Selector header, check its s= value. A selector of brand requires checking brand._bimi.offers.example.com and then brand._bimi.example.com, rather than substituting the parent's default record. Include the selector header in a passing DKIM signature whose domain satisfies DMARC; receivers are advised to ignore an unsigned selector header.
Publish one BIMI TXT record per selector and domain. Duplicate BIMI records stop discovery. A single TXT record split into multiple quoted DNS strings is valid and is different from publishing separate records.
Tie BIMI checks to real sending flows. A corporate newsletter, receipt stream, password reset stream, and sales automation stream can use different visible From domains, selectors, and DNS zones.
Hosting and redirects
Gmail needs to fetch the PEM and any published SVG reliably. Google's guidance calls for public HTTPS hosting and recommends TLS 1.2 or later. For an external SVG, Google says the public server should be in the domain used for the BIMI and outgoing-mail setup. A browser can hide redirects or access rules that stop a receiver fetch.
- Use HTTPS directly: The published URL should return the file without a redirect.
- Use current TLS: Configure TLS 1.2 or later with a trusted server certificate chain.
- Keep hosting in scope: Follow Google's domain-hosting guidance for self-hosted files. If the certificate authority hosts the PEM, verify that exact URL is public and current.
- Return the right file: The certificate URL must return the current PEM rather than an HTML page or download wrapper.
- Keep names stable: A changed path after renewal needs a matching DNS update.
- Avoid access controls: Do not put BIMI files behind cookies, bot checks, geofencing, or authentication.
Retrieve the files and inspect HTTP responsesBASH
curl -sS -D - -o /tmp/bimi-vmc.pem https://assets.example.com/bimi/vmc.pem

curl -sS -D - -o /tmp/bimi-logo.svg https://assets.example.com/bimi/logo.svg
These commands use GET without following redirects, so you can inspect the HTTP status and downloaded content. Expect a direct 200 response with the actual PEM or SVG, not a sign-in page. Skip the SVG request when l= is empty. A successful HEAD request alone does not verify the file body.
For any external SVG you publish, keep it square, static, and compliant with the BIMI SVG profile. Do not use JavaScript, external images, animation, or tracking pixels. If the logo changes, create a BIMI-specific SVG and obtain a certificate that contains the intended mark.
Where Suped fits
Suped cannot force Gmail to render a BIMI logo because Gmail makes the final display decision. Suped's product helps verify the DMARC and sending-source conditions that Gmail checks before it considers the certificate and brand mark.
DMARC record detail view showing SPF, DKIM, DMARC, rDNS diagnostics, and DNS records
Use Suped to confirm enforcement on the organizational domain and sending subdomains, identify sources that fail DMARC, inspect SPF and DKIM results, and check for blocklist (blacklist) listings. These listings do not measure Gmail's private reputation assessment. Validate the VMC or CMC status, PEM chain, and embedded SVG with the certificate authority and the live hosted file.
When BIMI stops showing after a VMC renewal, a practical Suped workflow is to confirm DMARC enforcement, review each legitimate sender for DMARC pass results, check DNS on any child domain that overrides the organizational record, and monitor for source-specific failures while the PEM issue is corrected.
?
What's your domain score?
Deep-scan SPF, DKIM & DMARC records for email deliverability and security issues.
Run a quick domain health check before inspecting BIMI files. If the domain still has DMARC, SPF, or DKIM failures, fix those first so the next Gmail test reaches the certificate and logo checks.
A practical fix sequence
When this problem appears after renewal, work through the checks in order. Each result determines whether the next test can produce useful evidence.
- Verify DMARC first: Use p=quarantine or p=reject with enforced organizational and sending-domain policies. Retain pct=100 to match Google's published BIMI guidance and leave policy testing disabled. Suped's Hosted DMARC can manage policy changes after legitimate sending sources are verified.
- Inspect the received message: Identify the visible From domain, BIMI selector, DMARC result, and any DKIM body-length tag.
- Query both DNS locations: Check the same selector on the From domain and at the organizational-domain fallback; remove duplicate BIMI records.
- Fetch the PEM: Confirm the live a= URL, validity dates, revocation status, SAN domain coverage, and full issued certificate chain.
- Validate the embedded SVG: Check SVG Tiny PS structure, Gmail's required dimensions, and its recommendations for file size and accessibility.
- Fix hosting: Use public HTTPS URLs, TLS 1.2 or later, and direct file responses. Follow Google's domain-hosting guidance for self-hosted assets.
- Send fresh mail: Test new messages after DNS TTLs expire, then use the reputation and retesting checks below if the logo remains absent.
If the old certificate worked and the renewed one does not, check the live PEM URL, certificate chain, embedded SVG, certificate status, and child-domain overrides before changing unrelated authentication records.
For a deeper validation workflow, the guide on how to validate BIMI records covers DNS, SVG, and certificate errors. The guide on whether you need a VMC explains the difference between Gmail logo display and the VMC-backed checkmark.
Reputation and retesting after technical checks pass
The BIMI Group note explains the broader caveat: a VMC does not guarantee display. Gmail still applies receiver policy and sender reputation checks, so a technically valid certificate can exist while the logo remains absent.
- Check recipient response: Review spam complaints and delivery errors for the affected domain and sending IP. Stop sending to recipients who did not request mail.
- Check sending history: Keep permission-based sending steady. A few test messages do not establish a reputation; do not manufacture volume to obtain a logo.
- Compare sending streams: If only one stream fails, compare its From domain and message authentication with a working stream before changing shared BIMI records.
- Keep evidence for escalation: Save the original received message, DNS answers, downloaded PEM, and HTTP responses so the certificate authority can investigate a reproducible failure.
Google's BIMI setup guide says logo display can take up to 48 hours after publishing the record. Passing technical checks and waiting 48 hours does not guarantee display. Retest with a fresh message in Gmail's own interface; reading a Gmail account through another mail app does not test Gmail's BIMI display.
Views from the trenches
Best practices
Check the SVG embedded in the live PEM after each VMC renewal, plus any external SVG.
Check the exact From subdomain, since stale child records often survive parent updates.
Keep BIMI logo and PEM URLs static, public, HTTPS-only, and free of redirect chains.
Common pitfalls
Teams renew the certificate but leave subdomain BIMI records pointing to old assets.
Browser success can hide redirect chains or access rules that prevent receiver retrieval.
The brand team supplies a similar logo, but the VMC embedded mark does not match it.
Expert tips
Send a fresh Gmail test after DNS TTLs expire and compare the exact message headers.
Let the certificate workflow own both hosted BIMI assets when drift keeps returning.
Fix DMARC failures before BIMI testing, since Gmail checks authentication first.
Marketer view
Marketer from Email Geeks says the first useful comparison is the VMC embedded image against the BIMI DNS logo.
2024-12-06 - Email Geeks
Marketer view
Marketer from Email Geeks says the exact sending domain matters because a subdomain record can stay stale after renewal.
2024-12-06 - Email Geeks
Frequently asked questions
No. Gmail still checks DMARC, the BIMI DNS record, PEM access, certificate validity, the full PEM chain, the embedded SVG, and sender reputation. Gmail supports VMCs and CMCs for BIMI logos, but only VMC-backed senders qualify for its verified checkmark.
The renewal can change the PEM file, public URL, certificate chain, or embedded SVG. DNS can also keep pointing to an older child-domain record. Fetch the live a= URL and check the new certificate's validity dates, revocation status, and SAN domain coverage before changing unrelated records.
A subdomain without an applicable BIMI record can use the same selector at the organizational domain. Without an accepted selector header, that selector is default. A child-domain record overrides that fallback and can keep an old certificate URL active. A custom selector does not switch to the parent's default record.
Yes. Publish the PEM and any external SVG at stable public HTTPS URLs that return the file directly. A browser can follow redirects, but that does not prove Gmail's receiver fetch accepts the same path.
Fix DMARC enforcement and source pass rates, remove the DKIM body-length tag when it is present on mail signed outside Google Workspace, verify BIMI DNS inheritance, retrieve the full PEM chain, validate the embedded SVG, and correct hosting or redirect problems. Replace the VMC only when those checks isolate the certificate.
Internal Google Workspace recipients can see a directory image, contact photo, or account profile image that is separate from BIMI. Test with an external personal Gmail inbox and inspect that received message before treating the internal logo as a BIMI pass.