What are the implications of using a DMARC policy of p=none?
Updated on 17 Oct 2026: We clarified DMARC report analysis and the receiver support checks needed before enforcement.
A DMARC policy of p=none means the domain owner requests no specific handling for messages that fail DMARC. With a reporting address, you gain visibility into who is sending mail using your domain, but the policy does not ask receivers to stop spoofed phishing mail that uses your exact domain.
Use p=none as a discovery phase when your sender inventory is incomplete. It is safer than jumping straight to enforcement when legitimate traffic still has SPF or DKIM domain mismatches. It is also weaker than p=quarantine or p=reject because fraudulent mail that fails DMARC is not contained by the policy itself.
- Visibility: Aggregate reports show sending sources, pass rates, and identifier alignment failures.
- No enforcement: Receivers are not asked to quarantine or reject DMARC failures.
- No inbox guarantee: Receivers still apply reputation, content, complaint, and abuse filters.
- Temporary state: The usual next step is an evidence-based move to an enforcing policy.
The strongest use of p=none is disciplined DMARC monitoring: collect reports, identify every legitimate sender, fix SPF or DKIM domain matching, then move to an appropriate enforcement policy.
What p=none actually does
DMARC passes when at least one of SPF or DKIM passes with identifier alignment to the visible From domain. In the default relaxed mode, the domains share the same organizational domain; strict mode requires an exact domain match. With p=none, the domain owner expresses no handling preference for DMARC failures.
Publish one DMARC TXT record at _dmarc.example.com for the domain example.com. Replace the example reporting address below with an address that receives and processes your reports.
Basic p=none DMARC recorddns
v=DMARC1; p=none; rua=mailto:dmarc-reports@example.com
That record publishes a monitoring policy. The rua tag requests aggregate reports; it is optional, so a record without it is valid but does not request aggregate reporting. For a reporting destination on another domain, confirm that the destination authorizes reports in DNS.
The short version
- Policy meaning: The domain owner requests no specific handling for DMARC failures.
- Reporting value: Send aggregate data if the receiver supports DMARC reporting.
- Receiver freedom: Spam filtering, reputation checks, and abuse controls still apply.
To confirm what your domain publishes today, Suped's DMARC checker is a direct first step. Check the policy and reporting address, then confirm whether the record has syntax errors before drawing conclusions from mail behavior.
DMARC checker
Look up a domain's DMARC record and catch policy issues.
?/7tests passed
How RFC 9989 affects a p=none rollout
RFC 9989 is the current Standards Track DMARC specification and obsoletes RFC 7489. The meaning of p=none remains monitoring without a requested enforcement action, but the rollout mechanics changed.
|
|
|
|---|---|---|
p=none | Monitoring policy | No requested enforcement action |
pct | Historic tag | Do not use percentage sampling for a new rollout |
t=y | Policy test mode | Supporting receivers apply one policy level below the declaration |
sp | Policy for existing subdomains | Overrides the parent p value when no more specific policy applies |
np | Policy for non-existent subdomains | Without np, these inherit sp if present, otherwise p |
DMARC policy tags that matter during a p=none rollout.
Under RFC 9989, p=quarantine; t=y requests an effective policy of none; p=reject; t=y requests quarantine. This is a binary test mode, not percentage-based sampling.
RFC 9989 quarantine test recorddns
v=DMARC1; p=quarantine; t=y; rua=mailto:dmarc-reports@example.com
Test mode depends on receiver support
Unknown tags are ignored. A receiver without t support can therefore ignore t=y and enforce the declared quarantine or reject policy. Do not treat this flag as a universal safety control; verify receiver behavior before relying on it.
Review subdomains before enforcement
A policy at the organizational domain also covers subdomains unless a more specific record or an applicable sp or np value changes the result. Inventory subdomain senders before leaving p=none.
Security and delivery implications
The biggest mistake is treating p=none as either useless or protective. It gives you authentication data when reporting is configured, but it does not ask receivers to contain mail that fails DMARC.
What p=none gives you
- Source discovery: You can see which services send using your domain.
- Failure patterns: You can find SPF, DKIM, and domain match gaps.
- Rollout safety: You can fix legitimate sources before enforcement.
What p=none does not give you
- No spoof block: DMARC failures are not rejected by your policy.
- No inbox pass: The receiver does not have to place mail in the inbox.
- No final state: The domain still needs a documented enforcement decision.
DMARC enforcement addresses unauthorized use of your exact From domain. It does not cover display-name impersonation or lookalike domains. Mail sent through a compromised authorized account can still pass DMARC.
Reputation and inbox placement
A p=none policy alone does not determine email reputation. Receivers assess the mail itself and their own reputation signals. Changing the policy value does not fix poor sending practices or guarantee inbox placement.
If authorized senders fail DMARC, investigate their authentication setup. Unknown sources need investigation before they are classified as abuse, because forwarding also changes the apparent sending source. Aggregate reports do not measure engagement, complaints, or sender reputation.
p=none meets the minimum published DMARC policy requirement for bulk senders to Gmail, Yahoo, and Outlook.com. It does not satisfy all sender requirements by itself: messages still need SPF and DKIM authentication and must pass DMARC. Receivers can reject noncompliant bulk mail even when the domain publishes a monitoring policy.
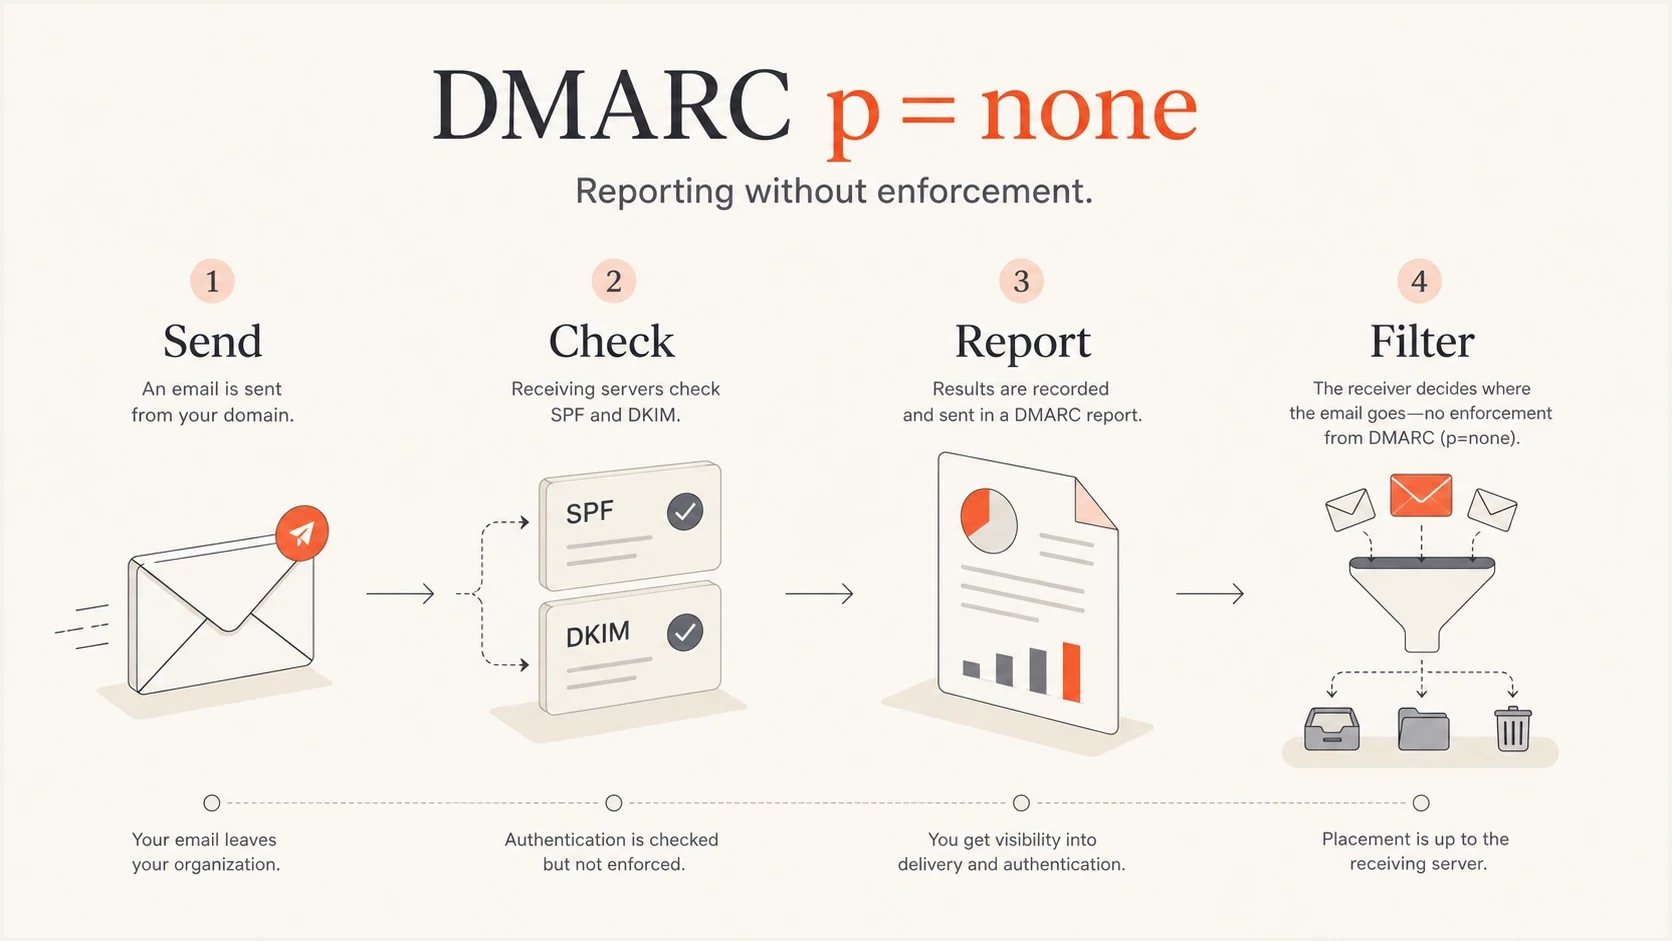
DMARC p=none flow showing SPF and DKIM checks, aggregate reporting, and receiver filtering.
Do not confuse reporting with protection
A domain at p=none provides useful visibility when reports are reviewed and failures are investigated. That visibility does not enforce a policy against failing mail.
- Good signal: You can see which mail sources need work.
- Bad assumption: Attackers are not stopped by this policy value.
- Next action: Fix legitimate senders and set a date for an enforcement review.
What to check in p=none reports
Aggregate reports are XML summaries of passing and failing mail, generally sent daily by participating receivers. RFC 9990 defines this reporting. The data includes source IPs, message counts, and authentication results; it is not a complete log of every message using your domain.
- Check domain matching, not just authentication passes. SPF checks the envelope sender (Return-Path), and DKIM checks its d= signing domain. A pass for a vendor domain does not establish DMARC for your visible From domain.
- Review each authorized sender separately. A low overall failure rate can hide a broken password reset stream. A high rate caused by spoofing does not mean legitimate mail is unready for enforcement.
- Investigate indirect mail. Forwarding often breaks SPF; a surviving DKIM signature with the required domain match can preserve a DMARC pass. Mailing-list changes to signed content can also break DKIM.
- Verify unfamiliar sources before authorizing them. Do not add an unknown IP to SPF just to improve a pass rate. Compare reports with your sender inventory and confirm ownership first.
A reported disposition of none means no DMARC quarantine or rejection was applied; it does not prove inbox delivery. Not every receiver sends reports, so also send test messages for critical mail streams and inspect authentication headers and actual delivery results.
Why starting at p=none is usually safer
Starting at p=none is usually safer because many organizations do not know every system that sends mail for them. Enforcement applied too early can send legitimate invoices or password resets to spam, or cause rejection at receivers that honor the policy.
A DMARC policy rollout path
Use monitoring to fix legitimate mail, and verify receiver support before relying on test mode.
Discovery
p=none
Collect reports and identify all real senders.
Optional policy test
p=quarantine; t=y
Use only after checking receiver support for t=y.
Enforcement
p=quarantine
Apply quarantine after reviewing authorized senders and indirect mail.
Stricter enforcement
p=reject
Use reject only after reviewing DKIM resilience and indirect mail.
Choose an observation period that covers a full sending cycle, including infrequent billing or seasonal mail. A small organization with two mail sources can move quickly. A larger organization needs enough history to identify overlooked senders before changing policy.
After legitimate mail passes consistently, introduce quarantine on a verified subdomain or other limited sending scope before expanding enforcement. Consider reject only after reviewing forwarding and mailing-list traffic. Domains with users who post to Internet mailing lists should generally avoid p=reject. A safe reject rollout should include DKIM domain matching, but DKIM cannot preserve a pass when intermediaries alter signed content.
How to use p=none without getting stuck
The main risk of p=none is inertia. Teams publish a record, see reports arrive, and never convert that visibility into a stronger policy. Treat p=none as a project phase with owners, dates, and exit criteria.
- Publish reports: Add a DMARC record with a valid aggregate reporting address.
- Group sources: Separate known services, internal systems, forwarders, and unknown senders.
- Fix senders: Configure SPF or DKIM to pass with the required domain match to the visible From address.
- Watch trends: Check each authorized mail stream across a full sending cycle; investigate repeated failures before changing policy.
- Test policy: Introduce quarantine on a limited sending scope. Use t=y only where receiver support has been verified.
- Keep alerts: Monitor after enforcement because sender changes happen later.
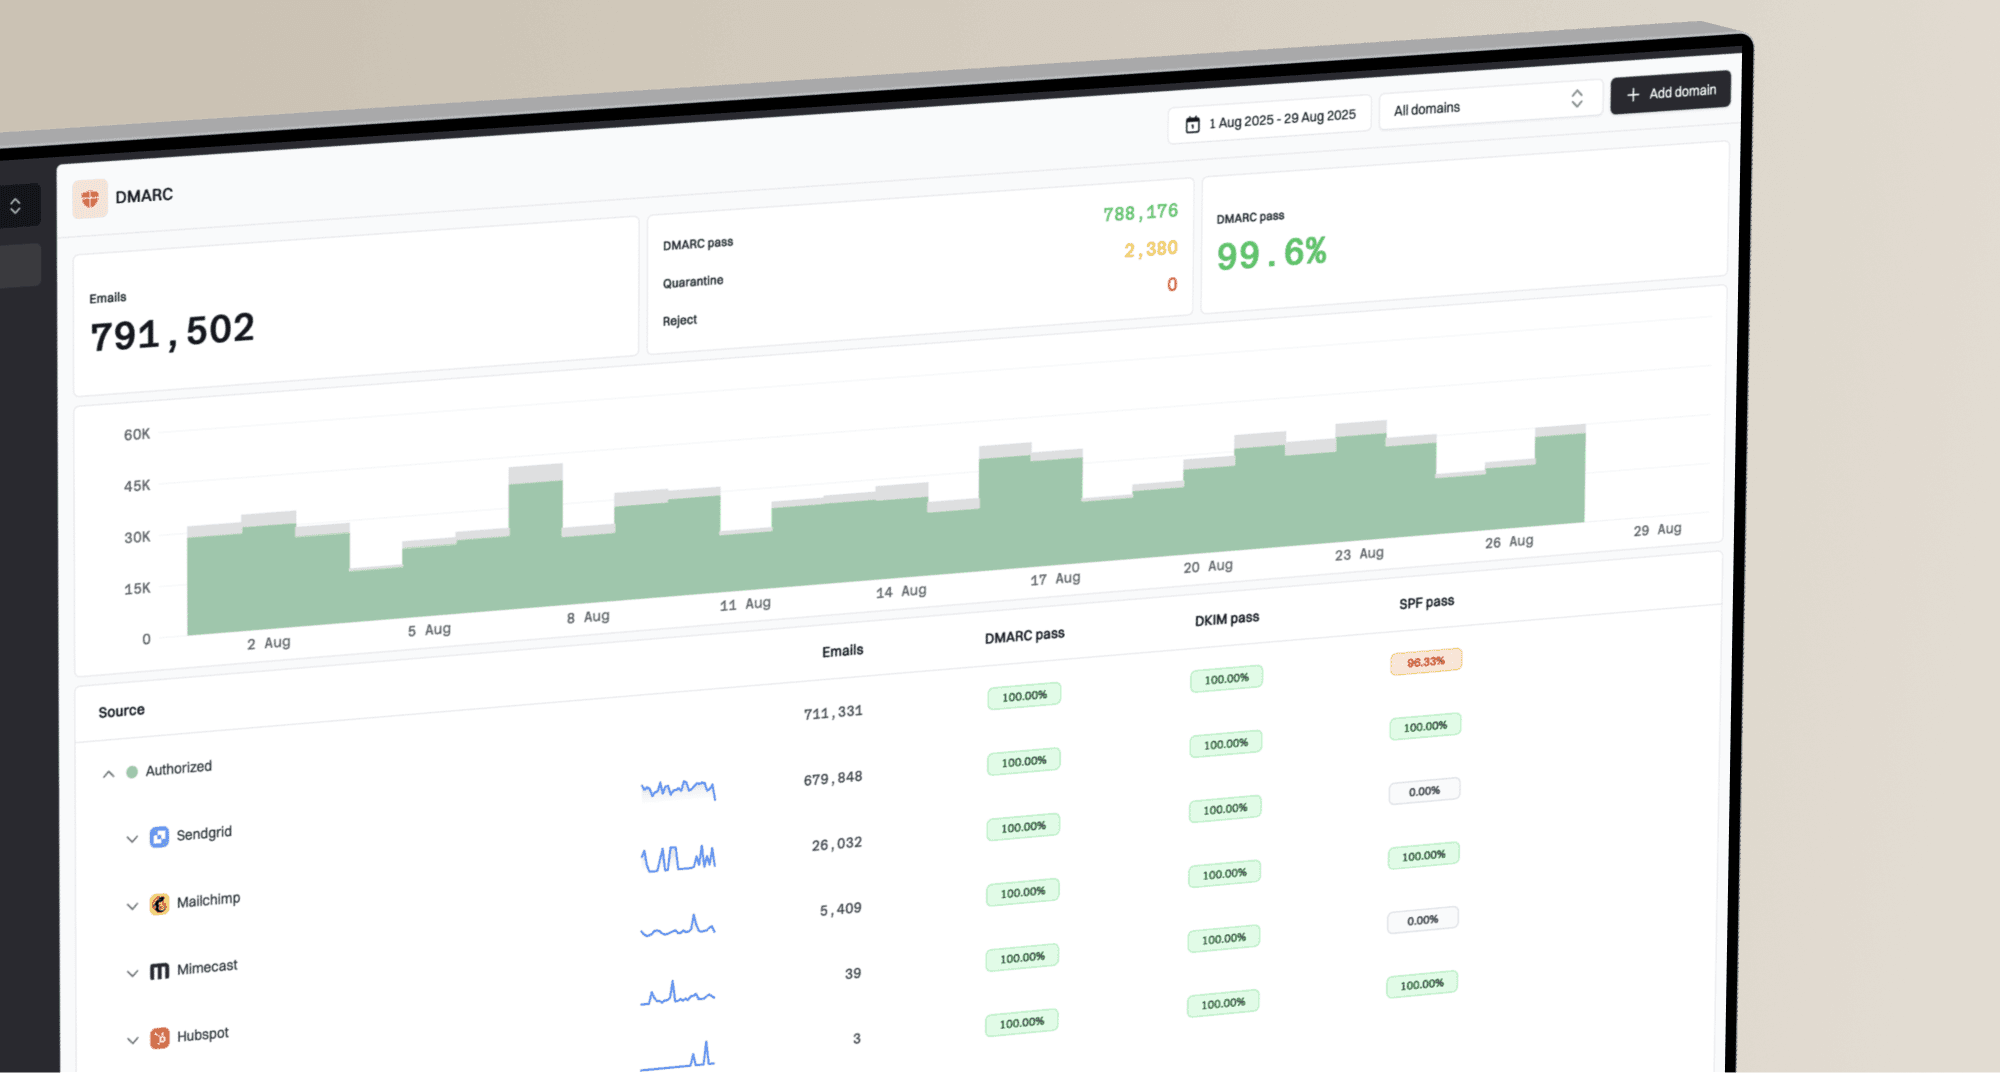
Suped DMARC dashboard showing email volume, authentication health, and source breakdown
Suped's DMARC reporting product turns aggregate reports into source lists and authentication results, with alerts for changes. Use those results to distinguish legitimate sender failures from spoofing and decide when to enforce a policy.
Teams can review DMARC authentication results in Suped and manage policy changes through Suped's Hosted DMARC. Review sender cleanup and monitor failures after each change.
If you are starting from scratch, a record generator helps create the first TXT value, but the ongoing work is interpreting the reports and making policy changes at the right time.
When to keep p=none or move to enforcement
A p=none policy is appropriate while you identify legitimate senders and fix authentication. Once authorized mail is ready, the next policy should follow evidence and the way the domain is used.
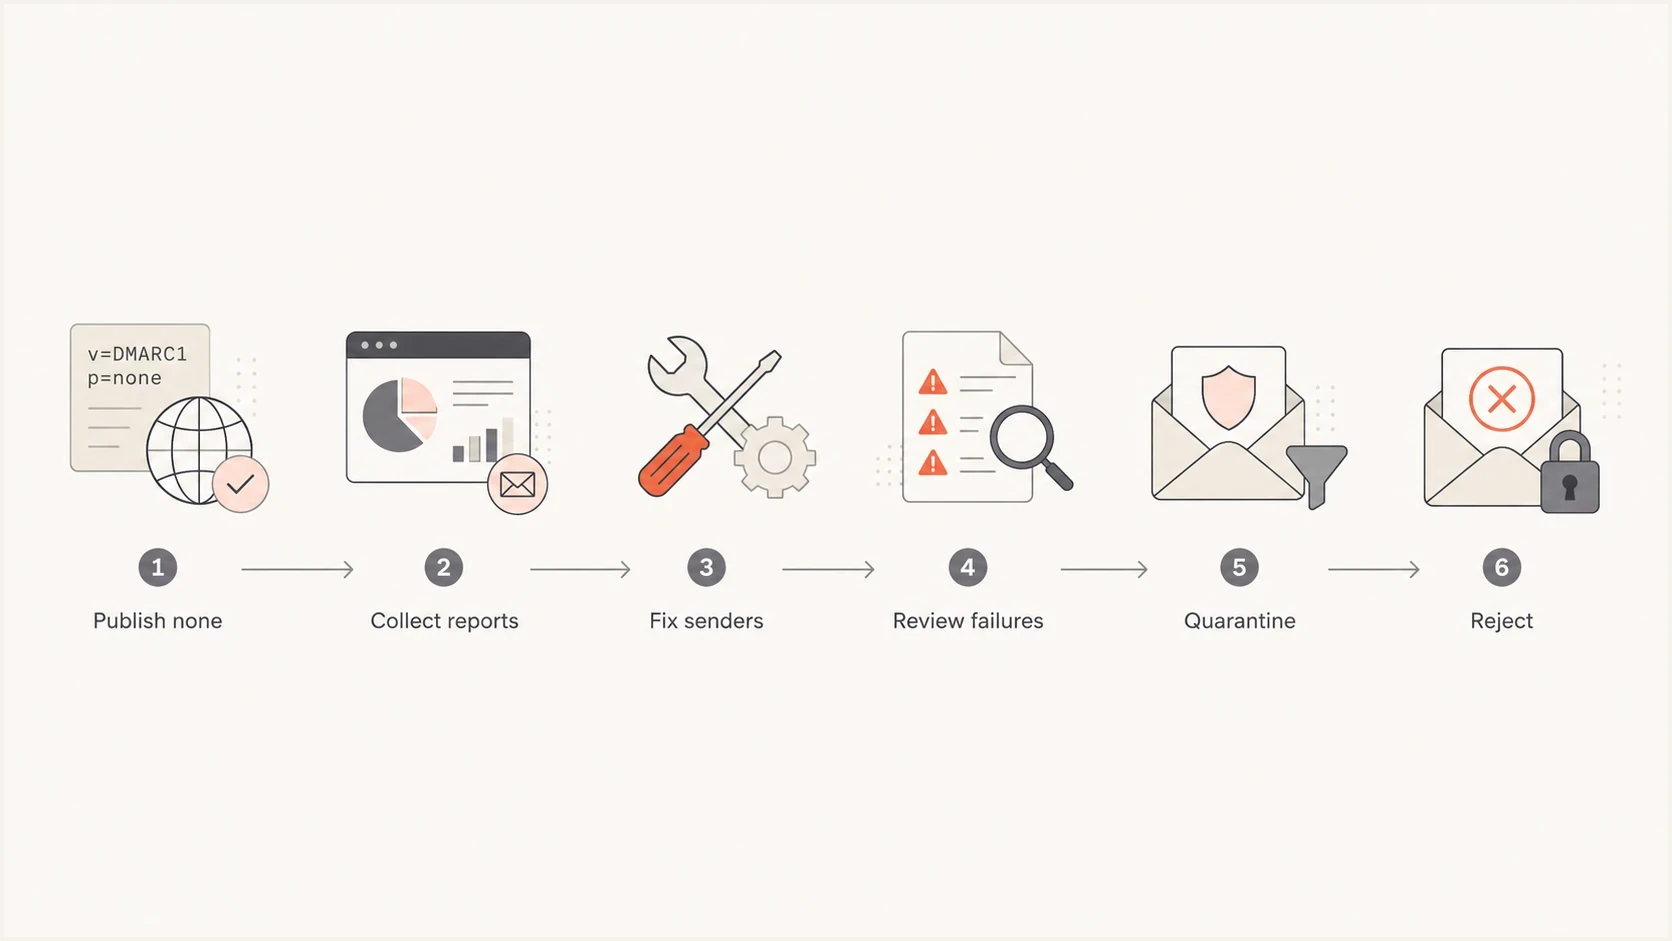
DMARC rollout showing p=none monitoring, sender fixes, failure review, quarantine, and reject.
When p=none is the right policy
- New rollout: You are publishing DMARC for the first time.
- Unknown sources: You cannot name every service sending mail for the domain.
- Active cleanup: You have owners fixing authentication failures.
When authorized streams pass consistently and remaining failures are understood, review quarantine even if spoofed traffic keeps the overall failure rate high. Continuing with p=none leaves those DMARC failures without a requested enforcement action.
When p=none is no longer enough
- Clean traffic: Legitimate senders pass consistently.
- Known abuse: Unknown sources are spoofing the visible domain.
- Completed checks: Subdomains and infrequent mail have been reviewed, including forwarding behavior.
Frequently asked questions
No. p=none publishes a DMARC policy, and a rua address requests aggregate reports. Having no DMARC record provides neither the published policy nor that reporting request. A p=none record remains valid without rua, but does not request aggregate reports.
The policy value alone does not determine sender reputation. Poor sending practices or complaints can affect reputation. Monitoring reveals authentication problems; it does not measure reputation or guarantee better delivery.
No. It only says the sender is not asking for DMARC-based quarantine or rejection. Receivers still use their own spam, abuse, reputation, and content filters.
Use a reporting window that covers your full sending cycle, including monthly billing and other infrequent mail. Move when authorized senders pass consistently and remaining failures are understood. There is no universal number of days or overall pass-rate threshold that makes every domain ready.
Move to quarantine when authorized senders pass consistently, remaining failures are understood, and someone is monitoring the change. Consider reject after reviewing quarantine results and DKIM behavior through forwarding. Domains whose users post to Internet mailing lists should generally avoid p=reject.
No. RFC 9989 made pct historic. t=y is a binary test mode, not a traffic percentage. Receivers without support for it can ignore the tag and enforce the declared policy, so verify support before relying on it.