How can I find out when my VMC expires?
Published 1 May 2025
Updated 17 Oct 2026
12 min read
Summarize with
Updated on 17 Oct 2026: We added automated VMC expiry checks and clarified certificate lookup, renewal timing, and Suped's BIMI renewal workflow.
The fastest way to find when a BIMI VMC expires is to open the VMC certificate file referenced in the domain's BIMI TXT record and read the X.509 validity field named notAfter. If the BIMI record has an a= tag, that tag points to the certificate URL. Download the PEM file, decode it, and read the expiry date.
For BIMI, VMC means Verified Mark Certificate. It confirms that a Mark Verifying Authority validated the organization and its right to use the logo, based on a registered trademark or a qualifying government mark. The expiry date lives inside the certificate itself, not in DMARC aggregate reports, the SVG logo file, or the visible BIMI DNS record.
Treat the date as an operational deadline. Mailbox providers that require a valid certificate can stop displaying the BIMI logo or related verified badge after expiry, subject to provider checks and caching.
Check your VMC expiry date
Check these places in this order. The live certificate gives the exact expiry date. The issuer portal is a fallback when the certificate URL is missing or inaccessible, or another internal team manages the file. The published certificate must be publicly retrievable over HTTPS without a login.
- Look up default._bimi for the sending domain, unless the message uses another BIMI selector, and copy the URL in the a= tag.
- PEM file: Download the certificate and read the notAfter field with a certificate viewer or openssl.
- If the file is inaccessible, check the certificate authority account or renewal order, then restore public HTTPS access for mailbox providers.
- Internal owner: If another team bought the VMC, ask for the certificate file, expiry date, and renewal owner.
|
|
|
|---|---|---|
BIMI TXT | Certificate URL | Fast lookup |
PEM | notAfter | Exact date |
CA portal | Certificate expiry and renewal status | Renewal admin |
Runbook | Renewal owner | Team handoff |
Common places where the VMC expiry date appears.
Use the live PEM and its notAfter value as the authoritative expiry date for what mailbox providers can retrieve. Check the issued certificate's expiry in the portal, rather than the subscription or order end date. A paid renewal does not prove that the current public file has been replaced.
The main trap is checking the wrong asset. The BIMI SVG has its own hosting URL, but the VMC expiry date is in the certificate referenced by the a= tag. If you only inspect the logo URL, you confirm the logo is reachable, but you do not confirm the certificate is still valid. The browser's connection certificate belongs to the HTTPS server; its expiry date is separate from the VMC inside the downloaded PEM.
Find the certificate URL in DNS
Start with the BIMI TXT record for the exact domain in the RFC5322.From address. If the sender does not specify another BIMI selector, start with default, which makes the lookup name default._bimi.example.com. The record should include a logo location in l= and, when a VMC or related certificate is published, a certificate location in a=.
Look up the BIMI TXT recordBASH
dig +short TXT default._bimi.example.com
Example BIMI TXT recordDNS
default._bimi.example.com. IN TXT (
  "v=BIMI1; "
  "l=https://assets.example.com/bimi/logo.svg; "
  "a=https://assets.example.com/bimi/vmc.pem;"
)
That vmc.pem file is the thing to inspect. If the a= value is empty or absent, there is no certificate URL to decode from DNS. That can be a self-asserted BIMI record, but support for self-asserted logos is limited and providers that require a mark certificate will not accept it as certificate-backed BIMI.
Check the real sending domain
Query the exact RFC5322.From domain with the selector used by the sender. If no BIMI record exists for a subdomain, also check that selector at the organizational domain, which is the fallback in BIMI record discovery. Separately confirm DMARC enforcement for both domains. A parent-domain record does not prove that its certificate covers every sending subdomain.
If you are also checking whether the domain is eligible for BIMI display, verify DMARC enforcement at the same time. Suped's domain health checker checks the domain's authentication records alongside the certificate lookup.
?
What's your domain score?
Deep-scan SPF, DKIM & DMARC records for email deliverability and security issues.
Decode the PEM certificate
After you have the certificate URL, use a certificate viewer or decode it locally. Local decoding gives the exact validity fields without adding another dependency to the process. The field you want is notAfter. That is the end of the certificate validity period.
Download and read the expiry dateBASH
curl -fLsS --proto '=https' --proto-redir '=https' --max-time 30 \
  https://assets.example.com/bimi/vmc.pem -o vmc.pem &&
openssl x509 -in vmc.pem -noout -dates -issuer -subject
Example outputTEXT
notBefore=Feb  1 00:00:00 2026 GMT
notAfter=Jan 31 23:59:59 2027 GMT
issuer=C = US, O = Example Certificate Authority
subject=jurisdictionC = US, O = Example Brand Inc.
In that output, the VMC expires at 23:59:59 GMT on January 31, 2027. Record that internally as 2027-01-31T23:59:59Z with a separate renewal-start date. The Z means UTC. ISO 8601 avoids the day/month confusion that happens when an interface shows a date such as 04/05/2027.
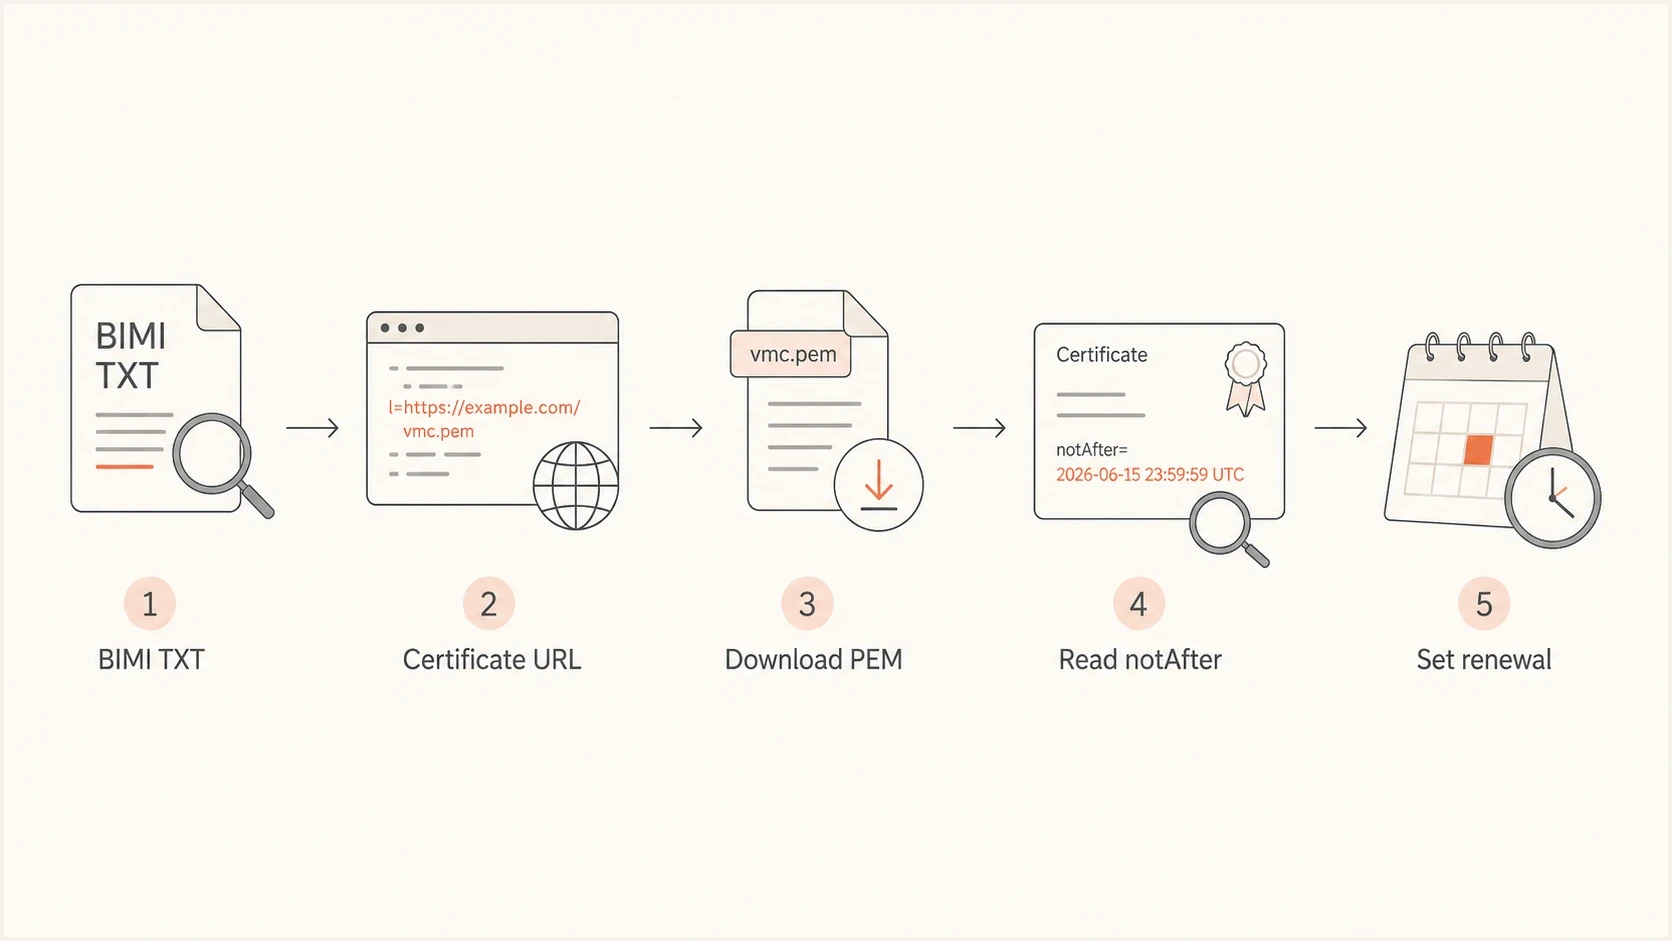
Steps to check a VMC expiration date using the BIMI TXT record, certificate URL, and PEM file.
Use one date format
Some interfaces display certificate dates as day/month/year. Others display month/day/year. Store the renewal record as an ISO 8601 timestamp, such as 2027-01-31T23:59:59Z, and include the source output beside it.
A future expiry date alone does not establish certificate validity. Also check the notBefore start date, revocation status, certificate chain, and coverage of the sending domain and logo.
Automate VMC expiry checks
Run a fresh download daily and use OpenSSL's -checkend option to check the days remaining without parsing a date string. The value is in seconds: 2592000 checks a 30-day renewal window.
Check whether the live VMC expires within 30 daysBASH
curl -fLsS --proto '=https' --proto-redir '=https' --max-time 30 \
  https://assets.example.com/bimi/vmc.pem -o vmc.pem &&
openssl x509 -in vmc.pem -noout -checkend 2592000
- Exit status 0 means the expiry date is more than 30 days away after a successful download and certificate parse.
- A nonzero status requires investigation: the certificate is within the renewal window or already expired, or the download or certificate parsing failed.
Schedule the command in your existing job scheduler and route nonzero results to the renewal owner. Use 5184000 for a 60-day threshold. Fetch the current a= URL each time and update the job when that URL changes. This is an expiry check; retain the separate checks for overall BIMI validity.
What VMC expiry changes
VMC expiry is a BIMI display event. It does not by itself stop email delivery or change the underlying authentication results. Mailbox providers that require a valid certificate can stop showing the logo or a VMC-based verified badge once they detect the expired certificate.
- Logo and badge display: Providers that validate the VMC can stop rendering the BIMI logo or related badge.
- Email delivery: Messages continue to send and receive because the VMC is not an SMTP delivery credential.
- Authentication: SPF, DKIM, and DMARC keep operating independently of the VMC validity window.
- Visible timing: Provider checks and caching can make the logo disappear or return at different times.
The BIMI TXT record can remain published after the certificate expires, but its a= URL then points to invalid evidence. Replace or remove the expired certificate reference promptly, and do not treat a cached logo as proof that the certificate is still accepted.
If the certificate is not in the BIMI record
If the BIMI record has no usable a= value, check the selector and any organizational-domain fallback first. Check whether the certificate is unpublished, the domain uses a self-asserted BIMI record, or another team manages the VMC in a certificate authority account. An issued certificate still needs a public URL before mailbox providers can retrieve it.
Public DNS path
- Best case: The BIMI record has an a= URL pointing to a public PEM file.
- Evidence: The decoded certificate shows issuer, subject, and notAfter.
- Action: Record the date, set alerts, and confirm the renewal owner.
Private admin path
- Common case: The certificate is owned by legal, security, procurement, or an agency.
- Inspect the issued certificate's validity window and renewal state in the issuer portal, rather than the order or subscription end date.
- Action: Ask for the PEM file, order ID, expiry date, and renewal contact.
When the admin path is the only option, ask for a screenshot of the certificate validity and a copy of the issued PEM. The screenshot helps with procurement, but the PEM is better for technical verification because you can decode it the same way mailbox systems do. Compare the portal date with the live PEM before closing the renewal task.
If you are trying to determine whether a domain uses a VMC or another BIMI certificate type, the differences are worth checking before you renew. The practical comparison is covered in VMC vs CMC.
Plan your VMC renewal
Once you know the date, turn it into a renewal workflow. BIMI Mark Certificates have a maximum validity period of 398 days, so renewal is normally an annual operational task. Shorter browser-trusted TLS certificate lifetimes do not automatically apply to VMCs. A multi-year subscription still requires replacement certificates before each published certificate expires. Start renewal about 60 days before expiry and confirm your issuer's lead time. Renewal can require time for trademark checks, organization validation, payment approval, certificate issuance, file hosting, DNS review, and provider-side caching.
VMC renewal timing
Suggested renewal milestones based on days remaining until notAfter.
Healthy
60+ days
Confirm the owner and start renewal about 60 days before expiry.
Watch
30-59 days
Renewal underway; follow up on validation and issuance.
Urgent
8-29 days
Issue, host, and validate the replacement certificate.
Critical
0-7 days
Escalate renewal and deployment before the expiry deadline.
Before expiry, keep the current certificate URL stable until the replacement certificate is published and verified. Do not continue publishing an expired certificate. If renewal gives you a new PEM file at a new URL, update the BIMI a= tag, then test the record after DNS propagation. If the same URL is reused, confirm the hosted file changed by downloading it again and reading the new notAfter value.
Minimum renewal record
- Domain: The visible From domain and the BIMI lookup name.
- Certificate: The PEM URL, issuer, subject, and notAfter output.
- Owner: The team or person responsible for renewal payment and validation.
- Alert dates: Calendar reminders at 60, 45, 30, 14, and 7 days before expiry.
Also check what happens operationally when the VMC expires. The visible result is not identical in every mailbox, and caching can hide or delay the impact. The practical failure modes are explained in what happens when VMC expires.
Keep DMARC healthy around the renewal
A valid VMC does not compensate for weak authentication. BIMI display depends on the domain meeting mailbox provider requirements, and DMARC enforcement is the foundation. A VMC renewal checklist should sit beside ongoing DMARC monitoring, SPF and DKIM source review, and DNS change control.
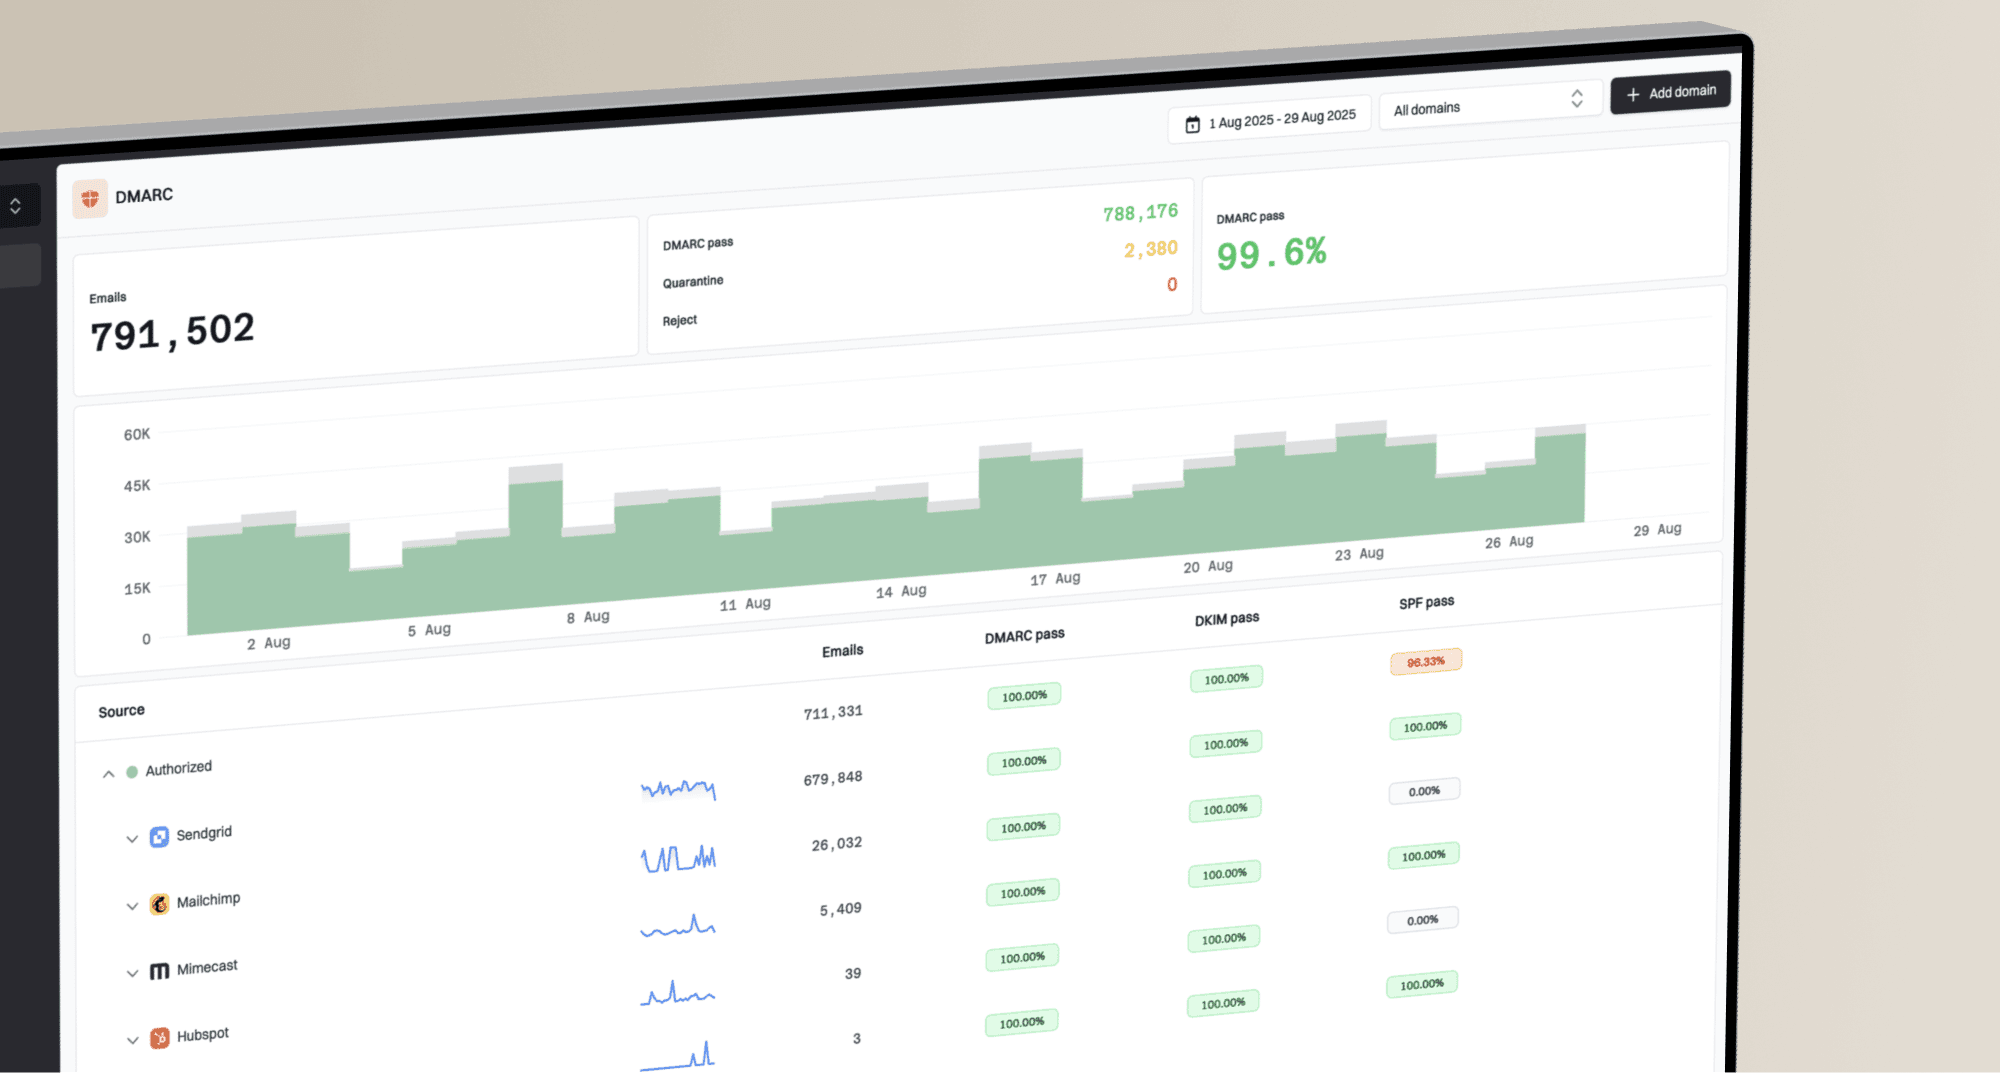
Suped's DMARC platform turns authentication reports into issues and fix steps, helping teams check enforcement and identify senders that fail authentication around a certificate change. Suped's BIMI service also handles certificate applications and ongoing renewals. Keep the live PEM's expiry date in the renewal record so the deployed certificate can be verified independently.
Suped DMARC dashboard showing email volume, authentication health, and source breakdown
The useful workflow is straightforward: confirm the VMC notAfter date, verify that DMARC is still at enforcement, check that authorized senders pass authentication, then publish the renewed certificate without changing unrelated DNS. Suped supports that authentication review by monitoring DMARC policy and showing failures reported by receiving providers.
If you only need to validate the current DMARC record before a BIMI change, Suped's DMARC checker gives a focused record check. For teams managing many domains, Suped centralizes DMARC reports and policy alerts around certificate work.
Troubleshoot VMC expiry checks
Most expiry checks are simple, but a few cases need extra care. Check these when the public record and certificate details do not match what the business expects.
- Wrong domain: The brand uses one domain for corporate mail and another for marketing mail.
- Old file: The certificate URL still serves the previous PEM after a renewal order completed.
- Bundle order: The PEM contains more than one certificate, so check the leaf certificate first.
- Date display: The interface shows local time or day/month order, while OpenSSL's default date output uses GMT.
- Provider cache: Mailbox provider caching delays the visible effect of a replaced certificate.
In a PEM bundle, OpenSSL reads the first certificate for the commands above. Confirm that it is the VMC leaf certificate by checking the subject and issuer, then inspect the remaining chain. The published bundle should put the VMC first, followed by its issuing intermediates; the root is optional. An expired intermediate can also invalidate the chain before the VMC's own expiry date.
Inspect a PEM bundleBASH
openssl crl2pkcs7 -nocrl -certfile vmc.pem |
openssl pkcs7 -print_certs -text -noout
After renewal, validate the whole BIMI setup, not only the certificate. That means checking the SVG profile, certificate chain, DNS record syntax, HTTPS hosting, and DMARC enforcement. A focused BIMI validation checklist is covered in validating BIMI records.
Views from the trenches
Best practices
Store the full VMC notAfter timestamp in UTC with the owner and renewal contact details.
Download the PEM from the live BIMI record, then keep the decoded output as evidence.
Start renewal about 60 days before expiry and confirm validation lead times with the issuer.
Check each sending domain and selector, including any organizational-domain fallback.
Common pitfalls
Reading the SVG logo URL confirms hosting, but it does not reveal certificate expiry.
Using local date formats causes month and day confusion when teams work across regions.
Assuming the issuer portal changed the live PEM leads to stale public certificates.
Assuming a parent-domain certificate covers every sending subdomain can conceal gaps.
Expert tips
Keep the valid current certificate available until its replacement is live and verified.
Set calendar alerts at 60, 45, 30, 14, and 7 days before the VMC certificate expires.
Capture the issuer, subject, and full notAfter timestamp together for each renewed VMC.
After renewal, check DNS, HTTPS hosting, the SVG profile, and DMARC enforcement together.
Marketer view
Marketer from Email Geeks says the public BIMI record is the first place to check when it links directly to the certificate file.
2024-01-11 - Email Geeks
Marketer view
Marketer from Email Geeks says decoding the PEM file gives the expiry date when a public checker or UI is not available.
2024-01-11 - Email Geeks
Frequently asked questions
It is stored inside the VMC certificate as the X.509 notAfter value. The BIMI record points to the certificate URL, but the record itself usually does not show the expiry date.
No. The SVG is the logo asset. The VMC expiry date is in the certificate file referenced by the BIMI a= tag.
Check the sending domain and selector, including the organizational-domain fallback when the subdomain has no BIMI record. If the a= tag is still missing, use the certificate authority account or ask the internal owner for the PEM file and expiry date. Publish a publicly accessible HTTPS certificate URL for certificate-backed BIMI.
No. VMC expiry affects certificate-backed BIMI display, not SMTP delivery. SPF, DKIM, and DMARC continue to operate, although providers that require a valid VMC can stop showing the logo or related badge.
Start about 60 days before expiry and confirm the issuer's lead time. Reserve time for validation and certificate issuance, then publish and verify the renewed PEM before the current certificate expires.
Suped's BIMI service handles certificate applications and renewals. For the exact expiry date of the certificate currently published, download the live PEM and read notAfter. Suped's DMARC platform supports the authentication checks around renewal.