What are the deliverability concerns of found mails that did not contain URLs in HTML tags within quoted-printable MIME-parts?
Updated on 16 Oct 2026: We clarified how to verify quoted-printable links and separate parser warnings from delivery failures.
A bare URL finding means a scanner found a literal URL written as text in the HTML body rather than inside an HTML attribute such as href, src, or action. Quoted-printable matters because that encoding escapes some characters and folds long lines, so the scanner must decode the MIME part correctly before it judges the HTML.
Do not treat the finding as proof of an inbox placement problem. A bare URL in an HTML part is usually a template quality issue, not a deliverability root cause. The risk rises when the final sent MIME also has broken markup, misleading link presentation, failed tracking rewrites, invalid transfer encoding, or authentication and reputation problems.
- Risk level: Low by itself, higher with malformed HTML, broken MIME boundaries, or link rewriting errors.
- Common cause: A URL was inserted as visible text in the HTML editor instead of being added through the editor's link control.
- Practical fix: Decode and inspect the delivered HTML part, wrap intended links in valid anchors, then send another test through the production path.
What the warning means
The wording is not a standard SMTP, MIME, or DMARC error. It does not identify a universal spam-filter rule or a fixed score. Confirm the detector's exact rule identifier and score, then inspect the raw message it flagged before deciding what to change. An HTML message with no links, or a message with URLs only in its text/plain alternative, does not need extra anchors.
A URL can appear in an HTML email in several ways. The first pattern below is a bare URL; the other patterns are explicit HTML links. Whether a detector flags a pattern depends on its rule.
Three URL patterns in HTML emailhtml
https://www.example.com/

<a href="https://www.example.com/">
  www.example.com
</a>

<a href="https://www.example.com/">
  Read the update
</a>
The first line is visible text. Many mail clients turn it into a clickable URL, but it is still not an HTML link. Link scanners and rewrite systems work more predictably when the target URL sits in a valid attribute. Malformed markup is a separate problem: validate the decoded HTML when a tag or attribute is broken.
Bare URL in HTML
- Markup: The URL is text in the body.
- Rendering: Some clients auto-link it, while others leave it as plain text.
- Scanning: Scanners can still extract the URL as text, but HTML-only rewrite systems have no explicit anchor target.
URL in an anchor
- Markup: The URL sits inside a valid HTML attribute.
- Rendering: The template controls the clickable text.
- Scanning: Link rewriting and URL checks have a defined target.
How quoted-printable encodes HTML links
Quoted-printable is a MIME content-transfer encoding defined by RFC 2045. It keeps much of the content readable in the raw source, encodes an equals sign as =3D, and uses an equals sign at the end of an encoded line as a soft line break. Encoded lines must not exceed 76 characters, excluding the ending CRLF.
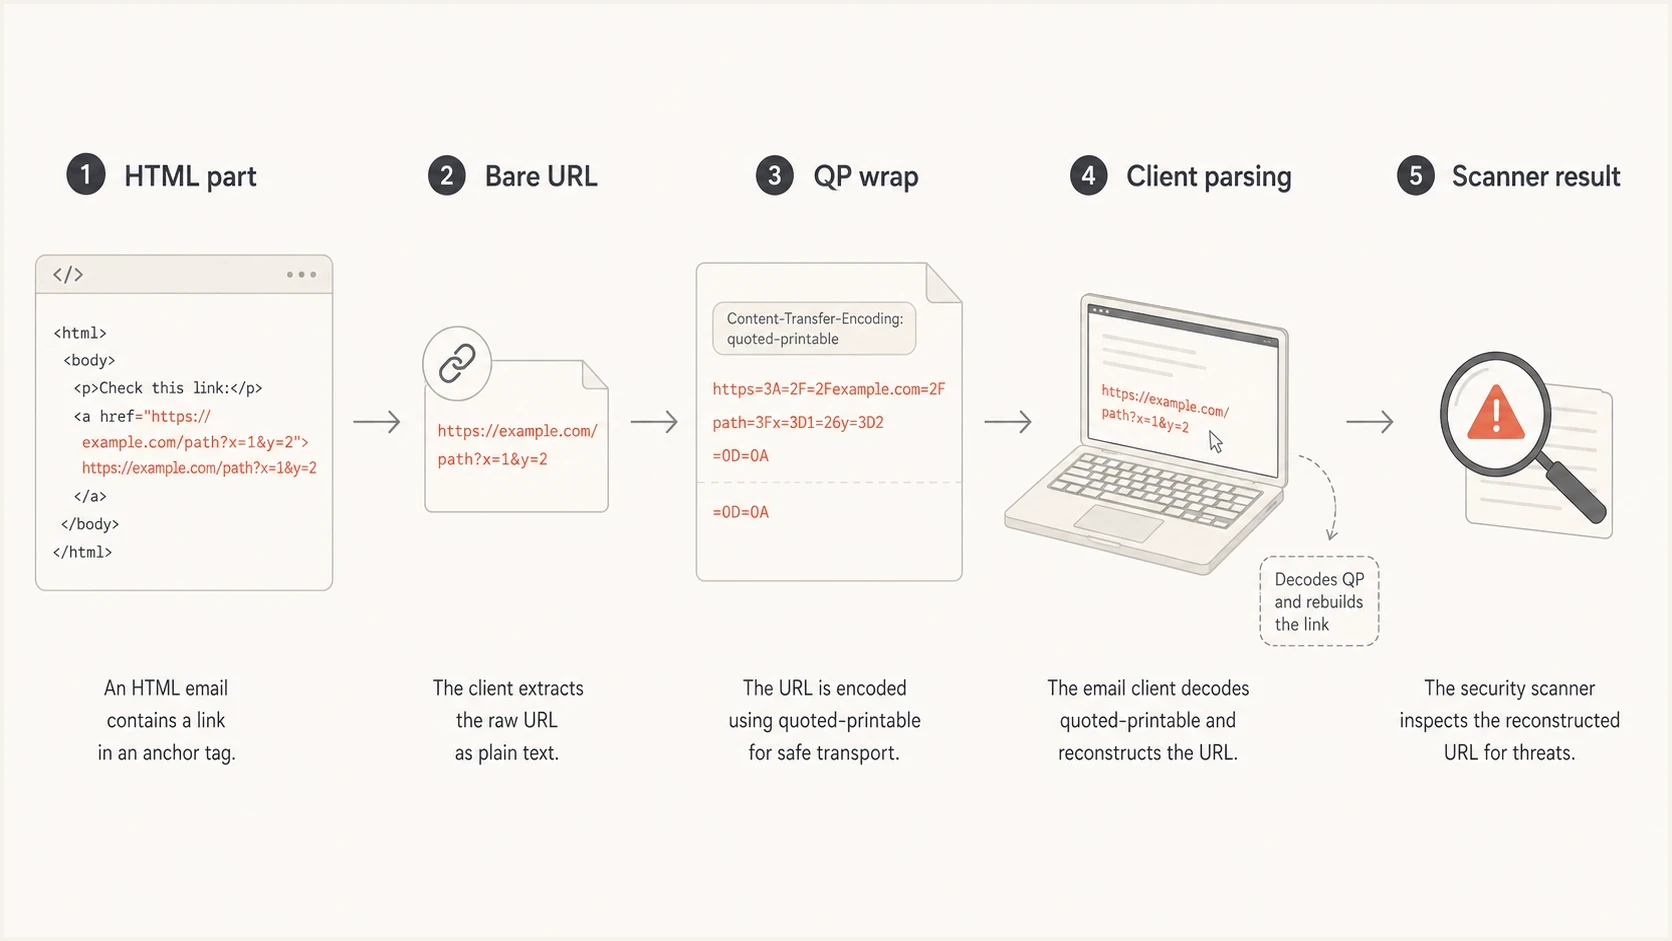
How quoted-printable encoding wraps an HTML URL before MIME decoding and scanning.
A valid link can look odd before decoding because equals signs are escaped and long lines are folded. A MIME-aware client restores =3D to = and removes soft line breaks before parsing the HTML. Seeing =3D in raw source is normal. An unexpected =3D left in the decoded href warrants checking the encoding header and whether the body was encoded twice. Encoding an existing =3D escape again produces =3D3D.
Valid quoted-printable link syntax
<a href=3D"https://www.example.com/path?campaign=3Dspring">
  Read the update
</a>

<a href=3D"https://www.example.com/a/very/long/path?campaign=3D=
spring">Read more</a>
A soft line break is an equals sign immediately followed by CRLF, and that equals sign counts toward the 76-character limit. Never split an =XX escape across lines. Encode trailing spaces and tabs as =20 and =09. Let the email library handle wrapping and encoding.
Do not debug only the template preview. The email service provider (ESP) can add tracking, rewrite links, inline CSS, add unsubscribe headers, and choose MIME encodings after the preview is rendered. The raw source of a delivered test email is the version that matters.
- Preview risk: The saved design can look correct while the sent MIME has a broken attribute.
- Encoding risk: An invalid soft break can leave an equals sign or line break inside a URL.
- Testing risk: A screenshot does not prove that the received source is structurally valid.
Decode MIME before judging HTML
MIME and HTML are separate layers. First identify the intended text/html body part using the multipart boundary and Content-Type header. Then apply its Content-Transfer-Encoding, using the declared charset when turning bytes into text. Only after those steps should a validator or scanner parse the result as HTML. Quoted-printable encodes bytes; a wrong charset can still garble text after transfer decoding.
Relevant MIME headers
MIME-Version: 1.0
Content-Type: multipart/alternative; boundary="mime-boundary"

--mime-boundary
Content-Type: text/plain; charset=UTF-8
Content-Transfer-Encoding: quoted-printable

Read the update: https://www.example.com/
--mime-boundary
Content-Type: text/html; charset=UTF-8
Content-Transfer-Encoding: quoted-printable

<a href=3D"https://www.example.com/">Read the update</a>
--mime-boundary--
- Select the part: Confirm the warning points to text/html rather than the text/plain alternative.
- Check the label: Verify that Content-Transfer-Encoding matches the body that follows.
- Decode once: Remove valid soft breaks and convert each hexadecimal escape before parsing HTML.
- Validate boundaries: Confirm every multipart delimiter opens and closes the intended body part.
If a quoted-printable body lacks its transfer-encoding header, has the wrong label, or was encoded twice, the recipient can see encoded characters or receive a damaged HTML part. A missing Content-Transfer-Encoding defaults to 7bit. If a boundary is broken, a client can select the wrong alternative or stop parsing early. Wrapping a visible URL in an anchor will not fix these message construction failures.
Use the decoded text/html part for HTML review, but keep the original raw message for MIME review. Editing raw source by deleting every occurrence of 3D can create a second equals sign or corrupt legitimate text because only the complete =3D escape decodes to one equals sign.
When the warning is a parser false positive
Each MIME part has its own transfer encoding. A base64 text/plain alternative and a quoted-printable text/html alternative in one message are valid. A parser that mishandles a multipart boundary can report encoded text or missing links even when another client renders the message correctly.
A documented MIME boundary bug involved encoded content displayed by one application while another displayed the same message correctly. The issue was closed after a boundary-detection fix.
Export the original .eml file without forwarding it and compare its decoded HTML in a second MIME-aware client. If the source is valid and the problem occurs only in one parser, update that parser and retest. Keep actual inbox or junk placement separate from parser warnings.
Actual deliverability concerns
Quoted-printable does not imply poor delivery, and a visible URL does not imply spam. The warning matters when it exposes invalid message construction, confusing link presentation, or generated HTML that changes after tracking and transport processing. Use valid HTML, and make the visible link text explain the destination.
|
|
|
|---|---|---|
Bare URL | Intended link lacks an explicit anchor | Add an anchor if it should be clickable |
Broken tag | Client parsing can differ | Validate decoded HTML |
Rewrite error | The tracked link can fail | Inspect delivered source |
MIME error | The body can render incorrectly | Fix encoding or boundaries |
Authentication failure | Spam or rejection risk rises | Investigate DMARC alignment |
Reputation issue | Filtering can increase | Review sending signals |
How to weigh the warning during triage.
Check two link-specific problems early: display mismatch and rewrite failure. Display mismatch means the visible URL or link text suggests a different destination domain. Rewrite failure means tracking or security processing changed the URL in a way the client or scanner cannot parse cleanly. Link handling has separate delivery and recipient-trust implications.
How serious this warning is
A bare URL finding matters most when it appears with other broken-message signals. These are qualitative triage priorities, not measured spam-score thresholds.
Low
Template cleanup
One visible URL with valid HTML and aligned authentication.
Medium
Send test
Bare URLs with link rewrite or rendering differences.
High
Full triage
Broken MIME or independently observed authentication or reputation failures.
When this warning appears on a campaign with authentication failures, weak engagement, or a blocklist (blacklist) hit, do not blame the bare URL first. Fix any confirmed template defect, then work through the higher-impact causes in priority order.
How to test a real send
Send the real campaign or a production-equivalent clone to a seed address, then inspect the delivered source. The final received MIME matters more than the editor canvas. Suped's email tester checks the received message's SPF, DKIM and DMARC results plus sending-setup issues such as blocklist (blacklist) listings.
Check the sending domain in parallel. A clean template does not compensate for failed DMARC alignment, a DKIM signing problem, an SPF lookup error, or damaged reputation. Suped's domain health checker checks published SPF and DMARC records and DKIM keys at common selectors. It cannot verify a message's signature or DMARC result from DNS alone; use the received-message test for that.
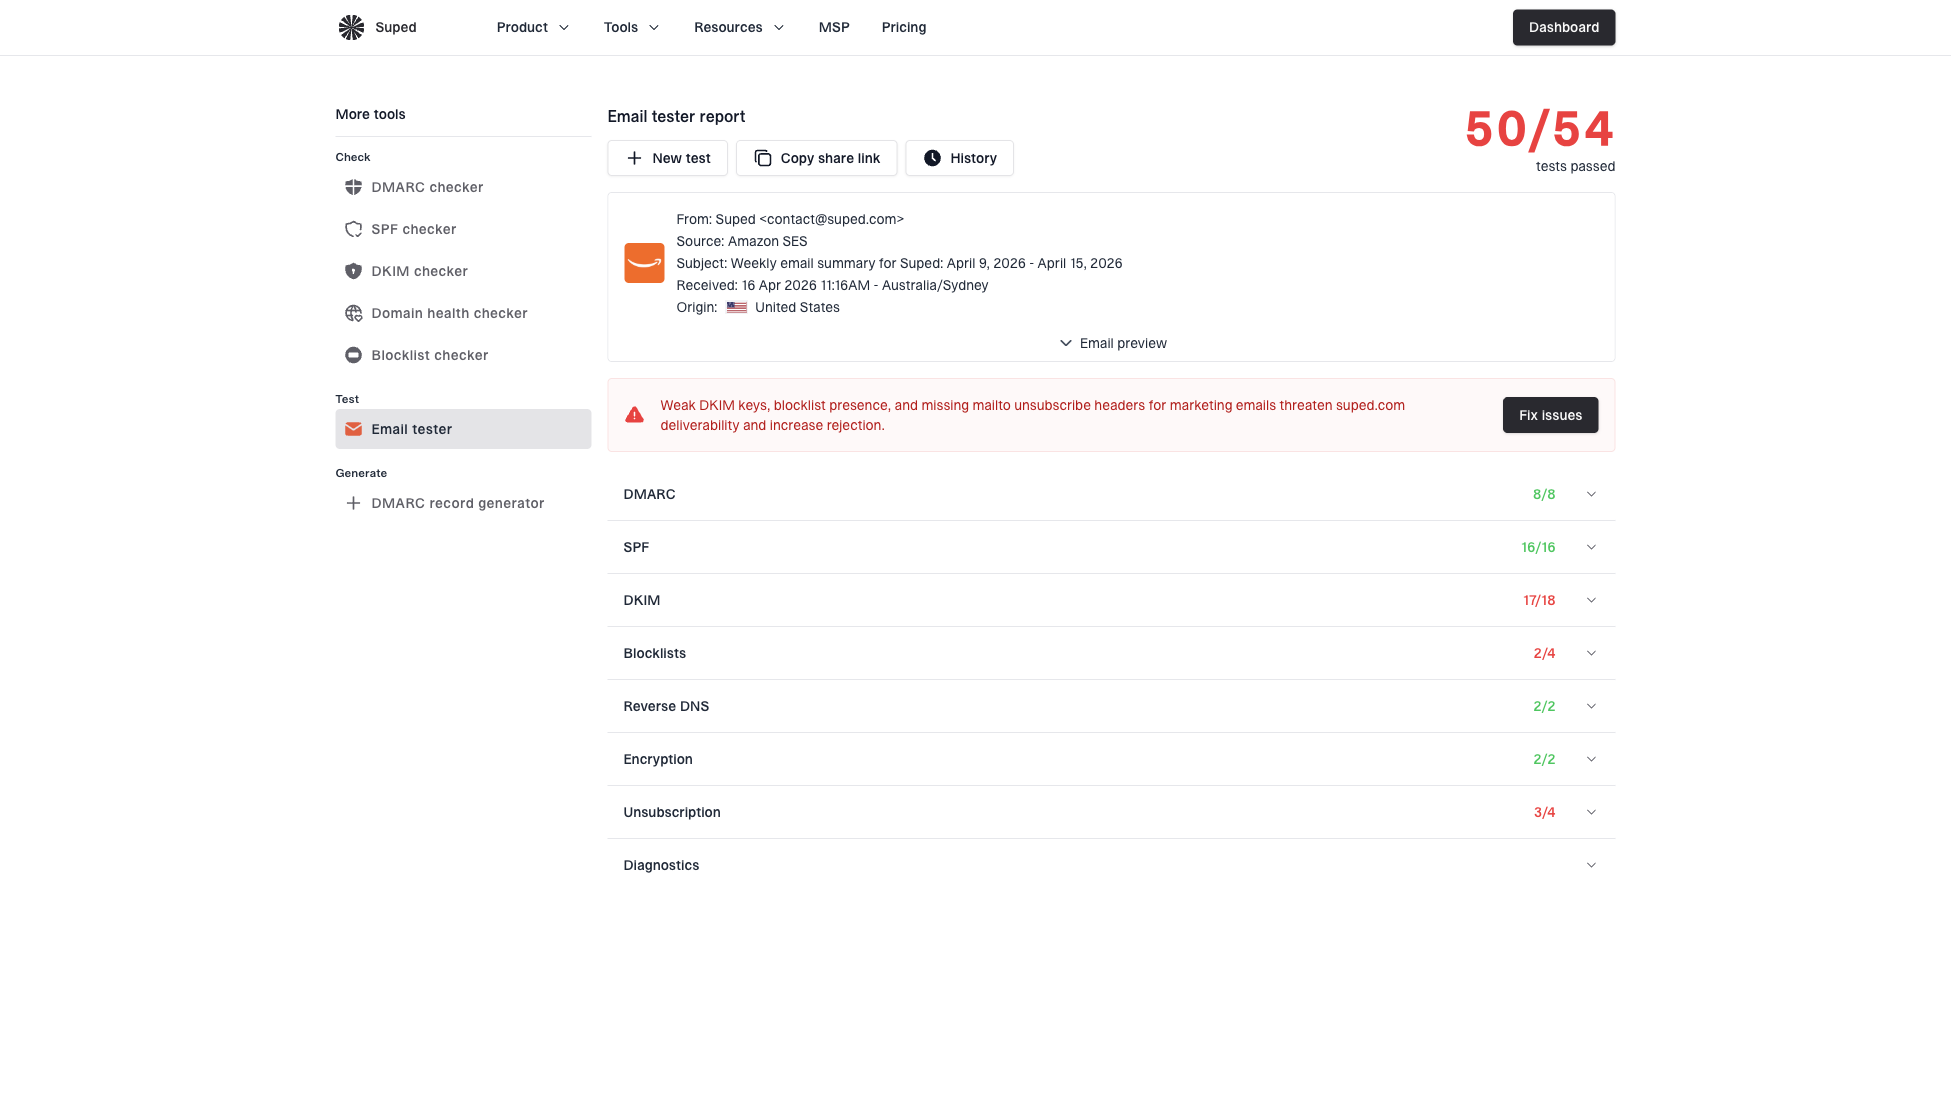
Email tester sample report showing total score, email preview, issue summary, and per-section results
Compare the decoded HTML from your test mailbox with the saved template. Suped's technical report helps investigate authentication and sending setup. Assess inbox placement separately at the mailbox providers your recipients use; the email tester does not run a multi-provider inbox test or a spam-content scoring engine.
- Send source: Use the same ESP, audience settings, tracking configuration, and link rewriting used in production.
- Open raw: Save the original .eml file without forwarding it. Locate the multipart/alternative structure if present, then isolate and decode the text/html part.
- Compare links: Confirm each intended link has a valid attribute and an expected destination domain.
- Compare parts: Check that the HTML and plain-text alternatives contain consistent destinations.
- Retest send: Fix the source, send again through the same path, and verify the decoded links. If the warning remains, compare its exact rule with the received source.
Email tester
Send a real email to this address. Suped shows a results button when the test is ready.
?/43tests passed
A cleared warning does not prove inbox delivery. Check actual inbox or junk placement and review SMTP responses or bounce logs for rejection evidence. If delivery remains weak, investigate authentication, reputation, sending volume, complaints, engagement, and mailbox-provider feedback.
How to fix the template
Put the URL in the attribute that matches its job. Use an anchor for a clickable text link and an image source for an image. For form submissions, link to an HTTPS page instead of relying on a form inside the email, because client support is inconsistent.
Patterns to avoid
- Bare link: A raw URL placed in an HTML paragraph.
- Split tag: An attribute damaged by unsafe templating or invalid quoted-printable wrapping.
- Hidden mismatch: Visible text implies one domain while the target uses another.
Patterns to use
- Anchor link: A clear href with concise visible text.
- Visible URL: Anchor the URL text if the full address must be shown.
- Tracked link: Let the ESP rewrite a valid anchor instead of guessing from text.
Safer HTML link patternshtml
<p>
  <a href="https://www.example.com/offer">
    View the offer
  </a>
</p>

<p>
  <a href="https://www.example.com/offer">
    https://www.example.com/offer
  </a>
</p>

<img src="https://www.example.com/image.png" alt="Product image">
Keep MIME transfer encoding separate from HTML entity escaping and URL percent-encoding. A query separator is written as & in HTML, while an equals sign becomes =3D only when quoted-printable encoding is applied. Percent-encoding uses % escapes inside a URL. Write ordinary HTML in the template and let the ESP apply the transfer encoding.
Avoid "click here" when the surrounding copy can name the action clearly, but treat that as a usability and trust choice rather than a deliverability rule. The stronger technical requirement is that the destination sits in valid markup that survives the ESP's final processing.
Use a simple acceptance test: after the HTML part is decoded from quoted-printable, every intended link should be obvious to a reader and parsable by a machine. If the decoded output requires guesswork, clean up the template or MIME generation.
- Human test: The visible copy tells the reader what happens next.
- Machine test: The target URL appears in a valid HTML attribute.
- Source test: The delivered MIME preserves the template's intent after decoding.
Where authentication fits
Template warnings attract attention because they point to concrete source text. Authentication and reputation usually have more delivery impact. DMARC can pass through either aligned SPF or aligned DKIM, so investigate alignment when neither path validates the domain in the visible From header. Bare-link cleanup cannot fix that failure.
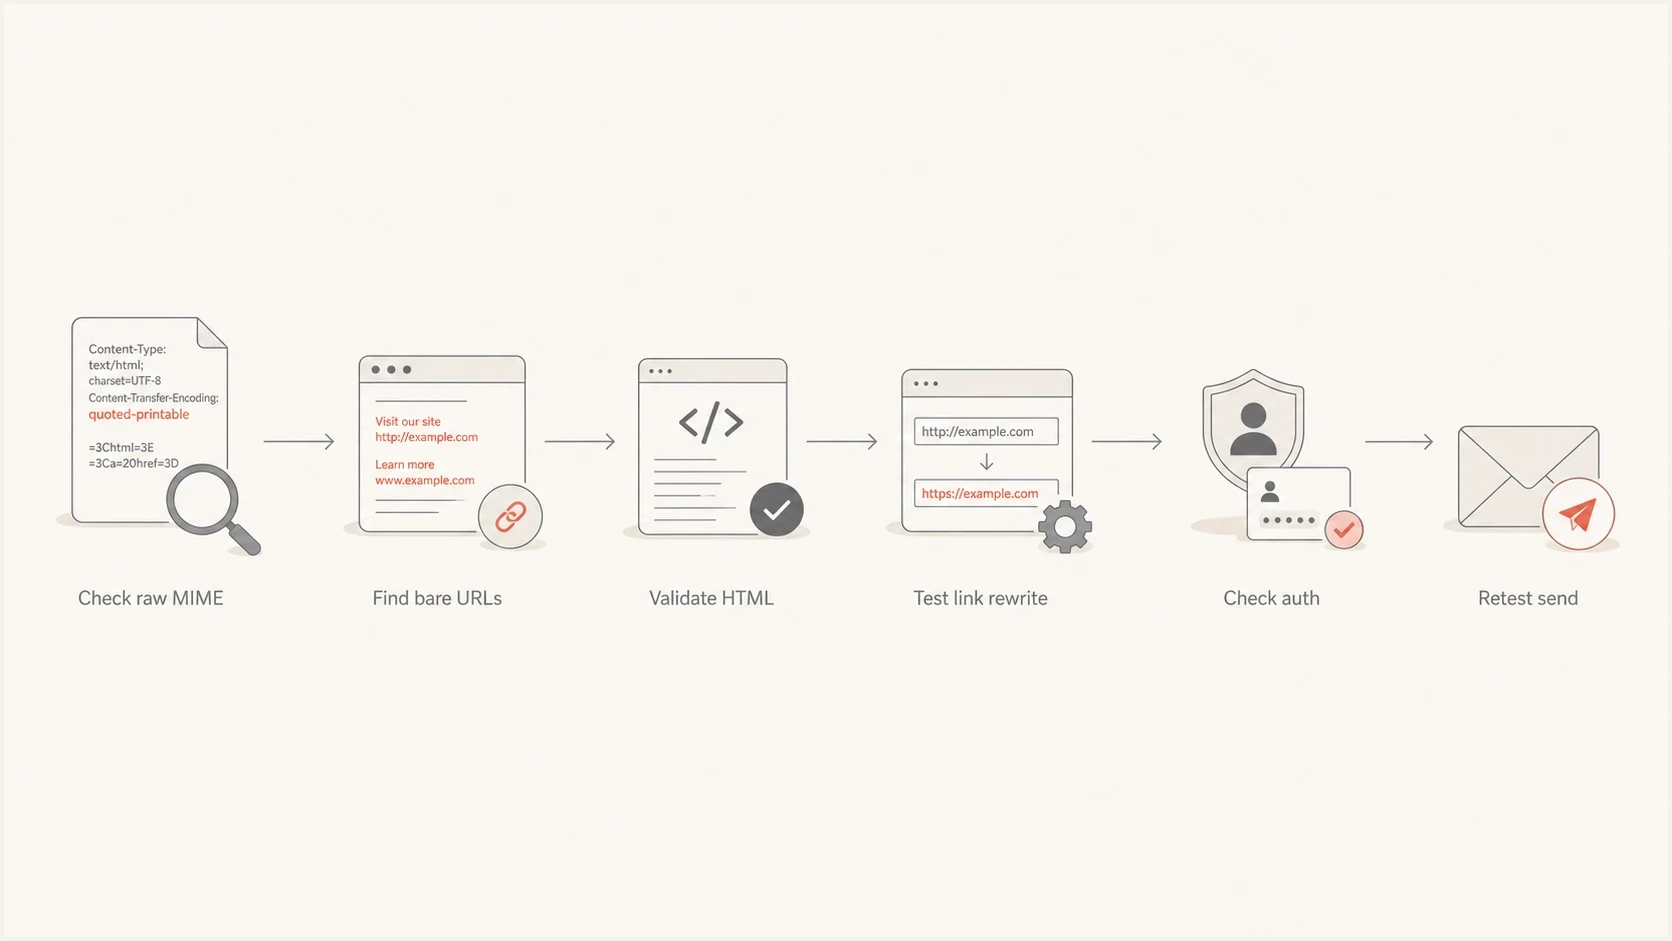
Triage steps for quoted-printable HTML link warnings and email authentication.
Suped's DMARC monitoring groups aggregate reports by sending source and shows SPF and DKIM alignment results. Compare those results with the received MIME. Aggregate reports do not include the email body or show inbox placement, so inspect content separately. Use Suped's blocklist monitoring for blocklist (blacklist) checks alongside that authentication evidence.
Apply tracking rewrites and MIME encoding before DKIM signing. RFC 6376 requires hashing the encoded body. Rewriting a URL or re-encoding a signed body afterward can invalidate its signature, even when the decoded content looks unchanged.
Views from the trenches
Best practices
Wrap visible URLs in anchor tags so scanners and mail clients see the same link target.
Inspect the raw MIME after the ESP sends, because editors can change generated markup.
Retest one seeded send after fixing templates, not only the saved design preview or editor.
Common pitfalls
Assuming the template editor output equals the final encoded MIME that subscribers receive.
Treating bare URL text as the root cause before checking authentication and reputation data.
Letting tracking rewrite links after encoding without checking final HTML validity in raw mail.
Expert tips
Keep a pre-send test inbox and archive raw source for every template family you ship.
Use one canonical link pattern across modules so audits find deviations quickly during QA.
When a mailbox provider flags a pattern, ask for raw examples before changing strategy.
Marketer view
Marketer from Email Geeks says a URL written as plain text in HTML usually does not cause a delivery problem by itself, because mail clients often make it clickable.
2022-04-08 - Email Geeks
Marketer view
Marketer from Email Geeks says the cleaner fix is to use the editor's link control, so the final HTML has a proper anchor instead of relying on client auto-linking.
2022-04-08 - Email Geeks