How can I resolve Microsoft Outlook S3140 errors blocking my transactional emails?
Updated on 7 Oct 2026: We clarified S3140 support routing, shared-IP ownership, and recovery for blocked transactional mail.
To resolve Microsoft Outlook S3140 errors, capture the full bounce, verify the sending IP, DNS, authentication, volume, and message stream, then submit a short mitigation request through the support path named by the receiving host. Because S3140 can affect an IP range, include proof of control when you administer the address space and involve the operator of the outbound sending network.
S3140 is not fixed by changing one DNS record. It is usually an Outlook.com policy block against part of the sending network, so a clean individual IP or public blacklist result does not rule it out. Treat the incident as a case file: remove every technical objection, document Microsoft-side reputation signals when available, request mitigation, and keep affected transactional mail moving through another clean route during review.
- Direct fix: Open or continue the correct Microsoft sender-support case and ask for mitigation of the exact sending IP, with a range review when appropriate.
- Evidence needed: Include the full NDR, receiving host, authentication results, FCrDNS, public blocklist results, volume, message type, and IP control evidence when available.
- Operational backup: Route affected Microsoft consumer mail through an established, authenticated sending route with capacity for the additional traffic.
What the S3140 error means
A Microsoft Outlook S3140 rejection means Microsoft has blocked mail from the sending IP or a range containing it. The bounce does not identify the exact size of the blocked range. It often appears as a 550 5.7.1 policy rejection with a diagnostic code containing S3140. A clean public blocklist (blacklist) result does not rule out an internal Microsoft reputation block.
Support replies can be generic. A statement that users are receiving unwanted mail does not prove that the current transactional stream generated complaints, especially when recent messages were rejected before acceptance. Ask for review of the sending IP and attach the full SMTP rejection rather than assuming the reply identifies the responsible message stream.
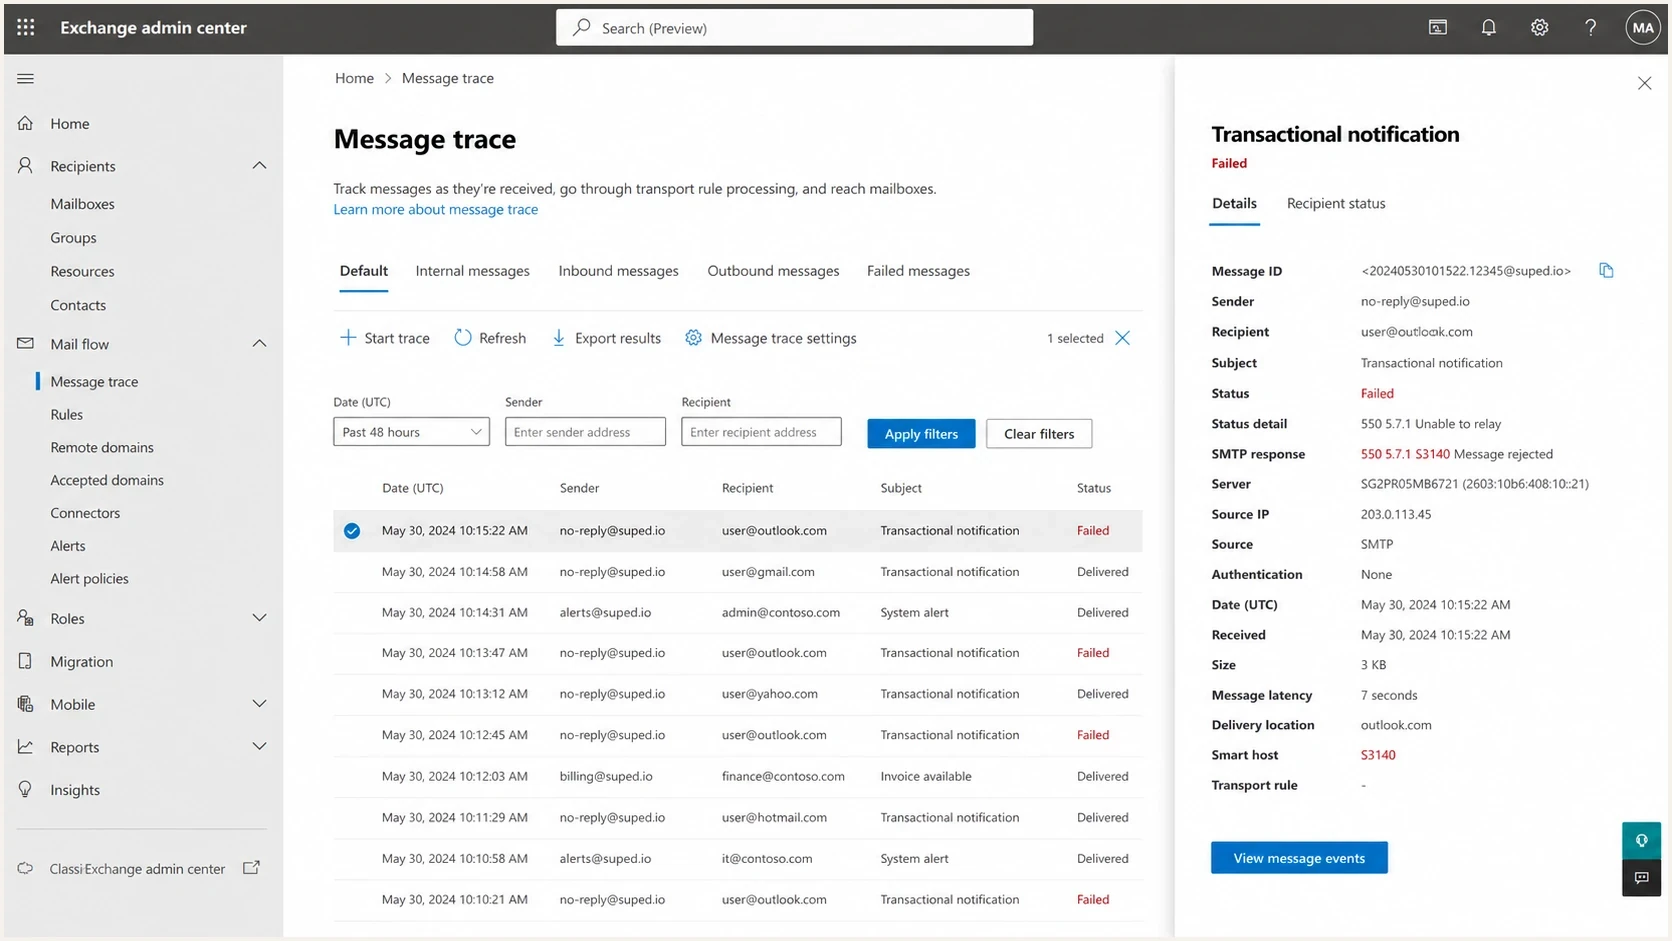
Microsoft Exchange admin center message trace illustrating an S3140 email rejection.
Do not treat S3140 as a normal DNS failure
Validate authentication and reverse DNS, but valid records do not force Microsoft to accept a blocked IP. Once S3140 is active, address reputation causes and request mitigation through the correct support channel.
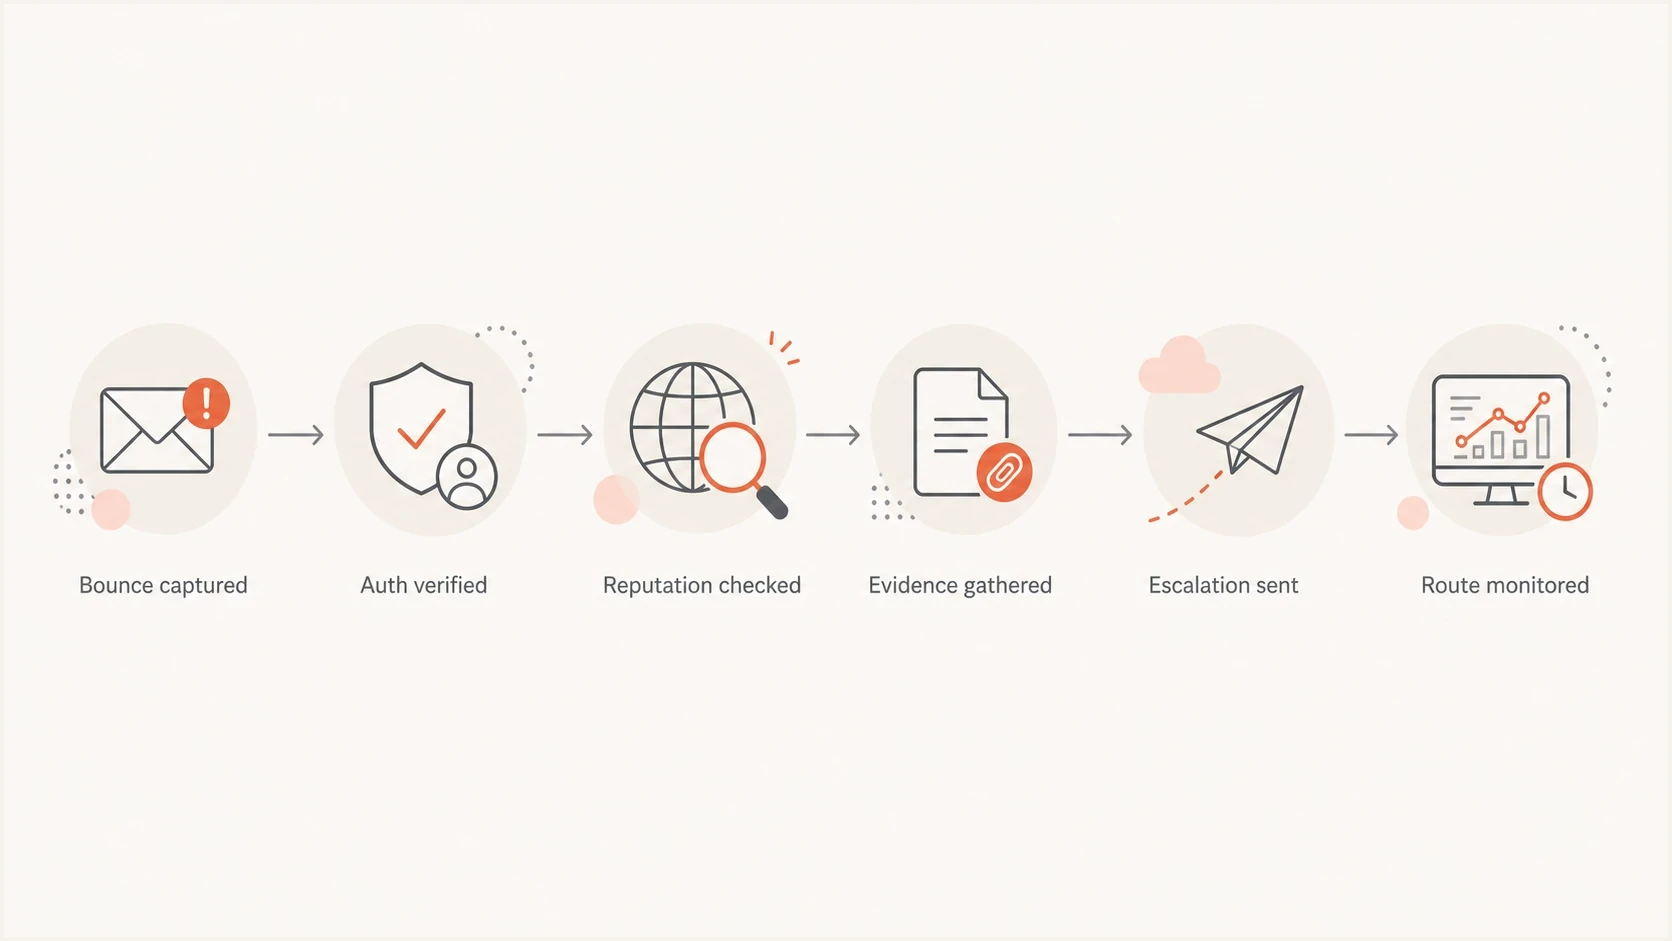
Steps to resolve Outlook.com S3140 email blocks, including authentication checks and escalation.
Confirm the block before changing infrastructure
Before changing IPs, isolate the failure. Pull a raw bounce from the mail server or ESP logs and confirm the recipient domain, receiving host, source IP, SMTP response, date, and message stream. Keep one clean example that proves Microsoft rejected the message during SMTP and that the same mail stream works elsewhere. Capture the timestamp in UTC and the SMTP stage (MAIL FROM, RCPT TO, or DATA) so support can match the event to its logs.
Illustrative S3140 bounce with an example IPtext
Remote server returned '550 5.7.1 Unfortunately, messages from
[203.0.113.24] weren't sent. Please contact your Internet service
provider since part of their network is on our block list (S3140).'
Then check whether the issue affects only Microsoft consumer domains or also Microsoft 365 tenants. A receiving host containing olc.protection.outlook.com points to the Outlook.com consumer path, while a Microsoft 365 tenant rejection can name a different delisting route in the NDR. Outlook.com, Hotmail, Live, and MSN mail can behave differently from business tenants, so choose the support route from the full bounce rather than the recipient brand alone.
|
|
|
|---|---|---|
Bounce | Full NDR, host, UTC timestamp, and SMTP stage | Proves S3140 and route |
IP | Outbound SMTP IP and provider range, if known | Scopes network review |
Stream | Transactional message type and sending source | Reduces ambiguity |
Volume | Daily count and trend | Shows stable sending |
Use compact evidence so support can review the ticket quickly.
For a broader check before escalating, run the domain through Suped's domain health check and save the results with the ticket notes. The goal is to remove easy technical reasons for support to close the case.
?
What's your domain score?
Deep-scan SPF, DKIM & DMARC records for email deliverability and security issues.
Identify who controls the blocked sending IP
The IP quoted in the bounce is the address that connected to Microsoft. It is not necessarily your application server or inbound MX address. When an application uses an email service provider (ESP), the network operator is the provider handling outbound SMTP. This distinction is explained in Microsoft's S3140 discussion.
- For a self-managed mail server, confirm its public outbound IP, including any NAT gateway, and involve the hosting provider that controls the range.
- For a shared IP pool, send the email provider the blocked IP, full NDR, UTC timestamps, and message identifiers. Ask it to investigate the pool and submit the mitigation request.
- For intermittent failures, group accepted and rejected attempts by sending IP. A rotating pool can explain why the same transactional stream sometimes succeeds.
- Keep transactional and marketing traffic in separate sending streams or pools where appropriate. This reduces shared reputation exposure, but a wider network block can still affect both.
A dedicated IP is not an automatic fix. It needs warmup and enough consistent traffic to establish reputation. For a low-volume application, an established provider-managed pool is an option to discuss with the provider before buying an IP. Microsoft explains the reputation limits of new IPs in its sender support guidance.
Check authentication and SMTP server configuration
When a support reply says to review Outlook.com technical standards, respond with a numbered compliance summary. Keep it factual. Avoid long explanations, speculation, and screenshots unless asked. The strongest response is a short list that shows each requirement has been checked.
- SPF alignment: The envelope sender domain authorizes the sending IP. When SPF supplies the DMARC pass, that domain must match the visible From domain under the published DMARC alignment mode.
- DKIM alignment: Transactional messages have a valid signature. When DKIM supplies the DMARC pass, the signing domain must match the visible From domain under the published DMARC alignment mode.
- DMARC pass: At least one aligned SPF or DKIM result passes for the domain in the visible From header.
- FCrDNS: The IP has reverse DNS, and that public hostname resolves forward to the same sending IP.
- Message type: The traffic is solicited transactional mail such as password resets, account confirmations, receipts, or security notices. Review product notifications separately if they contain promotional content.
- HELO/EHLO: The SMTP server identifies itself with a valid public hostname rather than a private IP address. Check this alongside PTR and forward DNS.
- Server security: Confirm the server is not an open relay. Review outbound logs for compromised accounts, abused application endpoints, or stolen SMTP credentials.
For domains sending 5,000 or more messages per day to Microsoft consumer services, check the high-volume sender requirements: SPF and DKIM must both pass, and DMARC must pass through at least one matching domain. A published DMARC policy of p=none meets the minimum policy requirement. Authentication enforcement also applies to high-volume transactional mail. The separate 550 5.7.515 authentication error needs an authentication correction; it should not be handled as an S3140 reputation block.
Example DMARC record for transactional maildns
_dmarc.example.com. 3600 IN TXT "v=DMARC1; p=none; rua=mailto:dmarc-reports@example.com"
This is a monitoring-policy example, not a delisting instruction. Replace the example domain and reporting mailbox with values you control, and use a reporting address that accepts aggregate reports. It leaves the default relaxed DMARC alignment in place; require strict matching only when every legitimate source supports it.
A one-click unsubscribe header is not generally expected for pure transactional mail like password resets and account confirmations. Separate notification mail carefully, because product notifications can drift into engagement or marketing territory. If a message promotes usage, nudges a dormant user, or contains broad product messaging, treat it more cautiously than a password reset.
DMARC record detail view showing SPF, DKIM, DMARC, rDNS diagnostics, and DNS records
Suped's DMARC reporting and email authentication platform helps review authentication by sending source. Record those findings alongside the S3140 support case. DMARC reports do not replace SMTP logs for messages rejected before message data is accepted.
Use Microsoft sender data and the correct support path
If you control the sending IP, request access in Microsoft's current Smart Network Data Services (SNDS) portal while opening the mitigation case. SNDS provides Outlook.com data for individual IPs and includes Junk Email Reporting Program (JMRP) settings for complaint reports. Neither program automatically removes S3140. Use the available data to identify causes and document cleanup, following Microsoft's SNDS documentation.
- Confirm IP control: Request access only for IPs or ranges you administer. Access expires 10 months after approval or migration unless ownership is reattested; check the expiry shown in Access Control.
- Compare recent signals: Compare the first S3140 timestamp with volume changes, complaint data, and available filtering results. Low-volume IPs can lack data, and SNDS is not a real-time delivery test.
- Process JMRP reports: Map each complaint to the responsible stream, stop unwanted mail of that type, and investigate any unexpected source.
- Escalate provider-owned space: If a hosting provider or email provider operates the range, send it the full NDR and timestamps. Ask it to investigate network abuse and coordinate mitigation with Microsoft.
Match support to the receiving system
For Outlook.com consumer S3140 bounces, use Outlook.com Delivery Support. For Microsoft 365 errors 550 5.7.606-649, follow the IP delist instructions in the NDR. For 550 5.7.511, follow the instruction to forward the full NDR to delist@microsoft.com instead. These are separate routes, as documented in Microsoft's delisting instructions. Registering for SNDS is not a prerequisite for opening an urgent delivery-support case.
Check IP and domain reputation before escalation
A public blocklist check does not fully explain Microsoft acceptance, but it still matters. Investigate relevant IP or domain listings and their causes separately from the S3140 case. A public blacklist listing is not proof that Microsoft uses that list or blocks the same range. Save each result with the lists checked and a timestamp.
For an ongoing process, use blocklist monitoring and repeat checks during warmup, provider migration, or a new netblock allocation. Reputation changes during these events, so save current results rather than relying on an old clean check.
Clean evidence
- Authentication: SPF, DKIM, and DMARC pass with aligned domains.
- DNS: Forward and reverse DNS identify the sending host.
- Reputation: No listing was found on the public blocklists checked at the recorded time.
Weak evidence
- Authentication: Only one sample message was tested, or DMARC alignment was not verified.
- DNS: Reverse DNS exists, but the hostname does not resolve to the sending IP.
- Reputation: Only one blacklist was checked, without a timestamp or saved results.
Suped's blocklist monitoring and DMARC reporting support the incident workflow. Watch for public listings and authentication failures, then record the findings alongside Microsoft-specific sender data and SMTP logs.
Blocklist checker
Check your domain or IP against 144 blocklists.





Send a short escalation that asks for the right action
The escalation wording matters. A long emotional reply gives support too much to skim past. Use a short list with one clear request: review the exact S3140 rejection and mitigate the affected sending IP or range. For newly assigned space, include the allocation evidence and explain the conservative ramp plan. Replace the bracketed fields below with verified facts and remove any claim you cannot support.
Escalation template for Microsoft S3140text
Hello,

Please review this S3140 case for mitigation of sending IP [IP].
Please review the affected range if a broader block applies.

The full NDR, receiving host, and UTC timestamps are attached.

1. SPF and DKIM results: [verified results].
2. DMARC result and matching domain: [verified result].
3. PTR, forward DNS, and HELO/EHLO: [verified values].
4. Our application sends solicited transactional mail.
   IP type: [shared/dedicated]; operator: [provider or owner].
5. Daily volume and recent changes: [count and summary].
6. Public blocklist checks: [lists, timestamp, and results].
7. SNDS findings: [summary, or unavailable and reason].
8. IP control or provider assignment: [evidence, if available].
9. Abuse investigation and fixes: [verified actions].

The rejection persists for Outlook.com consumer recipients.
Please re-evaluate the sending IP using this evidence.
If Microsoft asks for control or assignment proof, send the allocation record, invoice, or a provider letter that states the exact range, assignee name, and assignment date. Keep the full NDR and evidence attached to each reply, because a different support agent can handle the next response.
What to do after a denial
Reply in the same case with any new SNDS data, provider action, authentication correction, or abuse cleanup, then ask for re-evaluation of the exact IP. If the case closes, submit a fresh request only after the underlying evidence has changed. Repeated requests with identical evidence add no new information. Ask the network operator to investigate unresolved abuse or range-reputation issues.
After a mitigation acknowledgement, follow the waiting period stated in the reply and test with a small number of fresh transactional messages. Confirm SMTP acceptance rather than relying on the acknowledgement alone. If S3140 persists, reply with the new NDR, exact sending IP, and UTC timestamp. Microsoft discussions about S3140 blocks show how generic the wording can be. Do not argue with the wording itself. Keep the ticket focused on the facts Microsoft can use to approve mitigation.
Keep transactional mail flowing while Microsoft reviews
Do not let account confirmations and password resets sit behind a blocked route. If the mail is time-sensitive, route Microsoft consumer domains through an established, authenticated route with sufficient capacity while the S3140 ticket is open. Keep the network operator working on the underlying block while the fallback is active.
A 550 5.7.1 S3140 response is a permanent SMTP rejection. Stop automated retries against that blocked route; handle temporary 4xx deferrals separately with normal backoff. RFC 5321 distinguishes these response types. After mitigation or a verified route change, resend only still-relevant notifications. Generate fresh password-reset or magic-link messages if their tokens expired. Check whether the sending platform suppressed the recipient after the policy rejection, and restore sending only after validating the address and route.
- Route narrowly: Move only the affected Microsoft recipient domains if the block does not affect all destinations.
- Preserve identity: Authorize the fallback IP in SPF where required and verify DKIM, DMARC, envelope domains, and bounce handling before switching traffic.
- Watch volume: Pause routine sends to the blocked Microsoft route. After mitigation, use small controlled tests before gradually restoring volume.
- Measure recovery: Track S3140 counts, accepted mail, deferrals, and complaint signals after mitigation.
Sending posture during an S3140 case
Pause routine sending on the blocked route and verify acceptance before resuming volume.
Conservative
Pause, then test
Verify acceptance after mitigation
Risky
Sharp volume increases
Abrupt increases after delivery resumes
Critical
Stop rejected sends
Repeated S3140 rejections on the same route
If the same message delivers through a different IP, that supports a sending-path diagnosis but does not reveal the exact scope of the original block. It does not mean the original range should be abandoned. New IPs can inherit their own reputation problems, and buying a new block starts the same warmup and verification work again.
Know when to escalate, wait, or replace the IP
Decide whether to replace the IP after checking the sending path, provider response, and business impact. Keep pushing for mitigation when the sending configuration is correct and the provider has evidence of range cleanup or a recent assignment. Consider replacement when there is evidence of prior abuse, poor provider-network reputation, repeated refusal after the underlying causes have been addressed, or a business need that cannot wait.
|
|
|
|---|---|---|
New range | Escalate | Needs range review |
Clean auth | Keep case open | Fix is not DNS alone |
User impact | Reroute | Protects critical mail |
Bad range history | Replace | Limits repeated blocks |
Decision guide for S3140 remediation paths.
If the organization uses Microsoft 365, paid Microsoft support can document the impact and confirm whether the rejection belongs to the enterprise or consumer path. It does not replace the separate Outlook.com deliverability review, so keep the S3140 case with that sender-support channel.
If you are also seeing S3150, review the related S3150 bounce guidance. The handling can overlap, but the evidence and support path should match the exact diagnostic code and receiving host in the bounce.
Monitor authentication and S3140 delivery failures
Routine visibility helps detect authentication and reputation changes. Watch sending sources and volume alongside DNS and list quality. Microsoft can apply an internal block without a public blacklist warning, so alert on S3140 responses in SMTP logs as well.
Issues page showing top issues, verified sources, unverified sources, and authentication pass rates
Suped's DMARC reporting and email authentication platform supports source review and public blocklist monitoring during an S3140 incident. Record authentication results and listing changes alongside the support case. Use the mail server or provider's delivery logs to confirm whether Microsoft is accepting messages.
Use Suped's email tester to inspect a sample message, then monitor the production domain continuously. Sample tests diagnose authentication for the tested message; SMTP logs show whether the affected Microsoft route has recovered.
Views from the trenches
Best practices
Keep Microsoft replies short, factual, and focused on the exact mitigation request.
Attach ownership and assignment proof again when a different support agent replies.
Route urgent transactional mail through a clean path while the blocked range is reviewed.
Common pitfalls
Do not assume a clean public blacklist check means Microsoft has no private block.
Do not raise volume during a mitigation request, even when the sender feels confident.
Check provider remediation and a verified fallback before abandoning a newly assigned range.
Expert tips
Ask for review of the sending IP and its range when a newly assigned netblock is blocked.
Use the exact S3140 code in the ticket so the case stays tied to the bounce evidence.
Separate account security mail from product notifications when reviewing message risk.
Marketer view
Marketer from Email Geeks says persistence matters with Microsoft S3140 mitigation, and the request should use short bullet points with one clear ask.
2024-05-08 - Email Geeks
Marketer view
Marketer from Email Geeks says early support replies can miss the point, so the sender should keep asking for escalation and pre-emptive remediation.
2024-05-08 - Email Geeks
Frequently asked questions
No. S3140 is an internal Microsoft block on the sending IP or a range containing it. A clean public blocklist (blacklist) result does not rule it out, and the bounce does not reveal the exact blocked range.
Valid authentication removes configuration problems but does not guarantee removal of an internal reputation block. After correcting authentication and any abuse or reputation causes, request Microsoft mitigation for the affected IP through the appropriate support channel.
Pure transactional mail such as password resets and account confirmations generally does not need one-click unsubscribe. Product notifications need closer classification, so separate security-critical mail from engagement-style messages.
No. SNDS provides Microsoft reputation data for IPs you control, and JMRP provides junk complaint reports. Use those signals to fix the cause and support a mitigation request.
Replace it after checking range history, authentication, provider remediation, routing options, and Microsoft's support path. A clean newly assigned range with restrained transactional volume is worth escalating before replacement.