What causes Spamcop to block an IP address and how to resolve carrierzone issues?
Published 28 Apr 2025
Updated 7 Oct 2026
13 min read
Summarize with
Updated on 7 Oct 2026: We clarified SpamCop bounce handling and added steps for CarrierZone rejections that persist after delisting.
The SpamCop Blocking List (SCBL) lists an IP address when recent spam reports and spamtrap evidence, weighted against estimated traffic sampled through SCBL queries, cross its listing threshold. If a bounce says H:SC and names your sending IP alongside a SpamCop reference, treat it as an IP reputation incident first, not as proof that the recipient address is bad.
CarrierZone identifies the receiving-side routing context. If a recipient domain is hosted or filtered through CarrierZone and only some users bounce, that uneven behavior does not prove the domain is fake or every address is invalid. Different outbound IPs, delivery times, receiver routes, or cached blocklist (blacklist) results can produce mixed outcomes. Compare SMTP logs before assigning a cause.
The practical fix is to confirm the listed IP, stop the traffic source that caused the reports, identify who controls the IP, and keep monitoring after the listing clears. A simple blocklist monitoring workflow saves time because the issue can return if the underlying complaint, trap, or compromised source stays active.
Example SpamCop-style bouncetext
5.7.1 (delivery not authorized) smtp;
550 5.7.1 H:SC [192.64.237.171]
Connection refused due to abuse.
Please see spamcop.net/bl.shtml?192.64.237.171
or contact your E-mail provider.
What the bounce means
A 550 5.7.1 rejection with a SpamCop reference is a policy refusal at SMTP time. The receiving system rejected the connection because its filtering policy identified the connecting IP as listed. That differs from a mailbox not existing, a full mailbox, or a content rule firing after acceptance. A 550 is a permanent SMTP failure, even when the listing itself is short-lived. RFC 5321 distinguishes 5xx failures from retryable 4xx responses. Arrange a fresh, controlled send after remediation rather than relying on automatic retries.
This matters because bounce handling goes wrong when every 5xx response is treated as an address-quality problem. If six recipients at the same hosted domain produce mixed results, do not suppress all six because a few attempts returned a SpamCop rejection. First check whether the sending IP, sending stream, campaign, or property changed during the bounce window.
|
|
|
|---|---|---|
550 5.7.1 | Permanent SMTP policy rejection | Do not mark invalid |
H:SC | Receiver-specific marker | Confirm the SpamCop reference and IP |
IP shown | Connecting outbound or relay IP | Identify the IP owner |
CarrierZone | Receiver host | Compare MX records and SMTP hostname |
How to read common parts of the rejection
Do not convert this into an invalid-address bounce
A SpamCop rejection is about the sending IP at that moment. Hold further sends while you investigate, and arrange a controlled resend after remediation. Permanently suppress a confirmed nonexistent mailbox, an unsubscribe, a complaint, or an address without valid permission.
What causes SpamCop to list an IP
The SCBL is IP based. It weighs the volume and freshness of reports, gives added weight to spamtrap hits, and compares those signals with reputation points derived from sampled SCBL queries for non-reported traffic. The IP is the listed asset; a website URL or reply address mentioned in reported mail is not an SCBL listing target. See SpamCop's listing criteria.
- Spam reports: Recipients or SpamCop users report enough unwanted mail for the source IP to cross the listing threshold.
- Spamtraps: Mail sent to trap addresses carries extra weight and often points to harvested data, weak acquisition controls, or unsafe reactivation.
- Compromised systems: An infected device, stolen SMTP credentials, an insecure CGI or PHP script, or an abused relay or proxy can send reported mail through the IP.
- Misdirected bounces: Backscatter sent to a forged envelope sender (the SMTP MAIL FROM address) can reach SpamCop traps and count against the server. Misdirected autoresponders can also generate reports.
- Shared infrastructure: One customer, brand, property, or campaign can damage delivery for every sender using the same outbound IP.
- Repeat sending: Retries alone are not a listing criterion, but repeatedly sending the same unwanted traffic can generate fresh reports and extend the listing.
- Authentication and DNS: Broken SPF, DKIM, DMARC, rDNS, or HELO identity can hurt delivery elsewhere, but SpamCop does not list an IP merely for those configuration problems.
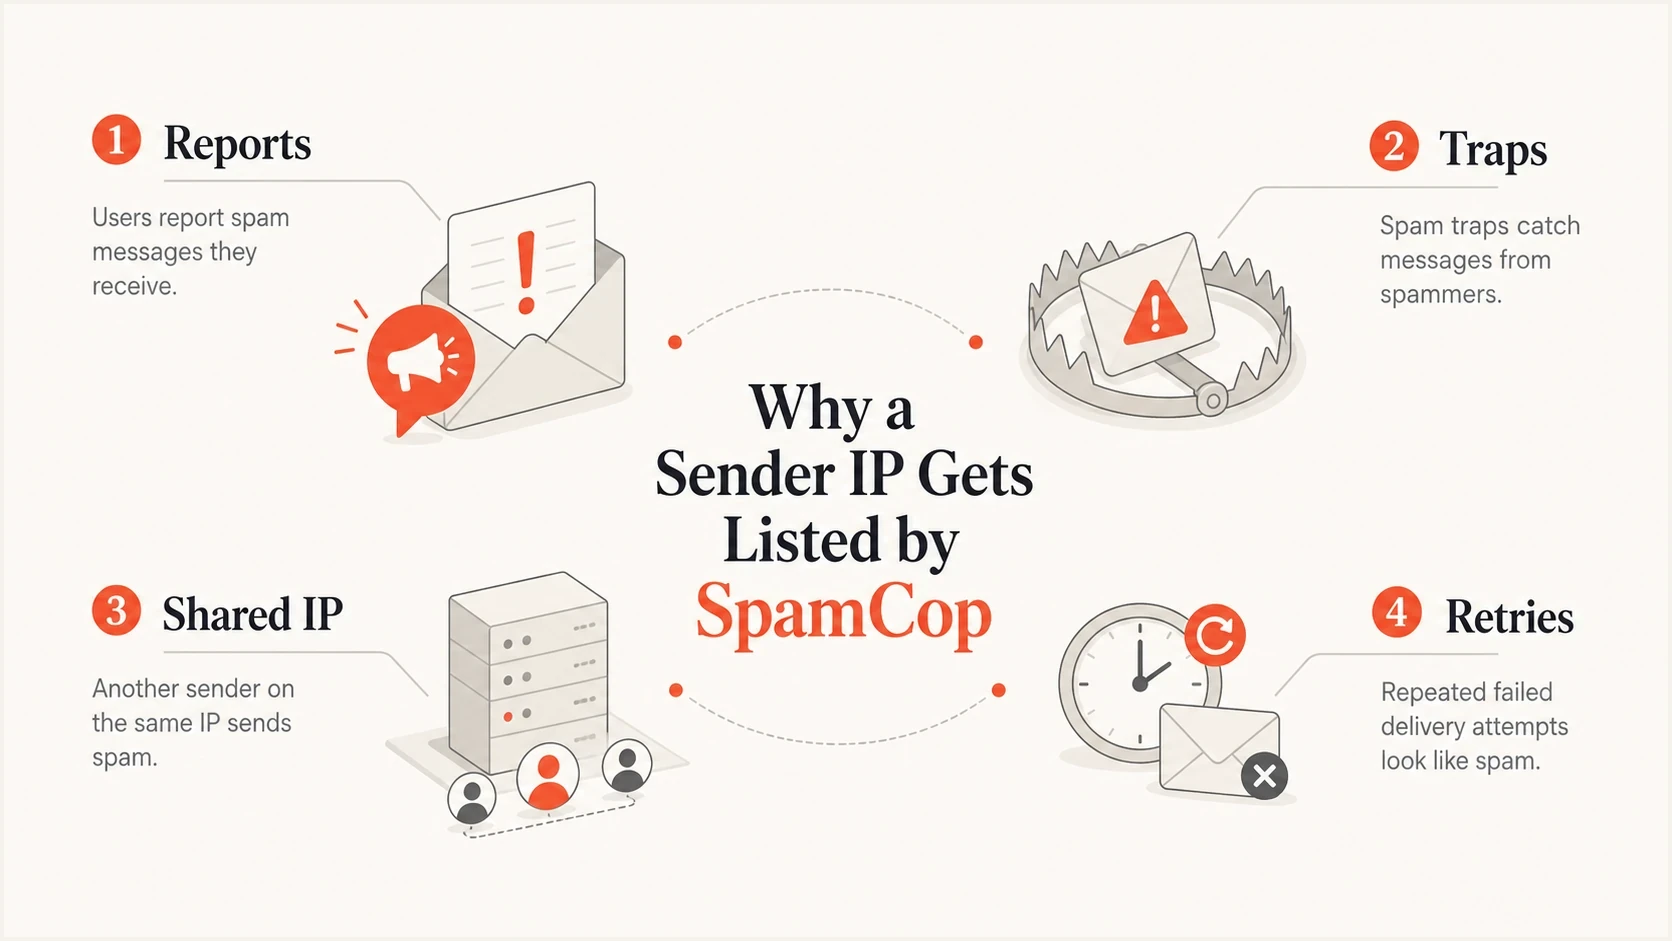
SpamCop listing signals and shared IP risks, with retries that continue reported traffic.
To avoid guessing, compare the bounce window with send and security logs. Check the exact IP in the bounce, recipient domain, campaign, account, property, list segment, and recent changes to scripts or SMTP credentials. If only CarrierZone-hosted recipients bounced, confirm the SpamCop reference in their SMTP rejections before attributing the difference to that receiver. Compare outbound IPs and receiving hosts for affected and unaffected attempts.
How CarrierZone changes the investigation
CarrierZone mail infrastructure can handle delivery for domains whose email service is sold through another hosting provider. A domain can be real, have a few engaged users, and still produce inconsistent bounces if delivery attempts land during a SpamCop listing window.
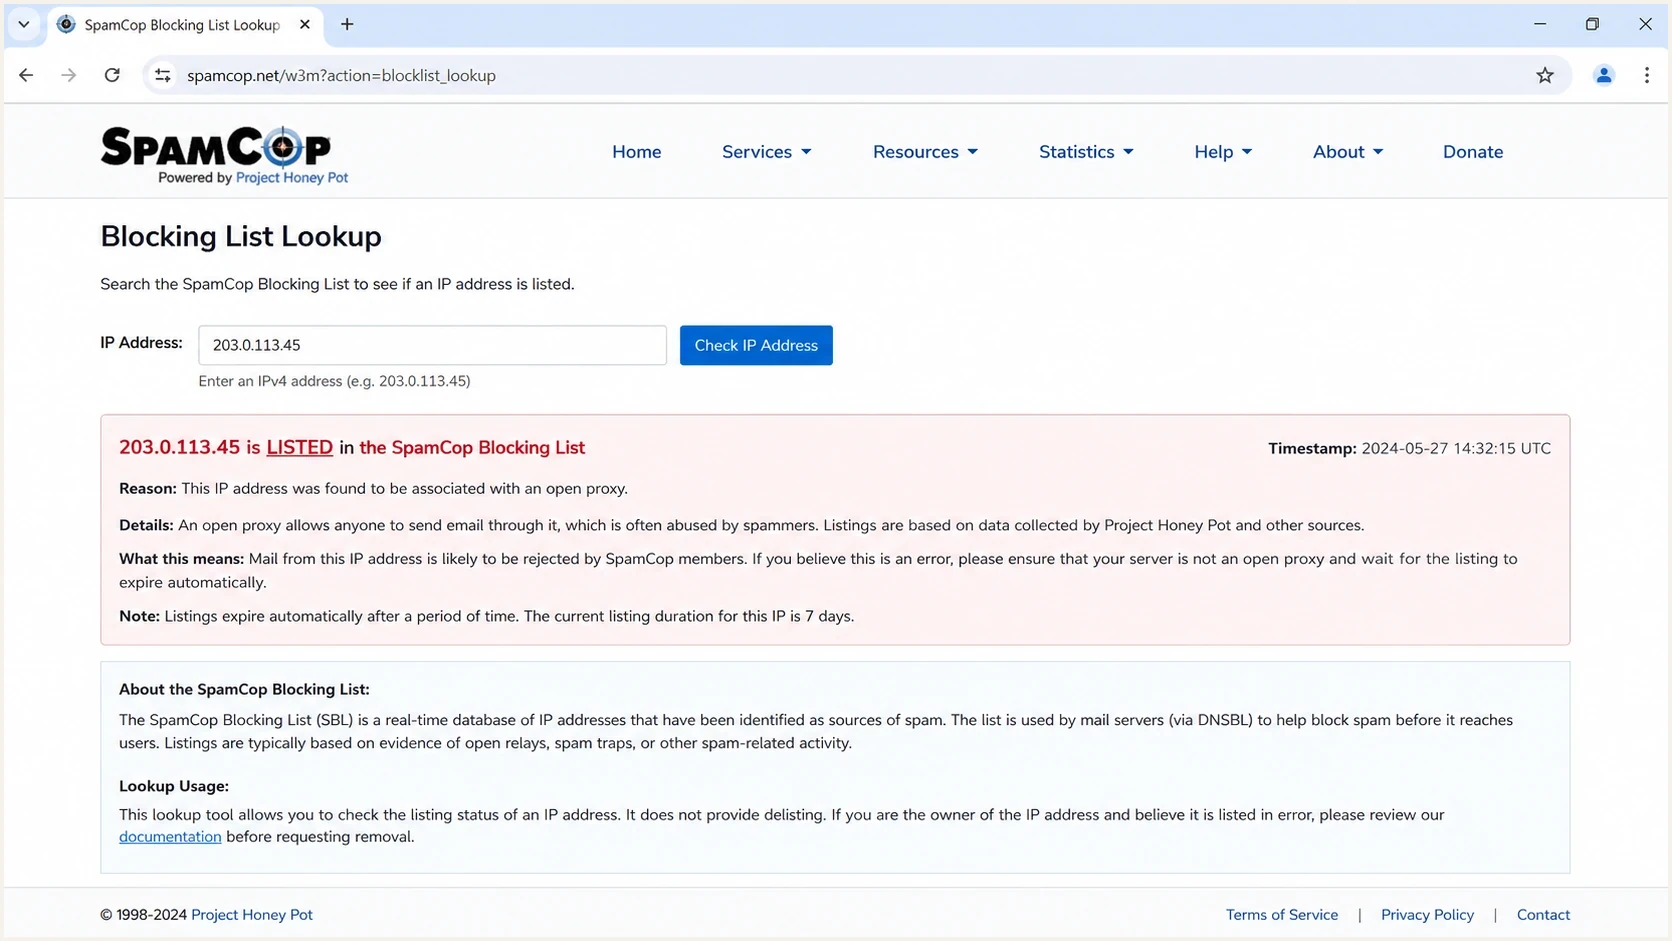
Illustration of a SpamCop IP listing status lookup for a CarrierZone email rejection.
Separate two questions. First, is the recipient domain valid? Second, is the sending IP being refused by a receiver that uses SpamCop? When the rejection names the sending IP, the second question matters more. The address can still be valid even when the message is rejected.
What CarrierZone tells you
- Provider clue: CarrierZone MX records or receiving hostnames identify the mail infrastructure used for that delivery attempt.
- Uneven bounces: Compare timestamps and connecting IPs to establish whether recipients encountered the same listing window.
- Receiver policy: That route rejected the connection using SpamCop data at the recorded time.
What it does not prove
- Bad address: A SpamCop policy bounce does not prove the mailbox is invalid.
- Fake domain: A low-volume or odd-looking domain can still belong to real users.
- Content-only issue: The named IP in the bounce keeps the investigation at IP level.
How to resolve a SpamCop IP block
Treat the incident as an IP reputation event, then tighten bounce handling so a temporary policy block does not cause permanent subscriber loss. The party that controls the outbound IP has to stop the source of the reported mail.
- Confirm the IP: Use the connecting IP shown in the bounce, not the visible From address, recipient domain, or return-path domain alone. If the IP is missing, ask your mail provider for the outbound SMTP log.
- Identify the owner: If the IP belongs to your mail provider or a shared pool, send the full bounce and timestamp to that provider. A tenant cannot directly remediate infrastructure it does not control.
- Stop the source: Pause traffic without verified permission, inspect compromised accounts and devices, rotate exposed SMTP credentials, audit web scripts, and disable misdirected autoresponders. Reject undeliverable inbound mail during SMTP instead of accepting it and generating backscatter.
- Preserve the evidence: Keep the complete SMTP rejection, UTC timestamp, receiving hostname, message ID, campaign, sending account, and any SpamCop report link available to the IP administrator.
- Separate sending streams: If the IP is shared across your own brands or properties, isolate the stream that created the reports before resuming full volume.
- Review authentication: Verify SPF, DKIM, DMARC, rDNS, and HELO identity as separate sender hygiene checks. Correcting them does not itself remove an SCBL listing.
- Resume carefully: After the listing and mirror results clear, restart with engaged recipients and watch bounces by provider before expanding volume.
Blocklist checker
Check your domain or IP against 144 blocklists.





A public lookup is one checkpoint. Also review other relevant blocklists (blacklists) and correlate their status with SMTP results. If several receivers reject the same IP at the same time, the problem is wider than CarrierZone.
Early delisting is not the fix
SpamCop listings are reactive and normally clear after new reports stop. If the same traffic resumes unchanged, the IP can be listed again. The fix is to remove the source, correct list acquisition or account security, segment risky traffic, and control retry behavior.
A suspected technical error or mistaken user report is different from an early removal request. SpamCop's dispute guidance asks the IP administrator to identify their relationship to the IP and use a postmaster or abuse role account. To challenge a specific report, include its complete subject and supporting evidence, such as a double opt-in confirmation. Responding to an abuse report documents your action; verify the IP's SCBL status separately.
How SpamCop automatic delisting works
The SCBL is time-based. An IP automatically delists after 24 hours with no new spam reports. If only two reports caused the listing, SpamCop documents a maximum listing period of 12 hours after the most recent reported message was sent. A new qualifying report can extend the incident, so waiting without stopping the source is not a resolution. These timings are documented in SpamCop's SCBL rules.
Allow time for mirror propagation
A lookup showing zero time remaining means the IP has entered the delisting process. SpamCop says removal can take up to four additional hours to reach its mirrors and blocklist users. Check again before a controlled resend; a message rejected with 550 generally does not remain queued for automatic delivery. See SpamCop's propagation guidance.
- Do not ask for early delisting as the first step. Stop the reported traffic and let the automatic process run.
- Use listing history as context, not proof that the current IP owner caused an earlier incident. IP addresses can change owners.
- Escalate through the provider when the listed IP belongs to hosted or shared mail infrastructure.
- Investigate recurring listings as evidence that reported mail or spamtrap traffic is still leaving the IP.
When CarrierZone still rejects mail after delisting
A clear SpamCop result shows current status, not the status when an earlier message bounced. Compare UTC timestamps, allow the documented propagation interval, then capture one fresh delivery attempt after the reported traffic has stopped.
- Confirm the new rejection's connecting IP. Shared pools and forwarding relays can use a different IP than the one previously checked.
- Compare the recipient domain's MX records with the receiving hostname in the SMTP log to establish whether CarrierZone handled the rejected connection.
- Read the complete new rejection. A different policy code or blacklist name needs its own investigation.
- If the same IP is clear beyond the propagation interval but the SpamCop rejection persists, ask the recipient to escalate through their hosting provider. Supply the bounce, UTC time, connecting IP, receiving hostname, and current listing status. Ask the provider to review cached SCBL results and local filtering policy.
SpamCop supplies list data, while the receiving administrator chooses how to use it. SpamCop's SCBL guidance recommends scoring and allowlisting wanted senders. The recipient administrator can assess a narrowly scoped exception after the sender has resolved the cause.
Monitor SpamCop incidents with Suped
Suped's product connects blocklist monitoring with DMARC source data, sender identity checks, DNS issue tracking, and alerts. For a SpamCop incident, use those workflows to record the affected IP, watch listing status, compare the incident with authenticated sending sources, and keep each domain or client attached to the correct remediation work.
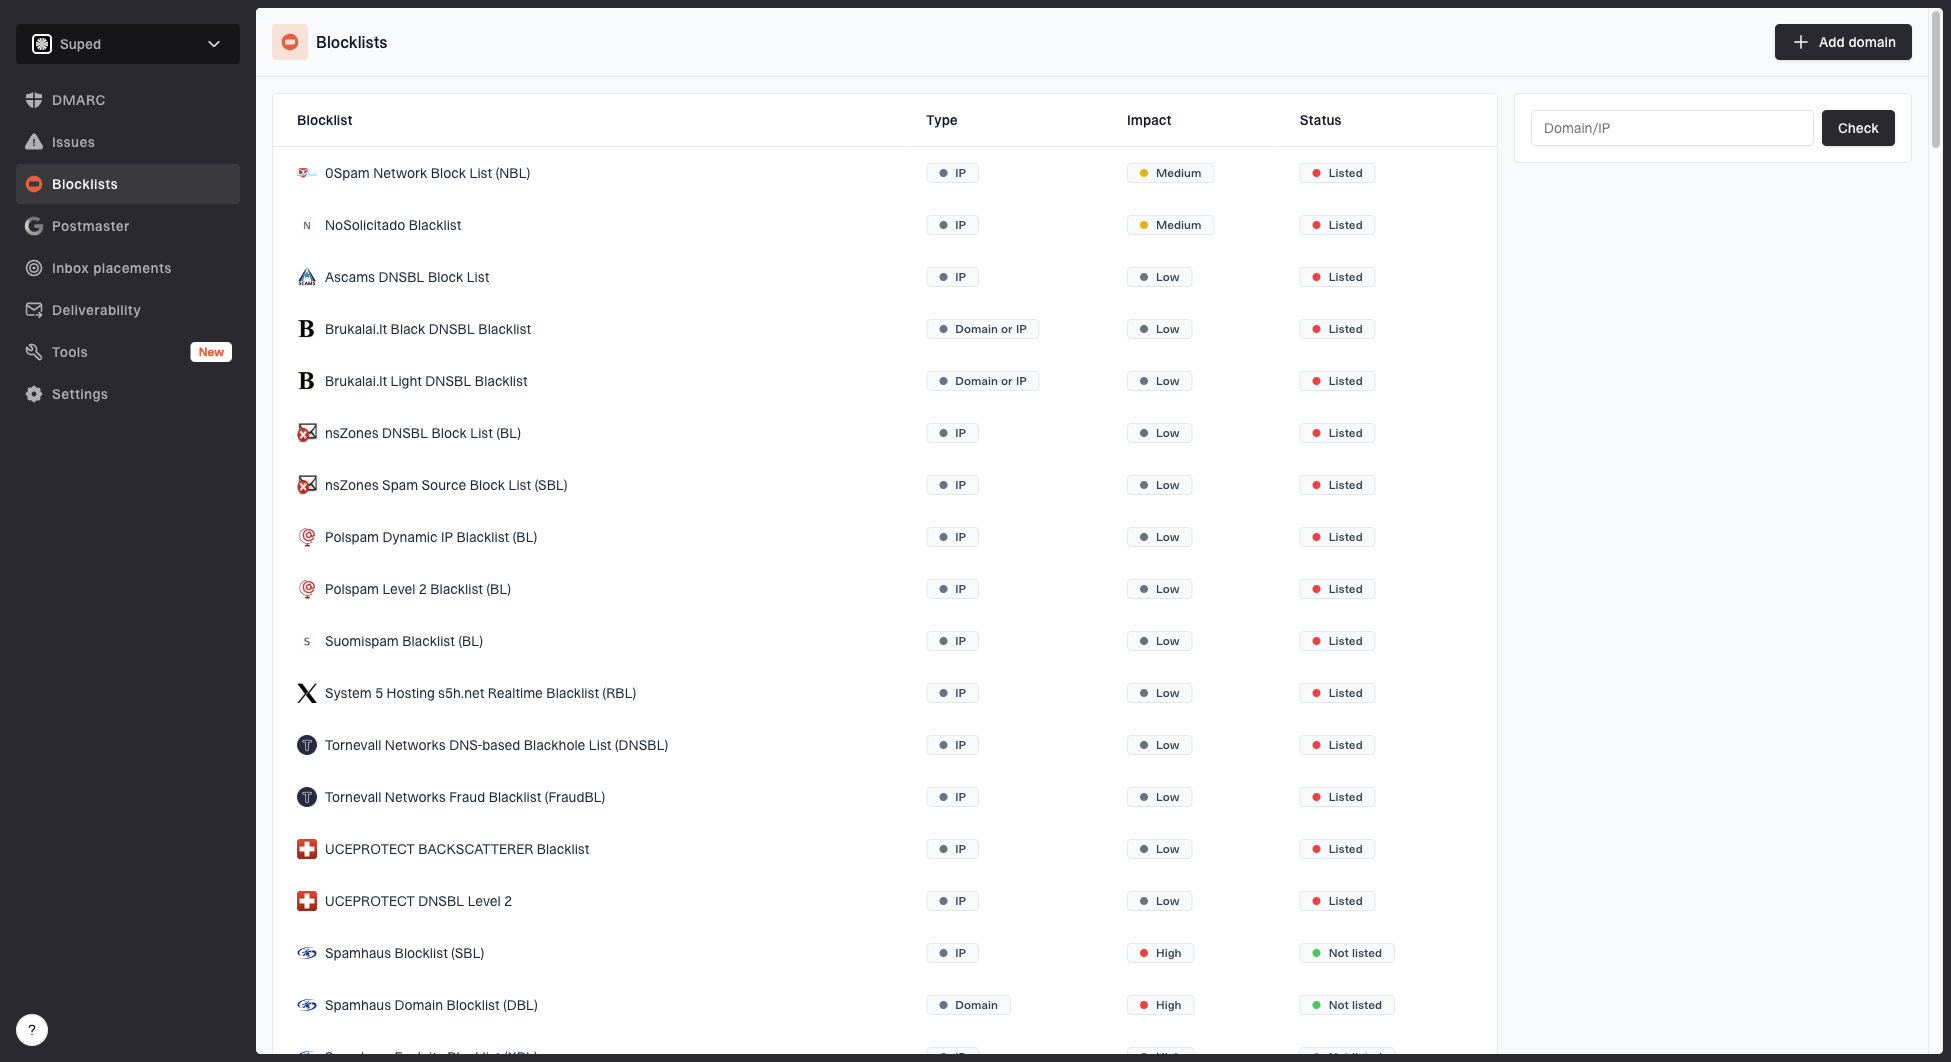
Blocklist monitoring page showing domain and IP checks across blocklists with importance and status
A practical Suped workflow is to confirm the IP in blocklist monitoring, review DMARC data for active sending sources, and use issue detection to separate authentication problems from the SpamCop trigger. A domain health check provides a DNS baseline for SPF, DKIM, and DMARC. Check the sending IP's reverse DNS separately with its provider. DMARC aggregate reports show traffic reported by participating receivers; they do not identify which message triggered a SpamCop report. Messages rejected before SMTP DATA are absent from these reports, as RFC 9989 explains.
|
|
|
|---|---|---|
Listed IP | Blocklist monitoring | Track status |
Sending source | DMARC source data | Correlate reported sending IPs |
DNS concern | Issue detection | Separate the fix |
Multiple domains | Domain views | Separate incidents |
How to map the investigation into Suped workflows
For teams managing multiple domains, keep the sending IP, source, authentication findings, and alert history attached to one incident record. That makes it easier to see whether the blacklist event cleared or moved to another shared IP.
When to keep or suppress the addresses
A CarrierZone-hosted domain with a small number of recipients deserves careful handling. If some recipients had prior engagement and bounced only during a known SpamCop window, keep them out of permanent suppression. Mark the event as an IP policy block and arrange a controlled resend only after the IP and its mirrors have cleared and the risky source has been stopped.
Suppression decision bands
Use the SMTP reason and engagement history before removing addresses.
Keep
Retain address
Permissioned address with a policy rejection tied to a listed IP.
Hold
Review
Policy rejections during an active SCBL listing.
Suppress
Remove
Confirmed nonexistent mailbox, unsubscribe, complaint, or no valid permission.
For dedicated IPs, ownership is clearer. For shared IPs, even when the sharing is only across your own properties, isolate the stream that changed. The same investigation applies to dedicated IPs when complaint or trap signals build up.
Avoid repeated delivery attempts into the same domain while the listing is active. Retries that resend unwanted traffic can create new reports, and retries during mirror propagation can produce more policy bounces. A controlled retry after the IP is clear gives a cleaner result.
Views from the trenches
Best practices
Treat SpamCop bounces as IP-level evidence before judging any recipient address as invalid.
Segment sends by property so complaint bursts do not hide inside shared IP traffic during review.
Keep bounce samples with timestamps, sending IPs, domains, campaigns, and provider names.
Pause reported traffic and verify automatic delisting before arranging any controlled resend.
Common pitfalls
Suppressing engaged addresses after one policy bounce removes valid users for the wrong reason.
Assuming CarrierZone will fix the issue ignores that the listed asset is the sender IP.
Waiting for automatic delisting without stopping the source causes the listing to return.
Mixing properties on one IP makes it harder to identify which audience created reports.
Expert tips
Compare affected and unaffected recipients to separate mailbox issues from IP reputation.
Ask the mail provider for source-specific complaint evidence and any available spamtrap clues.
Pause questionable traffic on the shared IP until the source of reports is identified and fixed.
Record the exact SMTP text because one phrase can change the whole troubleshooting path.
Expert view
Expert from Email Geeks says a SpamCop bounce that names an IP is not an address validation result; it is evidence that the sending IP is listed.
2024-06-12 - Email Geeks
Expert view
Expert from Email Geeks says shared traffic across properties means one property can create enough reports or trap hits to affect the rest of the IP.
2024-06-13 - Email Geeks
Frequently asked questions
No. A SpamCop rejection that names the connecting IP does not establish that the mailbox is invalid. Hold further sends while the IP issue is resolved. A 550 still ends that SMTP delivery attempt, so arrange a fresh send after remediation rather than relying on automatic retries. Suppress addresses after a confirmed nonexistent mailbox response, unsubscribe, complaint, or lack of valid permission.
Different outbound IPs, delivery times, receiving routes, and cached SCBL results can produce mixed outcomes. Compare SMTP logs for affected and unaffected recipients before assigning a cause. The recipient addresses can remain valid even when a CarrierZone route rejects the connecting IP.
Start with the party that controls the sending IP. If it is your provider's shared IP, send that provider the complete bounce and timestamp. Contacting the receiver is secondary when the rejection cites SpamCop. If the same IP is clear after propagation but a fresh rejection still cites SpamCop, ask the recipient to escalate through their hosting provider with the latest SMTP evidence.
SpamCop says an IP automatically delists after 24 hours with no new reports. Removal can then take up to four additional hours to propagate across mirrors and users of the blocklist.
No. DMARC does not remove a SpamCop listing, and authentication or rDNS errors are not direct SCBL listing criteria. Fix the source of reported mail while correcting authentication as a separate sender hygiene task.