Why is the wrong logo showing up in Yahoo with BIMI and how to fix it?
Published 12 May 2025
Updated 12 Oct 2026
16 min read
Summarize with
Updated on 12 Oct 2026: We updated this guide with current Yahoo BIMI requirements and checks for stale logo files.
The wrong logo in Yahoo Mail can come from an outdated BIMI SVG, a different selector or subdomain record, a cached logo, or older Yahoo brand data. BIMI (Brand Indicators for Message Identification) lets a domain publish its preferred brand logo. Start by checking the BIMI path before treating the problem as only a cache issue. The usual technical causes are an invalid SVG Tiny PS file, a BIMI record at the wrong DNS host, a delivered message that fails DMARC alignment, DMARC not at enforcement, or an incorrect selector.
The fix is to repair the SVG, publish BIMI and DMARC where Yahoo evaluates the visible From domain, verify that a delivered message passes DMARC, keep the organizational-domain policy consistent, send authenticated bulk mail, check the hosted asset, then test again after DNS and cache changes. A Verified Mark Certificate (VMC) is not the first fix for Yahoo because Yahoo's BIMI page says Yahoo currently does not require VMCs for BIMI logos, although Yahoo uses a certificate to inform eligibility when one is present.
What causes the wrong Yahoo BIMI logo?
If Yahoo shows an old logo after you publish BIMI, confirm which SVG the delivered message selects before blaming Yahoo caching. A failed BIMI check prevents use of your chosen logo, but does not prove where the displayed image came from. The fastest path is to verify the delivered message, DNS record, and retrieved SVG, then ask Yahoo to investigate the old mapping if it remains.
- SVG cause: The SVG fails BIMI SVG Tiny PS validation, so Yahoo cannot use it as the requested BIMI logo.
- Message-level cause: The delivered campaign does not pass DMARC through aligned SPF or DKIM for the visible From domain.
- Domain cause: The author domain or organizational domain has missing or inconsistent DMARC enforcement.
- Cache cause: The logo host, Yahoo, or the email client still has an older image after the records are corrected.
- Certificate check: Yahoo does not currently require a VMC, but an existing certificate must match a replacement logo.
Check authentication before blaming the cache
A cache refresh is useful after the BIMI record, SVG, DMARC policy, and delivered-message authentication are correct. An invalid SVG or failing DMARC result still prevents BIMI eligibility. A fresh browser session is also useful for identifying a local display cache issue.
How Yahoo can show an old sender logo
Yahoo supported sender logos before BIMI became the standard path for brand-controlled logos. A displayed sender image is therefore not proof that Yahoo used your current BIMI record. After a rebrand or domain migration, check the selected SVG and cached copies, then investigate older brand data if the published logo is correct.
The practical order is to prove the BIMI assertion record, delivered-message authentication, logo file, and DMARC policy first. Once those pieces are correct, Yahoo has a valid basis for evaluating the logo you publish, subject to its reputation and engagement requirements.
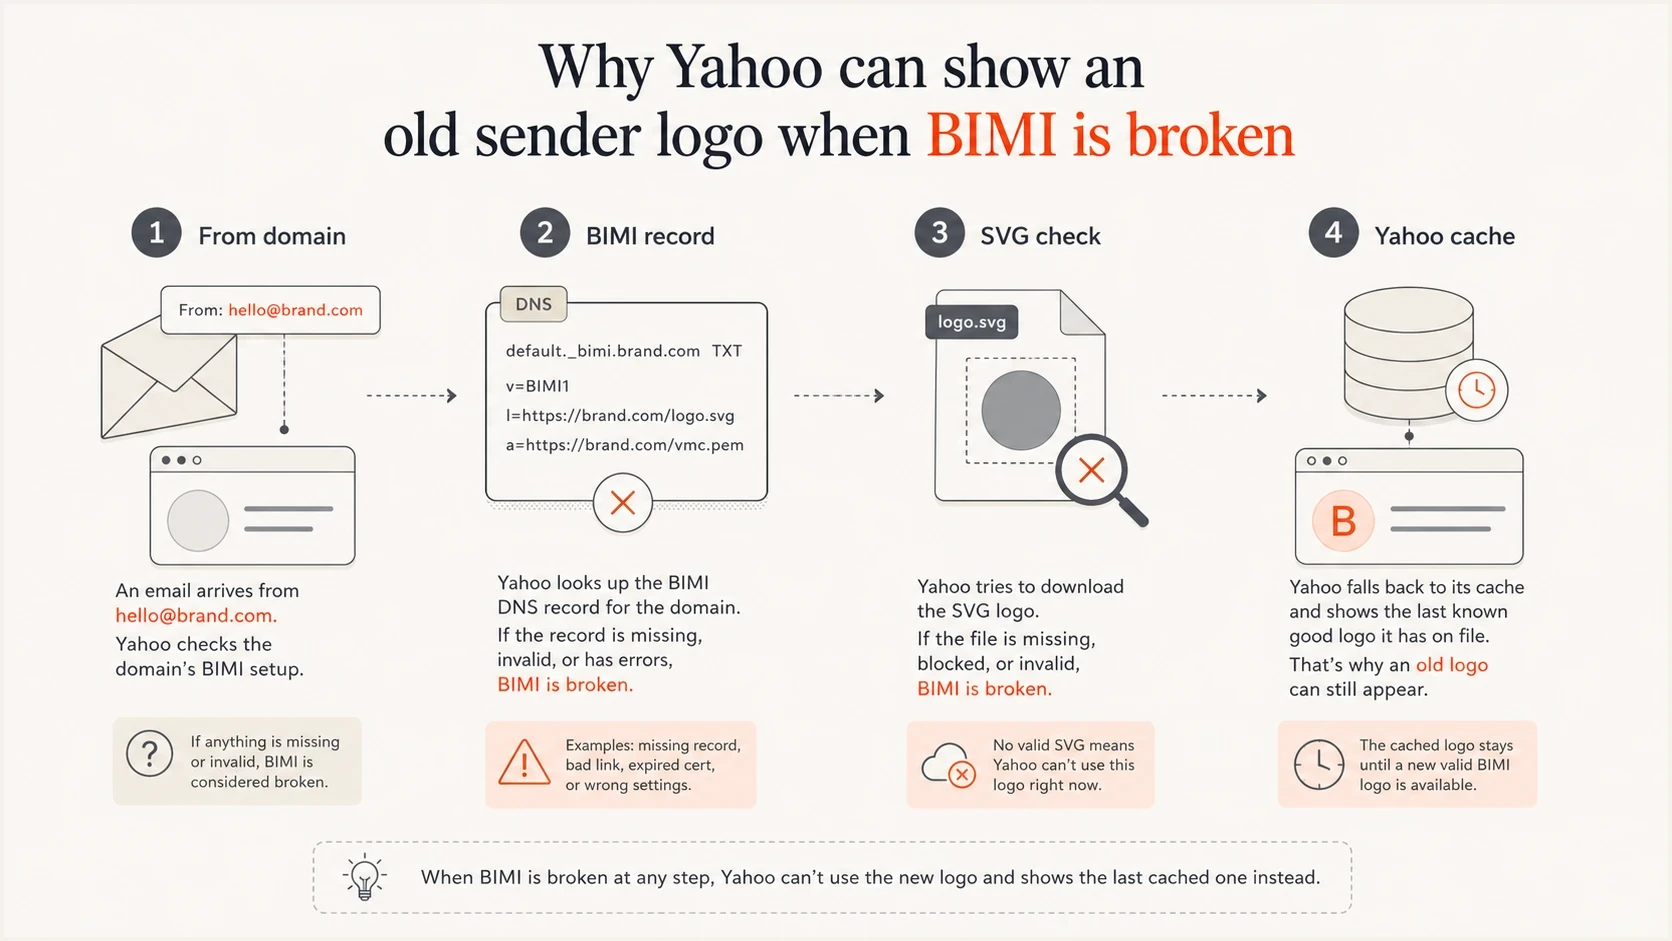
Yahoo BIMI logo lookup through the From domain, DNS record, SVG validation, and cache.
|
|
|
|---|---|---|
BIMI SVG | Invalid asset | Rebuild SVG |
DMARC | No enforcement | Use enforcement |
Message | DMARC fails | Fix alignment |
Selector | Wrong DNS host or old assertion | Match selector and inspect l= |
Cache | Old hosted or displayed image | Check hosting, then Yahoo |
Eligibility | Insufficient reputation or engagement | Review normal bulk sending |
Common Yahoo BIMI wrong-logo causes and fixes.
Fix the BIMI SVG first
The SVG is the first asset to check because BIMI is strict about the image format. A normal web SVG often fails. The logo needs the SVG Tiny Portable/Secure (Tiny PS) profile, a square aspect ratio, a title element, and fully vector content. It must not contain scripts, animation, external references, or x and y attributes on the root SVG element. An SVG 1.1 export can fail even when the BIMI record points to the right URL.
Keep the file at or below the recommended 32-kilobyte limit, center the artwork because Yahoo can crop it, and use a solid background because transparency can render unpredictably. The logo URL must load over HTTPS with a trusted certificate, return a clean success response, and use the image/svg+xml content type. Once the corrected asset is published, keep its URL stable while testing.
Required SVG opening patternxml
<svg version="1.2" baseProfile="tiny-ps"
     xmlns="http://www.w3.org/2000/svg"
     viewBox="0 0 1200 1200">
  <title>Brand name</title>
  <!-- Vector logo paths go here. -->
</svg>
SVG failures that prevent BIMI display
- Version mismatch: An SVG 1.1 export needs conversion to SVG 1.2 with the Tiny PS base profile.
- Missing title: A BIMI SVG needs a title element near the top of the file.
- Root attributes: Remove x and y attributes from the root SVG element.
- Raster content: A pasted PNG or JPEG inside the SVG is not a valid BIMI logo.
- Remote assets: Fonts, linked images, scripts, and external styles should be removed.
- Oversized file: A file above 32 kilobytes can be rejected under receiver limits.
If the BIMI record has a nonempty a= certificate URL, check its expiry and the logo it certifies. The BIMI Group's logo update guidance explains why a changed SVG needs matching certificate evidence. Yahoo accepts self-asserted BIMI without a VMC, but publishing an old certificate beside a new logo leaves inconsistent evidence.
After the logo passes, test the BIMI record itself. If you need a deeper checklist for record syntax and image problems, the related guide on how to validate BIMI records covers the common failure patterns.
Check the DNS that Yahoo evaluates
BIMI discovery starts with the domain in the visible From address. It queries the selected BIMI host at that author domain and falls back to the same selector at the organizational domain when no matching record is found. Yahoo says it honors subdomain BIMI but prefers BIMI and DMARC at the organizational-domain level.
The default BIMI TXT record sits at default._bimi under the From domain. If a delivered message contains a valid, authenticated BIMI-Selector header, a receiver can query that named selector instead. Publish exactly one BIMI TXT record at each selector host because multiple matching records stop assertion discovery. Start the record with the case-sensitive v=BIMI1 tag, and check that your DNS editor has not appended the domain twice.
DMARC needs an effective p=quarantine or p=reject policy for the author domain and organizational domain. A sending subdomain can inherit enforcement through the parent policy; it does not need a duplicate DMARC record when that inheritance is sufficient. An sp=none setting creates a BIMI enforcement gap. The BIMI Group's implementation guide requires enforcement at both domain levels.
Example BIMI and DMARC recordsdns
Host: default._bimi.example.com
Type: TXT
Value: v=BIMI1; l=https://assets.example.com/bimi.svg; a=;

Host: _dmarc.example.com
Type: TXT
Value: v=DMARC1; p=quarantine; rua=mailto:dmarc@example.com
RFC 9989 makes pct historic, so omit it from a new DMARC record. The BIMI Group's implementation guide still excludes pct values below 100, so remove legacy partial-enforcement settings after authenticating legitimate sending sources. Do not treat a legacy pct tag as a reliable enforcement control. The t=y tag requests test-mode handling under RFC 9989; omit it or use t=n when the policy is ready for full enforcement. Before testing Yahoo again, confirm that the DMARC record parses cleanly and covers every visible From domain used by the campaign. Suped's DMARC checker supports this focused DNS check by showing parsed tags and policy gaps that can block BIMI.
DMARC checker
Look up a domain's DMARC record and catch policy issues.
?/7tests passed
Verify the delivered message, not only DNS
A correct BIMI record does not make every message eligible. Open the original headers of a campaign delivered to Yahoo and confirm that Yahoo's receiver-added Authentication-Results shows dmarc=pass for the visible From domain. DMARC passes when either SPF or DKIM passes with an identity that matches that domain under DMARC rules. A sender-supplied Authentication-Results header is not evidence of Yahoo's evaluation.
Yahoo's bulk-sender requirements separately require both SPF and DKIM to be implemented. The DMARC pass needs at least one aligned method, but configuring only one method does not meet Yahoo's bulk-sender requirements. Its basic p=none policy minimum is also insufficient for BIMI, which needs quarantine or reject.
A message that requests a non-default logo also needs the expected BIMI-Selector header. Include that header in the h= list of a passing, DMARC-aligned DKIM signature. A receiver can ignore an unsigned selector and query the default selector instead, which can make a valid but older logo appear. The receiver hostname below is illustrative, and the DKIM signature is abbreviated.
Delivered header checkstext
From: offers@news.example.com
Authentication-Results: mx.example; dmarc=pass header.from=news.example.com
BIMI-Selector: v=BIMI1; s=campaign;
DKIM-Signature: v=1; d=news.example.com; h=from:subject:bimi-selector; ...
What to prove in the message
- Visible From domain: Use the exact domain Yahoo displays to the recipient.
- DMARC result: Confirm dmarc=pass in Yahoo's received copy, not only in a sending platform.
- Identifier alignment: At least one passing SPF or DKIM identity must match the visible From domain under DMARC rules.
- Selector protection: A non-default BIMI-Selector header should be covered by a passing, aligned DKIM signature.
Which domain's BIMI record controls the logo?
An organizational-domain BIMI record can provide the fallback when no matching record is found at the visible From subdomain. A record found at the author subdomain takes precedence, so an old subdomain assertion can override a newer root logo. An invalid SVG or an explicit empty l= value does not automatically trigger root fallback.
Use a subdomain-specific record when that exact From domain needs its own logo. Otherwise, an organizational-domain record gives related sending subdomains a shared fallback and reduces duplicate DNS maintenance. DMARC enforcement must still cover both domain levels. The BIMI discovery draft keeps the selected selector during organizational-domain fallback: campaign._bimi.news.example.com falls back to campaign._bimi.example.com, rather than default._bimi.example.com.
Subdomain-specific setup
- Exact scope: The visible From subdomain has its own BIMI record.
- Lookup priority: An author-domain assertion wins over the root fallback; an invalid logo still needs repair.
- Maintenance cost: Each sending subdomain and selector needs change control.
Organizational-domain fallback
- Shared logo: Subdomains without a matching record can use the same selector at the organizational domain.
- Fewer records: One stable default reduces duplicate asset changes for streams using the default selector.
- Policy condition: DMARC enforcement still has to cover the author domain and root.
If the old logo belongs to a former brand name, update the published SVG URL only when the replacement file is valid and final. For image dimensions and change control, use the related guide to update a Yahoo BIMI logo before asking Yahoo to investigate the old mapping.
Check the hosted logo and CDN cache
A valid BIMI record can still point to an old file. Fetch the exact HTTPS URL in l= without browser cookies and compare the returned SVG with the approved logo. A website or content delivery network (CDN) serving old bytes prevents Yahoo from retrieving the replacement.
Fetch the published SVG and response headersbash
curl --fail --silent --show-error --location \
  --dump-header /tmp/bimi-headers.txt \
  --output /tmp/bimi.svg \
  'https://assets.example.com/bimi.svg'
- Confirm the final response is HTTP 200 with Content-Type: image/svg+xml, rather than an HTML error page.
- Check Cache-Control, Age, and ETag headers for evidence of a stale cached response, then compare the actual SVG content.
- Remove login requirements, bot challenges, hotlink protection, or geographic restrictions that block logo retrieval.
- Check redirects and hosting logs to confirm the public URL reaches the intended SVG and has a trusted TLS certificate.
The BIMI Group's hosting guidance covers retrieval blockers. After validating the replacement, purge the hosting cache or publish one final versioned SVG URL in l=, then keep it stable. This fixes a cache you control; it does not force Yahoo to purge its own copy.
What to do about Yahoo caching
Yahoo does not publish a fixed BIMI cache refresh deadline. Allow the relevant DNS TTLs to expire, verify the updated TXT record and hosted SVG, then test newly delivered mail. DNS propagation, hosting caches, and Yahoo's stored logo data are separate checks, so a two-week wait is not a guaranteed fix or a required delay before contacting support.
Check a fresh message in a supported surface before calling it a cache failure. Yahoo documents BIMI logos in mobile message lists and read views, plus desktop webmail read views. A missing logo in the desktop message list is different from the wrong logo appearing in the desktop read view. Yahoo's sender FAQ recommends a cleared browser cache and a new web session; this clears local display data rather than Yahoo's server-side logo cache.
Save the exact visible From domain, selector, BIMI host, SVG URL, DMARC policy, delivered Authentication-Results, a screenshot of the wrong logo, and a fresh DNS check. Include the Message-ID and delivery time in UTC so Yahoo can identify the message. Yahoo's BIMI support guidance lists mail-questions@yahooinc.com as the contact for BIMI problems. Ask Yahoo to investigate whether cached or older brand data is supplying the image.
Yahoo Mail showing an outdated sender logo beside an open marketing email.
Yahoo support evidence
- Fresh check: Verify public DNS and the SVG after TTL expiry, then compare newly delivered mail in a new web session.
- Support note: Include the From domain, BIMI host, selector, old logo shown, SVG URL, Message-ID, and UTC delivery time.
- Stable asset: Keep the final SVG URL unchanged while Yahoo investigates.
- Clear request: Ask Yahoo to investigate the incorrect logo and any stale mapping for the domain.
Yahoo support note templatetext
To: mail-questions@yahooinc.com
Subject: Wrong BIMI logo for example.com

Visible From domain: example.com
BIMI host: default._bimi.example.com
Selector: default
Logo URL: https://assets.example.com/bimi.svg
DMARC policy: p=quarantine
Delivered Message-ID: [Message-ID]
Delivery time (UTC): [timestamp]

The SVG is valid and publicly retrievable over HTTPS.
The delivered message passes DMARC for example.com.
Fresh mail in a new Yahoo web session still shows an older logo.
Authentication-Results, DNS evidence, and a screenshot are attached.
Please investigate whether cached or older brand data is causing the incorrect logo.
How Suped helps with the fix
Suped's product supports the DMARC work behind a Yahoo wrong-logo investigation. Add the organizational domain and visible From subdomains, use DMARC monitoring to confirm which sending sources pass through aligned SPF or DKIM, fix enforcement gaps, and keep alerts on while Yahoo reevaluates the sender. Aggregate reports show source-level authentication patterns, so keep Yahoo's received headers for individual message evidence.
For this workflow, compare the root domain and sending subdomain, confirm the policy applied to each source, then preserve the final BIMI selector and SVG URL during the cache investigation. If policy ownership is spread across teams, Hosted DMARC keeps policy changes in one managed workflow without repeated manual DNS edits.
DMARC record detail view showing SPF, DKIM, DMARC, rDNS diagnostics, and DNS records
- Policy checks: Suped identifies missing or weak DMARC policies that make a sender ineligible for BIMI.
- Source evidence: Aggregate data shows whether reporting receivers observed DMARC passes through aligned SPF or DKIM.
- Domain coverage: Root domains and visible From subdomains can be reviewed in the same investigation.
- Change alerts: Teams can respond when authentication changes during the Yahoo cache investigation.
A practical troubleshooting sequence
This order removes false explanations quickly. First prove which logo and Yahoo surface are affected. Then verify the delivered message, domain policy, selector record, and SVG. Once those checks are clean, check hosting caches and Yahoo's reputation and engagement requirements before attributing the result to its logo cache.
Yahoo BIMI readiness
Use this quick status map before deciding whether to contact Yahoo.
Ready
Test fresh mail
DMARC passes, policy is enforced, the SVG is valid and retrievable, and normal bulk mail is authenticated.
Review
Check evidence
The record exists, but the message, selector, domain scope, or sender eligibility is uncertain.
Waiting
Check propagation
The setup is correct, but fresh mail still shows older data after local cache checks.
Blocked
Repair setup
The SVG fails, retrieval is blocked, the message fails DMARC, or policy is not enforced.
- Capture the symptom: Save the wrong-logo screenshot and note the Yahoo device and view.
- Confirm the From domain: Use the domain in the visible From address, not a tracking or return-path domain.
- Inspect the delivered headers: Confirm dmarc=pass and identify the aligned SPF or DKIM domain.
- Validate DMARC policy: Check effective quarantine or reject policies for the author domain and organizational domain, including inherited subdomain policy.
- Match the selector: Query the authenticated selector named in the message, or default when no usable BIMI-Selector header exists.
- Validate the SVG: Fix the profile, title, root attributes, vector content, file size, and external references. Check matching certificate evidence when present.
- Check public retrieval: Fetch the exact l= URL and confirm the current SVG, HTTP response, MIME type, and hosting cache.
- Use normal bulk mail: Test an authenticated production stream with both SPF and DKIM configured. Do not increase volume just to trigger a logo.
- Recheck after propagation: Allow DNS TTLs to expire and compare fresh mail in a supported Yahoo view with a new web session.
- Escalate with proof: Contact Yahoo if the wrong logo persists after the technical and local cache checks pass; there is no published two-week deadline.
Mistakes that keep the wrong logo alive
Most prolonged Yahoo BIMI logo problems come from fixing the visible symptom while leaving the cause intact. A new logo URL will not help if the SVG profile is wrong. A VMC will not make a message eligible if DMARC fails or policy remains at none. A Yahoo support request will not settle the result if the sender keeps changing the selector or asset during review.
Avoid these loops
- Changing too much: Do not rotate selectors, domains, and asset URLs at the same time.
- Skipping message checks: A correct DNS record cannot compensate for dmarc=fail in Yahoo's received copy.
- Trusting previews: A local preview can render a logo that BIMI validation rejects.
- Publishing duplicates: Multiple BIMI TXT records at one selector host stop record discovery.
- Ignoring eligibility: Yahoo considers bulk-mail status, sender reputation, and engagement. It does not publish a BIMI volume threshold.
The clean fix uses one valid SVG, one final logo URL, one BIMI TXT record per selector host, enforced DMARC, and a passing delivered message. Continue normal mail to opted-in recipients while Yahoo evaluates the sender; extra test volume is not evidence that a cache has refreshed.
Views from the trenches
Community troubleshooting reports describe individual cases. Use current DNS, the retrieved SVG, and Yahoo's received headers to establish the cause for your own domain.
Best practices
Validate the SVG Tiny PS profile before asking Yahoo to investigate a stale sender logo.
Check effective DMARC enforcement for both the From domain and organizational domain.
Keep the final logo URL stable during testing so cache behavior can be diagnosed clearly.
Common pitfalls
Treating Yahoo as a cache issue before checking whether the published SVG actually passes.
Assuming a VMC fixes Yahoo display when DMARC policy and SVG validity still fail checks.
Changing selectors, logo URLs, and sender domains together during one logo investigation.
Expert tips
Save the wrong-logo screenshot and current DNS evidence before opening a Yahoo support case.
Use normal authenticated bulk mail for testing, rather than increasing volume for a logo.
Check stale subdomain assertions and cached SVG files after a rebrand or domain migration.
Marketer view
Marketer from Email Geeks says invalid SVG Tiny PS details can make Yahoo ignore the published BIMI logo and fall back to another image.
2025-02-25 - Email Geeks
Marketer view
Marketer from Email Geeks says Yahoo can remove the wrong image mapping after the sender proves the corrected BIMI setup is valid.
2025-02-25 - Email Geeks
Frequently asked questions
No. Yahoo currently says it does not require VMCs for BIMI logos to appear, although Yahoo uses a VMC to inform overall eligibility when it is included in the BIMI record. A published certificate must be current and match the logo it certifies.
It can provide the organizational-domain fallback when no matching record exists at the visible From subdomain. A subdomain assertion takes precedence, and fallback keeps the same selector. A broken SVG or explicit empty l= value does not automatically trigger root fallback. DMARC enforcement still must cover both domain levels.
A DMARC pass needs at least one aligned method, SPF or DKIM. Yahoo separately requires bulk senders to implement both SPF and DKIM, so a DMARC pass alone does not prove that all Yahoo sending requirements are met.
An invalid SVG prevents Yahoo from using your requested BIMI logo. An older displayed image can come from another assertion, a cached file, or older brand data, but the failed SVG alone does not establish which source supplied it.
Yahoo publishes no fixed BIMI refresh deadline. Allow relevant DNS TTLs to expire, verify the hosted SVG, and test newly delivered mail in a supported view with a new web session. Keep the final selector and SVG URL stable, then contact Yahoo if the wrong logo persists after those checks.
Fix the SVG, selector record, DMARC policy, and delivered-message alignment first. Then email mail-questions@yahooinc.com with the From domain, BIMI host, SVG URL, policy evidence, Authentication-Results, Message-ID, UTC delivery time, and a screenshot of the wrong logo.