What causes Proofpoint to block or defer emails sent to iCloud addresses and how can I resolve it?
Updated on 9 Oct 2026: We clarified Proofpoint IP block review, forwarding authentication, and iCloud recovery steps based on SMTP results.
Email to icloud.com, me.com, and mac.com can be blocked or deferred because of sending IP reputation, authentication, content, or traffic patterns. If the SMTP response names Proofpoint, separate hard blocks from temporary deferrals, then investigate the signal named in the error.
If the response includes 421 4.7.0 Deferred, treat it as a temporary failure and read the response text to distinguish reputation delays from rate limits. If the visible delivery report later shows 554 5.4.7 [internal], the sending system usually retried until its own queue timed out. That final 554 can look like a Proofpoint block, but the key event was the earlier 421 deferral.
For rate or reputation deferrals, pause broad marketing sends to Apple mailbox domains, keep essential transactional mail flowing at a controlled rate, check authentication, review recipient demand, and ask the ESP to reduce concurrency. Suped's product combines DMARC reporting with authentication and blocklist monitoring. Compare those results with your ESP's delivery logs to investigate the same sending source.
Why Proofpoint defers or blocks iCloud mail
An iCloud MX response that contains a Proofpoint DNSBL URL shows that Proofpoint reputation data influenced that SMTP decision. It does not prove that every Apple delivery path uses the same filter or that the sending IP appears on a public blacklist or blocklist. Proofpoint can slow the SMTP transaction, defer delivery, or reject the message depending on the signal and policy outcome.
A deferral permits a later delivery attempt. A permanent SMTP rejection ends the affected attempt; it does not establish how long an IP restriction will last. Those two cases need different responses. Re-warming a dedicated IP without changing audience selection, cadence, complaints, bounce handling, or authentication usually does not solve a 421 pattern. It only repeats the same traffic at a slower starting point.
Read the SMTP code before changing strategy
A 4xx response permits a later retry. A 5xx response is a permanent failure for the affected SMTP operation. When both appear in one report, the earlier transfer failure often tells you more than the final generated bounce.
- 4xx: Temporary failure. Retry with backoff and investigate the response text.
- 5xx: Permanent failure. Resolve the stated cause before resending; do not keep retrying an unchanged rejected message.
- Internal: A sending server or ESP queue can give up after repeated temporary failures.
Sender queue expiry after temporary deferralstext
554 5.4.7 [internal] message timeout
(exceeded max time, last transfail:
421 4.7.0 Deferred - see Proofpoint DNSBL lookup)
That example says the sending queue expired after repeated temporary failures. Investigate the earlier 421 and the sender's retry settings before increasing volume. The generated timeout alone does not establish a permanent IP listing.
Sending IP reputation and iCloud filtering signals
Proofpoint's IP reputation system evaluates the connecting IP for spam or malicious mail. iCloud also assesses IP and domain reputations, message content, and user feedback. A clean public blocklist result does not establish that every receiver policy will accept the mail. Also check URLs in the message and signature, including redirects, for compromised linked sites. Proofpoint identifies infected websites as a blocking cause. See Proofpoint's IP reputation FAQ. See Proofpoint postmaster guidance.
|
|
|
|---|---|---|
421 4.7.0 | Temporary failure; read the accompanying explanation | Retry with backoff; reduce traffic if indicated |
554 5.7.0 | Permanent receiver rejection when the response says Blocked | Investigate the named IP and request review after remediation |
554 5.4.7 [internal] | Sender queue expired after unsuccessful delivery attempts | Read the earlier receiver response and retry history |
IP | Reputation or listing concern | Check the actual sending IP's listing status |
Domain | Authentication or reputation concern | Verify message authentication results |
Volume | Too much mail too quickly | Reduce concurrency |
Common Proofpoint and iCloud delivery signals
The most useful split is between technical legitimacy and recipient demand. Technical legitimacy means SPF, DKIM, DMARC, rDNS, HELO, and TLS are set up correctly. Recipient demand starts with explicit subscription and is supported by clicks, replies, purchases, logins, unsubscribes, and direct complaints. iCloud does not offer a bulk-sender feedback loop, and Apple Mail Privacy Protection makes raw opens unreliable. See iCloud postmaster requirements. See Apple Mail Privacy Protection.
When authentication passes but deferrals coincide with weak Apple-domain engagement, focus on traffic quality and recipient selection. Send less mail to inactive Apple recipients, segment recent clickers and customers, reduce repeated campaign pressure, and do not retry the same audience at full speed.
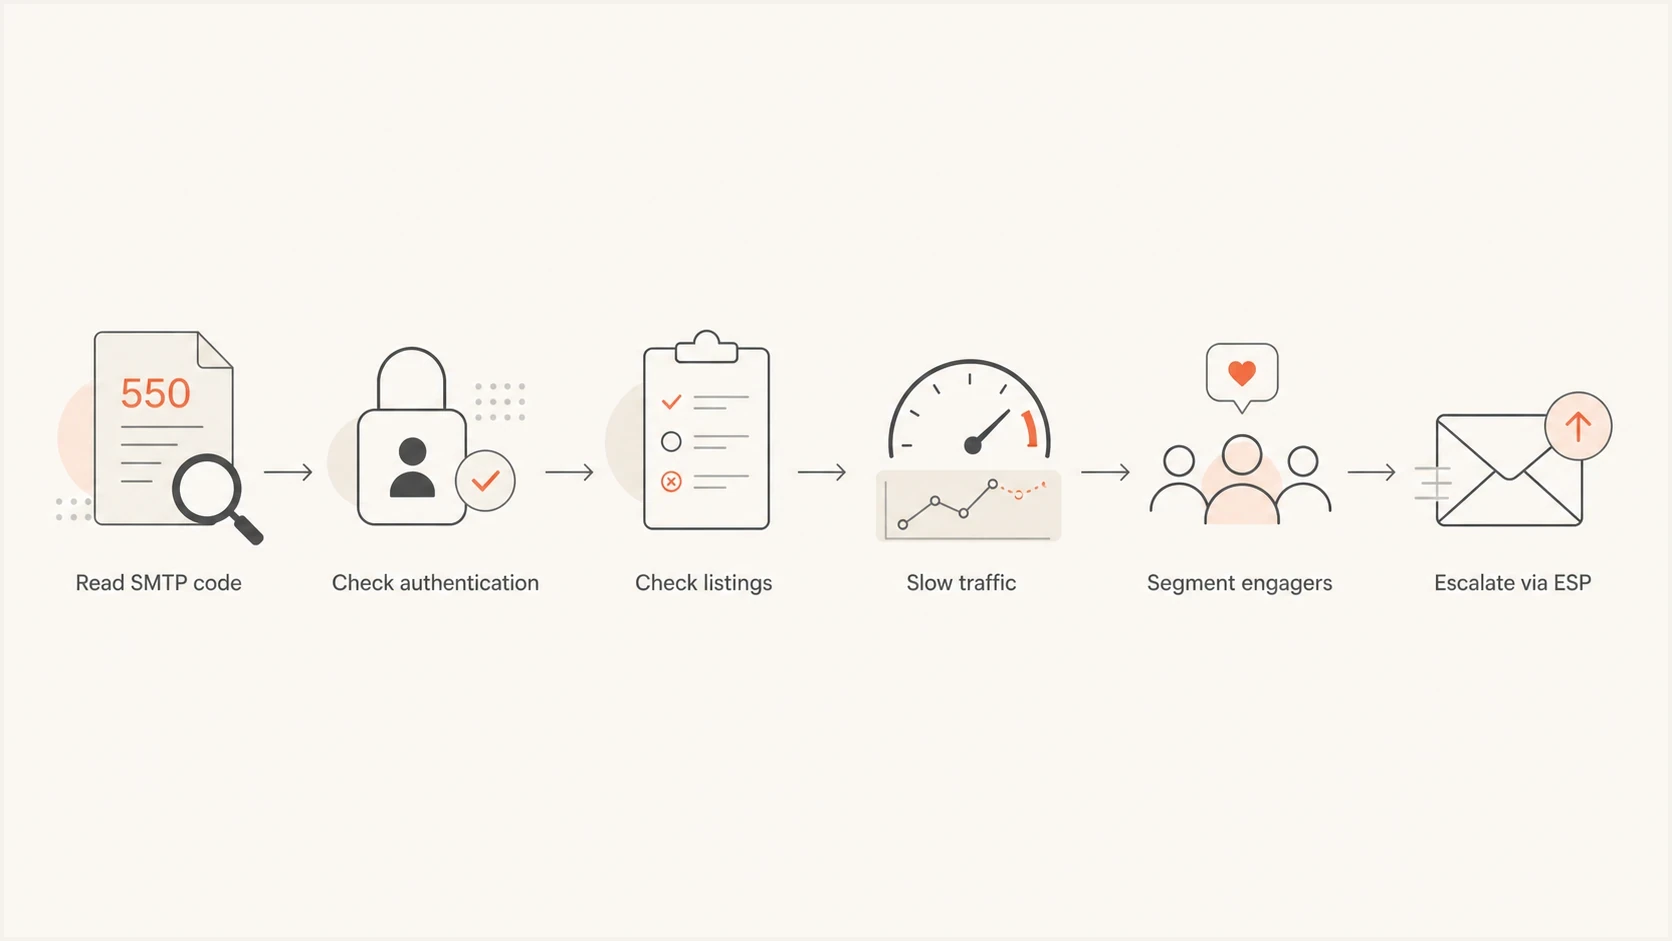
Troubleshooting Proofpoint blocks and iCloud email deferrals with authentication checks and sending controls.
Forwarded mail and shared relay IPs
Forwarding changes the diagnosis. When a routing service accepts a message and sends it onward to iCloud, the connecting IP belongs to that relay. A 554 5.7.0 Blocked response with a Proofpoint DNSBL URL that names the relay IP points first to the relay's shared reputation or routing, not automatically to the original author's domain.
- Match the IP: Compare the address in the SMTP response with the forwarding provider's actual outbound IP.
- Escalate to the owner: The relay operator controls shared pool cleanup, route changes, and any review of its IP.
- Preserve authentication: SPF often fails after forwarding. Sender Rewriting Scheme (SRS) can make SPF pass for the relay's envelope domain without satisfying DMARC for the original From domain. DKIM can survive if signed content is unchanged, and Apple requires Authenticated Received Chain (ARC) headers on forwarded mail.
- Contain carefully: An alternate forwarding destination can restore urgent access, but it does not repair the affected relay IP or route.
Changing DMARC on the original domain will not clear a reputation block against a relay IP. Suped's DMARC reporting can show authentication results for forwarded mail evaluated by reporting receivers, while the relay operator handles the connecting IP's listing. A rejection before authentication evaluation has no DMARC result to report.
How to resolve iCloud deferrals
Start with evidence. Pull the full SMTP transcript or bounce detail for several failed messages, rather than only the friendly ESP status. Collect the first Proofpoint response, retry history, final queue timeout, sending IP, envelope sender, DKIM selector, and campaign or mail stream. Record which SMTP stage fails. A rejection before DATA occurs before the receiver has the message content or DKIM signature, so investigate connection and envelope evidence first. See SMTP transaction sequence.
- Classify: Split failures into temporary deferrals, receiver 5xx rejections, sender queue timeouts, and mailbox-address errors. Do not suppress an address as invalid solely because of a 421 or an internal timeout.
- Throttle: Ask your ESP to reduce concurrency and per-domain throughput when the errors indicate rate or reputation limits. Check retry backoff and queue expiry so retries do not add another traffic burst.
- Segment: Restart with recent Apple engagers first, then add older cohorts only after deferrals fall.
- Authenticate: Inspect SPF and DKIM results on actual messages and confirm DMARC passes for the visible From domain. Verify the sending IP's PTR record and the HELO/EHLO hostname.
- Comply: Send bulk mail only to explicit subscribers, offer an immediate unsubscribe link, and keep sending identities consistent. Never restore unsubscribed addresses to a campaign.
- Monitor: Track iCloud SMTP outcomes alongside clicks, conversions, unsubscribes, and direct complaints. Review any abuse reports supplied by the ESP.
- Escalate: If deferrals persist after cleanup, ask the ESP to contact Proofpoint with IPs, logs, timestamps, and remediation steps.
For rate or reputation deferrals, reduce sending pressure and improve audience selection before restoring volume. Ask the ESP to use delayed retries rather than immediate repeated attempts. RFC 5321 generally recommends retry intervals of at least 30 minutes, with more adaptive strategies permitted when the cause is known; use the ESP's queue policy and the message's useful lifetime to plan recovery. See SMTP retry guidance.
Recovery actions to avoid
- Pause-only: A fixed pause gives no evidence that the cause has been resolved. Check current SMTP responses before restarting.
- Full blast: Sending to every iCloud recipient at once can recreate volume-related deferrals.
- DNS-only: Fixing authentication cannot repair weak engagement by itself.
Recovery actions to test
- Lane control: Limit Apple-domain throughput separately rather than slowing every recipient domain.
- Engager-first: Send first to people with recent clicks, purchases, replies, or logins.
- Evidence pack: Give the ESP IPs, timestamps, SMTP responses, domains, and cleanup actions.
For a dedicated IP, review all sources using that IP rather than only the affected campaign. For a shared IP, the issue can come from another sender on the same pool, so the ESP has to investigate the pool reputation and routing choices.
What to check in DNS and authentication
Authentication is the baseline. For bulk email, Apple requires SPF and DKIM and a published DMARC policy. A valid DNS record alone does not establish that an actual message passes authentication. See iCloud bulk-mail requirements.
?
What's your domain score?
Deep-scan SPF, DKIM & DMARC records for email deliverability and security issues.
Use Suped's domain health checker to review published DNS records. Then send a controlled test and inspect the receiving server's Authentication-Results header to verify the actual sending stream. Check the DKIM selector used in that message, because a scan of common selectors does not cover every selector.
Conservative DMARC starting pointdns
_dmarc.example.com TXT "v=DMARC1; p=none; rua=mailto:dmarc@example.com"
This example omits pct because RFC 9989 made the tag historic. A p=none policy remains useful for collecting reports while legitimate sources are identified. See RFC 9989.
For a sender already under delivery pressure, do not jump straight to a stricter DMARC policy unless reports show all legitimate mail matches the right domain. Suped can show which sources pass, which fail, and which authenticated sources remain unverified. That matters when marketing, product, billing, and support mail use different platforms.

Issue steps to fix dialog showing the issue overview, tailored fix steps, and verification action
The envelope sender's SPF record must authorize the sending IP and stay within the limit of 10 DNS-lookup-causing mechanisms and modifiers, including nested evaluations. DKIM needs a valid public key for the selector used in the message. DMARC passes when SPF or DKIM passes and the authenticated domain meets the policy's matching rule for the visible From domain. Relaxed mode permits the same organizational domain; strict mode requires an exact match. The PTR hostname should resolve back to the sending IP, and HELO/EHLO should identify a valid mail-server hostname. See SPF lookup limits. See DMARC domain matching.
How blocklists and blacklists fit in
A Proofpoint DNSBL URL in an SMTP error identifies a reputation-review path, but a clean lookup does not overturn that rejection. Check the exact connecting IP and record the lookup time. A blocklist (blacklist) result does not cover every local iCloud filtering decision.
Blocklist checker
Check your domain or IP against 144 blocklists.




Check the IPs and domains against a blocklist checker, then treat the results as one part of the diagnosis. If an IP is listed, fix the cause before asking for removal. If it is clean, keep working through authentication, traffic rate, and audience quality.
Use blacklist data carefully
A clean lookup and a temporary SMTP rejection can occur at the same time. Compare the result with the exact IP and timestamp in the failed delivery.
- Listed: Remove spam sources, fix authentication, suppress bad recipients, then request delisting.
- Clean: Investigate throttling, engagement, complaints, and per-domain volume.
- Mixed: Compare listed IPs with actual sending IPs in the failed messages.
Suped's blocklist monitoring tracks IP and domain listings alongside authentication status. Compare listing alerts with the incident timestamps and ESP logs to check whether the same sending IP is involved.
How to request removal of a Proofpoint IP block
For an IP-specific 550 or 554 rejection, confirm that the named IP is the actual outbound server or forwarding relay. The IP owner should follow the delist-request path in Proofpoint's postmaster documentation after investigating and fixing any abuse. If logs show only wanted traffic, request a false-positive review with evidence. On a shared service, the ESP or relay operator should coordinate the request. See Proofpoint postmaster guidance.
- Inspect outbound logs for compromised accounts, unexpected traffic, malware, or an open relay. Disable unwanted sending and secure access before requesting delisting.
- Include the affected recipient, mail type, sending IP, exact SMTP error, timestamps, and completed remediation. Explain whether the mail is personal correspondence or a subscribed bulk stream.
- If the lookup says the IP is unlisted, save that result and its timestamp with the rejection. Ask the operator and iCloud postmaster to investigate the current error rather than repeatedly requesting removal of an absent listing.
- After review, retry a small sample and confirm receiver acceptance in the SMTP logs. Delisting does not guarantee inbox placement or remove every iCloud filtering restriction.
When to escalate Proofpoint and iCloud failures
If you send through an ESP, involve them early. They control queue behavior, connection limits, retry timing, pool assignment, and sometimes the relationship path into Proofpoint. A sender can fix list quality and authentication, but the ESP often has to change throttle settings or open the reputation conversation.
Give the ESP a tight packet of evidence. Include sending IPs, sending domains, envelope sender domains, timestamps with time zone, the exact SMTP response, a sample message ID, and the cleanup actions already taken. Do not send only a screenshot of a dashboard that says deferred.
If the rejection comes from an iCloud MX and continues after remediation, contact the iCloud postmaster at icloudadmin@apple.com. Include the company name, email domain, affected sending or relay IPs, exact SMTP errors, incident start time, and completed fixes. iCloud has no bulk-sender allowlist, so provide evidence instead of asking to be allowlisted. See iCloud postmaster contact guidance.
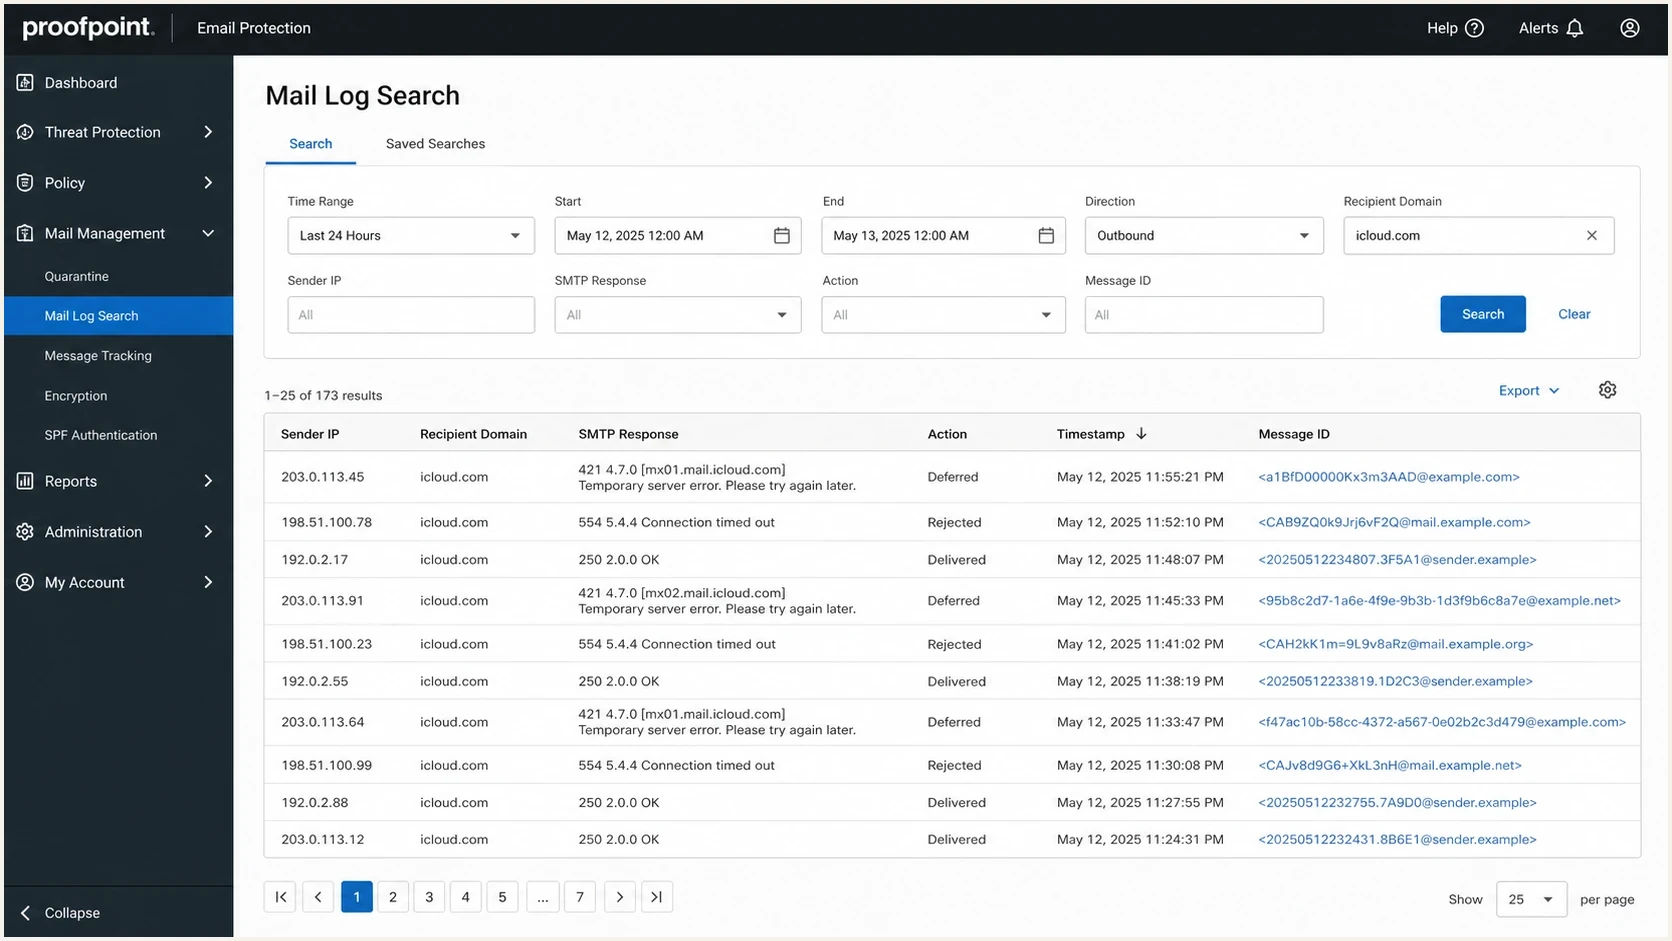
Illustrated Proofpoint mail logs showing iCloud 421 deferrals and 554 sender queue timeouts.
If the mail is important transactional traffic, separate it from bulk marketing wherever possible. Shared reputation between receipts, password resets, lifecycle campaigns, and old reactivation campaigns makes troubleshooting harder and can put critical mail at risk.
|
|
|
|---|---|---|
Concurrency | ESP | Reduce sessions |
Audience | Sender | Suppress inactives |
DMARC | Sender | Fix domain match |
Sending IP listing | IP owner, ESP, or hosting provider | Stop abuse and request review |
Relay IP | Relay provider | Remediate shared pool |
Persistent Apple rejection | Sender or ESP | Contact iCloud postmaster |
Who should handle each fix
Apple Mail is a mail client used with multiple providers. Apply these iCloud delivery checks to iCloud-hosted destinations, not every address opened in Apple Mail. The related guidance on iCloud blocking covers other iCloud rejection causes.
A recovery plan based on SMTP results
Use measured SMTP outcomes to decide when to restore iCloud volume. Track temporary failures separately from final delivery failures and queue age; repeated retries otherwise inflate the apparent share of affected messages.
Start with containment. Pause nonessential Apple-domain marketing, suppress confirmed invalid addresses and complaint recipients, remove stale unengaged subscribers, and confirm that transactional mail has its own sending path. If all mail shares one dedicated IP, lower total Apple-domain throughput while the problem is active.
Once the cause is addressed, test a small, controlled sending segment. Send only to the strongest Apple-domain segment, then watch SMTP outcomes by hour. Do not judge recovery by aggregate opens because Apple Mail Privacy Protection distorts them. Use clicks, replies, conversions, unsubscribes, direct complaints, and actual SMTP outcomes.
After the deferral rate drops, add volume in small steps. If deferrals rise again, compare the added cohort with any change in throughput or sending IP before attributing the issue to list quality. The ESP can keep a separate Apple-domain throttle until the stream has several stable sending days.
Set measurable restart criteria
Increase volume only when SMTP acceptance improves and queue age remains manageable. If deferrals return, reduce throughput and investigate the current response before adding another cohort.
Suped's platform supports the technical checks through DMARC reporting and authentication alerts. Compare its blocklist history with the ESP's SMTP logs while the marketing team adjusts audience selection.
Frequently asked questions
No. A 421 is a temporary SMTP deferral. The final delivery report can become a bounce if the sender keeps retrying until its queue expires.
Re-warming is not the first step. Fix the issue identified in SMTP logs, reduce pressure when errors indicate rate or reputation limits, and resume with wanted mail. A 421 alone does not establish that the IP needs another warm-up.
Yes. A clean blocklist result does not override current SMTP errors. Check the actual connecting IP and lookup time, then investigate iCloud policy or traffic restrictions with the ESP or relay operator.
The forwarding relay becomes the connecting sender to iCloud. If the rejection names that relay's IP, the relay operator owns the reputation and routing fix. ARC and preserved DKIM help iCloud evaluate the original authentication.
Send the exact SMTP response, timestamps, sending and relay IPs, message IDs, sending domains, current throttle settings, and cleanup steps already completed.
DMARC helps prove domain legitimacy, but it does not fix unwanted traffic or a listed relay IP. Good list hygiene, controlled volume, strong recipient demand, and ARC on forwarded mail still matter.