Why are email clients being blocked by AT&T and how was it resolved?
Updated on 2 Oct 2026: We clarified the 2023 AT&T blocking incident, today's Yahoo routing, and the evidence to collect before escalating a new rejection.
The short answer is that sending accounts affected in the reported July 2023 incident were blocked during a weekend AT&T mail filtering issue that hit selected sender IPs across multiple platforms. The pattern did not point to one sender, one email service provider, or one shared authentication mistake. Delivery recovered after the receiver issue cleared and affected IPs were reviewed.
Here, "email clients" means customer sending accounts, client domains, or mail streams. If a desktop mail app cannot sign in or send any mail, check the app settings and account instead. The incident discussed here involved SMTP rejections when senders tried to deliver to AT&T recipient domains. Some affected senders had only a subset of dedicated IPs blocked.
- The reported cause was a temporary AT&T mail filtering issue in July 2023 that produced IP-specific blocks across separate senders.
- Blocks appeared across different platforms, domains, and dedicated IP pools, which pointed to a receiver-side issue.
- Affected IPs were escalated for review, and reports said most delivery recovered after the weekend issue cleared.
- Check the bounce, DNS, authentication, and reputation before treating a new AT&T-domain block as the same incident.
What happened in July 2023
The key signal in the July 2023 reports was correlation. Multiple senders reported AT&T blocks beginning around the same weekend. The affected senders were not all on the same platform. Some were on different sending systems with their own dedicated IP addresses. That pattern matters because sender-side reputation problems often follow a clear source, such as one campaign, one client, one IP range, one bad authentication setup, or one sudden complaint spike.
This incident did not behave that way. Affected mail streams varied, and the blocking was uneven. Some clients had only a few IPs blocked, while nearby IPs remained usable. Other clients had no issue at all. That unevenness supports a two-step response: verify the local sending system, then collect evidence for the receiving team to check the block.
How it was resolved
Reports said the 2023 blocking eased after the weekend mail issue was corrected and affected IPs were checked through the receiver escalation channel. The documented response was to confirm the incident, collect affected IPs, escalate them, and verify that delivery returned.
|
|
|
|---|---|---|
Many platforms | Shared receiver issue | Compare reports |
Some IPs only | IP-specific impact | List IPs |
Weekend start | Common incident window | Keep timestamps |
Fast recovery | Block cleared | Retest delivery |
Signals that pointed to a receiver-side blocking event.
AT&T consumer mail now routes to Yahoo
The 2023 incident is historical context. Yahoo announced in June 2025 that AT&T consumer domains would move from a separate AT&T gateway to direct Yahoo MX routing. The change covered att.net, currently.com, sbcglobal.net, bellsouth.net, pacbell.net, and other legacy AT&T domains. Current rejections to those domains generally come from Yahoo infrastructure, so the old AT&T DNSBL/RBL removal process is not the default path.
Check the recipient domain's live MX records and the remote host in the full SMTP response before escalating. The brand in the recipient address does not identify the gateway that made the decision. Use the current route and exact error text to choose the support path.
- For a Yahoo-routed rejection, follow the current receiver guidance indicated by the Yahoo gateway response.
- For an AT&T DNSBL/RBL blacklist rejection, use abuse_rbl@abuse-att.net when the live bounce identifies an AT&T-operated block or directs you there.
- For a 4xx response, treat the failure as temporary, retry with controlled backoff, and keep repeated response samples.
- For a 5xx response, treat the attempt as rejected, stop automatic repeat sends, and fix or escalate the stated cause before sending again.
How to separate a receiver incident from a sender problem
AT&T-domain blocking can happen for normal reputation reasons too. A blocklist or blacklist issue, missing reverse DNS, a broken DKIM selector, a new IP with poor warmup, or a complaint spike can produce delivery failures. Passing SPF, DKIM, and DMARC confirms authenticated identity, but it does not override IP reputation, recipient complaints, or sending behavior. The diagnosis also depends on whether the receiver rejected the connection, deferred the message, or accepted it and filtered it later.
Find the layer where the failure happened. Start with the raw bounce, not a dashboard summary. The exact SMTP code, enhanced status code, recipient domain, sending IP, HELO name, timestamp, remote host, and queue ID help distinguish a connection block from an IP reputation or message policy decision. A public blocklist check cannot rule out a receiver's private blacklist.
Receiver-side incident
- Many unrelated senders fail at the same receiver during the same window.
- Only certain IPs fail, even when adjacent mail streams are clean.
- Collect affected IPs, escalate through the current receiver path, and retest.
Sender-side issue
- One domain, list, campaign, or sending source has the highest failure rate.
- Failures follow one authentication path, IP pool, or content stream.
- Repair DNS, reduce risky mail, handle complaints, and request review.
Illustrative SMTP bounce cluestext
550 5.7.1 Connections not accepted from 203.0.113.10
553 5.3.0 DNSBL:RBL 521<203.0.113.10>_is_blocked
421 4.7.0 Temporarily deferred by receiving system
550 5.7.1 Reverse DNS missing or mismatched
If the bounce references a listed IP, start with blocklist monitoring and check whether the IP or sending domain appears on public blocklists (blacklists). If the bounce references DNS or identity, check SPF, DKIM, DMARC, PTR, and HELO before asking the receiving team to recheck the sender.
?
What's your domain score?
Deep-scan SPF, DKIM & DMARC records for email deliverability and security issues.
How the 2023 AT&T block was resolved
The reported path to recovery was evidence-led escalation. Senders narrowed the issue to AT&T, gathered affected IPs, and had those IPs checked. Reports said most delivery recovered after the weekend issue cleared, with some mail streams recovering by Monday morning Pacific time. The reports do not establish one exact remediation time for every sender.
Receiving teams need exact data. A request that only says "our mail is blocked" gives them little to search. Sender IPs, affected recipient domains, full bounce text, timestamps with a time zone, message counts, and examples make a false block easier to investigate.
- Confirm the scope by grouping affected recipient domains by live MX records and comparing remote hosts and bounce patterns.
- Collect sending IPs, domains, timestamps with time zones, and exact SMTP responses.
- Verify SPF, DKIM, DMARC, reverse DNS, HELO identity, and public blocklist status.
- Escalate through the route named by the live bounce. Use abuse_rbl@abuse-att.net only for a current AT&T-operated DNSBL/RBL rejection or an explicit instruction in that response.
- Retest with controlled mail after the block clears and watch the next production send.
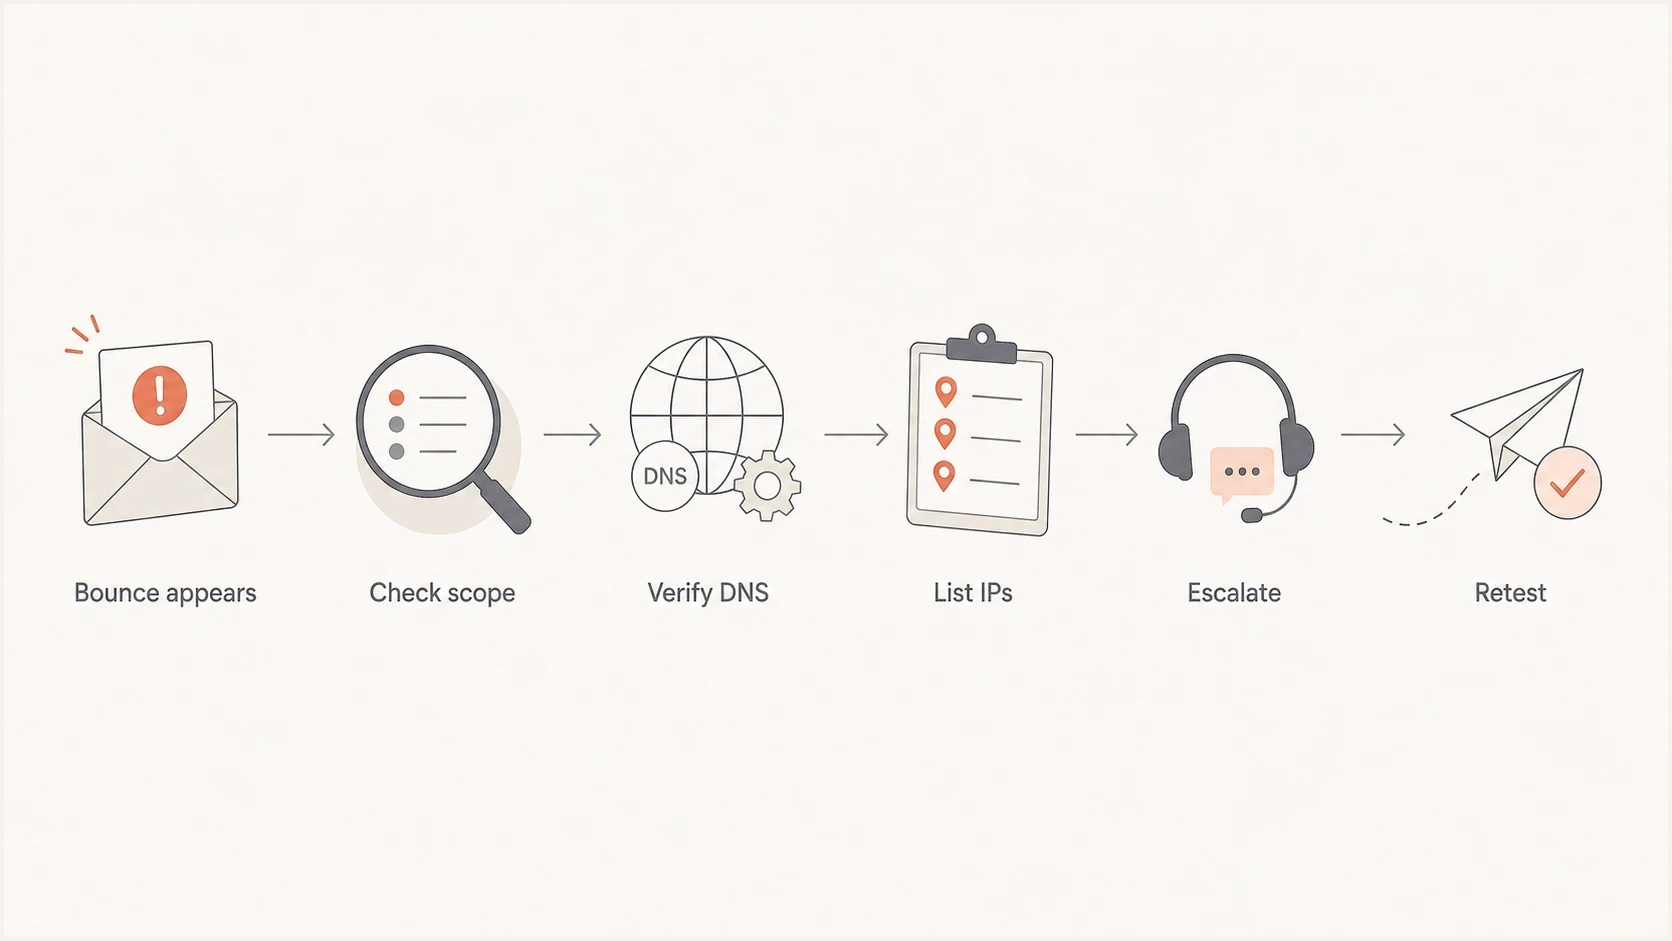
AT&T email block resolution flowchart with bounce review, DNS checks, IP escalation, and retesting.
For AT&T-specific next steps, document the evidence and follow the route identified by the live MX records and bounce. The guide to AT&T blocklist removal covers the request format in more detail, including the IP and SMTP data to provide.
What to check before escalating an AT&T block
Even when the timing points to a receiver incident, check the sender's own configuration. Receiver incidents and local sender problems can overlap. If a domain has broken DKIM or a sending IP has no reverse DNS, the receiver has a separate reason to reject or defer mail.
Check DNS authentication, IP identity, reputation status, and recent sending behavior. Use a domain health check for domain-level basics, then send a real message through an email tester to inspect the actual headers and authentication outcome.
|
|
|
|---|---|---|
SPF | Envelope sender is authorized | Unauthorized sending IP |
DKIM | Valid signature | Missing or invalid selector |
DMARC | Aligned SPF or DKIM passes | No aligned pass |
PTR and HELO | Valid reverse DNS and HELO | Missing or invalid identity |
Blocklists | No relevant public listing | Sending IP or domain listed |
Compact pre-escalation checklist.
Illustrative DNS records to validatedns
_dmarc.example.com. 3600 IN TXT "v=DMARC1; p=none; rua=mailto:d@example.com"
example.com. 3600 IN TXT "v=spf1 include:send.example.net -all"
s1._domainkey.example.com. 3600 IN TXT "v=DKIM1; k=rsa; p=MIIB..."
Avoid changes that complicate diagnosis
When evidence points to a receiver-side incident, avoid emergency DNS edits, sudden IP moves, or aggressive retry bursts. Those changes can create a second problem after the original block clears.
- Throttle failed queues so the receiving gateway does not see repeated pressure.
- Use backup routes only when they are warmed and authenticated.
- Fix clear DNS errors, but leave working records in place.
Where Suped fits
Suped is our DMARC and email authentication platform. During an AT&T-domain blocking incident, teams can compare DMARC results, sending source IPs, DNS changes, and blocklist or blacklist status in one workflow. That helps identify affected sources before assembling bounce evidence for the receiver.
Use Suped to confirm which sources passed authentication before the block started, flag domains with separate SPF or DKIM problems, and preserve IP status changes alongside bounce evidence. Its alerts and issue steps support the decision to fix a sender-side problem or prepare a receiver escalation packet.
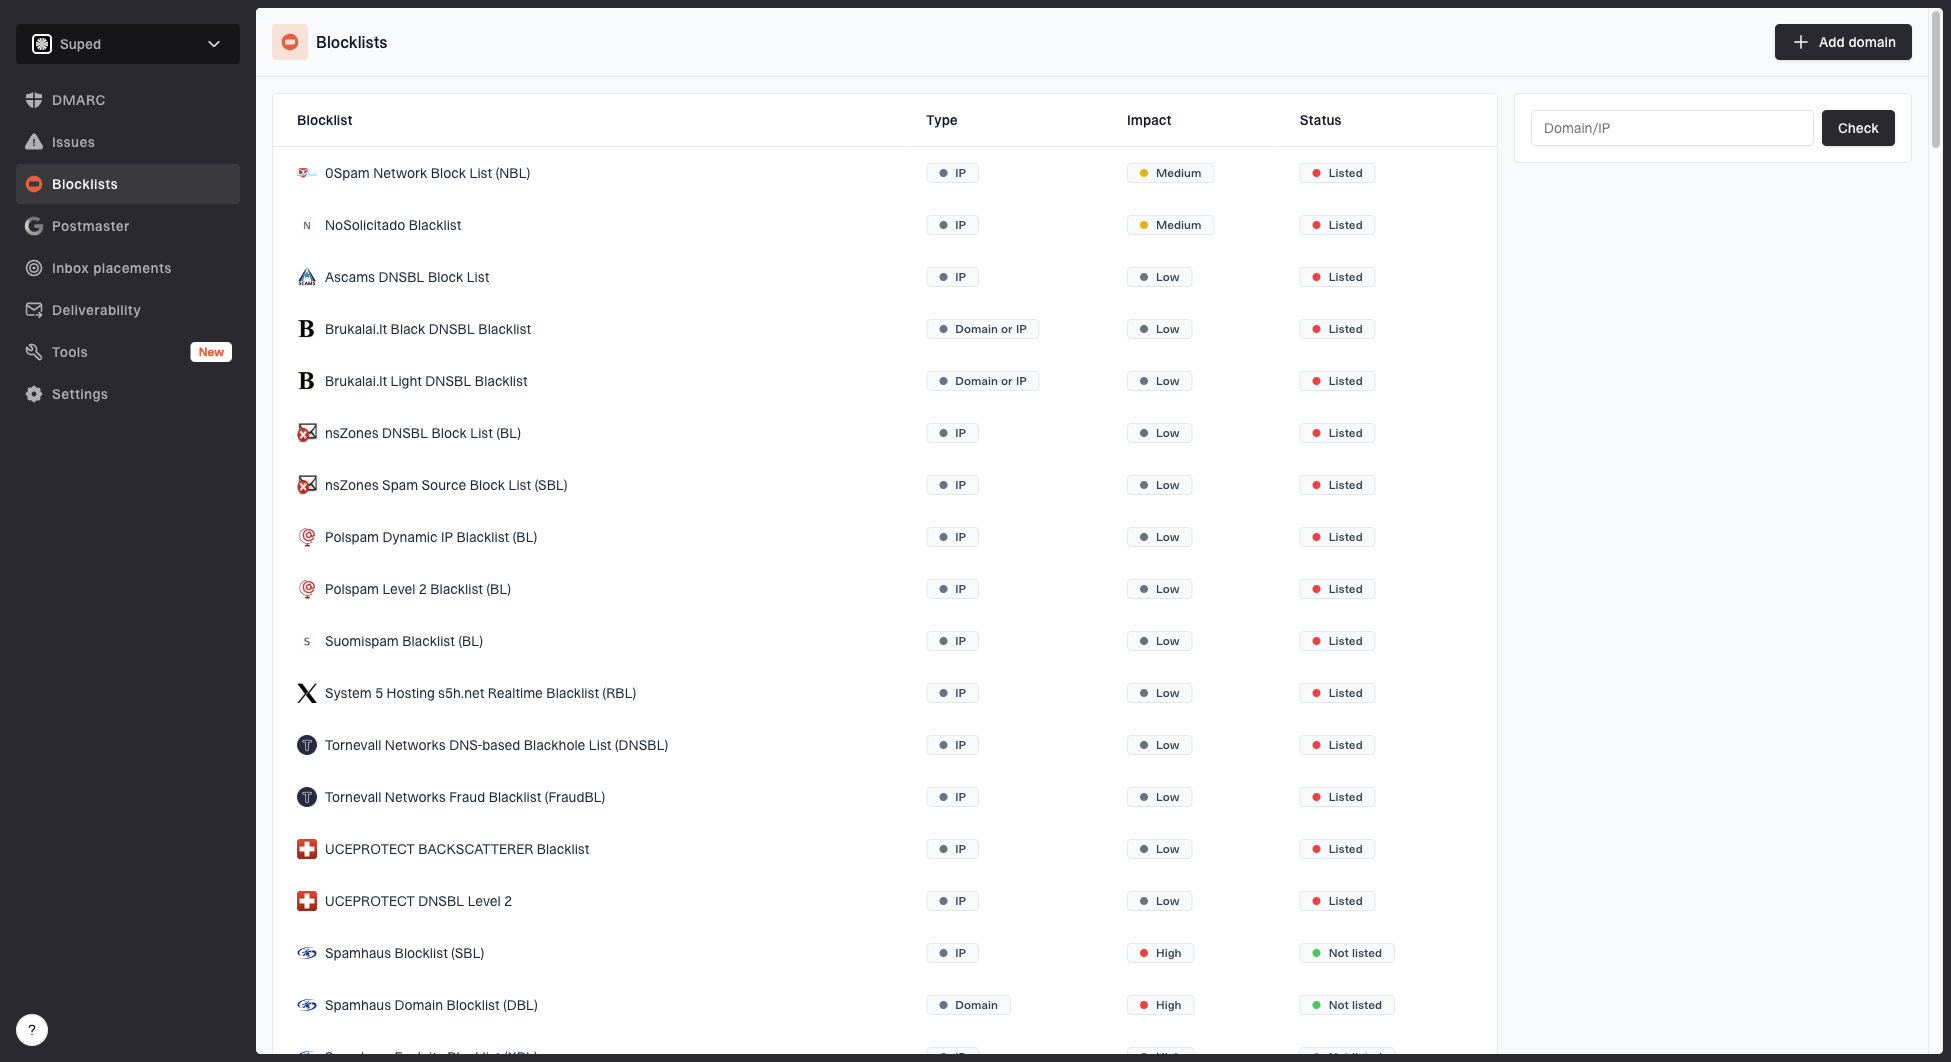
Blocklist monitoring page showing domain and IP checks across blocklists with importance and status
For agencies and managed service providers, the multi-tenant view supports cross-client comparison. If several clients report AT&T-domain blocks at the same time, an MSP can compare domains, sources, policies, and reputation signals. A shared receiver-side event can become apparent while a separate local problem remains visible.
Blocklist checker
Check your domain or IP against 144 blocklists.





What to include in an escalation packet
Keep the escalation packet short and complete. Send the facts that let the receiving side search logs and identify the block. A long campaign history can follow if the receiving team asks for it.
AT&T publishes abuse_rbl@abuse-att.net for its DNSBL blocklist or blacklist decisions, but that historical route is not the default for Yahoo-routed consumer domains. Follow the current MX host and SMTP response. The broader blocklists context still matters because a receiver can use internal reputation even when public blocklist checks are clear.
Include these fields
- List affected sender IPs and state whether each is dedicated or shared. If the IP is shared, ask the sending provider to investigate its pool.
- Include the visible From domain, envelope sender domain, and HELO name.
- Paste exact SMTP responses with timestamps, time zones, remote hosts, and recipient domains.
- State SPF, DKIM, and DMARC results from a current test message.
- Show recent recipient volume and whether retries were throttled.
After the receiving team confirms or clears the issue, monitor several sending cycles. A recovered receiver can still reveal a separate domain-level issue when delayed queues drain.
Views from the trenches
Best practices
Keep raw AT&T bounces with sender IPs, recipient domains, exact times, and SMTP text.
Compare affected IPs across clients before changing DNS, routing, or sending volume.
Throttle retries during receiver incidents so queues do not increase suspicion or load.
Retest after clearing with small seeded messages before resuming normal production sends.
Common pitfalls
Assuming every AT&T block is sender reputation without checking shared incident timing.
Sending vague postmaster requests that omit sender IPs, bounces, times, and domains.
Changing working SPF, DKIM, or DMARC records during a temporary receiver-side issue.
Ignoring partial impact when only some dedicated IPs are blocked and others pass cleanly.
Expert tips
Separate AT&T-side failures from downstream filtering before escalating the case.
Keep a living incident sheet with IPs, bounces, owners, timestamps, and current status.
Pair public blocklist checks with live message tests to avoid false confidence in reviews.
Record the recovery time so future AT&T spikes can be compared quickly with prior data.
Marketer view
Marketer from Email Geeks says the strongest clue was that unrelated clients on different platforms saw AT&T blocks during the same weekend.
2023-07-31 - Email Geeks
Marketer view
Marketer from Email Geeks says the impact was uneven, with some clients blocked on only certain IPs while other mail streams stayed clean.
2023-07-31 - Email Geeks
Frequently asked questions
The reported pattern pointed to an AT&T-side filtering issue rather than a universal DMARC failure. Check DMARC on affected mail because a failed aligned identity can give the receiver a separate reason to reject it.
Receiver filters can make decisions by sending IP. Reports described some dedicated IPs being affected while others stayed clear, so the exact IP list mattered.
Move traffic only to warmed, authenticated infrastructure after identifying the cause. An untested IP move can create a new reputation problem while the original block remains unresolved.
Send affected sender IPs, domains, timestamps with time zones, exact SMTP bounce text, remote hosts, recipient domains, authentication results, and recent volume. If the IP is shared, involve the sending provider.
Run controlled test sends, check for accepted SMTP responses, review authentication results, and monitor the next production send for deferrals and hard bounces.
Yahoo announced direct MX routing for AT&T consumer domains in June 2025. For a current rejection, check the live MX record and remote host because the receiving system determines the escalation path.