Is it possible to point one subdomain to multiple email service providers?
Updated on 1 Nov 2026: We clarified DNS delegation and SPF setup for multiple ESPs, with checks for reply routing and migration timing.
Yes, it is possible to use one visible sending subdomain with more than one email service provider. One exact DNS hostname cannot have two ESP-owned CNAME targets. Share the visible From subdomain with distinct DKIM selector sets and separate bounce hosts. Give each ESP a separate tracking hostname if tracking is enabled, and check SPF at its actual MAIL FROM domain.
Start by asking which name the ESP means by "subdomain". ESP setup screens often use sending domain, sender domain, MAIL FROM, return path, bounce domain, tracking domain, and DKIM domain as if they are one thing. These labels describe different roles, although several refer to the same hostname. Once those names are separated, the answer gets much less confusing.
Fast answer
- Visible From: One subdomain can appear in the visible From address at two ESPs if authentication is set up cleanly.
- Bounce host: One exact bounce or return-path hostname should belong to one ESP, not two.
- DKIM selectors: Each ESP can use its own selector set under the same signing domain, including selectors for key rotation.
- SPF record: One SPF record can authorize multiple ESPs, but duplicate SPF records at one name return permerror.
- DMARC policy: One DMARC policy record applies to both ESPs at a given _dmarc hostname; duplicate policy records are discarded.
What pointing means in email
The word "pointing" causes most of the confusion. In DNS, it usually means a CNAME, MX, TXT, or other record at a specific hostname. In an ESP onboarding screen, it can mean branding the visible From domain, delegating bounce handling, publishing DKIM keys, adding an SPF include, or setting a click tracking host. Those are different operations.
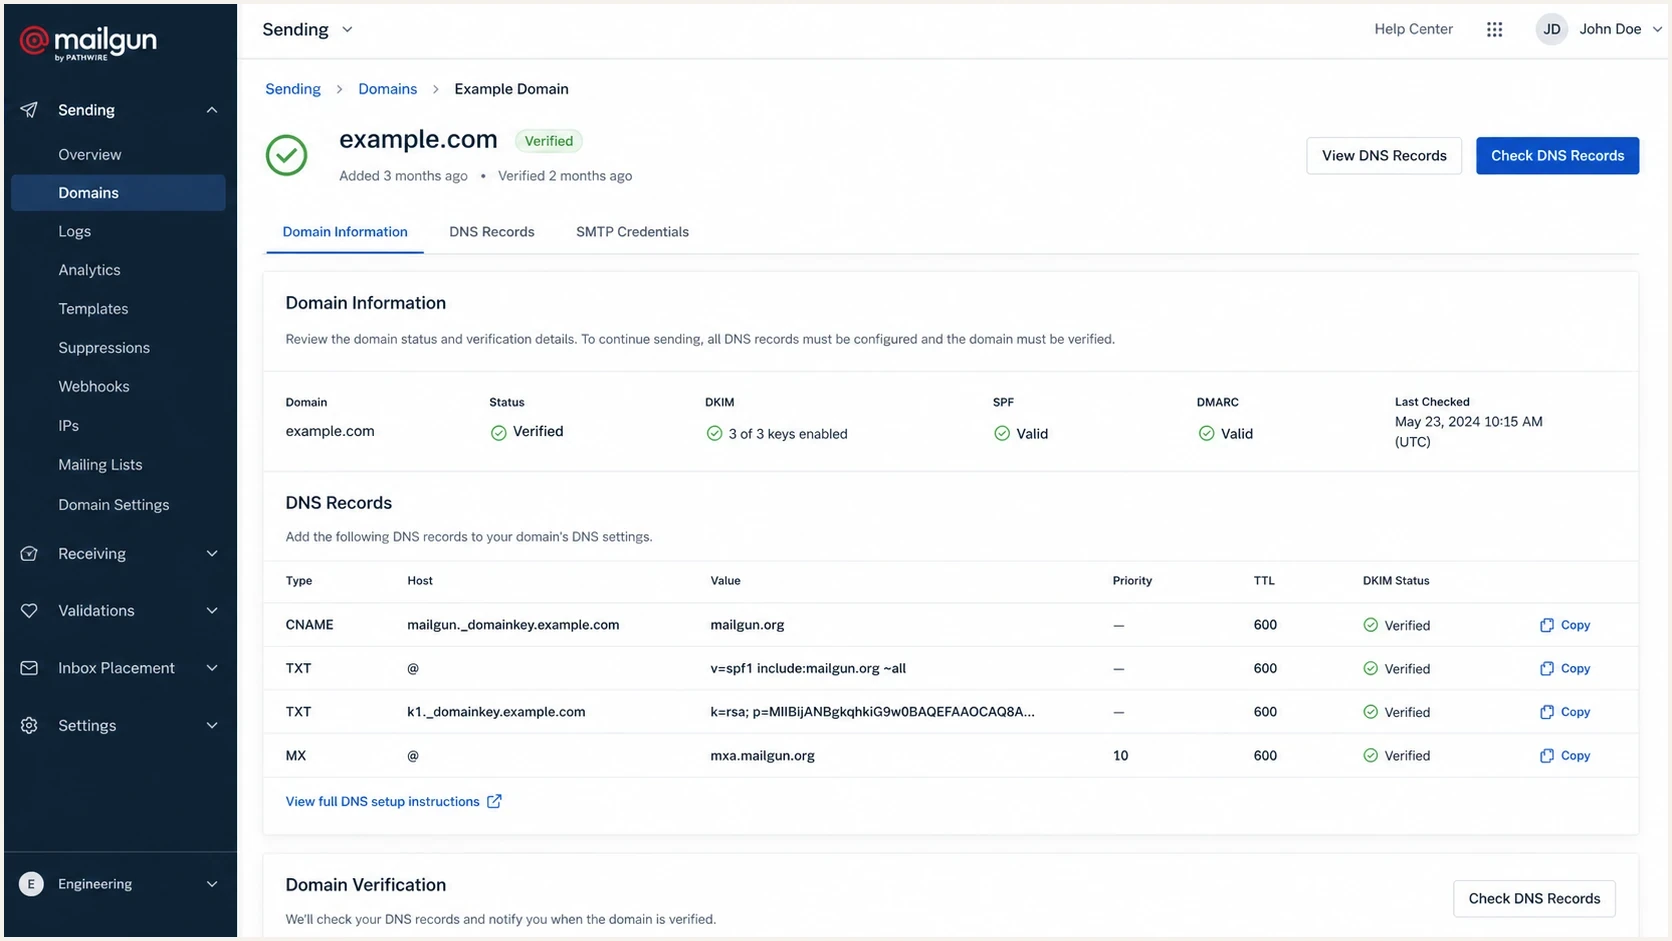
Mailgun DNS verification screen for an email subdomain with CNAME, TXT, MX, and DKIM records.
A real ESP verification screen makes this clearer because it asks for several records, not one universal pointer. The sending identity can be the same, while the bounce and tracking names stay different. The wrong setup happens when both ESPs demand the same hostname for their own CNAME or MX record.
|
|
|
|---|---|---|
From domain | Visible sender | Yes, with SPF or DKIM alignment |
Bounce domain | Return handling | No, use separate hosts |
DKIM selector | Signature key | Different selectors under one domain |
SPF include | Sender authorization | Yes, in one record |
Tracking domain | Click and open branding | No, use separate hosts |
Common ESP labels and whether they can be shared
The DNS rule that creates the conflict
DNS is keyed by name and record type. Under RFC 2181, a CNAME owner name has one target and cannot also hold ordinary MX, TXT, A, or AAAA records. That is why one exact bounce host or tracking host cannot be handed to two independent ESPs by adding conflicting CNAMEs. Separate hostnames avoid the collision.
Conflicting CNAME setupDNS
# This is not a workable setup.
mail.news.example.com. 300 IN CNAME esp-a.example.net.
mail.news.example.com. 300 IN CNAME esp-b.example.net.
Subdomains do not inherit SPF authorization. Check whether the envelope sender domain needs its own SPF record, and publish DKIM selectors under the d= signing domain. DMARC first checks _dmarc at the visible From domain. Without a valid policy there, RFC 9989 specifies a DNS tree walk to discover the applicable policy. A separate subdomain DMARC record is optional when an applicable parent policy already covers it.
Same hostname
- CNAME conflict: Two ESP-owned CNAME targets at one hostname do not work.
- Bounce conflict: Two ESPs cannot both process failures for one return-path host.
- TXT conflict: Two separate SPF records at one name cause an SPF error.
Separate hostnames
- Clean routing: Each ESP gets its own bounce and tracking name.
- Clean DKIM: Each ESP publishes a different selector under the sender domain.
- Clean SPF: All authorized senders are combined into one SPF record where needed.
Separate bounce hosts with provider-managed CNAMEsDNS
# Illustrative only. Use CNAMEs only when supplied by each ESP.
bounce-a.news.example.com. 300 IN CNAME esp-a.example.net.
bounce-b.news.example.com. 300 IN CNAME esp-b.example.net.
Check who controls the subdomain's DNS
Some ESPs request NS records instead of individual authentication records. NS delegation gives the designated nameservers authority for news.example.com and its descendants. DKIM and bounce records beneath that name must be published in the delegated zone; adding them only to the parent example.com zone does not make them authoritative. RFC 1034 explains this boundary between parent and child zones.
- Keep DNS under your control and publish each ESP's individual records when both providers support that setup.
- If one ESP already hosts the delegated zone, ask it to publish the second ESP's records, or use a separate subdomain. Confirm that the provider permits a shared From domain.
All authoritative nameservers for a zone must provide consistent records. Adding nameservers from a second ESP does not merge their DNS records. If the provider cannot publish the required records, give the new ESP a separate subdomain rather than replacing the live delegation.
When changing the bounce domain helps
Changing the bounce domain is the real caveat behind the "use two ESPs" answer. It is the normal way to let a second ESP send mail for the same visible From subdomain without taking over the first ESP's return handling.
A workable split
The second ESP can send as news.example.com when its verified DKIM d= value matches that domain exactly, or shares its organizational domain under relaxed alignment. SPF can provide a pass with identifier alignment when the verified MAIL FROM domain satisfies the active DMARC alignment mode. The second ESP still needs its own bounce hostname, such as bounce2.news.example.com.
Do not approve an ESP change until the complete record list is visible. If the request is "add another provider to the same sending domain," that is often fine. If the request is "reuse the same return-path CNAME," that fails.
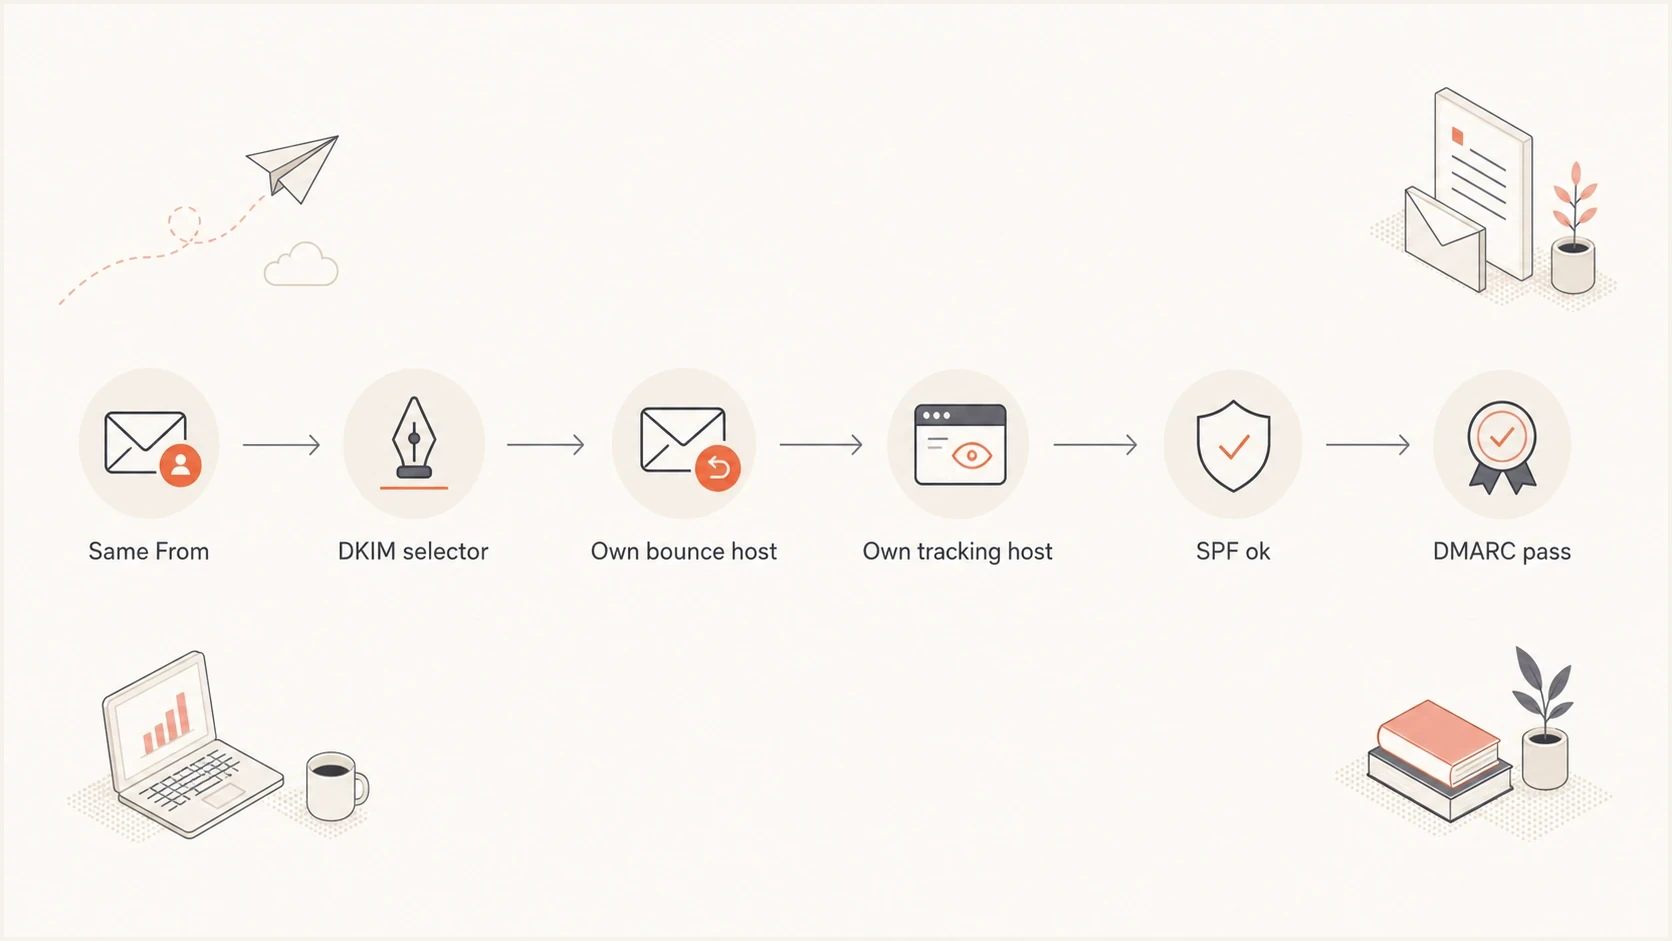
Flowchart for sharing one From subdomain across two ESPs with DKIM, bounce, tracking, SPF, and DMARC checks.
If the visible From address uses a different From domain than the return path, DMARC still needs an SPF or DKIM pass with identifier alignment. In practice, DKIM is usually the easiest way to share the visible From subdomain because each ESP can publish a unique selector.
Two DKIM selectors under one sender subdomainDNS
s1._domainkey.news.example.com. 300 IN CNAME s1.esp-a.example.
s2._domainkey.news.example.com. 300 IN CNAME s2.esp-b.example.
# Publish every selector the ESP supplies for key rotation.
# Two ESPs must not publish different keys at the same selector name.
How DMARC alignment works across ESPs
Each message needs at least one authenticated identifier with alignment to the visible From domain. DKIM compares the verified d= signing domain. SPF compares the verified MAIL FROM domain, not the visible From address and not the tracking hostname. Configure both mechanisms where the ESP permits it, then confirm that at least one result has both authentication and identifier alignment.
Relaxed alignment accepts domains with the same organizational domain. Strict alignment requires an exact domain match. A return path such as bounce.news.example.com has relaxed SPF alignment with news.example.com, but it fails strict alignment. A DKIM signature using d=news.example.com has alignment in either mode when the visible From domain is news.example.com.
|
|
|
|---|---|---|
DKIM | d=news.example.com | d=esp.example.net |
SPF, relaxed | MAIL FROM bounce.news.example.com | MAIL FROM esp.example.net |
SPF, strict | MAIL FROM news.example.com | MAIL FROM bounce.news.example.com |
DMARC paths for a visible From domain of news.example.com
Keep one DMARC policy record
Both ESPs use the same DMARC policy for a given _dmarc hostname. Do not publish one DMARC TXT record per provider because multiple policy records at one target are discarded. Use one policy record, then separate the providers in aggregate reporting by source IP and authentication identifiers.
An ESP's domain verification badge only confirms the checks that provider performed. Send a real message through each stream and inspect the From, Return-Path, DKIM-Signature, and the receiving server's Authentication-Results headers. DMARC aggregate reports then show whether receivers see the same authentication and alignment results at normal traffic volume.
SPF when several ESPs send
SPF is another place where people think they are pointing a whole subdomain to a provider. SPF only authorizes servers for the domain used in the envelope sender. If two ESPs use the same MAIL FROM domain, both ESPs must be authorized in one SPF record at that domain. Other verification TXT records can coexist at that name; the conflict is multiple records beginning v=spf1. When combining include-based policies, keep one all mechanism at the end rather than concatenating complete SPF records.
One SPF record for a shared MAIL FROM domainDNS
news.example.com. 300 IN TXT (
  "v=spf1 include:esp-a.example "
  "include:esp-b.example -all"
)
The two quoted strings in this zone-file example form one TXT record. In a DNS control panel, enter one combined value unless the provider asks otherwise. Replace both example includes with the values supplied by the ESPs.
With separate bounce domains, each domain has its own SPF evaluation. Publish the provider's MX and SPF TXT records where required, or its supplied CNAME if SPF is hosted at the target. Do not add TXT beside that CNAME. The visible From domain's SPF record does not cover a different envelope sender.
Before adding another sender, run an SPF checker on the exact bounce or MAIL FROM domain. That catches duplicate SPF records that return permerror, missing includes, and records that already sit near the lookup limit. RFC 7208 limits evaluated DNS lookup terms to 10, including nested includes; ip4, ip6, and all do not consume that term budget.
SPF lookup pressure
Count evaluated include, a, mx, ptr, exists, and redirect terms, including nested includes. Only the 10-term cap is a protocol limit; the lower bands are planning guidance.
Working margin
0-5 terms
Some room remains, but nested evaluation still needs testing.
Near the limit
6-10 terms
Review every include before adding another sender.
Over the limit
More than 10
SPF evaluation exceeds the permitted term count.
SPF checker
Find SPF syntax issues, lookup limits, and weak records.
?/16tests passed
When provider changes make direct DNS editing risky, Hosted SPF in Suped's product keeps a stable public reference while authorized sources are managed in Suped. Suped's SPF flattening can reduce lookup-causing include chains. Validate the published result after every sender change.
Recommended setup patterns
A reliable setup is explicit: use one visible From subdomain if the brand needs it, separate operational hostnames for each ESP, and one monitored authentication policy. Bounce and tracking names can appear in message headers or links, so use recognizable names.
|
|
|
|---|---|---|
One From | Brand needs one sender | Needs clean DKIM |
ESP subdomains | Providers need CNAMEs | More DNS names |
Separate From | Teams need isolation | More visible domains |
Hosted SPF | Sender list changes | Needs delegated control |
Practical patterns for one subdomain and multiple ESPs
Separate bounce hosts using MX and SPF TXT recordsDNS
# Illustrative only. Replace targets with each ESP's supplied records.
s1._domainkey.news.example.com. 300 IN CNAME s1.esp-a.example.
s2._domainkey.news.example.com. 300 IN CNAME s2.esp-b.example.
bounce-a.news.example.com. 300 IN MX 10 feedback.esp-a.example.
bounce-a.news.example.com. 300 IN TXT "v=spf1 include:esp-a.example -all"
bounce-b.news.example.com. 300 IN MX 10 feedback.esp-b.example.
bounce-b.news.example.com. 300 IN TXT "v=spf1 include:esp-b.example -all"
This example uses direct MX and TXT records at each bounce hostname. For CNAME-based bounce setups, publish the supplied CNAME instead of adding MX or TXT at that same name. The visible From domain does not need another SPF include for these streams merely because it appears in the From header.
SPF flattening drawer showing an over-limit record, sender editing, lookup counts, and the hosted record setup
In Suped, our DMARC reporting platform, review both ESP sources and confirm SPF or DKIM with identifier alignment for each mail stream. Mark legitimate sources as verified so Suped tracks their authentication issues and sends alerts. Use Hosted SPF when authorized senders change often, then validate the published result before retiring old DNS records.
Migration checklist
A second ESP should be added like a migration, even when the first ESP stays live. Do not start with DNS edits. Start with an inventory of every hostname the current ESP uses, then compare that list against the new ESP's required records. If a cutover will replace existing records, lower their TTL in advance and wait for the previous TTL to expire before the change.
- Inventory: List the visible From domain, DKIM selectors, bounce host, tracking host, SPF name, and DMARC name. Record any NS delegation and who controls the authoritative zone.
- Ask: Ask which records are required and which names are customizable. Confirm that both ESPs support the shared From domain and can supply distinct DKIM selector sets.
- Separate: Give the new ESP unique bounce and tracking hostnames before touching the existing provider.
- Check: Review SPF lookup practices before adding another include.
- Verify: Send through each ESP, inspect the From, Return-Path, DKIM-Signature, and Authentication-Results headers, and confirm at least one SPF or DKIM pass with identifier alignment. Test the Reply-To mailbox and a controlled bounce to confirm that replies and delivery failures reach the intended systems.
- Monitor: Use a domain health checker after the records are live, then review DMARC aggregate reports for both sources.
Do not skip the hostname inventory
The most common mistake is approving a new ESP's DNS checklist without noticing that a current ESP already owns the same bounce or tracking hostname. That change can break bounce processing, link tracking, SPF, or DKIM verification for the existing mail stream.
Keep the old ESP's authentication and bounce records until its queued messages and retries have finished. Keep tracking hosts active for links in previously sent messages. DNS cache expiry alone does not mean those records are safe to remove.
Inbound mail and other DNS edge cases
Inbound mail is a different question. A subdomain can have its own MX records, and those MX priorities do not interact with the parent domain's MX records. Multiple MX records at one exact domain apply to the whole recipient domain, so they cannot split user1@news.example.com to one mailbox provider and user2@news.example.com to another by themselves.
Lower MX preference numbers are tried first; higher numbers are fallback destinations. Equal-priority MX records can distribute connections, but neither arrangement routes selected recipients to different mailbox providers. Both providers need to accept or route every intended recipient. Use split-domain routing with an explicit recipient map when two mailbox platforms must coexist. Copying messages with IMAP does not configure incoming mail routing. These MX selection rules are defined in RFC 5321.
Human replies normally go to Reply-To when it is set, otherwise to the visible From address. Give that recipient domain MX records for the mailbox service that will receive replies. The return-path domain handles delivery failures, and its MX records are separate when it uses another hostname. Website hosting is separate too: A or AAAA records can direct web traffic to one host while MX records at the same name direct incoming mail elsewhere, provided that name is not a CNAME.
Tracking domains are also separate from authentication. If one ESP uses click.news.example.com for branded links, the second ESP should use a different tracking host. A tracking CNAME does not prove SPF, DKIM, or DMARC is correct.
Use separate sender subdomains when isolation matters
For marketing, transactional mail, product notifications, and one-off campaigns, separate sender subdomains reduce operational risk. If one team changes an ESP, the other streams keep their own DKIM selectors, bounce handling, SPF policy, and DMARC reporting path. Separate subdomains do not guarantee separate sender reputation; receivers also assess related domains and sending IPs.
The main exception is brand consistency. If a company insists that all customer-facing mail comes from one subdomain, make DKIM the primary authentication path and keep every ESP's operational hostnames separate.
Views from the trenches
Best practices
Use one visible From subdomain, but give each ESP its own DKIM selector and bounce host.
Keep one SPF record per name and check lookup count before adding another ESP include.
Document each ESP's terms for From, Return-Path, bounce, tracking, and DKIM hostnames.
Common pitfalls
Putting two CNAME targets on one hostname breaks DNS instead of sharing traffic cleanly.
Letting two ESPs reuse one bounce domain creates SPF matching and return handling errors.
Mixing unrelated mailbox providers in one MX set causes delivery errors and lost replies.
Expert tips
Use separate bounce subdomains so each ESP can route delivery failures to its own system.
Confirm the new ESP passes DMARC and let queued mail finish before removing old DNS records.
Ask every ESP which exact hostnames require CNAME, TXT, MX, or DKIM selector records.
Marketer view
Marketer from Email Geeks says one exact subdomain cannot be handed to two ESP-owned CNAME targets at the same time.
2021-10-06 - Email Geeks
Marketer view
Marketer from Email Geeks says the cleaner pattern is to create a second operational subdomain for the new ESP.
2021-10-06 - Email Geeks
Frequently asked questions
Yes. Each ESP needs a distinct DKIM selector set and usually its own return-path or bounce subdomain. Publish every selector required for key rotation. DMARC passes when at least one verified SPF or DKIM identifier has alignment with the visible From domain.
No. A bounce domain normally points to one ESP using CNAME or MX records. Give each ESP a separate bounce host such as bounce-a.news.example.com and bounce-b.news.example.com.
Yes, when both ESPs use the same MAIL FROM domain. Add their authorization terms to one SPF record and stay within the 10 evaluated DNS lookup term limit, including nested includes. Separate MAIL FROM domains have separate SPF records or provider-managed CNAMEs. Multiple SPF records at one name return permerror.
MX priority is for receiving mail and fallback. A subdomain can have its own MX records, separate from the parent domain, but multiple MX records at one exact domain do not split different recipient addresses between mailbox providers. Use separate subdomains or split-domain routing through an inbound gateway.
Ask which exact hostnames the ESP needs for DKIM, Return-Path, tracking, DMARC reporting, and SPF. Check existing records and NS delegation, confirm that the provider permits a shared From domain, and keep one DMARC policy record per name. Verify authentication plus identifier alignment in a real test message.