Is domain authentication required for all Mailchimp senders after Gmail and Yahoo changes?
Updated on 20 Oct 2026: We clarified Mailchimp authentication requirements, SPF and DKIM alignment, and the checks to complete before your next campaign.
No, custom domain authentication is not mandatory for every Mailchimp Marketing sender. Bulk senders using their own From domain need custom authentication to meet Gmail and Yahoo requirements. Gmail requires all senders to use SPF or DKIM, while bulk senders must use SPF, DKIM, and DMARC. Yahoo has comparable all-sender and bulk-sender requirements but does not publish a numeric bulk threshold. Mailchimp recommends authenticating every owned custom sending domain and publishing DMARC. Mailchimp Transactional requires authentication before sending transactional email to external recipients.
The practical setup is stricter than the minimum provider rule. Domain verification confirms access to the From address, while custom authentication lets Mailchimp apply aligned DKIM for the brand's domain. Even below Gmail's bulk threshold, aligned DKIM reduces authentication failures. A DMARC record with a working reporting address helps expose unauthorized sources and prepares the domain for higher volume.
- Marketing sends: Mailchimp requires verification for applicable From addresses and recommends custom authentication for every owned domain.
- Transactional sends: Mailchimp Transactional requires authenticated domains before sending to outside recipients.
- Bulk classification: Gmail aggregates traffic across the same primary domain, while Yahoo uses an undisclosed significant-volume threshold.
- Best next step: Authenticate first, send tests, then review real DMARC results before the next large campaign.
What changed for Mailchimp senders
Gmail and Yahoo began enforcing their sender requirements in 2024. Gmail increased enforcement in November 2025, including temporary and permanent rejections of noncompliant traffic, according to Gmail's sender FAQ. Mailchimp's guidance directs large senders and companies using branded From domains to set up the right authentication. It also recommends moving away from free Gmail or Yahoo From addresses because a Mailchimp customer cannot authenticate a public domain it does not control.
Mailchimp separates domain verification from domain authentication. Verification proves that you can receive mail at the address. Authentication proves that Mailchimp has permission to sign mail using your domain. Mailchimp documents the current automatic and manual methods in its Mailchimp setup guide and summarizes the provider requirements in its Mailchimp sender update.
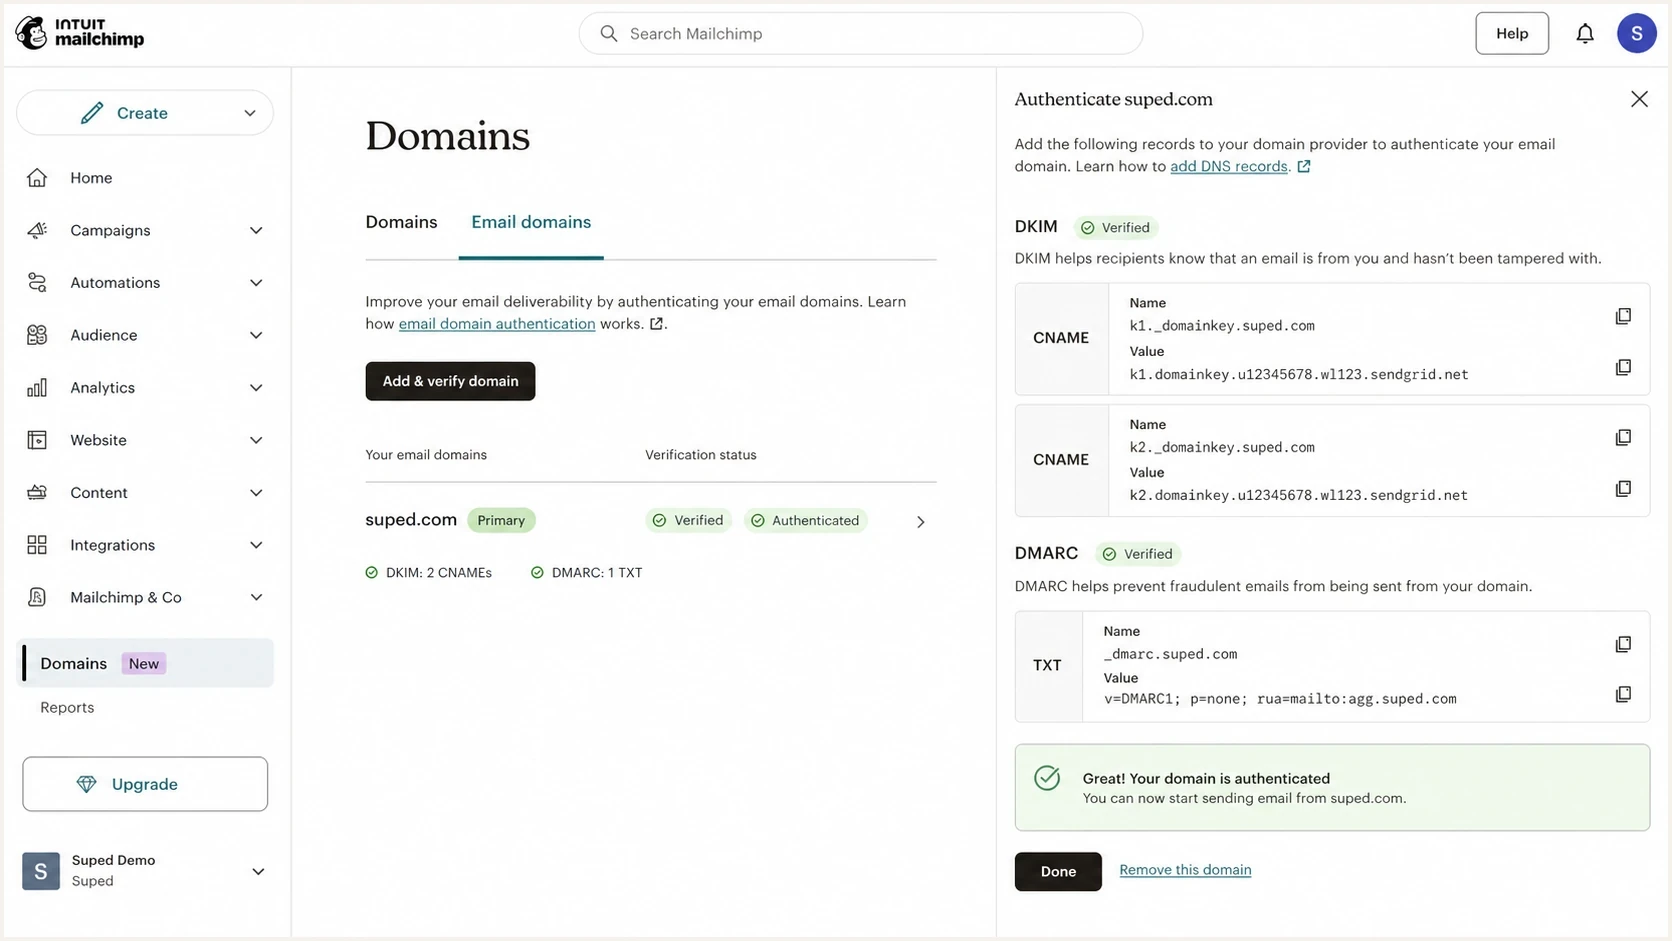
Mailchimp domain settings screen for verifying and authenticating a sending domain.
Do not treat 4,999 as a safe line
Gmail describes a bulk sender as one that sends around 5,000 messages or more to personal Gmail accounts within 24 hours. It combines messages sent by the same primary domain, including subdomains, and bulk-sender status does not expire after classification. Yahoo says it looks for significant volume but deliberately does not publish a number. The Gmail requirements apply to personal @gmail.com and @googlemail.com accounts, rather than Google Workspace recipients. Yahoo's sender FAQ confirms that Yahoo has no published bulk-sender cutoff.
- Gmail counting: Traffic using the same primary domain counts together, including subdomains and messages sent through other services, not just Mailchimp.
- Yahoo threshold: Yahoo uses more than volume to classify a bulk sender and does not disclose a fixed cutoff.
- Mailchimp controls: Mailchimp can prompt for authentication before a mailbox provider returns a rejection.
Authentication is only part of compliance
Passing authentication does not complete the Gmail and Yahoo checklist. Bulk marketing mail also needs DMARC alignment, a working one-click unsubscribe mechanism, a visible unsubscribe link in the message, and spam complaint rates below 0.3%. Gmail recommends staying below 0.1% so an occasional increase does not reach the enforcement limit.
|
|
|
|---|---|---|
Authentication | SPF or DKIM | SPF, DKIM, and DMARC |
DMARC alignment | Recommended | Required for the From domain |
Spam complaints | Keep below 0.3% | Keep below 0.3% |
Marketing unsubscribe | Mailchimp requires it for marketing mail | One-click header and visible link |
Core Gmail and Yahoo sender requirements relevant to Mailchimp campaigns.
Mailchimp supplies one-click unsubscribe handling for its marketing emails and requires an unsubscribe link in campaigns. Gmail requires the List-Unsubscribe and List-Unsubscribe-Post headers for RFC 8058 one-click unsubscribe; a footer link alone is insufficient. Gmail and Yahoo require unsubscribe requests to be honored within two days. Mailchimp describes its automatic handling in its sender requirements guidance. The sender still controls audience permission and the complaint rate. Authentication can pass while unwanted mail is filtered or rejected.
The Gmail sender guidelines also require TLS for transmission. Both Gmail and Yahoo require valid forward and reverse DNS (PTR records) for sending IPs and correctly formatted messages. Mailchimp manages its sending infrastructure; these requirements do not mean adding a PTR record to the domain used in your From address.
What Mailchimp needs in DNS
For normal Mailchimp Marketing sends, manual setup uses two Mailchimp DKIM CNAME records and one DMARC TXT record. Mailchimp manages SPF for its own sending domains, so customers should not add a Mailchimp SPF include unless Mailchimp specifically instructs them to do so. Aligned DKIM normally supplies the DMARC pass for the visible From domain. Copy the CNAME names and targets shown in your Mailchimp account. If DMARC is already published, check the existing policy instead of adding another record or replacing a stricter policy with p=none.
|
|
|
|---|---|---|
Domain verification | Email | You control the From address. |
Mailchimp DKIM | CNAME | Mailchimp can sign with your domain. |
DMARC policy | TXT | Publishes a requested policy for DMARC failures; rua requests aggregate reports. |
SPF path | Mailchimp managed | Mailchimp's envelope domain authorizes its sending IPs. |
Mailchimp authentication pieces and what each one proves.
For a domain without an existing DMARC policy, start with p=none while you confirm that Mailchimp and every other legitimate sender passes. This requests no quarantine or rejection based on DMARC; receivers still apply spam filtering. Aggregate reporting requires a working rua destination. A valid p=none policy meets the bulk-sender policy minimum, but each message still needs a DMARC pass. To create the record, use the Suped DMARC record generator.
Starter DMARC recordDNS
_dmarc TXT "v=DMARC1; p=none; rua=mailto:dmarc@example.com"
Replace the example reporting address with a working address for your domain. After publishing the TXT record, check that it resolves cleanly. Literal extra quote characters in the value, a duplicate DMARC record, or a DNS host value entered as _dmarc.example.com when the provider expects only _dmarc can keep Mailchimp stuck in pending status. A focused DMARC checker catches those mistakes before the next campaign.
DMARC checker
Look up a domain's DMARC record and catch policy issues.
?/7tests passed
Why SPF pass does not guarantee DMARC pass
SPF checks the envelope sender domain, usually visible in the Return-Path header. Normal Mailchimp Marketing campaigns use a Mailchimp domain for that address. SPF can therefore pass for Mailchimp without matching the domain in your visible From address. Custom DKIM supplies the domain alignment needed for your branded mail.
|
|
|---|---|
SPF and DKIM pass only for provider domains | Fail, because neither passing domain matches your From domain under the DMARC alignment rules. |
SPF passes for the provider; DKIM passes for your From domain | Pass through DKIM, even without SPF alignment. |
Illustrative results for a message that retains your branded From address.
In the received message, compare the DKIM signing domain (d=) with the From domain. Relaxed alignment accepts the same organizational domain; strict alignment requires an exact domain match. Gmail's sender guidelines require SPF and DKIM for bulk mail, but DMARC needs a pass through only one method with domain alignment. Adding a Mailchimp include to your own SPF record does not change the Return-Path or fix missing DKIM alignment.
Do you need to warm up after Mailchimp authentication?
Usually, no. Authenticating a domain in Mailchimp is different from moving to a new sending platform, changing the From domain, or switching to a dedicated IP. If the brand already sends Mailchimp campaigns from that domain, the list is engaged, and the daily send size stays similar, adding DKIM and DMARC alone does not require a separate warm-up.
Increase volume gradually when authentication accompanies a new sending identity or a substantial volume change. Clean stale lists and confirm subscriber permission before sending; a warm-up does not fix an unconsented audience. Authentication fixes identity. It does not erase complaint history or weak engagement. A stricter DMARC policy should be staged against report data, but it does not require a volume warm-up when legitimate mail already passes.
Warm-up decision bands
Base the pace on engagement, complaints, and delivery errors. These are decision categories, not fixed schedules.
No warm-up
Send normally
Same domain, same Mailchimp account, engaged list, similar volume.
Gradual ramp
Increase as results allow
New authenticated subdomain or a larger campaign than usual.
Reputation rebuild
Use a tailored plan
New brand domain, dedicated IP move, or major volume increase.
Authentication change
- Normal volume: Keep the next campaign close to recent daily patterns.
- Same audience: Use recent human clicks or other reliable engagement signals. Account for inflated open metrics.
- Same content: Avoid combining DNS fixes with an untested offer or a stale segment.
Reputation change
- New identity: Ramp when the From domain or sending subdomain is new.
- List quality: Clean stale segments and confirm permission before increasing volume.
- Policy shift: Stage quarantine or reject using DMARC reports, not a sending warm-up.
How to verify before sending a campaign
Publish the records, wait for DNS validation, then send a small campaign to a test segment containing only inboxes you control. Mailchimp says validation usually takes minutes but can take up to 48 hours in its setup guide. Confirm DKIM and DMARC pass at the receiver, with DKIM domain alignment for the visible From address. Passing authentication does not guarantee inbox placement.
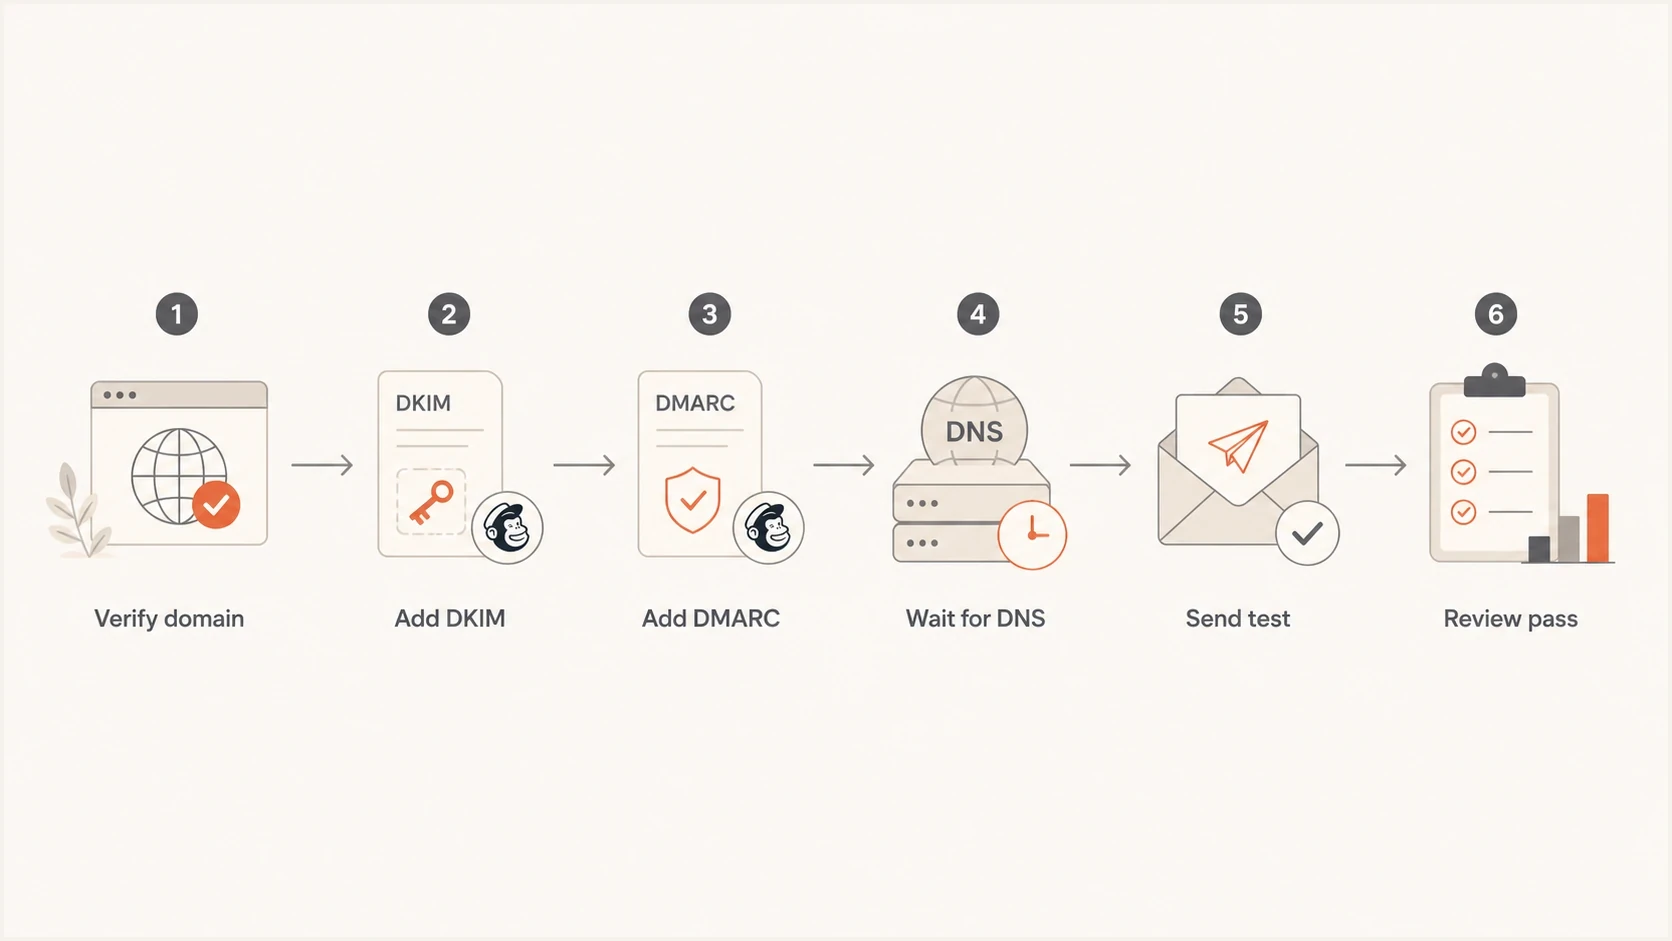
Flowchart for verifying Mailchimp DKIM and DMARC before sending.
- Confirm Mailchimp status: The domain should show verified and authenticated in the Mailchimp domains area.
- Query DNS: Check the two DKIM CNAME records and the DMARC TXT record outside Mailchimp.
- Send a test: Use the normal campaign workflow to send only to Gmail and Yahoo inboxes you control.
- Read results: Open the received message source, such as Show original in Gmail, and inspect Authentication-Results for DKIM pass and DMARC pass.
- Watch reports: Use aggregate DMARC data to confirm that Mailchimp is the source you expect.
What to check before approval
Confirm that a real message passes DMARC at the receiver, then check aggregate reports for Mailchimp traffic under the expected domain. After changing DNS providers, recheck the authentication records and keep the DKIM CNAME records in place. Authentication changes affect future messages; they do not repair mail already sent. Validate a fresh message before deciding whether a resend is appropriate.
If you are handling several sending domains, keep a checklist by domain and source. The same rules apply when you verify your setup; check the CNAME records Mailchimp displays for each domain instead of assuming another domain's values apply.
Monitor Mailchimp DMARC results with Suped
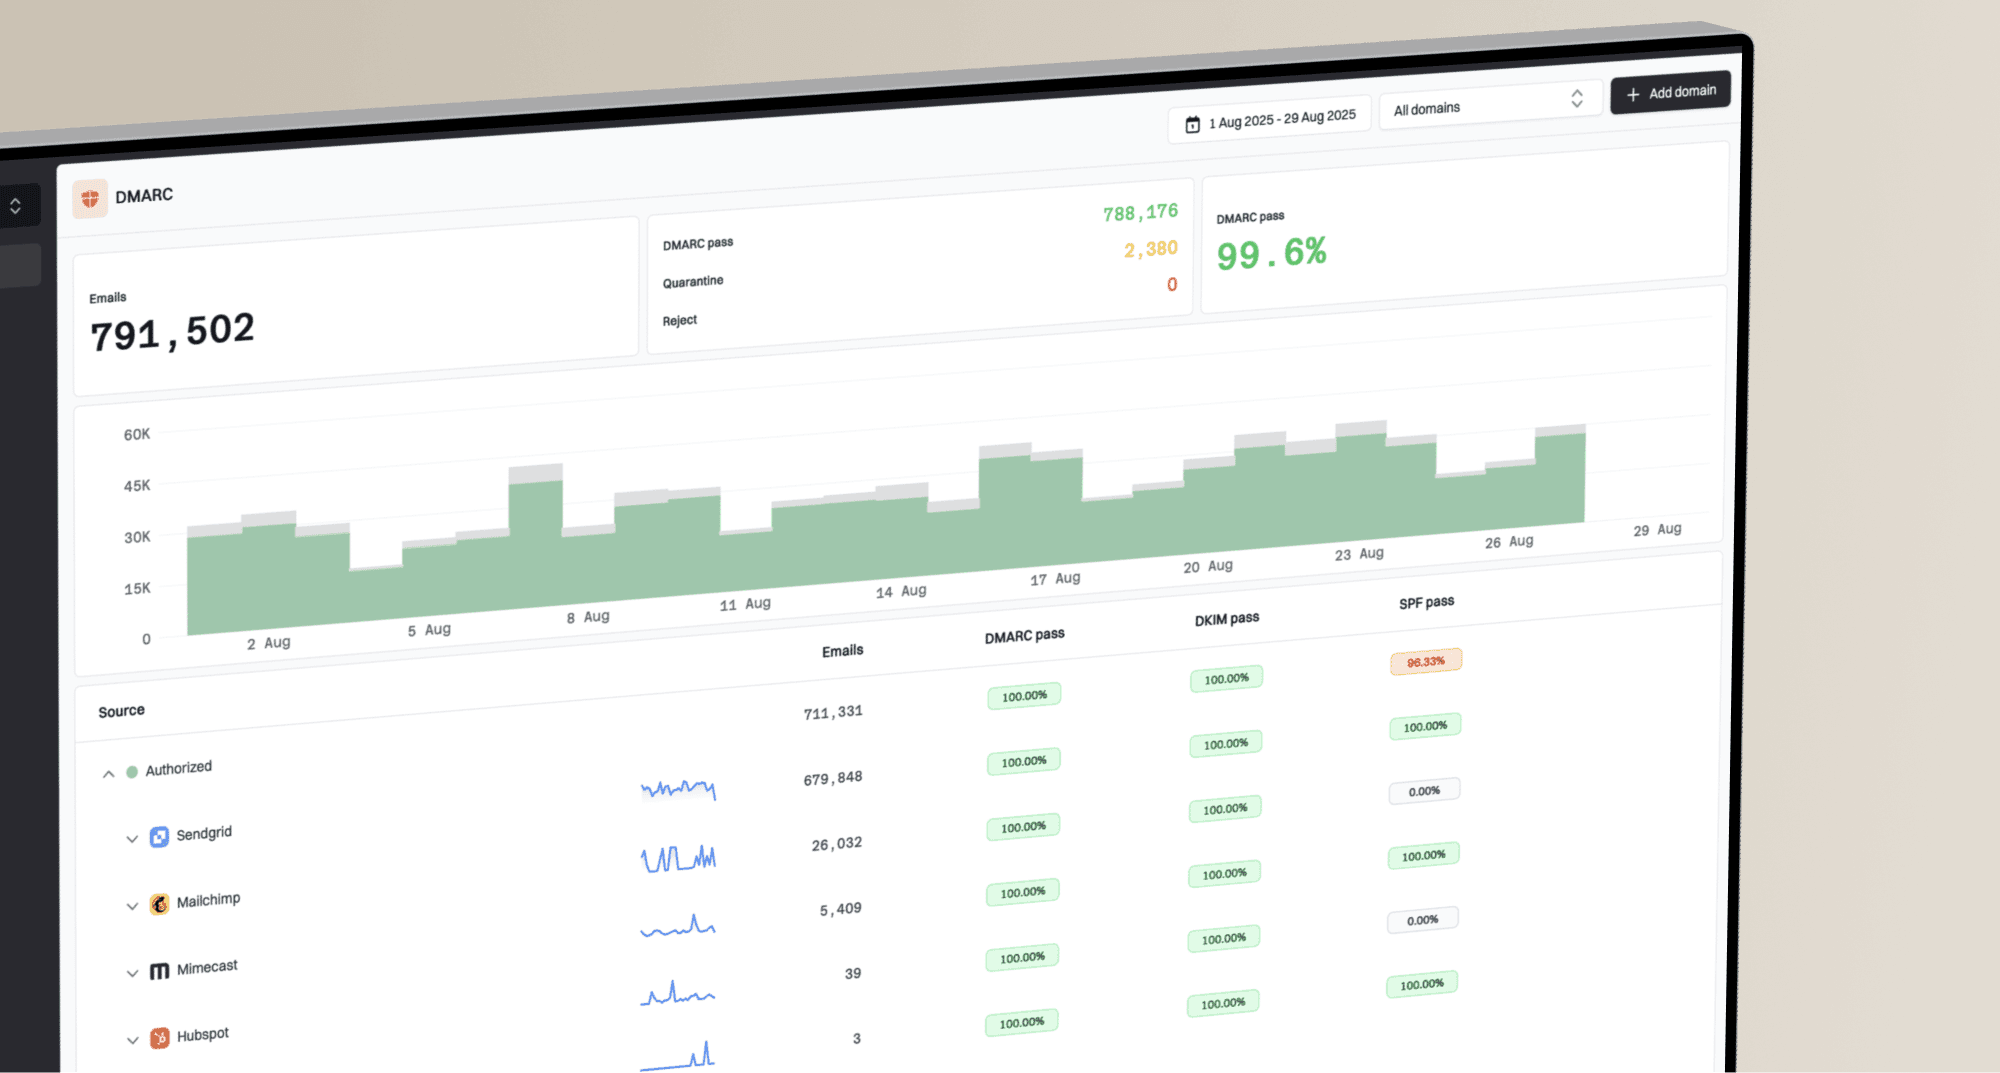
Suped's product provides DMARC monitoring to review Mailchimp authentication alongside other sources using your domain. Use aggregate reports to identify legitimate senders with failed authentication and investigate unknown sources.
Add the domain to Suped, publish its reporting address in your existing DMARC record, and review the sources reported by participating receivers. Fix authentication for approved senders and investigate unauthorized traffic before increasing policy enforcement.
DMARC record detail view showing SPF, DKIM, DMARC, rDNS diagnostics, and DNS records
Suped's Hosted DMARC workflow also helps non-technical teams stage policy changes without editing DNS each time. That becomes useful after Mailchimp is fixed, because every new approved sender must be identified and checked before enforcement increases.
Common Mailchimp authentication problems
Most Mailchimp authentication problems come from ownership and DNS process issues, not complicated records. Direct DNS access often makes setup quick. When a client, IT team, registrar, or agency controls DNS, approval and propagation usually determine the timeline.
- Free From address: A public Gmail or Yahoo domain cannot be authenticated by a Mailchimp customer. For affected free addresses, Mailchimp automatically changes the From domain to send.mailchimpapp.com or mail.mailchimpapp.com. Replies still go to the original address, as explained in its free email address guidance. Use an owned custom domain to retain a branded From address.
- Multiple domains: Authenticate each From domain separately. Use a repeatable process for multiple Mailchimp domains.
- Subdomains: A marketing subdomain helps separate sending streams, but it does not guarantee separate reputation or remove Gmail bulk-sender classification. It still needs DKIM alignment and DMARC coverage.
- Duplicate DMARC: Only one DMARC TXT record belongs at the DMARC host. Duplicates break evaluation.
- SPF record: Do not add a Mailchimp include to the visible From domain's SPF record unless Mailchimp instructs you to. Maintain that SPF record for other services that use the domain in their envelope sender.
- Sender rules: Use the broader Gmail and Yahoo rules to check authentication, unsubscribe handling, and spam complaints together.
Recommended setup
Use a branded From domain, verify it in Mailchimp, add the supplied DKIM CNAME records, and check DMARC coverage at _dmarc. Preserve an existing policy. For a new p=none policy, monitor legitimate traffic across representative sending cycles before moving beyond p=none.
Views from the trenches
Best practices
Authenticate Mailchimp DKIM first, then use DMARC reports to confirm real passing traffic.
Keep initial sends close to normal volume unless the domain, audience, or platform changed.
Give DNS access to the person doing setup, or expect approval delays before validation.
Common pitfalls
Treating 5,000 as a loophole leaves near-bulk senders exposed to sudden enforcement.
Adding duplicate DMARC TXT records causes failures even when each record looks valid alone.
Assuming a green setup label replaces receiver-side checks hides real delivery problems.
Expert tips
For a new policy, use p=none and review reported sources before adding quarantine or reject.
Send the first post-auth campaign to engaged contacts and compare complaint patterns.
Review Mailchimp plus every other sender before tightening DMARC for the root domain.
Marketer view
Marketer from Email Geeks says custom DKIM in Mailchimp followed by brand DMARC is the normal pattern for ESP authentication.
2024-02-02 - Email Geeks
Marketer view
Marketer from Email Geeks says a full warm-up is not needed for stable, engaged Mailchimp lists at normal campaign volume.
2024-02-02 - Email Geeks
Frequently asked questions
No. Gmail requires SPF or DKIM for all senders, then adds SPF, DKIM, and DMARC for bulk senders. Mailchimp recommends custom domain authentication and DMARC for owned domains because unauthenticated mail can still be filtered or rejected. Mailchimp Transactional separately requires domain authentication before sending to external recipients.
Yahoo does not publish a numeric bulk-sender threshold. It describes bulk senders as domains sending significant volume and considers other signals during compliance review. Its classification should not be inferred from Gmail's 5,000-message guideline.
Gmail combines messages sent to personal Gmail accounts by the same primary domain within 24 hours, including traffic from subdomains and other sending services. Messages to Google Workspace accounts are outside these specific requirements. Once Gmail classifies that primary domain as a bulk sender, the status does not expire.
Mailchimp supports verified free addresses, but you cannot authenticate gmail.com. For affected free addresses, Mailchimp rewrites the From domain to send.mailchimpapp.com or mail.mailchimpapp.com, while replies still go to your original address. Use an owned custom domain to keep your branded From address.
For a domain without DMARC, start with p=none and a working rua reporting address while you confirm that all authorized senders pass. Preserve an existing quarantine or reject policy and fix Mailchimp authentication instead of weakening it.
Correctly configured DKIM and DMARC support sender authentication but do not guarantee inbox delivery. Incorrect DNS values or a strict DMARC policy applied before all legitimate senders pass can disrupt delivery. Adding authentication alone does not require a separate warm-up for a stable sending program.