Why is Microsoft blocking my automated emails?
Updated on 9 Oct 2026: We clarified Microsoft's bounce codes and the review paths for Outlook.com and Microsoft 365 blocks.
Microsoft is blocking your automated emails because its filtering systems see a risk signal strong enough to reject, throttle, quarantine, or junk the mail. The most common causes are failed authentication checks, authenticated domains that do not match the visible From domain, poor sender reputation, spam complaints, sudden volume changes, and shared IP problems. If your automation sends through Microsoft 365, outbound sending limits or a restricted account can also stop delivery.
Treat this as an evidence problem before treating it as a generic Microsoft problem. The bounce text, message headers, source IP, sending domain, authentication results, and recipient pattern usually explain whether the block is technical, reputation-based, policy-based, or content-based.
- Hard block: Microsoft rejects the SMTP transaction, often with a 5xx code and a policy, authentication, reputation, or content reason.
- Temporary block: Microsoft returns a 4xx code, which usually means throttling, deferral, or a rate limit.
- Post-acceptance filtering: The email is accepted but lands in Junk, Quarantine, Deleted Items, or a folder selected by a mailbox or transport rule.
Before changing infrastructure, send a real sample through the email tester and compare the result with your Microsoft bounce logs. A test result without the bounce text is useful, but the rejection message is the thing that usually narrows the cause fastest.
Read the Microsoft bounce code
If your automated emails are getting blocked by Outlook.com, Hotmail, Live, MSN, or Microsoft 365 recipients, read the full non-delivery report (NDR) before changing the sending setup. The enhanced status code and diagnostic text identify which restriction needs attention.
The exact reason depends on where the block happens. A rejection during SMTP points to a policy, reputation, rate, authentication, or content problem. Acceptance followed by Junk or Quarantine points to filtering after receipt. Intermittent delivery points to volume, shared infrastructure, recipient-level reputation differences, or tenant policy.
Do not fix this blind
The full bounce message matters. Redacted snippets hide the source IP, enhanced status code, policy text, and Microsoft host that made the decision. Without that, you end up changing DNS, content, and sending volume at random.
- Keep headers: Save the original headers and the SMTP transcript before retrying.
- Keep timing: Record the send time, recipient domain, campaign type, and source IP.
- Keep separation: Do not mix transactional alerts with cold outreach or warm-up traffic.
Microsoft NDR codes and their meaningstext
5.7.515: Outlook.com sending domain fails required authentication
4.7.500: Temporary sending restriction; retry later
5.7.520: Exchange Online automatic external forwarding blocked by policy
5.7.606: Microsoft 365 sending IP is banned
Those examples are not a complete list, and the meaning depends on the Microsoft service and full diagnostic text. In Exchange Online, 5.7.520 concerns external forwarding policy rather than a generic spam-content verdict. Check Microsoft's NDR reference for the code in your bounce. A 5xx rejection needs a different response than a 4xx deferral, and both differ from accepted mail placed in Junk.
Separate sender rejection from mailbox filtering
If verification codes, login links, password resets, or reminders never appear, first confirm whether the sender received an NDR. A bounce identifies a delivery failure, but it is not always a spam block. Check the sender's SMTP logs for a successful acceptance response; no bounce alone does not prove Microsoft received the message.
- Check mailbox folders: Search Junk, Deleted Items, Archive, and any custom folders for the sender, subject, or recipient address. If the message is in Junk, mark it as Not junk before requesting another copy.
- Review mailbox controls: Check blocked senders, safe senders, Inbox rules, forwarding, and Sweep rules. A safe-sender entry can help with mailbox junk placement, but it cannot override an SMTP rejection or an administrator's security policy.
- Trace Microsoft 365 mail: Ask an Exchange Online administrator to run message trace in the Exchange admin center. It can show whether the service received, rejected, deferred, delivered, redirected, filtered, or quarantined the message.
- Return to the sender: If there is no trace and no mailbox copy, ask the sending organization for its SMTP logs, NDR, source IP, and exact send time.
Consumer Outlook and Microsoft 365 differ
Outlook.com, Hotmail, Live, and MSN use Microsoft's consumer filtering. Microsoft 365 work and school mailboxes also have tenant policies controlled by an administrator. Recipient troubleshooting must follow the service that owns the mailbox.
How Microsoft sees automated email
Automated mail is not bad by itself. Password resets, invoices, product alerts, security notifications, and double opt-in emails are automated. The problem starts when the mail stream carries weak identity, unstable volume, low engagement, poor list quality, or patterns associated with bulk prospecting.
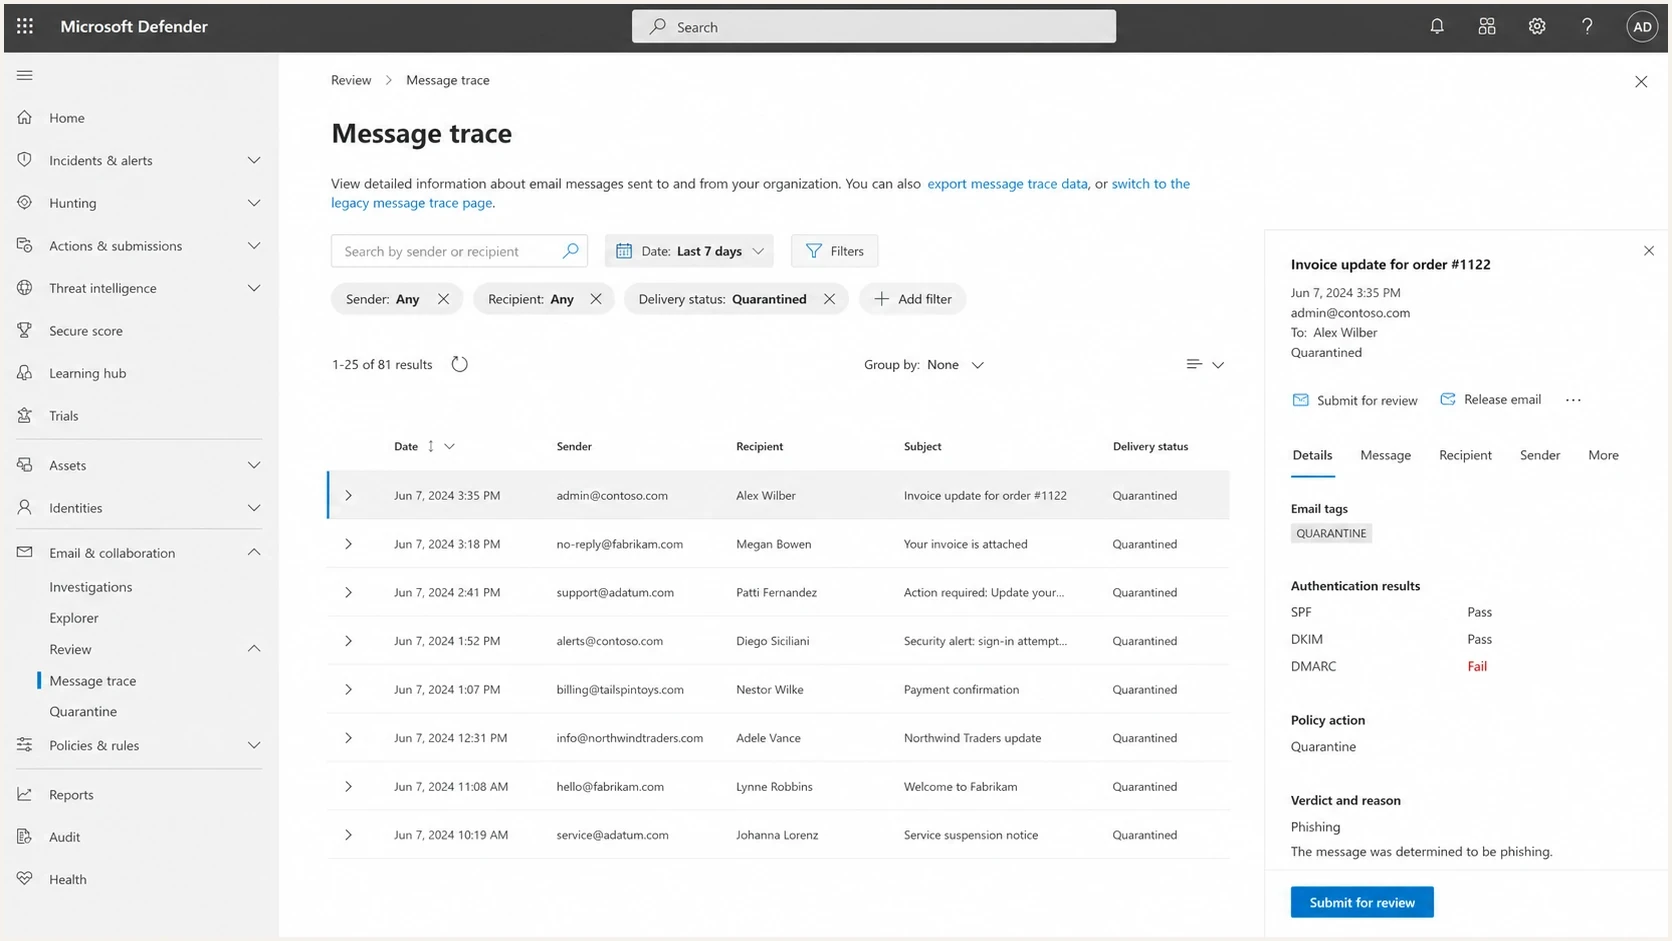
Microsoft Defender for Office 365 message trace and quarantine investigation screen.
For Microsoft 365 recipients, the recipient tenant's security policies also matter. A sender can pass DMARC and still be quarantined by an organization's policy. For consumer Outlook.com and Hotmail recipients, sender reputation and recipient engagement carry more of the practical weight. For content-related failures, review linked domains, redirects, attachments, and message formatting. A repeated transactional template is not itself evidence of abuse.
|
|
|
|---|---|---|
Authentication | Domain mismatch | Fix authentication and DMARC domain matching |
Reputation | Complaints | Reduce complaints |
Volume | Burst pattern | Stage sends |
Content | Untrusted links or attachments | Review URLs and attachments |
Blocklist (blacklist) | Listed source | Investigate cause |
Microsoft blocking signals to sort first.
For other Microsoft delivery failures, use the troubleshooting checklist for Microsoft domains. Review sending schedules and shared sources when only automation is affected.
Check authentication and sender reputation
Start with checks that separate identity problems from reputation problems. If identity fails, fix that first. If identity passes, treat the block as a reputation, volume, policy, or content problem.
- Bounce evidence: Collect the full SMTP rejection, enhanced status code, source IP, recipient domain, and timestamp.
- Authentication: Use Suped's domain health checker to check SPF, DKIM, and DMARC DNS records. Then inspect Authentication-Results in a Microsoft-received sample to confirm actual pass/fail results and domain matching.
- Reputation: Review bounces, complaints, clicks, replies, unsubscribes, list source, and recent volume changes.
- Blocklists and blacklists: Check relevant public blocklists for the sending domain and IP, then fix the cause before requesting removal. A clean public result does not rule out Microsoft's internal blocklist.
- Monitoring: Add ongoing blocklist monitoring so new public listings trigger investigation. Public monitoring does not reveal Microsoft's internal blacklist.
Email tester
Send a real email to this address. Suped shows a results button when the test is ready.
?/43tests passed
A test mailbox does not replace production evidence. It gives a controlled sample. If your production bounces show Microsoft rejecting at SMTP but the test passes, the issue is tied to recipient segment, source IP, send timing, tenant policy, or reputation history.
Authentication problems that cause blocks
Authentication does not guarantee inbox placement, but broken authentication makes a Microsoft block easier to trigger. Automated systems often fail here because a product team adds a sender, a marketing team adds another sender, and nobody updates DNS or confirms that the authenticated domains match the visible From domain.
Microsoft's large-sender rule
For a domain sending 5,000 or more messages a day to Microsoft's consumer email services with the same domain in the RFC 5322 From address, Microsoft requires SPF and DKIM to pass, a valid DMARC record with at least p=none, and a DMARC pass through a matching SPF or DKIM identity. A failure can produce 550 5.7.515. This rule covers Outlook.com, Hotmail, Live, and MSN recipients; Microsoft 365 tenants also apply their own security policies. See Microsoft's authentication requirements.
RFC 9989 DMARC monitoring exampledns
_dmarc.example.com. 3600 IN TXT (
  "v=DMARC1; p=none; "
  "rua=mailto:dmarc@example.com"
)
RFC 9989, published in May 2026, replaced RFC 7489 and RFC 9091 and makes the pct tag historic, so do not use it to stage DMARC enforcement. A starting policy of p=none with a rua address requests aggregate reports without requesting DMARC enforcement. For a dedicated sending domain, move to p=quarantine or p=reject only after legitimate senders pass DMARC and indirect mail flows have been assessed. Under RFC 9989, t=y requests testing treatment one policy level below the published policy, rather than a percentage rollout. Receivers that do not support this tag ignore it; p=none is the broadly compatible starting policy.
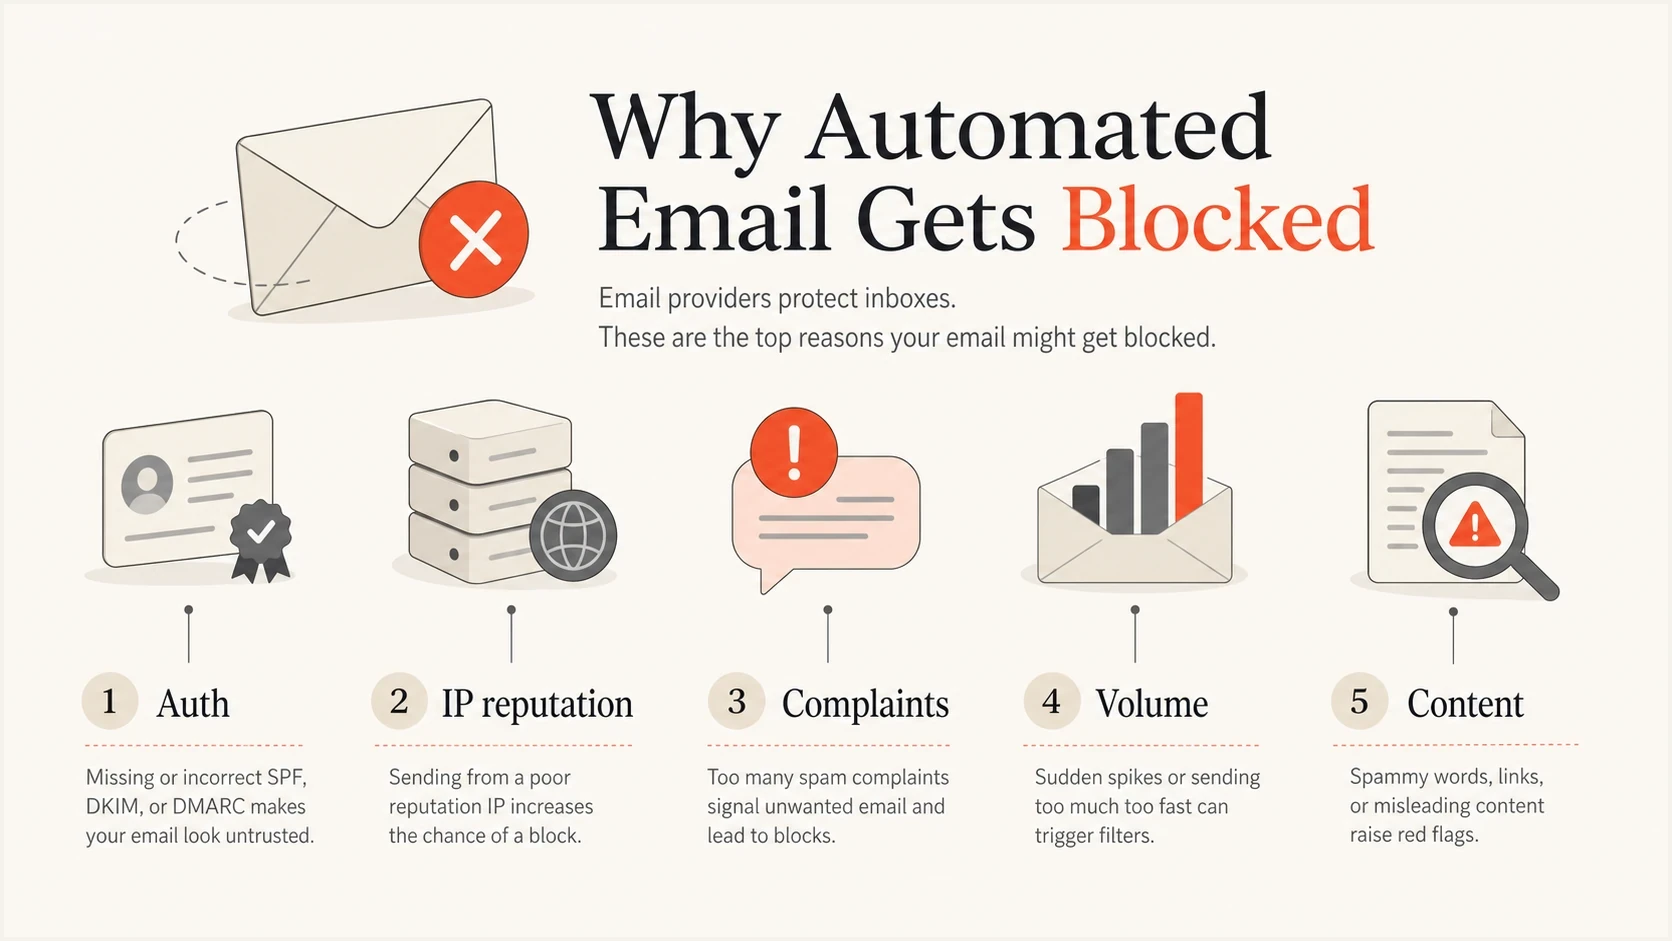
Five Microsoft blocking signals: authentication, IP reputation, complaints, volume, and content.
- SPF: Authorize the sending IP in the envelope sender (Return-Path) domain's SPF record. Publish one SPF record there and keep mechanisms and modifiers that trigger DNS lookups within SPF's limit of 10.
- DKIM: A valid signature authenticates the DKIM d= domain. For DKIM to satisfy DMARC, that domain must match the visible From domain under the record's matching mode.
- DMARC: At least one SPF or DKIM check must pass and its domain must match the visible From domain. Relaxed matching allows the same organizational domain; strict matching requires an exact domain match.
- Forwarding: Forwarded mail often breaks SPF, so a surviving DKIM signature from a matching domain becomes more important.
Reputation and behavior are usually decisive
When authentication passes and Microsoft still blocks the mail, look at behavior. Automated email with low recipient engagement, high unknown-user rates, spam complaints, aggressive retry patterns, and sudden bursts can hit filtering even when DNS is correct.
Healthy automation
- Consent: Recipients expect the email and understand why it arrived.
- Segmentation: Transactional, lifecycle, and sales streams use separate domains or subdomains.
- Cadence: Volume changes follow a steady pattern with low complaint pressure.
Risky automation
- Cold lists: Recipients have weak or no relationship with the sender.
- Shared sources: Critical alerts share IPs or domains with prospecting mail.
- Artificial activity: Open, click, reply, or inbox placement patterns look manufactured.
Automated warm-up that manufactures opens, clicks, or replies does not establish recipient consent or fix spam complaints and authentication errors. Stop that behavior, clean the sending streams, and rebuild reputation with mail recipients expect.
For a Microsoft 365 false positive, ask the recipient's administrator to follow Microsoft false positive guidance to submit a legitimate message for analysis and inspect the applied policy. Include the original headers and business context.
Where Suped fits
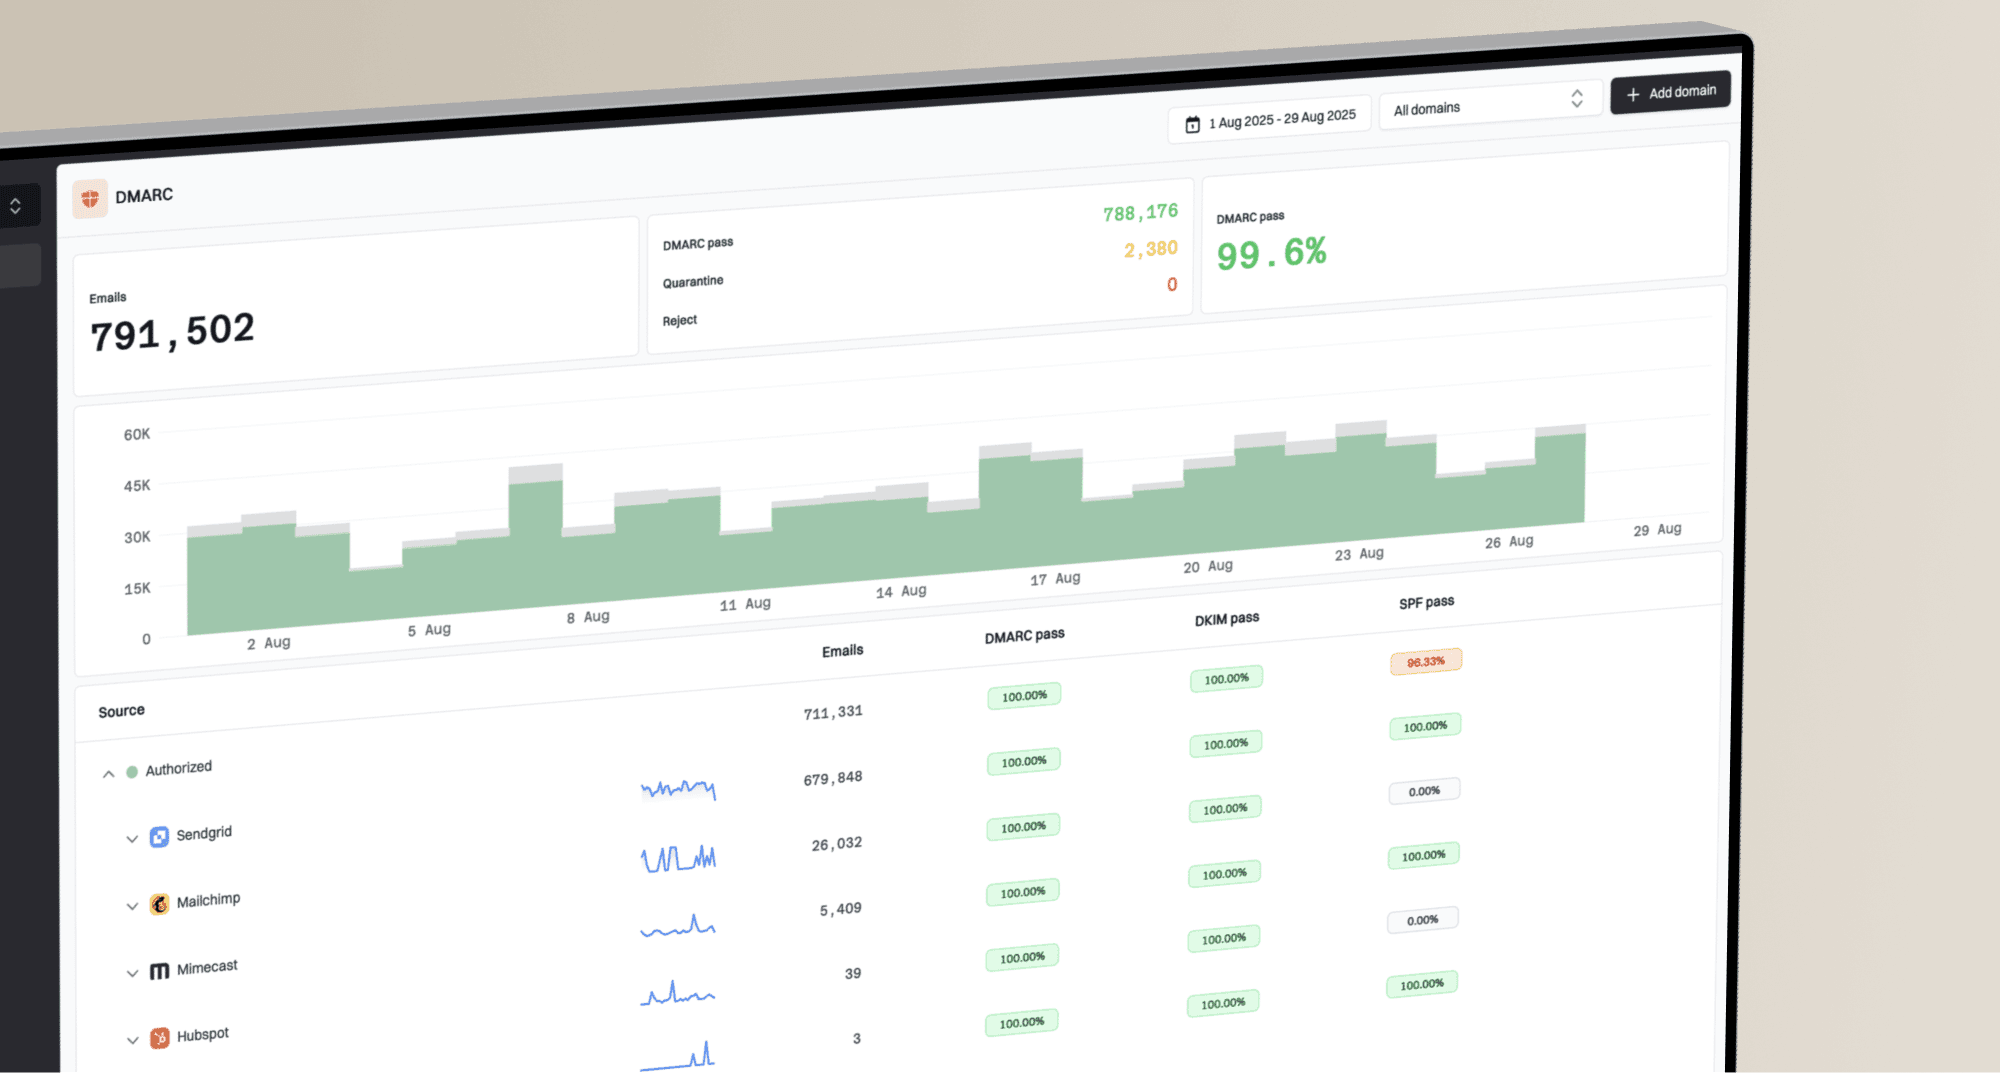
Suped's product supports the sender-side investigation by combining DMARC aggregate data, SPF and DKIM checks, and blocklist (blacklist) monitoring in one workflow. Use Suped to map the IP or domain in a Microsoft NDR to the sending source, confirm whether its authenticated identities match the From domain, and alert the owner when a source starts failing.

Issue steps to fix dialog showing the issue overview, tailored fix steps, and verification action
DMARC aggregate reports are receiver summaries, usually delivered daily, rather than live SMTP logs or proof of inbox placement. Match the report period with bounce timestamps before attributing an incident to a source. Suped cannot override Microsoft filtering, so Microsoft message trace, NDR evidence, and recipient policy checks still matter.
- DMARC monitoring: See which sources pass, fail, and match before moving a dedicated sending domain toward enforcement.
- Hosted SPF: Manage approved senders and reduce manual DNS edits when automated systems change.
- Alerts: Investigate new authentication failures, blacklist listings, or source changes when Suped reports them.
- Multi-tenancy: MSPs and agencies can monitor client domains without manual spreadsheet work.
A practical recovery plan
Do the work in order. If you rotate domains, switch IPs, or rewrite templates before you understand the failure, you often spread the problem across more assets. Microsoft filtering is sensitive to sender history, and frantic changes create more unusual signals.
- Pause risky streams: Stop cold outreach, warm-up automation, scraped list sends, and high-complaint campaigns first. Suppress hard-bounced addresses and honor unsubscribe requests; promotional automation needs a visible, working unsubscribe link.
- Protect critical mail: Keep password resets, invoices, and account alerts separate from risky marketing sources. Separate authenticated subdomains and sending IP pools help isolate streams, but parent-domain reputation still matters.
- Fix identity: Verify SPF authorization, DKIM signing, DMARC domain matching, reverse DNS (PTR), and a consistent SMTP EHLO hostname.
- Reduce volume: For marketing or lifecycle campaigns, send to recently engaged recipients first, then increase slowly after bounces and complaints stay low. Send critical transactional mail when its user action triggers it.
- Submit evidence: Use Microsoft review paths only after you have clean headers, sample messages, and proof the source is controlled.
What not to do
Do not treat a Microsoft block as a reason to hide the sender. New domains, new IPs, and slightly changed templates do not erase reputation. If the underlying behavior stays the same, the block returns.
After a 4xx deferral, use retry backoff and discard verification messages once their tokens expire. Do not repeatedly resend unchanged mail after a 5xx rejection. Test recovery with a small legitimate send and compare the full NDR or Microsoft 365 message trace before restoring normal volume.
Choose the correct Microsoft review path
Match the review request to the mailbox service and the restriction named in the NDR. Outlook.com consumer blocks, Microsoft 365 IP blocks, and restrictions on your own Microsoft 365 account have different owners.
|
|
|
|---|---|---|
Outlook.com, Hotmail, Live, or MSN rejection, including S3150 | Sending organization or IP owner | Use consumer Outlook.com sender support. Include the full rejection, source IP, timestamps, and corrective steps. |
Microsoft 365 banned sending IP, 5.7.606-649 | Sending organization or IP owner | Follow the IP-delisting instructions in the NDR. This route does not remove consumer Outlook.com blocks. |
Microsoft 365 banned sender, 5.7.511 | Sending organization or IP owner | Forward the full NDR and source IP to delist@microsoft.com as instructed. This code uses a separate review process. |
Microsoft 365 quarantine or tenant policy block | Recipient's Microsoft 365 administrator | Use message trace to identify the policy and submit a legitimate sample for analysis when the verdict is incorrect. |
Route Microsoft delivery failures using the full NDR and affected service.
Microsoft's IP-delisting guidance distinguishes the 5.7.606-649 process from 5.7.511 and consumer Outlook.com review. If the source IP is shared or provider-managed, ask the provider to investigate and request review; delisting alone does not repair abusive traffic.
If automation sends through Microsoft 365 and fails across recipient providers, ask your own administrator to check outbound restrictions. Error 5.1.8 indicates a restricted outbound sender; inspect Restricted entities and investigate account compromise before unblocking it. Error 5.7.233 indicates the tenant external recipient rate limit (TERRL); review the Tenant Outbound External Recipients report and reduce sending until the rolling usage falls below the limit. Exchange Online is not designed for bulk campaigns. See Microsoft's outbound sending guidance.
Views from the trenches
Best practices
Collect the full SMTP rejection before changing DNS, content, volume, or sending source.
Keep transactional mail separate from prospecting traffic so reputation problems do not spread.
Use real recipient engagement and complaint trends instead of seed inbox guesses alone.
Common pitfalls
Assuming a clean DMARC pass fixes Microsoft blocks misses reputation and behavior signals.
Using automated warm-up to simulate engagement does not fix authentication or complaint issues.
Rotating IPs or domains after blocks usually extends the reputation damage across assets.
Expert tips
Build a timeline that compares bounce codes, volume changes, complaint spikes, and source changes.
Pause risky streams first, then test authentication and content with a small known-good send.
Document Microsoft-specific failures separately because Outlook.com and Microsoft 365 differ.
Marketer view
Marketer from Email Geeks says a sender should provide company context and the full rejection text before asking others to diagnose Microsoft blocking.
2024-09-10 - Email Geeks
Expert view
Expert from Email Geeks says inbox testing alone is not enough if production recipients show different Microsoft results.
2024-09-10 - Email Geeks
Frequently asked questions
Yes. A DMARC pass means SPF or DKIM passed with a domain that matches the visible From domain. Microsoft also evaluates sender reputation, spam complaints, volume, content, and recipient policies.
Microsoft rejected the message because the RFC 5322 From domain did not meet its required authentication level for a large sender. Check that SPF and DKIM pass, publish DMARC, and confirm that DMARC passes through a matching SPF or DKIM domain.
Automated mail often uses a different sending source and authentication configuration than personal mail. Check those differences, sending bursts, and recipient expectations. Repeating a legitimate template is not itself a reason for rejection.
Change IPs only when you know the old source is the problem and the new source has clean, controlled sending. Moving the same behavior to a new IP usually repeats the block.
No. A listing is one signal. Microsoft can block mail without a public blocklist entry, and a public blacklist entry does not explain every Microsoft rejection.
Collect the full bounce, original headers when available, sending IP, sending domain, recipient domain, send time in UTC, message sample, authentication results, and recent volume history. For Microsoft 365, include the message trace ID when available.