
How do I resolve Cloudmark deliverability issues?
Published 30 Jul 2025
Updated 16 Oct 2026
13 min read
Summarize with
Updated on 16 Oct 2026: We clarified Cloudmark CSI remediation and added checks for content filtering and SMTP rejections.
To resolve Cloudmark deliverability issues, start with the exact bounce or filtering evidence and the sending IP. Determine whether the problem follows the sending IPs, the sending domain, a subscriber segment, a campaign type, or a specific message stream. Then pause risky traffic, verify SPF, DKIM, and DMARC, check Cloudmark Sender Intelligence (CSI) reputation signals, compare complaint and engagement data, remove suspect addresses, and escalate with full headers and evidence.
When the issue starts right after an email service provider (ESP) move, the new sending IPs deserve immediate attention. Cloudmark CSI supplies IP reputation data, while each receiving provider decides how to use that data. Spam trap hits, user complaints, reverse DNS, nearby IP reputation, and traffic patterns can all affect the result. The Cloudmark CSI FAQ is the Cloudmark-owned reference for reputation and remediation.
- Scope: List the exact domains, IPs, campaigns, segments, recipient domains, and SMTP responses affected.
- Stabilize: Pause the stream that triggers filtering at receivers using Cloudmark data instead of changing every campaign.
- Authenticate: Confirm SPF passes, DKIM signs with the intended domain, and DMARC passes for the visible From domain.
- Clean: Suppress complainers, hard-bouncing addresses, confirmed signup errors, and contacts without current permission.
- Escalate: Submit the rejected IP, exact bounce, full headers, timeline, and evidence of remediation.
Why Cloudmark problems appear after an ESP move
An ESP migration can change more than the interface used to send mail. Check return-path domains, DKIM selectors, sending IPs, bounce handling, header structure, tracking domains, throttling behavior, and the mail merge logic. Receivers using Cloudmark data can treat those changes as a new reputation pattern, even if the subscribers and offers are the same.
Cloudmark deliverability issues commonly involve IP reputation, nearby IP-range reputation, complaint pressure, spam trap exposure, or message fingerprints. A paid membership list can still create complaints if the offer cadence, subject line, or promise at signup no longer matches what people expect. Opt-in status helps, but it does not override current recipient behavior.
What changed with the ESP
- IPs: Shared IPs carry pool history, while newly assigned dedicated IPs can have prior reputation or little recent history.
- Headers: New headers and tracking domains can alter filtering decisions at receivers using Cloudmark data.
- Cadence: Migration work often changes send timing, batching, and resend behavior.
What did not automatically change
- Permission: A paid or opt-in relationship still needs current interest and clear expectations.
- Identity: The From domain and brand promise still carry subscriber memory.
- Evidence: Engagement outside Cloudmark-protected mailboxes helps, but it does not close the case alone.
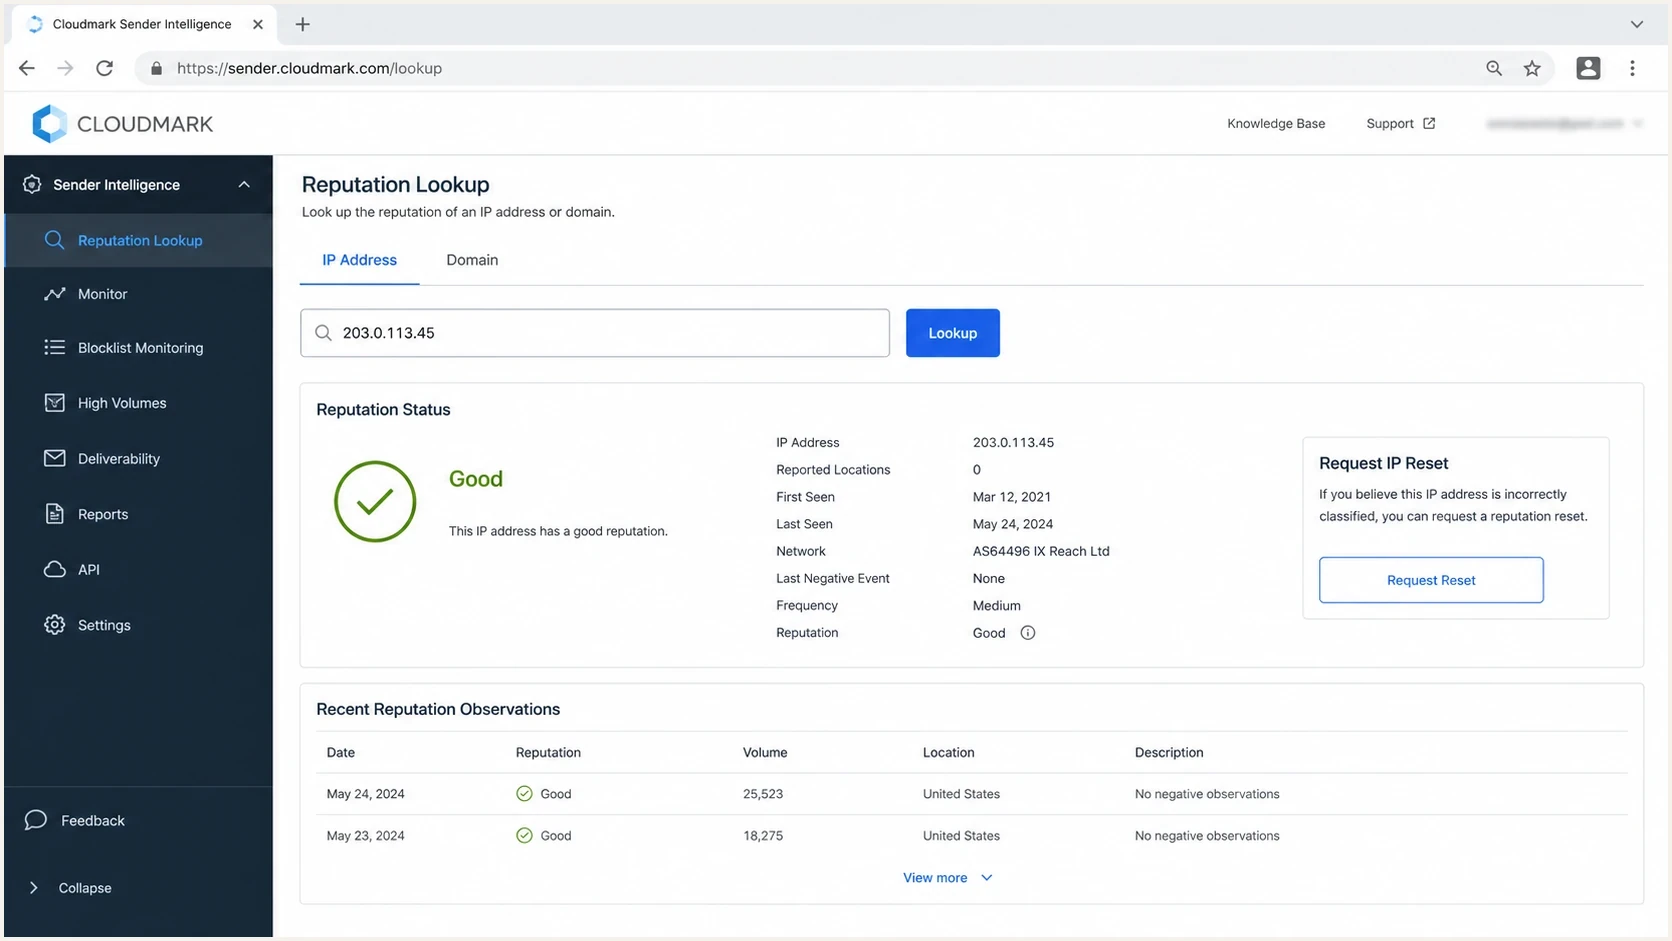
Illustrative Cloudmark CSI screen for sending IP reputation and reset requests.
Confirm Cloudmark errors in your bounce logs
Before changing copy, templates, or sending infrastructure, build a short evidence pack. The goal is to separate a confirmed Cloudmark reputation problem from a general inbox-placement problem that only looks receiver-specific.
A clean baseline starts with DNS and authentication. Run the sending domain through the domain health checker before making changes, then save the result next to your campaign data. That keeps the investigation grounded when several teams are changing DNS, ESP settings, and suppression rules at the same time.
?
What's your domain score?
Deep-scan SPF, DKIM & DMARC records for email deliverability and security issues.
Confirm the exact SMTP response before calling the incident a CSI problem. Save the status code, rejected sending IP, timestamp with time zone, recipient domain, and full diagnostic text. Then send a controlled message to real test accounts at affected domains and to control accounts elsewhere. Keep the content, segment, domain, and send time the same. If only receivers using Cloudmark data fail, investigate their filtering decision; that pattern alone does not prove a CSI problem. If both groups fail, investigate the wider mail program. Treat seed tests as diagnostic clues and verify the pattern against actual delivery logs, complaints, and subscriber responses.
A 4xx SMTP response is a temporary deferral: let the sending server retry with backoff and reduce sending pressure. A 5xx response such as 550 5.7.1 is a permanent rejection of that attempt: correct the cause before resending. A policy rejection does not establish that the recipient address is invalid, so distinguish it from an unknown-user bounce before applying address suppressions.
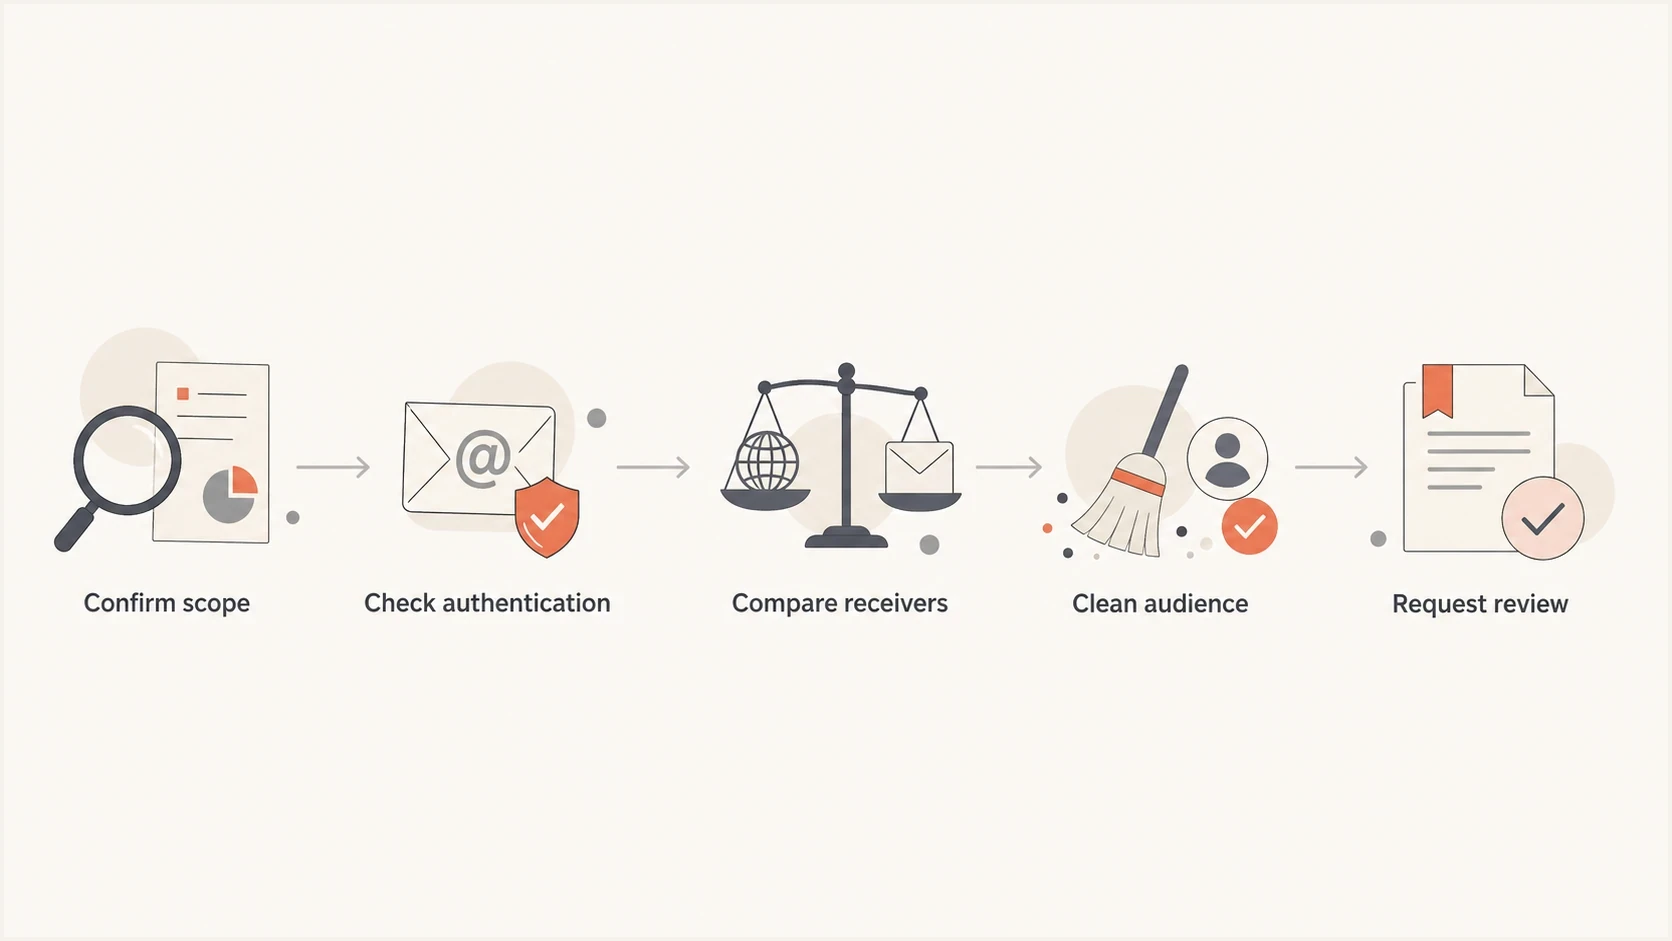
Cloudmark deliverability troubleshooting: confirm scope, check authentication, compare receivers, clean the audience, and request review.
Illustrative rejection and separate accepted-message headers
# Rejected attempt: delivery-status notification excerpt
Final-Recipient: rfc822; member@recipient.example
Action: failed
Status: 5.7.1
Diagnostic-Code: smtp; 550 5.7.1 [203.0.113.10] listed on Cloudmark CSI-Global

# Separate accepted test message: header excerpts
Return-Path: <bounce@example.com>
Authentication-Results: receiver.example; spf=pass smtp.mailfrom=example.com;
 dkim=pass header.d=example.com; dmarc=pass header.from=example.com
Received: from mta1.esp.example by mx.receiver.example
DKIM-Signature: v=1; a=rsa-sha256; d=example.com; s=s1; ...
Check reverse DNS and unauthorized sending
Cloudmark's remediation guidance requires valid reverse DNS for the sending IP. Confirm that the PTR record returns a public hostname and that the hostname resolves back to the same IP. The SMTP HELO or EHLO name should identify a valid public hostname. Generic, missing, or malformed names can contribute to a poor CSI reputation.
Also check whether the IP sent unwanted mail without the expected team's knowledge. Review outbound logs for abnormal volume, unfamiliar accounts, unexpected destinations, and sends outside normal hours. Audit gateways and credentials, close any open relay, and stop rogue scripts before asking for remediation.
- PTR: Ask the IP owner to correct reverse DNS when the ESP or hosting provider controls it.
- HELO/EHLO: Verify the identity seen on the final outbound SMTP connection, not an internal relay name.
- Security: Disable compromised accounts, rotate exposed credentials, and document the last unauthorized send.
- Shared IP: Ask the ESP to inspect other senders on the shared IP and handle the CSI request when it owns the IP.
If the IP was assigned recently, record the assignment date and the full allocation supplied by the provider. Include that history in the remediation request so prior use can be separated from current traffic.
Separate IP, domain, audience, and content
Cloudmark filtering is easier to resolve when every symptom points to a specific cause. Avoid broad conclusions such as Cloudmark hates this ESP. The better question is whether the same domain, offer, and audience perform differently when sent through another IP or message stream.
Cloudmark describes CSI as an IP reputation system rather than a blacklist. Operationally, a CSI-Global rejection is still a blocklist (blacklist) incident because a receiving provider is refusing or deferring mail based on the sending IP. If the only material change is the ESP, inspect the new IPs first. If the issue appears only for one audience cohort, inspect complaints and acquisition source. If it appears only for one offer, review message expectations and unsubscribe friction.
|
|
|
|---|---|---|
Only new ESP IPs fail | IP reputation | Check CSI and warm slower |
PTR or HELO is invalid | SMTP identity | Ask the IP owner to fix it |
One segment fails | Audience quality | Suppress stale contacts |
One offer fails | Content or expectation gap | Check links and recipient expectations |
All receivers fail | Program issue | Audit list and infrastructure |
Authentication fails | DNS or ESP setup | Fix SPF, DKIM, or DMARC |
Use the smallest matching cause before changing the whole program.
Use any trap evidence supplied by the ESP or receiver to investigate acquisition and suppression practices. Pristine traps point toward weak acquisition controls, while recycled traps often point toward stale contacts and missed hard-bounce suppression. Typo traps point toward poor address capture or validation. Remove the affected source and repair the collection or suppression process before requesting reputation relief. Repeating the same sending practices after a reset risks renewed filtering.
When CSI is clear but messages are still filtered
A clean public blocklist (blacklist) check does not rule out Cloudmark filtering. CSI evaluates sending IP reputation, while Cloudmark content filtering also uses message fingerprints. A receiving provider can reject or quarantine a message under its own filtering policy even when the sending IP has no current CSI issue.
If mail is accepted but lands in spam, or the error does not identify CSI, ask the receiving provider to inspect the message trace and filtering reason. Keep the sending IP and recipient test accounts constant while comparing a plain-text message with the affected template. Change one content element at a time, such as a tracking link or signature. Treat the result as a diagnostic clue, then investigate the underlying cause.
- Save the original message as an .eml file with complete headers; copied body text loses evidence.
- Include the X-Authority-Analysis header or equivalent MTA log event if the receiving provider can supply it.
- For a confirmed content false positive, ask the receiving provider to submit the sample for Cloudmark accuracy review.
- Keep the case reference and retest the original affected template after the review outcome.
Cloudmark's accuracy reporting guidance requests the complete message and available analysis details. An IP reputation reset addresses a different issue, so use the receiver's diagnosis to choose the remediation route.
Fix causes before requesting a reset
Correct active causes before requesting a CSI reset. If the IP repeats the same complaint pattern or reaches the same bad addresses after a reset, receiving providers have reason to make the same filtering decision. Fix the mailstream first, then use the remediation path. Receiving providers still apply their own policies after a reset.
Do not rotate infrastructure blindly
Changing IPs or subdomains without fixing complaints, traps, authentication, or unauthorized sending can spread the problem. It also makes the evidence harder to explain during remediation.
- Pause: Stop the affected promotional stream for the risky cohort.
- Repair: Fix SPF, DKIM, DMARC, bounce processing, unsubscribe handling, and tracking domains.
- Resume: Restart with the most engaged subscribers, then expand based on measured results.
Authentication does not repair poor IP reputation, but it removes avoidable doubt. The visible From domain should be one subscribers recognize. For DMARC to pass, SPF or DKIM must pass, and the domain authenticated by that passing mechanism must satisfy the visible From domain's DMARC matching rules. Relaxed matching requires the same organizational domain; strict matching requires an exact domain match. Configure both SPF and DKIM correctly. Aggregate reports then show which sources use the domain and whether the ESP authenticates them correctly. If the domain already has an enforcement policy, do not weaken it just for this investigation.
Example DMARC TXT record at _dmarc.example.comdns
_dmarc.example.com. IN TXT "v=DMARC1; p=none; rua=mailto:dmarc-reports@example.com"
Use this monitoring example only for a domain without DMARC. Replace the example domain and report address with values you control. The p=none policy requests monitoring without requesting quarantine or rejection; keep any existing enforcement policy.
Send a real message through the ESP after DNS changes and inspect the result with the email tester. Use the same template and sending domain that triggered the issue. A passing DNS record in isolation is useful, but a received message proves how the ESP signed and routed the mail.
- Complaints: Register for available complaint feedback loops (FBLs) through the ESP or mailbox provider, suppress reported complainers promptly, and reduce frequency for marginally engaged contacts.
- Traps: Investigate old imports using consent records and meaningful activity; suppress purchased data, unconfirmed signups, and hard-bouncing addresses.
- Paid members: For members with current marketing permission, make benefits, expected frequency, and unsubscribe choices clear. Keep unsubscribed and complaining addresses suppressed.
- Cadence: Reduce resend pressure and avoid sudden volume jumps during recovery.
Request Cloudmark CSI remediation with evidence
If the evidence points to CSI and active causes have been corrected, follow the remediation instructions in the Cloudmark CSI FAQ. Reply to the automated message sent after submission so the request can be processed, then test again after receiving the outcome. If an ESP owns the sending IP, ask its deliverability team to handle the request. A useful submission states what changed, what was fixed, which IPs and domains are affected, and why the remaining traffic is legitimate.
Weak request
- Vague: Says messages are blocked without naming IPs, domains, timestamps, or the exact SMTP response.
- Unproven: Claims subscribers opted in but omits complaint and engagement evidence.
- Unchanged: Requests a reset before suppressions, DNS fixes, or security checks.
Strong request
- Specific: Includes affected IPs, domains, message IDs, full headers, bounce lines, and PTR results.
- Corrected: Explains list cleanup, authentication fixes, security findings, and reduced sending pressure.
- Measured: Shows recent complaint rates, bounce patterns, and control mailbox results.
Cloudmark escalation checklist
Affected IPs and domains:
Exact SMTP response and timestamp with time zone:
ESP migration or IP assignment date and full IP allocation:
Message IDs and full headers:
PTR, forward DNS, and HELO/EHLO results:
SPF, DKIM, and DMARC results:
Complaint rate before cleanup:
Suppressions completed:
Security audit findings:
Current send volume and cadence:
Control mailbox results:
IP owner or ESP case ID:
Keep the request factual. Do not argue that the list is valuable or that members paid for access. Those facts matter to the business, but the remediation team needs evidence that the mailstream is wanted, authenticated, and no longer creating the same negative signals.
Monitor authentication and reputation with Suped
Suped is our DMARC reporting and email authentication platform. Use Suped to compare sending sources and authentication results before and after the incident, then save those findings alongside your Cloudmark bounce logs.
Review DMARC aggregate data for the reporting periods around the first failed delivery and investigate unfamiliar sources. Use blocklist monitoring to track changes on supported lists during recovery. DMARC reports describe authentication, while your ESP's delivery logs and receiver feedback establish Cloudmark-specific delivery outcomes.

Blocklist monitoring page showing domain and IP checks across blocklists with importance and status
Use monitoring after the reset
After a reset, use authentication reports and supported blacklist alerts to catch changes during recovery. Confirm Cloudmark delivery in your ESP's bounce logs.
- Watch DMARC failures, new sending sources, and supported blocklist changes.
- Compare SPF and DKIM results for the affected ESP after each configuration change.
- Record each DNS change and suppression action alongside the next delivery result.
Resume sending after Cloudmark remediation
After Cloudmark processes the request, test delivery at the affected domains and compare the new SMTP response with the original error. Resume at a reduced volume and increase it only while complaints and policy rejections stay low. SMTP acceptance confirms that the receiver accepted the message; verify inbox placement separately.
For paid-member promotional mail, isolate that stream, send only to engaged recipients with current permission during recovery, and document every change. Confirm authentication passes, complaints are down, suspect addresses are suppressed, and reverse DNS is valid before expanding the audience. Keep unsubscribes and complaint suppressions active as volume grows.
Frequently asked questions
Usually no. Authentication problems can make filtering worse, but Cloudmark CSI reputation also uses IP behavior, complaints, traps, reverse DNS, nearby IP reputation, and traffic patterns. Fix authentication anyway because it removes a common reason for distrust.
Fix the source of the issue first. A reset before cleanup often creates a short improvement followed by the same filtering. Submit the CSI remediation form after suppression, DNS, security, and cadence work is complete, then reply to the automated message Cloudmark sends.
Yes. Payment proves a relationship, not ongoing consent for every offer. If the subject line, frequency, or offer type no longer matches expectations, paid members can still mark messages as unwanted.
Include the rejected IP, sending domains, exact SMTP response, full headers, message IDs, IP assignment or ESP migration date, PTR and HELO results, authentication results, complaint data, cleanup actions, security findings, and control mailbox results. Ask the ESP to submit the request if it owns the IP.
There is no fixed recovery time. DNS corrections can be verified after they publish, but reputation recovery depends on the cause, the remediation review, and subsequent sending behavior. Restart with engaged recipients and expand only when delivery results stay stable.
A clean public blocklist (blacklist) check does not establish how the receiving provider rates your sending IP or message. Check the exact rejection and the IP used for that send. If CSI is clear, ask the receiving provider to investigate content filtering or local policy and submit an original message sample for a confirmed false positive.




