Do spam traps ever open or click on emails?
Published 24 Apr 2025
Updated 15 Oct 2026
14 min read
Summarize with
Updated on 15 Oct 2026: We clarified how automated opens and clicks affect spam trap investigations and tightened the guidance on consent and suppression.
Yes, spam traps can generate recorded opens or clicks. Those events do not prove that a person read the email or wanted it. Pristine and recycled spam traps operated for reputation measurement receive mail without ordinary subscriber intent. The catch is that "spam trap" is a broad term, and different trap networks, mailbox providers, security systems, and researchers handle trapped mail differently.
The practical answer is this: a trap hit should never be treated as proof of engagement just because an open pixel fired or a link received a request. A spam trap can sit behind automated content analysis, malware inspection, link detonation, image proxying, or human review. Some traps never engage at all. Some networks reserve the right to fetch content. Practices vary by operator; there is no universal rule that traps never access message content.
That does not mean spam traps are acting like active readers. It means open and click telemetry has to be interpreted with care, especially when deliverability risk, blocklist (blacklist) exposure, and list hygiene decisions are involved. A single pixel load is weak evidence. A trap source in your mail stream is strong evidence that your acquisition, permission, suppression, or reactivation process needs work.
Do spam trap clicks prove engagement?
Do not assume a spam trap is inert: recorded opens or clicks can result from automated checks or an investigation. Do not use opens or clicks alone to clear a suspected spam trap from your suppression logic.
- Treat trap engagement as suspicious, not as normal subscriber activity.
- A trap hit tells you more about list quality than the open or click tells you about intent.
- Repeated trap hits increase blocklist risk even when engagement metrics look acceptable.
A real subscriber can read a message or choose a link because it is relevant. A recorded open or click alone does not establish either action. A trap-related open or click, when it happens, usually comes from a system evaluating the message or a person investigating it. Those are different events. They do not indicate consent, interest, or inbox placement strength.
This matters because many senders still use engagement rules such as "keep anyone who opened in the last 180 days" or "send reactivation to anyone who clicked once." Those rules can preserve bad addresses when automated opens and clicks are mixed into the data. The same issue affects spam traps, security scanners, mailbox image proxies, privacy-prefetched opens, and enterprise link protection systems.
Spamhaus's explanation of spam trap clicks describes researchers following links in mail sent to pristine traps during investigations. It also explains why privacy protections and security scanning weaken engagement measurements. These examples do not establish that all traps click or that traps routinely confirm subscriptions.
Why some traps generate opens or clicks
The main reason is that email is processed by more than a mailbox interface. A message can pass through filters, scanners, proxies, sandboxes, and review systems before any human sees it. Some of those systems fetch remote images. Some rewrite and visit links. Some load a landing page to detect malware, credential collection, suspicious redirects, or unwanted content.
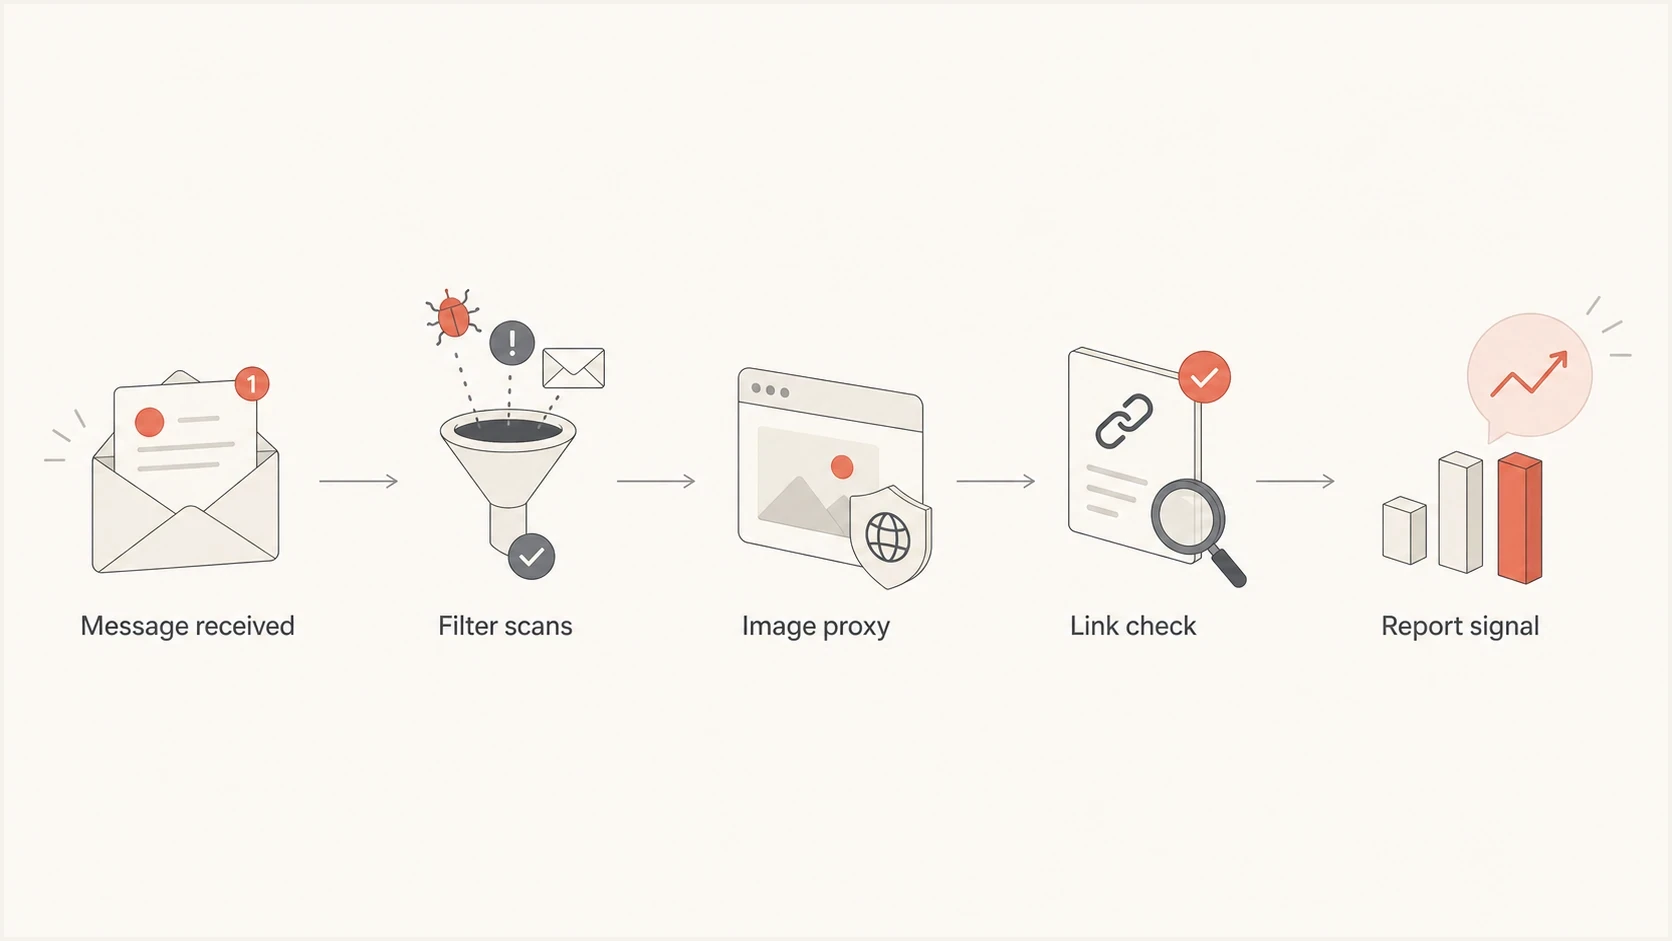
Spam trap email moving through filter scans, an image proxy and link checks to a reporting signal.
- A trap network or mailbox system fetches links or images to inspect the message body, redirects, attachments, or landing page behavior.
- Security systems detonate links in controlled environments to check whether a URL changes destination, downloads files, or collects credentials.
- A researcher reviews a sample manually, especially when the message is part of abuse tracking or a sender reputation investigation.
- A trapped address can receive mail through a forwarding path, alias, shared mailbox, or abandoned account workflow that changes how the message is handled.
- A confirmation endpoint that activates a subscription when its URL is fetched can mistake an automated link check for consent.
The operational distinction resolves the apparent contradiction. Spam traps are not normal subscribers, but a tracking request can still occur when a system or investigator evaluates the mail. Treat the request according to its behavior and keep the trap hit tied to the underlying list-quality problem.
What a click from a trap means
A click from a suspected trap means the message or link was accessed. It does not mean the recipient was a person, it does not mean the address opted in, and it does not mean the address is safe to keep. The right interpretation depends on the surrounding pattern.
|
|
|
|---|---|---|
Open only | An image loaded; the reader is unknown | Do not reclassify |
Fast click | A quick request; automation needs corroboration | Compare timing and session behavior |
Many links | A pattern consistent with a security crawl | Flag as bot-like |
Form submit | A form was submitted; intent still needs context | Review source and session |
Trap report | Reported trap delivery; the source needs investigation | Pause the implicated source and review |
What email engagement signals establish.
Timing helps assess automation, but it does not identify a spam trap. A link request that occurs within seconds of delivery, hits every link in the email, uses a scanner user agent, or comes from a data center IP should be treated differently from a click that follows a normal read path. Even then, bot detection is probabilistic. The goal is not perfect attribution of every event. The goal is to prevent automated events from driving permission and deliverability decisions.
If you are diagnosing this in live campaigns, compare the behavior against known patterns of spam filter clicks. That makes the trap question easier to separate from the broader problem of machine-generated engagement.
How spam trap types affect the investigation
The type of trap changes the likely cause and the right response. A pristine trap points toward address collection, form abuse, purchased data, poor partner controls, or weak validation at signup. A recycled trap points toward old data, weak sunset rules, or missed bounces. A typo trap points toward form quality and address correction problems.
Pristine traps
Pristine traps were not used by a real person for normal email. They point to acquisition quality, scraping, injected addresses, list rental, co-registration abuse, or unchecked partner sources.
- Permission cannot be trusted.
- Pause the source and audit the collection path.
Recycled traps
Recycled traps were once valid addresses, then were abandoned and repurposed. They point to old lists, weak bounce processing, or reactivation that keeps mailing inactive people.
- Suppression and sunset rules are too loose.
- Tighten inactivity windows and bounce handling.
A click from either type should not distract you from the source problem. A confirmation-link visit requires review of the signup and confirmation records; it does not establish that a pristine trap intentionally subscribed. An open from a recycled trap does not show that its former owner returned.
For a deeper breakdown of trap categories, see types of spam traps. The category helps decide whether you should investigate acquisition, aging, suppression, or all of them together.
Why you cannot identify every spam trap
Spam traps do not normally appear as a distinct status in campaign reports, and trap operators rarely disclose the individual addresses. Revealing them would make the trap network easy to evade. A delivered message, an open, or a click therefore cannot confirm that an address is safe. A trap hit is also different from a spam complaint: receipt at the trap records delivery, while a complaint normally follows a recipient reporting spam. Neither requires a tracked open or click.
- Store the signup time, form, consent record, import batch, and partner source so a trap report can be traced to a collection path.
- Check syntax, domain spelling, and whether the domain accepts mail. Validation reduces bad data but cannot certify that an address is not a trap.
- Use confirmed opt-in (COI), also called double opt-in, and keep contacts pending until confirmation is complete. Review suspicious automated confirmations against the signup record.
- Retain hard-bounce and unsubscribe records across imports so old addresses cannot be added back by another source.
- Do not send a full campaign to an old or undocumented list. Review permission and suppress long-inactive contacts before any limited reactivation.
If scanners activate confirmation links, make the initial link request display a confirmation page and require a separate explicit action to activate the subscription. This reduces accidental activation by link fetchers; the action still needs a valid signup and consent record.
The objective is not to find a secret list of traps. It is to remove the acquisition and retention conditions that allow pristine, recycled, or typo traps to remain in the audience. Permission-based list building and regular list cleaning reduce risk more reliably than address-level guesswork.
How to detect automated opens and clicks
You cannot reliably identify a spam trap from one event, and you should not try to build a secret trap detector from click logs alone. What you can do is separate human-like engagement from machine-like engagement so bad signals do not pollute your list decisions. Automated activity also occurs for legitimate subscribers, so a bot flag alone is not a reason to label an address as a trap or suppress it.
Automation indicators to review together, not proof of a traptext
event_time - delivery_time < message_specific_time_threshold
distinct_links_clicked >= message_specific_link_threshold
user_agent contains security scanner terms
source_ip belongs to cloud or security infrastructure
open and click occur almost simultaneously
same IP clicks many recipients across one campaign
A single indicator is not enough, and the timing threshold should match the message type. Fast clicks can happen when a real person is already waiting for a message, especially in password reset or double opt-in flows. A cloud IP can appear because of privacy proxies. The strongest pattern combines very fast timing, multiple links, no dwell time, an unusual user agent, and repeated behavior across many recipients. Privacy-prefetched opens, including those associated with Apple Mail Privacy Protection (MPP), are not proof of reading. Spamhaus's discussion of engagement signals distinguishes privacy-related open measurements from automated link inspection; neither identifies a spam trap on its own.
Email tester
Send a real email to this address. Suped shows a results button when the test is ready.
?/43tests passed
For controlled testing, send a real message through Suped's email tester and review authentication, reverse DNS and blocklist results. This identifies separate sending-setup issues; it does not identify spam traps, inspect recipient clicks, or prove inbox placement.
Do not use hidden links as a simple bot filter without thinking through the side effects. Hidden or near-hidden links can look deceptive, trigger automated inspection, create accessibility problems, and produce false conclusions.
- Use timing, link breadth, user agent, IP pattern, and session depth together.
- Treat a verified downstream action, such as an account login or purchase, as stronger evidence of activity than a tracking request; it does not replace marketing consent.
How to respond after a trap hit
The response should be operational. Do not spend days debating whether the trap "really" clicked. Treat the event as a warning that your mail reached an address it should not have reached, then narrow the exposure.
- Pause the affected acquisition source, upload path, partner feed, old segment, or reactivation audience while you investigate.
- Check whether the issue clusters by signup date, source, form, domain, geography, campaign, or import batch.
- Verify SPF, DKIM, DMARC, rDNS, and alignment because authentication failures and trap exposure are distinct causes of delivery trouble.
- Suppress long-inactive contacts under your sunset policy, retain hard-bounce and unsubscribe suppressions, and review repeated soft-bounce causes before removing addresses. Automated activity must not reset inactivity clocks.
- Watch domain and IP reputation for blacklist listings after the affected campaign.
Suped's DMARC reporting shows sending sources and authentication results, while its blocklist monitoring flags listed IPs and domains. Use those findings alongside your own campaign and consent records. DMARC aggregate reports do not contain open or click events and do not reveal individual trap addresses.

Issue steps to fix dialog showing the issue overview, tailored fix steps, and verification action
For teams that manage multiple brands, clients, or sending platforms, this matters because trap hits are rarely isolated to a single metric. An unknown platform can send on your domain without proper SPF or DKIM alignment, while trap exposure can come from the list source. A blocklist (blacklist) listing can appear after the campaign rather than at the moment of the trap hit. Suped's issue detection and remediation steps turn those findings into a clear queue of work.
How trap hits affect blocklist risk
Spam traps can inform blocklist (blacklist) decisions, but the relationship is not always one-to-one. A single trap hit does not guarantee a listing. Repeated trap hits, high complaint rates, unknown-user failures, poor sending infrastructure, or other reputation problems make a listing more likely. Operators use different criteria; there is no universal safe trap-hit count, and a clean lookup does not prove that a list is trap-free.
Blocklist checker
Check your domain or IP against 144 blocklists.





If you suspect trap exposure, check your sending IPs and domains for active listings, then continue monitoring after cleanup. Suped's blocklist monitoring supports that ongoing workflow, especially when you need alerts instead of one-off lookups.
A one-time lookup still helps during triage. If you need to inspect a domain or IP quickly, use the blocklist checker and record the results beside the campaign, source, send time, and affected segment. Use that timeline to guide investigation; timing alone does not prove that your campaign caused a listing. On a shared sending IP, an IP-level trap count or listing can involve another sender, so confirm the attribution with your sending provider.
Trap-hit response urgency
Illustrative triage guidance, not blocklist operator thresholds; adjust the response to the confirmed source and impact.
Low
Investigate
One reported hit without a listing still needs a source review.
Medium
Pause
Repeated hits tied to one source, segment, or import batch.
High
Contain affected sending
Trap hits plus blocklist, complaint, or bounce deterioration.
How to prevent trap-driven false confidence
The biggest mistake is allowing a low-quality address to stay active because it opened or clicked once. Engagement-based retention rules are useful, but only when the engagement signal has been cleaned. If your system treats every open as equal, bot and trap-adjacent activity will inflate your active audience.
Weak rule
Keep every address that opened or clicked in the last 180 days, regardless of timing, link pattern, source, age, or downstream behavior.
- Machine activity keeps risky addresses active.
- Open rate looks healthier than list quality.
Stronger rule
Keep addresses with clean source history, recent human-like engagement, low bounce risk, and useful downstream activity.
- Retention reflects real audience quality.
- Reactivation decisions are less exposed to bot noise.
A good engagement model separates weak signals from strong signals. Weak signals include opens, very fast clicks, and clicks on every link. Stronger signals include account login, reply, checkout, preference update, support interaction, or sustained behavior across multiple campaigns. For B2B lists, a click from a corporate security scanner should not reset the same lifecycle clock as a real content download. A purchase or login does not by itself grant marketing permission.
The right list hygiene policy also depends on sending cadence. A daily sender needs faster suppression because bad addresses receive more volume. A seasonal sender needs consent and activity records reviewed before each sending period; do not send a blanket reconfirmation campaign to undocumented contacts. A sender with partner acquisition needs source-level scoring, because one poor partner can contaminate the whole program.
Before keeping a risky or long-inactive address in a core sending segment, require a verified action beyond a tracking request and a documented permission history. That action can be a login, purchase, reply, preference update, or verified support interaction; activity alone does not restore missing consent.
Practitioner views on spam trap clicks
These dated practitioner comments describe individual experiences, not verified trap classifications or policies shared by every operator. Treat reports of subscription confirmations as anecdotes rather than proof that traps routinely subscribe.
Best practices
Separate bot-like clicks from lifecycle scoring before suppressions or reactivations.
Investigate trap hits by source, signup path, segment age, and authentication results.
Keep blocklist and blacklist monitoring active after cleanup, not only during incidents.
Common pitfalls
Treating a single open or click as proof that a suspected trap is a real subscriber.
Letting old recycled-trap risk persist because inactive addresses still show opens.
Ignoring confirmation-flow abuse when pristine-looking traps complete opt-in steps.
Expert tips
Use downstream actions, not email clicks alone, to define active audience quality.
Pause the source first when trap hits cluster, then resume only after evidence changes.
Review DNS authentication and sender inventory while investigating trap-related risk.
Marketer view
Marketer from Email Geeks says different trap networks behave differently, and some message access happens for payload or content evaluation rather than engagement.
2020-03-12 - Email Geeks
Marketer view
Marketer from Email Geeks says a trap that opens or clicks usually has an operational reason behind it, such as analysis or investigation.
2020-03-12 - Email Geeks
Frequently asked questions
No. Many traps do not open emails, but some systems fetch images or links for analysis, security scanning, or research. Treat trap-related opens as suspicious signals, not subscriber engagement.
No. A click can come from a scanner, sandbox, researcher, or unusual trap workflow. A real downstream action carries more weight than an email click.
No. Trap operators rarely reveal individual addresses, and a validation result cannot certify that an address is not a trap. Trace incidents to the source, preserve consent records, and remove risky acquisition or retention patterns.
A click must not override a credible trap report or an existing suppression. Automated activity alone does not identify a trap; review consent, source history and other evidence before suppressing a legitimate subscriber.
No. Double opt-in substantially reduces risk when unconfirmed addresses stay out of campaigns. Scanner-triggered confirmations and later address recycling still require good confirmation handling, bounce processing and ongoing list hygiene.
Check source, signup date, segment age, bounce history, complaint pattern, authentication alignment, sending platform, and active blocklist or blacklist status.