ELK DMARC vs.
Open-DMARC-Analyzer in 2026
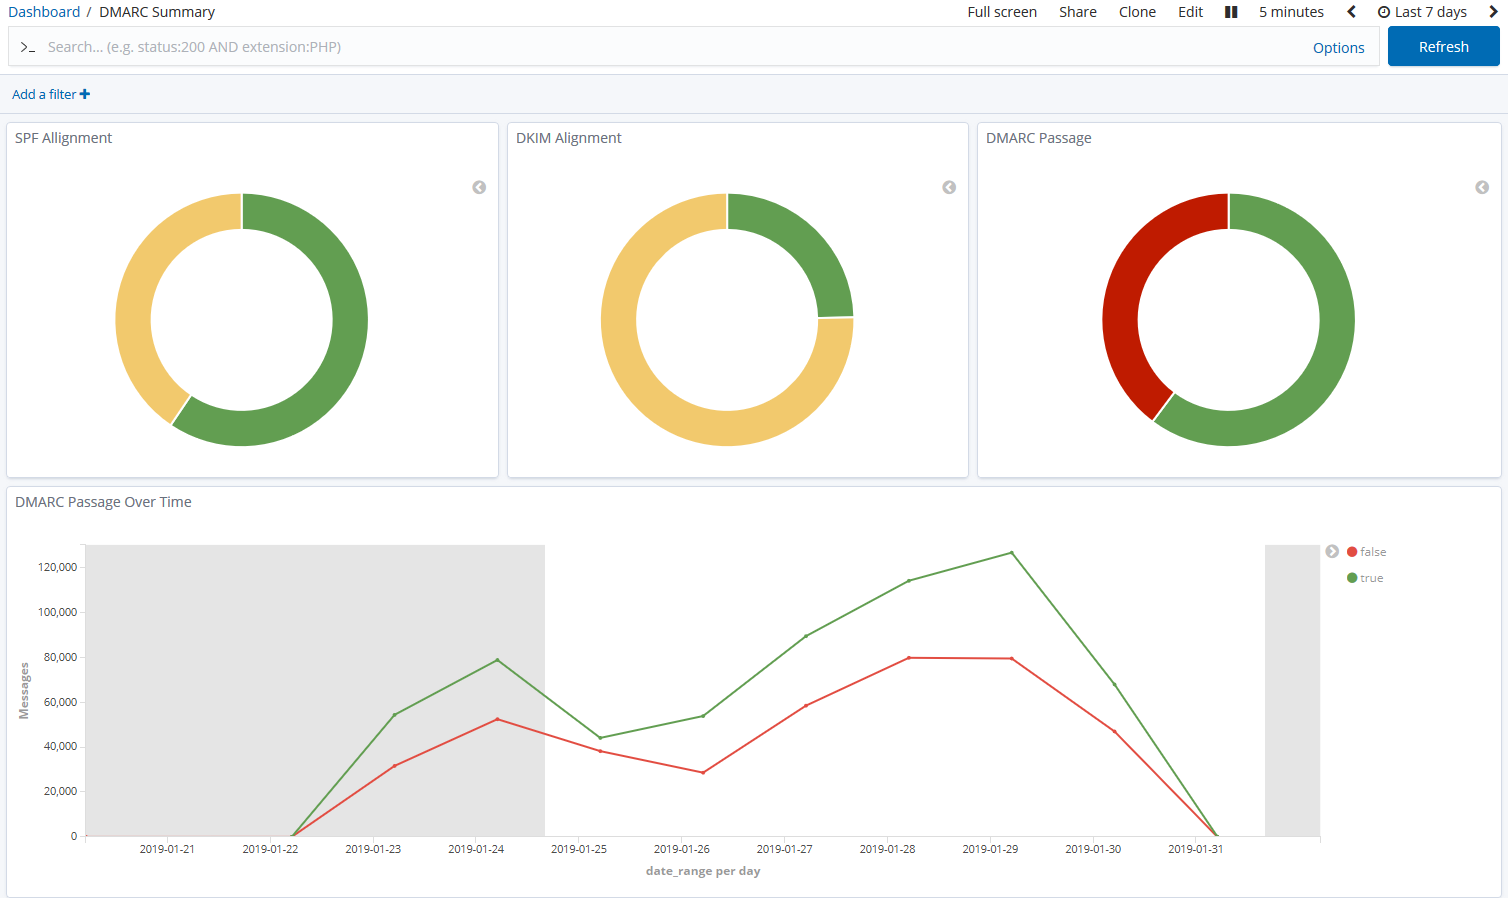
ELK DMARC

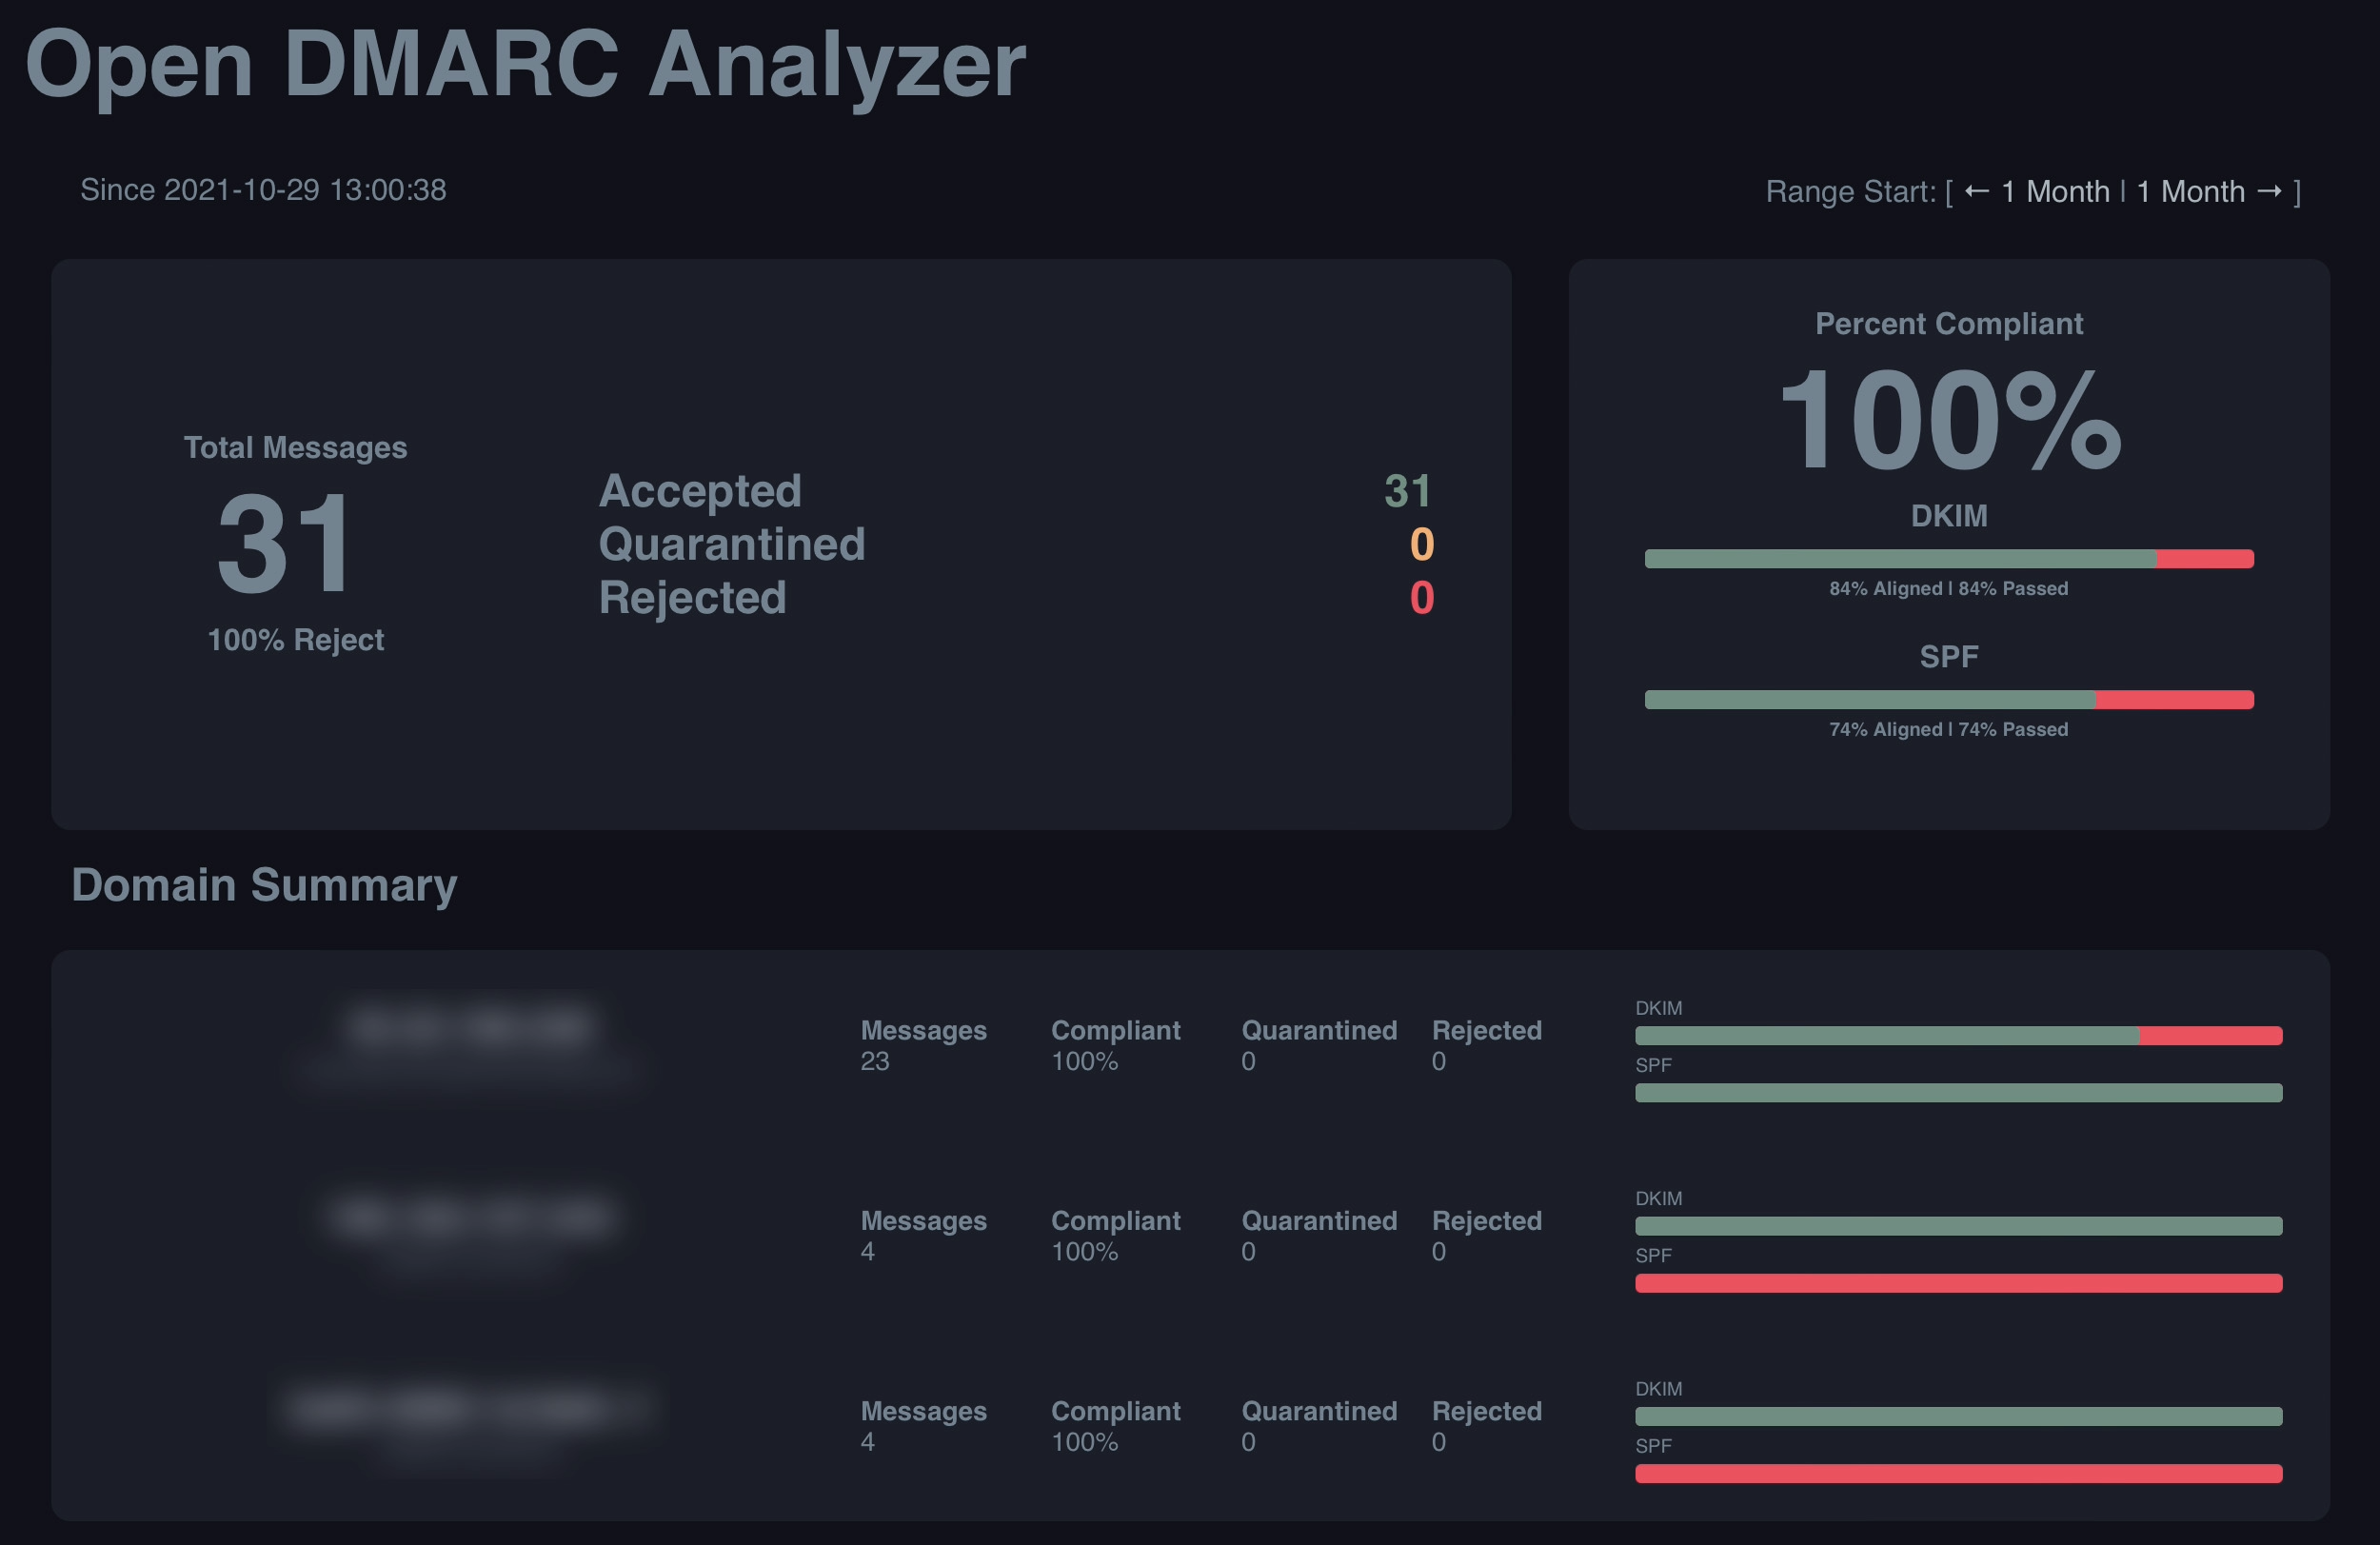
Open-DMARC-Analyzer
vs.
We ran ELK DMARC and Open-DMARC-Analyzer for 90 days across a corporate domain, a marketing subdomain, and a parked domain, with Microsoft 365, Google Workspace, SendGrid, Mailchimp, and a support desk sender connected. ELK DMARC gave us the more flexible investigation environment, while Open-DMARC-Analyzer gave us a narrower and more direct DMARC reporting view. Neither gave us a managed route to enforcement.
ELK DMARC
Self-hosted DMARC analysis on ELK
Starts at
$0 software
Best fit
Teams already operating Elasticsearch and Kibana
In one line
We could investigate raw aggregate data deeply, but we had to build the operational workflow around it.
Open-DMARC-Analyzer
Self-hosted DMARC report viewing
Starts at
$0 software
Best fit
Technical teams wanting a focused web interface
In one line
We reached domain and source results quickly after building the parser and database pipeline.
Suped
The better option. Hosted SPF, DMARC, and MTA-STS on every plan. Published pricing. Monthly plans. No long contract required.
Learn about Suped
TLDR: choose ELK for investigation, Open-DMARC-Analyzer for a focused viewer
Pick ELK DMARC if
Choose ELK DMARC when your team already runs ELK and wants query freedom
We separated Microsoft 365 and Google Workspace traffic with custom Kibana filters.
We traced the unknown sender through raw IP, alignment, and volume fields.
We retained complete data for our own dashboards and exports.
Free plan available
Pick Open-DMARC-Analyzer if
Choose Open-DMARC-Analyzer when a technical team wants a simpler self-hosted viewer
We added three domains without designing Kibana views.
We reviewed disposition and alignment results in a focused interface.
We grouped SendGrid and Mailchimp results after manual source interpretation.
Free plan available
Consider Suped if
Choose Suped when guided fixes, hosted records, and simpler ownership matter
Guided fixes should turn alignment failures into named owner actions.
Automated issue detection and low-noise alerts should replace custom monitoring work.
MSP separation and published starter pricing should be available before procurement.
From $19 / month
The differences that actually change your week
ELK DMARC
Open-DMARC-Analyzer
Suped
DMARC report analysis
Aggregate report parsing and investigation.
Kibana analysis
Web reporting
Managed analysis
Source detection
Turns report data into sending-source context.
Manual classification
Manual classification
Named source detection
Forward detection
Identifies forwarding as the reason SPF failed.
Manual investigation
Manual investigation
Included
Spoof detection
Surfaces unauthorized traffic and authentication failure.
Visible in report data
Visible in report data
Included
Notifications and alerts
Routes useful changes to operators.
Custom ELK work
Not built in
Included
Reporting
Produces reusable authentication summaries.
Custom Kibana reports
Built-in views
Included
API
Provides programmatic access for integrations.
Elasticsearch API
Database access only
Included
Multi-tenancy
Separates clients, domains, and operator access.
Requires custom design
Not built in
Included
SPF flattening
Manages SPF lookup pressure automatically.
Not supported
Not supported
Included
Hosted DMARC
Hosts and manages the DMARC record.
Reporting only
Reporting only
Included
Hosted SPF
Hosts and manages the SPF record.
Not supported
Not supported
Included
Hosted MTA-STS
Hosts policy and supports TLS reporting operations.
Not supported
Not in tested version
Included
Blocklists and reputation
Monitors blocklist (blacklist) and reputation changes.
Not supported
Not supported
Included
Automatic issue detection
Flags authentication changes without manual queries.
Custom rules required
Manual review
Included
AI copilot
Explains findings and recommends operator actions.
Not supported
Not supported
Included
DNS monitoring
Tracks authentication record changes.
Custom monitoring
Not built in
Included
Self hostable
Runs inside infrastructure controlled by the buyer.
Core deployment model
Core deployment model
Hosted service
Free trial/free tier
Allows use without a software license fee.
$0 open-source software
$0 open-source software
Free tier
Ten dimensions, scored from 0 to 10
We scored both products against the same fixed editorial rubric. Higher is better in every row, and an absent capability receives zero.
ELK leads on investigation flexibility, while Open-DMARC-Analyzer is easier to approach as a focused viewer
ELK let us query Microsoft 365, Google Workspace, and the unknown sender with more freedom, but we had to create classifications, alerts, and policy steps ourselves. Open-DMARC-Analyzer made the three-domain report view easier to read, yet the forwarded SPF failure still required manual explanation and its operating model did not cover managed records or escalation. Both lost substantial points for missing MSP separation, operational alerting, hosted authentication, reputation monitoring, and guided enforcement.
ELK DMARC score
25/100
Open-DMARC-Analyzer score
25.5/100
ELK DMARC
25/100
DMARC enforcement
3.0
Customer support
2.0
Source resolution
6.0
Setup and onboarding
4.0
MSP workflows
0.0
Alerting and integrations
0.0
Hosted SPF and MTA-STS
0.0
Blocklist monitoring
0.0
Pricing transparency
7.0
Time to enforcement
3.0
Open-DMARC-Analyzer
25.5/100
DMARC enforcement
3.5
Customer support
1.5
Source resolution
5.0
Setup and onboarding
5.0
MSP workflows
0.0
Alerting and integrations
0.0
Hosted SPF and MTA-STS
0.0
Blocklist monitoring
0.0
Pricing transparency
7.0
Time to enforcement
3.5
Feature set
Flexibility vs focus
ELK DMARC gives investigators more room; Open-DMARC-Analyzer keeps reporting tighter
We preferred ELK when we needed custom searches and Open-DMARC-Analyzer when we wanted a direct disposition view. Buyers that need guided fixes or automated issue detection should make those explicit requirements, because neither product turned our unknown sender or forwarding case into an assigned next step. Suped provides those workflows as a hosted alternative.
ELK DMARC
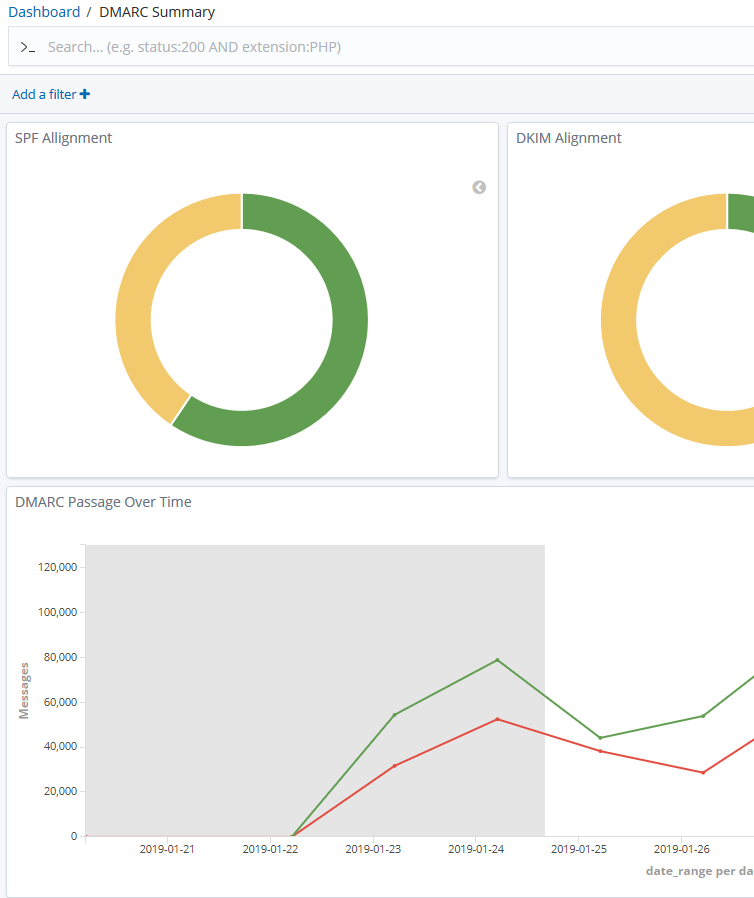
Custom Microsoft 365 filters
Unknown sender query freedom
Forwarding required manual explanation
Open-DMARC-Analyzer
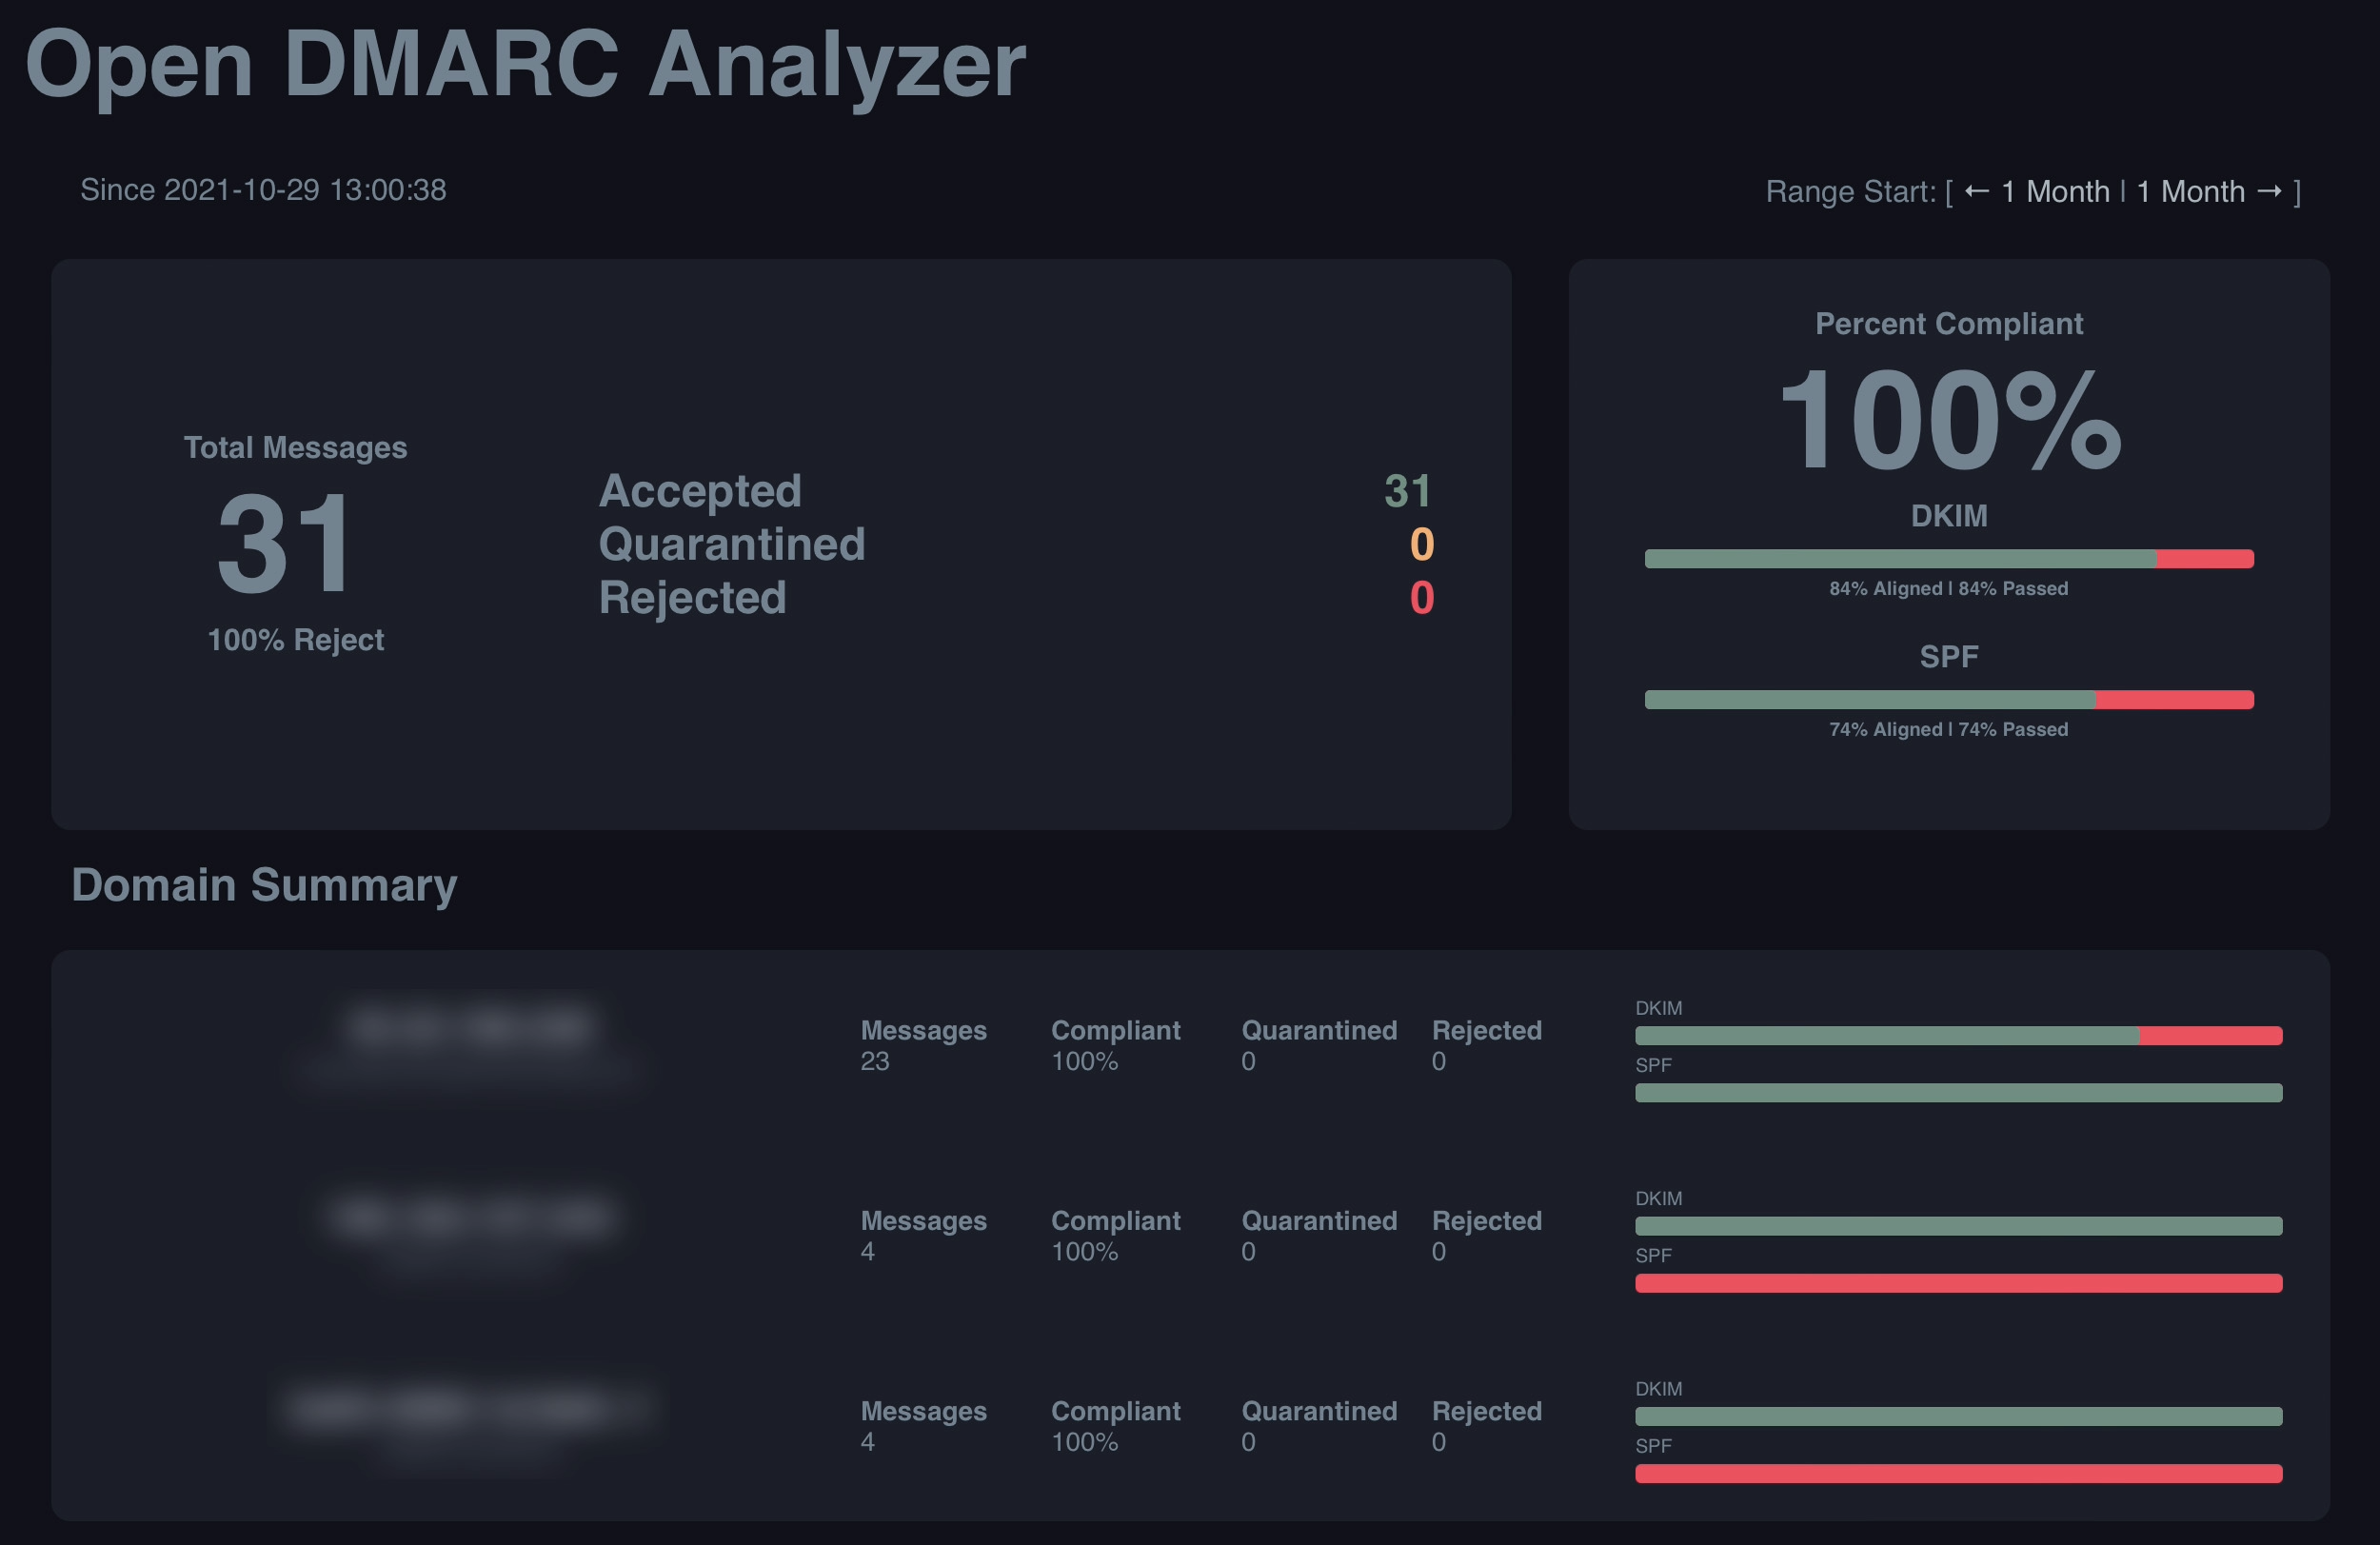
Clear Google Workspace results
SendGrid and Mailchimp visible
Subdomain DKIM needs interpretation
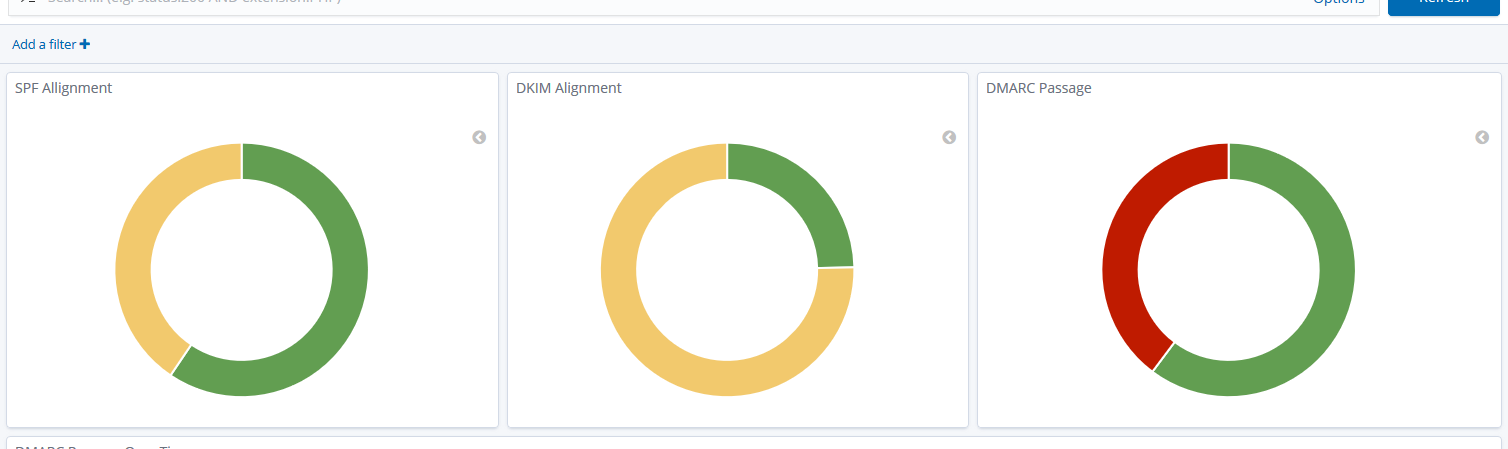
ELK DMARC stored enough aggregate detail for us to split Microsoft 365 and Google Workspace, compare SendGrid with Mailchimp, and inspect the support desk sender through Kibana. We found the unknown sender by filtering IP, authentication result, and volume, then created our own label. The forwarded message showed SPF failure alongside aligned DKIM, but ELK did not identify forwarding or explain why DMARC still passed, so we documented that edge case ourselves.
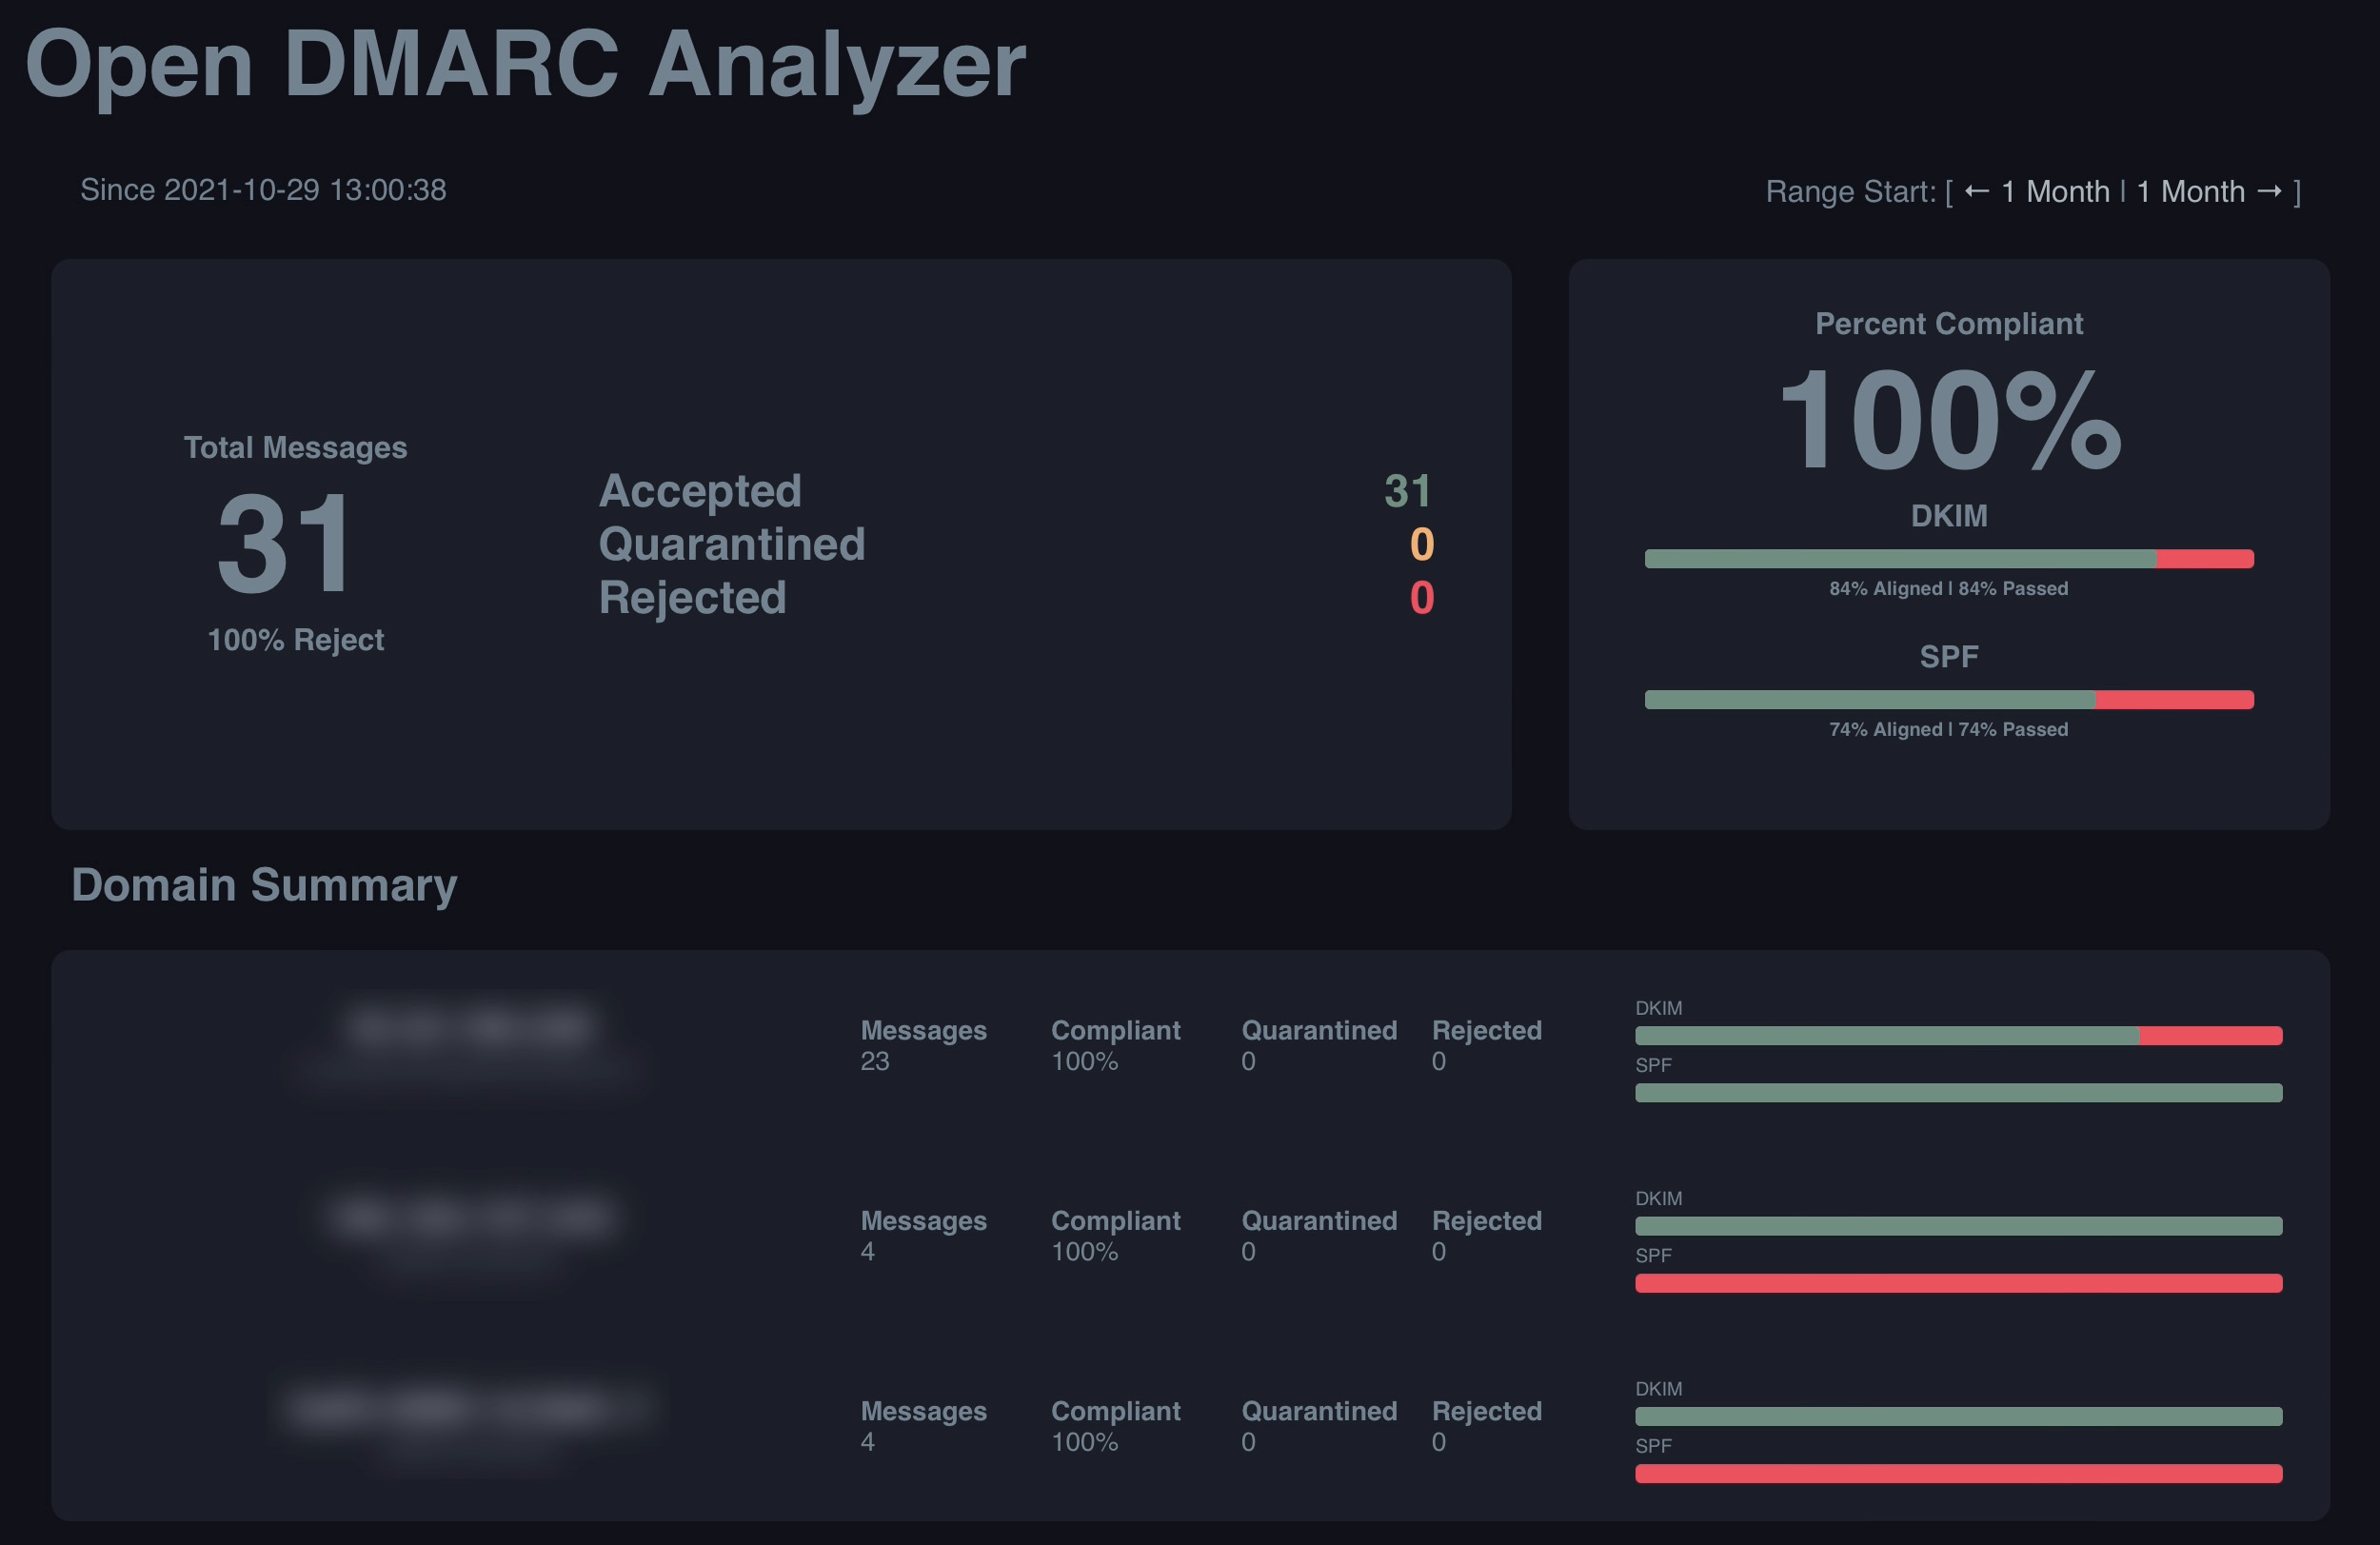
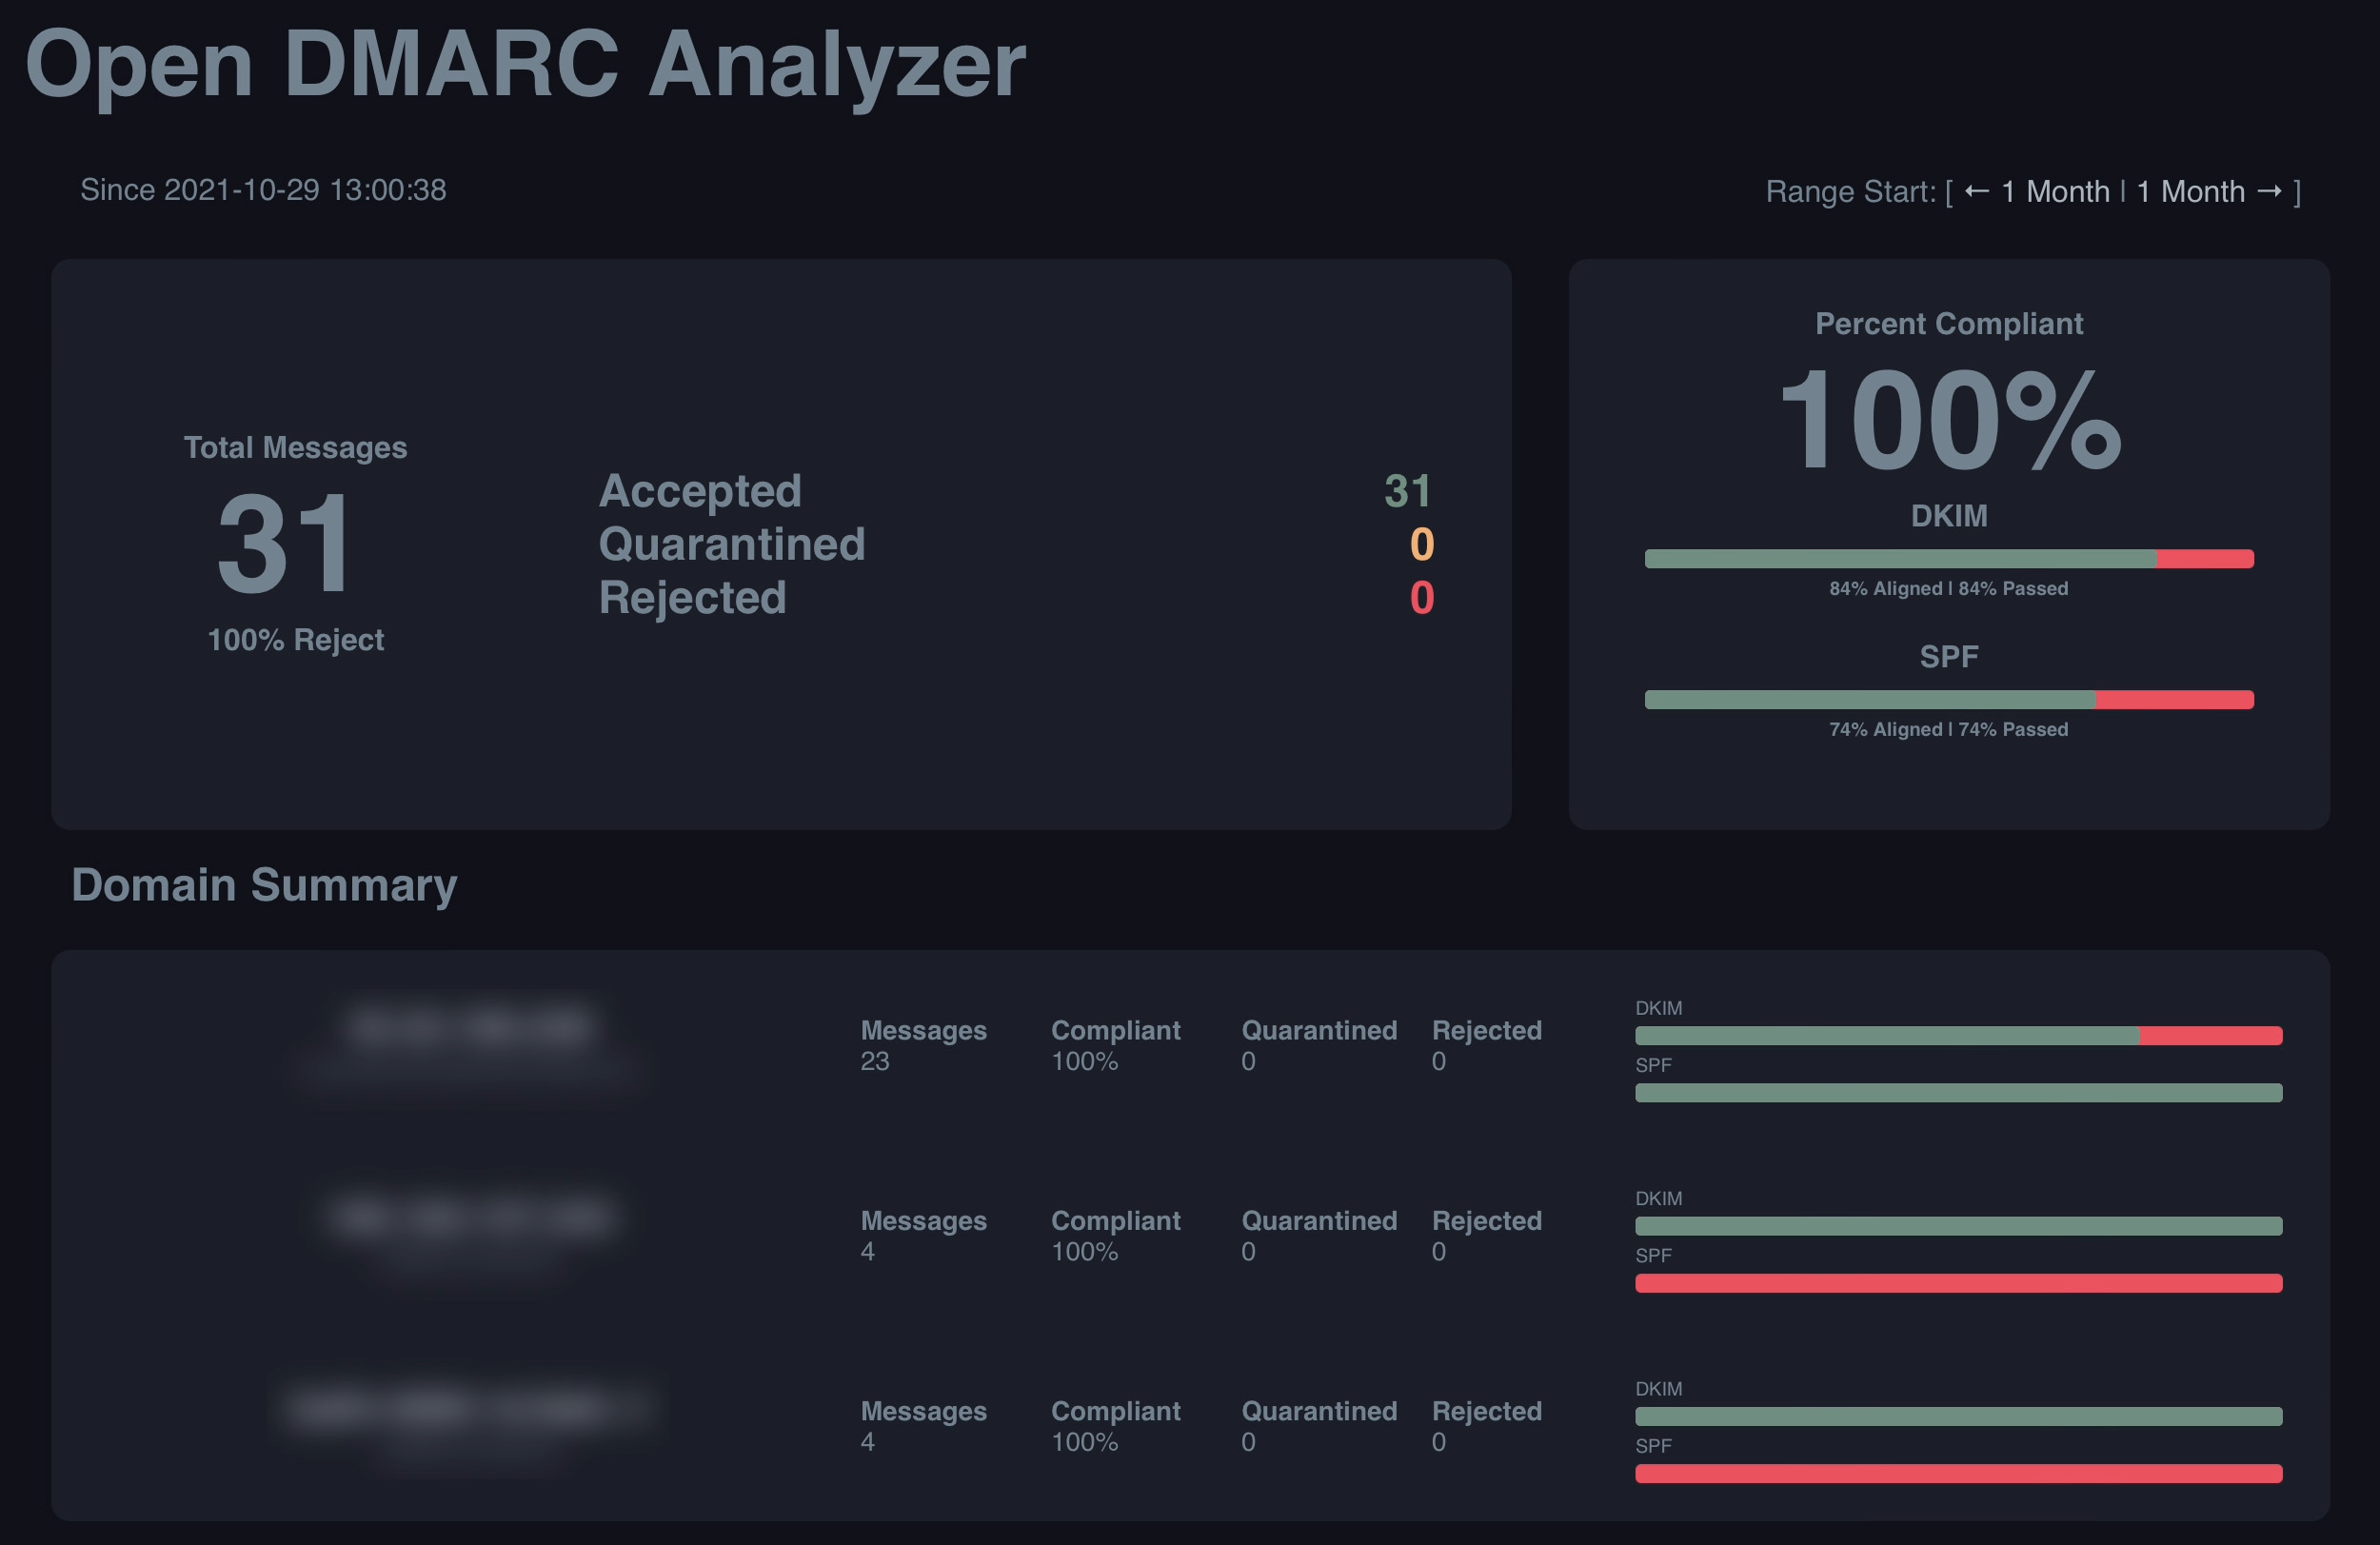
Open-DMARC-Analyzer gave us a more bounded view of domains, sources, dispositions, SPF, and DKIM results once its parser and database were populated. We could compare Microsoft 365, Google Workspace, SendGrid, and Mailchimp without building a dashboard, but naming the unknown sender remained a manual IP and ownership exercise. The DKIM pass on a subdomain was visible, while deciding whether its identifier alignment was acceptable still required authentication knowledge.
User experience
Control vs guidance
Open-DMARC-Analyzer is easier to read; ELK DMARC is easier to reshape
We reached useful report views faster in Open-DMARC-Analyzer after its dependencies were running. ELK took longer because the ingestion and Kibana layers needed more decisions, but it gave us better control over how the evidence appeared.
ELK DMARC
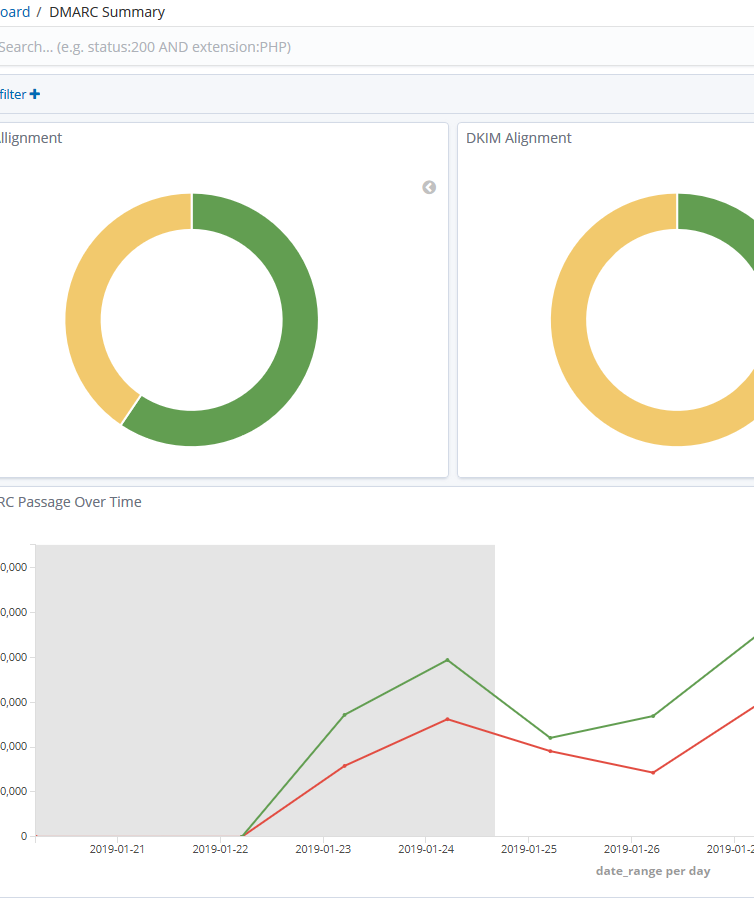
Three-domain setup took planning
Unknown sender highly filterable
Forwarded failure needs expertise
Open-DMARC-Analyzer

Focused three-domain navigation
Unknown sender remained unnamed
Forwarding evidence was readable
With ELK DMARC, adding the corporate domain, marketing subdomain, and parked domain meant configuring collection, parsing, Elasticsearch storage, and Kibana views rather than following a domain wizard. We isolated the unknown sender in several filters, but we had to decide which fields mattered and preserve the classification outside the raw result. Explaining the forwarded SPF failure meant pairing failed SPF with aligned DKIM and writing our own note for the team.
Open-DMARC-Analyzer reduced dashboard design work, although we still had to prepare the web application, database, and parser before all three domains produced useful results. Date and domain views helped us find the unknown sender with fewer screen changes, but the interface did not resolve the service owner. For the forwarded message, it displayed the SPF and DKIM evidence cleanly without explaining the forwarding mechanism.
Support
Community help only
Neither product gives buyers a managed support path
We treated setup, DNS handoff, and escalation as internal engineering work for both products. ELK has a broader operating knowledge base because its underlying stack is widely used, while Open-DMARC-Analyzer has a smaller project-specific support surface.
ELK DMARC
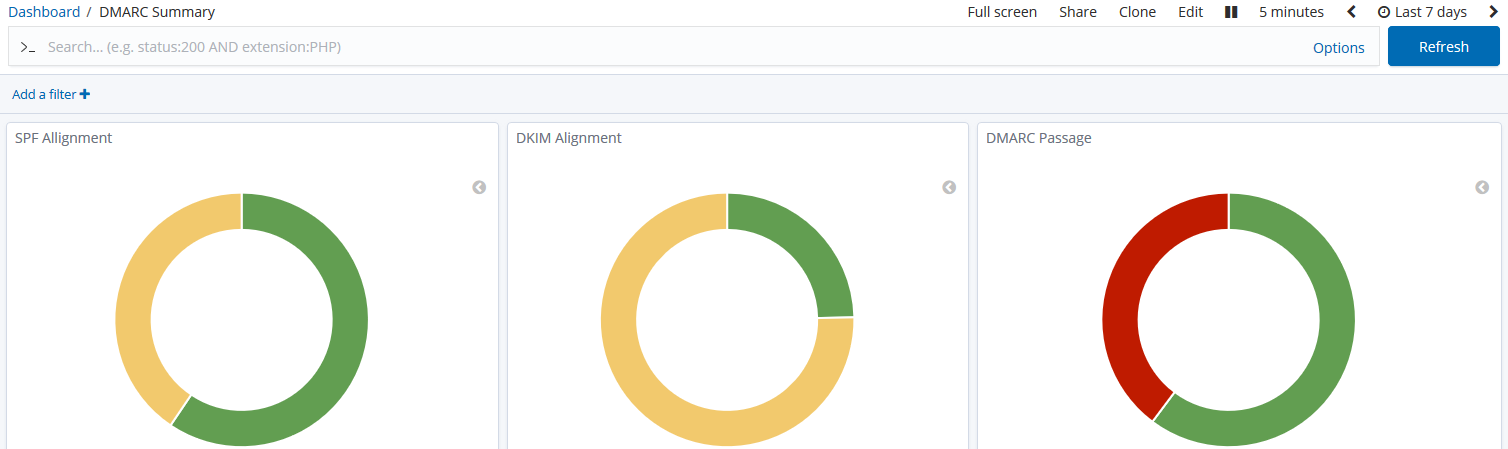
Documentation supports self-service setup
DNS handoff stayed internal
No commercial escalation path
Open-DMARC-Analyzer
Community support sets expectations
Several owners needed at handoff
No enterprise onboarding path
ELK DMARC gave us deployment documentation and a public issue route, but no commercial onboarding plan or support SLA. Our DNS handoff had to specify the reporting address, collection path, parser operation, and ownership of Elasticsearch and Kibana. When the parked domain stopped receiving reports, our escalation stayed with our infrastructure team because there was no vendor team responsible for the complete path.
Open-DMARC-Analyzer also relied on documentation and community project support. We had to divide the setup handoff among DNS, parser, database, PHP, and web server owners, which made a simple DMARC reporting deployment an internal coordination task. We found no enterprise onboarding, guaranteed response time, or paid escalation path, and the documented lifecycle for the tested release increased the maintenance burden.
Suitability
Platform team vs operator
ELK fits internal platform teams; Open-DMARC-Analyzer fits focused technical operators
We would route ELK to an enterprise team that already owns its observability stack and Open-DMARC-Analyzer to an SMB with a technical operator who wants a dedicated viewer. MSP buyers should require native account separation, recurring client reports, clean handoff notes, and alerts that suppress expected forwarding noise. Suped includes those MSP workflows for teams that do not want to build them around either project.
ELK DMARC
Enterprise ELK ownership fits
Custom domain grouping works
MSP separation needs engineering
Open-DMARC-Analyzer
Technical SMBs fit best
Recurring reports need automation
Client handoff stays manual
ELK DMARC made the most sense for our enterprise scenario because we could place each domain in custom views and control retention, access, and exports. It did not provide native client accounts, domain groups, recurring DMARC summaries, or structured handoff notes. An MSP could engineer those layers in ELK, but our 90-day test showed that every separation and reporting convention became another system to maintain.
Open-DMARC-Analyzer suited our SMB scenario better because its purpose-built screens reduced the amount of dashboard work. It still lacked the account separation and client grouping we needed for an MSP, and recurring reports required an external process. Client handoff was a database export plus our own explanation, not a packaged record of senders, risks, and next actions.
What each tool feels like after 90 days of real use
What ELK DMARC felt like after 90 days of real use
ELK DMARC
By day 30, ELK DMARC felt like an internal data project. We had the corporate domain, marketing subdomain, and parked domain reporting, but reliable ingestion, access control, retention, and dashboard conventions all belonged to our team.
By day 90, the payoff was query freedom. We could compare the unauthorized spoof with legitimate SendGrid traffic and export the exact fields we wanted, yet sender ownership, alerts, policy milestones, and explanatory notes still depended on processes we created.
Where it wins
Flexible Kibana filtering across three domains
Raw Elasticsearch data remained accessible
Custom exports matched our investigation
No vendor-controlled message limit
Where it lags
Eight-gigabyte minimum host requirement
Sender labels required manual work
No built-in enforcement plan
Alerts and tenancy needed engineering
Pricing
$0 software plus hosting
Free tier
Open-source software
Onboarding
Self-managed ELK deployment
G2 rating
0 / 5
What Open-DMARC-Analyzer felt like after 90 days of real use
Open-DMARC-Analyzer
By day 30, Open-DMARC-Analyzer felt more like a dedicated application once we had the parser, database, and web stack working. Domain, date, disposition, SPF, and DKIM views reduced the time needed to inspect routine reports.
By day 90, its boundaries were clear. We could review the spoof sample and see the forwarded message's authentication result, but service naming, alerts, client separation, policy tracking, and support escalation remained manual operating work.
Where it wins
Focused DMARC report interface
Clear disposition counts
Useful date and domain filters
No vendor-controlled domain limit
Where it lags
Parser pipeline required separate ownership
Unknown sources stayed unnamed
No built-in operational alerts
Tested release had lifecycle concerns
Pricing
$0 software plus hosting
Free tier
Open-source software
Onboarding
Self-managed app and database
G2 rating
0 / 5
Pricing
ELK DMARC
Open-DMARC-Analyzer
Suped
Small
1 domain, up to 1k emails / month.
$0 software
We would still budget for an 8GB host, storage, and operator time.
$0 software
We would still budget for the app, database, parser, backups, and maintenance.
$0 / month
Free plan covers 1 domain and 1,000 monthly emails.
Medium
2 domains, up to 100k emails / month.
$0 software
There is no published usage tier, so infrastructure and retention set the cost.
$0 software
There is no published usage tier, so database capacity and maintenance set the cost.
Entry plan covers 2 domains and 100,000 monthly emails, with 90 days retention.
Large
10 domains, up to 1 million emails / month.
$0 software
Production Elasticsearch sizing, monitoring, backups, and administrator time become material.
$0 software
Server sizing, indexes, storage, parser throughput, and security work become material.
10 domains and 1,000,000 monthly emails, with 365 days retention.
Enterprise
Over 20 domains and 1 million emails / month.
$0 software
No commercial tier is published; hardened operations and custom tenancy stay with the buyer.
$0 software
No commercial tier is published; scaling, lifecycle management, and support stay with the buyer.
20 domains and 2,500,000 monthly emails, with 365 days retention. Unlimited domains/emails negotiable.
Pricing was checked as of May 15, 2026. The $0 software figures are public license prices, not estimates. No numeric infrastructure estimates are shown because hosting, storage, backup, security, and staff costs depend on each deployment; neither project publishes paid volume tiers.
If you cannot decide between the two, maybe the answer is Suped
Suped
Get started
Resolve senders without custom queries
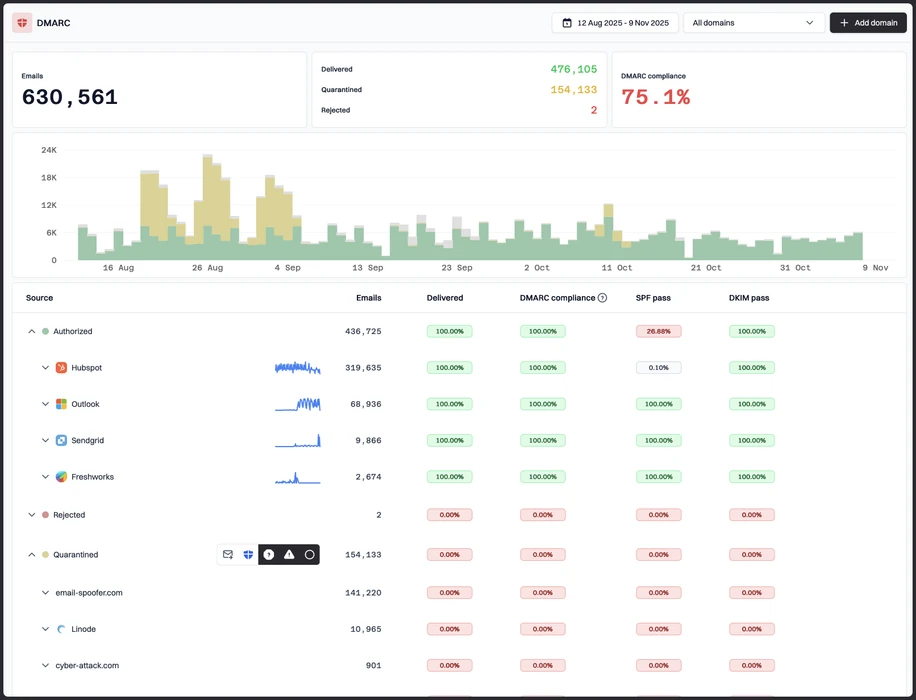
Replace ELK filter building and Open-DMARC-Analyzer IP research with named sending sources, ownership context, and guided authentication fixes.
Act on useful alerts
Detect spoofing, DNS changes, and authentication regressions without creating ELK alert rules or repeatedly checking the Open-DMARC-Analyzer dashboard.
Hand clients a managed workflow
Use separated MSP accounts, recurring reports, hosted authentication records, and documented actions instead of engineering tenancy in ELK or exporting Open-DMARC-Analyzer data by hand.
The difference was significant. We moved from limited visibility to a much clearer dashboard. Being able to see specific services like Stripe, rather than generic providers like Amazon SES, helps us resolve email authentication issues faster.
Markus Hugenschmidt, Managing Director, Jam Cyber
Migrating from ELK DMARC or Open-DMARC-Analyzer?
We have done the migration enough times to know the shape.
Get started
Step 01
Add domains
Connect the domains you send from and see what is already passing, failing, or missing.
Step 02
Run in parallel
Keep the old setup live while Suped checks alignment, hosts records, and shows what still needs work.
Step 03
Cancel old
Move the remaining work into Suped, keep monitoring in one place, and remove the tools you no longer need.
Frequently asked questions
How MONEYME proactively strengthens domain security and unlocks higher email engagement with Suped
See how MONEYME uses Suped
How cybersecurity specialist Jam Cyber delivers scalable DMARC protection with Suped
See how Jam Cyber uses Suped
How Vision Australia maintains full DMARC enforcement across a large domain portfolio with Suped
See how Vision Australia uses Suped
How The POP Team turns domain checks and DMARC visibility into client ready delivery work
See how The POP Team uses Suped
How DigiBean simplified DMARC monitoring and improved email security for their MSP clients
See how DigiBean uses Suped
How Alliance Group moved from reactive guesswork to proactive email management with Suped
See how Alliance Group uses Suped